Offline evidence copy
A full copy of files and database is stored before cleanup, so nothing useful is lost.

For owners whose site redirects visitors, shows spam, or got a malware notice from the host: we clean files, database, and server, then close the way in. From $550.
100%
Files compared with clean copies
3layers
Files, database, server cleaned
How your project runs
01 · FreeTeams we have built for:














The Problem
Most infections stay quiet for weeks. They surface when a customer mentions a strange redirect, your host suspends the account, or a scanner flags your domain.
Hidden redirect
Only some visitors get sent away, so you never see it.
Hidden redirect
We browse as a first-time phone visitor from Google and remove the trigger rule.
Dirty backup
Restoring an old backup brings the backdoor straight back.
Dirty backup
Every file is compared with a trusted copy before anything is restored.
Rogue jobs
A cron job nobody created rewrites files every hour.
Rogue jobs
Cron jobs, extra FTP and SSH users, and server rules are audited and cleaned.
Open door
The outdated module that let them in is still there.
Open door
The entry point is patched or replaced before the cleaned site goes live.
Your host's email lands at 7 a.m.: malware found in your account, suspension unless it's cleaned this week. In the file manager, dozens of PHP files changed last Tuesday, and none of them by your developer. Your contact form now sends spam to strangers, and a pharmacy link sits in your footer. Someone restores last month's backup, and by Friday the files are back, because the backdoor was in that backup too. Meanwhile, a cron job nobody created rewrites index.php every hour.
We start with a full copy of the site and database, kept offline as evidence. Then we compare every file with a clean source: your git history, the vendor's release, or the last backup we can trust. Injected database rows, rogue cron jobs, extra FTP and SSH users, and rewritten server rules go next. We close the entry point before the clean site goes back, so the cleanup holds instead of repeating every week.
Every file compared
Each file is checked against a clean copy instead of trusting a scanner's verdict alone.
Database cleaned too
Injected scripts and spam links come out of content tables, not just the files on disk.
Entry point closed first
The outdated module, leaked password, or upload hole is fixed before the clean site returns.
Our Website Malware Removal Process
You approve the cleanup plan before any file changes, see the list of what we removed, and confirm the site works before warnings go to review.
We look at the symptoms you've seen, your host's notice, and any warnings in Google Search Console or browsers. You get a first read on the likely infection, what to avoid for now (restoring or deleting files), and a fixed price.
What's Included
A full offline copy, a file-by-file comparison, database and server cleanup, the entry point patched, warning reviews requested, and a written list of everything removed.
Compare Options
Scanner subscriptions cost little and watch daily, and some hosts clean infected accounts for free. Here is where each fits a website malware cleanup.
| Feature | DeveloperLookBest fit | Scanner subscription | Host cleanup |
|---|---|---|---|
| Upfront cost | From $550, fixed price | Low monthly fee | Often free with hosting |
| Daily scanning | Separate monitoring plan | Sometimes, account level | |
| Custom code reviewed | Yes, read by an engineer | Signature matches only | |
| Database cleanup | Common patterns only | Rarely included | |
| Server jobs and users | Cron, FTP, and SSH checked | Account level only | |
| Entry point fixed | Patched before the site returns | Firewall rule, if any | |
| Warning reviews | Google and blocklists requested | Sometimes included | |
| Re-clean if it returns | Free within your plan window | While you stay subscribed | Case by case |
Projects We've Built
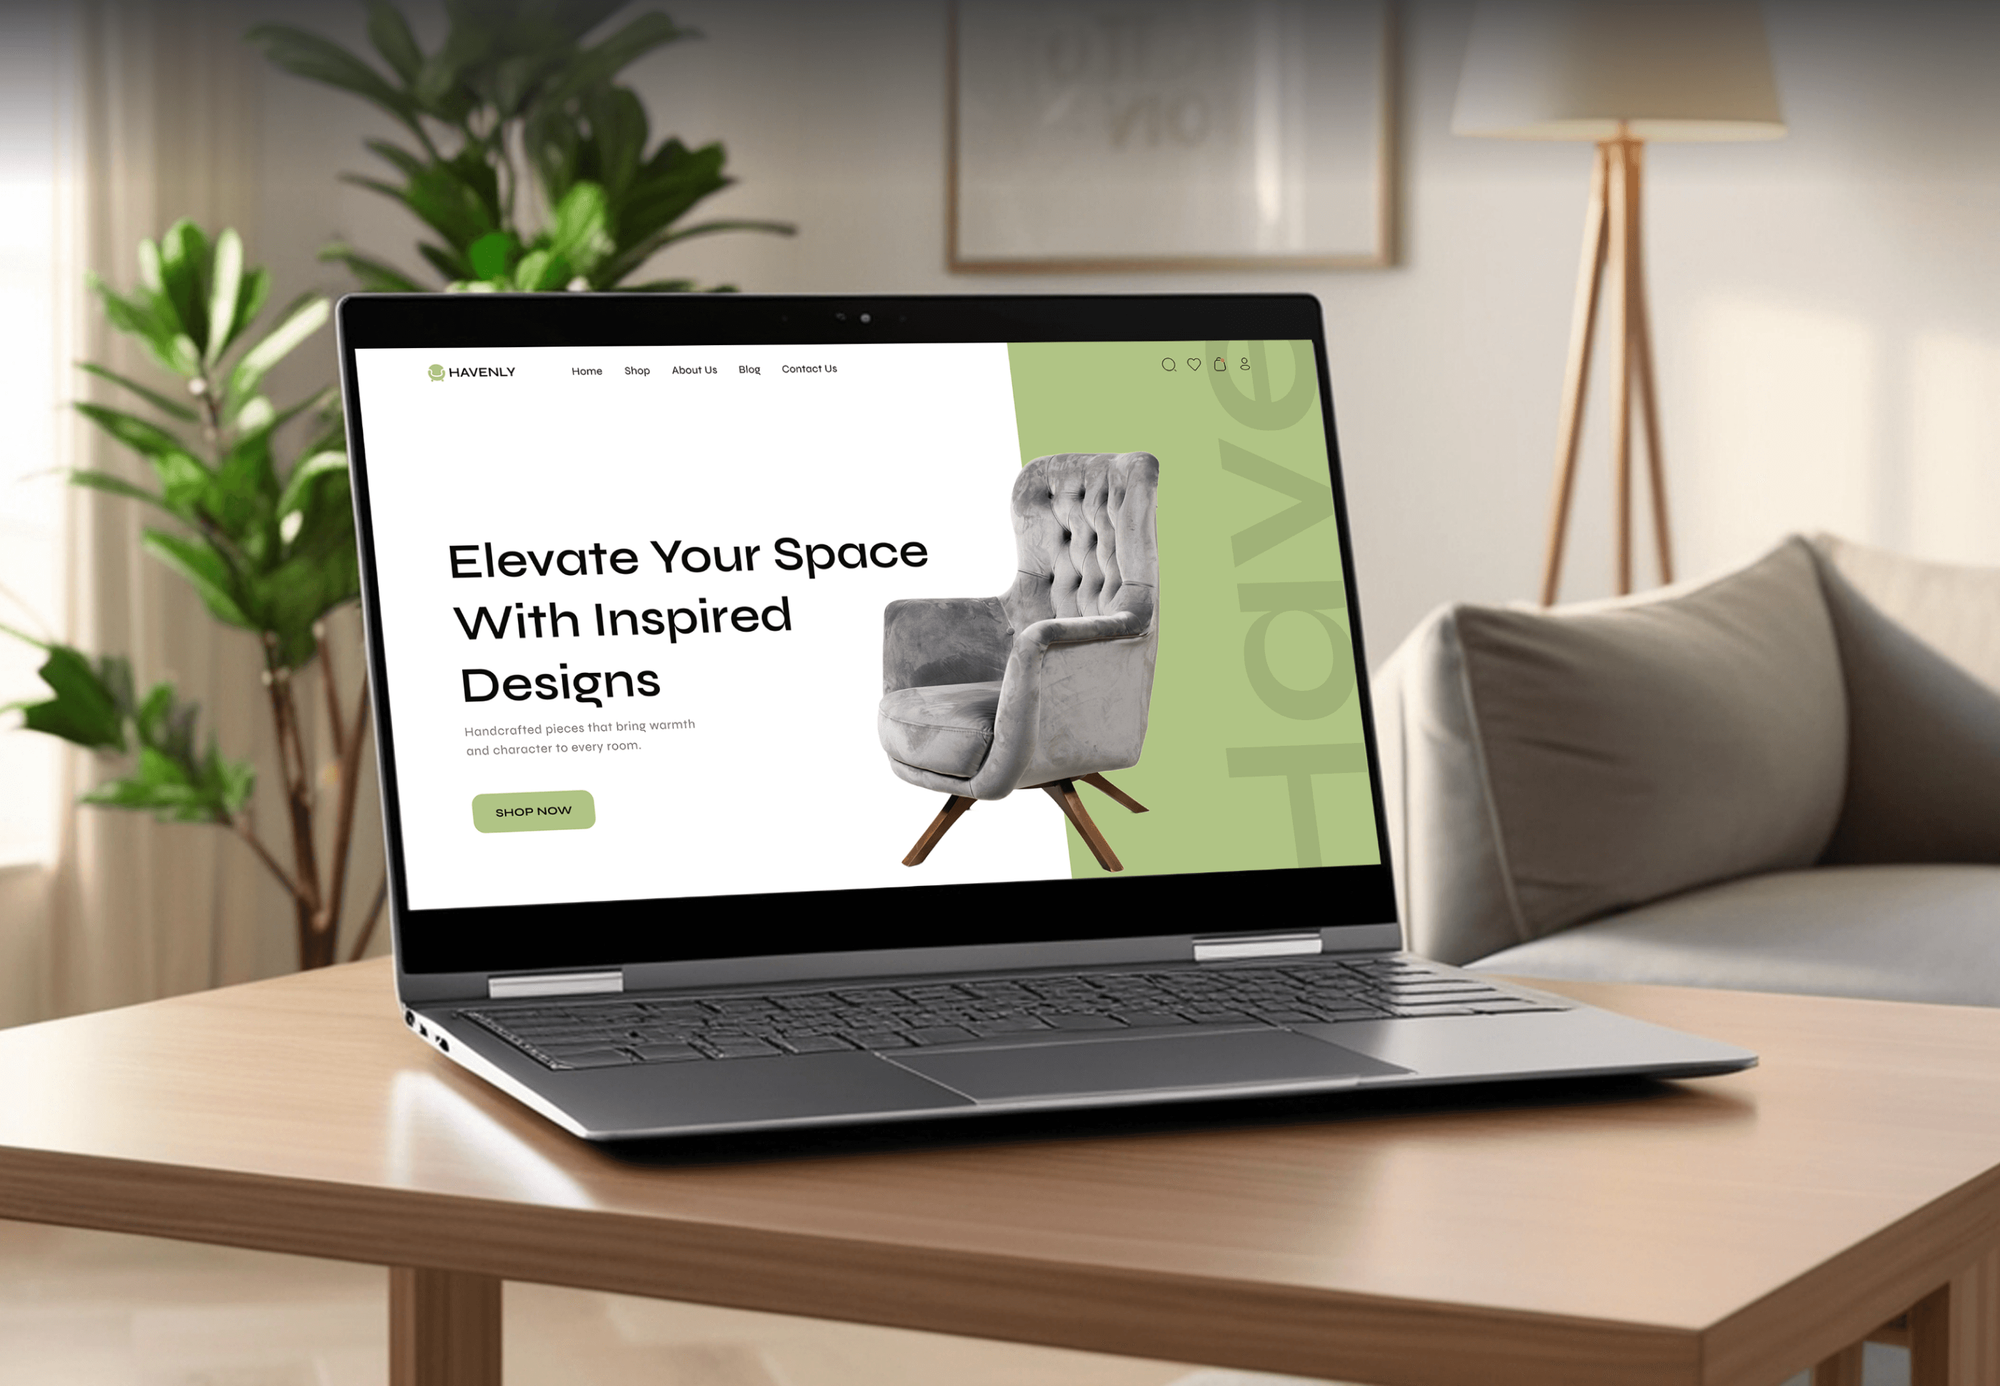
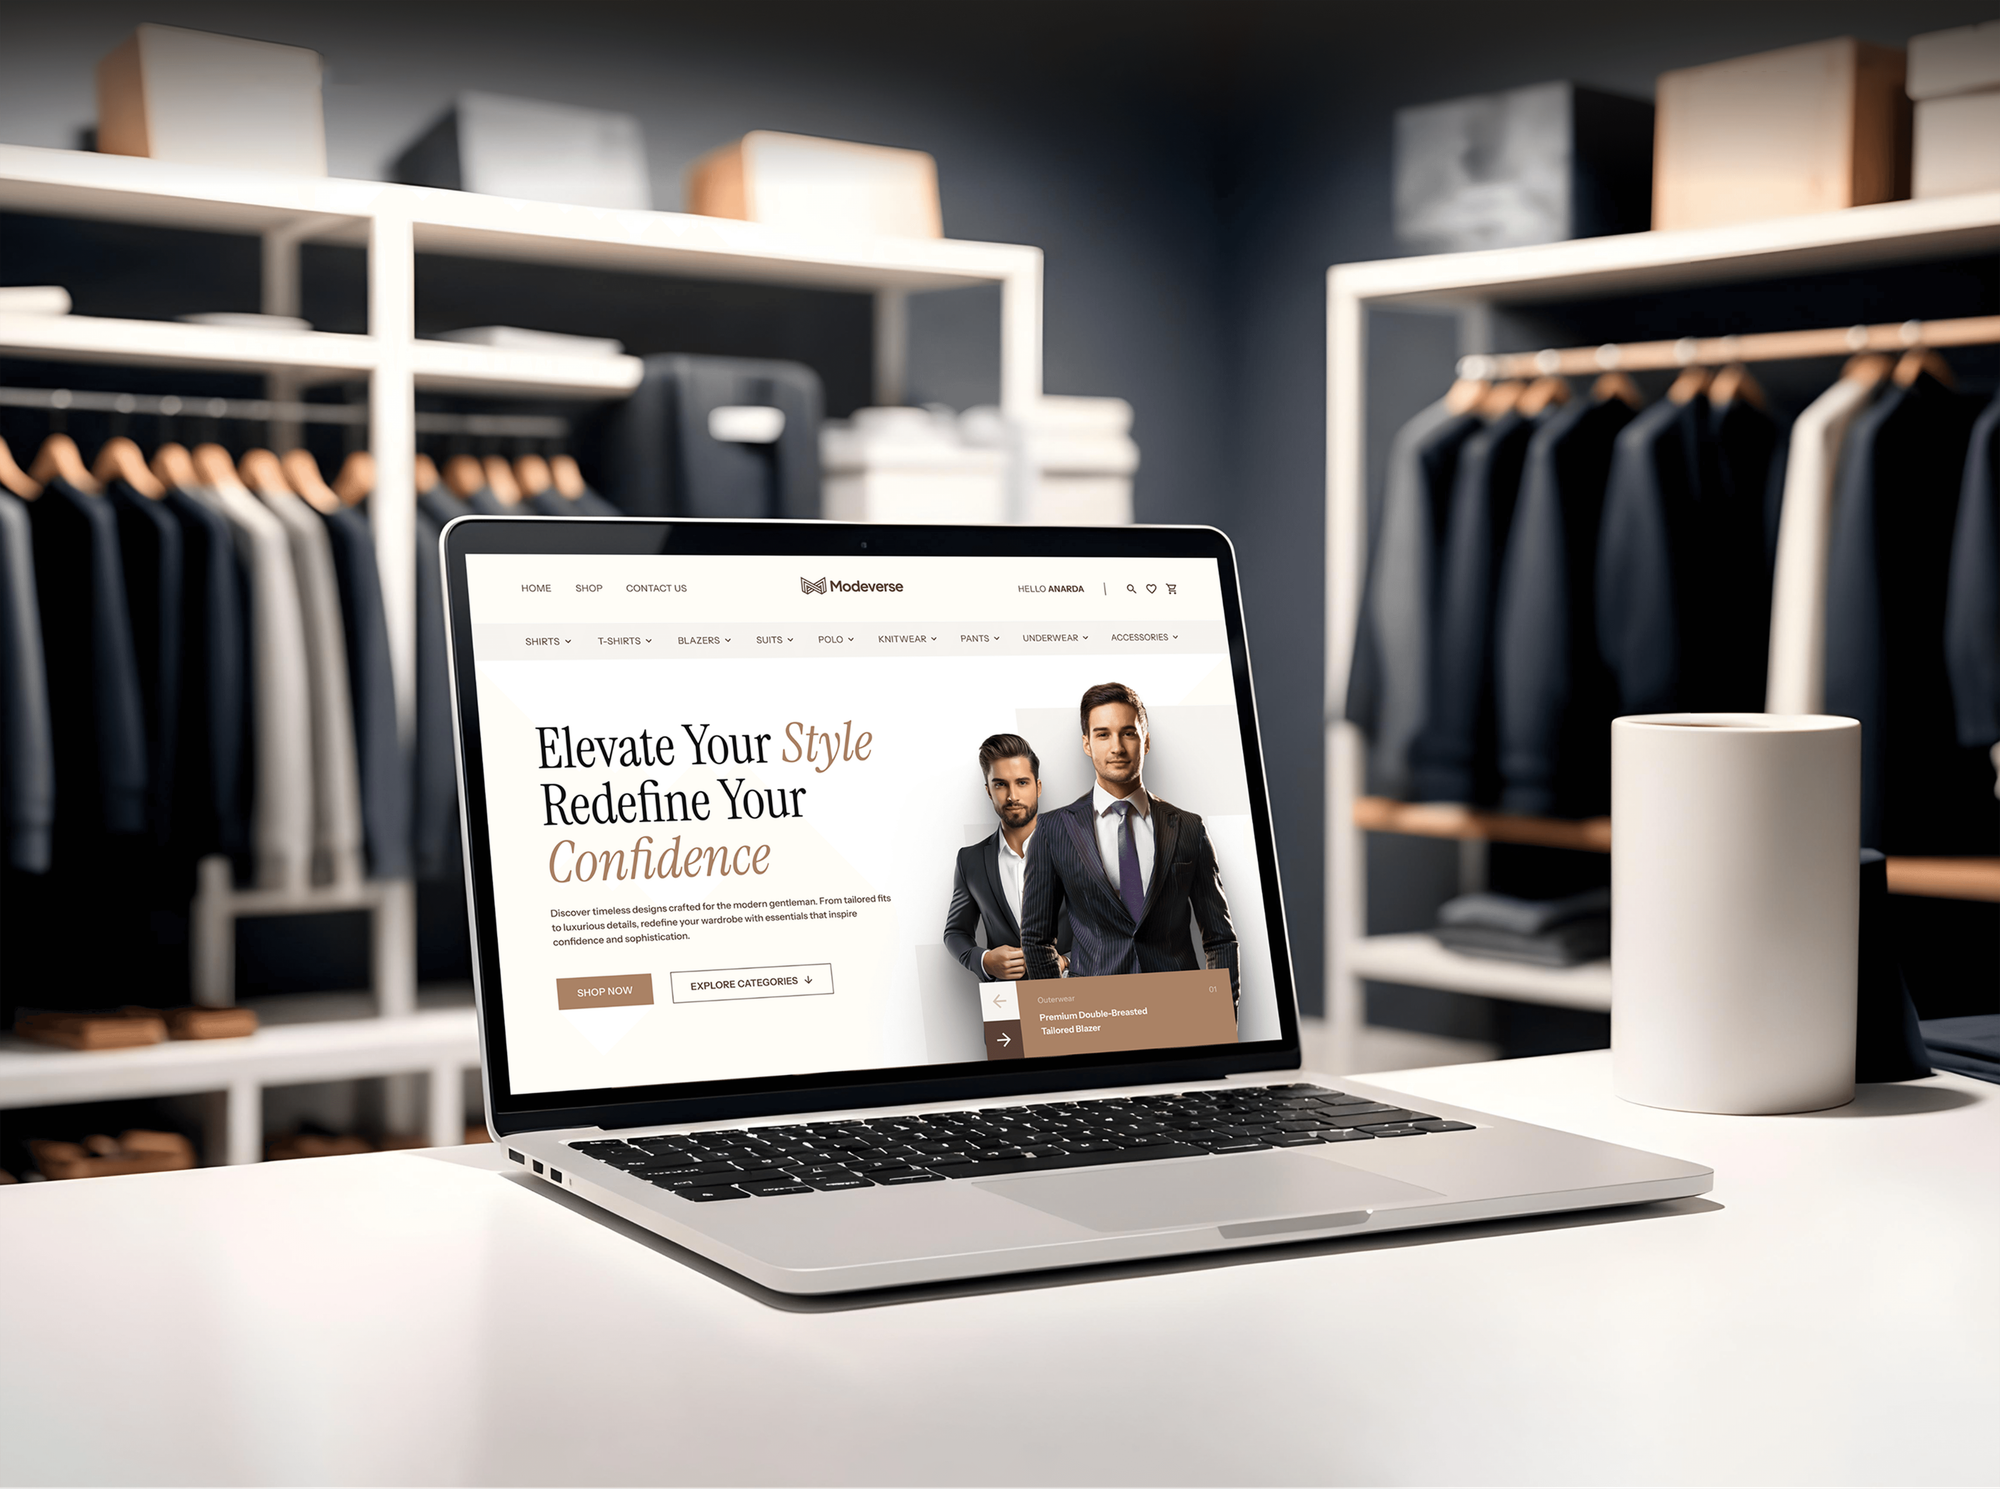
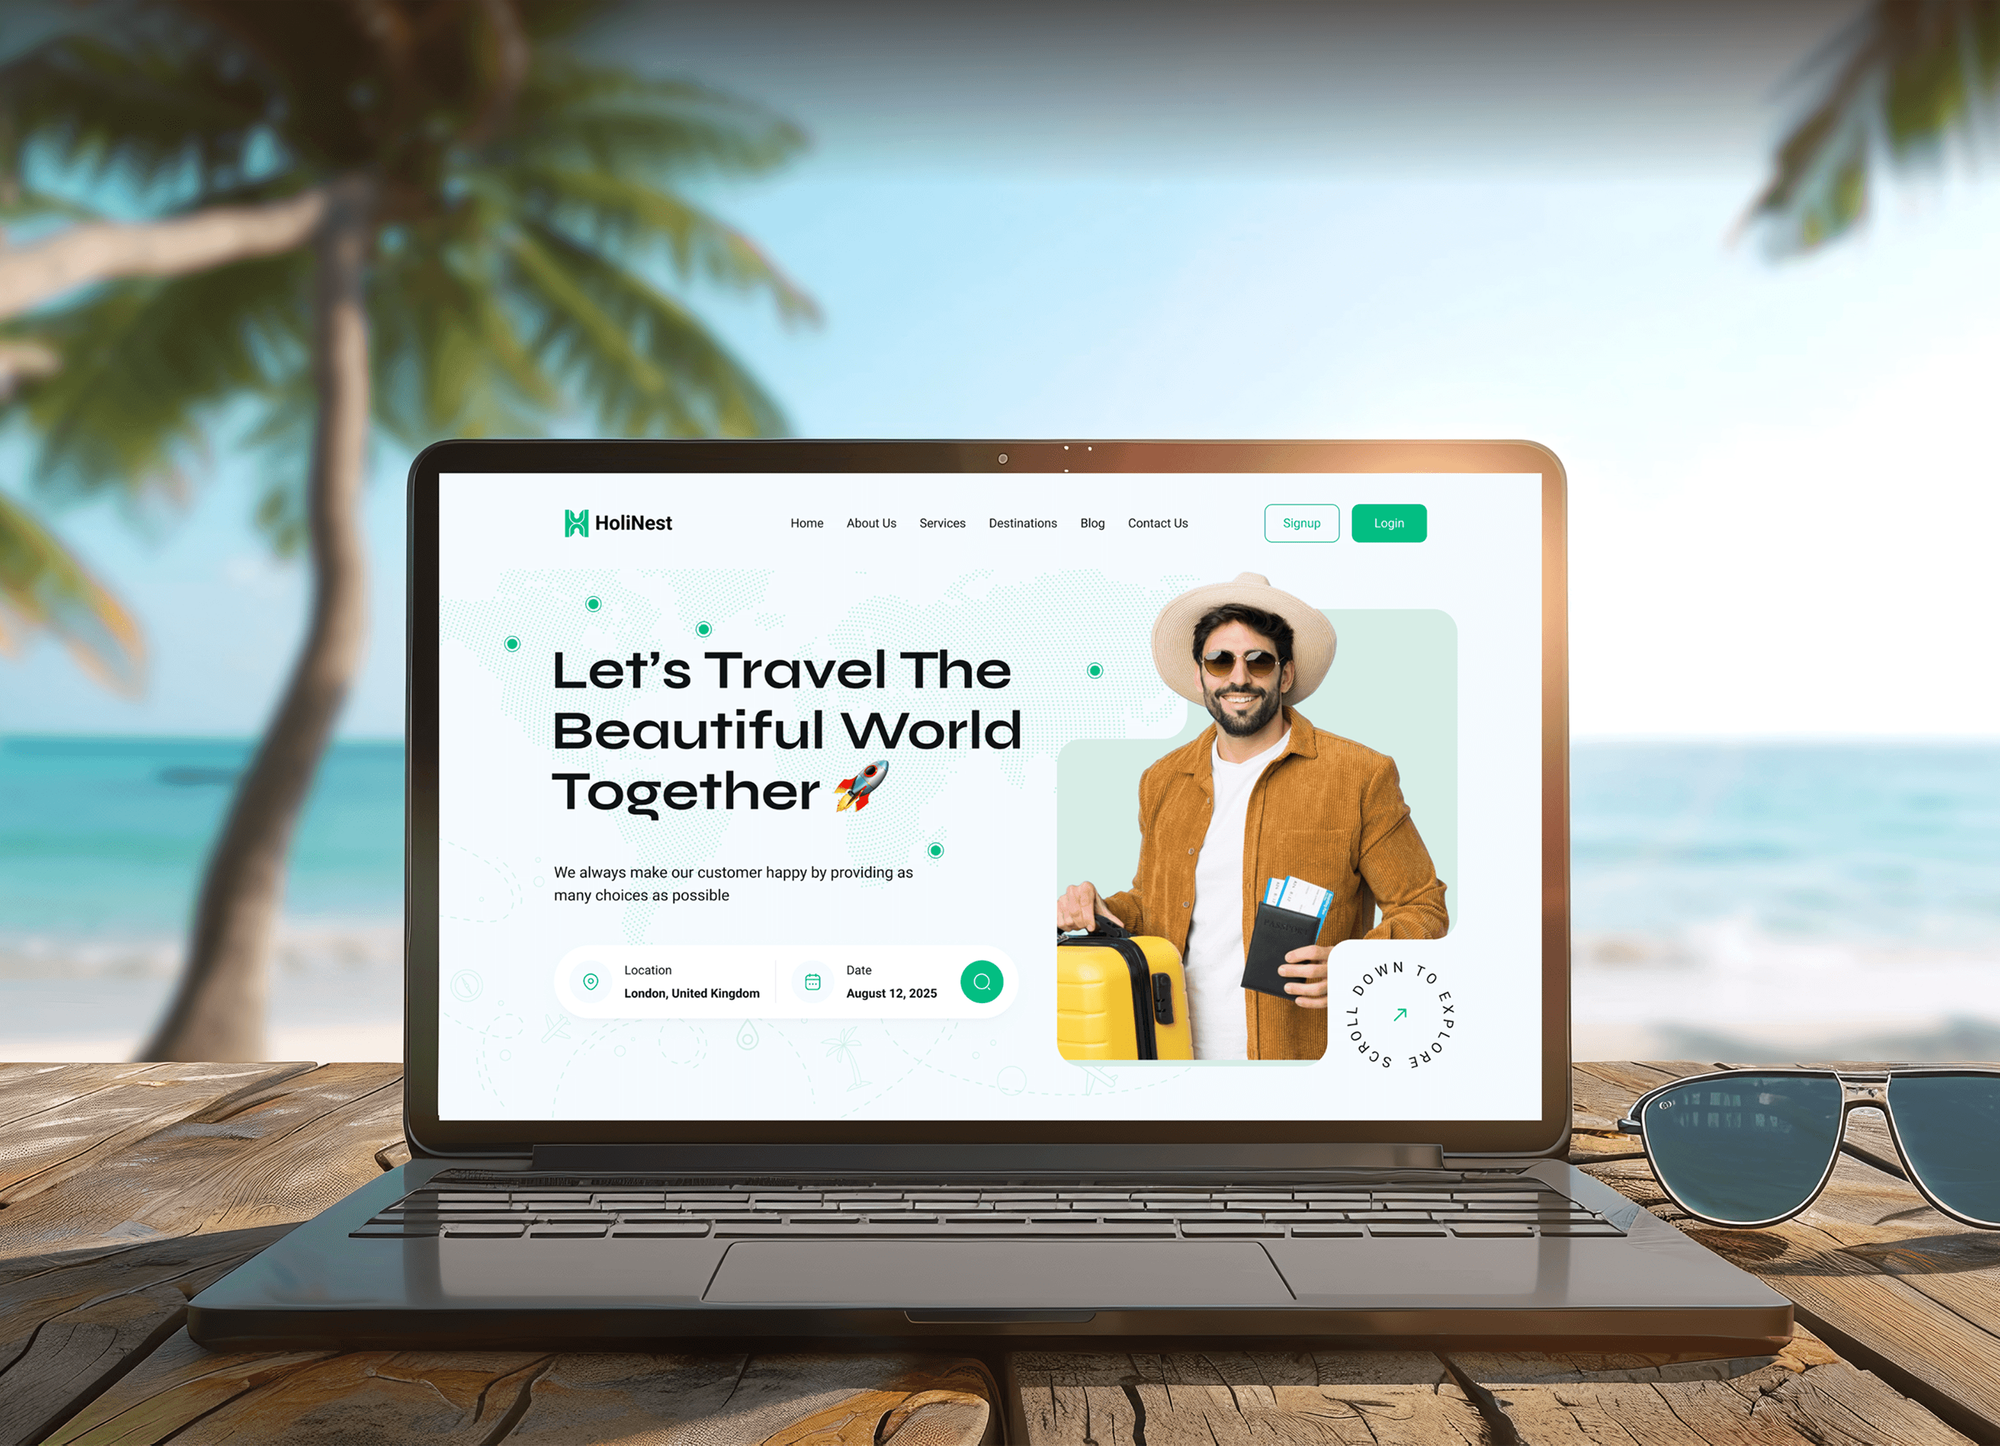
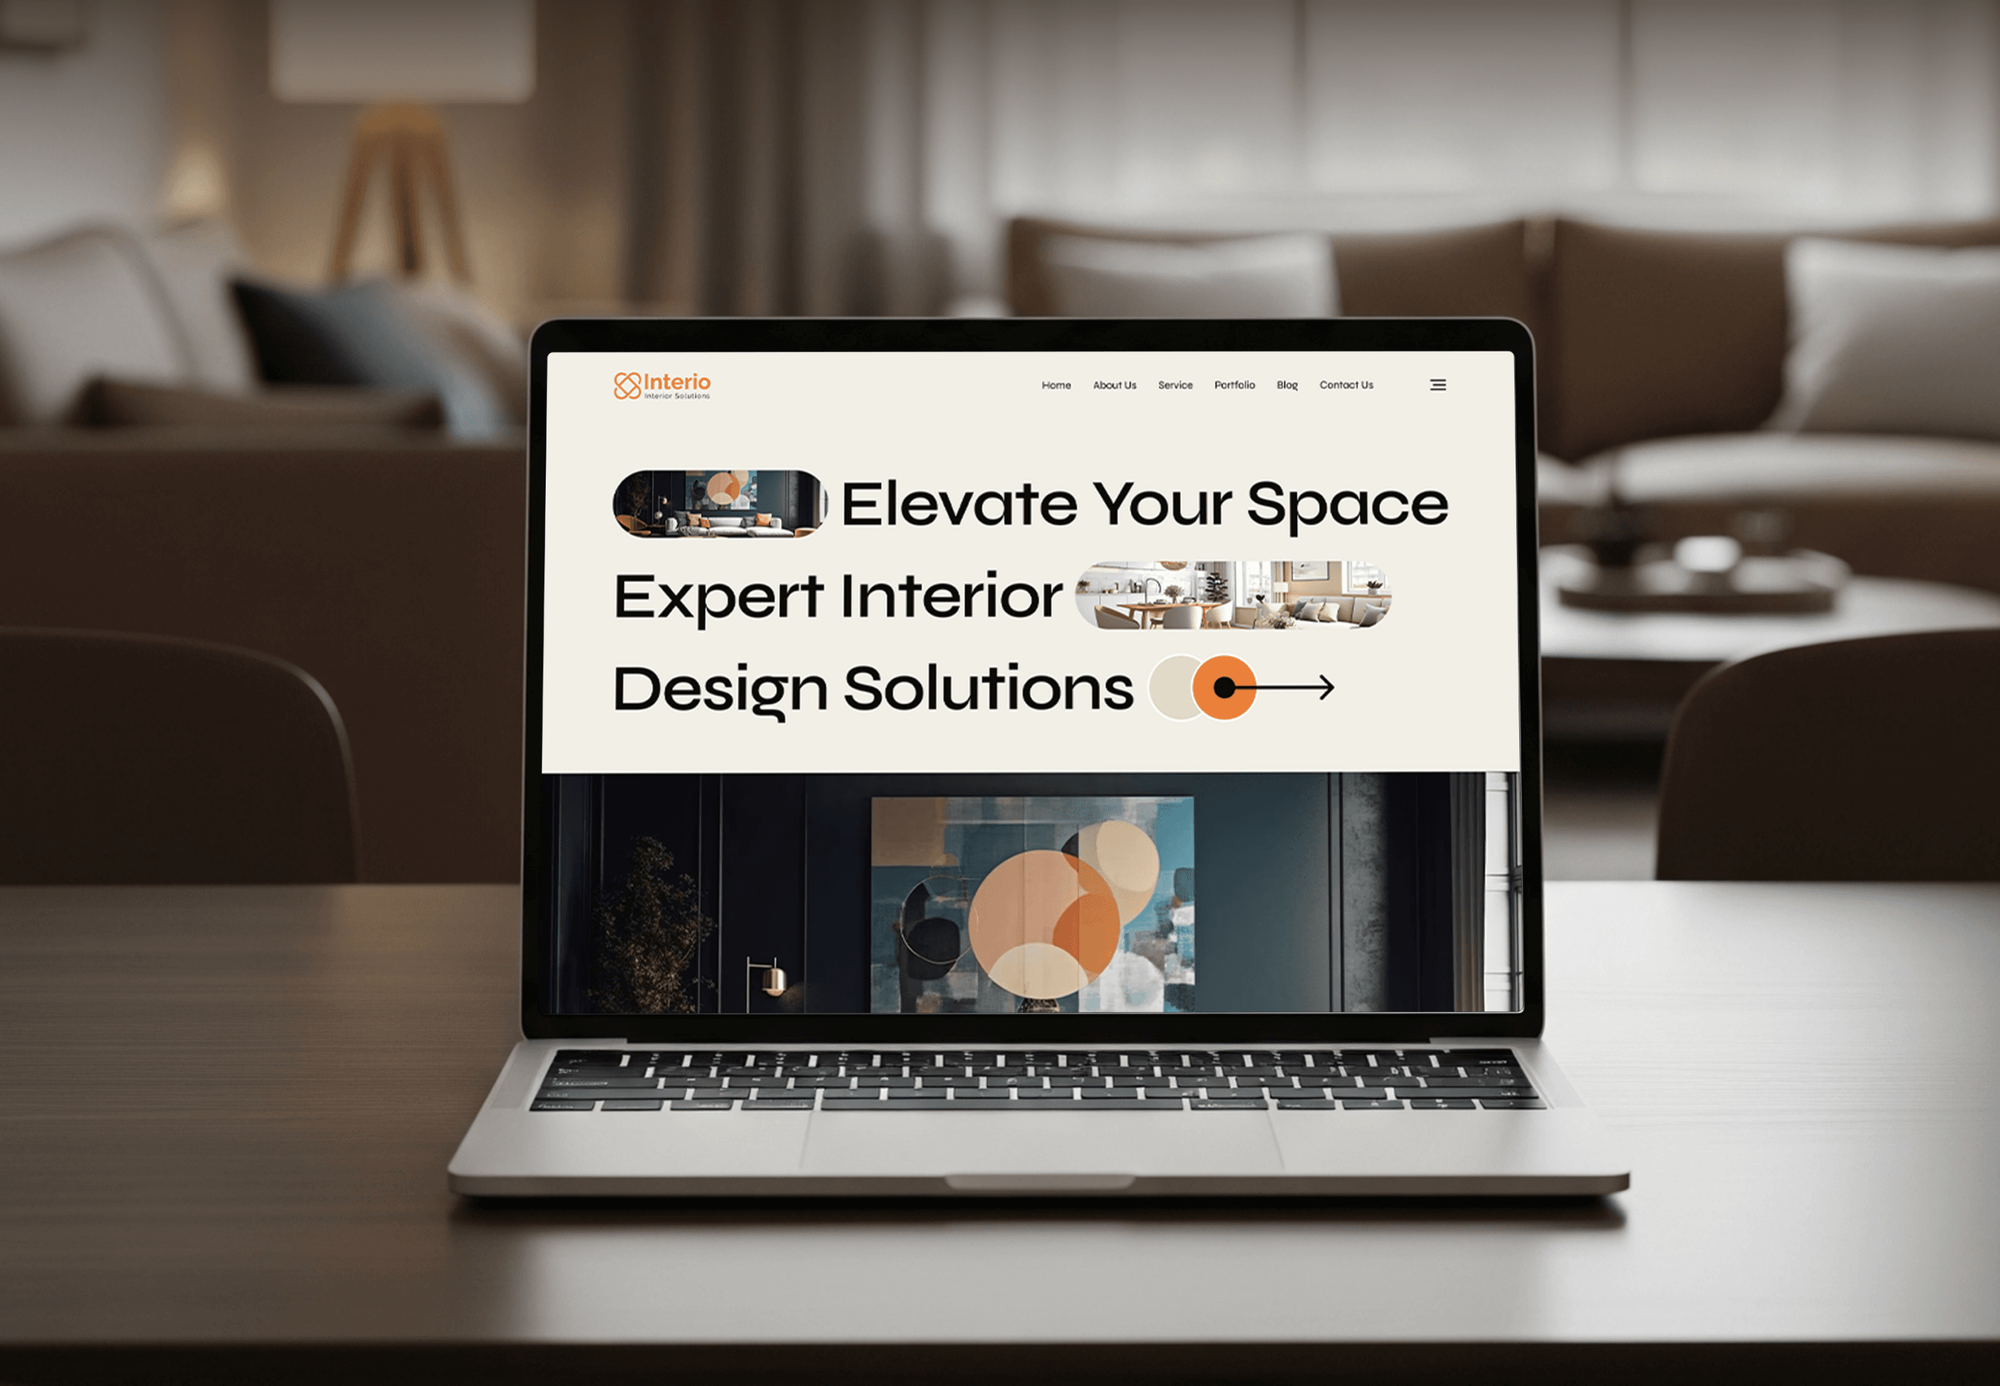
Sites we designed and built for retail, travel, and design businesses, the kind of busy sites malware targets. These are builds we delivered, not malware cases.
What Our Clients Say
Feedback from teams we have built websites, apps, and platforms for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Malware cleanup goes wrong when someone deletes first and asks later. These habits keep your data safe, your site working, and the attacker from walking back in.
We take a full offline copy before touching a single file. If a removed file turns out to matter, or your insurer asks for evidence, it's still there.
Redirect malware often hides from logged-in owners and desktop browsers. We load your pages as a phone visitor arriving from Google, because that's who the attacker targets.
Scanners match known signatures and miss code written for your site alone. An engineer reads changed files in your custom modules, so hand-made backdoors don't survive.
Every infected file, database row, and server job goes on a list you keep. You know exactly what was wrong instead of hearing that it's fixed.
Some sites are so old or so infected that cleaning costs more than a rebuild. If a rebuild is the cheaper path, we'll tell you before we quote.
The price is set by site count and platform after the free check. If the infection is wider than it looked, you hear it before extra work starts.
Overview
DeveloperLook provides website malware removal for business sites on PHP, Joomla, Drupal, Magento, Laravel, and custom stacks. We copy the site, compare every file with a clean source, clean the database and server jobs, close the entry point, and request warning reviews. Cleanups start from $550, and most finish in 2 to 5 business days.
DEVELOPERLOOK
Project facts · Website Malware Removal
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Owners of custom PHP or Laravel sites
Your site runs on custom code no plugin scanner understands, and visitors report pop-ups. You need someone who reads changed files, not just signature matches.
Joomla and Drupal sites with warnings
Your Joomla or Drupal site shows a browser warning, and its extensions haven't been updated in years. You need the malware cleaned and that outdated extension fixed.
Stores hit by redirect malware
Your Google Ads were disapproved for malware, and some shoppers land on a fake pharmacy instead of your store. You need the conditional redirect found and removed.
Accounts suspended by the host
Your host suspended the account over a malware notice and wants proof it's clean. You need the cleanup done and a report the host will accept.
Agencies with an infected client site
Your client's site is infected and your developers are booked. You want web malware removal done quietly under your name, with a report you can forward.
Not a fit
Site runs on WordPress
Your site is a WordPress install. Our WordPress malware removal service is priced for it, with core and plugin checksum checks built in.
Spam pages in Google
Google shows thousands of Japanese or pharma spam pages under your domain. Our Japanese keyword hack cleanup handles the search side as well as the code.
Only want ongoing scans
Nothing is infected yet, and you want daily scans and alerts. Our website security monitoring plan is the better fit for that.
Hosted builder site
Your site runs on Wix, Squarespace, or Shopify, where the platform runs the servers and core code. Their support team is the right first call.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the platform and how much custom code needs reading, and you get a fixed proposal after a free malware check.
For Agencies
You own the client relationship. We supply the cleanup engineers: file comparison, database and server work, and the entry point fix, with the report under your agency's name. Your client hears the site is clean from you, and your developers stay on billable work.
White label: your client only ever sees your brand
Send hosting, database, and admin access, plus what the client noticed.
You get the likely infection, the cleanup plan, and a fixed price.
We clean, patch, and test, then hand back the report under your name.
Send hosting, database, and admin access, plus what the client noticed.
You get the likely infection, the cleanup plan, and a fixed price.
We clean, patch, and test, then hand back the report under your name.
The Right Technology for Your Project
We clean with plain, auditable tools: version control, server logs, and Google's own reports, so every change can be checked afterward.
 PHP
 Laravel
 Magento
 MySQL
 Google Search Console
 Google Chrome
 Cloudflare
Related Services
Cleanup removes this infection. These services handle WordPress sites, search spam, browser warnings, and the monitoring that catches the next one early.
This page
Website Malware Removal
Pairs with the 6 services around it
FAQ
Straight answers on cost, timing, redirect malware, scanning, warnings, and whether a cleanup lasts.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Cleanup starts at $550 for one infected site. Hardening with up to 3 replaced extensions starts at $1,150, and server-wide cleanup for up to 5 sites starts at $2,250. The price is fixed after the free malware check and changes only if the infection proves wider and you approve it.
Most single-site cleanups take 2 to 5 business days from access to a clean site. Servers with several infected sites take up to 10, because each site is traced and isolated. Google and blocklist reviews follow on their own schedule: Google's guidance is a few days to a few weeks.
In four layers: files, database, server jobs, and the entry point. Every file is compared with a clean source, injected rows are deleted, and rogue cron jobs and users go. Then the hole that let the attacker in is patched, because skipping that step often means a repeat infection within weeks.
Copy the files and database first, then compare files with a clean source instead of deleting whatever a scanner flags. Scanners sometimes flag legitimate code, and deleting it can break checkout or forms. We clean from that comparison, then retest key pages and forms on phone and desktop.
Yes, when it removes the cause as well as the code. Cheap cleanups often delete flagged files and leave the backdoor or outdated extension in place, so the infection returns. Ask any provider what they compare files against, whether they check the database and cron jobs, and what happens if it returns.
Start with the Security Issues report in Google Search Console and a free online scanner, then check the server itself. Online scanners only see the pages they load, so they miss backdoors and database injections. A server-side check compares files with clean copies. For daily scans after cleanup, see our website security monitoring plan.
Find the rule that triggers it, usually in .htaccess, an Nginx config, a header file, or a database setting. These rules check the visitor's device, referrer, or cookies, so a logged-in owner rarely sees them. Test from a clean phone browser arriving from search, remove the rule and the backdoor that rewrites it, then clear cached and CDN copies.
Clean the site completely, then request a review in the Security Issues report in Google Search Console. Google's help pages put that review at a few days to a few weeks. Norton Safe Web, McAfee, and other blocklists have their own forms, and we submit those too. A review sent before the site is clean usually fails.
Search content and settings tables for script tags, iframes, and encoded strings that don't belong, then compare suspicious rows with an older export. Attackers hide redirects in configuration tables and spam links in page content. We remove those rows, check for added admin accounts, and change the database password the attacker may have read.
It can if the entry point stays open, which is why we patch it before the site goes live again. Every plan includes a free re-clean if the same infection returns within 30, 60, or 90 days, by plan. After that, updated software and file change alerts keep the risk low.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.