
Identity and access review
Every account and admin role checked. Fix plans enforce MFA, add passkeys for admins, and move shared passwords into a vault.

For businesses with no security team: we review accounts, email, devices, cloud, and web apps, fix what puts you at risk, and recheck every fix. From $1,150.
5
Security areas assessed
100%
Findings ranked with a fix
How your project runs
Teams we have built for:














The Problem
It shows up as a company grows. Microsoft 365 or Google Workspace, laptops, a cloud account, and a website all get set up by different people, and nobody checks them.
01 · Spoofed email
A fake invoice arrives from your own domain.
SPF, DKIM, and DMARC records stop others from sending mail as you.
02 · Old logins
A former contractor still has an admin account.
Every account is checked against its owner's current job, and stale ones go.
03 · Weak sign-in
Half the team signs in with a password alone.
MFA is enforced for everyone, with phishing-resistant passkeys for admin accounts.
04 · Untested backups
The only backup sits on the server it protects.
Backups move to a separate location, and a real restore proves they work.
Your bookkeeper gets an email from your own address asking to change a vendor's bank details, and it looks real. A former contractor still has an admin login. Half the team signs in with a password alone. The only backup sits on the server it's meant to protect. Then your cyber insurance renewal asks which controls you have, and nobody can answer. None of it feels urgent until a payment goes to the wrong account or ransomware locks the shared drive on a Monday morning.
We start with one assessment across identity, email, devices, cloud, and web apps. Each finding is ranked by how an attacker would use it and mapped to NIST CSF 2.0 and the CIS Controls. Then our engineers fix what you approve. That means MFA for every account, SPF, DKIM, and DMARC on your domain, no stale accounts, and a backup restore that's actually tested. Every fix gets rechecked, so you get proof instead of promises.
One review, five areas
Identity, email, devices, cloud, and web apps get checked together, so gaps between them don't slip through.
Engineers who fix things
The same team that finds a gap can close it, test it, and document the change.
Proof for insurers and customers
A dated report shows which controls are in place, ready for insurance forms and questionnaires.
Our Cybersecurity Services Process
You approve the scope before we log in, see every finding ranked before anything changes, and sign off on each fix. Critical issues reach you the same day we find them.
We talk through your systems, your data, and what prompted the call: an insurance form, a customer questionnaire, or a scare. You get a written scope, the access we'll need, and a fixed price before any work starts.
What's Included
One assessment across identity, email, devices, cloud, and web apps, then the fixes and a recheck. Larger plans add policies, staff phishing training, and an incident response plan.
Compare Options
Your IT provider keeps systems running, and cybersecurity solutions sold as software block known threats. Neither one usually reviews your whole setup or fixes the settings attackers rely on.
| Feature | DeveloperLookBest fit | IT provider | Security software |
|---|---|---|---|
| Starting cost | From $1,150, fixed scope | Often in your monthly fee | Per user, per month |
| Whole-setup assessment | Five areas, ranked findings | Varies by provider | Its own product only |
| Configuration fixes | Done and rechecked | Routine changes only | Not included |
| Email spoofing protection | SPF, DKIM, and DMARC set | Sometimes set up | Filters incoming mail |
| Blocking known malware | Advice on what to run | Installs your antivirus | Strong, runs continuously |
| Help desk and uptime | Not part of this service | Day-to-day support | Vendor support only |
| Evidence for insurers | Dated report with proof | Rarely written up | Product dashboards |
| Best for | Finding and closing gaps | Keeping systems running | Ongoing threat blocking |
Projects We've Built
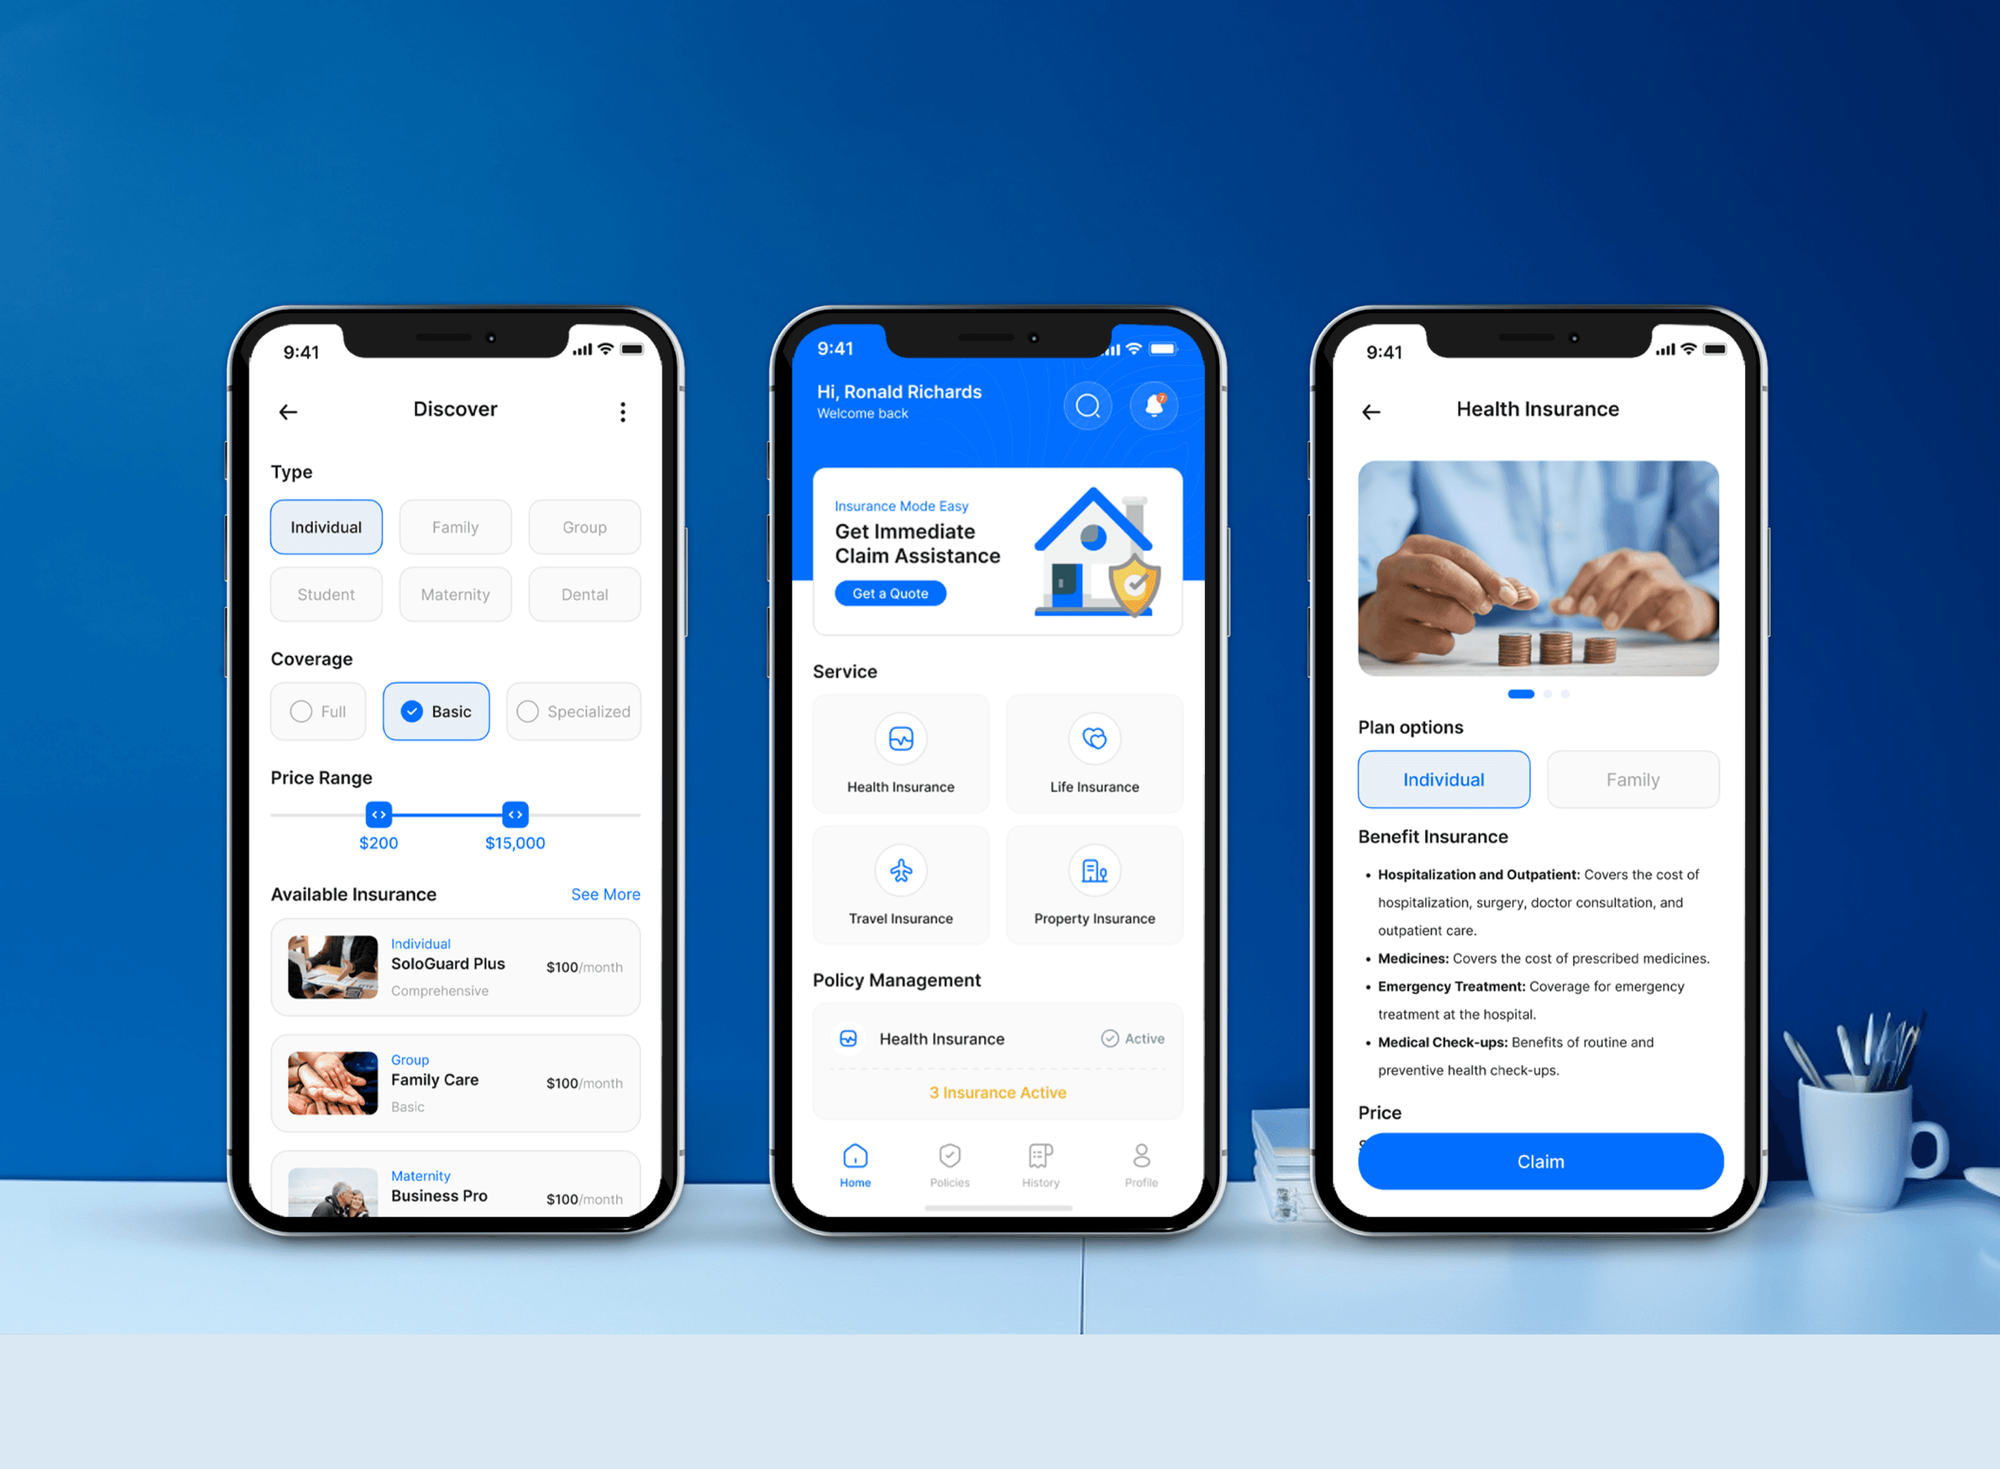
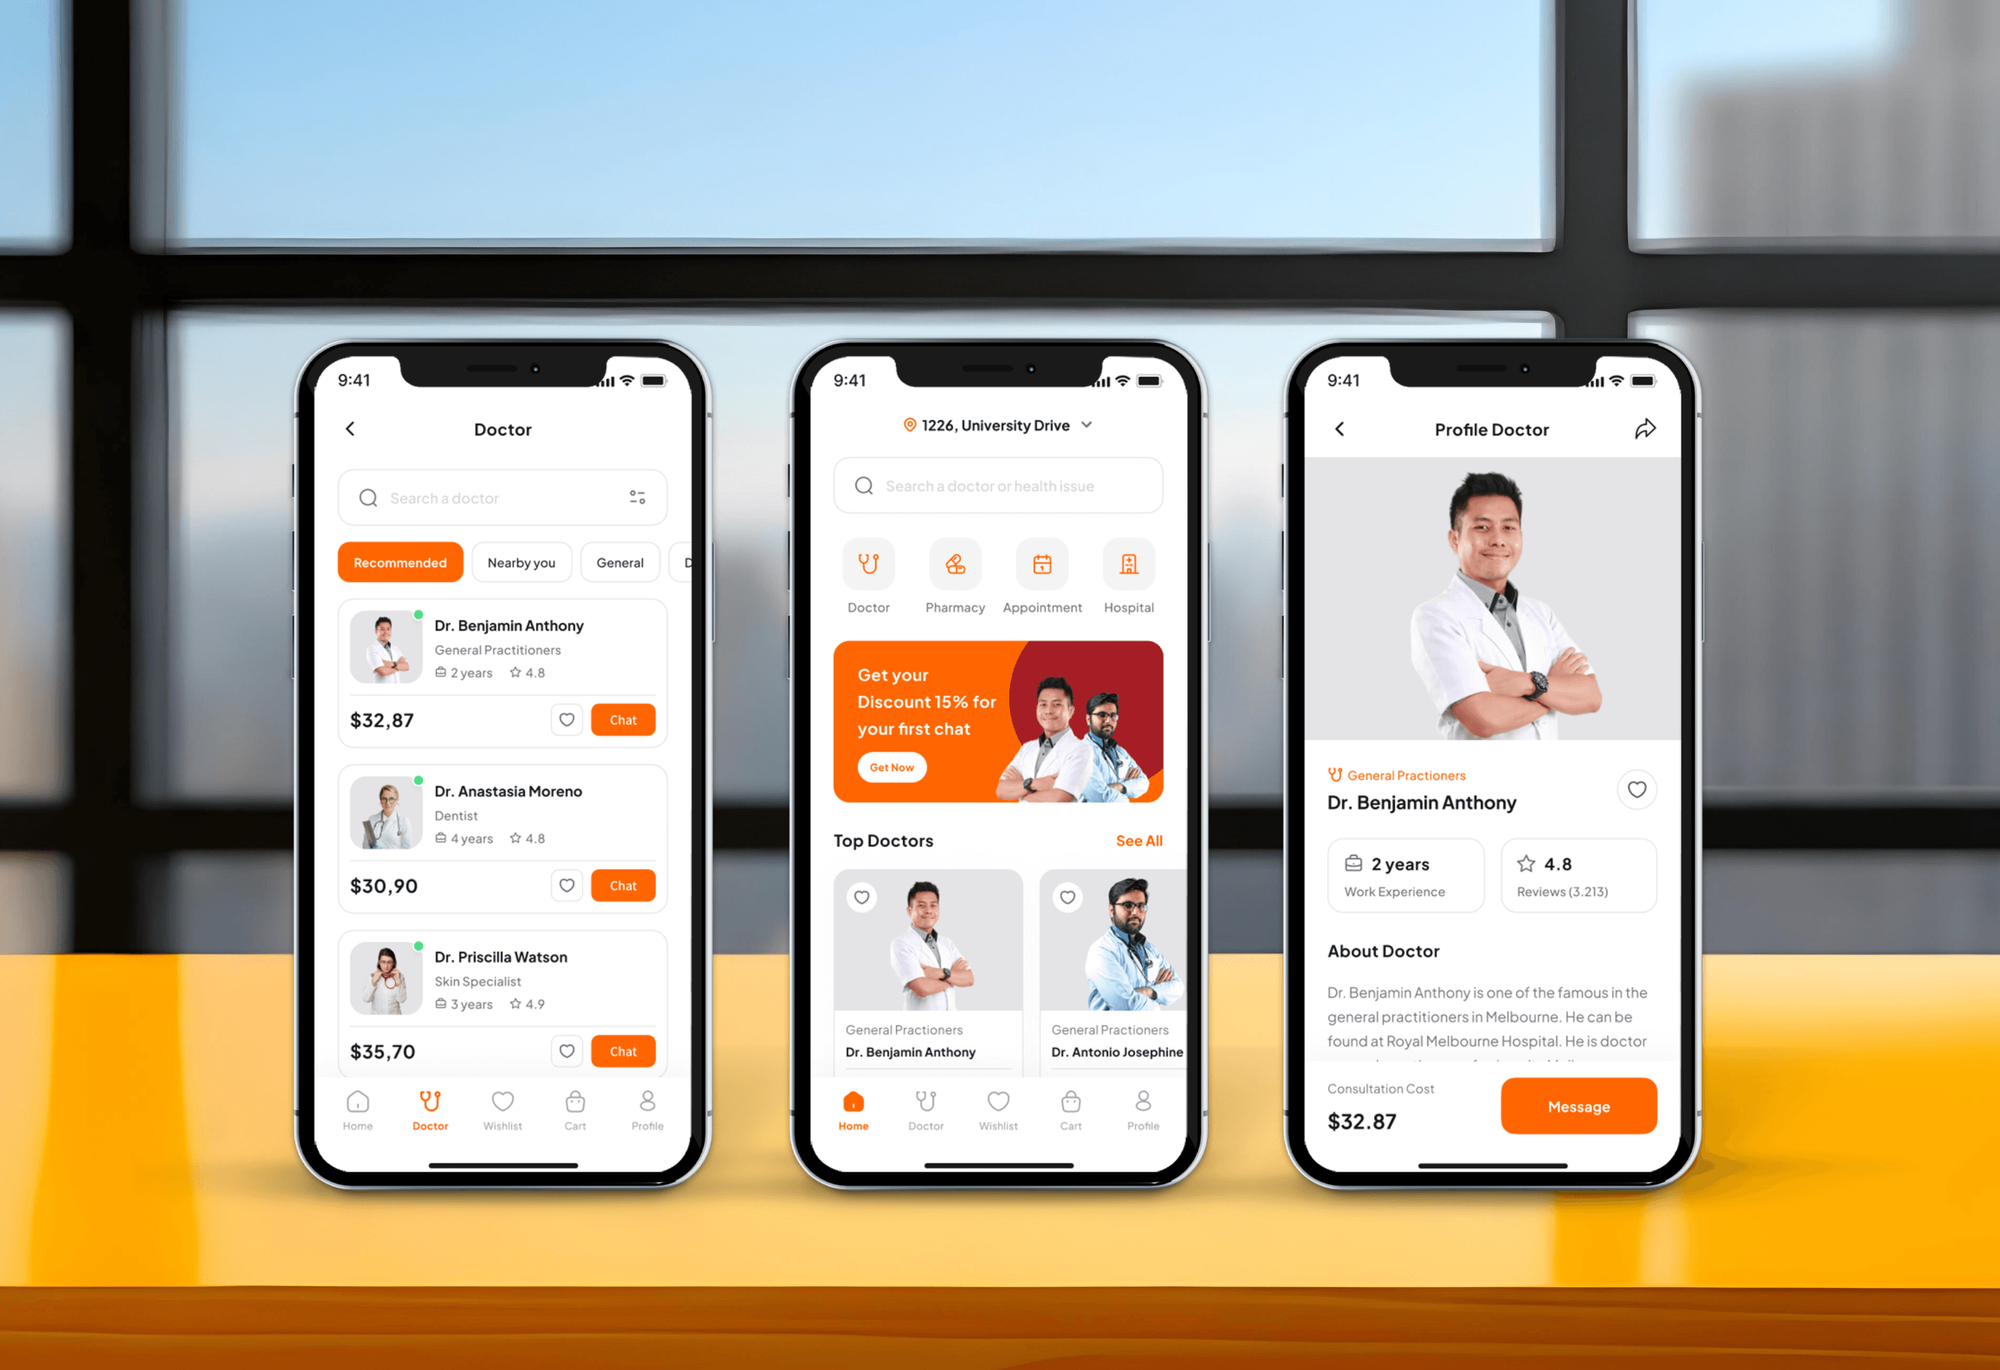
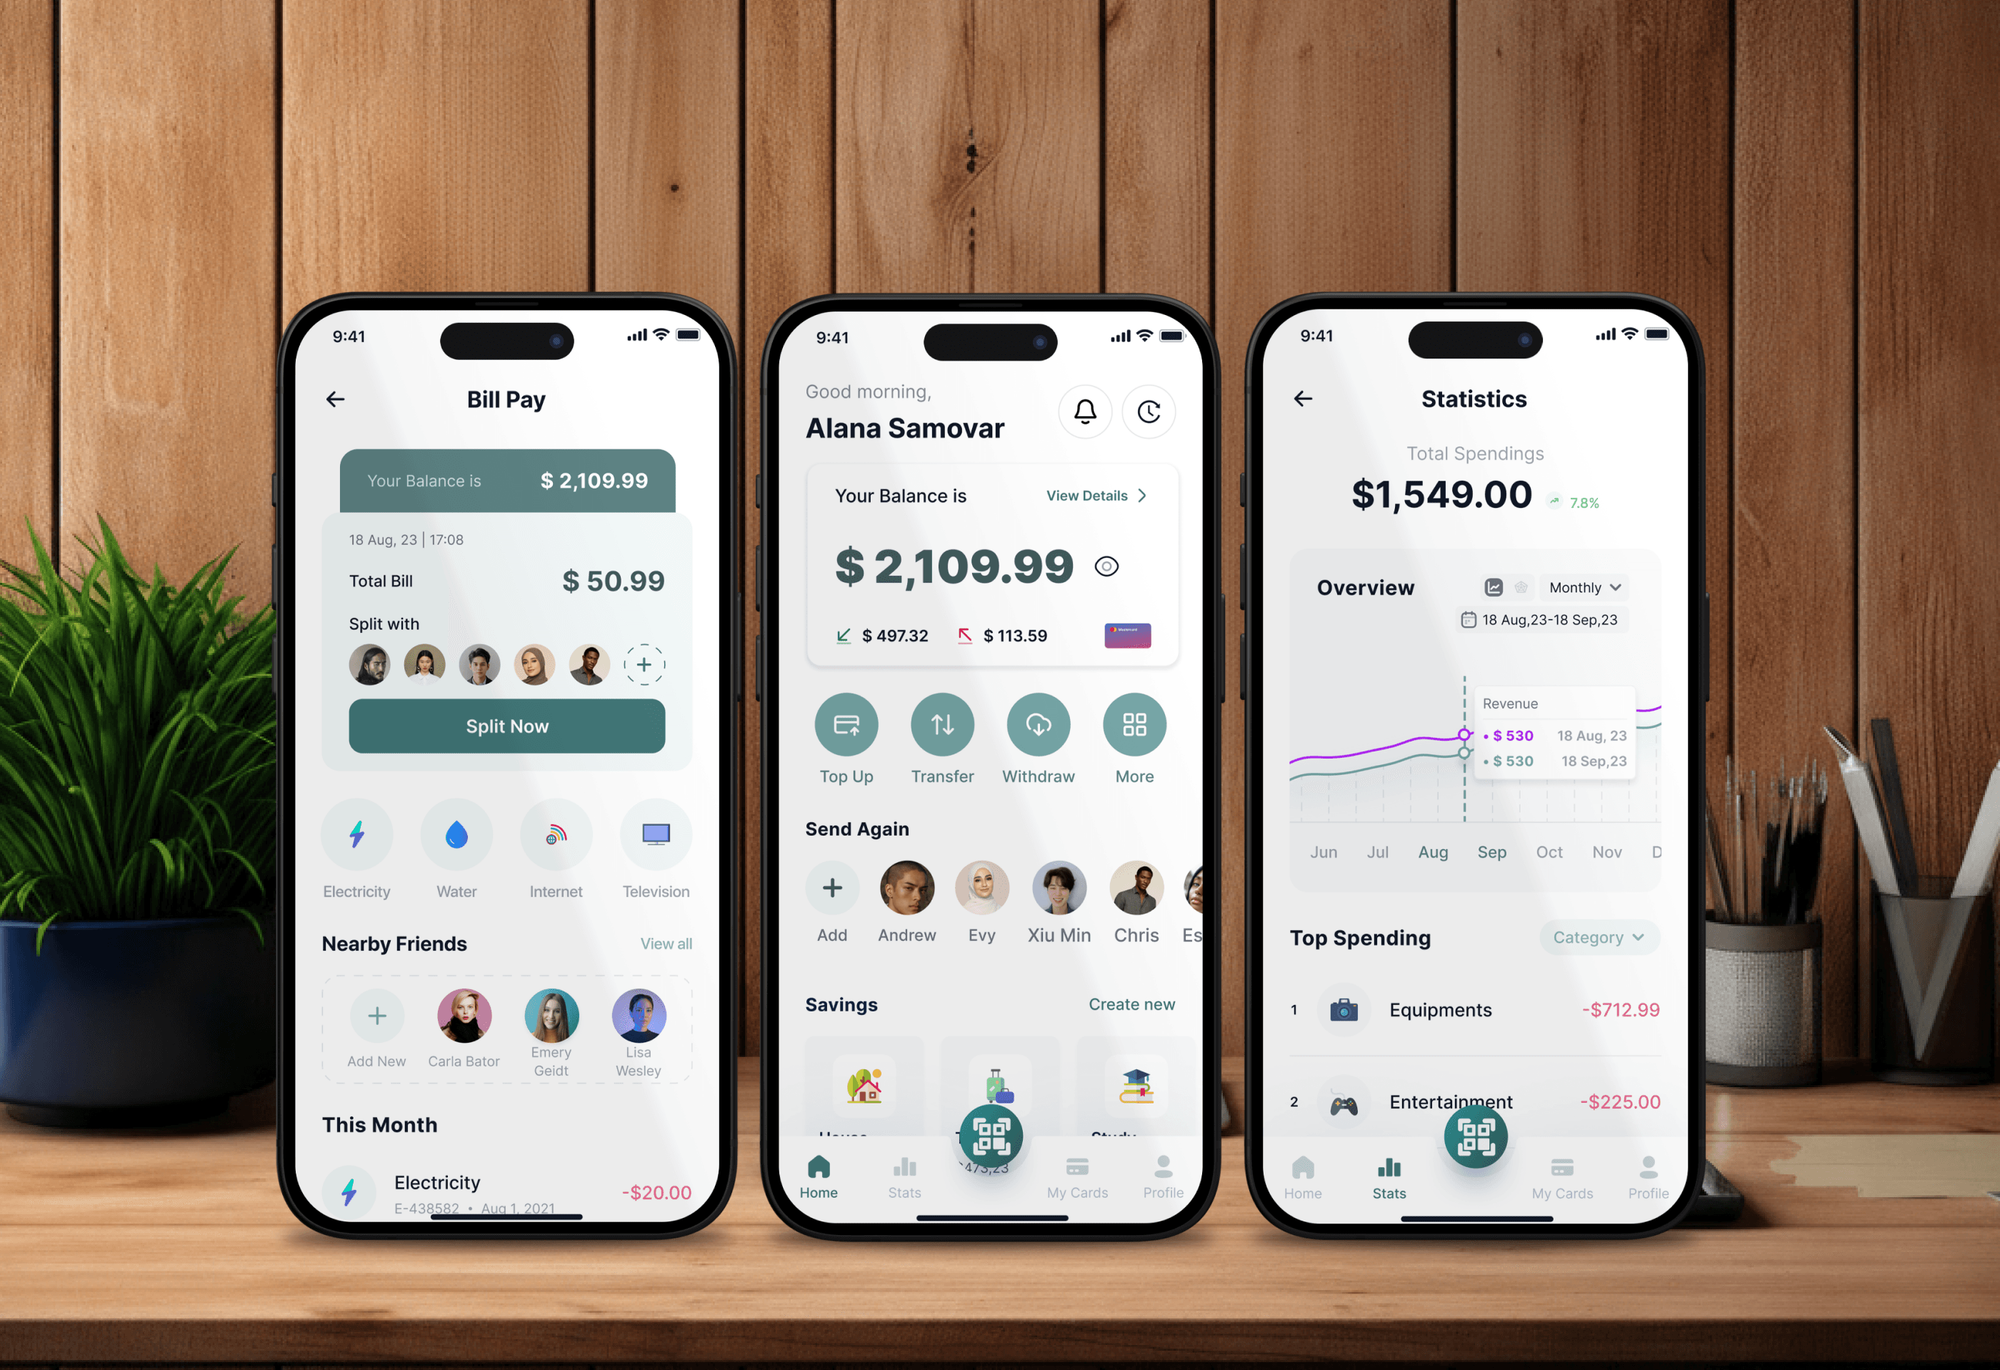
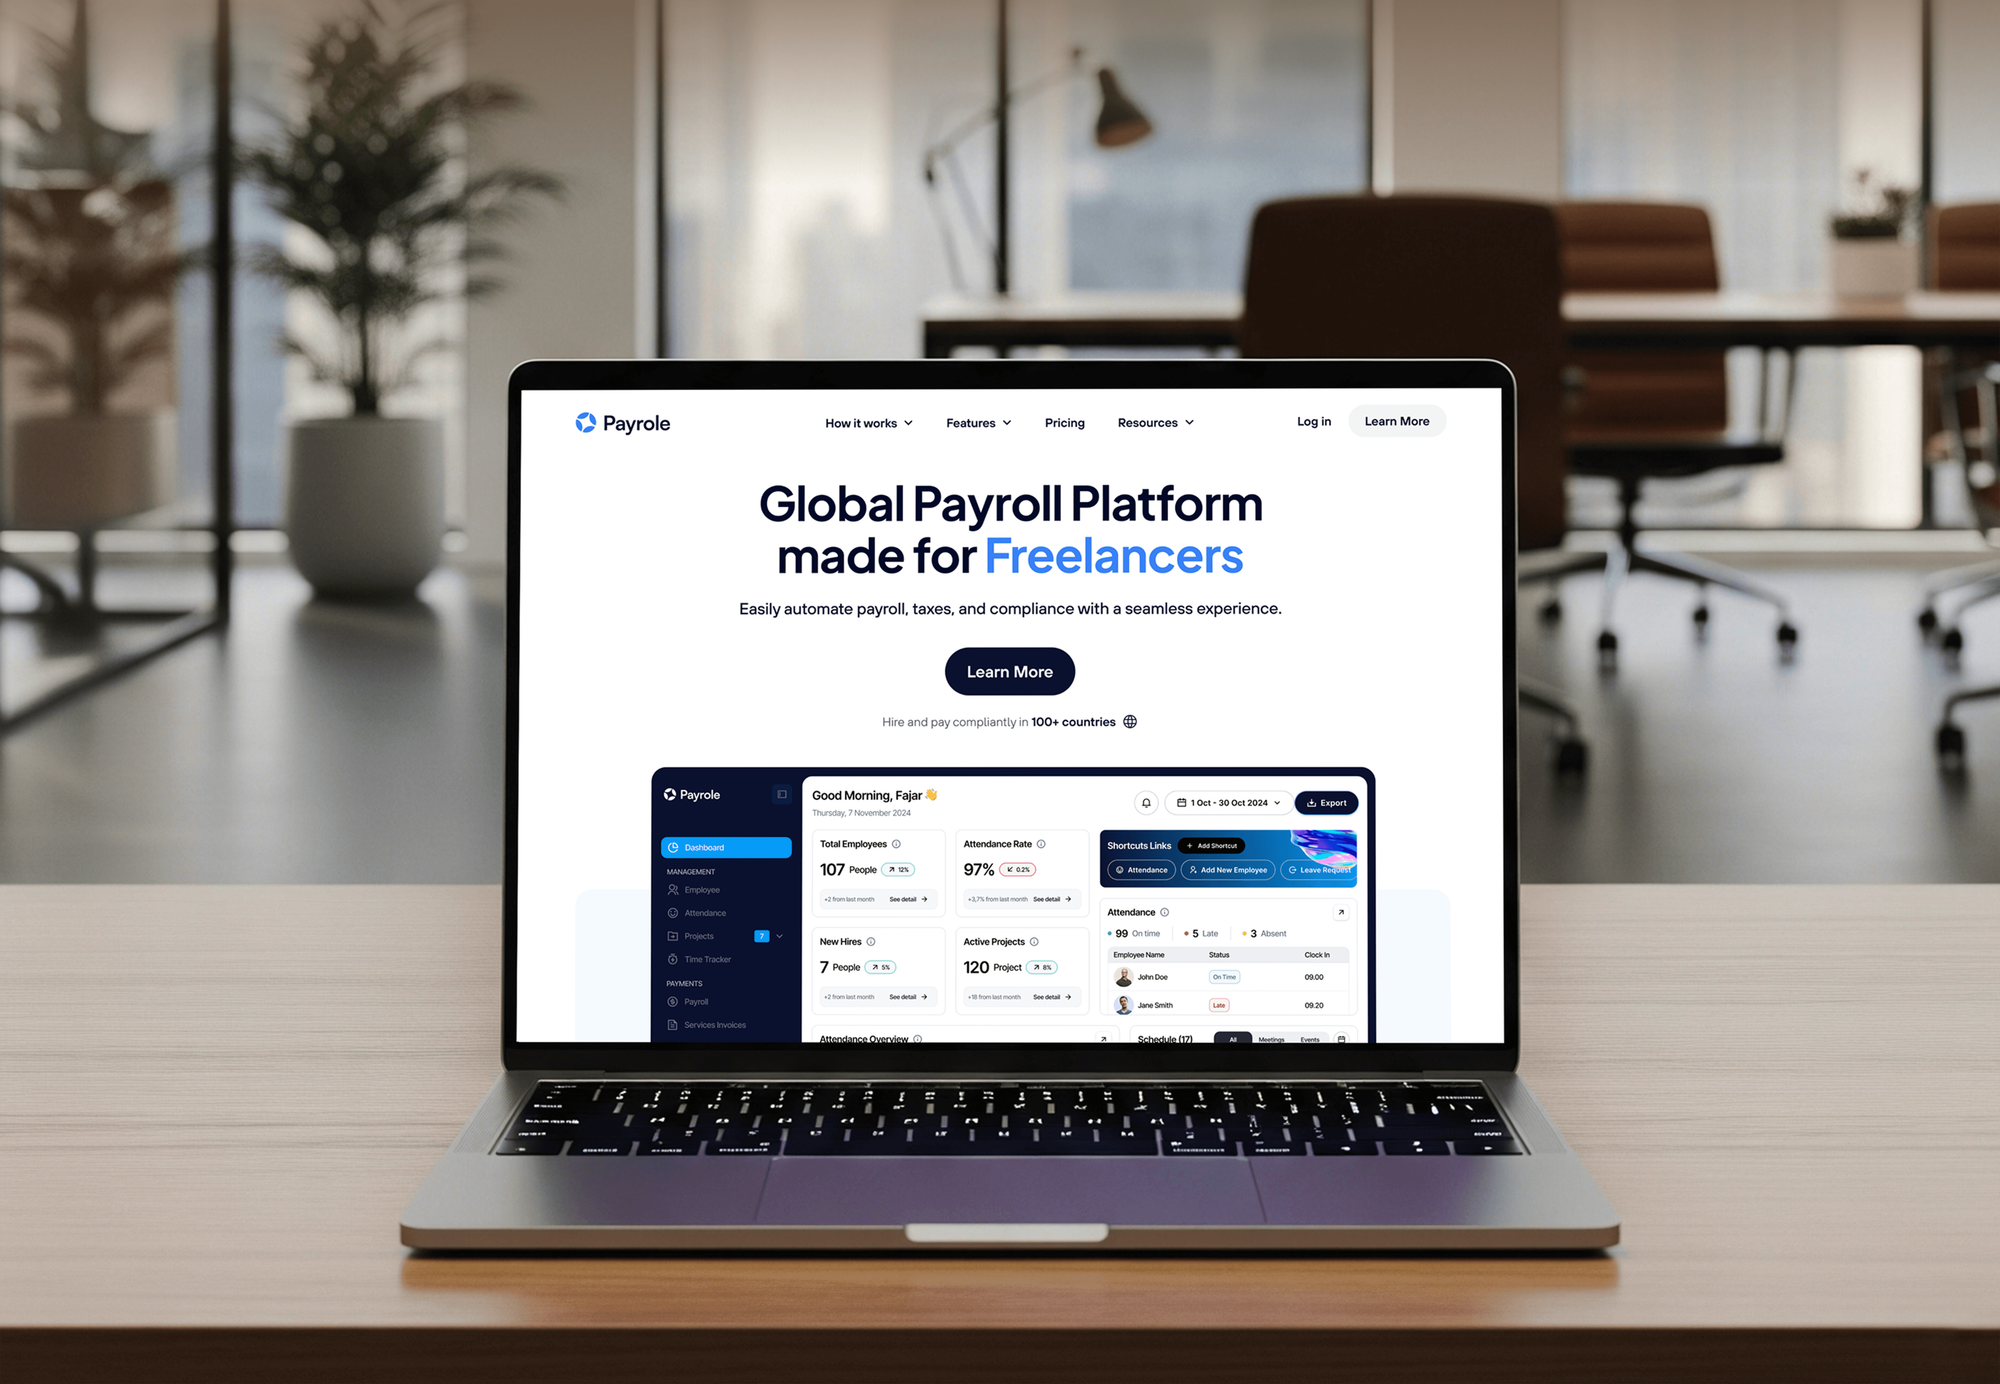
Apps and dashboards we designed and built for insurers, clinics, finance, and payroll teams. Systems like these hold the data a security program exists to protect.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A cybersecurity service provider works inside your accounts. These habits keep your data private, your team working during changes, and every finding worth fixing.
We start with read-only access and take admin rights only for approved fixes. Our accounts are removed when the work closes.
Sign-in and mail changes go live in a window you choose, with a rollback ready. Your team keeps working instead of losing email mid-week.
Scanners flag plenty of noise, so a person confirms each result before it reaches your report. Your budget goes to real gaps, not false alarms.
Each finding opens with the business risk in one sentence, before any technical detail. You decide what to fix first without decoding jargon.
If your IT provider or a tool you already pay for covers a gap, we'll tell you before we quote. You pay only for missing controls.
Reports and evidence belong to you to share with insurers or auditors. We delete our working copies of your data when the engagement closes.
Overview
DeveloperLook provides cybersecurity services for growing businesses that have no security team of their own. We assess identity, email, devices, cloud accounts, and web apps, then fix the gaps you approve and recheck each one. Projects start at $1,150 and take 2 to 10 weeks, and our engineers do the fixes instead of handing you a list.
DEVELOPERLOOK
Project facts · Cybersecurity Services
Reviewed 6 Oct 2026 by Saimul Islam
Good fit
Businesses with no security staff
Your office manager handles IT on top of a full job, and nobody has checked sign-in rules or backups since the Microsoft 365 tenant was created.
Teams facing a cyber insurance renewal
Your insurer's application asks about MFA, offline backups, and endpoint protection, and you want truthful answers backed by a dated report.
Companies answering security questionnaires
You sell to larger companies, and their security questionnaires ask how your AWS or Azure setup protects their data. You need real controls first.
Google Workspace teams after a phishing scare
Your teammate typed a password into a fake sign-in page, and you want to know what an attacker could still reach in Google Workspace.
Agencies and MSPs adding security work
Your agency or managed IT business keeps getting asked for security reviews, and you want a partner who does them under your brand.
Not a fit
Advice without hands-on fixes
You want an independent risk assessment and a roadmap your own IT team will carry out. Our Cybersecurity Consulting Services page covers that.
Ongoing security leadership
You need someone to own security every month, report to leadership, and handle customer audits. Our vCISO Services page offers that as a monthly role.
Website only, under $1,150
Your budget is under $1,150, and your website is your main worry. Our Website Security Audit Services page starts lower and covers the site itself.
Round-the-clock monitoring
You need people watching security alerts overnight and on weekends. That's a managed detection and response provider's job, and these plans don't include it.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on how many users and systems you have and which fixes you want, and you get a fixed proposal after a free security call.
For teams that want a clear, ranked picture of their security gaps before paying for fixes.
$1,150one-time, USD
For businesses that want critical and high findings fixed by our engineers and rechecked.
$2,950one-time, USD
For teams that need policies, staff training, and an incident plan on top of the fixes.
$5,850one-time, USD
For Agencies
You own the client relationship. We run the assessment and fixes under your brand, write findings in your template, and stay off client calls unless invited. Your clients get security work without a new hire.
White label: your client only ever sees your brand
Send the client's systems, user count, and the security questions they've been asked.
You get a written scope, an access list, and a fixed price for each client.
We assess, fix what the client approves, and report in your template.
You present findings and fixes while we work behind your brand.
Scope and price agreed for each client before anyone logs in.
The people who assess your client's tenant also configure the fixes.
Take on one client review or a whole book of them.
The Right Technology for Your Project
We test with standard security tools and our own scripts, inside the Microsoft 365, Google Workspace, and cloud consoles you already use.
 Burp Suite
 Python
 AWS
 Cloudflare
 Google Sheets
 Slack
 Loom
FAQ
Straight answers on what cybersecurity does, its main types, cost, common threats, compliance, and how to choose a provider.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Cybersecurity keeps your systems and data confidential, accurate, and available, so attackers can't read, change, or lock what your business runs on. In practice, that means controlling sign-ins, patching software, filtering email, backing up data, and watching for odd activity. NIST's Cybersecurity Framework 2.0 groups the work into six functions: Govern, Identify, Protect, Detect, Respond, and Recover.
The five general types are network, application, cloud, critical infrastructure, and Internet of Things (IoT) security. Most businesses mainly need the first three, plus identity and email security, which the classic list folds into network security. That's why our assessment covers identity, email, devices, cloud, and web apps, where a typical company's data lives.
At DeveloperLook, assessments start at $1,150 for identity, email, devices, cloud, and web apps, with a ranked report. Fixing critical and high findings, enforcing MFA, setting up DMARC, and testing a backup restore costs $2,950. The $5,850 program adds policies, an incident plan, staff training, and a 90-day rescan. Prices are fixed after a free call.
Cybersecurity matters because one stolen password or fake invoice can cost a growing business money, customers, and days of downtime. Automated phishing and password attacks don't check company size first. Customers, insurers, and regulators also want proof. Security questionnaires, insurance forms, and rules like the FTC Safeguards Rule expect controls such as MFA to be in place.
Cybersecurity risk is the combination of how likely a threat is to exploit a weakness and how much damage it would do. A shared admin password on your accounting software is high risk: likely to be abused and costly when it is. We rank every finding this way, and our consulting work builds a full risk register with owners.
The most common threats are phishing, business email compromise, ransomware, stolen or reused passwords, and unpatched software. Business email compromise is the quiet one: someone in a real mailbox, or on a lookalike domain, asks your finance team to pay a new account. Misconfigured cloud storage and over-permissioned apps complete the list.
Start with the basics that block common attacks: MFA on every account, prompt patching, tested offline backups, and admin rights only where needed. Then add DMARC on your domain, endpoint protection on every device, and phishing training for staff. CIS publishes these steps free as Implementation Group 1, the 56 safeguards we use as our baseline checklist.
Cybersecurity compliance means meeting the security rules of a law, contract, or standard, and being able to prove it. Examples include the HIPAA Security Rule, PCI DSS for card payments, SOC 2 for software vendors, and ISO/IEC 27001. Passing an audit doesn't mean you have no gaps. Auditors issue the reports; we help you get ready for them.
Any business that stores customer data, takes payments, or runs on email and cloud apps needs cyber security services in some form. The need turns urgent when an insurer, a large customer, or a regulator starts asking questions, or right after a scare. Companies with security staff may only need testing. Teams without it usually need the fixes done too.
Choose a vendor that names who does the work, puts scope and price in writing, and fixes what it finds. Ask cybersecurity companies for a sample report, the access they need, and how they remove it afterward. Be wary of cybersecurity firms that pitch a product before looking at your setup. A good vendor also tells you what you don't need.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.