


02Our Security Audit Process
From Website Vulnerability Scan to a Prioritized Fix List
You see the scope and what we will and will not test before we begin.
05Projects We've Built
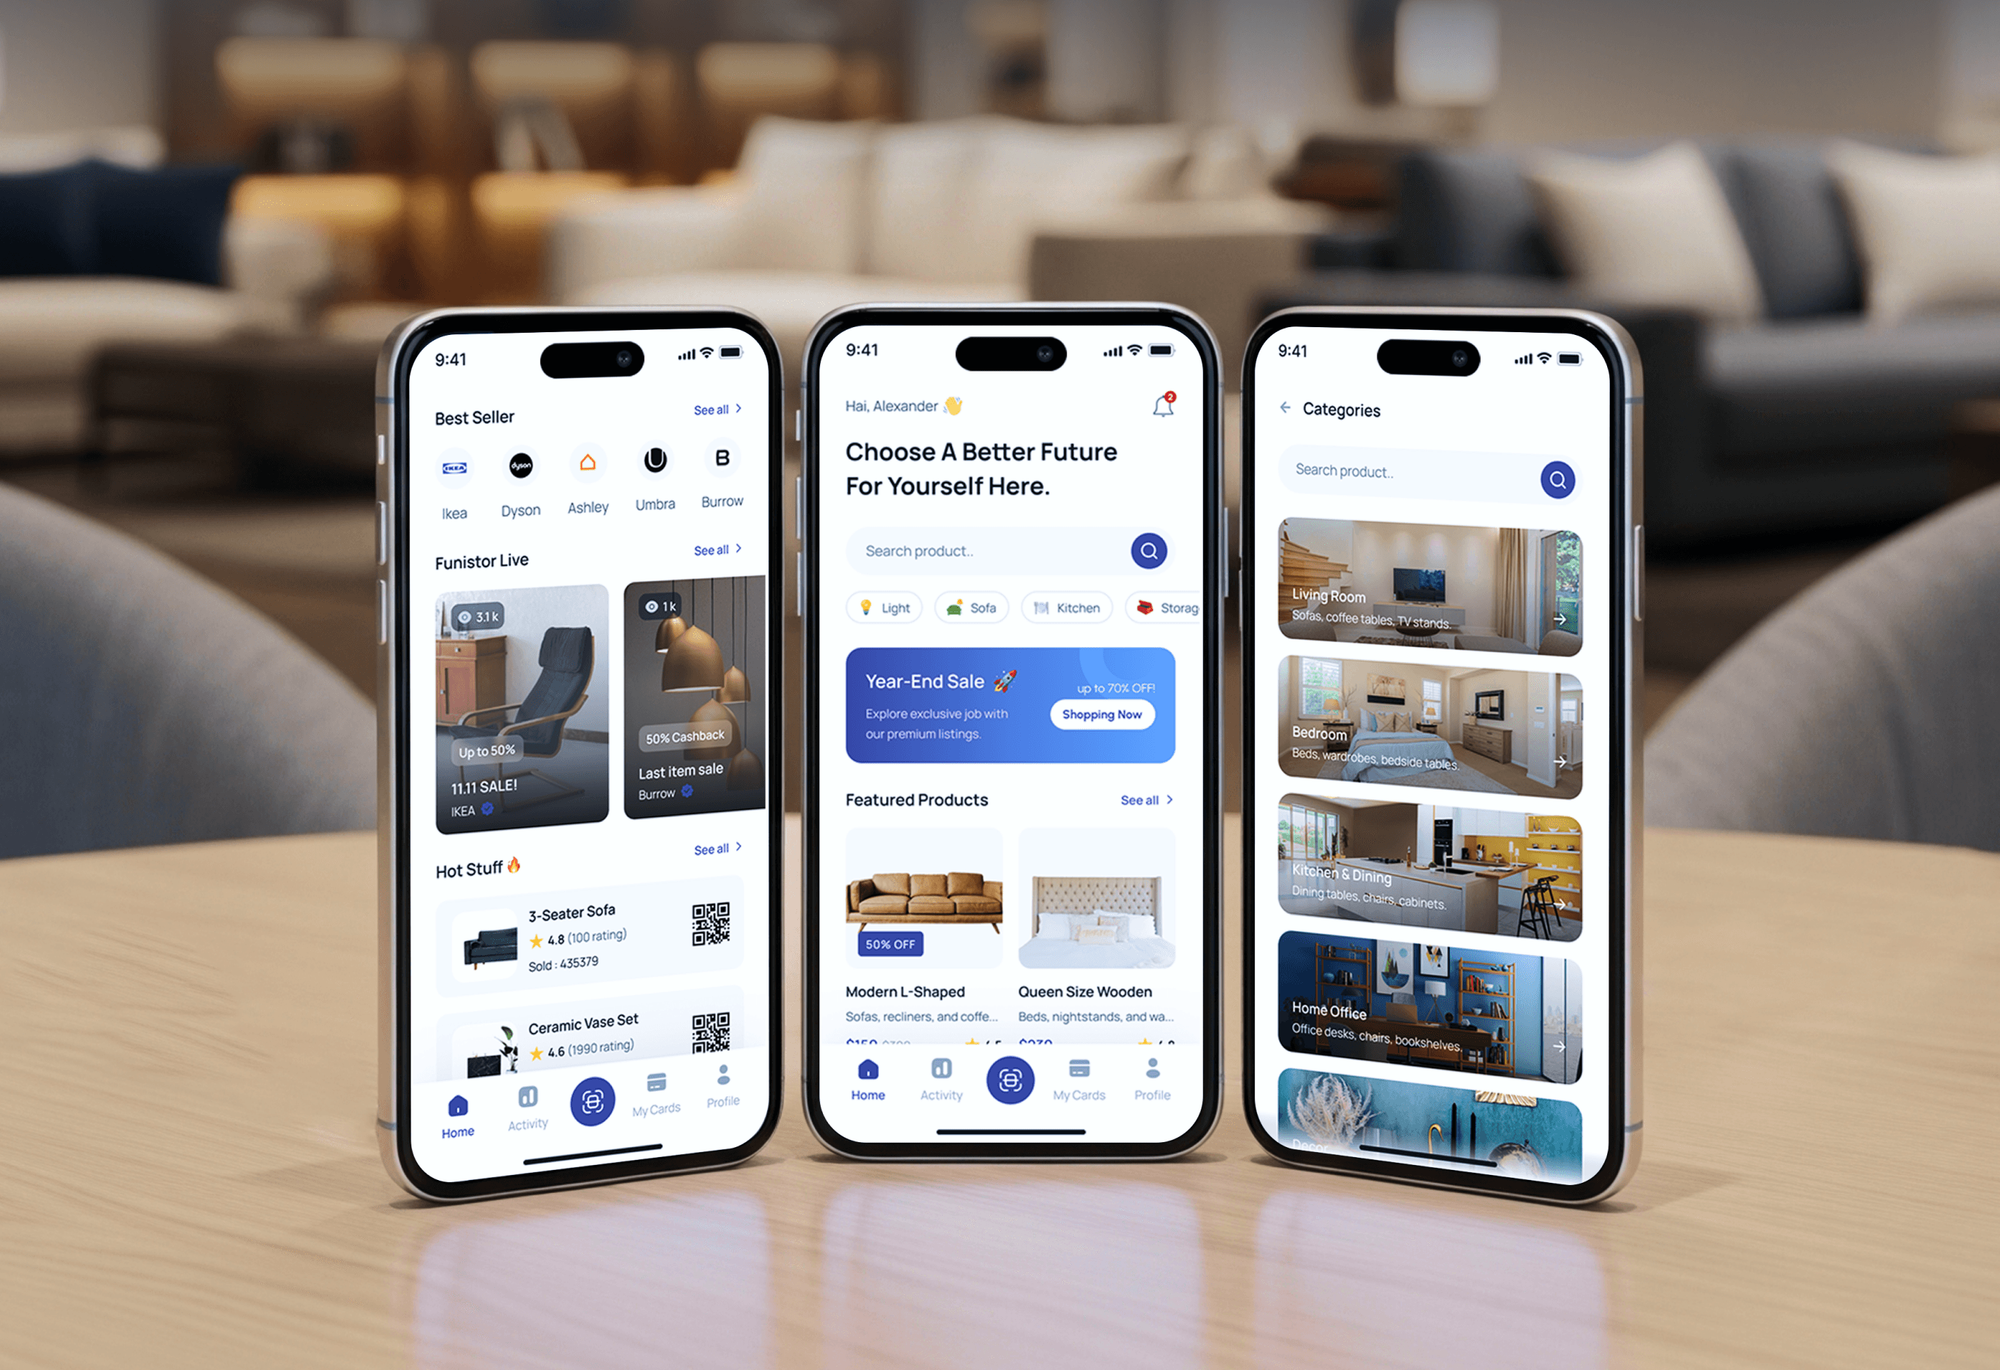
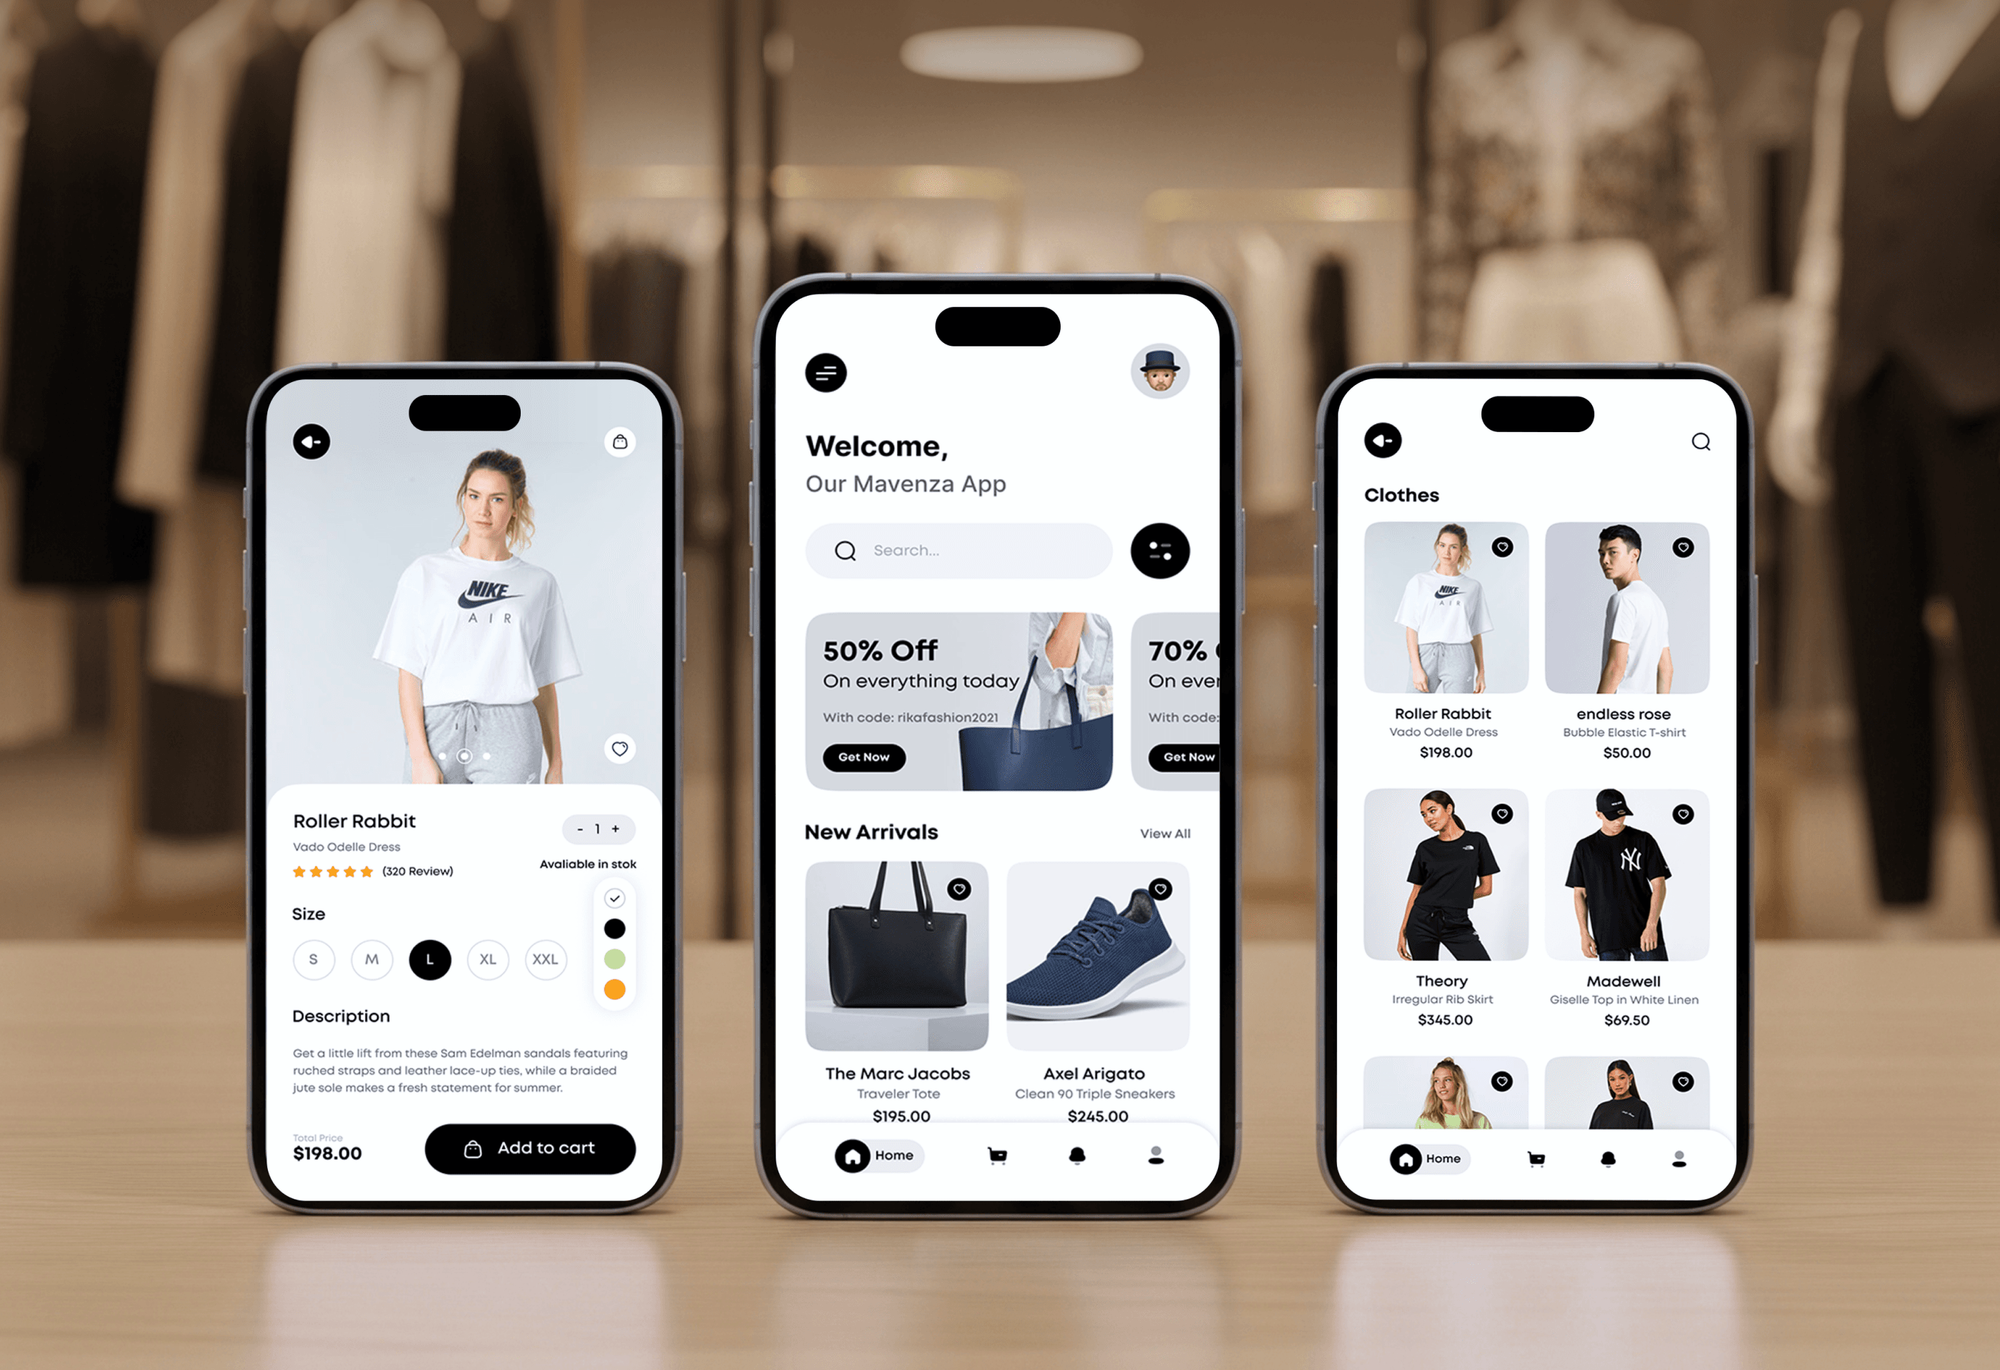
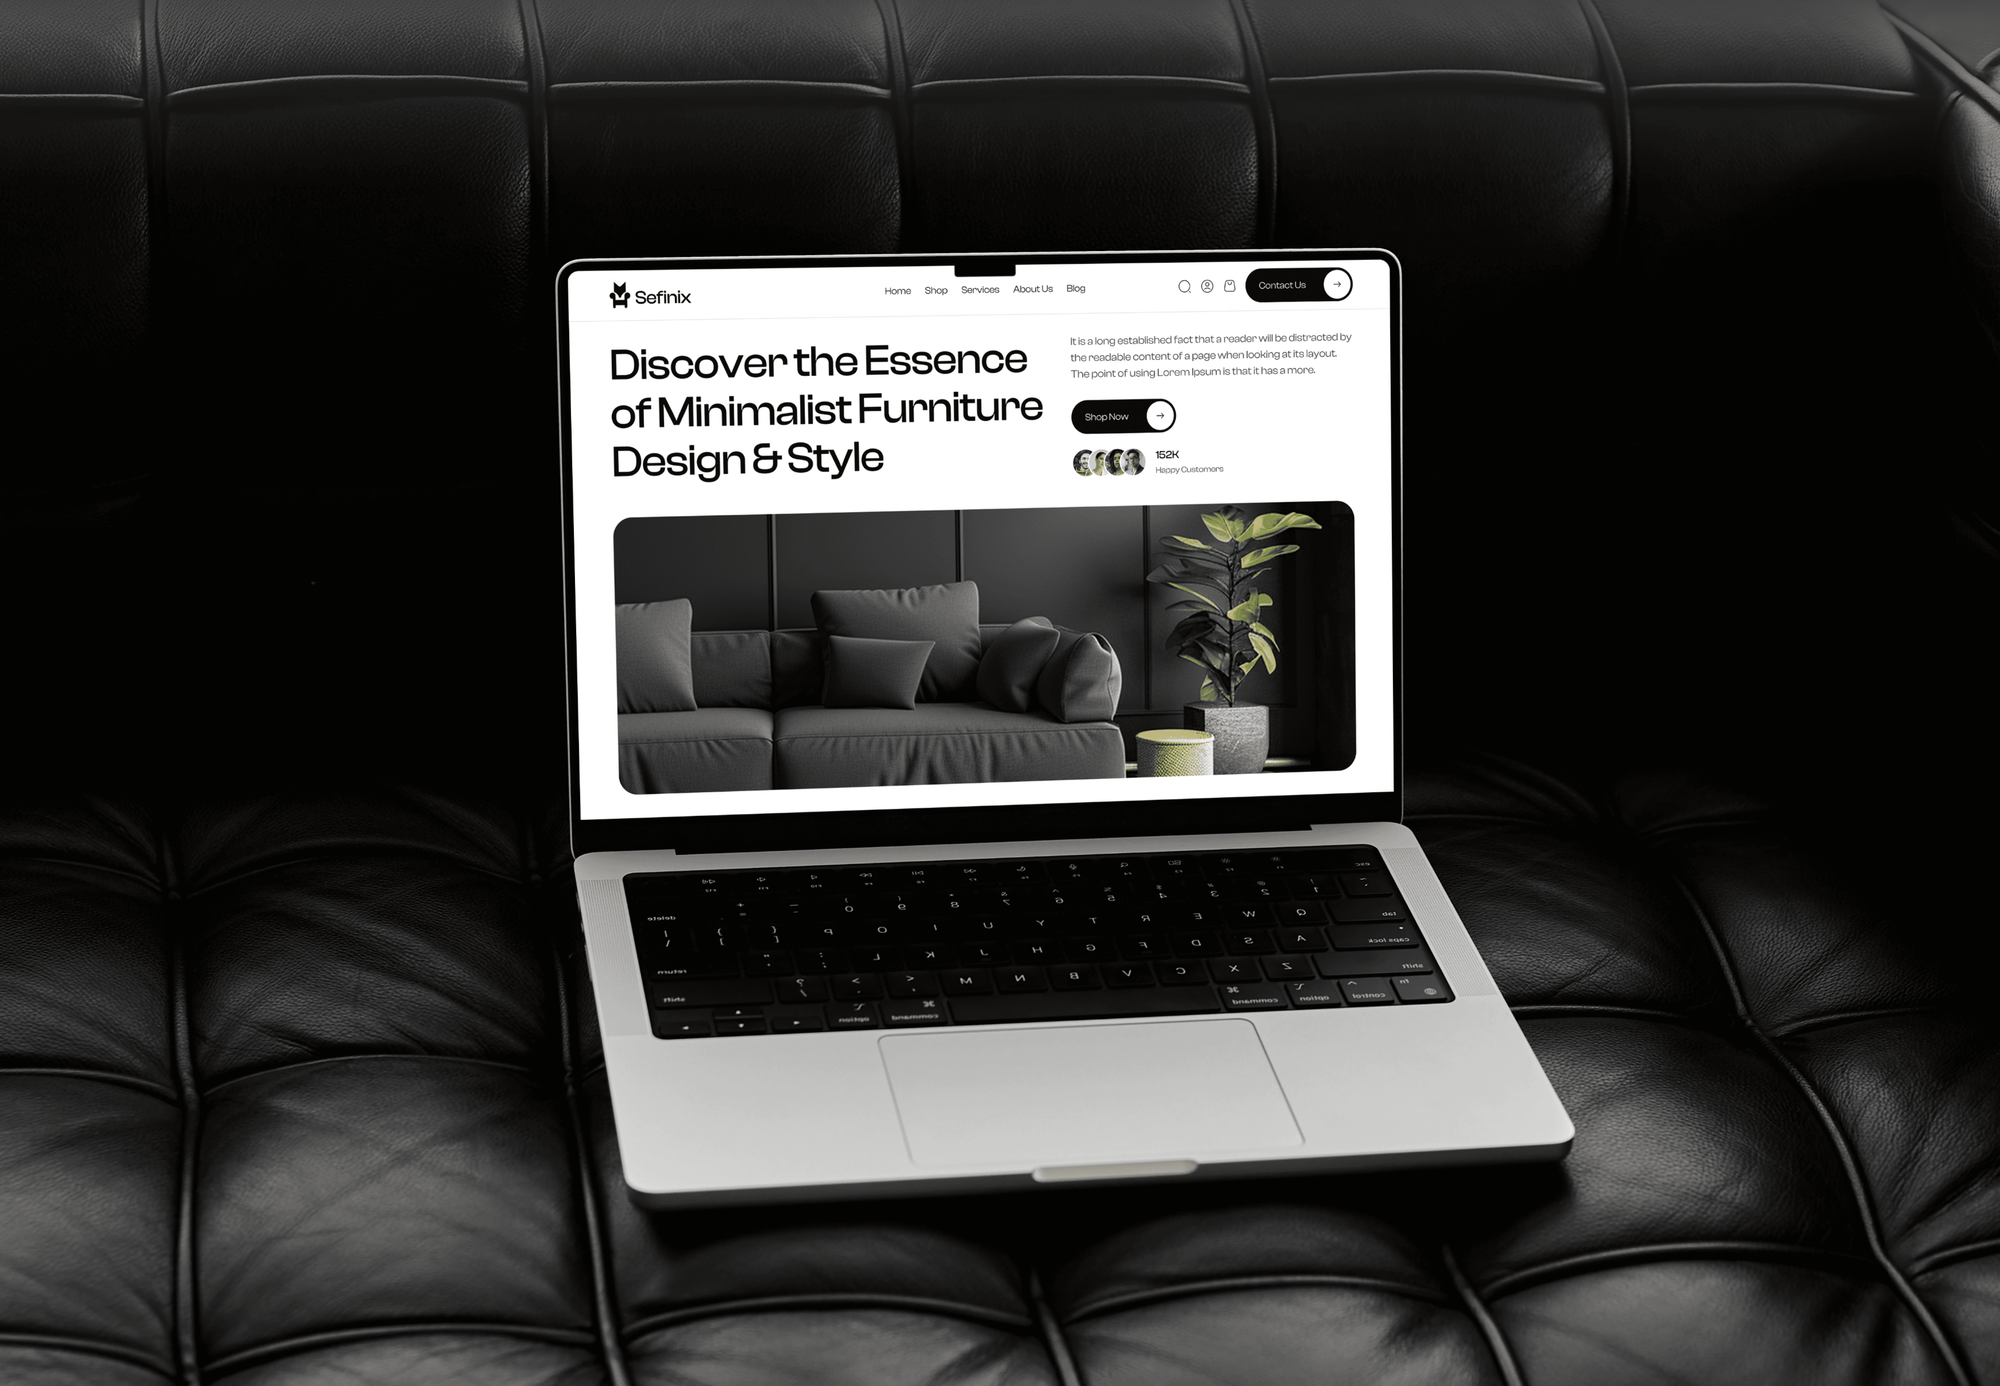
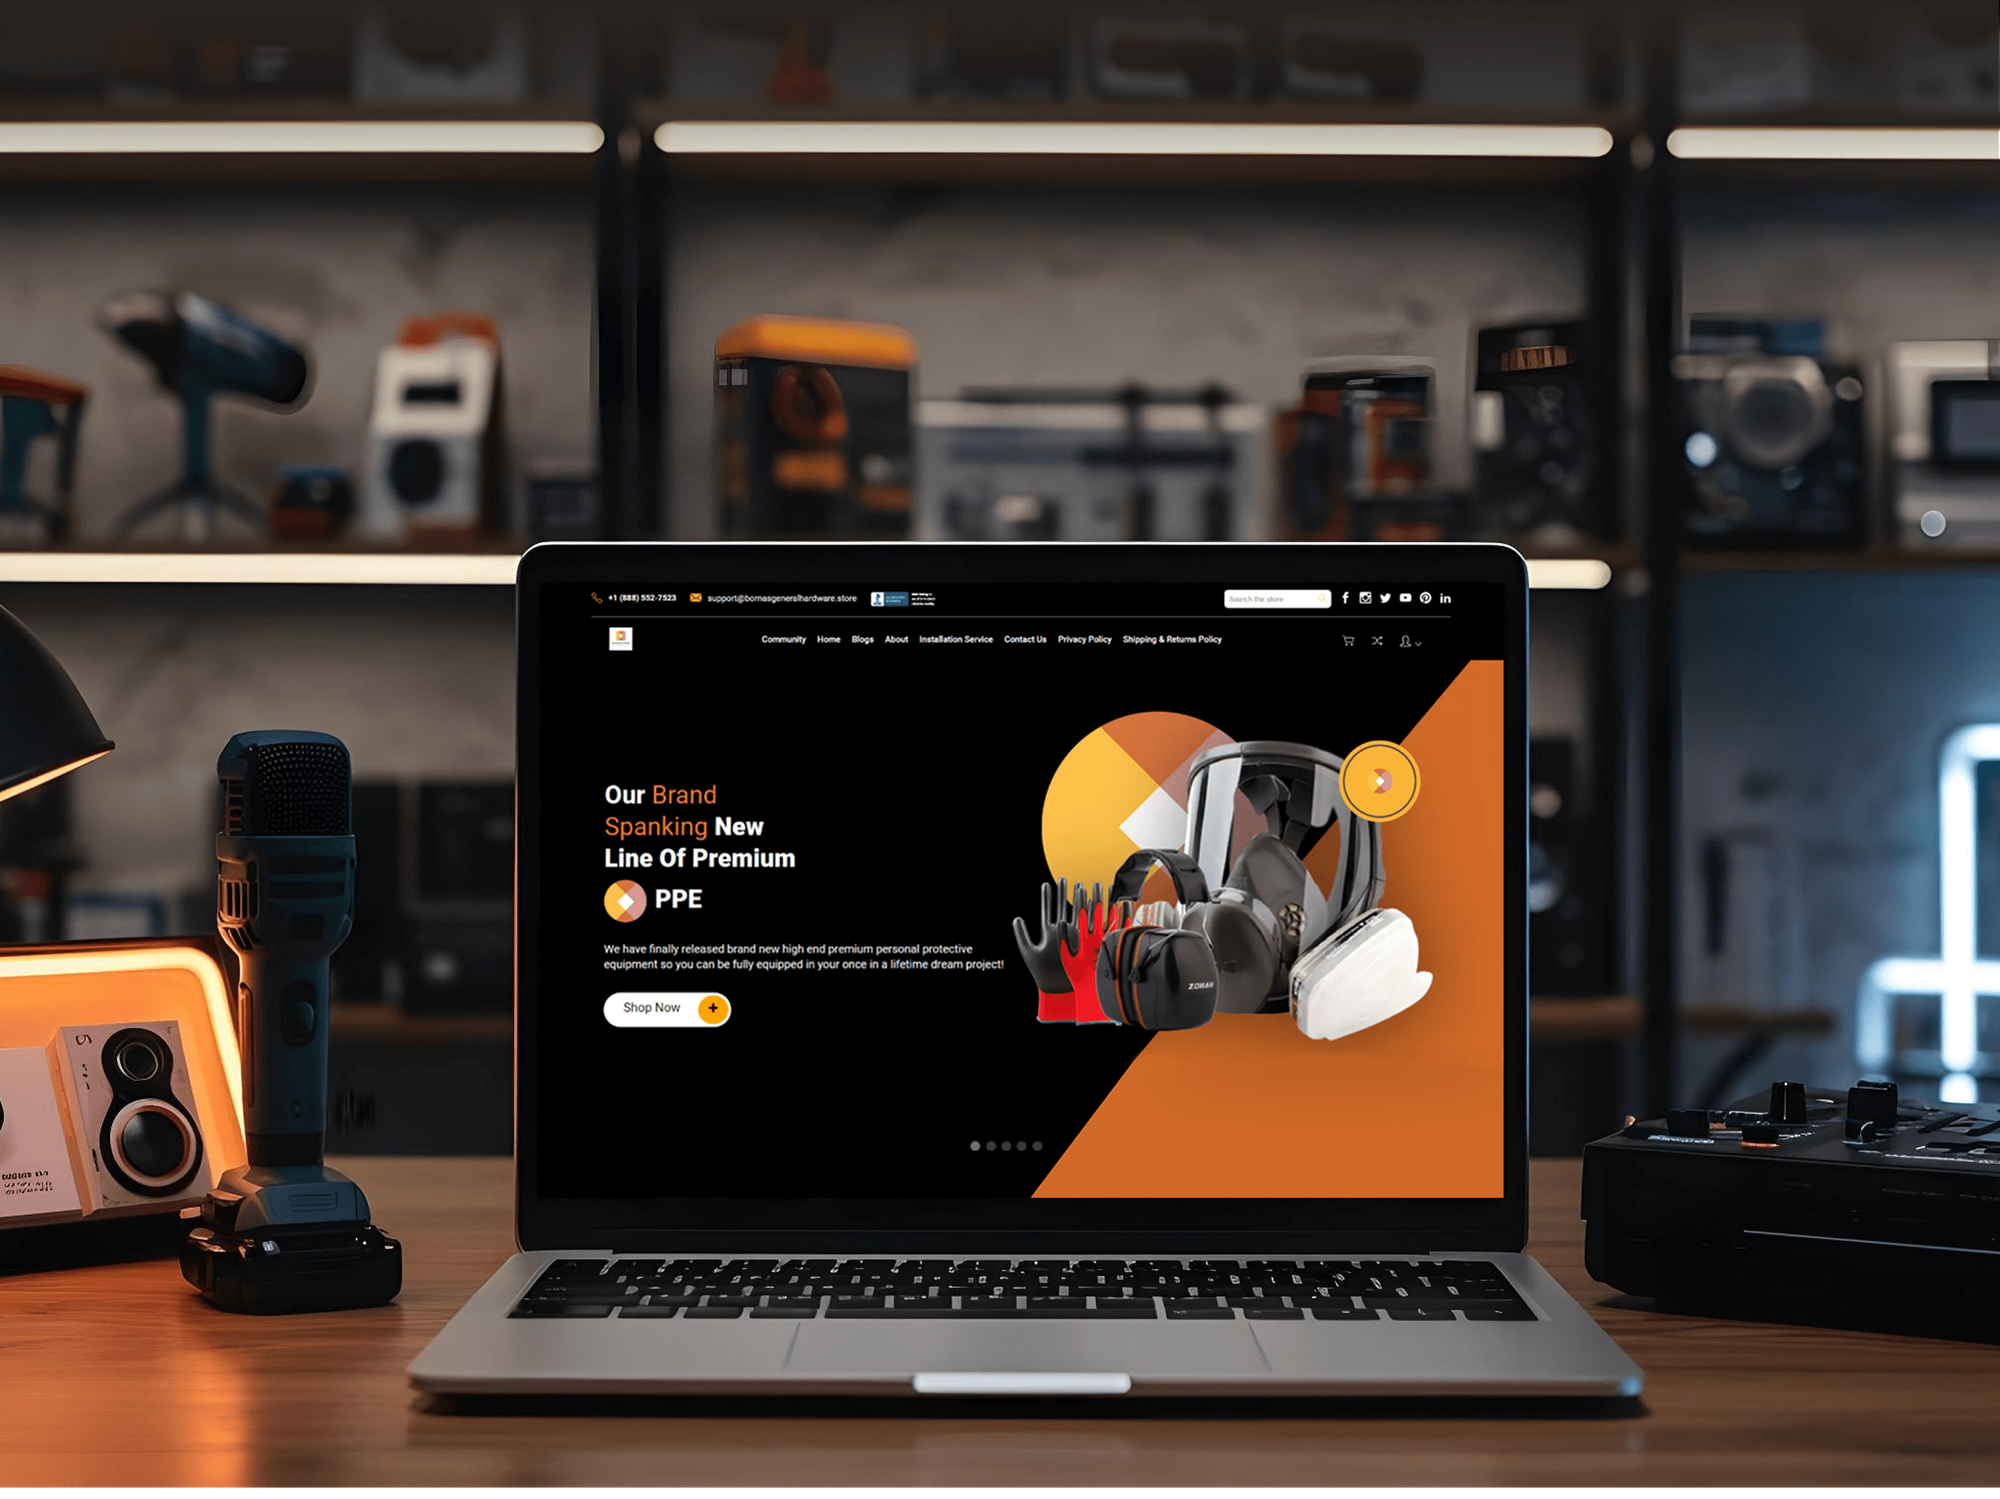
Ecommerce Projects We Have Built
A selection of Shopify and ecommerce builds shipped for clients, the kind of stores where a website security audit protects revenue and customer data.

Ready to find your weak spots first? ⚡ Get a free quote!
LET'S DISCUSS
We had a different kind of problem. People were visiting the store, adding products to their carts, and then disappearing before they finished the order. We had tried a few apps and made changes here and there, but nothing really seemed to solve the bigger issue. The team went through the shopping experience with us and pointed out things we hadn't really noticed ourselves. They cleaned up the cart and checkout flow, made the mobile experience much smoother, and helped us make the store feel easier to shop. I’m not going to pretend we fixed everything overnight, but it finally feels like the store is helping the sale instead of getting in the way of it.
Ethan Parker
Founder of Elite Academy
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
James Whitmore
Head of Marketing of Lumen Outdoor
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
Michael Bennett
Founder & CEO of Northbridge Consulting
07Work Culture
Why Store Owners Trust Us With Security
A long list of scary findings helps nobody, so we rank issues by real risk. These are the habits we bring to every website security service.

Ranked by risk
You see what to fix first and why.

Plugins reviewed
Third-party code is one of the biggest risks, so we check it.

Permissions checked
Too many admins and roles are a common weakness.

Mapped to OWASP
Findings use a standard framework your developers know.

Fixes available
We can fix what we find, or hand the list to your team.

Honest scope
We state up front what an audit covers.
08Overview
What does a website security audit include and how much does it cost?
DeveloperLook combines automated vulnerability scanning with manual testing, privilege escalation checks, form injection tests, and API token review, then maps findings to the OWASP Top 10 with a severity ranking. You get a prioritized fix list, not just a report, and we can implement fixes directly. Audits start at $1,500 and typically complete in 3-5 business days for a standard WooCommerce or Shopify store.
- Starting price
- From $1,500 for a standard WooCommerce or Shopify store
- Typical timeline
- 3-5 business days for a standard store, longer for larger or custom platforms
- What's scanned
- Outdated plugins and apps, SSL/TLS config, exposed admin panels, weak roles and permissions
- Manual testing included
- Privilege escalation, form injection, and API token checks beyond what automated scanners catch
- Framework used
- Findings mapped to the OWASP Top 10 with severity ranking and remediation guidance
- Fixes included
- You get a prioritized fix list, and we can implement the fixes directly as part of the engagement
- Recommended cadence
- Quarterly, or immediately after any major plugin, app, or theme change
- Audit vs pen test
- An audit finds and catalogs vulnerabilities, a penetration test actively attempts to exploit them
Who it's for
Store owners after a security scare
You've had a hack, suspicious admin activity, or a flagged malware warning and need to know exactly what's exposed before you keep operating.
Stores with a large app or plugin stack
You've installed dozens of Shopify apps or WordPress plugins over the years and don't know which ones introduced a vulnerability or went unmaintained.
Businesses preparing for compliance or insurance
A cyber insurance policy, PCI DSS requirement, or enterprise client contract requires proof of a recent security audit.
Sites handling customer payment or personal data
You store or process customer payment details, addresses, or account data and want to confirm access controls and roles are locked down correctly.
Agencies inheriting an unfamiliar codebase
You've taken over management of a site built by someone else and want a security baseline before making changes.
Not a fit for
If you want us to actively attempt to break into your site the way an attacker would, that's a penetration test, not an audit, see our Web Application Penetration Testing Services page.
If your main concern is losing data rather than being breached, our Website Backup and Disaster Recovery page covers tested, restorable backups instead.
If you're worried about GDPR or CCPA fines rather than hacking, that's privacy compliance, our Privacy Compliance and Consent Management page covers cookie consent and data rights.
09Pricing
Transparent Starting Prices for a Website Security Audit
These are starting points in USD. Your final price depends on your platform and how deep you want the manual testing, and you get a fixed proposal after a free scoping call.
Audit + Fix Implementation
Adds manual testing beyond automated scanners, with fixes implemented directly as part of the engagement.
- Everything in Standard Security Audit
- Manual testing (privilege escalation, form injection, API tokens)
- Fixes implemented directly by our team
- Prioritized fix list with remediation guidance
11The Right Technology for Your Project
Technology Stack
We use vulnerability scanners and manual review, and map findings to the OWASP Top 10 for WooCommerce, Shopify and custom platforms.
No tools available for the selected category.
Book Your Exclusive Strategy Session Today!
Pick a 30-minute slot that works for you. We meet on Google Meet to align on goals, scope, and the right next step.
What does a website security audit include?
Our audits combine automated vulnerability scanning for outdated plugins, apps, and SSL/TLS misconfigurations with manual testing for privilege escalation, form injection, and exposed API tokens. We also review server-level settings like database permissions and firewall rules, then map every finding to the OWASP Top 10.
How much does a website security audit cost?
Audits start at $1,500 for a standard WooCommerce or Shopify store. Larger sites, custom applications, or stores with extensive third-party integrations are scoped separately based on complexity.
How do I scan my store for vulnerabilities?
We run automated scanners to catch outdated software, exposed ports, and known CVEs, then follow up with manual testing that simulates real attack techniques scanners alone tend to miss, like chained privilege escalation or business-logic flaws in checkout flows.
What do you do after finding vulnerabilities?
You get a prioritized report ranking every finding by severity and exploitability, with clear remediation steps for each. If you want us to handle the fixes rather than your own team, that's included as part of the engagement rather than a separate handoff.
How often should I audit my site security?
We recommend a full audit quarterly, and an immediate re-audit any time you add a major new app, plugin, theme, or custom integration, since those are the most common sources of newly introduced vulnerabilities.
Can you fix the issues, not just report them?
Yes. Our audit engagement includes implementing the fixes for the vulnerabilities we find, not just handing you a report and leaving the remediation work to your team.
How do roles and permissions get reviewed?
We audit every admin and staff account against the principle of least privilege, checking whether accounts hold more access than their role requires, whether former employees or old integrations still have active credentials, and whether API tokens are scoped too broadly.
How long does an audit take?
A standard WooCommerce or Shopify store audit typically completes in 3-5 business days. Larger or more complex platforms with custom code and extensive integrations take longer, scoped upfront based on your specific setup.