Applicability and threshold check
Whether you're a covered financial institution and whether the 5,000-consumer exemption trims your duties.

For auto dealers, finance companies, and tax firms that hold customer financial data: every Safeguards Rule element in place, with evidence your team can show.
100%
Customer data systems mapped
5,000
Consumer threshold checked first
How your project runs
01 · FreeTeams we have built for:














The Problem
It shows up when a lender, a manufacturer audit, or a cyber insurer asks for your written security program and the honest answer is a shared login.
Logins
Managers share one login to the lender portal.
Logins
Named accounts with MFA on the DMS, CRM, email, and lender portals.
Paper
Deal jackets with Social Security numbers sit in an open cabinet.
Paper
Locked storage, access rules, and disposal schedules for paper customer files.
Vendors
The DMS vendor's remote access goes unreviewed for years.
Vendors
A service provider review with contract terms and access checks for each vendor.
Breach plan
Nobody knows when the FTC must hear about a breach.
Breach plan
A written incident plan with the FTC 30-day notice step for 500+ consumers.
Your F&I office runs credit applications all day. Deal jackets with Social Security numbers sit in an open cabinet, and two managers share one login to the lender portal. Your DMS vendor has remote access nobody reviews. The website's credit app emails PDFs to a sales inbox. Then your cyber insurer asks for your Qualified Individual, your risk assessment, and proof of MFA. You have an old policy binder with a former manager's name on it.
We start by checking how the rule applies to you, including the 5,000-consumer threshold. Then we map every place customer data lives: DMS, CRM, lender portals, email, paper, and the website. Next we work through each required element, from a Qualified Individual and a written risk assessment to MFA, encryption, vendor oversight, training, and an incident plan. You end up with a program the store runs, not a binder nobody opens.
Built for dealership systems
DMS, F&I menus, lender portals, CRM, and deal jackets covered, not only office laptops.
Qualified Individual set up
One accountable person named, with written duties, a backup, and a yearly board report template.
MFA for everyone with access
Every user who reaches customer data signs in with MFA, including managers and vendors.
Our FTC Safeguards Rule Compliance Process
You confirm which duties apply, approve each document, and test each new safeguard with staff before it reaches the sales floor.
We ask what financing, leasing, or tax work you do and roughly how many consumers' records you keep. You get a fixed quote and an early read on which parts of the rule apply.
What's Included
Each project covers an applicability check, a data map, a written risk assessment, the required safeguards, vendor oversight, training, and an incident plan.
Compare Options
Your DMS vendor and local IT provider both cover pieces of the rule well. Here is where each fits when you need the whole program.
| Feature | DeveloperLookBest fit | DMS vendor add-on | Local IT provider |
|---|---|---|---|
| Applicability check | Done first, in writing | Rarely included | Not usually |
| Systems covered | DMS, CRM, portals, paper, website | Their own system | Devices and network |
| Risk assessment | Written to the rule's criteria | For their platform only | Technical risks they see |
| MFA and encryption | Set up across every system | Inside their product | Strong on managed devices |
| Vendor oversight | Reviews each provider | Not their role | Sometimes, on request |
| Qualified Individual | Named, briefed, with report template | Not included | Sometimes acts as one |
| Cost | Fixed price from $950 | Often a monthly add-on | Inside monthly fees |
| Ongoing monitoring | Handover plus yearly checklist | Strong for their product | Strong for day-to-day IT |
Projects We've Built
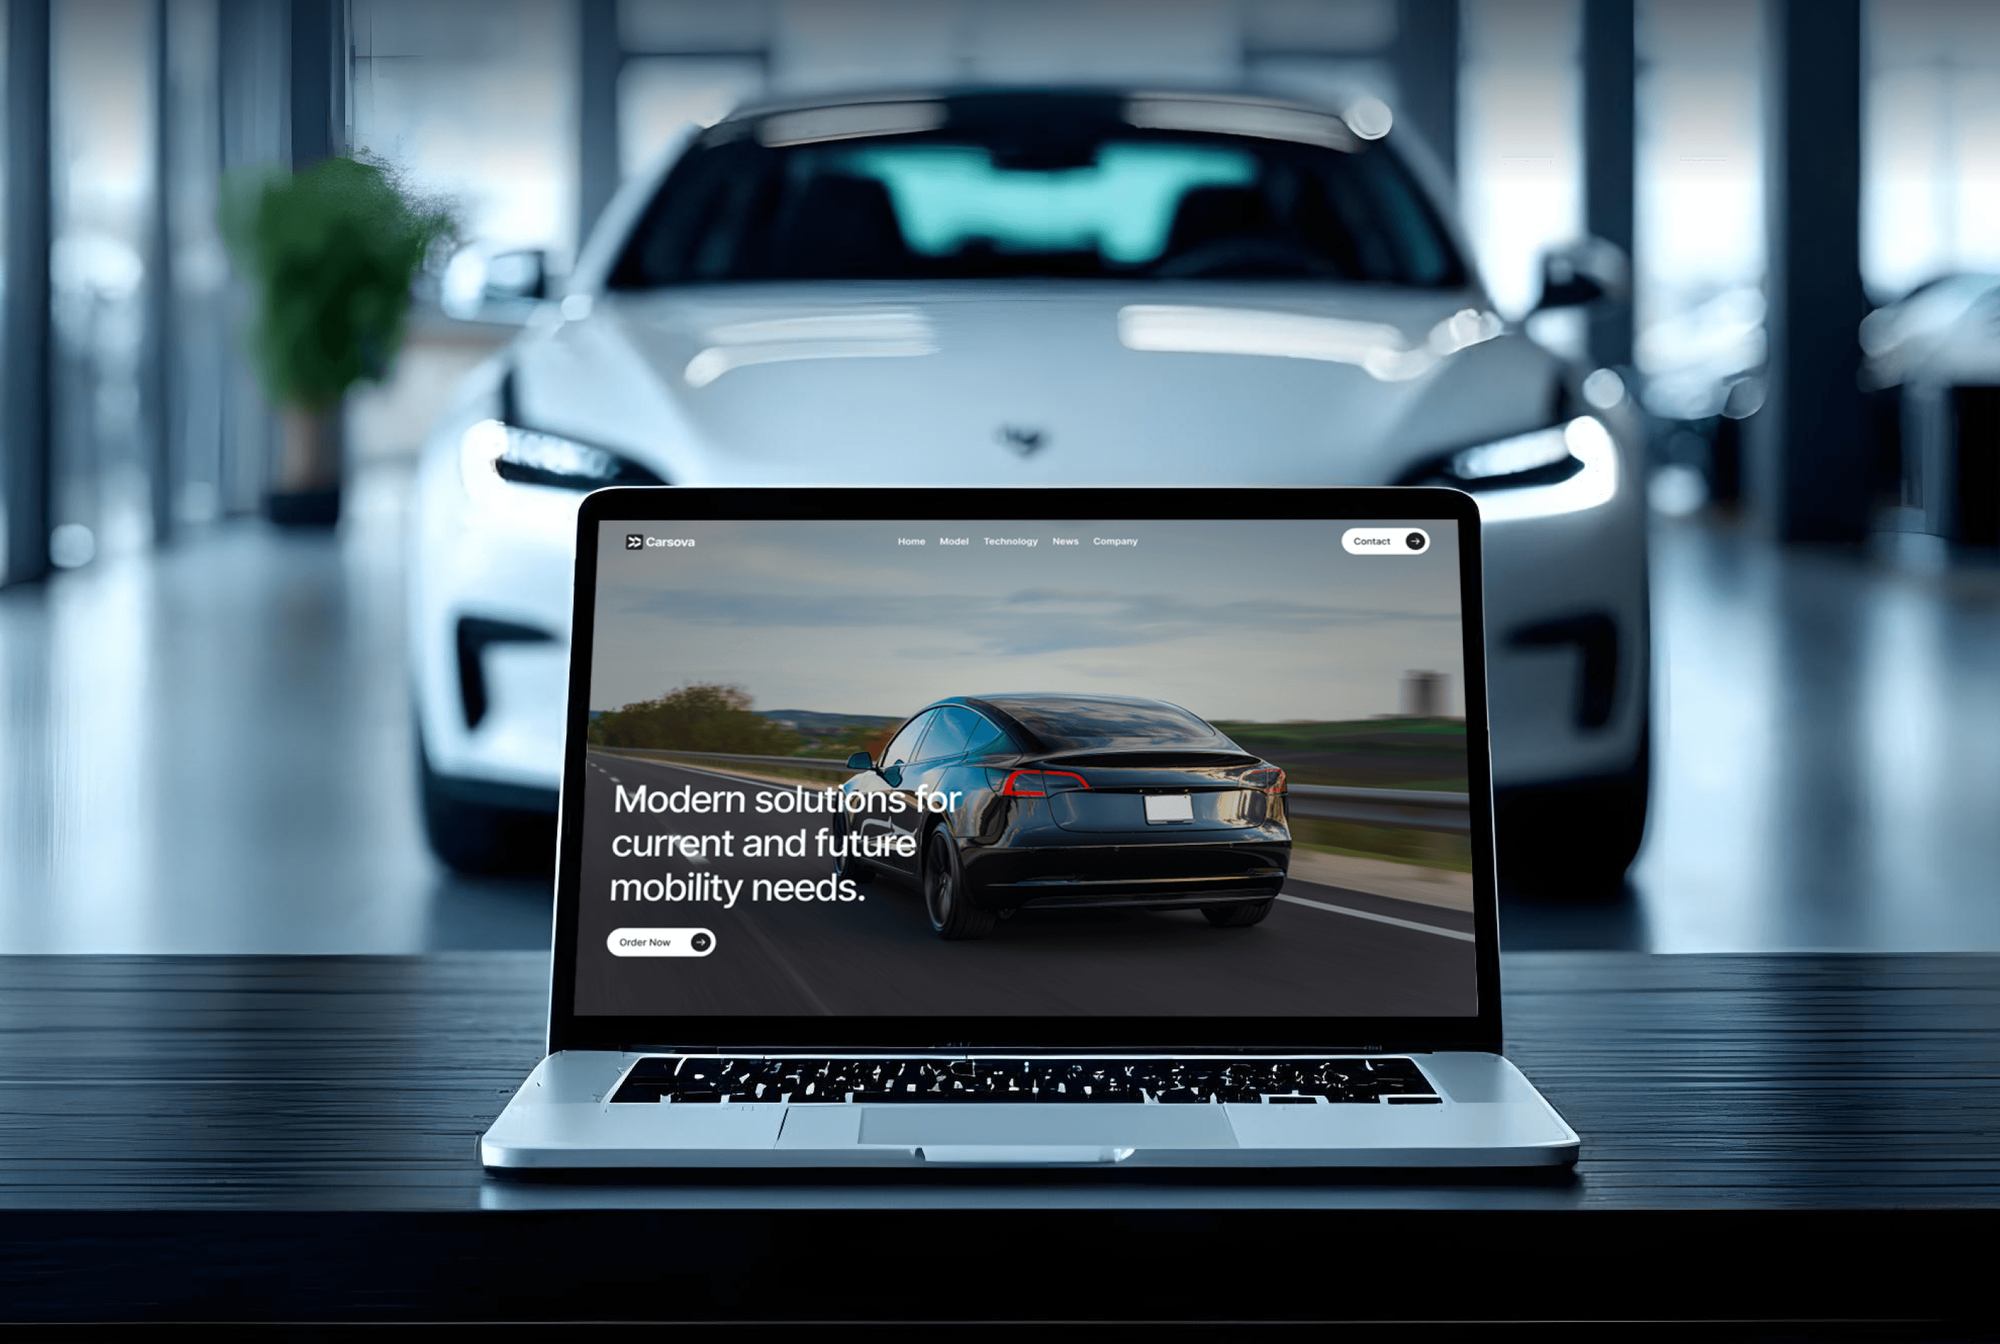
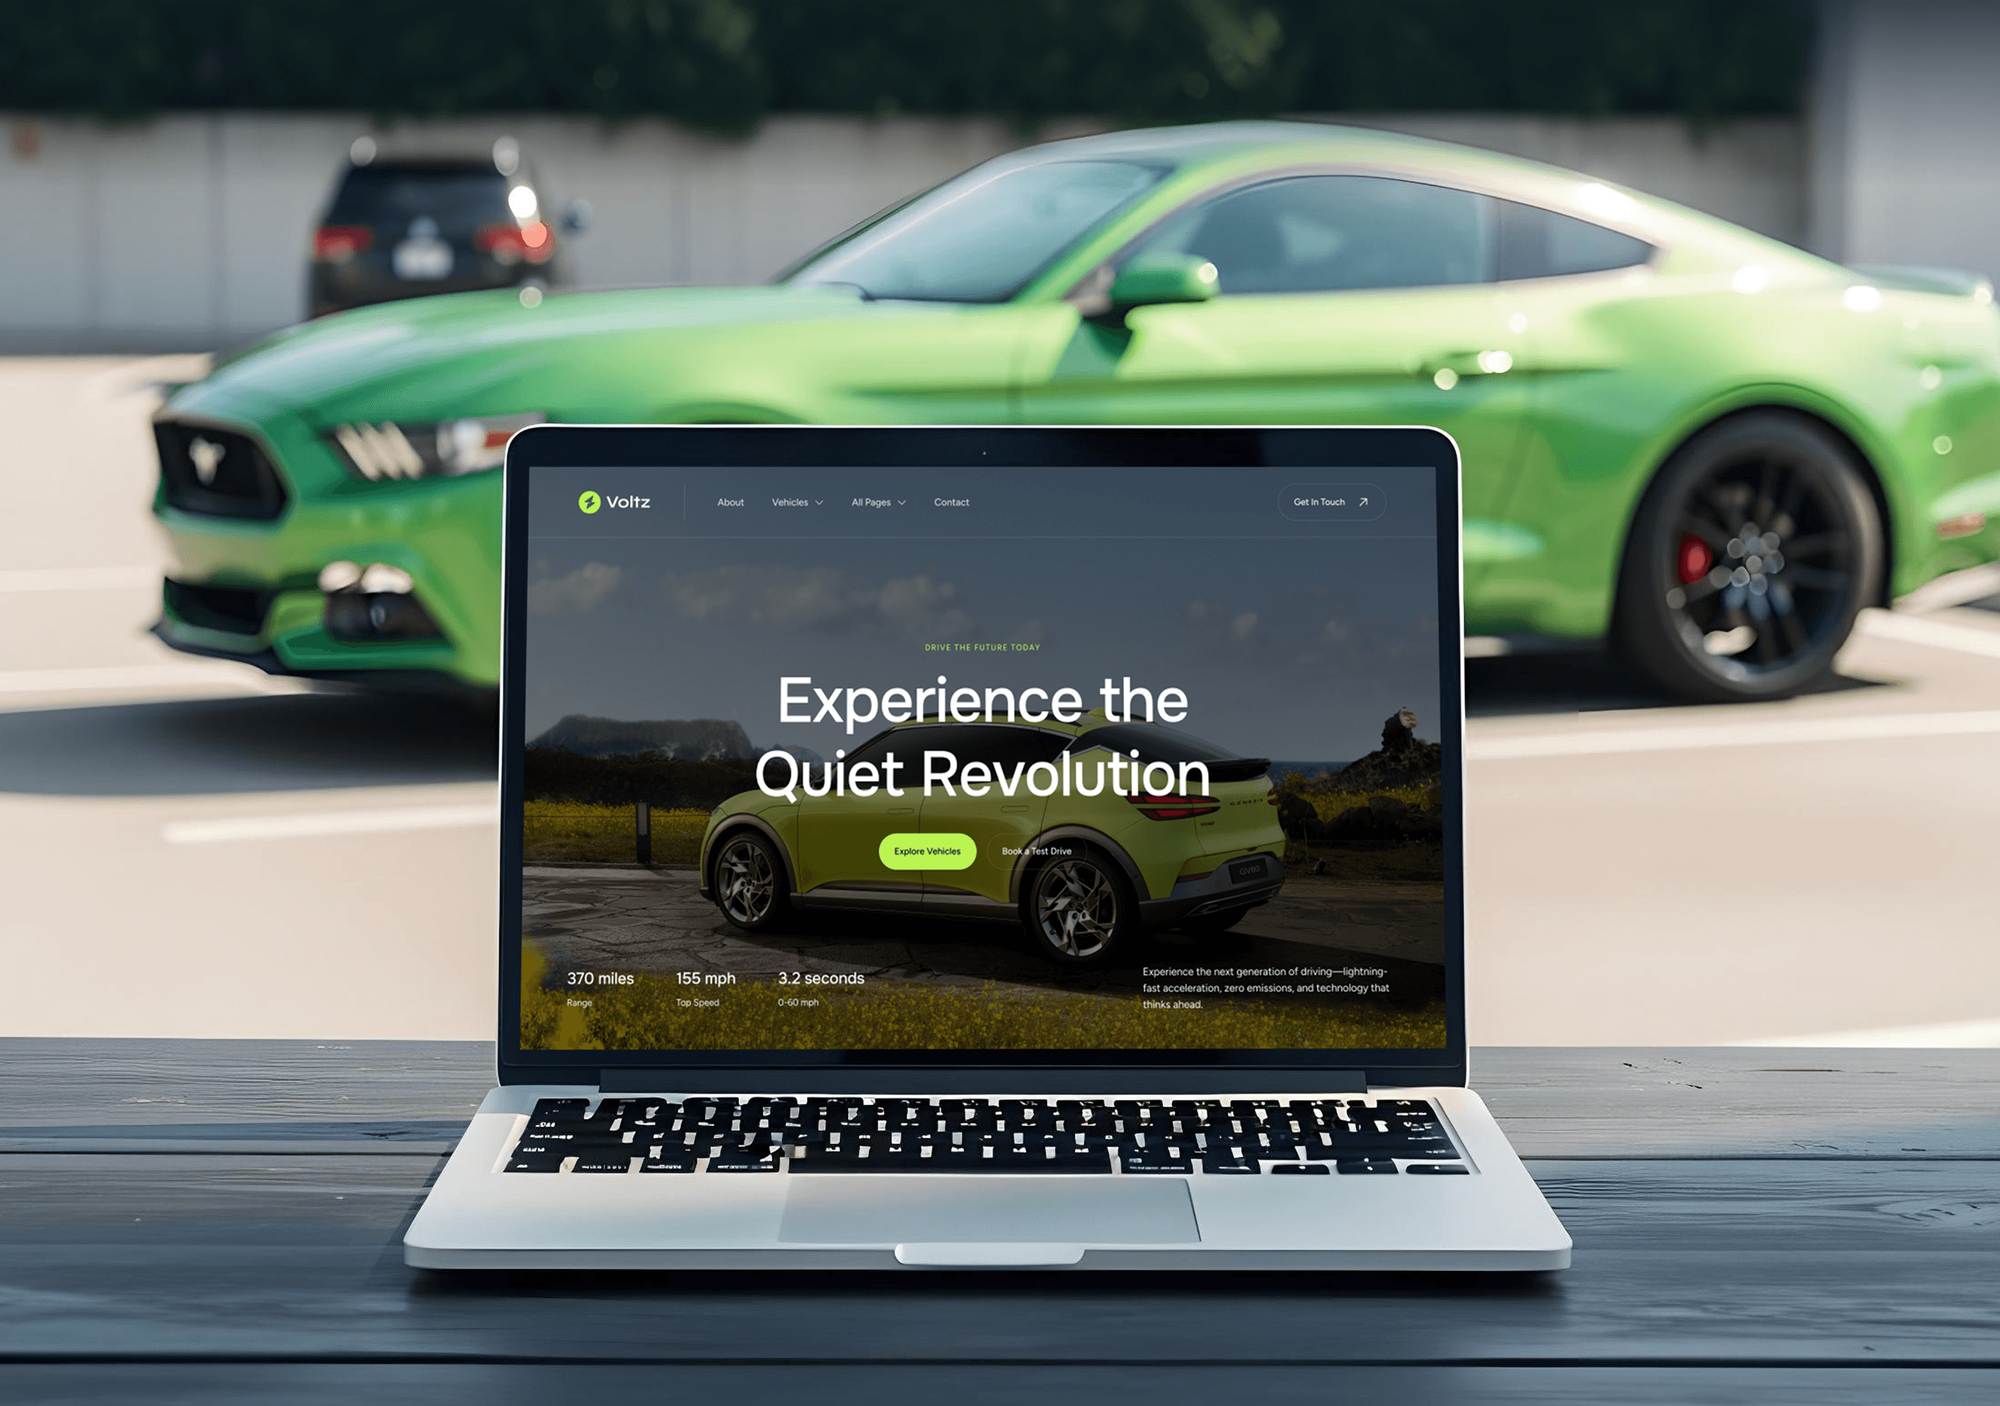
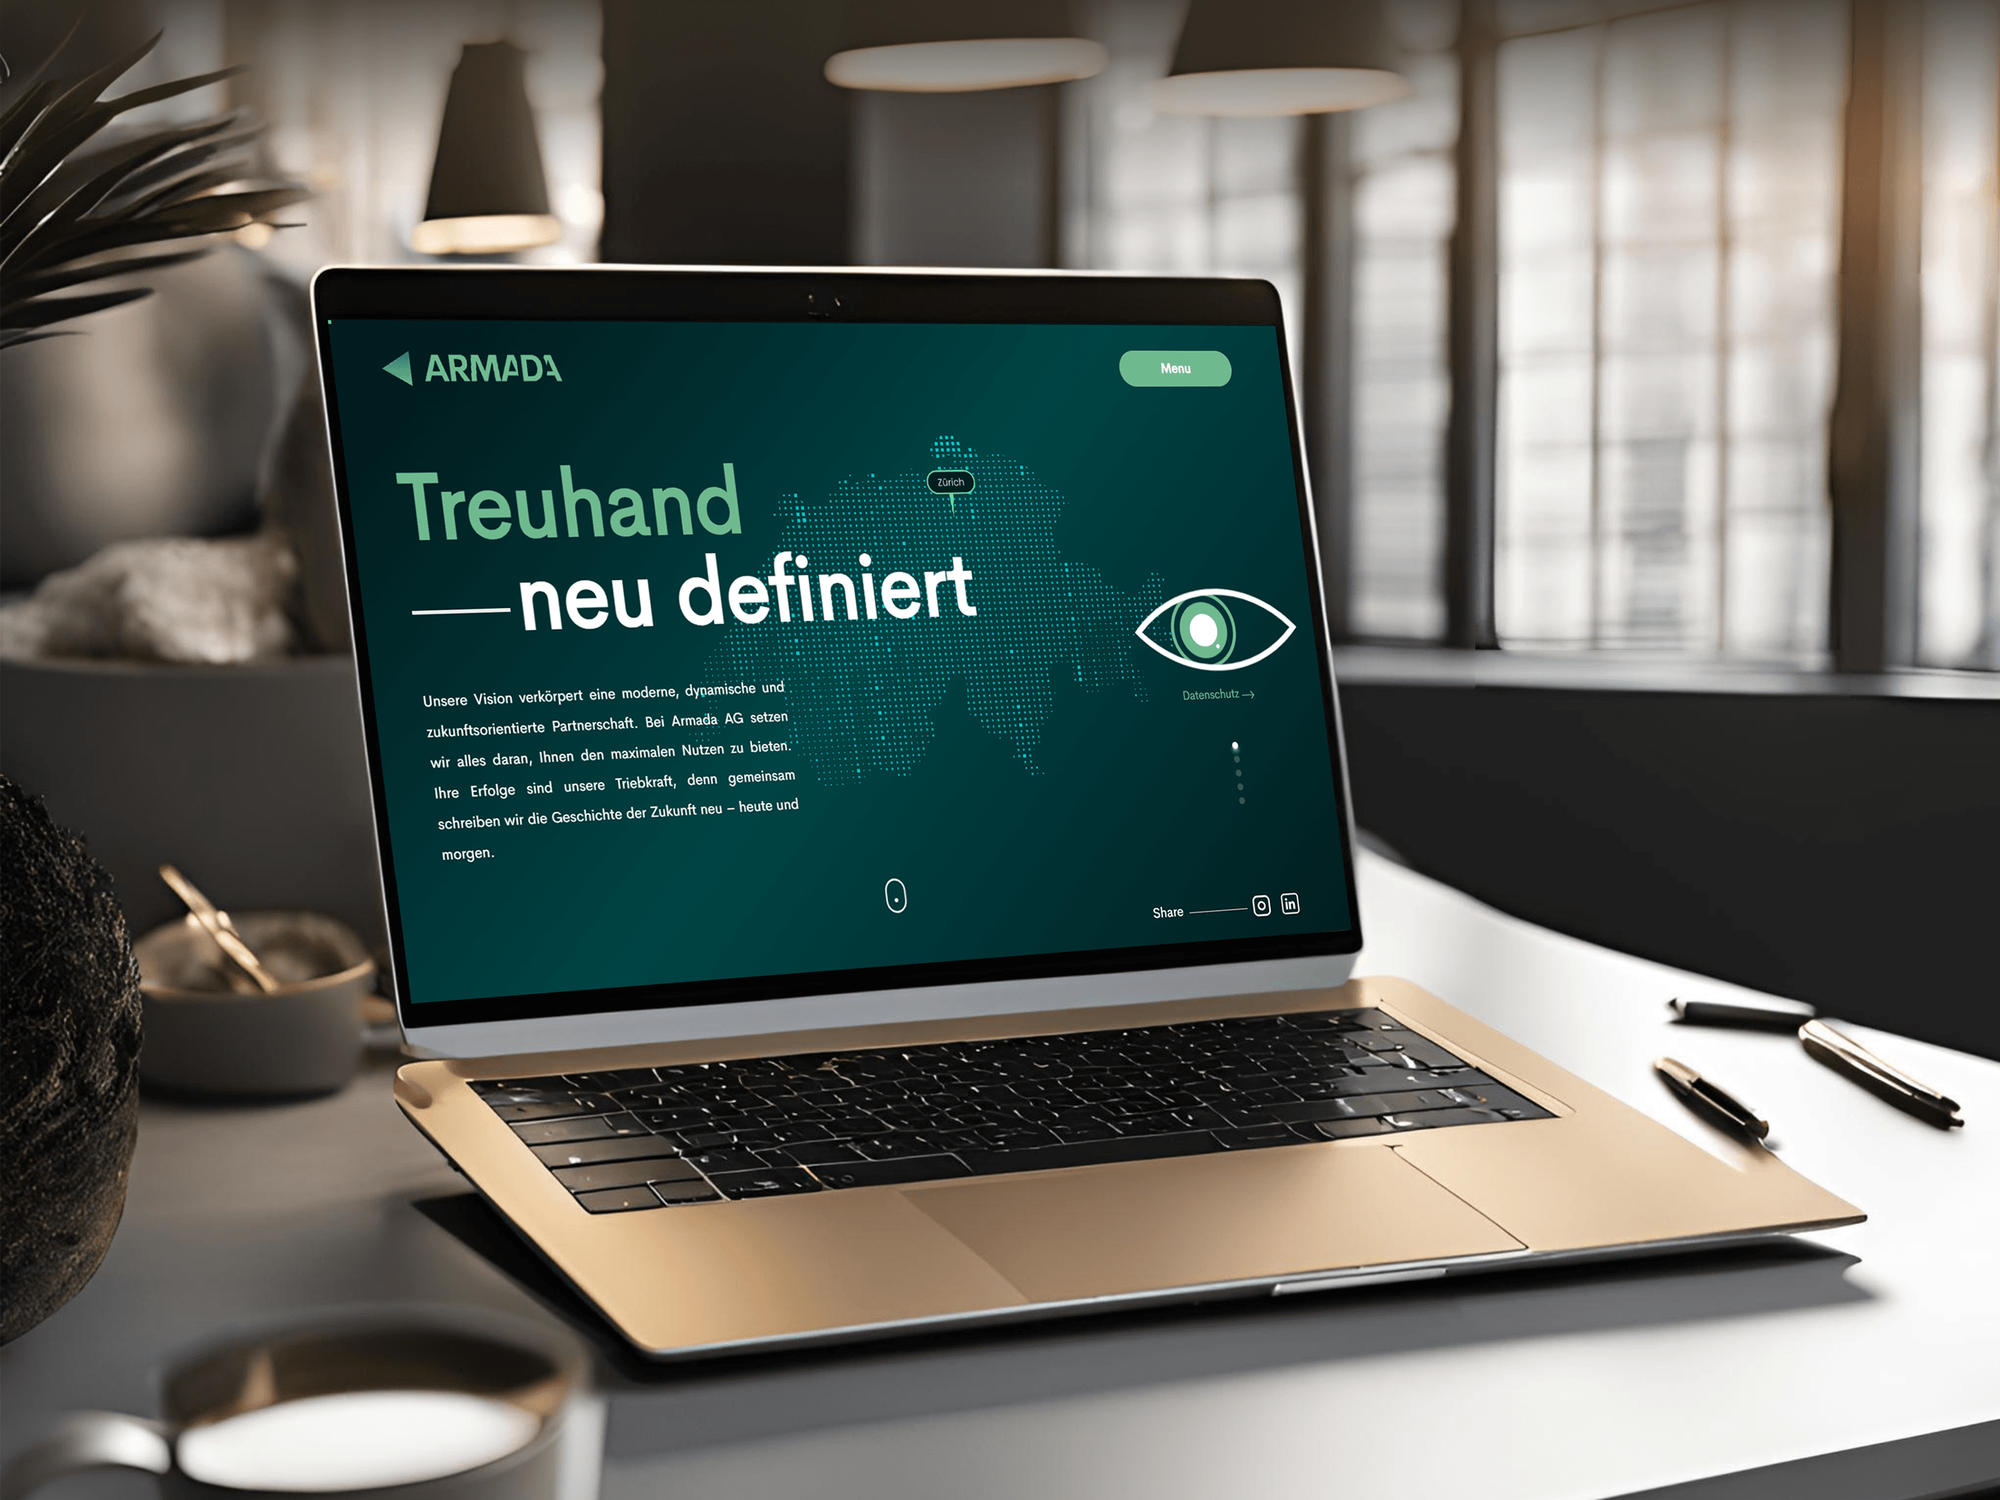
Automotive sites and finance platforms we designed and built. They show our build work for businesses that handle customer data, not Safeguards Rule projects.
What Our Clients Say
Feedback from teams we have built platforms, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A security program only works if the sales floor can live with it. These habits put the rule's requirements in place without slowing deals.
MFA and access changes are tested with F&I and sales first. Deals keep moving, and nobody meets a new login screen during a customer's signing.
If you keep records on fewer than 5,000 consumers, some duties drop away. We'll tell you before we quote, so you don't pay for parts you don't need.
Every safeguard in your program is checked in the system itself. When a lender or insurer asks, you can show the setting, not just the policy.
We put the rule's security requirements in place and write the program. Questions about state law, contracts, or regulator letters go to your lawyer.
Multi-store groups get one program with store-level checklists. Each location follows the same rules without keeping its own separate binder or policy set.
You get a fixed quote based on rooftops, offices, and systems. Extra stores are priced before work starts on them.
Overview
DeveloperLook delivers FTC Safeguards Rule compliance for auto dealers, lenders, and other non-bank financial businesses. We check applicability, map customer data, write the risk assessment and program, and set up MFA, encryption, vendor reviews, training, and the FTC breach notice steps. Projects start at $950 and take 2 to 8 weeks.
DEVELOPERLOOK
Project facts · FTC Safeguards Rule Compliance
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Franchise and independent auto dealers
Your store arranges financing and leases, and you need the FTC Safeguards Rule auto dealers must follow turned into settings, not a binder.
Dealer groups with several rooftops
Your manufacturer audit asked how each store meets the FTC safeguard rule for auto dealers, and every location answered differently.
Mortgage brokers and finance companies
You're a non-bank lender or broker, and a bank partner wants proof of your FTC safeguards compliance before renewing.
Tax and accounting practices
Your practice prepares returns, so the FTC Safeguards Rule CPA firms must follow when they handle tax clients now needs MFA, testing, and vendor reviews.
Owners starting from a checklist
You downloaded an FTC Safeguards Rule checklist and want someone to check each line in your systems instead of ticking boxes.
Not a fit
Only need the written plan
You're a small tax office that only needs the written plan. Our Written Information Security Plan page covers that faster and for less.
Bank or insured credit union
You're a bank or a federally insured credit union. Your own regulator's safeguards guidelines apply instead of the FTC rule.
Need an ongoing security lead
You want someone to act as your Qualified Individual every month. Our vCISO Services page covers that ongoing role.
Need legal advice
You need advice on a regulator letter, state privacy law, or customer contracts. A lawyer should handle that, and we'll share our documents with them.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on rooftops or offices, systems holding customer data, and the safeguards to fix, and you get a fixed proposal after a free call.
For Agencies
You own the client relationship. We supply applicability checks, risk assessments, and safeguard setup under your brand, so your dealer and finance clients get a program that fits the rule.
White label: your client only ever sees your brand
Send rooftops, DMS and CRM vendors, financing activity, and any audit requests.
We run the assessment and set up safeguards alongside your team.
We hand over the program and board report template under your brand.
Send rooftops, DMS and CRM vendors, financing activity, and any audit requests.
We run the assessment and set up safeguards alongside your team.
We hand over the program and board report template under your brand.
The Right Technology for Your Project
We secure the dealer, finance, and office systems that hold customer information, and add the identity and testing tools the rule calls for.
 Burp Suite
 OWASP
Related Services
Dealers and lenders often add an MFA rollout, an outside security lead, small business security basics, or a dealer CRM.
This page
FTC Safeguards Rule Compliance
Pairs with the 6 services around it
FAQ
Straight answers on cost, who the rule covers, what it requires, and when it started.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Compliance work with us starts at $950 for an applicability check, data inventory, risk assessment, and gap list. The written program with MFA, encryption, vendor reviews, training, and an incident plan starts at $2,950. Dealer groups with testing and reporting start at $6,300. You get a fixed quote after a free call.
Most single stores take 5 to 8 weeks from first call to a working program. The gap assessment alone takes 2 to 3 weeks. MFA rollouts drive the timing, because we test them with sales and F&I staff before switching them on. Dealer groups take longer.
It's the regulation under the Gramm-Leach-Bliley Act that tells non-bank financial institutions how to protect customer information. It requires a written information security program with specific elements, from a Qualified Individual to MFA, encryption, testing, and an incident response plan. It's codified at 16 CFR Part 314.
It applies to non-bank financial institutions under the FTC's jurisdiction. That includes most auto dealers that finance or lease vehicles, mortgage brokers, payday lenders, finance companies, and tax preparation firms, including CPA practices that prepare returns. Banks and federally insured credit unions follow their own regulators instead. Below 5,000 consumers, a few duties fall away.
Its goal is to protect the security, confidentiality, and integrity of customer information. In plain terms, it pushes businesses to know where customer data is, limit who can reach it, and protect it in storage and transit. It also expects a fast response when something goes wrong. It sets a process, not a specific product.
Yes, most are. The FTC says the rule covers most auto dealers that finance or lease vehicles, since that makes them financial institutions under the Gramm-Leach-Bliley Act. That brings in the F&I office, credit applications, the DMS, and lender portals. A cash-only dealer that doesn't arrange financing or leases may fall outside it.
The FTC issued the original rule in 2002, and it took effect in May 2003. Major amendments followed in 2021, with the last of the new requirements taking effect on June 9, 2023. A breach notification amendment took effect on May 13, 2024, adding the 30-day FTC notice for events involving 500 or more consumers.
The rule requires a Qualified Individual, a written risk assessment, and safeguards based on it. Those include access controls, a data inventory, encryption, secure development, MFA, disposal within 2 years of last use, change management, and activity monitoring. You must also test or monitor, train staff, oversee vendors, keep an incident plan, and report to the board yearly.
A useful checklist follows the rule's elements and names your dealership systems. It should cover the DMS, CRM, lender portals, F&I menus, website credit apps, email, and paper deal jackets. For each one, check MFA, encryption, who has access, how long records are kept, and which vendor can reach them. Then verify each line in the system itself.
Yes, for most covered businesses. The Qualified Individual reports to the board in writing at least once a year, and testing continues through monitoring or yearly pen tests with scans every 6 months. You get 30 days of questions and program updates after handover, plus a yearly review checklist.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.