
Named security lead
One person who learns your systems and owns the decisions month after month, instead of a rotating help desk.

For SaaS and service companies facing customer audits: a named security lead who owns your roadmap, policies, and questionnaires, from $950 per month.
1
Named security lead
2days
Questionnaire turnaround
How your project runs
Teams we have built for:














The Problem
It shows up when enterprise customers, insurers, or auditors ask who leads security, and the honest answer is your CTO, on weekends, between releases.
01 · Midnight answers
Your CTO answers questionnaires after hours.
Your lead keeps an answer library and drafts each questionnaire response.
02 · Draft policies
Your incident response plan is still an unfinished draft.
Policies and the incident plan get finished, approved, and reviewed on a schedule.
03 · Slipping audits
SOC 2 readiness slips by another quarter.
A tracked roadmap gives each control an owner and a due date.
04 · No owner
Every decision waits for someone with free time.
One named lead makes the calls and reports to leadership each month.
Your CTO is answering security questionnaires at midnight again. A prospect wants your SOC 2 status, your insurer wants proof of MFA, and the incident response plan is a draft someone started last year. Every security decision waits for someone with time, and nobody has any. A full-time CISO would fix it, but the search takes months and the salary doesn't fit this year's plan. Meanwhile, deals stall in procurement and audits slip another quarter.
We start with a 30-day baseline of your risks, policies, and customer commitments, led by the person who will own your program. Each month, that lead moves the roadmap forward, keeps policies current, answers questionnaires, and reports to leadership in plain language. You get the decisions and paperwork of a security leader on a set number of hours. Security finally gets an owner instead of a waiting list.
One named lead
The same person leads your program every month, learns your systems, and joins your leadership calls.
Published hours, fixed fee
Each plan lists its monthly hours, so you know what leadership time you're buying.
Support for deals and audits
Questionnaires, customer security reviews, and auditor requests get answered from one maintained library.
Our vCISO Services Process
You meet your lead before signing, approve the first 90-day plan, and see progress in a monthly report you can forward to leadership.
We talk through your customers' demands, your audits, and your current setup, and you meet the lead who would own your program. You get a written plan, the monthly hours, and a fixed fee before signing.
What's Included
Our vCISO services give you a named security lead with set monthly hours, owning the roadmap, the policies, and the paperwork customers ask for. Higher plans add vendor reviews, compliance tracking, and audit support.
Compare Options
The vCISO vs CISO choice comes down to workload and budget, and a compliance platform automates evidence collection well. Here's what each option gives you.
| Feature | DeveloperLookBest fit | Full-time CISO | Compliance platform |
|---|---|---|---|
| Monthly cost | From $950 per month | A full executive salary | Annual software license |
| Leadership hours | 6 to 16 hours a month | Full time, every week | None included |
| Time to start | Right after the fit call | Months to recruit | Quick to connect |
| Evidence collection | Tracked by your lead | Built by their team | Automated, its strongest point |
| Policies and decisions | Written and owned | Written and owned | Templates only |
| Customer questionnaires | Answered in 2 business days | Answered in-house | Some automate drafts |
| Board reporting | Monthly and quarterly | Ongoing, in person | Dashboards only |
| Best for | Growing teams with few incidents | Large or high-risk companies | Teams with security staff |
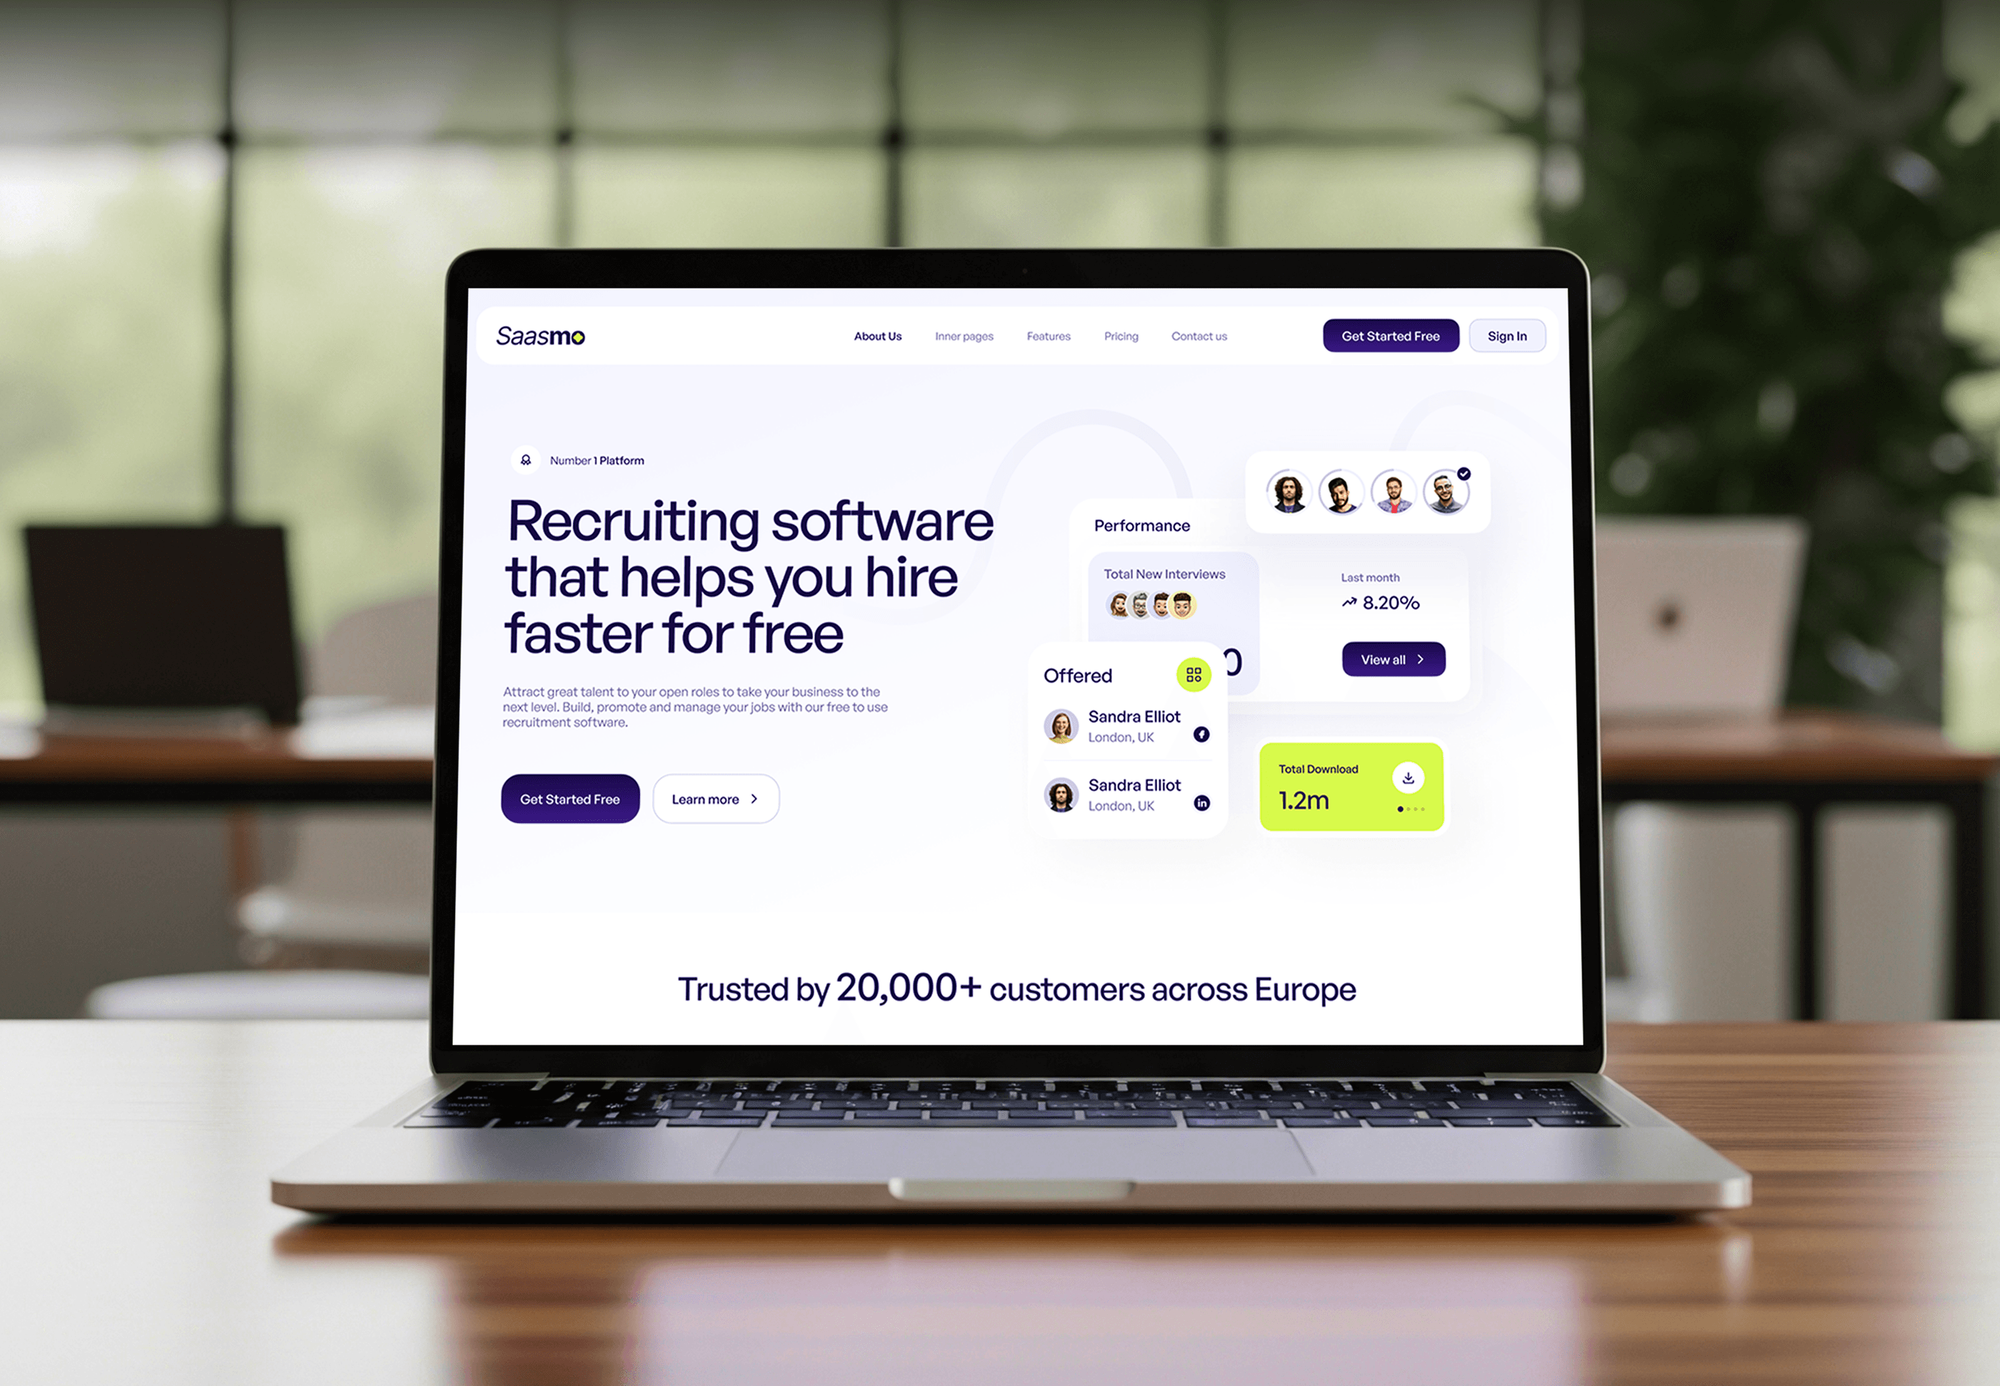
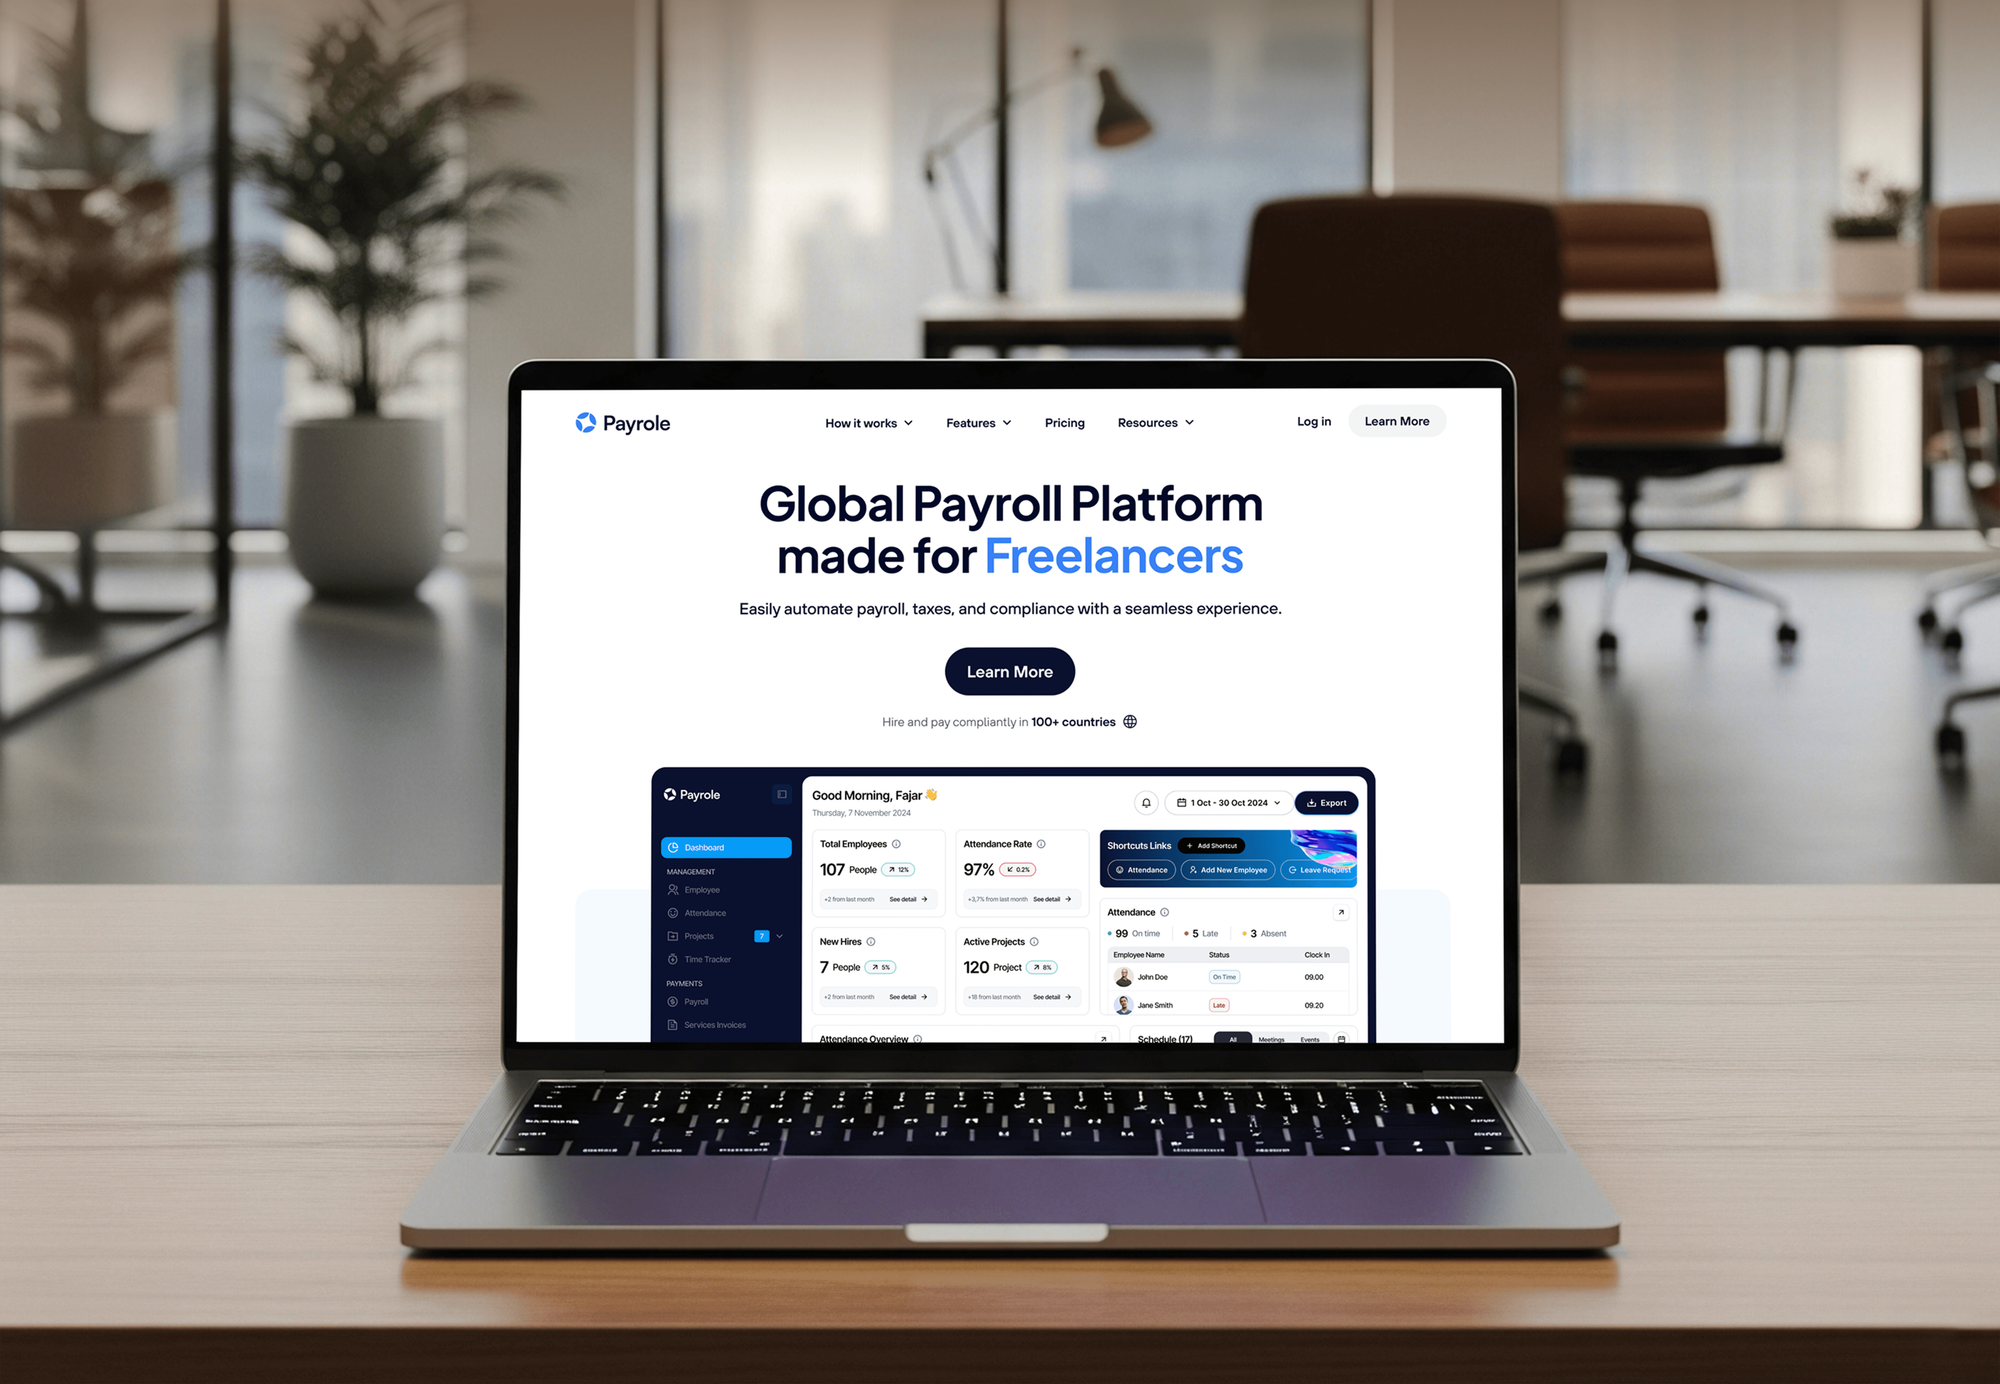
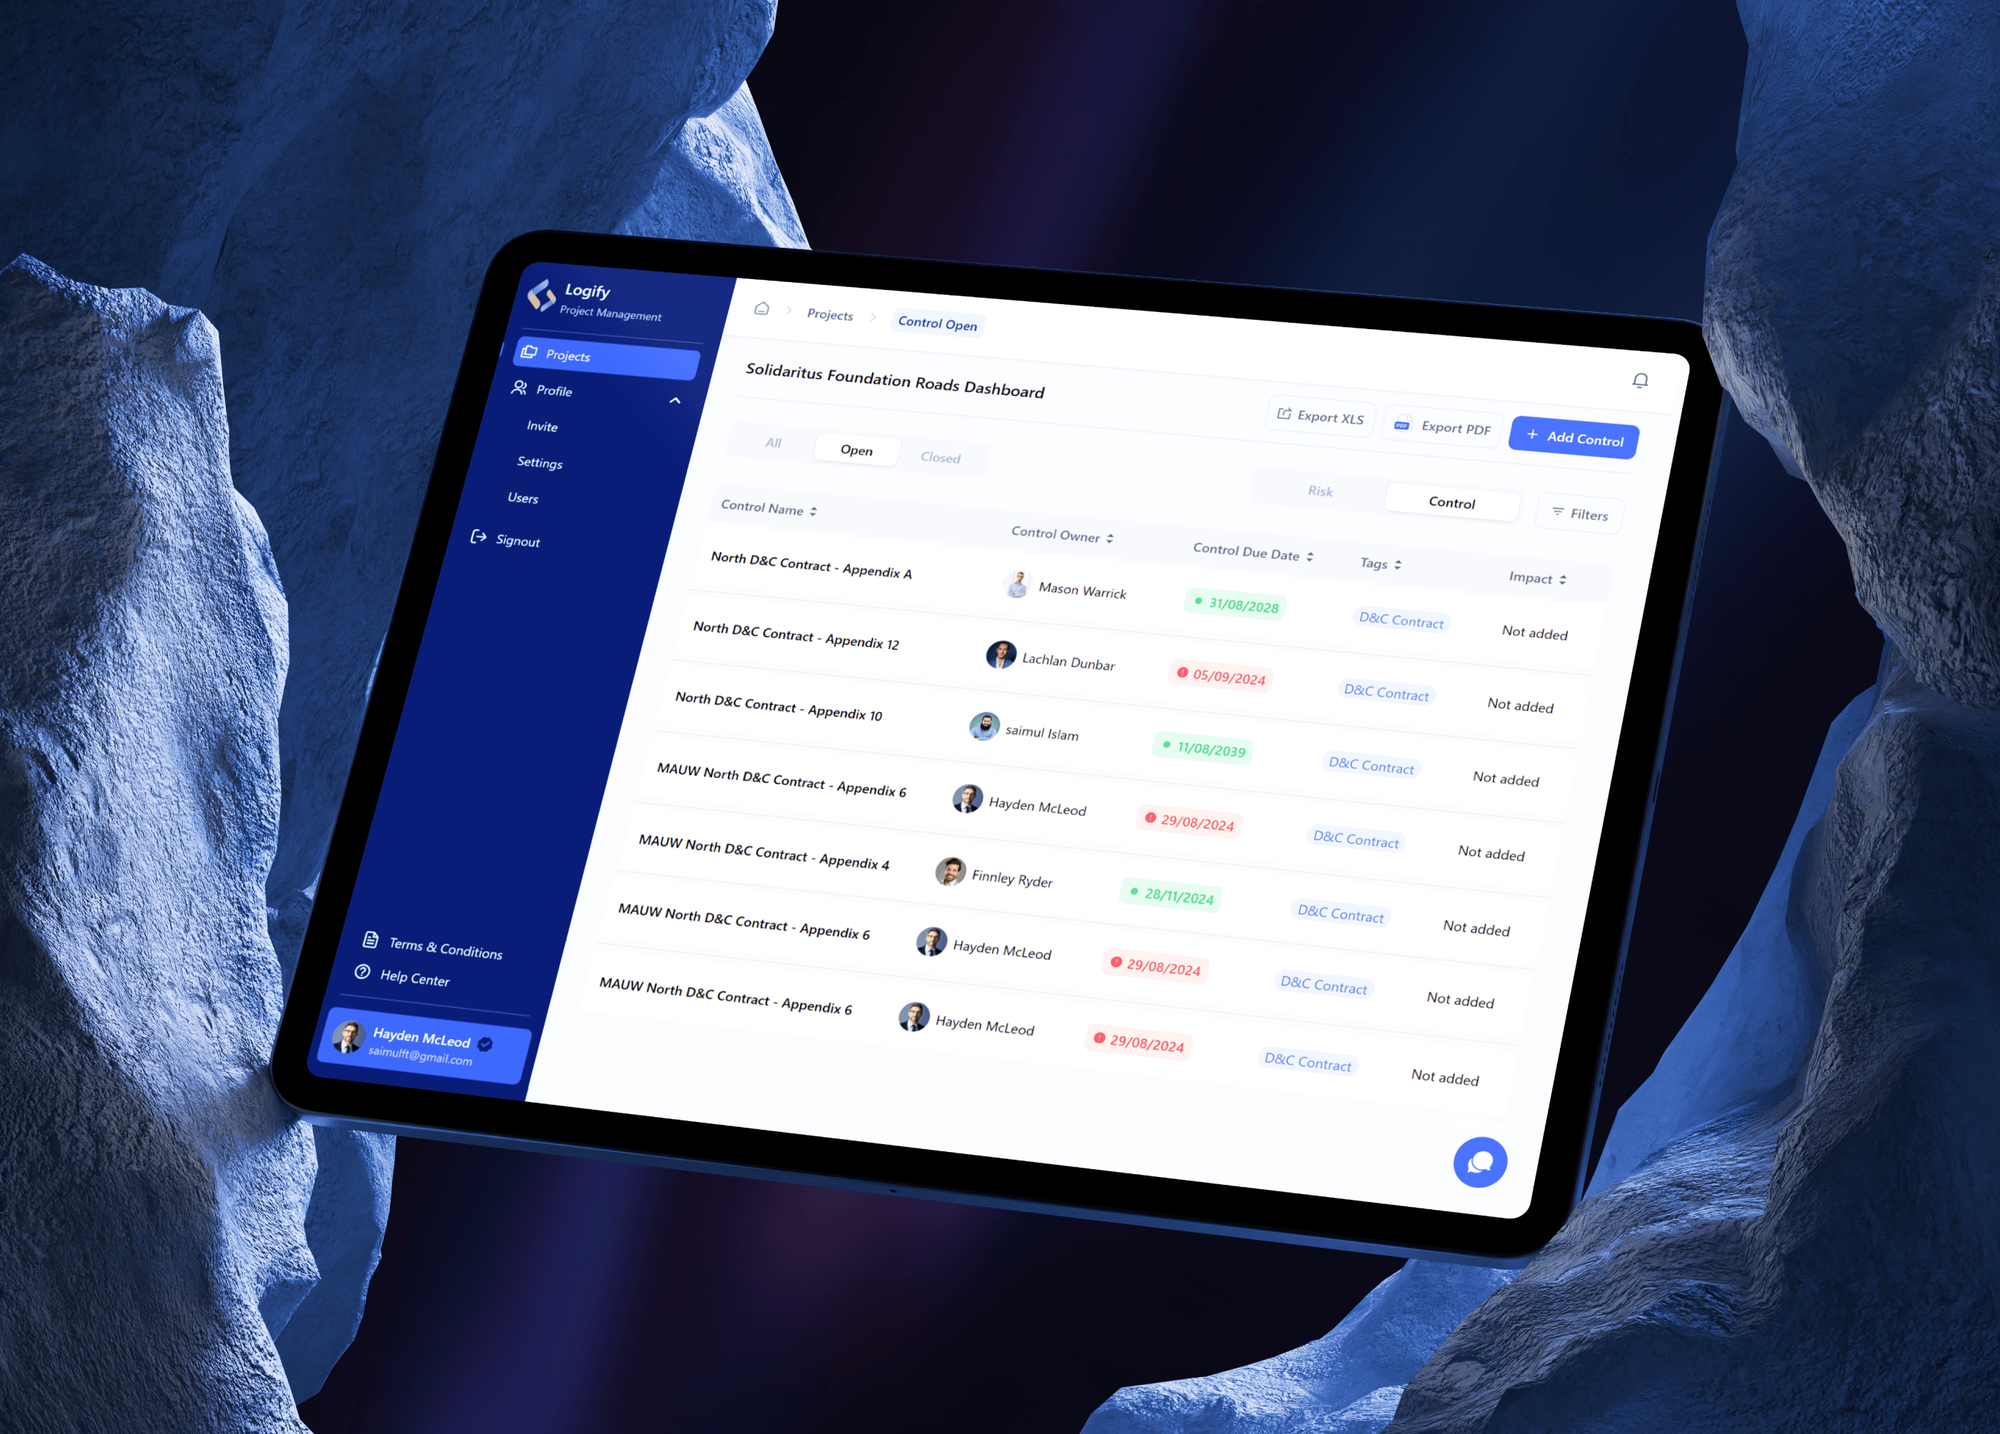
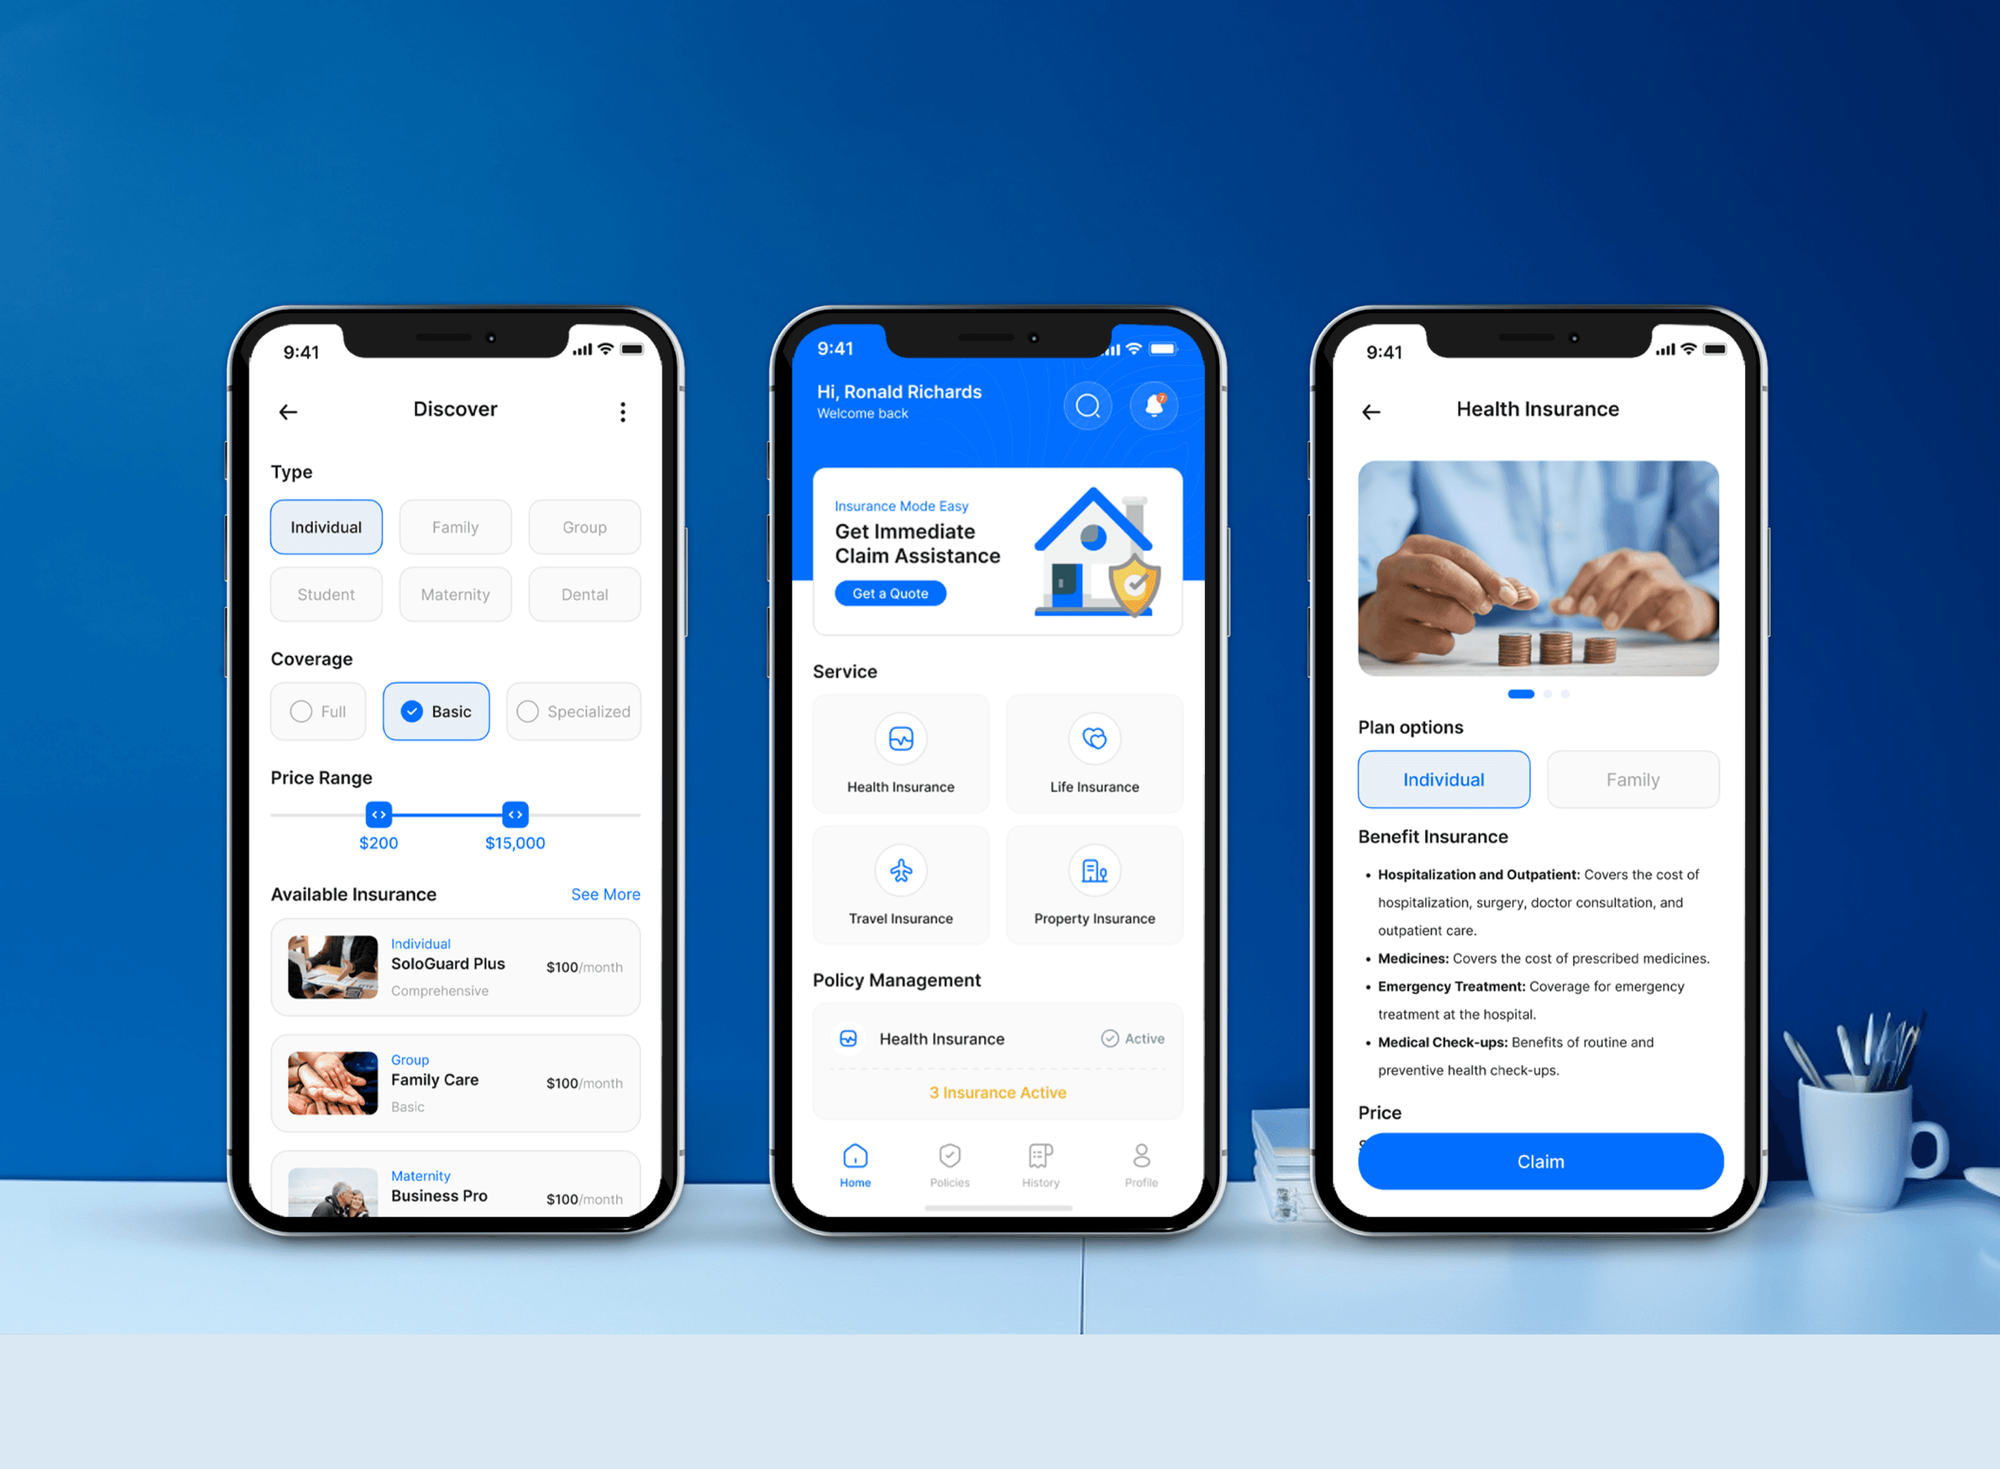
Projects We've Built
SaaS platforms, payroll systems, and apps we designed and built for growing companies. Products like these are what a security lead's policies and questionnaires describe.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Leading someone else's security program takes judgment and restraint. These habits keep your lead useful to your engineers and credible with your customers.
You work with one named person, not whoever is free that week. Context builds over time, so the advice gets sharper instead of starting over.
Each monthly report lists how your plan's hours were spent and on what. You know what leadership time bought before you renew.
Your lead can read a cloud console and a pull request, not just a policy. Recommendations come with steps your engineers can actually ship.
If your workload outgrows a part-time lead, we'll say so and help you write the full-time CISO job description. Part-time leadership should be a bridge, not a trap.
We keep one approved answer library and update it as controls change. Sales stops waiting on security, and answers stay consistent across customers.
Policies, registers, and the answer library live in your workspace from day one. If you end the plan, everything stays with your team.
Overview
DeveloperLook offers vCISO services for SaaS and service companies that need security leadership without a full-time hire. A named lead owns your risk register, roadmap, policies, incident plan, and customer questionnaires. Plans start at $950 per month for up to 6 hours, the first 30 days produce a baseline and plan, and every hour is reported.
DEVELOPERLOOK
Project facts · vCISO Services
Reviewed 6 Oct 2026 by Saimul Islam
Good fit
SaaS startups selling to enterprises
Your first enterprise customer sent a security questionnaire and asked about SOC 2, and nobody on your team owns security full-time.
Firms covered by the FTC Safeguards Rule
You run a tax practice, lender, or auto dealership, and the FTC Safeguards Rule requires a Qualified Individual to oversee your security program.
Companies between security leaders
Your security lead just left, and you need someone to keep audits, policies, and vendor reviews moving while you hire.
Boards asking for security reporting
Your board or investors want a regular update on risk, and you'd rather hear it from a security leader than piece it together yourself.
IT providers adding security leadership
Your managed IT business keeps getting asked for a virtual CISO, and you want a partner who can fill that role under your brand.
Not a fit
Budget under $950 a month
Your budget is under $950 a month, or you only need a plan once. Our Cybersecurity Consulting Services page delivers a one-time roadmap your team can run.
Hands-on engineering needed
You need configuration work, such as MFA rollouts and cloud fixes, more than leadership. Our Cybersecurity Services page covers that hands-on work.
Full-time security workload
Your company has frequent incidents, many products, or regulators who expect a full-time executive. At that point, hiring a full-time CISO is the better investment.
App testing only
You only need your app tested for a customer's security review. Our Web Application Penetration Testing Services page covers that without a monthly plan.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are monthly starting points in USD. Your plan depends on your audit goals, questionnaire volume, and team size, and you get a fixed proposal after a free fit call.
For startups that need a named security lead for up to 6 hours a month.
$950/month
For companies preparing for SOC 2 or ISO/IEC 27001 that need a program owner.
$1,650/month
For teams with active audits, several frameworks, or a board that expects regular reporting.
$2,400/month
For Agencies
You own the client relationship. Our lead runs your client's security program under your brand, joins their meetings as part of your team, and keeps every document in your templates. You add security leadership without a senior hire.
White label: your client only ever sees your brand
Share the client's audits, questionnaires, and the security questions they keep asking.
You get a named lead, a plan with hours, and a fixed monthly fee.
Our lead runs the client's program and reports through you each month.
Your clients meet our lead as a member of your team.
Each client plan has fixed hours and a fixed monthly fee.
Leads who read cloud consoles and code, not only policies.
Add clients one at a time as your contracts grow.
The Right Technology for Your Project
Your lead works inside the tools your team already uses to track work, manage accounts and devices, and run your cloud and code.
 Google Sheets
 AWS
 Slack
 Loom
FAQ
Straight answers on what a vCISO does, what it costs, how it differs from a full-time CISO, and how to hire one.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
A vCISO, or virtual chief information security officer, is a part-time security leader you contract instead of hiring full-time. The role sets security strategy, owns policies and risk decisions, and represents security to customers, auditors, and your board. Most work a set number of hours each month, remotely, alongside your engineers and IT provider.
A vCISO runs your security program: assessing risk, setting priorities, writing policies, and making sure the work gets done. Month to month, that includes vendor reviews, customer questionnaires, audit preparation, and progress reports to leadership. During an incident, they coordinate the response plan while engineers or a response firm handle the technical cleanup.
There's no reliable single average, because vCISO cost depends on monthly hours, the frameworks involved, and how much hands-on work is included. Our vCISO pricing is published: $950 per month for up to 6 hours and $1,650 per month for up to 10. Up to 16 hours with audit support is $2,400 per month. Compare offers on hours and deliverables, not titles.
A vCISO works part-time under contract, while a traditional CISO is a full-time executive on your payroll. Both own strategy, policies, and risk decisions. The difference is capacity. A full-time CISO can build a security team and handle constant incidents, while the part-time role suits companies whose workload fits into set monthly hours.
The main benefits are senior security leadership for a fraction of a full-time salary and an accountable owner from the first month. You also get experience drawn from many environments, a faster start than an executive search, and one person answering audits and questionnaires. The trade-off is fewer hours, so a good one prioritizes hard.
You need a vCISO when security decisions, audits, or customer questionnaires keep landing on people with other full-time jobs. Common triggers include a first enterprise customer, a SOC 2 or ISO/IEC 27001 goal, the FTC Safeguards Rule's Qualified Individual requirement, or a security lead who just resigned. If none apply, a one-time roadmap may be enough.
Start by writing down what needs covering: frameworks, questionnaires, board reporting, and hours per month. Then interview several vCISO companies, meet the actual person who would lead your program, and ask for a sample policy and monthly report. Agree on hours, deliverables, and how documents stay with you if the plan ends.
Pick a security leader who has worked with startups selling to larger customers, because your first milestones will be questionnaires and SOC 2. Ask how they'd spend the first 90 days and which policies they'd write first. Check that they can work with your engineers inside GitHub and your cloud console. Skip anyone who pushes a heavy framework your stage doesn't need.
Choose a vCISO who ties every security goal to a business goal you already track, such as closing enterprise deals or passing an audit. They should re-rank risks as your company changes and report in terms your board understands. A good one also plans for the day you hire a full-time CISO. Continuity matters, so keep the same named lead.
The best virtual CISO service is one with a named lead, published hours, and deliverables you can check every month. Some vCISO solutions are software dashboards with a few advisory hours attached, which suits teams with engineers to do the work. Ours pairs a lead with engineers you can bring in for fixes, quoted separately.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.