
Website and app data check
Every form, cookie, and tag tested, so you know exactly what personal data your site collects.

For Singapore and Malaysia businesses with websites, apps, and CRMs: forms checked, notices fixed, data mapped, and a breach plan your DPO can run. From $650.
10/10
Obligations in force covered
3days
PDPC breach deadline planned
How your project runs
Teams we have built for:














The Problem
It shows up when a customer asks what you hold about them, someone emails the wrong spreadsheet, or a client's procurement team asks who your DPO is.
01 · Forms
Enquiry forms ask for NRIC numbers sales never uses.
Fields are cut to what each purpose needs, with a notice shown before submitting.
02 · Consent
Ad tags fire before visitors see any notice.
Tags wait for consent where it's needed, and notices say plainly what happens next.
03 · Retention
Old leads and CVs stay in spreadsheets indefinitely.
A retention schedule sets deletion dates, and the deletion steps are written down.
04 · Breaches
Nobody knows when the regulator must be notified.
A breach plan assigns roles and assessment steps against the notification deadlines.
Your enquiry form asks for full name, mobile number, NRIC number, and date of birth, though sales only needs a name and a number. Analytics and ad tags fire before anyone sees a notice. Leads sit in a CRM, a shared spreadsheet, and an agency's inbox. Nobody knows how long old records are kept. When a customer asks what you hold about them, it takes a week to find out. Then a laptop goes missing, and nobody knows whether the regulator must be told.
We start with what your website and app actually collect: every form, field, cookie, and tag. Then we trace where that data goes and write down why you hold it and for how long. Notices, consent wording, and retention steps get fixed in the tools themselves. You end up with a breach plan and a DPO who knows the deadlines, not a policy PDF nobody opens.
Every form tested
We submit each form and record which fields, cookies, and tags capture personal data.
A breach plan on the clock
Roles, assessment steps, and templates written around the regulator's notification deadlines.
Your DPO, supported
A named DPO with published contact details, a role description, and a review calendar.
Our PDPA Compliance Services in Singapore Process
You approve the scope, every change to your forms and notices, and the final policy before anything goes live or reaches your staff.
We ask what personal data you collect, where customers give it, and which systems keep it. You get a written scope and a fixed price. If PDPC's free guides already cover your setup, we'll tell you before we quote.
What's Included
Each engagement covers a website and app check, a personal data inventory, notices and consent, a checklist of your obligations, a breach plan, and DPO support.
Compare Options
A template pack is the cheapest start, and an outsourced DPO service takes the officer role off your hands. Neither checks what your website collects. Here is where each fits.
| Feature | DeveloperLookBest fit | Template pack | DPO service |
|---|---|---|---|
| Website check | Forms, cookies, and tags tested | Not included | Usually not included |
| Data inventory | Traced across your real systems | Blank template | Questionnaire you fill in |
| Notices and consent | Rewritten and fixed in your forms | Generic sample wording | Reviewed on request |
| NRIC handling | Fields found and removed | General guidance | Advice when asked |
| Breach plan | Written for your systems | Template plan | Plan plus PDPC contact |
| DPO role | Support for your named DPO | Not included | Yes, the role itself |
| Support | 30 days after handover | None | Ongoing retainer |
| Cost | Fixed price from $650 | Lowest upfront cost | Monthly fee |
Projects We've Built
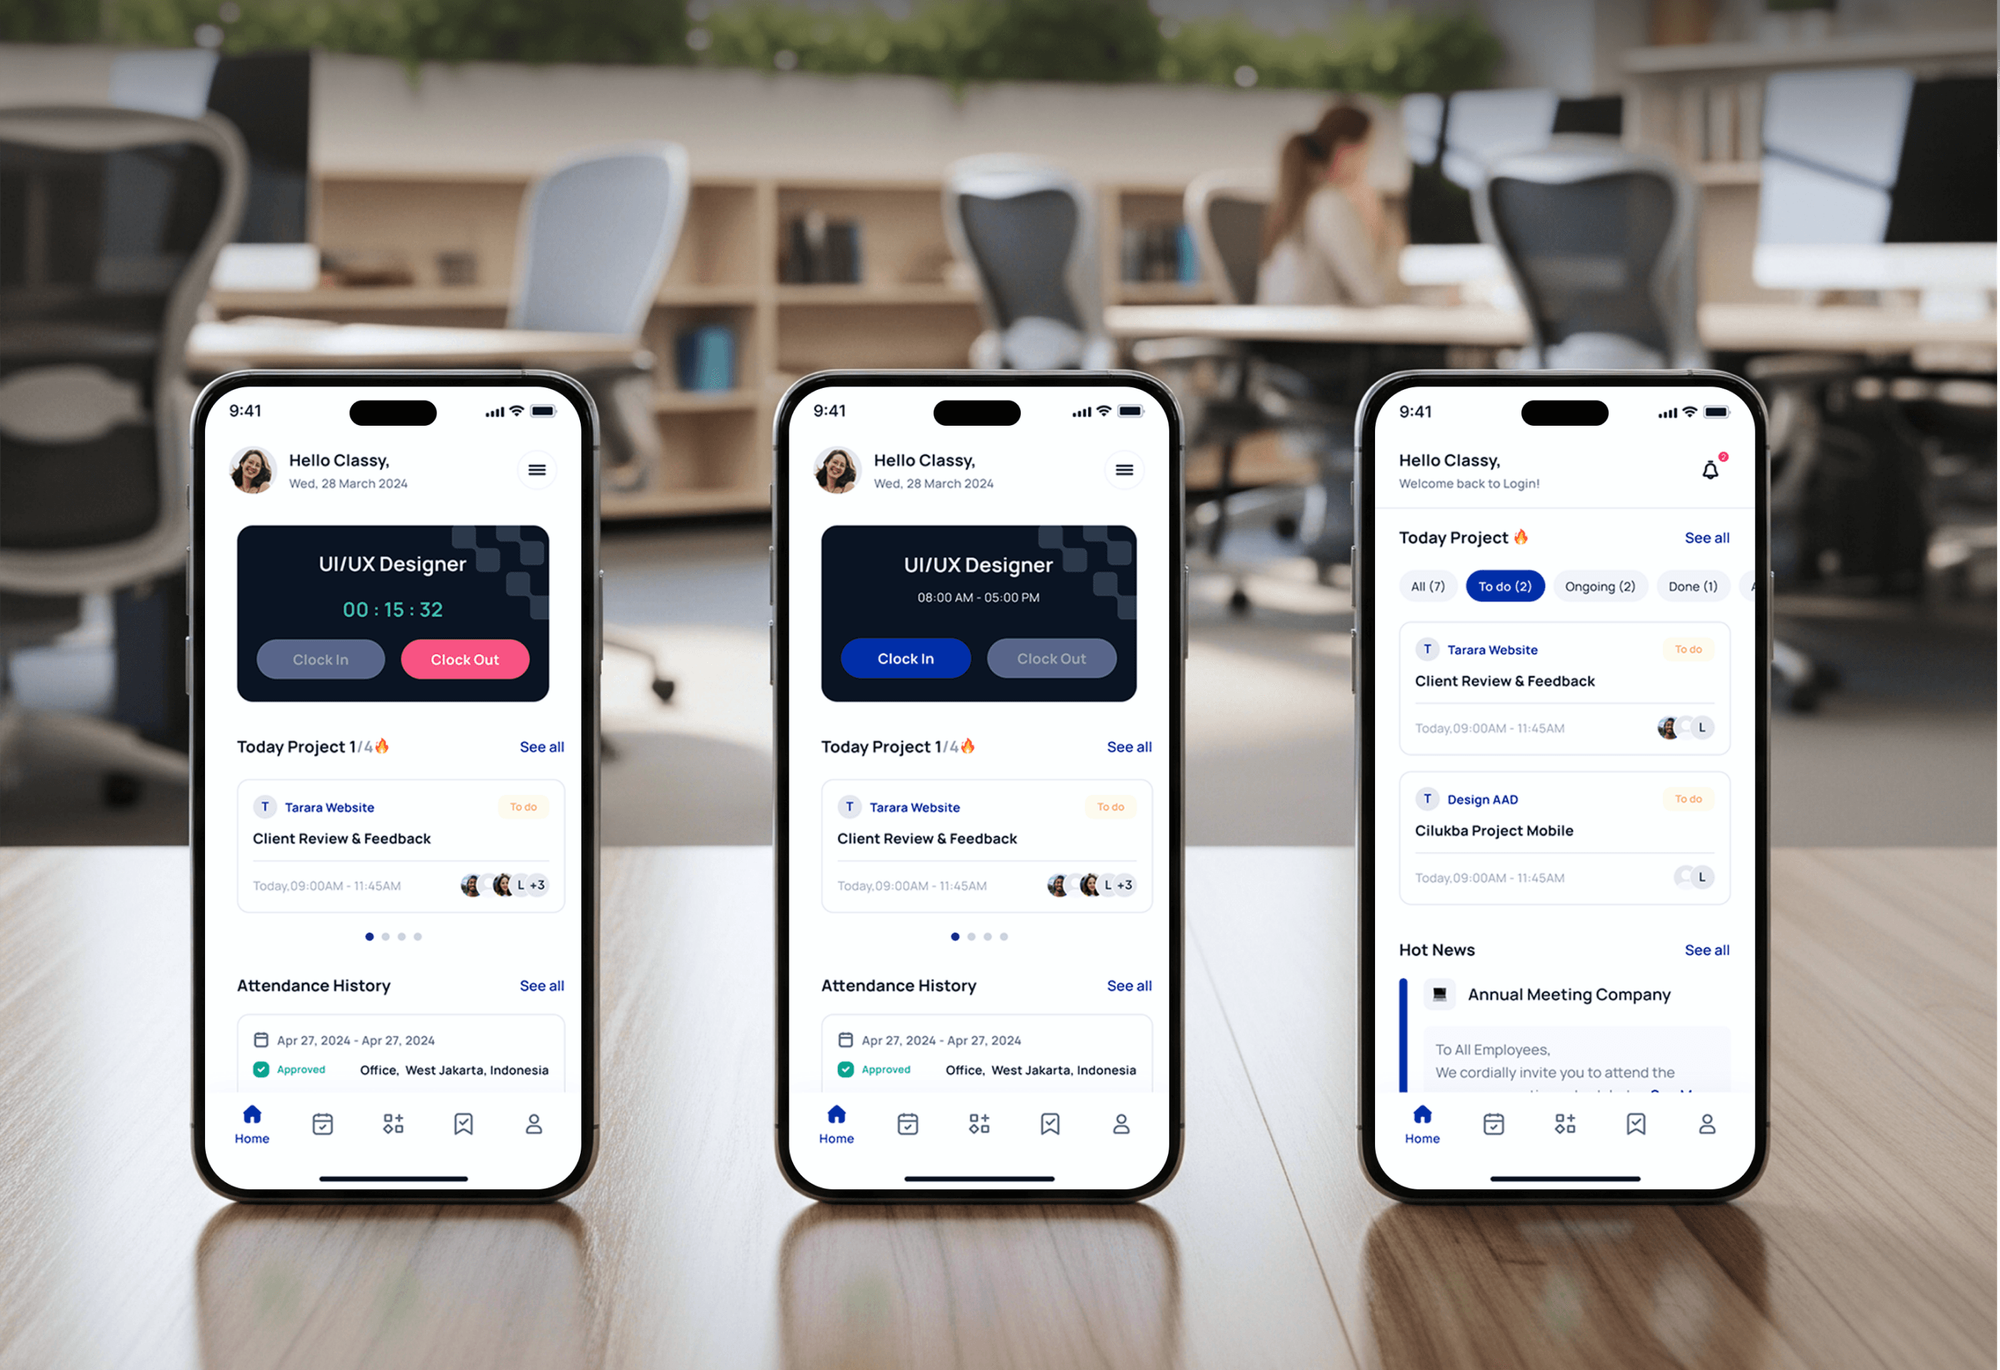
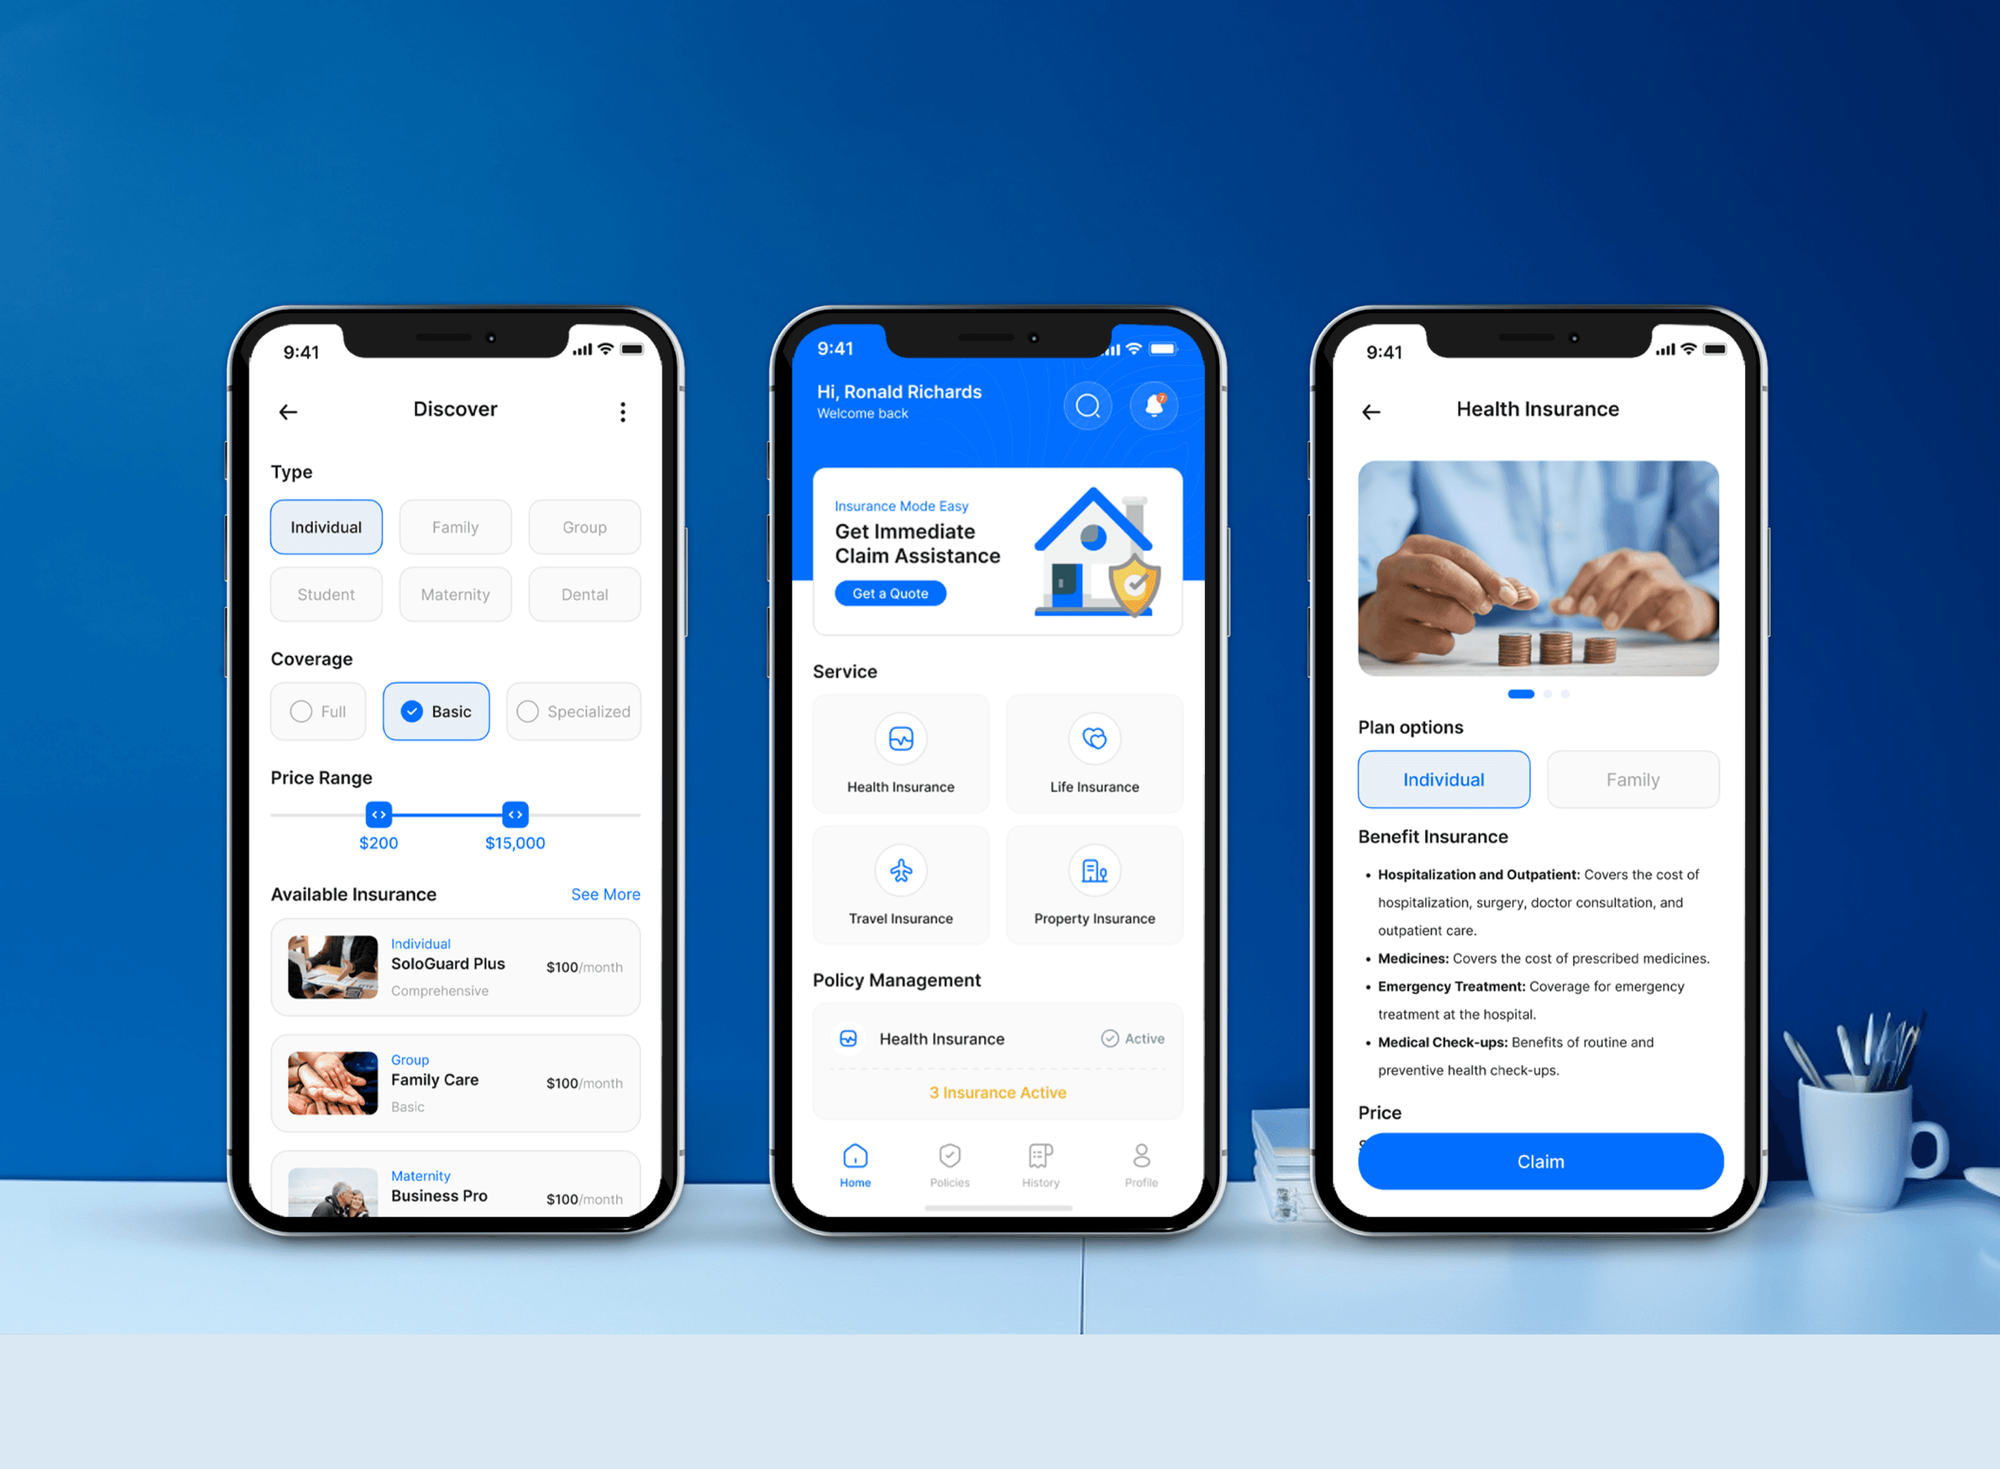
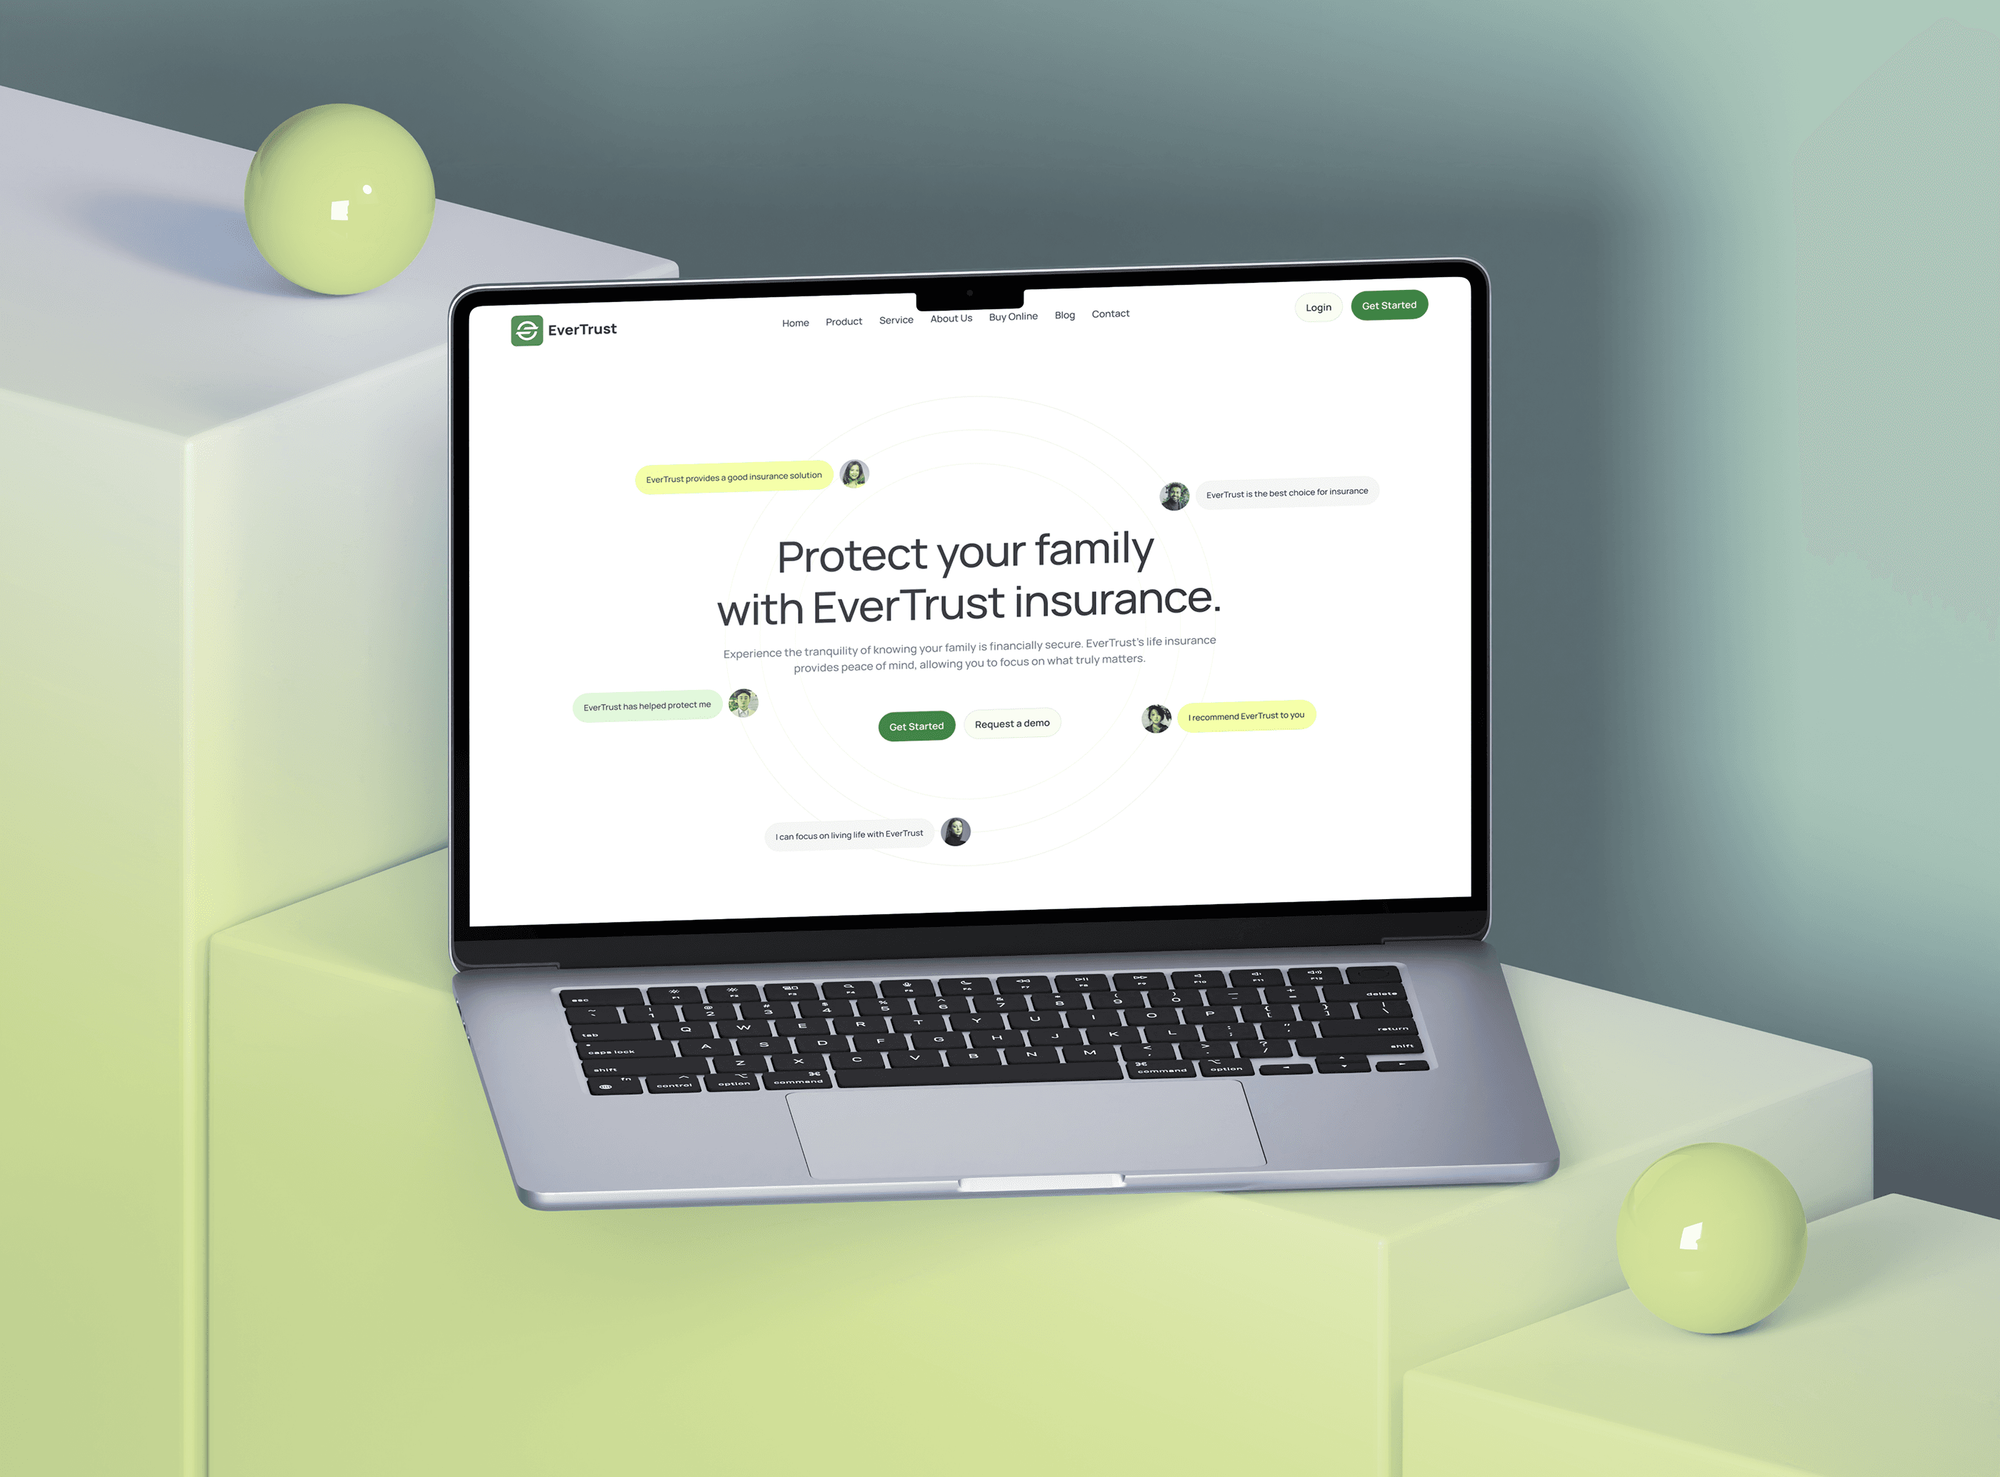
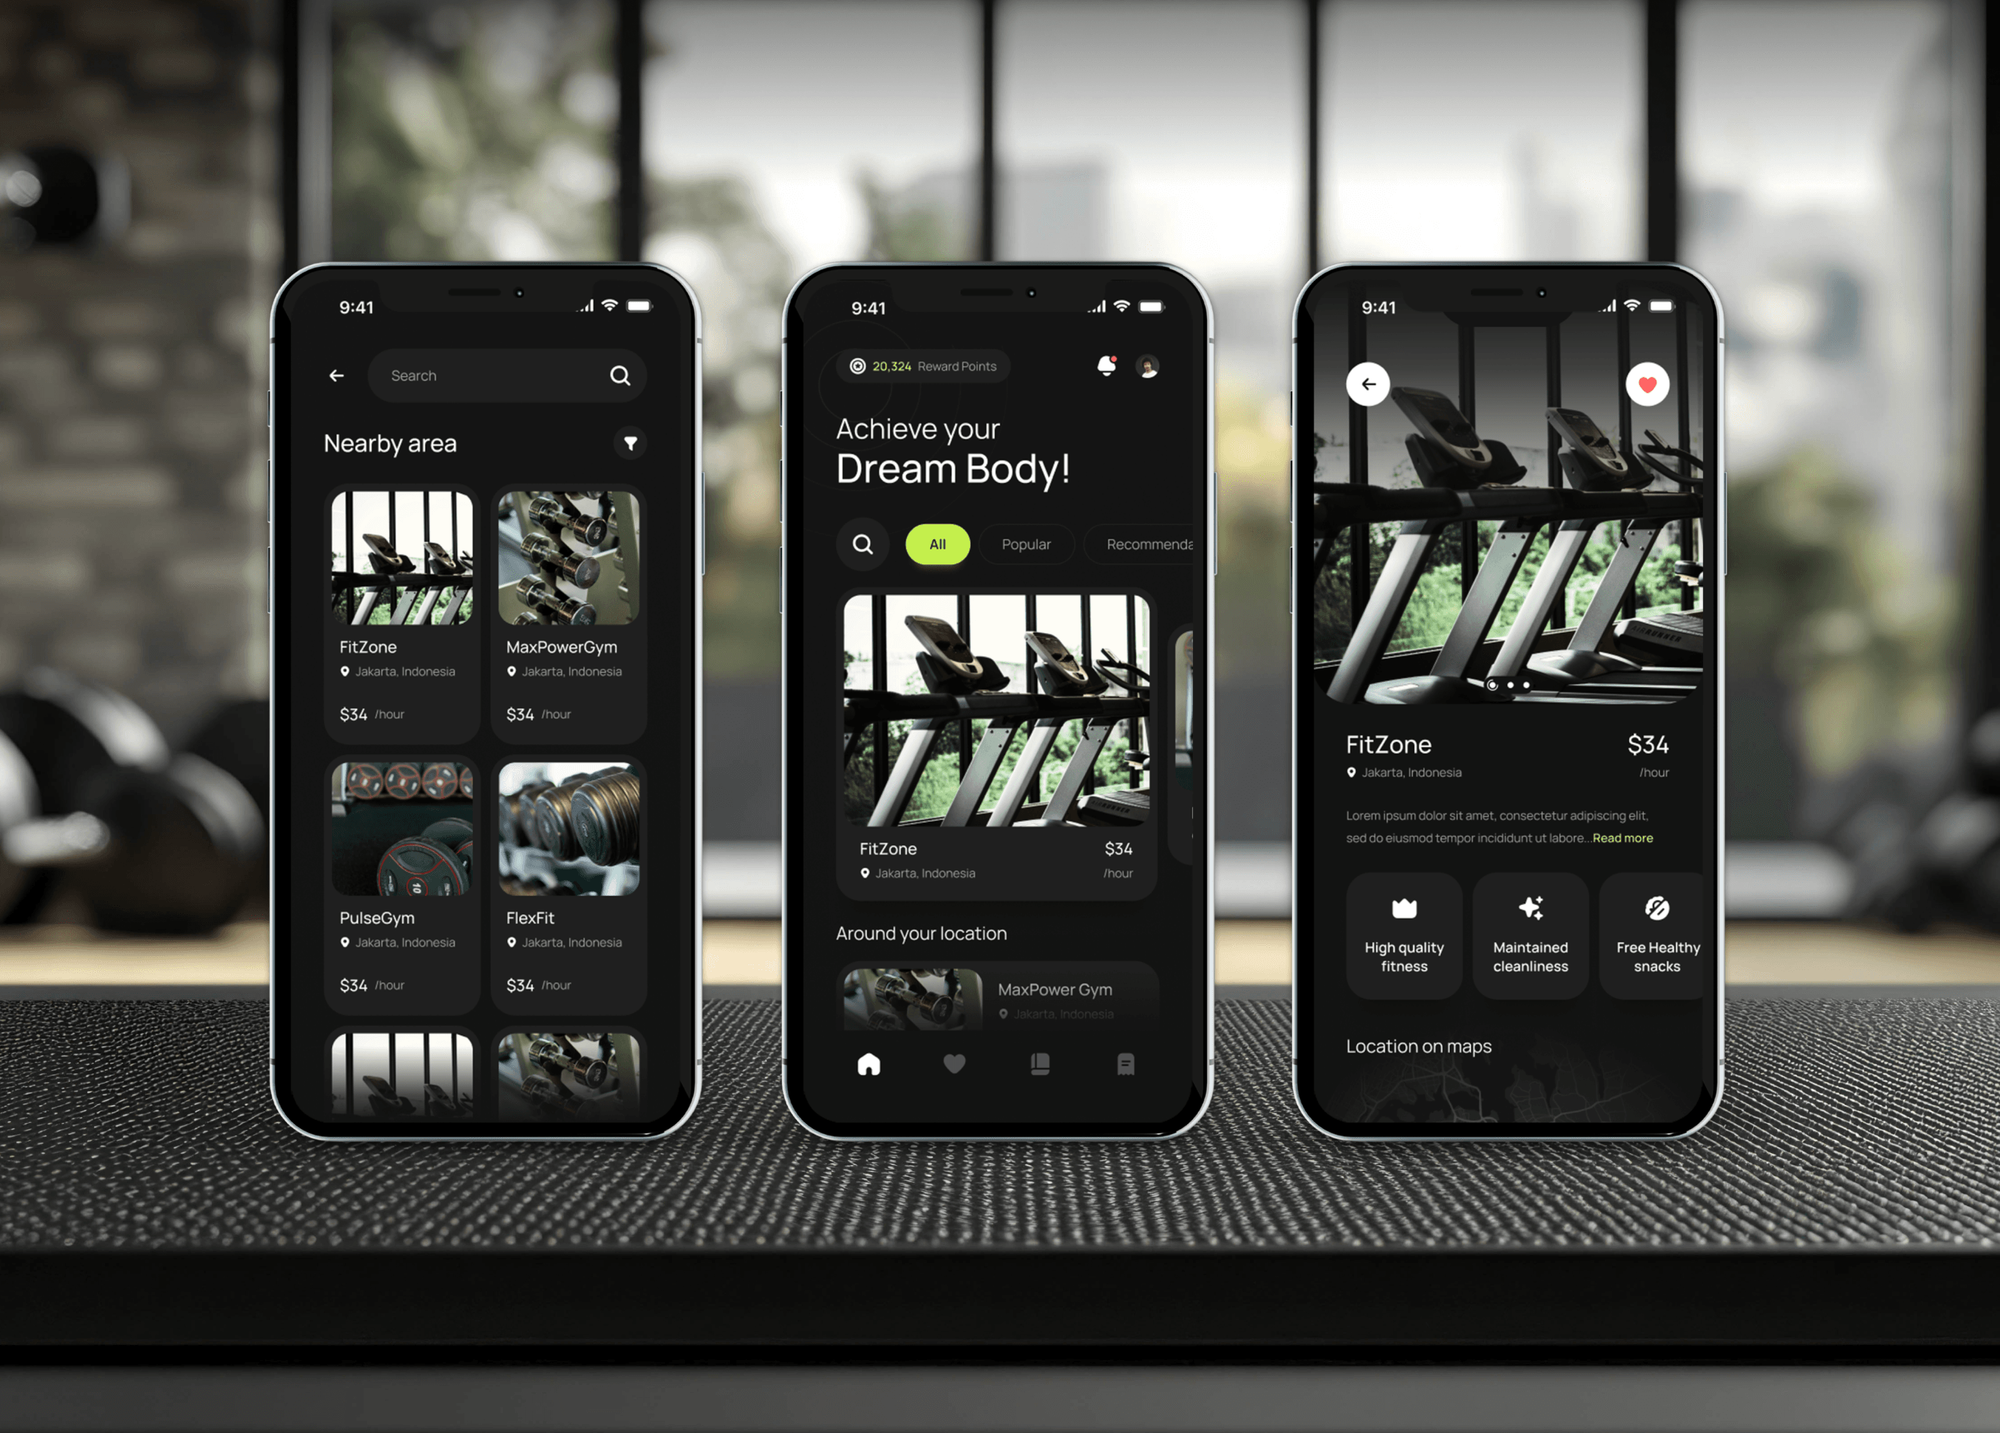
Insurance, HR, and membership apps and websites we designed and built. Each one collects names, contact details, and account data that data protection law covers.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Checking personal data means seeing where your shortcuts are. These habits keep customer records safe while we look, and keep the advice practical rather than legalistic.
Every form check uses test entries, never real customer details. For the inventory we record fields and locations, not the records themselves.
We explain what the PDPA guidelines ask in plain English and say when a question needs a lawyer. Legal conclusions stay with your counsel.
We suggest dropping fields like NRIC numbers before we secure them. Data you never collect can't leak, and it needs no retention rule.
Notices are written in short, plain sentences your customers understand. A notice nobody can follow doesn't protect you or them.
On the top plan we walk your team through a mock breach. The first hours of a real one shouldn't be the first time anyone reads the plan.
Inventories, policies, and the breach plan live in your storage. At handover we close our accounts and give you the list of every one we used.
Overview
DeveloperLook provides PDPA compliance services for businesses in Singapore and Malaysia, starting with what your website and apps collect. We test forms and tags, map personal data, fix notices and consent, set retention, and write a breach plan for your DPO. Projects start at $650 and take 1 to 8 weeks, with no legal opinions dressed up as consulting.
DEVELOPERLOOK
Project facts · PDPA Compliance Services in Singapore
Reviewed 22 Oct 2026 by Saimul Islam
Good fit
Singapore SMEs with online enquiry forms
Your WordPress or Webflow site collects names, phone numbers, and NRIC details through enquiry forms, and nobody has checked them against the PDPA obligations.
Apps and online stores with customer accounts
Your Shopify store or app holds customer accounts and order history, and you need PDPA compliance built into sign-up, consent, and deletion.
Companies without a named DPO
Your company has no named data protection officer, and you need DPO Singapore support without hiring someone full time.
Businesses serving Malaysia too
Your team serves customers in Singapore and Malaysia from one HubSpot or Salesforce CRM, and you need both countries' rules mapped to one process.
Agencies building sites for local clients
Your clients ask whether the websites you build follow the PDPA Act, and you need a partner who checks them under your brand.
Not a fit
Need legal advice
You need a legal opinion on a PDPC investigation or a contract dispute. A Singapore data protection lawyer is the right first call, and we handle the technical and process work.
Cookie banner only
You only need a cookie banner and consent mode for Google tags. Our privacy compliance and consent management service covers that from $600.
Buyers want SOC 2
Your enterprise buyers ask for a SOC 2 report rather than local data protection documents. Our SOC 2 compliance services page covers the controls and evidence auditors test.
Budget under $650
Your budget is under $650 and you run a simple brochure site with one contact form. PDPC's free guides and starter kit are a sensible first step.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your forms, your data systems, and whether Malaysia is in scope, and you get a fixed proposal after a free scoping call.
For small businesses that need their website and forms checked against Singapore's rules.
$650one-time, USD
For businesses that need a data inventory, policy, retention schedule, and breach plan.
$1,450one-time, USD
For organizations that want vendor checks, Malaysia coverage, and support for their DPO.
$2,950one-time, USD
For Agencies
You own the client relationship. We supply the form checks, data inventories, notices, and breach plans under your brand, and join client calls only when you ask. Your clients get practical data protection work without you hiring a specialist.
White label: your client only ever sees your brand
Send the client's website, systems, and the question that started the request.
You get a written scope, a form list, and a fixed price per client.
We test the forms, fix notices, and hand over policies in your template.
You present the findings while we work quietly under your brand.
Forms, tags, and CRMs checked by people who build them every week.
Policies and notices delivered in your format, ready for client review.
Check one client's website or run yearly reviews across your client list.
The Right Technology for Your Project
We work inside the website platforms, tag managers, and CRMs where personal data is collected, so fixes land where customers type their details.
 WordPress
 Shopify
 Webflow
 Salesforce
 Google Sheets
FAQ
Straight answers on cost, timing, what counts as personal data, phone numbers, DPOs, and Malaysia.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our work starts at $650 for a check of one website's forms, cookies, and notices. A full setup with a data inventory, policy, retention schedule, and breach plan starts at $1,450. The $2,950 program adds vendor and transfer reviews, Malaysia coverage, a mock breach, and 3 months of support for your DPO.
A website and forms check takes about 1 week. A full setup with inventory, policy, retention schedule, and breach plan takes 3 to 4 weeks. The program with vendor reviews and Malaysia coverage takes 5 to 8 weeks. Slow replies from vendors about where they store data are the usual delay.
PDPA is the Personal Data Protection Act 2012, the data protection act Singapore organizations follow when they collect, use, or disclose personal data. The Personal Data Protection Commission (PDPC) administers and enforces it. The same act carries the Do Not Call rules for marketing messages to Singapore phone numbers.
Personal data is data, true or not, about an individual who can be identified from it alone or with other information you can likely access. Paper and electronic records both count. Business contact information, such as a work email given for business purposes, falls outside the main data protection provisions.
Common examples include a full name with an NRIC number, a photo of a face, a mobile number, a home address, and a personal email. Account IDs and order histories count too once they're linked to a person. PDPC's NRIC guidelines limit collecting NRIC numbers, and PDPC is phasing out their use to authenticate people.
A detail constitutes personal data when it can identify someone once combined with other information you hold or can likely get. A first name alone usually doesn't, but a first name plus a workplace and job title often does. That's why our inventory looks at whole datasets, not single fields.
A phone number is personal data when it can identify an individual, alone or with other details you hold. A number given purely as business contact information is excluded from most obligations. Separately, the Do Not Call provisions limit marketing calls and messages to Singapore numbers, whoever holds them.
You become PDPA compliant by naming a DPO, mapping the personal data you hold, and setting policies that meet each obligation. Then fix notices and consent in your forms, set retention periods, protect the data, and prepare a breach plan. Notify PDPC within 3 calendar days once you assess a breach as notifiable.
Yes, every organization covered by the law must designate at least one person responsible for compliance and publish that person's business contact details. The DPO can be an employee or an outsourced provider, but the organization stays responsible. Our top plan includes 3 months of desk support while your officer settles in.
Malaysia has its own Personal Data Protection Act 2010, separate from Singapore's law, and a 2024 amendment added new duties. Since June 2025, data controllers must notify the Commissioner of breaches within 72 hours and appoint a DPO once they pass set thresholds. Our top plan maps both countries' duties side by side.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.