
Readiness gap assessment
Your current controls checked against the Trust Services Criteria, with each gap rated by audit risk and effort.

For SaaS and B2B teams whose buyers want a SOC 2 report: controls built in the tools you run, policies you follow, and evidence ready for your auditor. From $1,350.
9/9
Common criteria mapped
1owner
Named for every control
How your project runs
Teams we have built for:














The Problem
It shows up when an enterprise security questionnaire stalls a deal, or when your compliance platform shows a wall of failing tests that nobody owns.
01 · Access
Contractors and former staff still hold admin accounts.
Quarterly access reviews and same-day offboarding, recorded in your identity provider.
02 · Change control
Engineers push straight to production without review.
Branch protection and required reviews in GitHub or GitLab, with tickets linked.
03 · Policies
Template policies describe a company that doesn't exist.
Short policies written around how your team ships, approves, and responds.
04 · Evidence
Nobody knows what the auditor will ask for.
An evidence calendar names the owner, tool, and date for every control.
Your biggest prospect's security team wants a SOC 2 report before legal will sign. Your engineers deploy straight to production, a few contractors still have admin access, and offboarding depends on someone remembering to revoke accounts. You bought an automation platform, connected AWS and GitHub, and it flagged a long list of failing tests. The policies came from templates nobody read. The deal date is fixed, and the audit firm wants evidence you've never collected.
We start with a readiness assessment against the Security criteria and any others your customers need. Then we build the missing controls inside the tools you already run: MFA, access reviews, branch protection, logging, and backups. Policies describe how your team really works. An evidence calendar names who collects what and when, so the auditor tests controls that ran, not controls that were promised.
Controls in your real tools
Branch protection, access reviews, and logging set up in your repos, cloud, and identity provider.
An evidence calendar
Every control gets an owner, a source, and a due date across the observation window.
Ready before fieldwork
Your system description and evidence index are drafted before the CPA firm starts testing.
Our SOC 2 Compliance Services Process
You approve the criteria in scope, every control change, and each policy, so nothing reaches your auditor that your team hasn't seen.
We ask what your customers want (Type 1 or Type 2, and which criteria) and how your product is built and hosted. You get a written scope and a fixed price. If a short security questionnaire would satisfy your buyer, we'll tell you before we quote.
What's Included
Each engagement covers the readiness assessment, a criteria checklist, policies, controls built in your stack, an evidence calendar, and support while your CPA firm audits.
Compare Options
An automation platform collects evidence well, and only a licensed audit firm can issue the report. Neither builds your controls. Here is where each option fits.
| Feature | DeveloperLookBest fit | Automation platform | Audit firm |
|---|---|---|---|
| Gap assessment | Done by engineers with your team | Automated tests and templates | Formal readiness review, extra fee |
| Control fixes | Built in your cloud and code | Flagged, then left to you | Can't build what it audits |
| Policies | Written for how you work | Template library | Reviewed, not written |
| Evidence | Calendar with named owners | Collected automatically | Requested during fieldwork |
| The report | Prepared for your auditor | Not included | Yes, the signed report |
| Speed to start | Within a week of scoping | Same week sign-up | Booked weeks ahead |
| Support | 45 days after handover | Vendor success team | During the audit |
| Cost | Fixed price from $1,350 | Yearly subscription | Separate audit fee |
Projects We've Built
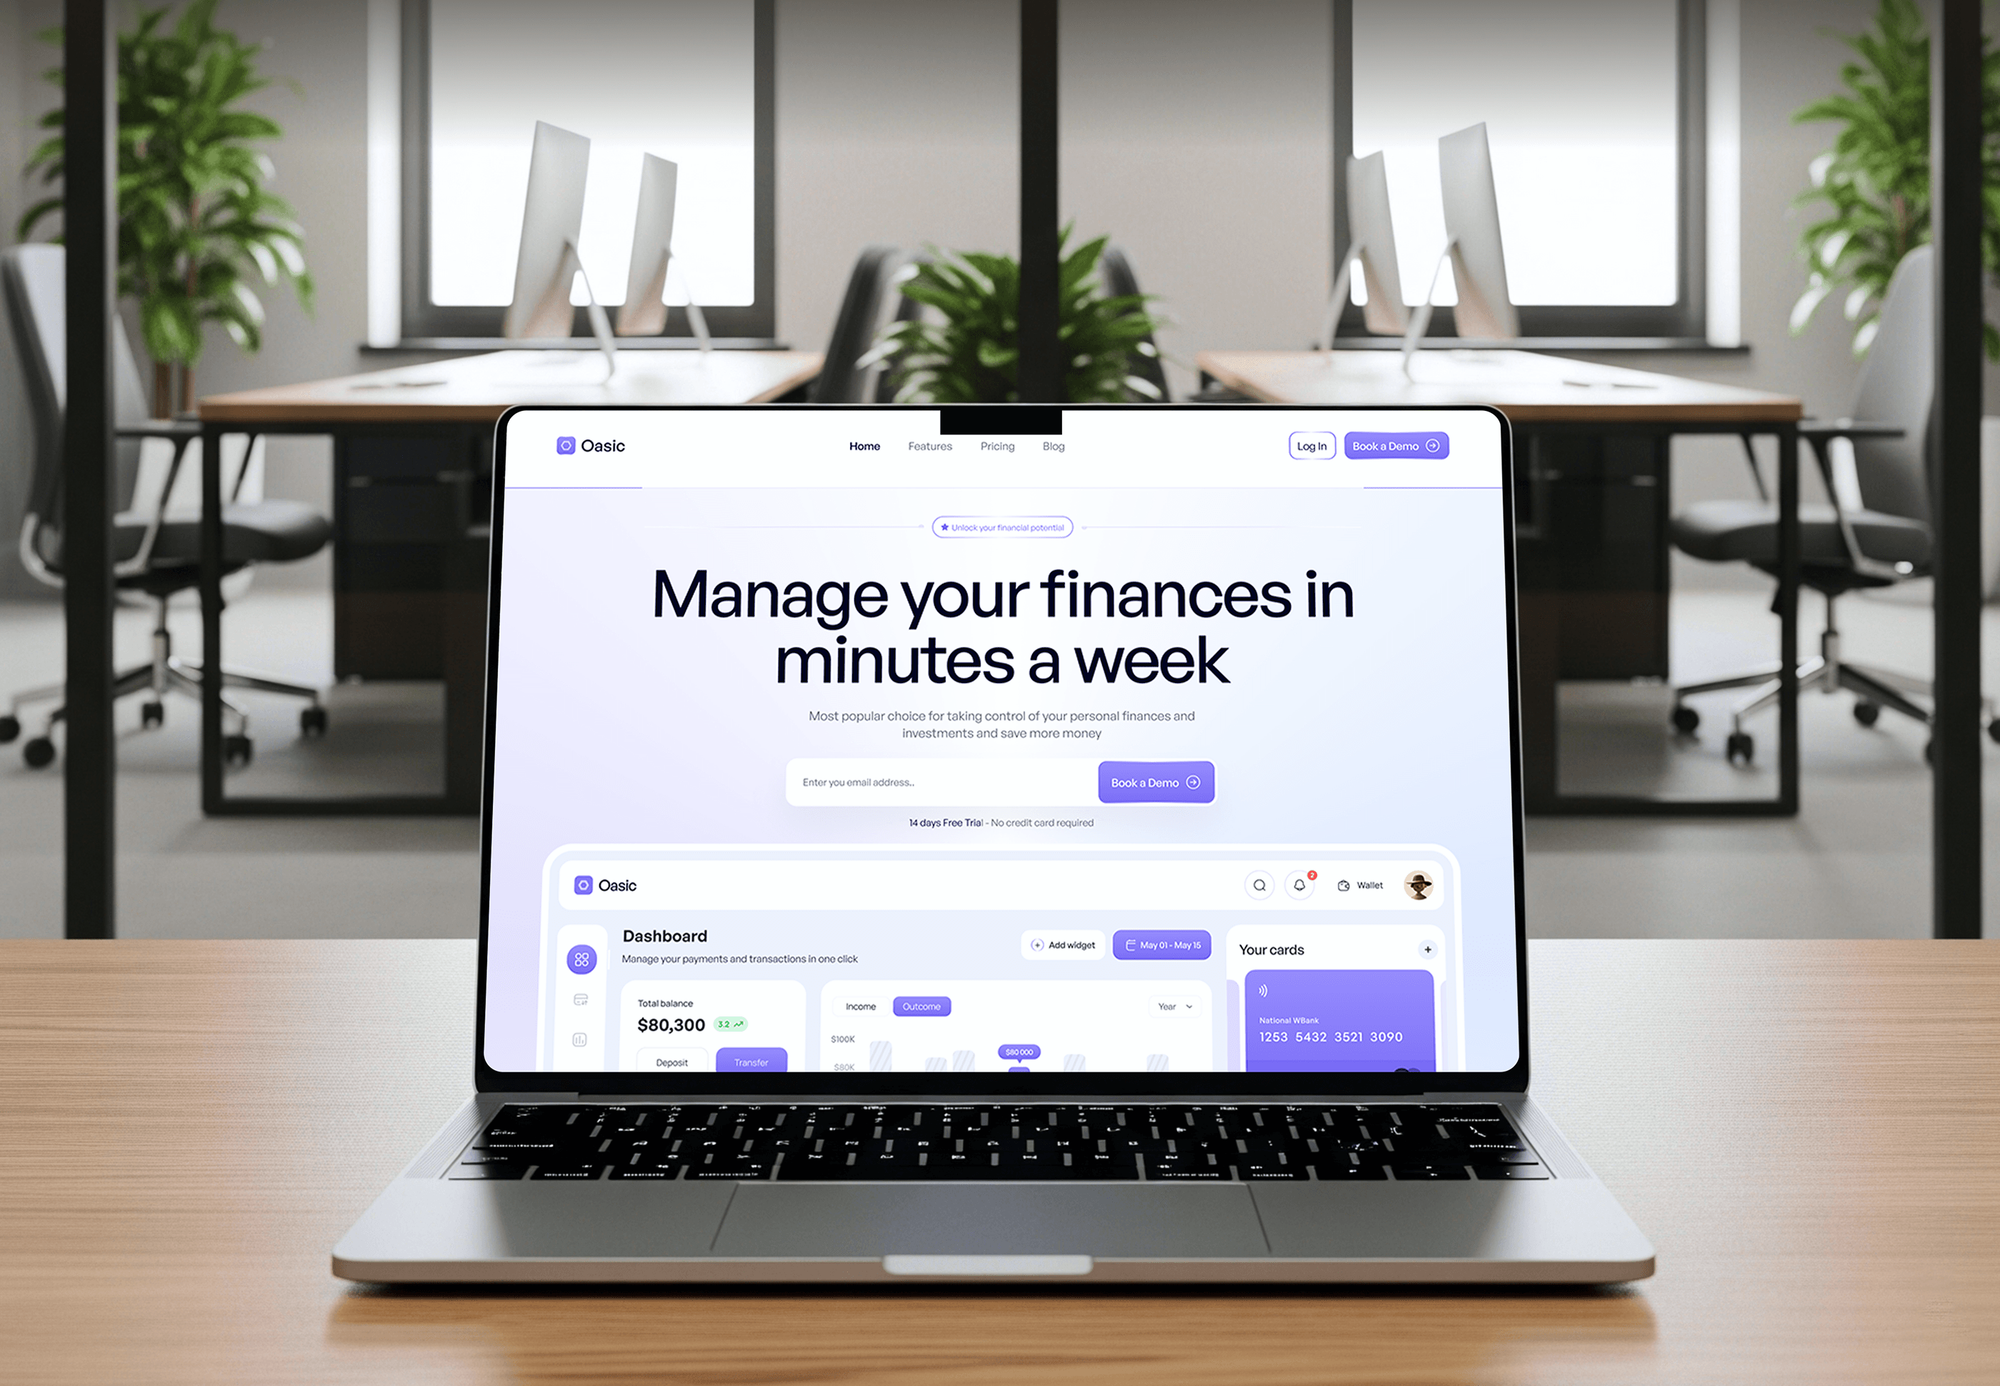
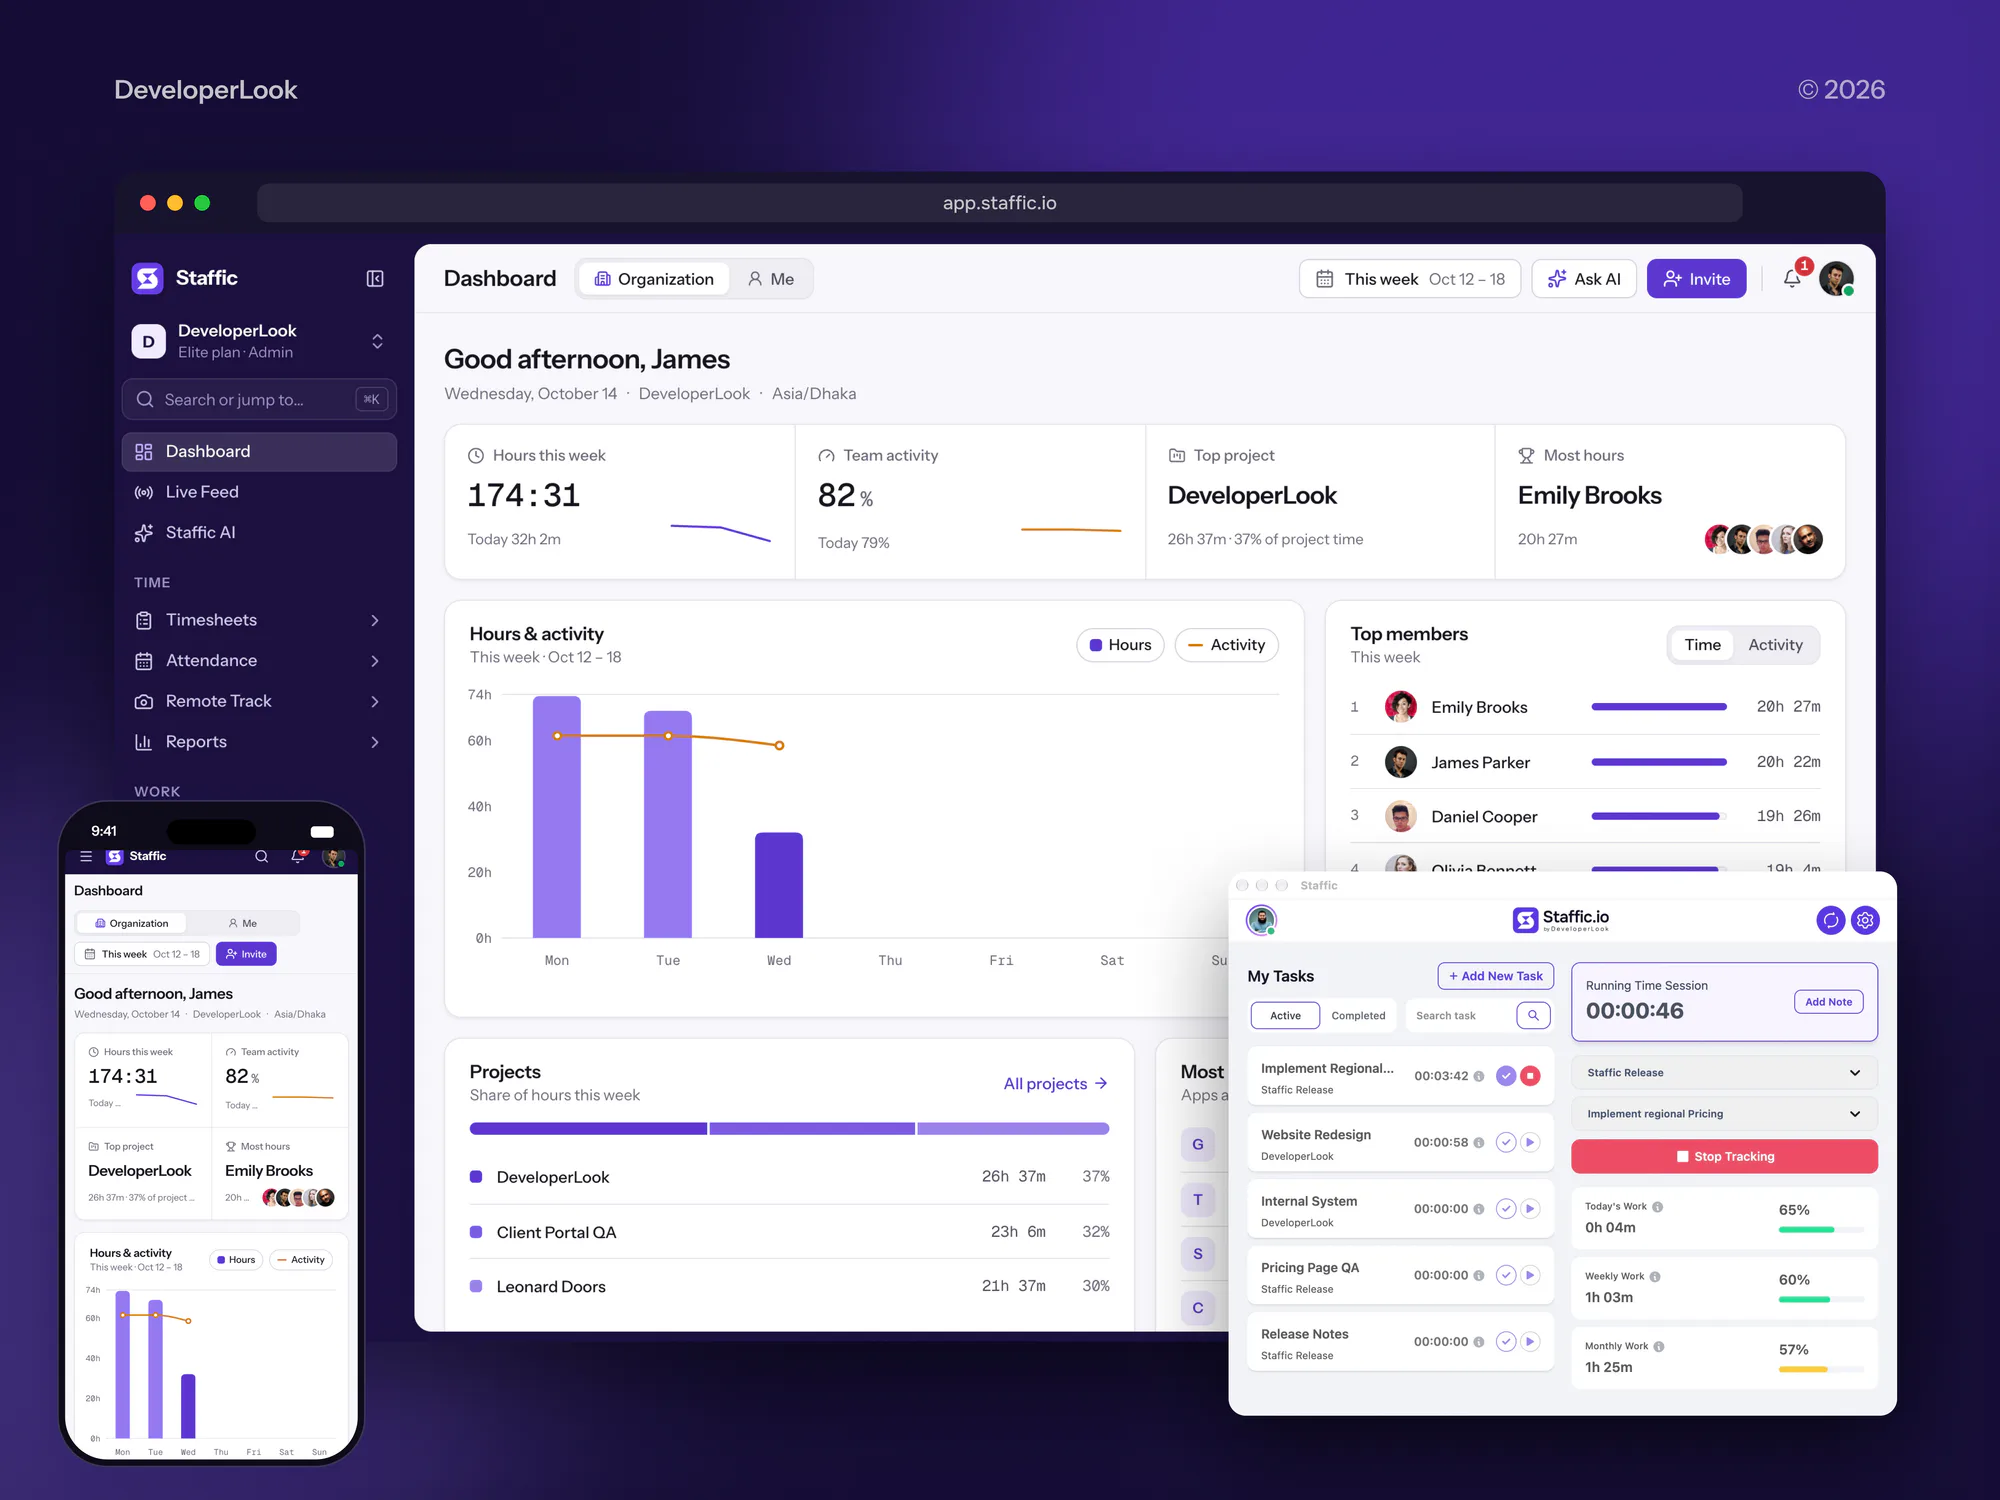
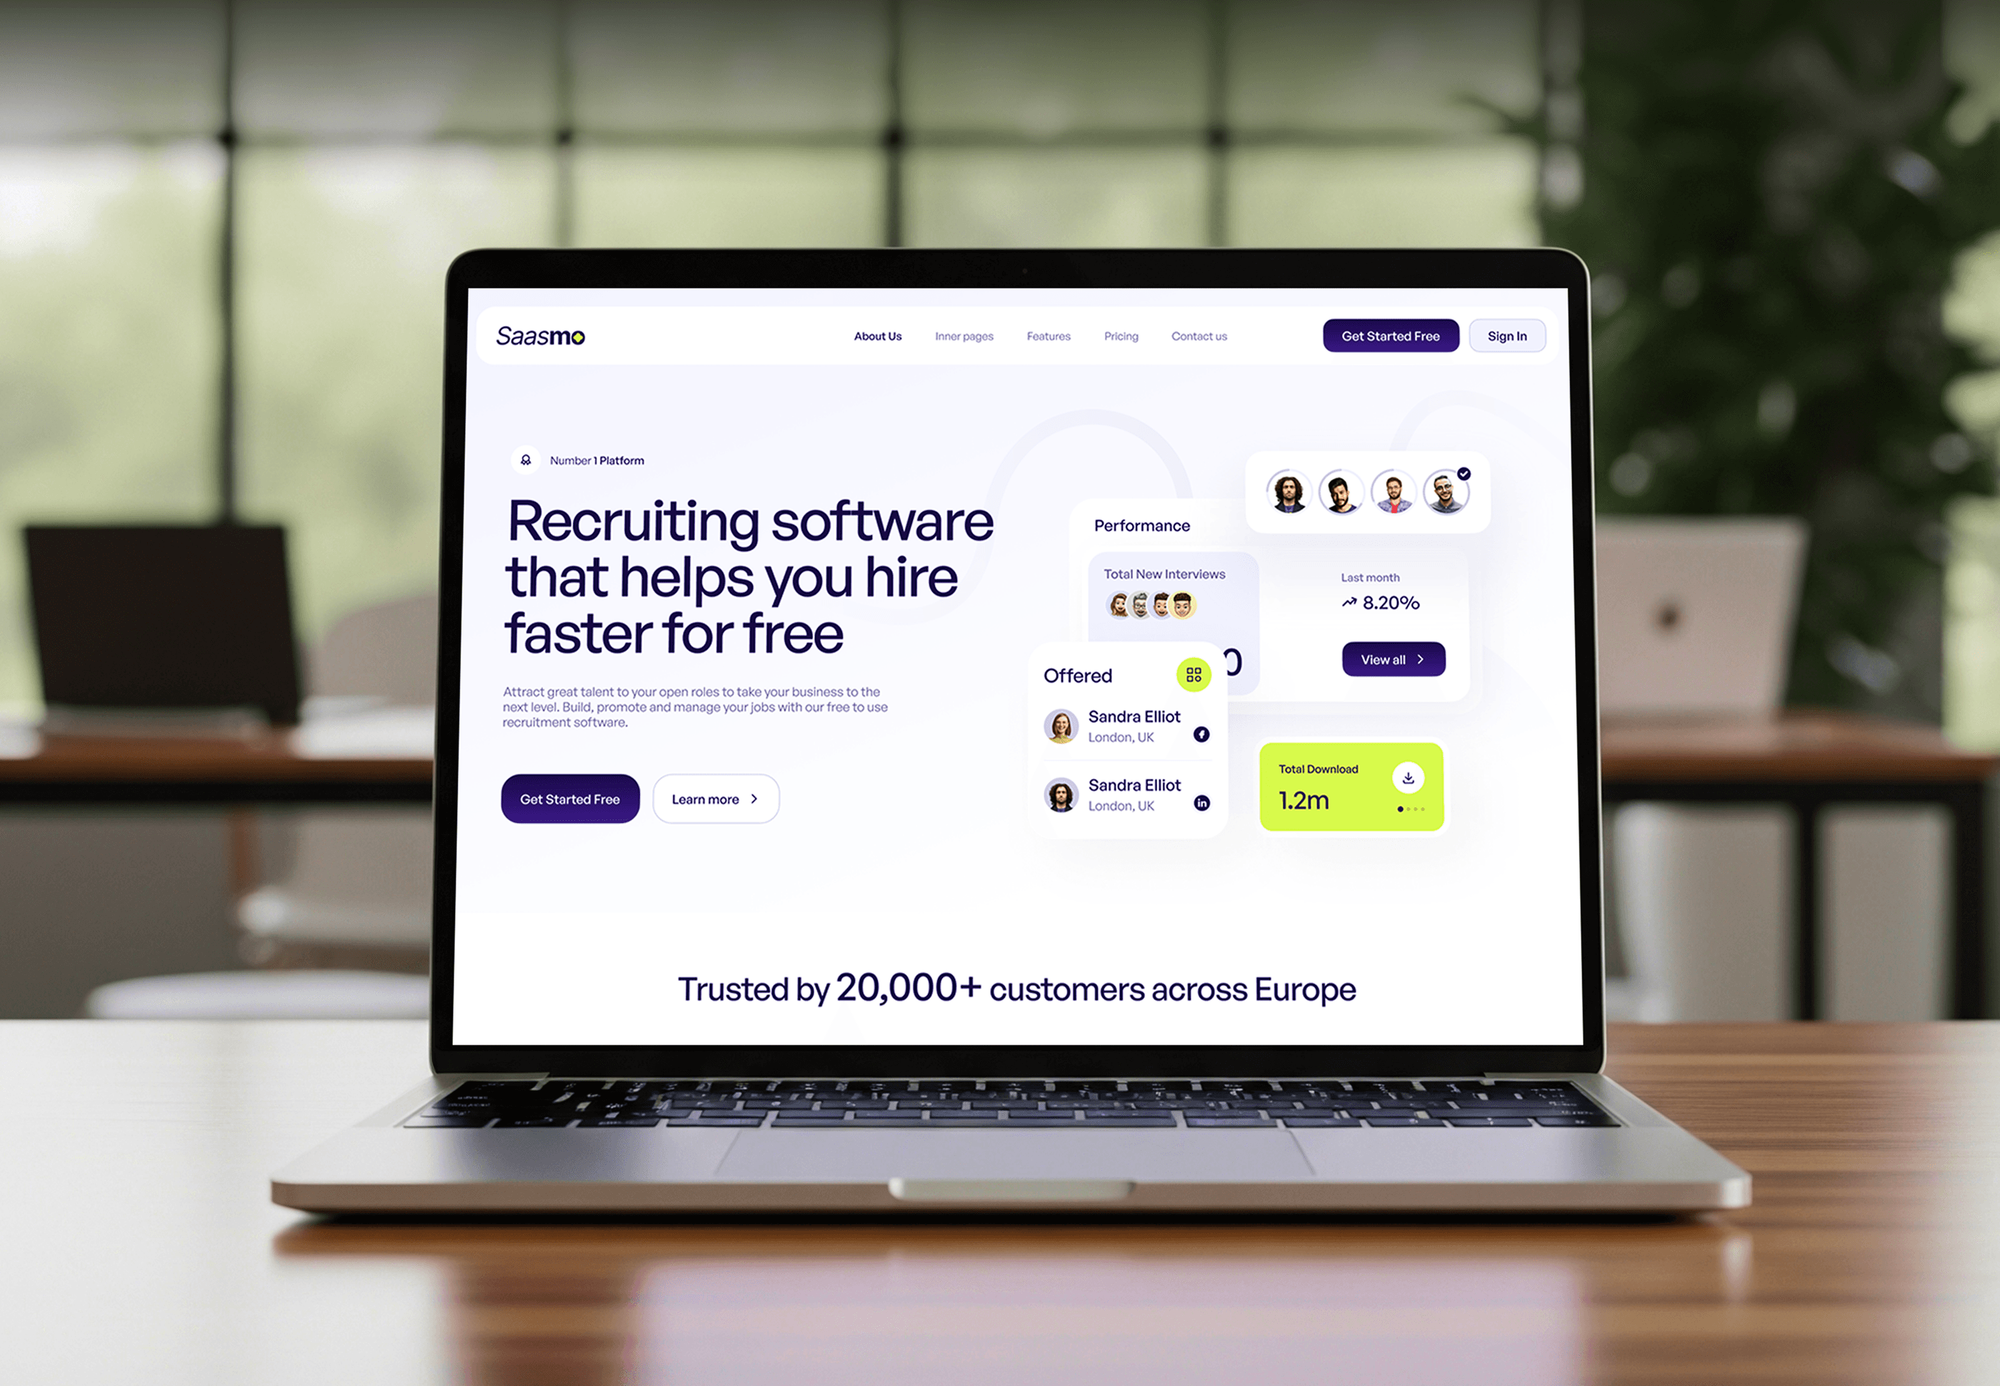
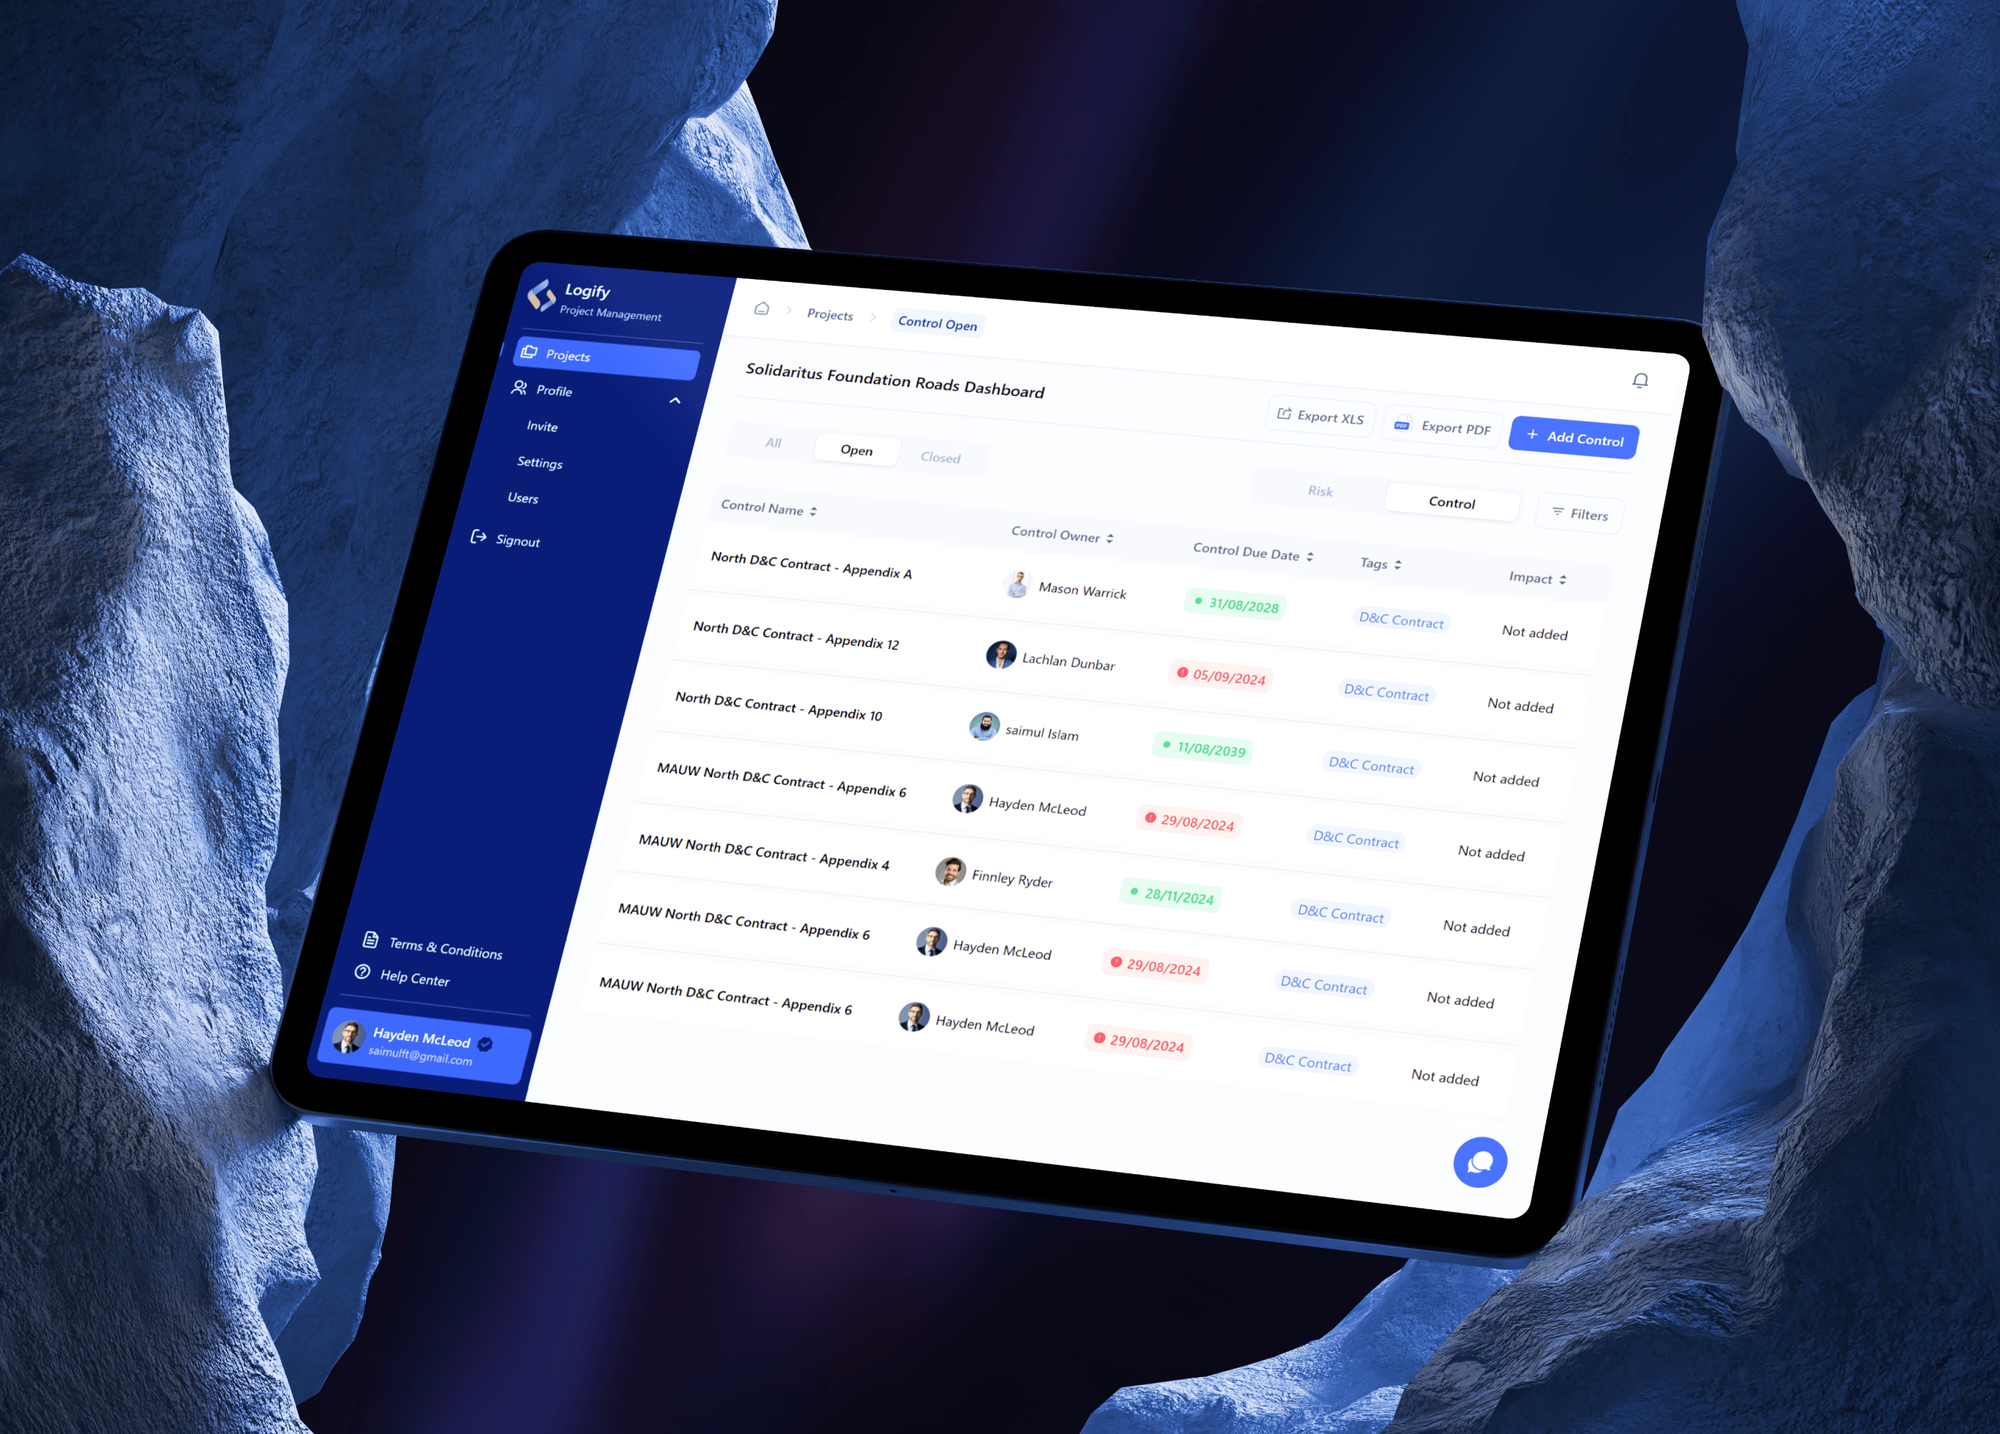
SaaS products and web apps we designed and built, from finance software to time tracking. Products like these hold the customer data SOC 2 controls protect.
What Our Clients Say
Feedback from teams we have built SaaS products, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
SOC 2 work touches production, identity, and code. These habits keep your releases moving while controls go in, and keep the evidence honest.
Every control we add goes through your normal review process. Your engineers see and approve each change before it reaches production.
We use named accounts with the least access each task needs. They're removed at handover, and you get a list of everything we touched.
Independence matters in SOC 2. We prepare you and support the audit, while a separate CPA firm tests the controls and signs the report.
We'd rather write a short policy you follow than a long one you don't. Auditors test what a policy says, so every line has to be true.
If Security alone satisfies your buyers, we won't sell you the other criteria. Each extra criterion adds controls, evidence, and audit cost.
Evidence, policies, and the control matrix live in your storage and your tools. Nothing about your audit depends on staying with us.
Overview
DeveloperLook provides SOC 2 compliance readiness for SaaS and B2B companies whose customers ask for a report. We assess gaps against the Trust Services Criteria, build controls in your cloud and code workflow, write policies, and set up an evidence calendar. Projects start at $1,350 and take 2 to 10 weeks before the CPA audit.
DEVELOPERLOOK
Project facts · SOC 2 Compliance Services
Reviewed 22 Oct 2026 by Saimul Islam
Good fit
SaaS startups closing enterprise deals
Your biggest prospect's security team sent a questionnaire asking for a SOC 2 report, and the deal stalls until you have a plan.
B2B platforms on AWS, Google Cloud, or Azure
Your product deploys from GitHub or GitLab to a major cloud, and you need SOC 2 compliance requirements mapped to what you already run.
Teams that bought a compliance platform
You signed up for an automation platform, connected it to your cloud, and now face a long list of failing tests nobody has time to fix.
CTOs comparing providers
Your board wants SOC 2 this year, and you're comparing SOC 2 compliance companies that do the engineering work, not just send templates.
Agencies and dev shops with SaaS clients
Your SaaS clients ask you to help with SOC 2, and you need a partner who handles readiness quietly under your brand.
Not a fit
Need the audit itself
You need the SOC 2 report itself. Only a licensed CPA firm can issue it, so we prepare you and support the audit while your chosen firm tests and signs.
Need an ongoing security lead
You need someone to own security every month, answer questionnaires, and lead audits for years. Our vCISO services cover that as an ongoing role.
Buyers ask about HIPAA
Your customers are healthcare providers who ask about HIPAA, not SOC 2. Our HIPAA compliance services page covers the risk analysis and policies they expect.
Budget under $1,350
Your budget is under $1,350 and no customer has asked for a report yet. Turn on MFA everywhere, require reviewed pull requests, and come back when a buyer asks.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the criteria in scope, your team size, and existing controls, and you get a fixed proposal after a free scoping call.
For SaaS teams that need to know how far they are from a SOC 2 audit.
$1,350one-time, USD
For teams preparing a Type 1 report to unblock an enterprise deal.
$3,600one-time, USD
For teams running the observation period ahead of a Type 2 report.
$7,400one-time, USD
For Agencies
You own the client relationship. We supply the readiness assessment, control builds, and evidence work under your brand, and join client calls only when you ask. Your SaaS clients get audit-ready without you hiring a compliance engineer.
White label: your client only ever sees your brand
Send the client's stack, target report type, and the buyer questionnaire driving it.
You get a fixed price per client, a written scope, and the access we'll need.
We close the gaps, write the policies, and hand over an audit-ready evidence folder.
You present the roadmap while our engineers build controls under your brand.
Controls built in your client's cloud, repos, and identity provider.
Policies and control matrices delivered in your template and naming.
Take on one client's audit or several observation windows at once.
The Right Technology for Your Project
Controls live in the cloud, code, and identity tools your team already uses, so evidence comes from real systems rather than spreadsheets alone.
 AWS
 Google Cloud
 Microsoft Azure
 Cloudflare
 Docker
 Google Sheets
 Slack
FAQ
Straight answers on cost, timing, Type 1 versus Type 2, and what a SOC 2 audit involves.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our SOC 2 readiness work starts at $1,350 for a gap assessment and control matrix. Getting Type 1 ready, with policies and controls built, starts at $3,600, and the Type 2 program with monthly checks starts at $7,400. The CPA firm's audit fee and any platform subscription are separate, and you pay them directly.
Most SaaS teams become audit-ready for Type 1 in 6 to 10 weeks, including a 2 to 3 week readiness assessment. A Type 2 report then needs an observation period, agreed with your auditor and often several months long, before testing ends. Starting that window early is the biggest lever on your overall date.
SOC 2 compliance means a CPA firm has examined your controls against the AICPA Trust Services Criteria and issued a SOC 2 report. Security is included in every report, and availability, processing integrity, confidentiality, and privacy are added when customers need them. There's no pass certificate: the report is an opinion with any exceptions listed.
For customers, it means an independent auditor has checked how you protect their data and written down what it found. Their security team reads your report instead of sending a long questionnaire. They focus on the opinion, any exceptions, and the controls the report expects them to run on their side.
SaaS companies and service providers that hold customer data usually need SOC 2 once enterprise buyers start asking. It's common in B2B software, fintech, HR tech, and health tech vendors. No law requires the report: demand comes from customer contracts and security reviews, so let your buyers' requests set the timing.
SOC 2 Type 2 compliance means your controls were tested over a period of time, not on one day. The auditor samples evidence across the whole observation period, so access reviews, change approvals, and backups must run every time. Buyers usually trust Type 2 more, because it shows controls operating, not only designed.
Often yes, because SOC 2 Type 1 compliance checks that controls are designed properly on a single date, and you can reach it sooner. It can unblock deals while your Type 2 observation period runs. If your buyers insist on Type 2 from the start, skip Type 1 and begin the observation window once controls are live.
You get SOC 2 compliance by choosing the criteria and report type, closing the gaps, and passing an examination by a licensed CPA firm. In between, you build missing controls, write policies, and collect evidence. For Type 2, controls must run through the observation period first. A readiness assessment keeps avoidable exceptions out of your report.
Avoid the usual pitfalls by scoping only the criteria buyers need, writing policies you follow, and giving every control a named owner. Many exceptions come from controls that ran once and then lapsed, such as a skipped quarterly access review. An evidence calendar and monthly spot checks catch those before your auditor does.
A SOC 2 audit is an attestation examination by a licensed CPA firm under AICPA standards. The auditor reads your system description, tests your controls against the criteria in scope, and issues an opinion. We don't perform audits: we prepare you, then support your team while the CPA firm does its fieldwork.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.