DNS move without surprises
Every record exported, compared, and approved before cutover, with DNSSEC turned off and back on in the right order.

For business sites and stores moving onto Cloudflare: DNS, email, SSL, caching, and firewall rules set up properly, with your server hidden behind it. From $450.
2X
Faster cached page loads
100%
DNS and email records kept
How your project runs
01 · FreeTeams we have built for:














The Problem
It shows up after a quick install. Email stops for a day, redirects loop after an update, a cart page gets cached, or attackers reach your server directly.
Missed records
The DNS scan misses a mail record, and email goes quiet.
Missed records
Every record is exported and matched before the nameservers change.
Flexible SSL
Traffic to your server is unencrypted, and redirects start looping.
Flexible SSL
SSL runs in Full (strict) mode with an origin certificate on your server.
Open origin
Attackers find your server's IP and go straight past Cloudflare.
Open origin
Your server accepts web traffic from Cloudflare only, or through a tunnel.
Cached carts
A broad cache rule serves one shopper's cart to another.
Cached carts
Cache rules bypass carts, checkouts, accounts, and logged-in sessions.
You turned on Cloudflare in an afternoon, and it mostly worked. Then email stopped for a day, because the DNS scan missed a mail record. The SSL mode is Flexible, so traffic from Cloudflare to your server still travels unencrypted, and a plugin update started a redirect loop. Your server's real IP sits in old DNS history, so attackers skip Cloudflare entirely. And the account login belongs to a freelancer who left last year.
We start with an export of every DNS record from your current provider and match it against Cloudflare's scan before the nameservers change. SSL moves to Full (strict) with an origin certificate, cache rules skip carts and logged-in pages, and firewall and bot settings fit your Cloudflare plan. Then your server answers only Cloudflare. Your site moves behind Cloudflare without an email outage, not after one.
Records checked before cutover
Every DNS record, including mail and domain verification records, is compared before the nameservers change.
Encrypted the whole way
Full (strict) SSL from visitor to Cloudflare to your server, then HSTS once every page loads over HTTPS.
Origin locked to Cloudflare
Your server drops direct traffic, so attackers can't step around the firewall and DDoS filtering.
Our Cloudflare Setup and Security Process
You approve the DNS zone before the nameservers change, review each firewall and cache rule before it goes live, and keep a rollback note for every setting.
We look at your registrar, DNS host, hosting, SSL, and any existing Cloudflare account. You get a note on the risks, the Cloudflare plan you need, and a fixed price. If Cloudflare's own setup wizard covers your case, we'll tell you before we quote.
What's Included
You get a DNS move with every record checked, Full (strict) SSL, CDN cache rules, and WAF and bot settings for your plan. Your origin server answers Cloudflare only.
Compare Options
Cloudflare's own wizard gets most small sites online in an hour, and a good freelancer handles a simple zone. Here is where each one stops once you add email, logins, or a store.
| Feature | DeveloperLookBest fit | DIY setup | Freelancer |
|---|---|---|---|
| DNS records | Exported and matched by hand | Scan only, you check | Depends on the person |
| Email records | Mail, SPF, DKIM, DMARC verified | Easy to miss | Often checked |
| SSL mode | Full (strict) with origin certificate | Automatic mode picks one | Depends on the person |
| Cache rules | Carts and logins bypassed | Default caching only | Sometimes tuned |
| Firewall rules | Tuned to your plan and site | Managed defaults only | Basic rules |
| Origin protection | Server locked to Cloudflare | Not covered | Sometimes covered |
| Setup time | 2 to 5 business days | An hour or two | A few days |
| Cost | From $450, fixed price | Free on the Free plan | Hourly, often lower |
Projects We've Built
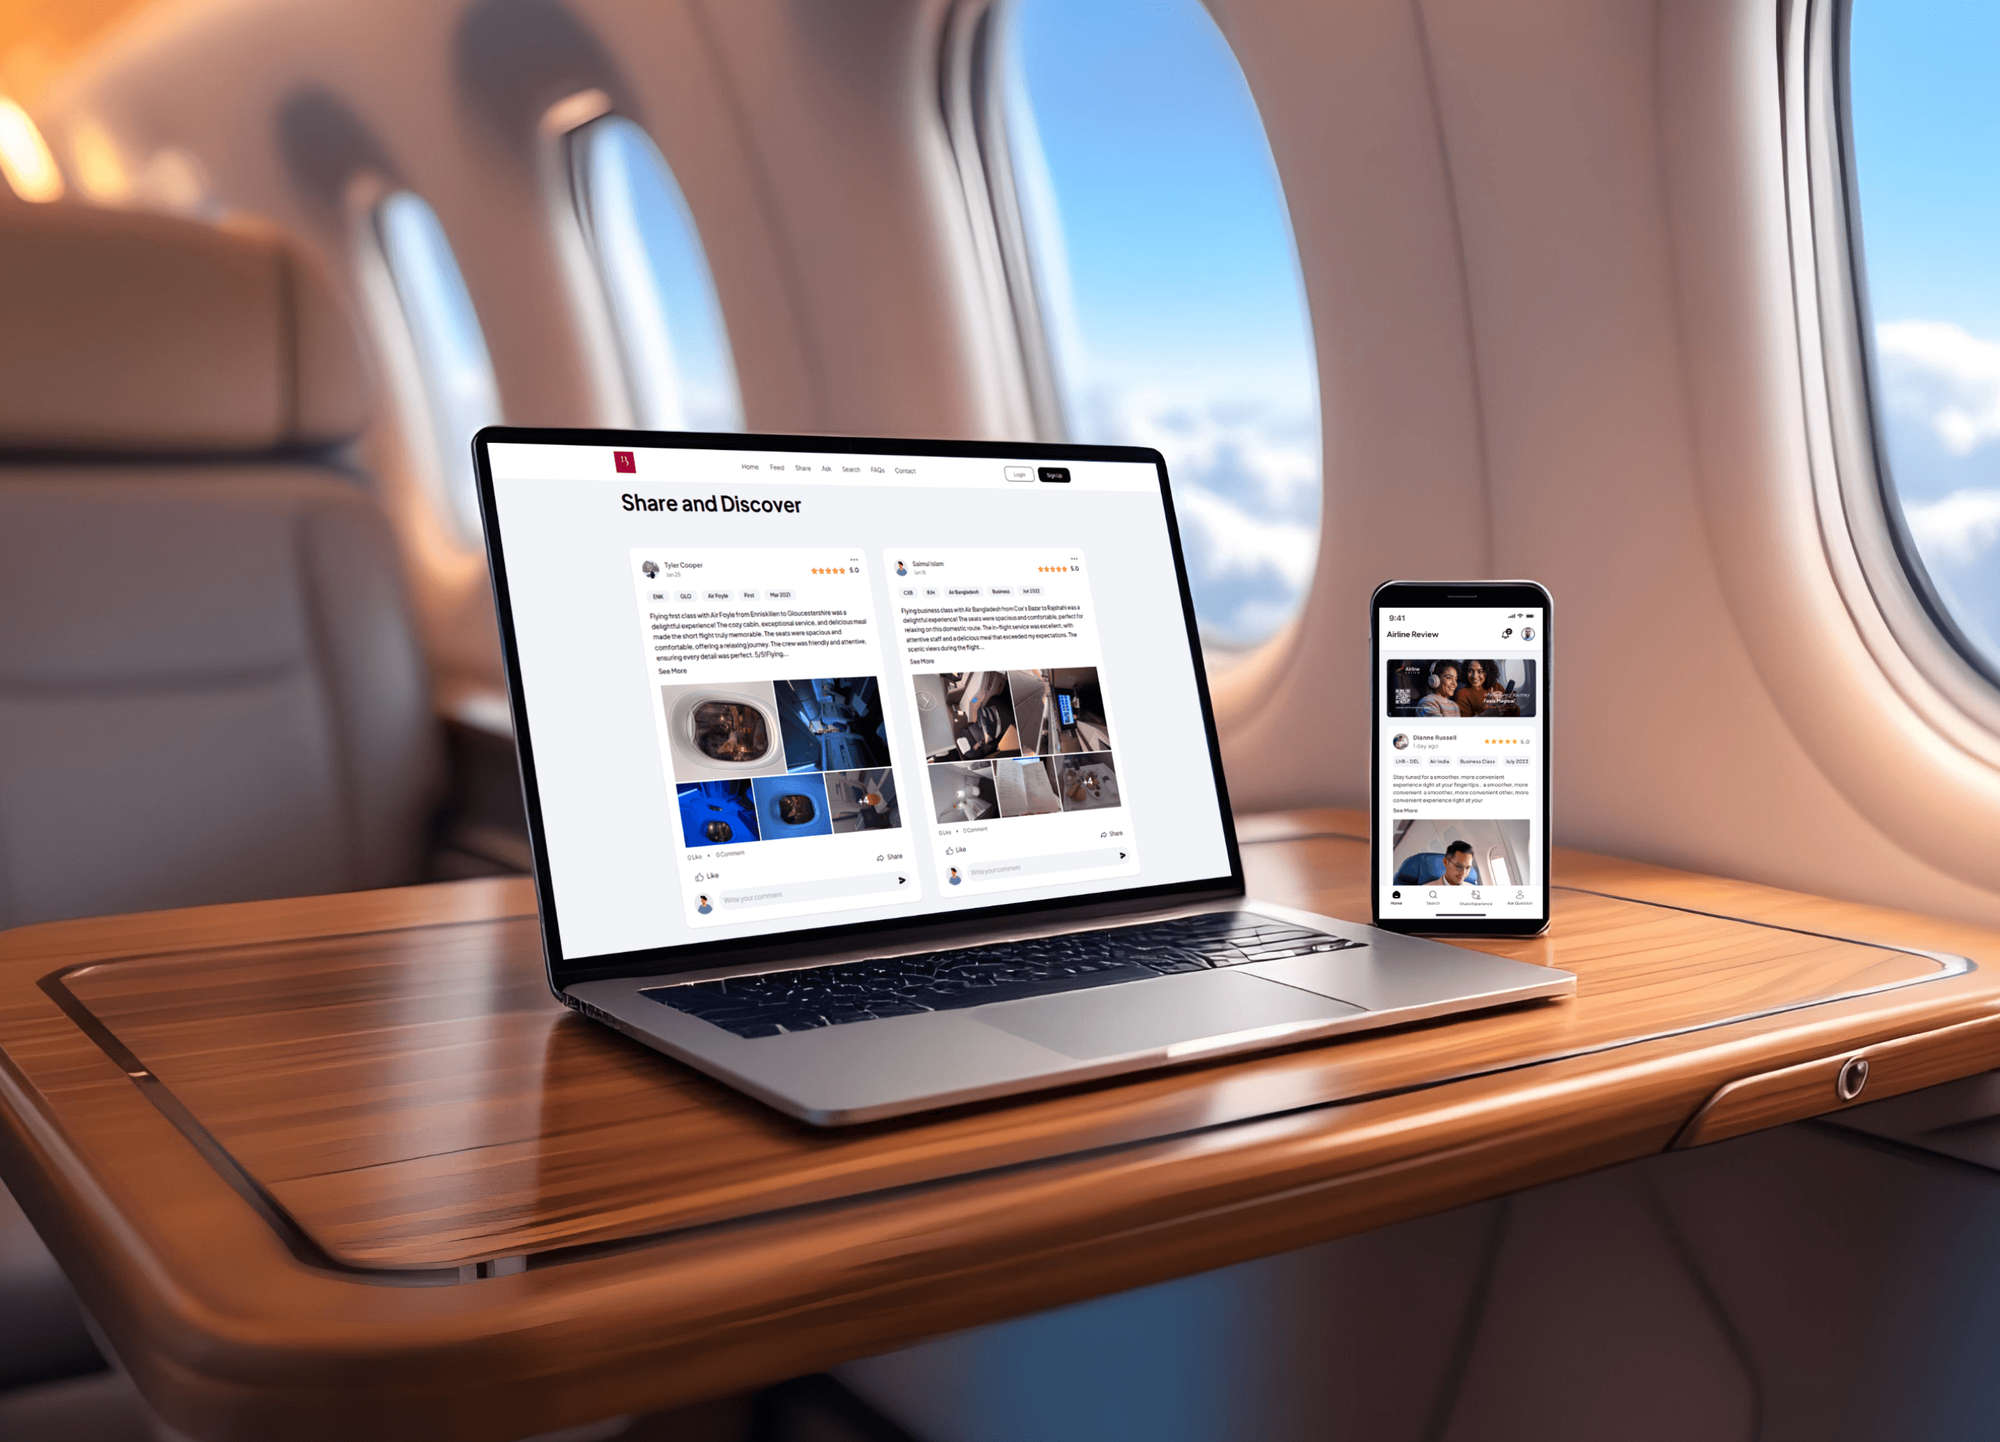
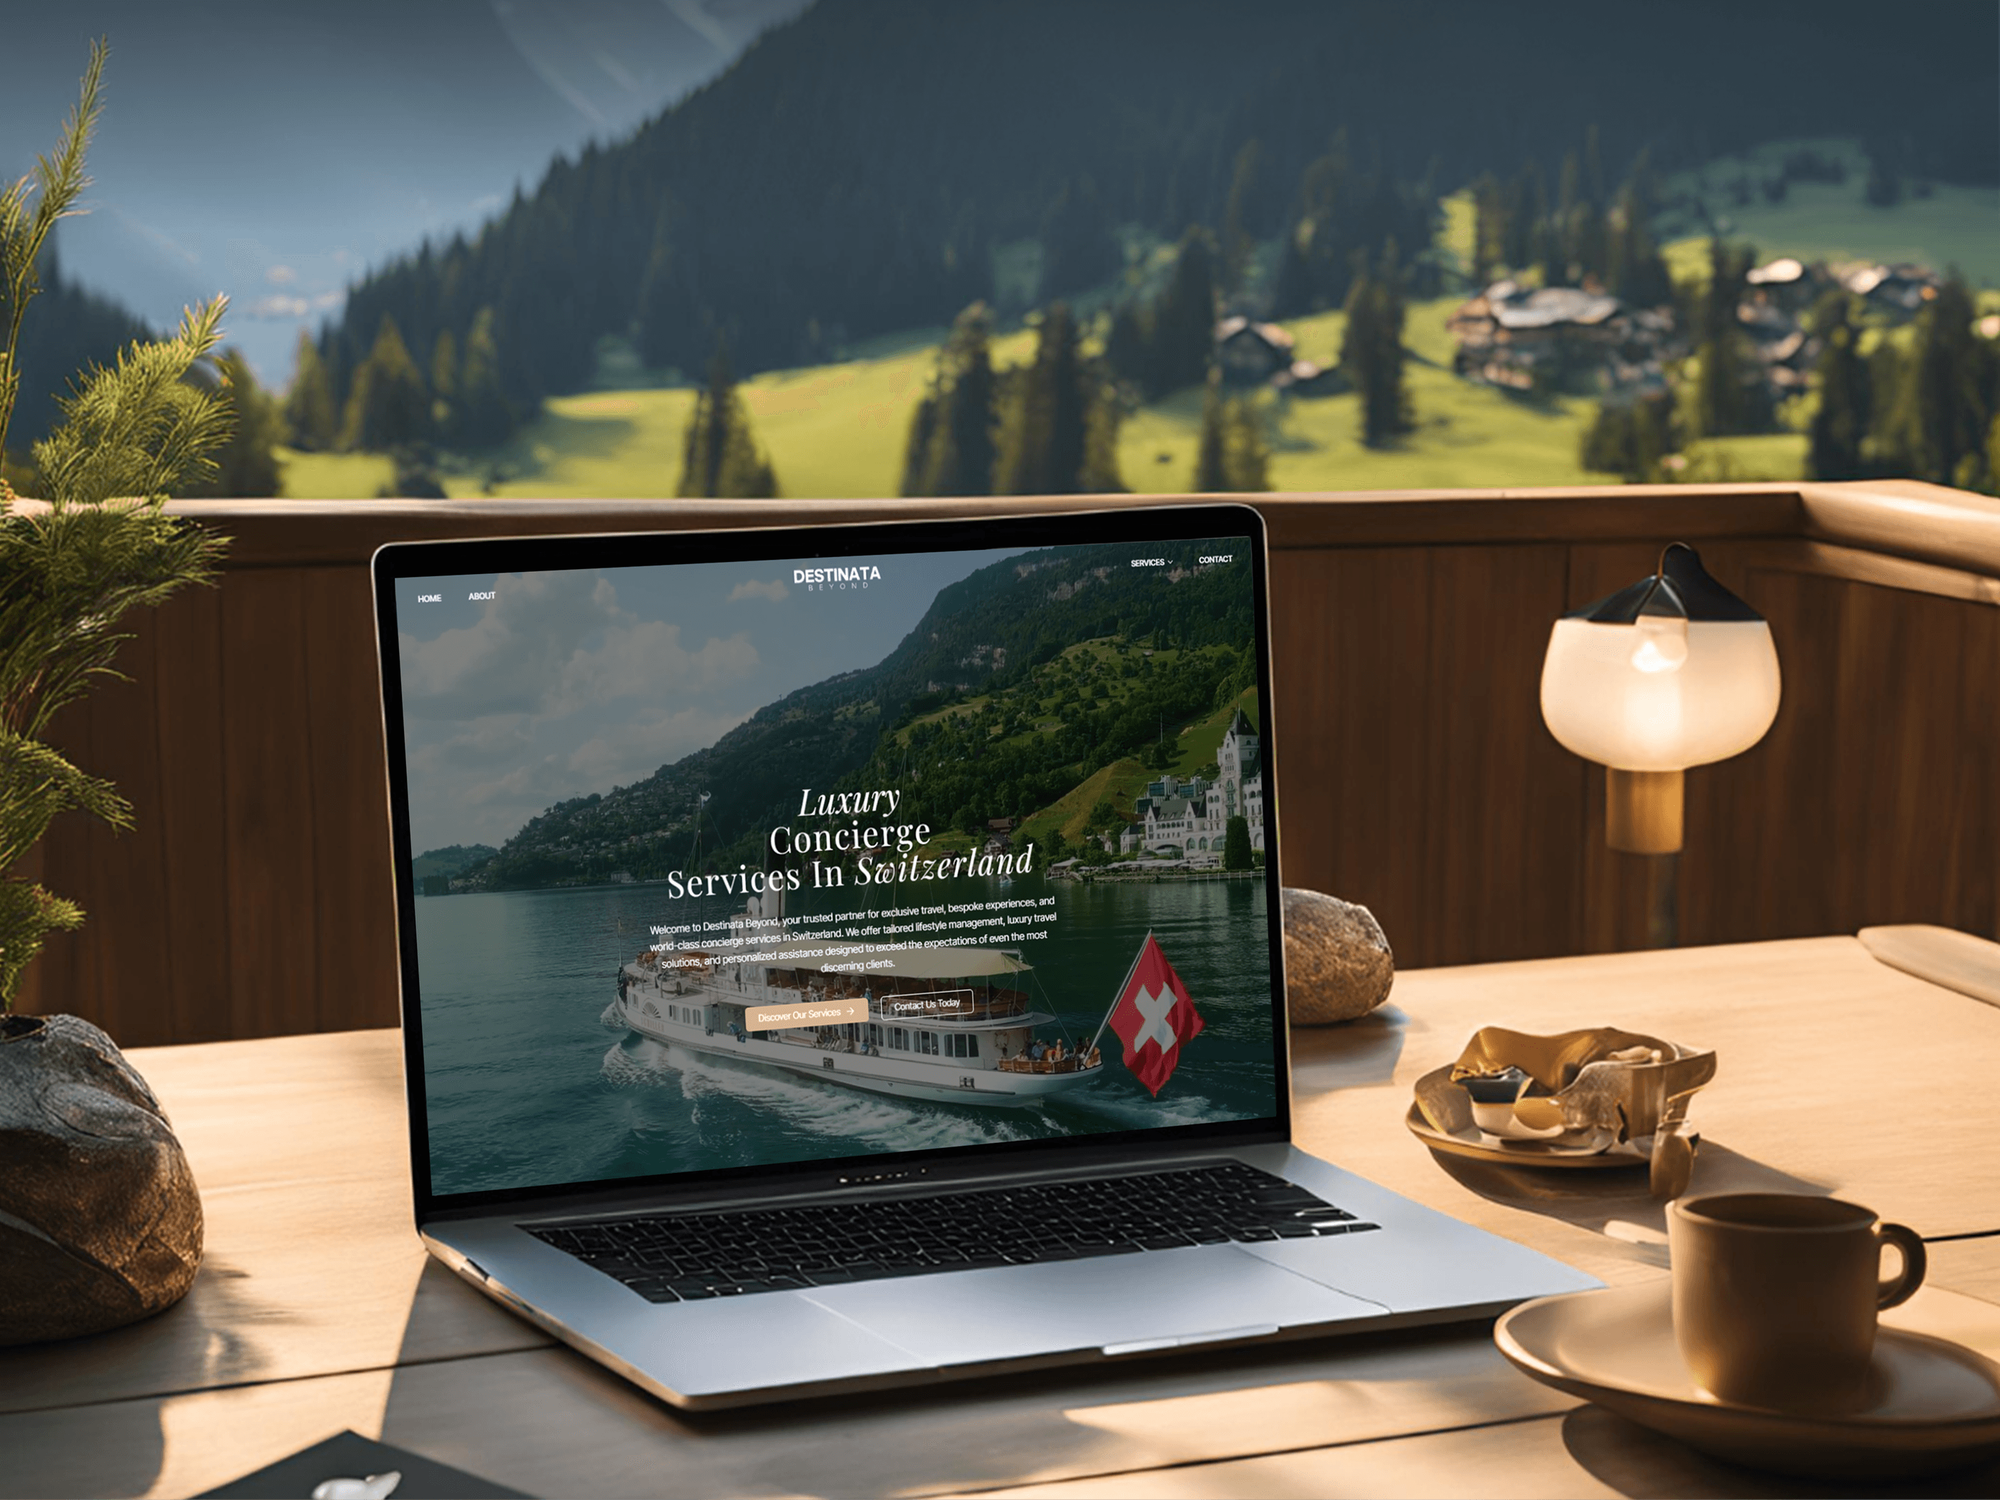
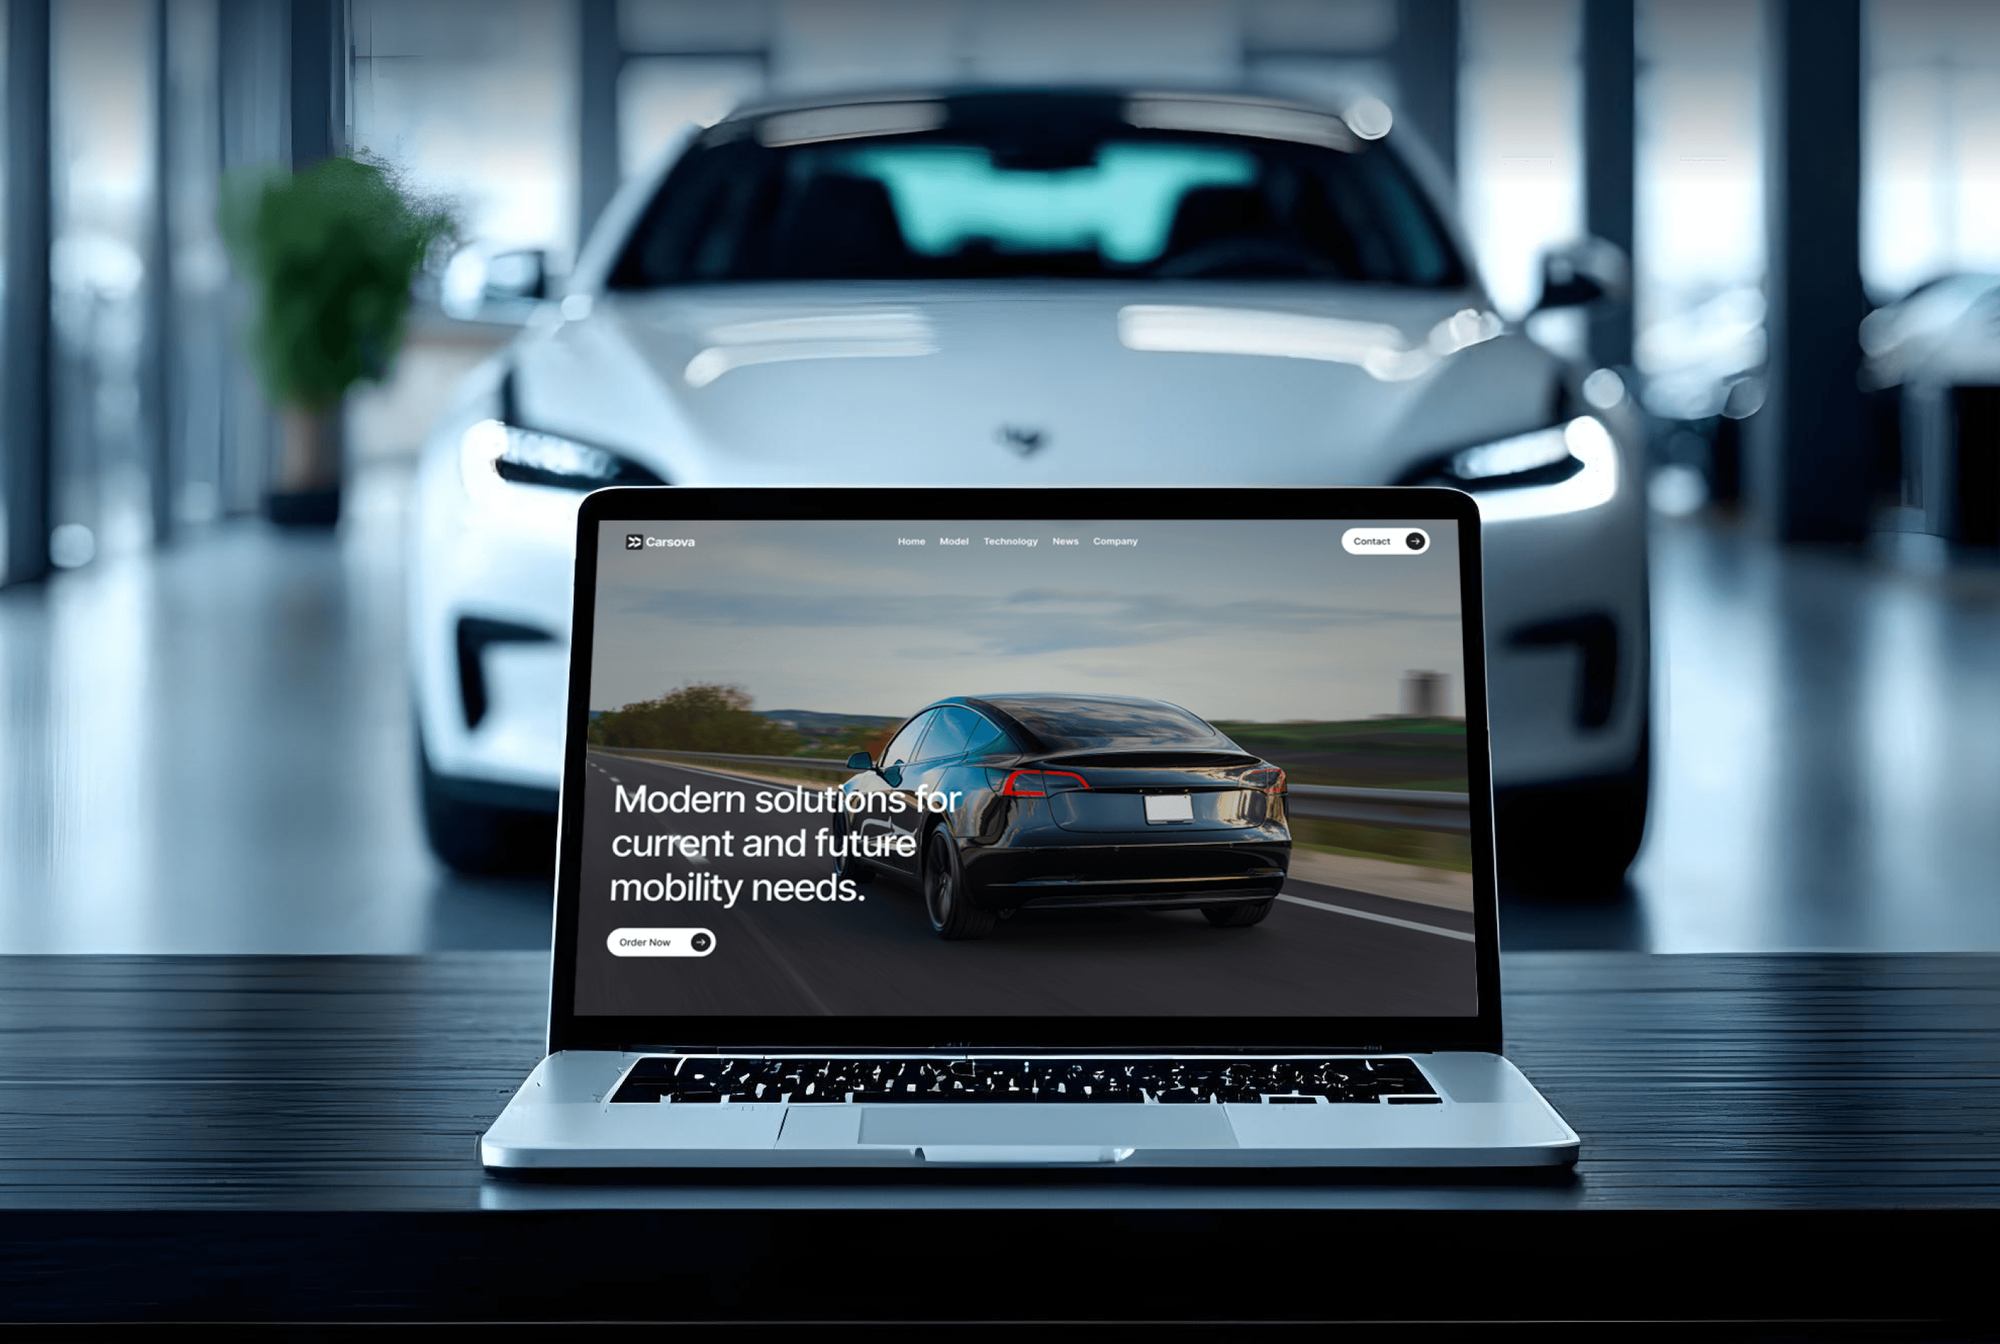
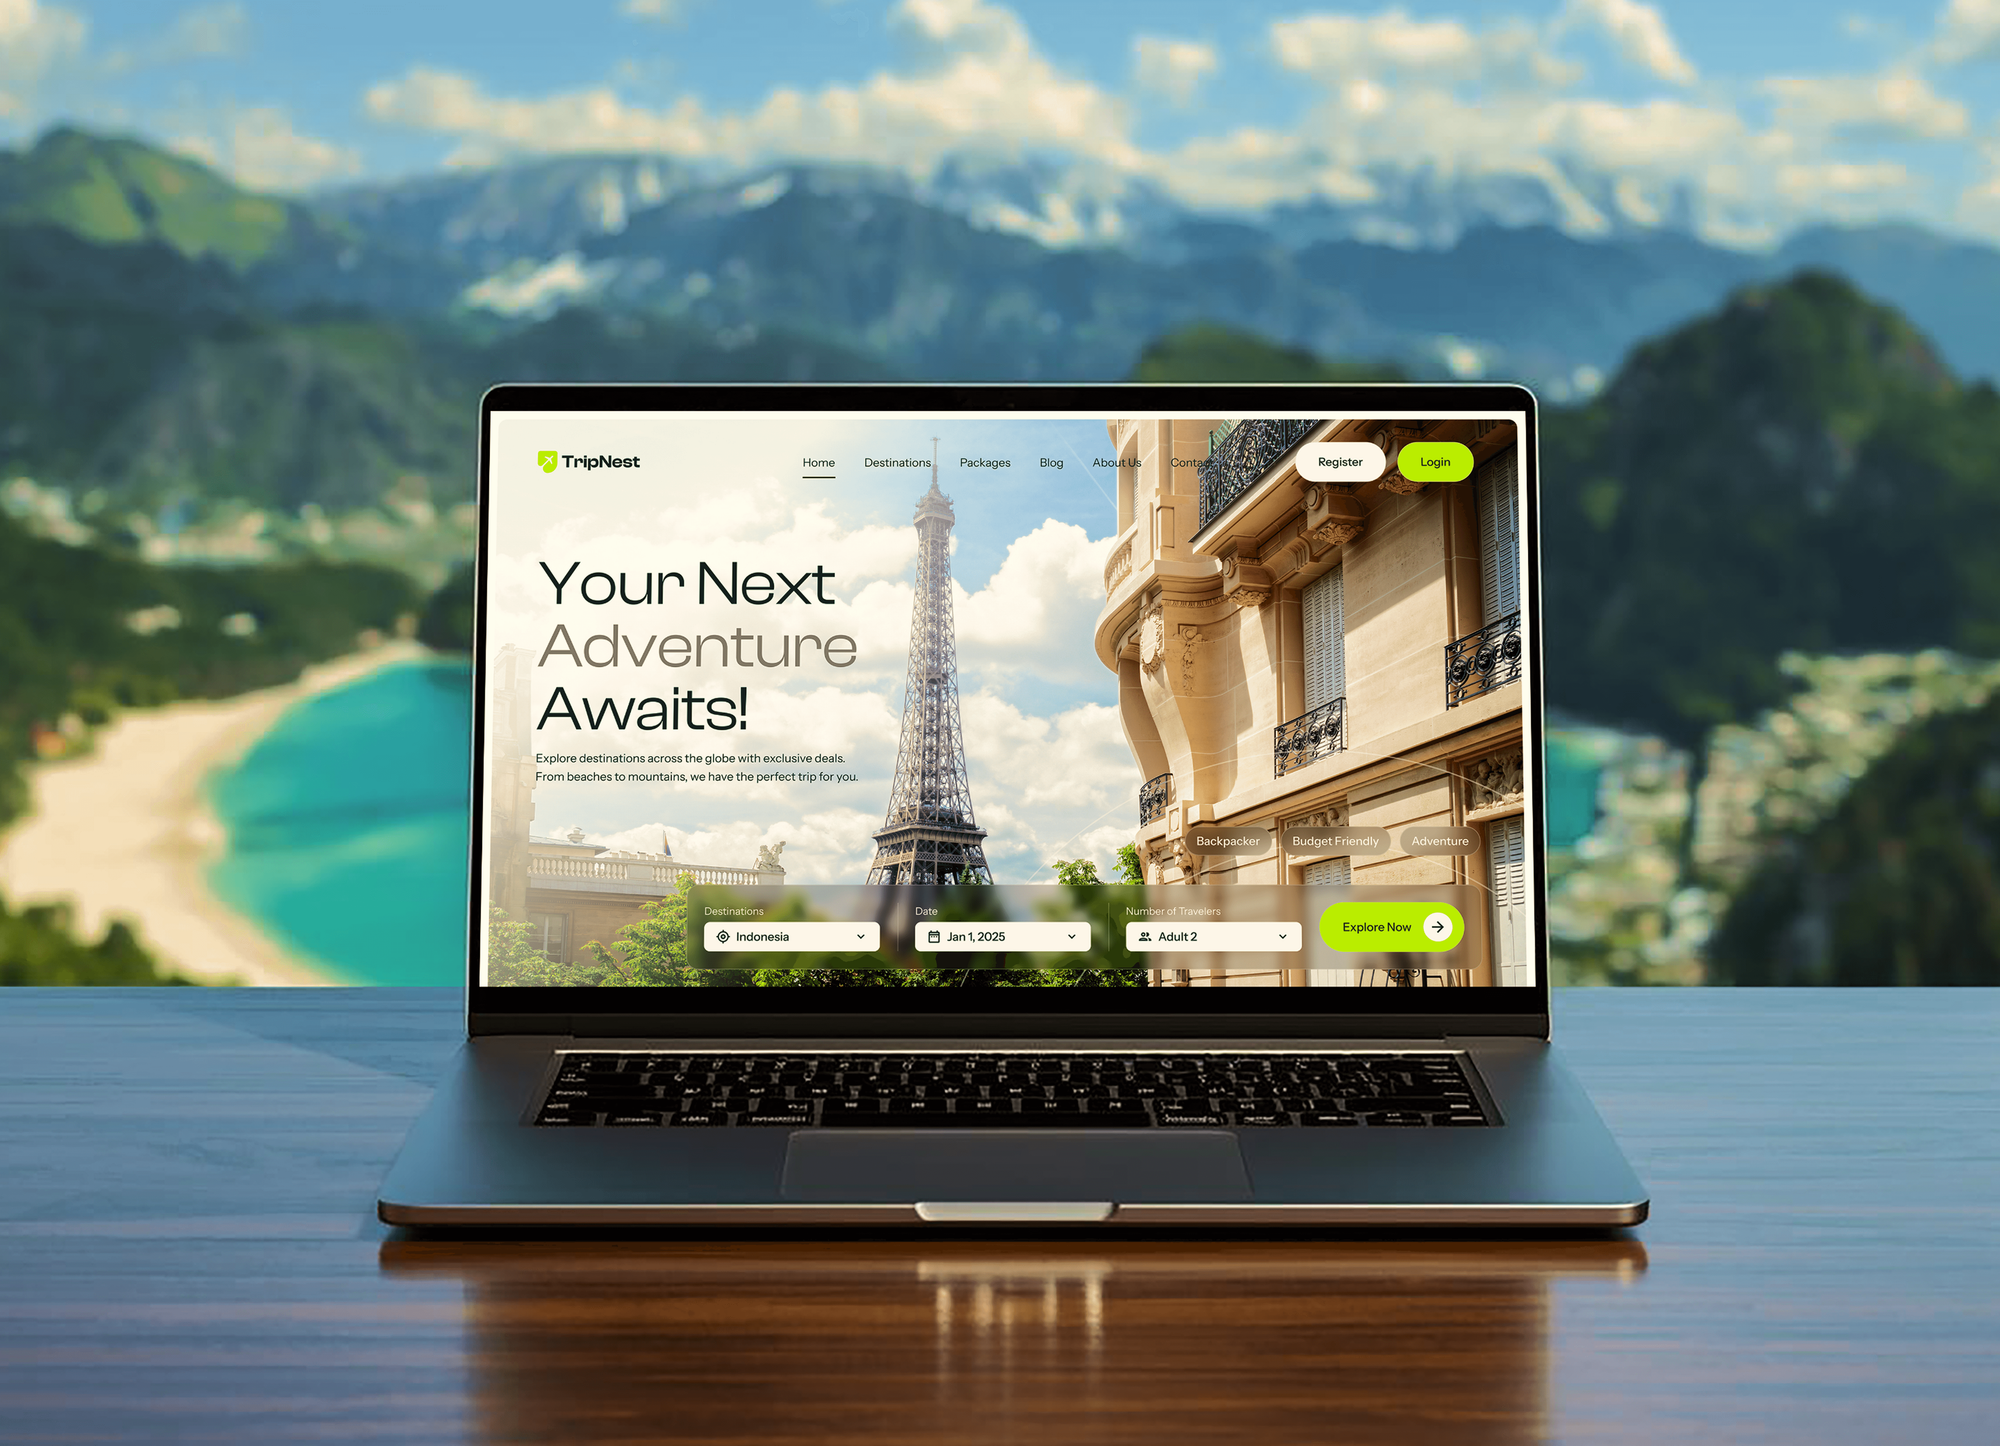
Community, concierge, automotive, and tour booking sites we designed and built. They weren't Cloudflare projects, but they're the kind of busy business sites this setup protects.
What Our Clients Say
Feedback from teams we have built websites, platforms, and apps for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A Cloudflare setup and security project touches your DNS, email, and checkout at once. These habits keep each change small, tested, and easy to undo.
You get a test message sent and received before and after the nameserver change. A site that loads but loses a day of email isn't finished.
You get what your Cloudflare plan actually includes, plus a note on what a paid plan would add. You don't pay for an upgrade you won't use.
Each rule goes in a written list with how to undo it. If one blocks a real customer, anyone on your team can switch it off.
Your Cloudflare account, domain, and billing stay with you, and we join as a member with our own login. When we finish, you remove us.
We test checkout, login, forms, and payment webhooks after every change. A setting that looks safe in a dashboard can still break a page.
You get one price after the free zone review, and it doesn't grow if a record takes longer to untangle. New work waits for your approval.
Overview
DeveloperLook handles Cloudflare setup for business websites and stores. We move your DNS without losing email records, set SSL to Full (strict), add cache, WAF, bot, and rate limiting rules, and lock your server to Cloudflare. Projects start at $450, and most single-domain setups take 2 to 5 business days, with the account in your name.
DEVELOPERLOOK
Project facts · Cloudflare Setup and Security
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Business sites moving onto Cloudflare
You want Cloudflare's speed and protection, but your email, booking form, and SSL depend on records you're afraid to touch.
WordPress sites with an old setup
Your Cloudflare install happened years ago, and now redirect loops, cached admin pages, and a Flexible SSL setting keep causing odd bugs.
Stores and booking sites
You run checkout, accounts, or bookings, and you need cache rules and firewall settings that leave every shopper's session alone.
Sites hit by bots or floods
Your login page gets hammered by password attempts, or a traffic spike took the site down, and you want Cloudflare DDoS protection set up properly.
Agencies managing client domains
Your agency runs many client domains and needs each zone set up the same way, with accounts and billing kept in the clients' names.
Not a fit
Staying on AWS or Azure
Your traffic runs through AWS CloudFront or Azure Front Door, and it's staying there. Our Web Application Firewall Setup covers those edges.
Only a certificate problem
Your site shows a certificate warning, and you don't want Cloudflare at all. Our SSL Certificate Installation Service fixes the certificate and the HTTPS move from $350.
Speed is the only goal
Your site is slow, nobody attacks it, and you mainly want better Core Web Vitals. Our Website Speed Optimization service fixes the pages themselves first.
A small personal site
Your site is a hobby page with no logins, forms, or sales. Cloudflare's Free plan and setup wizard cover you without paying anyone.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your price depends on your domain count, Cloudflare plan, and hosting, and you get a fixed proposal after a free zone review.
For Agencies
You own the client relationship. We supply the Cloudflare work behind it: DNS moves, SSL, cache and firewall rules, and origin locks on every client domain. Accounts stay with your clients, and handover notes carry your name.
White label: your client only ever sees your brand
Send the client domains, hosting details, and who owns each Cloudflare account.
We run a free zone review on each domain and give you a fixed price.
We move and secure each zone, then hand off notes under your brand.
Send the client domains, hosting details, and who owns each Cloudflare account.
We run a free zone review on each domain and give you a fixed price.
We move and secure each zone, then hand off notes under your brand.
The Right Technology for Your Project
We use Cloudflare's own tools for the zone, standard web servers at the origin, and Terraform when your rules need to live in code.
 Cloudflare
 WordPress
 WooCommerce
 AWS
 Microsoft Azure
 Google Cloud
 Docker
 Chrome DevTools
 PageSpeed Insights
Related Services
Cloudflare work pairs well with deeper firewall tuning, DDoS planning, bot defenses for logins and checkouts, a clean HTTPS move, or speed work on the pages themselves.
This page
Cloudflare Setup and Security
Pairs with the 6 services around it
FAQ
Straight answers on cost, timing, DNS and email, DDoS, WordPress, caching, Turnstile, and which Cloudflare plan you need.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Cloudflare setup and security from DeveloperLook starts at $450 for one domain. It covers the DNS move, Full (strict) SSL, cache rules, managed WAF rules, and an origin lock. The $1,050 plan adds custom rules, rate limits, and Turnstile for up to 3 domains. The $1,900 plan covers up to 10 domains in Terraform. Cloudflare's own fees are separate.
Most single-domain setups take 2 to 5 business days. The record audit takes a day, and Cloudflare says a nameserver change can take up to 24 hours to go active. Rules and the origin lock follow once your zone is live. Up to 10 domains take about 3 weeks, moved in small groups.
You add the domain in Cloudflare, check every DNS record it found, and switch your nameservers at the registrar. Turn off DNSSEC first, as Cloudflare asks. Once your zone is active, set SSL to Full (strict), add cache and firewall rules, and restrict your server to Cloudflare's IP ranges.
Export every record from your current DNS host and compare it with Cloudflare's scan before you change nameservers. Cloudflare's docs say the scan may not find every record, and mail records are the ones people miss. Keep MX and mail records set to DNS only, then send and receive a test email after the switch.
Cloudflare DDoS protection starts once your web records are proxied, and Cloudflare says it's unmetered on every plan. Your setup work is around it: hide the server's real IP, lock the origin to Cloudflare, and rate-limit costly pages. DDoS protection by Cloudflare only helps traffic that actually passes through it.
Use Full (strict) SSL with an origin certificate, because Flexible mode loops redirects when WordPress forces HTTPS. Bypass the cache for wp-admin, logged-in cookies, and WooCommerce cart and checkout pages. Rate-limit wp-login.php. Then set your server to log real visitor IPs, or every request looks like it came from Cloudflare.
Cloudflare caches your images, CSS, and scripts once traffic is proxied. Faster pages come from cache rules for public HTML, longer edge cache times, and a purge when you publish. The careful part is exclusion: carts, checkouts, account pages, and anything personal must skip the cache.
Create a Turnstile widget in Cloudflare, add its site key to your form, and check each token on your server. That check uses Cloudflare's Siteverify API, and Cloudflare says the widget alone doesn't protect a form. Each token lasts 5 minutes and works once. Turnstile runs even on sites not proxied through Cloudflare.
No, many small sites do well on Cloudflare's Free plan. It includes unmetered DDoS mitigation, the Free Managed Ruleset, one rate limiting rule, and Bot Fight Mode. On Pro, the Cloudflare web application firewall adds the Cloudflare Managed Ruleset and the OWASP Core Ruleset. Cloudflare bot protection on Free can't take exceptions, so it may challenge API traffic.
You do. Your Cloudflare account, domain, and billing stay in your name, with two-factor sign-in on. We work as an invited member with our own login, so you can remove us when the project ends. You keep a written list of every rule and how to undo it.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.