Leak containment
Exposed buckets, keys, accounts, or forms locked down, with system and log copies taken first.

For businesses that just found customer or staff data exposed: we close the leak, trace which records left, and give your counsel the facts to decide on notice. From $1,200.
3answers
What left, whose, and how
1list
Affected people for counsel
How your project runs
01 · FreeTeams we have built for:














The Problem
It often arrives as an email from a stranger, your bank, or a researcher who found your data online. Then the questions come faster than the facts.
Deleted evidence
The leak gets fixed by deleting the logs that prove scope.
Deleted evidence
We copy logs and system images before any fix changes them.
Unknown scope
Nobody can say how many people or which fields left.
Unknown scope
We trace records and fields from access logs and the exposed data itself.
Whose laws
Nobody knows which residents' laws apply to this breach.
Whose laws
Affected people are sorted by state or country so counsel can apply the rules.
Vendor claims
The vendor says the hole is closed, with no proof.
Vendor claims
We test the vendor's fix ourselves, as the FTC's breach guide recommends.
A security researcher emails a link: your customer database is downloadable from an open cloud bucket. Your counsel asks how many people are affected and which states they live in. Your insurer wants a timeline. Your developer has already deleted the bucket, along with the access logs that showed who downloaded it. Nobody can say whether card numbers were in the export, and the clock on notice deadlines may already be running.
We start by closing the leak without destroying the record of it: logs copied, access revoked, systems preserved. Then we trace what was reached, record by record and field by field, and sort affected people by data type and where they live. Your counsel gets a facts summary and an affected-people list to decide on notice. You make legal decisions from evidence, not from a developer's best guess.
Leak closed, logs kept
Access is cut without deleting the logs that show who reached the data.
Records traced by field
Each affected record is listed with the fields exposed: names, emails, IDs, card or health data.
Counsel decides on notice
We supply facts and lists, and your lawyer decides who must be told and when.
Our Data Breach Response Services Process
You and your counsel approve each step, and we keep notes they can rely on, so legal decisions rest on facts instead of guesses.
We learn what was found, how, and which systems hold the data. You get first steps (don't wipe or power off machines, rotate exposed keys, call your counsel and insurer, keep every log) and a fixed price.
What's Included
Containment that keeps evidence, a record-level scope, affected people sorted for counsel, the cause fixed and verified, and a short checklist for the next incident.
Compare Options
Notification vendors mail letters and run call centers, and breach counsel handles the law. Both are essential, so here is where our technical work fits beside them.
| Feature | DeveloperLookBest fit | Notice vendor | Breach counsel |
|---|---|---|---|
| Closes the leak | Yes, with evidence kept | ||
| Traces affected records | Record and field level | No, uses your list | Hires a technical firm |
| Legal advice on notice | No, counsel decides | ||
| Mails notices, runs calls | Coordinates the vendors | ||
| Credit monitoring offers | Yes, often bundled | Advises on it | |
| Verifies vendor fixes | Yes, tested ourselves | Requests written assurances | |
| Facts summary for insurer | Uses technical reports | ||
| Cost predictability | Fixed price from $1,200 | Per letter and per call | Hourly legal rates |
Projects We've Built
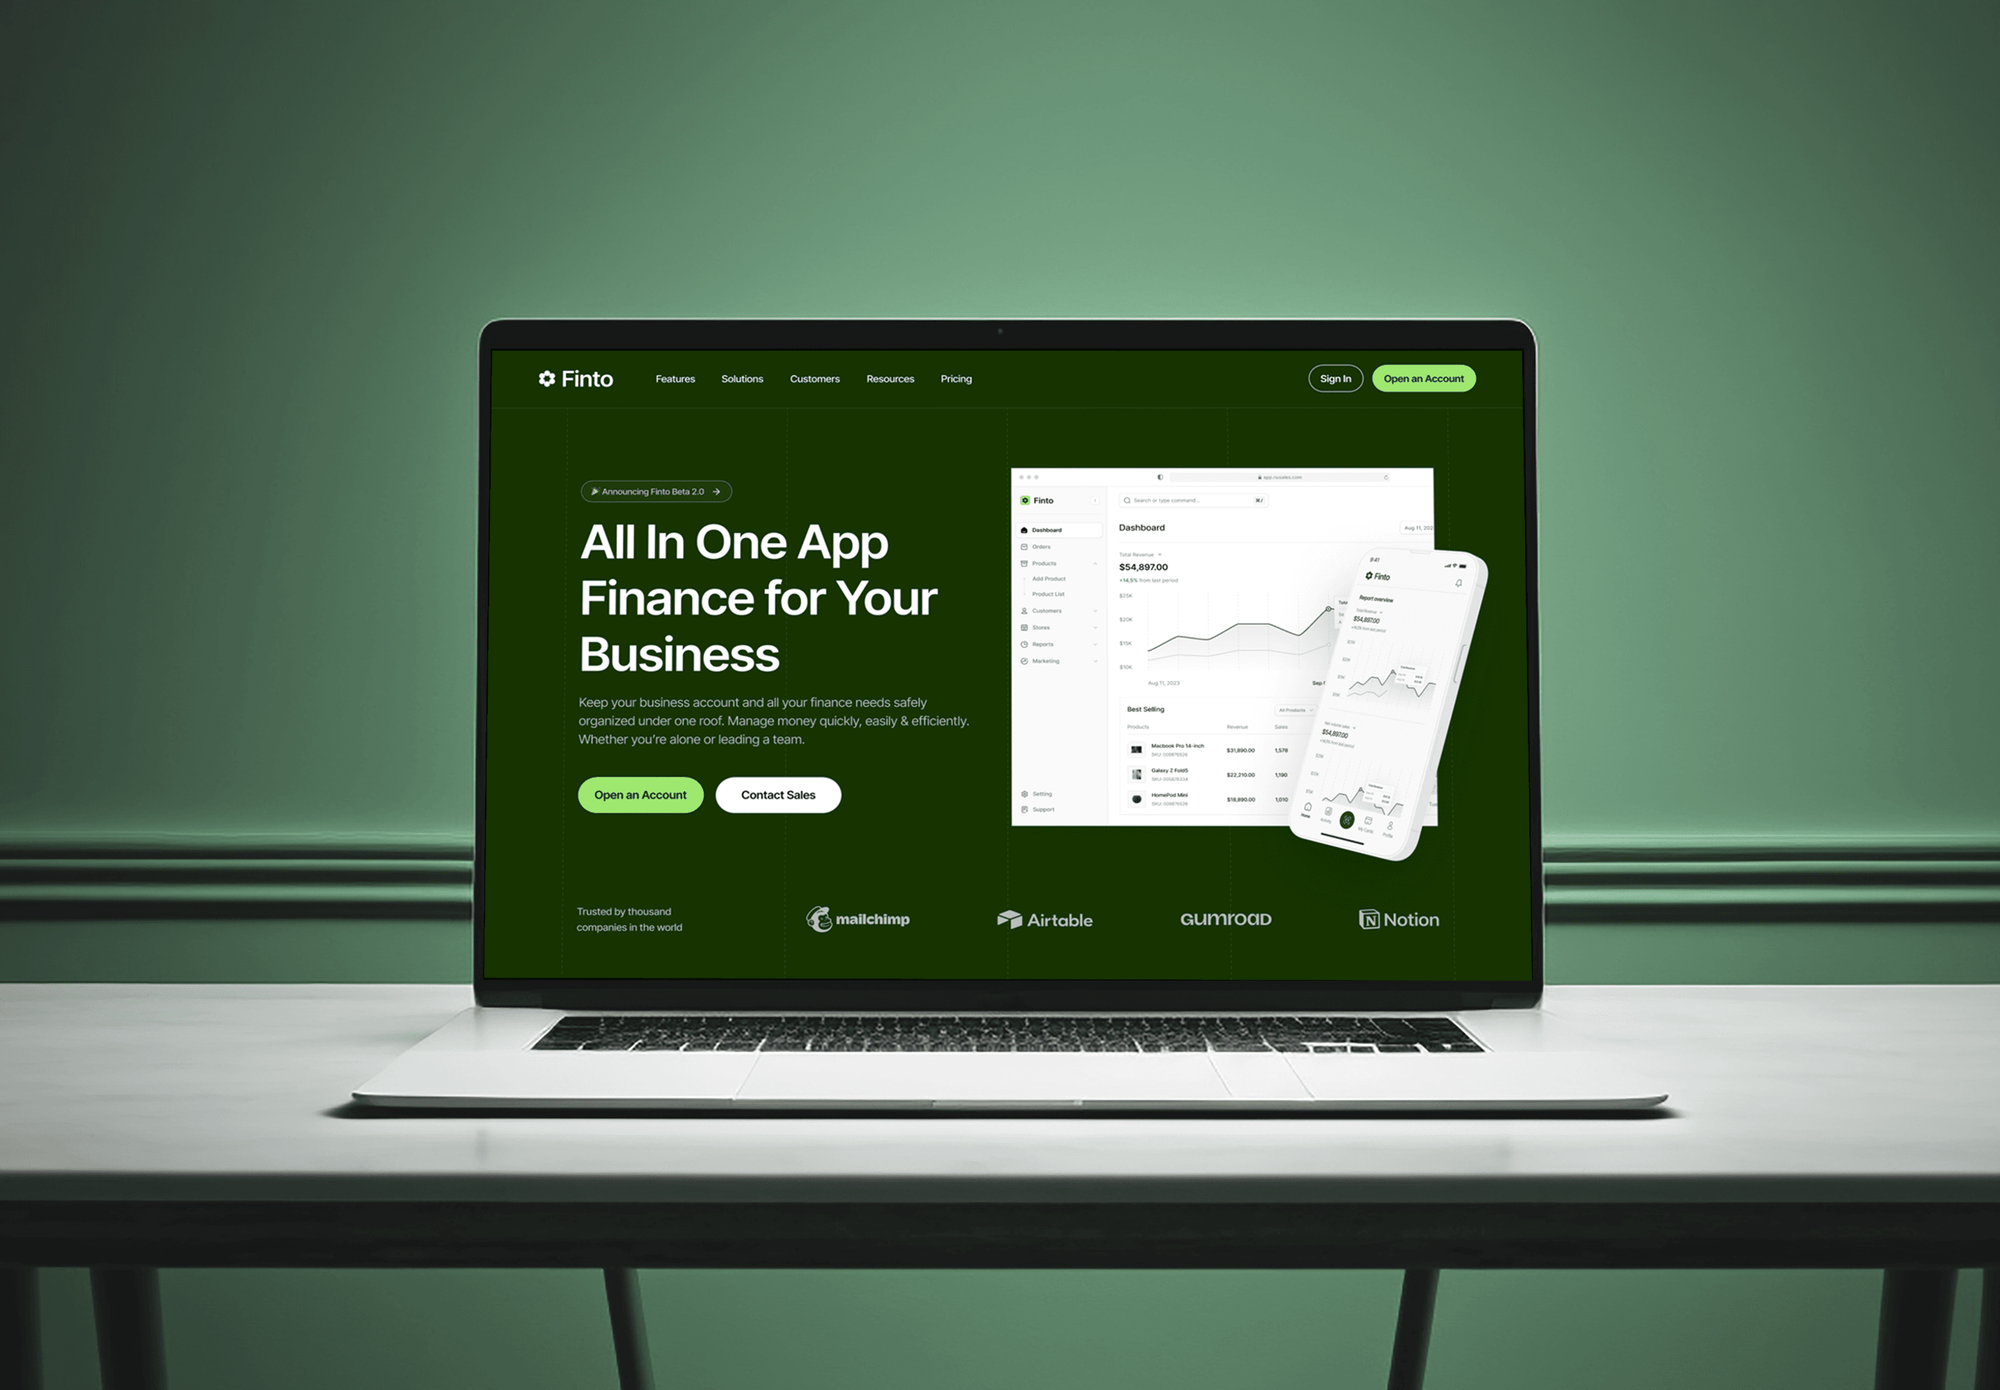
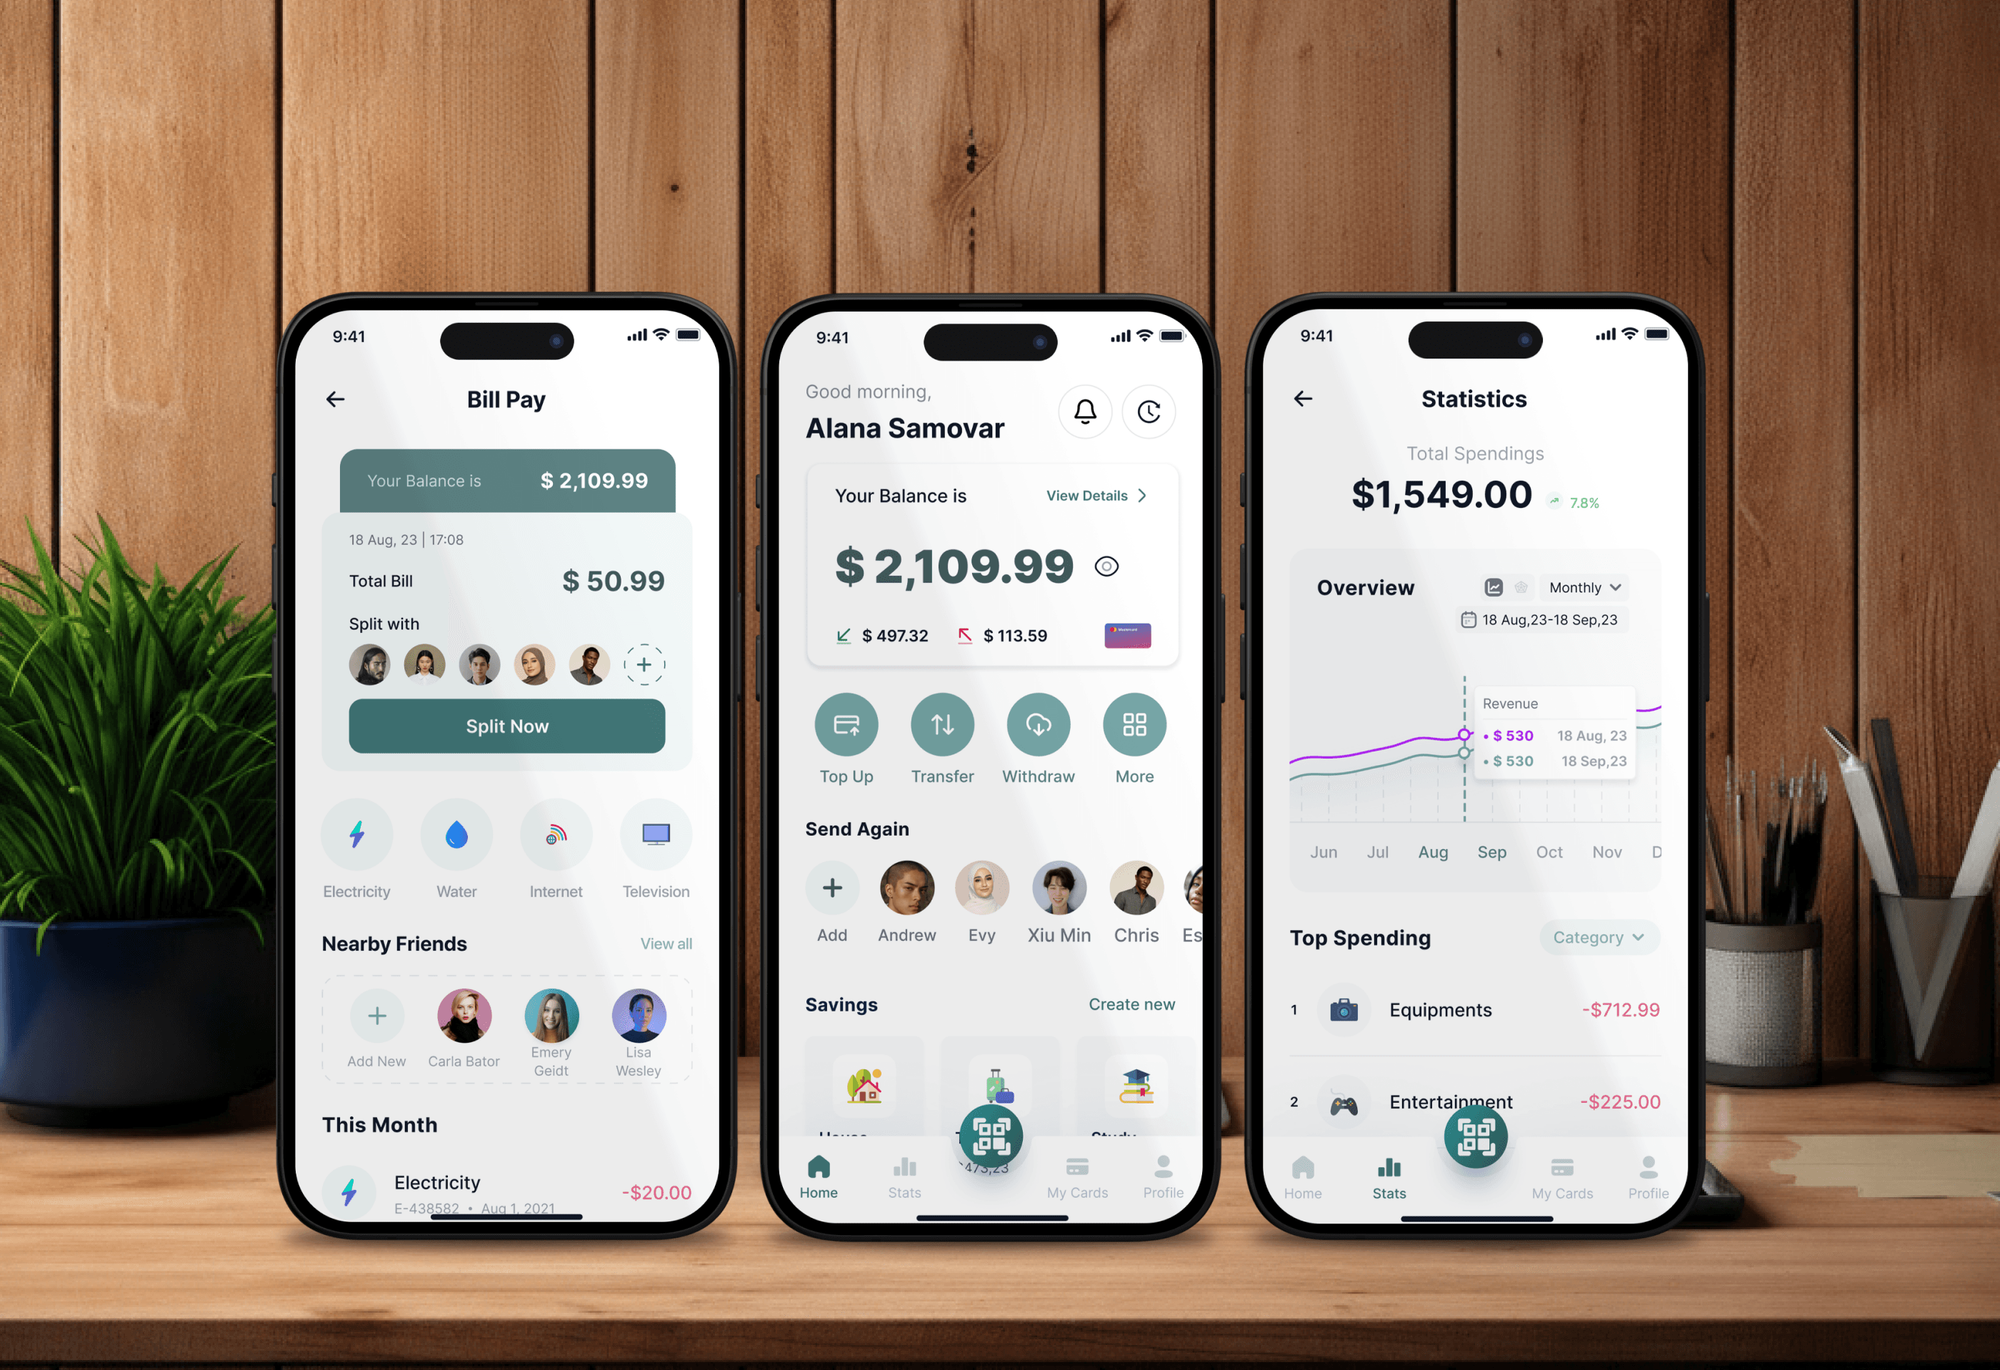
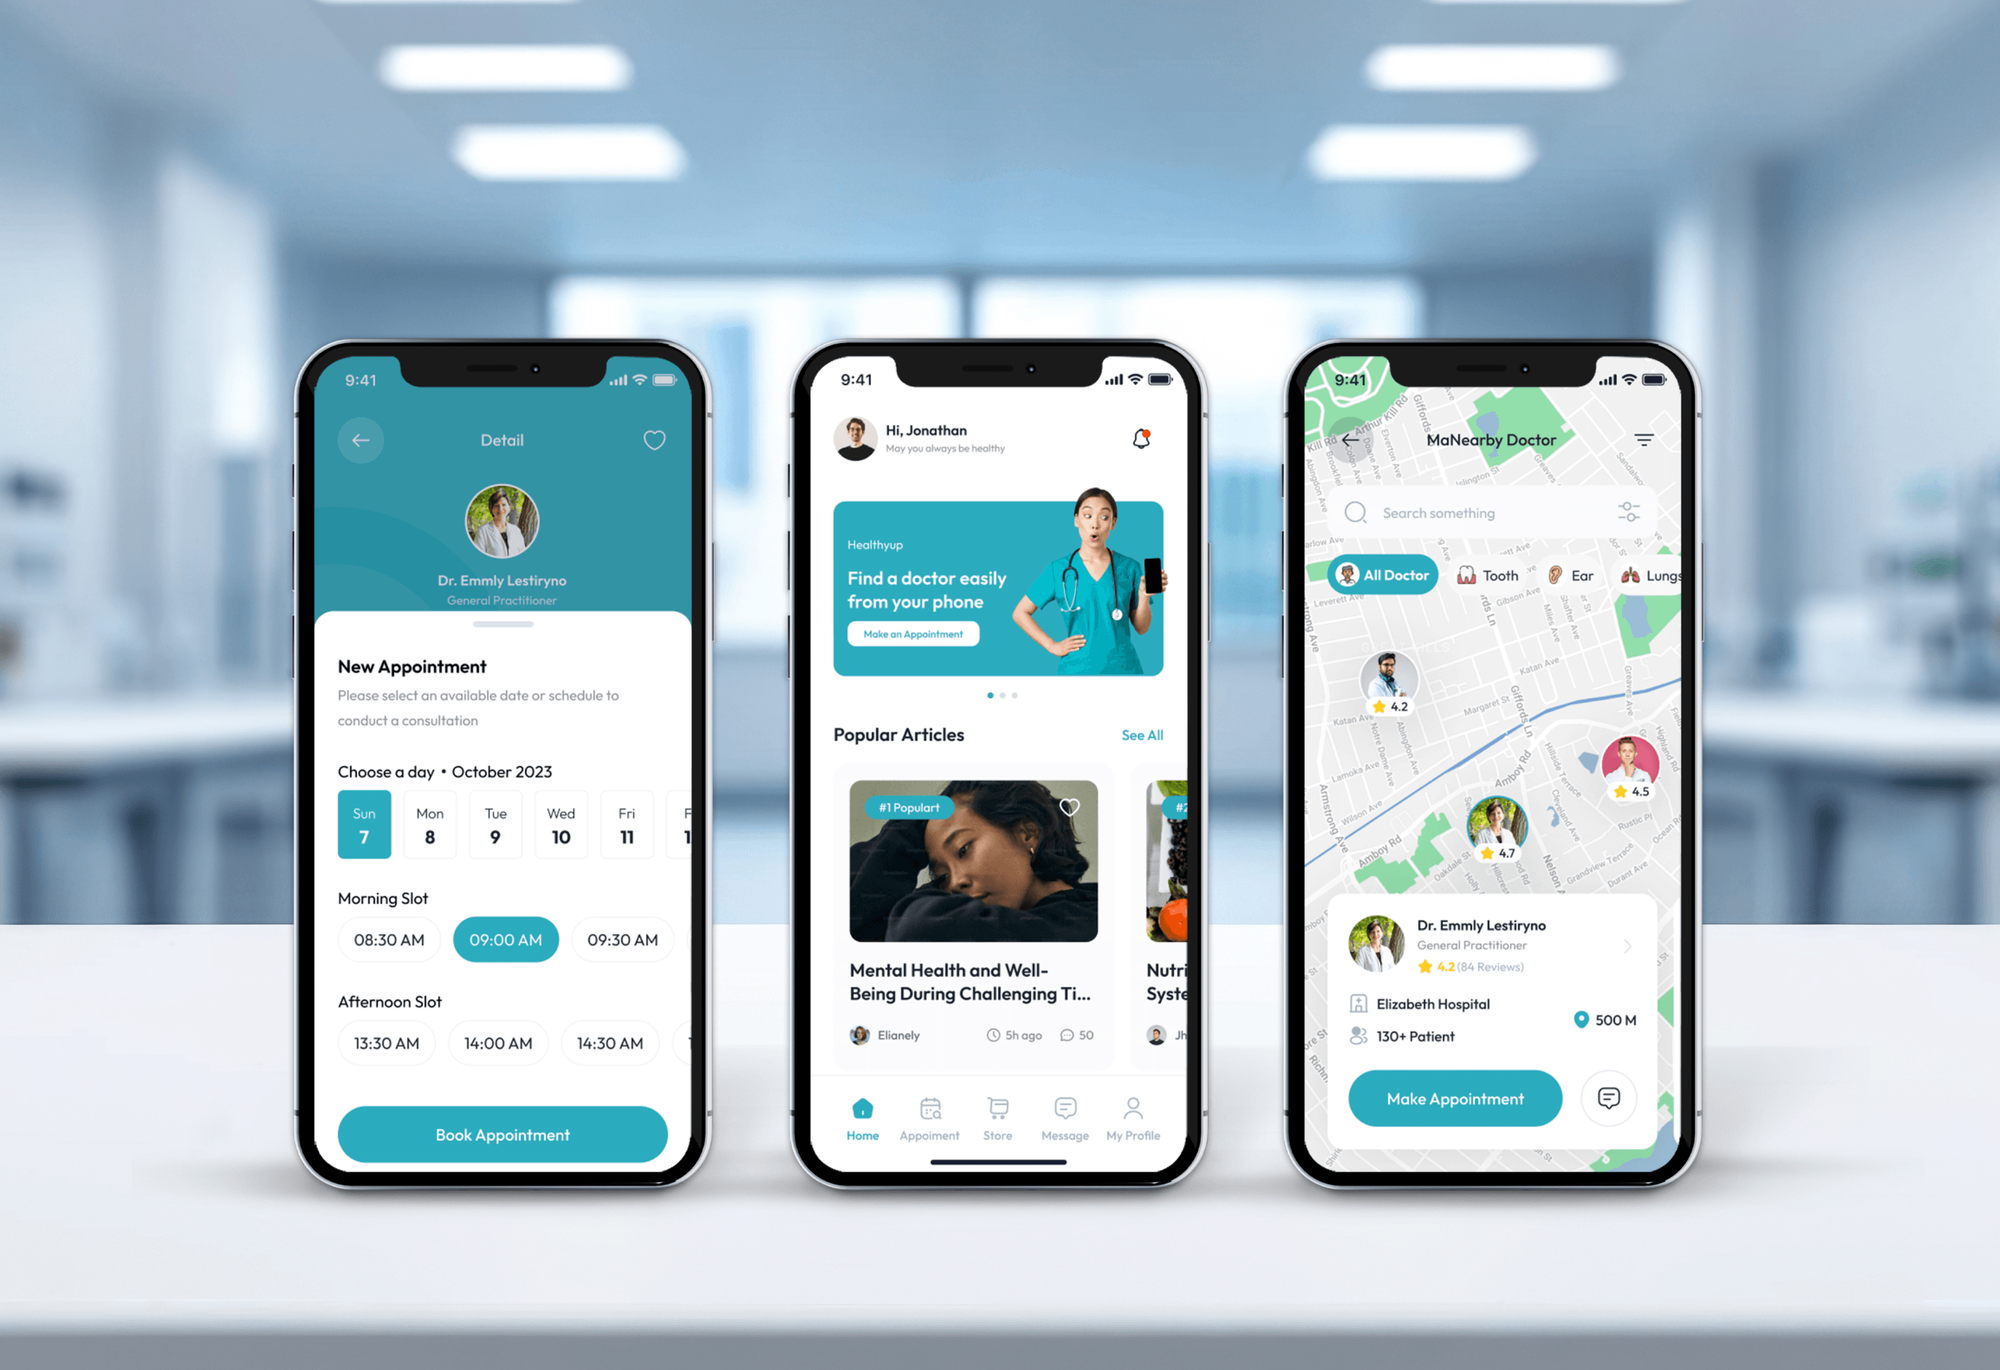
Apps and sites we built that hold personal, financial, or health data, the records a breach puts at stake. These were builds, not breach cases.
What Our Clients Say
Feedback from teams we have built websites, apps, and platforms for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A breach mixes technical work with legal stakes. These habits keep the evidence usable, the facts accurate, and the decisions with the people who should make them.
Your lawyer decides on notices and regulators. We supply the facts they ask for, in the format they need, and stay out of legal calls.
We copy logs and systems before anything changes. The FTC's breach guide warns against destroying evidence, and insurers ask for it too.
Every number in the facts summary traces back to a log line or a record. If a count is an estimate, the summary says so.
When a vendor says the hole is closed, we test it ourselves. An unverified fix is how the same leak opens twice.
Your executives get a short brief on what happened, without jargon. Counsel gets the detail, and nobody hears two different stories.
The price is set by the systems in scope after the free call. If your insurer's panel firm already covers this, we'll tell you before we quote.
Overview
DeveloperLook provides data breach response services for businesses that hold customer or staff data. We close the leak while keeping evidence, trace exposed records field by field, sort affected people by residence for your counsel, and fix the cause. Responses start from $1,200, with the leak closed in 1 to 2 days and facts in 1 to 3 weeks.
DEVELOPERLOOK
Project facts · Data Breach Response Services
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Companies with an exposed cloud bucket
Your customer export sat in a public storage bucket, and a researcher found it. You need to know who downloaded it and which fields were inside.
Clinics and practices with patient data
Your patient portal leaked records through a broken link, and HIPAA questions are coming. You need the scope traced so counsel can assess the breach.
Stores whose checkout data leaked
Your bank flagged cards used at your store, and you suspect the checkout. You need data breach detection and response that finds the leak and its dates.
Firms with a breached vendor
Your payroll or CRM vendor reported a breach that includes your staff or clients. You need breach response services that test their claims and scope your exposure.
MSPs supporting a client's breach
Your client's data was exposed, and their counsel wants technical facts fast. You want a team that works under your name and speaks counsel's language.
Not a fit
Attack still in progress
An attacker is active in your network, and nothing is known to be exposed yet. Our incident response team contains the attack first.
Legal advice on notice
You need someone to decide whether you must notify customers or regulators. That decision belongs to a breach lawyer, and we work alongside one.
Court-grade evidence only
You need forensic copies and a chain of custody for a lawsuit or HR case. Our digital forensics service is built for that.
Planning before any breach
Nothing has been exposed, and you want a written plan and drills. Our incident response plan development service is the better fit.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on how many systems held the data and how far back logs go, and you get a fixed proposal after a free breach call.
For Agencies
You own the client relationship. We supply the breach engineers: containment that keeps evidence, record-level scoping, and the facts summary counsel needs. Your client hears from you, and your team keeps the rest of your clients running.
White label: your client only ever sees your brand
Send what leaked, from where, and the access you already hold.
You get containment steps, a scope plan, and a fixed price.
We contain and trace, then hand the facts over under your name.
Send what leaked, from where, and the access you already hold.
You get containment steps, a scope plan, and a fixed price.
We contain and trace, then hand the facts over under your name.
The Right Technology for Your Project
We work from the logs your systems already keep, plus a few open tools, so every number in the summary can be traced.
 AWS
 Microsoft Azure
 Google Cloud
 MySQL
 Python
 Google Sheets
 Slack
Related Services
Breach response settles what was exposed. These services handle live attacks, court-grade evidence, written plans, and watching for leaked credentials afterward.
This page
Data Breach Response Services
Pairs with the 6 services around it
FAQ
Straight answers on cost, timing, who to report to, responsibility, and building a response plan.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Responses start at $1,200 for a leak from one system, with containment, record tracing, and a facts summary. Breaches across up to 3 systems or a vendor start at $3,300, and larger responses with a written plan and drill start at $6,100. You get a fixed price after the free breach call.
We usually close the leak within 1 to 2 days and deliver the facts in 1 to 3 weeks. Legal clocks run separately. GDPR gives 72 hours to tell the regulator once you're aware, HIPAA allows up to 60 days for notices to people, and US state laws vary. Your counsel decides which deadlines apply.
It's the work a business does after personal data is exposed. That means containing the leak, learning what was taken and whose, fixing the cause, and meeting any notice duties. The FTC's guide for businesses splits it into securing operations, fixing vulnerabilities, and notifying the right parties. We handle the technical parts and support counsel on the rest.
In order: contain, preserve, investigate, fix, then notify as counsel advises. The common mistakes are fixing before saving logs, guessing at scope, and making public statements before the facts are known. The FTC's guide also warns against misleading statements, so we keep one facts summary that every team works from.
It depends on the data and where affected people live, so your counsel makes the final list. Common recipients are the people affected, state attorneys general, and regulators such as HHS for health data or the ICO in the UK. The FTC's guide also advises calling local police, or the FBI, right away.
Under most breach notice laws, the business that owns the data has to notify, even when a vendor caused the breach. Vendors that only hold the data usually must tell that business. Liability for costs is a separate question for your lawyer and your contracts, and we document the technical cause so they can answer it.
Companies are expected to protect the personal data they hold, and regulators can act when security was unreasonable. In the US, the FTC has brought cases against companies over weak data security, and many states require reasonable safeguards. Whether your company is at fault in a given breach is a legal question, so we stick to the technical facts.
It's a short document naming who leads, who to call, what to preserve, and how decisions get made when personal data leaks. It sits inside your wider incident planning and focuses on records, notices, and regulators. Our Response and Readiness plan writes one with you after an incident.
Start by mapping where personal data lives, then name a response lead, your counsel, your insurer, and a technical team. Write the first-hour steps: contain, preserve logs, and don't wipe machines. Then test it with a tabletop drill, because a plan nobody has rehearsed tends to fail on the first real call.
The best provider contains the leak without destroying evidence, traces records to the field, and works under your counsel. Ask how they preserve logs, how they count affected people, and whether insurers have accepted their reports before. If your cyber insurer has a panel firm, start there, and we'll work alongside them.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.