Read-only collection
Disk images and triage collections taken without changing the original device or account.

For owners, HR leads, and counsel who need facts, not guesses: we collect evidence without changing it, rebuild the timeline, and report what we can prove. From $1,050.
SHA-256
Hash on every evidence copy
1:1
Copies made, originals untouched
How your project runs
01 · FreeTeams we have built for:














The Problem
The question usually comes after the dust settles: did the former employee take the client list, which records did the attacker open, and when did it start?
Browsing first
IT opens files and changes the timestamps you need.
Browsing first
Devices are copied read-only before anyone looks at a single file.
No custody
Nobody can say who handled the laptop or when.
No custody
Every handoff, hash, and storage move goes into a chain-of-custody log.
Scattered logs
Device records and cloud logs sit in separate places.
Scattered logs
File, browser, USB, and cloud audit records merged into one timeline.
Opinion reports
Conclusions rest on someone's impression, not on records.
Opinion reports
Each finding points to the evidence item and record that supports it.
A sales manager resigns, and a week later a competitor calls your best clients. Or your insurer asks which records an attacker opened before you reset everything. Your IT person logs in to look around, opens files, and runs a few tools. Every click changes timestamps and can overwrite deleted data. By the time anyone writes a report, the evidence can't show what happened first, and the other side's lawyer will say so.
We start by collecting, not browsing. Laptops, servers, and cloud accounts are copied read-only, each copy gets a SHA-256 hash, and every handoff goes into a chain-of-custody log. Then we rebuild the timeline from file system records, browser history, USB logs, and cloud audit trails. You get findings tied to specific evidence. Each conclusion points to its source, not to an opinion.
Copies, not the original
We work on hashed forensic copies, so the original device stays exactly as it was.
Chain of custody kept
Every handoff, hash, and storage move is logged with a name, a date, and a time.
A timeline you can follow
Events from devices and cloud logs merged into one dated sequence anyone can read.
Our Digital Forensics Services Process
You agree the questions up front, see what we collect and how, and get findings tied to evidence. Nothing is analyzed on the original device.
We agree the questions the investigation must answer, which devices and accounts hold the answers, and who may authorize collection. If the matter may reach court, we flag it here, because licensing and expert rules then apply.
What's Included
Read-only collection, hashed copies, a custody log, analysis across devices and cloud accounts, and a report that ties every finding to its evidence.
Compare Options
Your IT team knows the systems, and litigation firms bring examiners who testify. Here is where each one fits a business investigation.
| Feature | DeveloperLookBest fit | In-house IT | Litigation firm |
|---|---|---|---|
| Evidence collection | Read-only, hashed, and logged | Often browsed directly | Read-only, hashed, and logged |
| Chain of custody | Kept from the first copy | Rarely kept | Kept to court standards |
| Expert testimony | |||
| Cloud account review | Partial, through admin consoles | ||
| Memory analysis | Included on larger plans | Not usually | |
| Time to start | Scoping call, then days | Immediate, already inside | Depends on engagement terms |
| Report style | Plain English for decisions | Informal notes | Formal expert report |
| Cost predictability | Fixed price from $1,050 | Staff time only | Hourly, the highest rates |
Projects We've Built
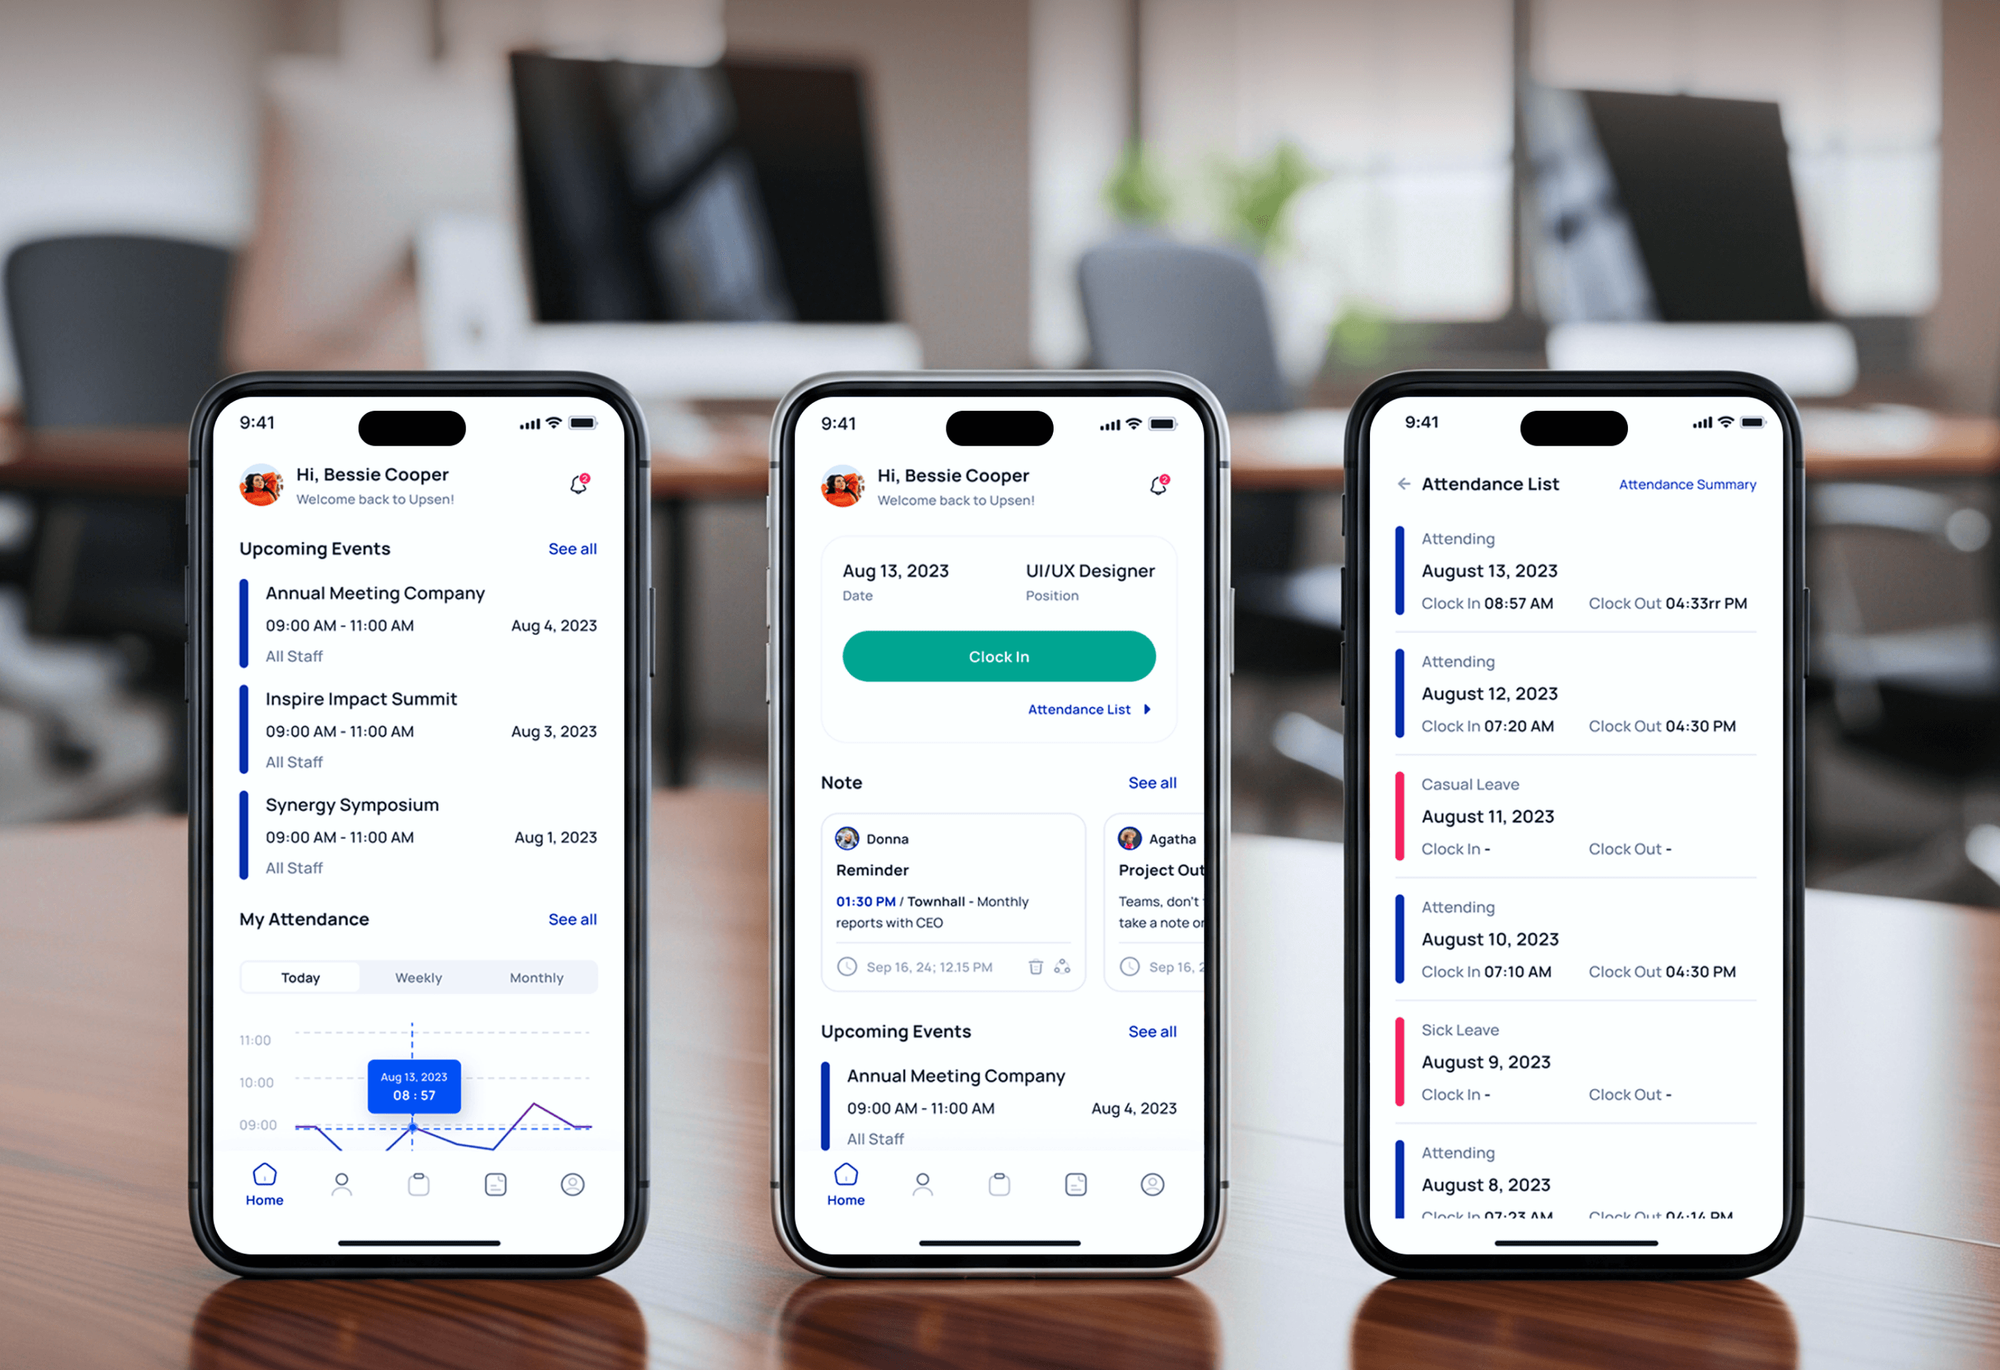
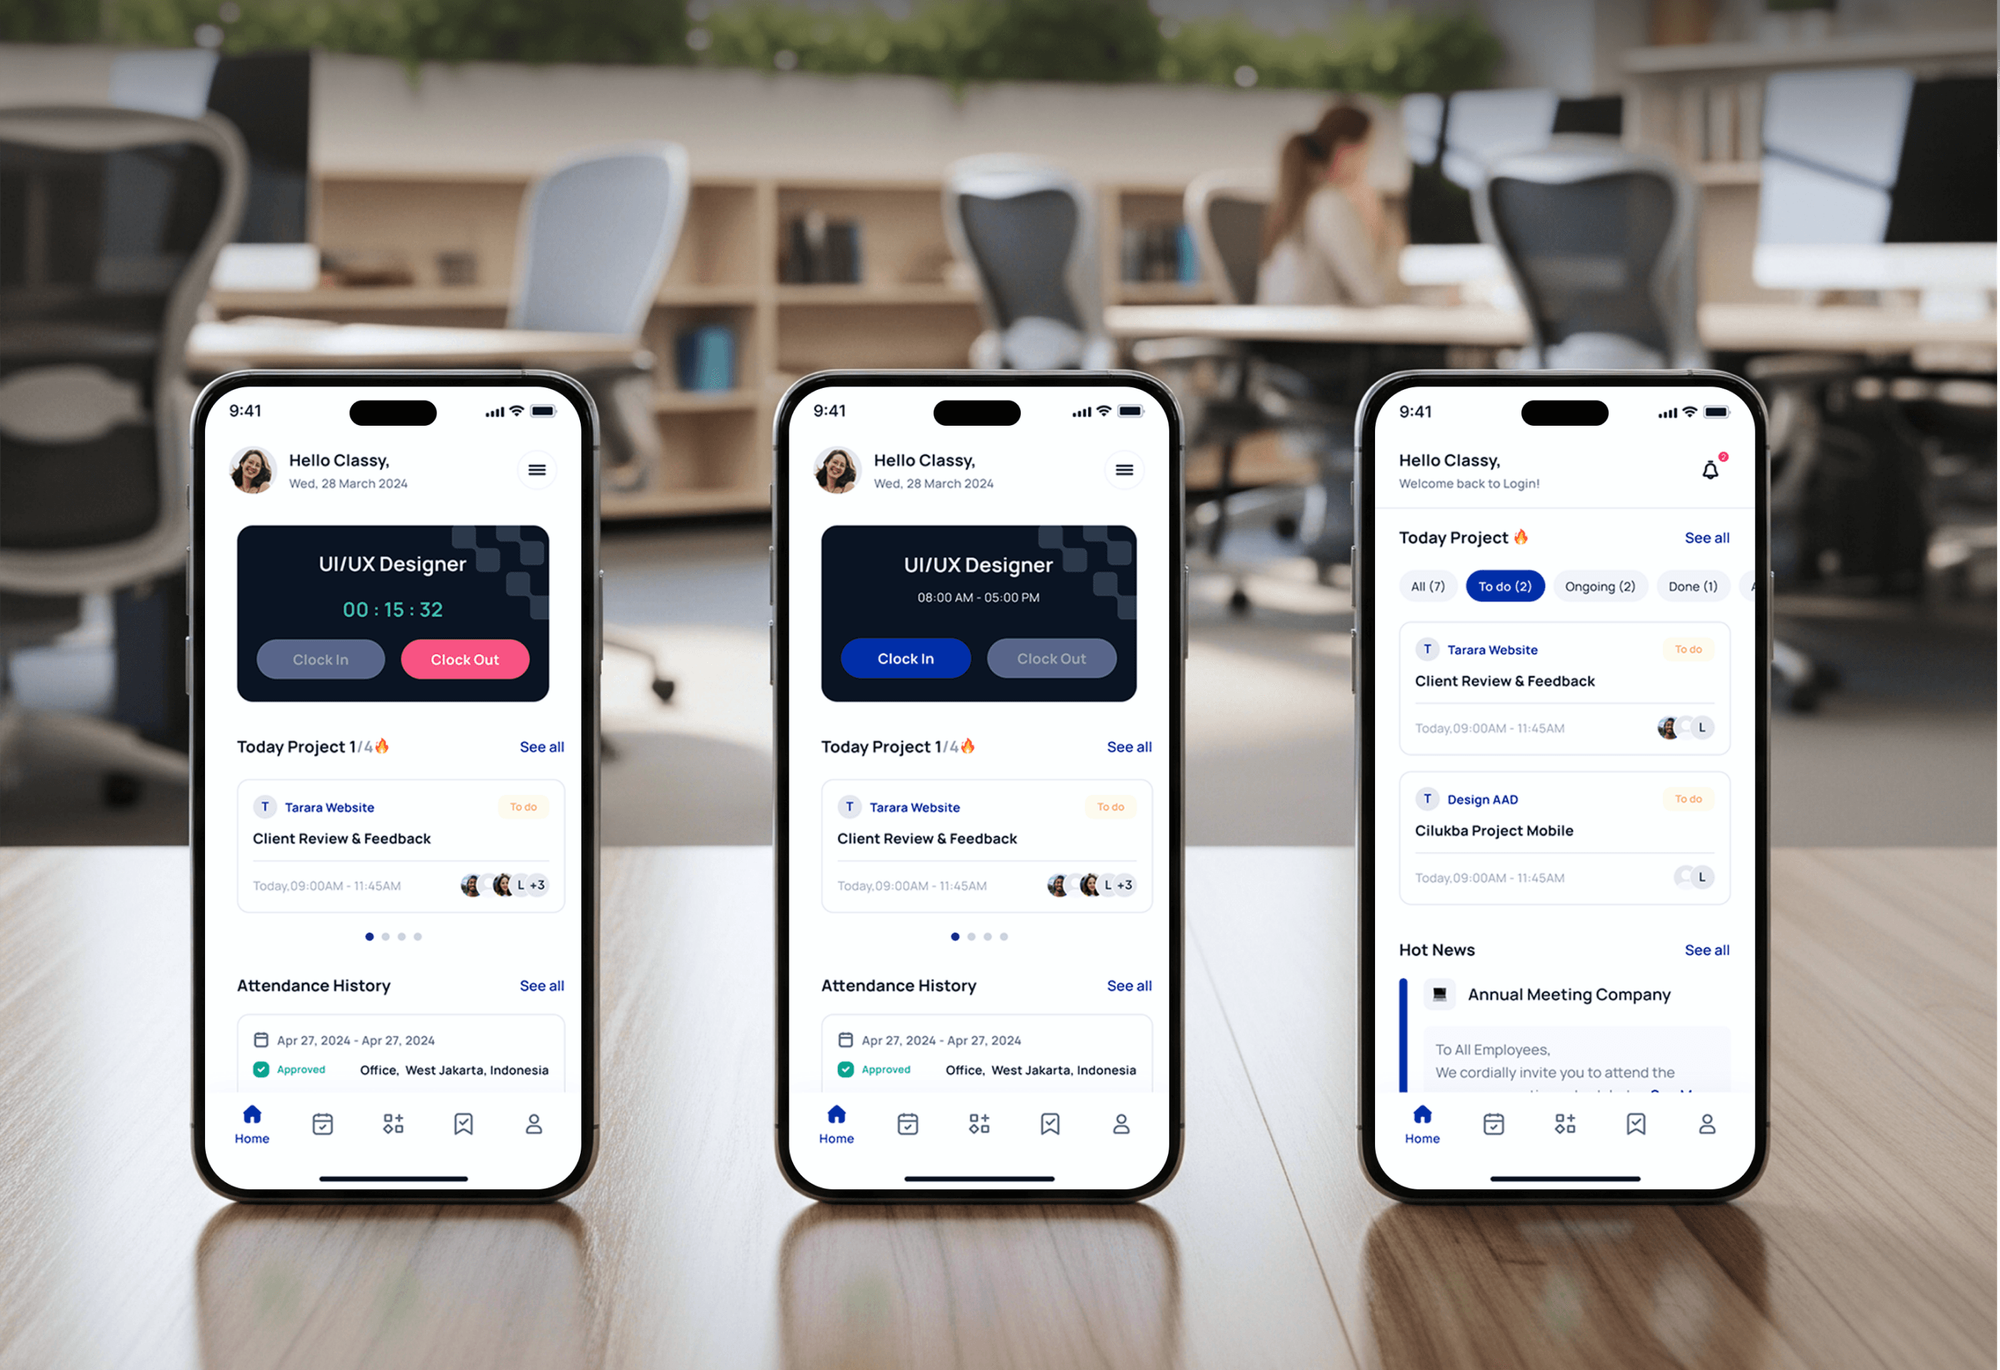
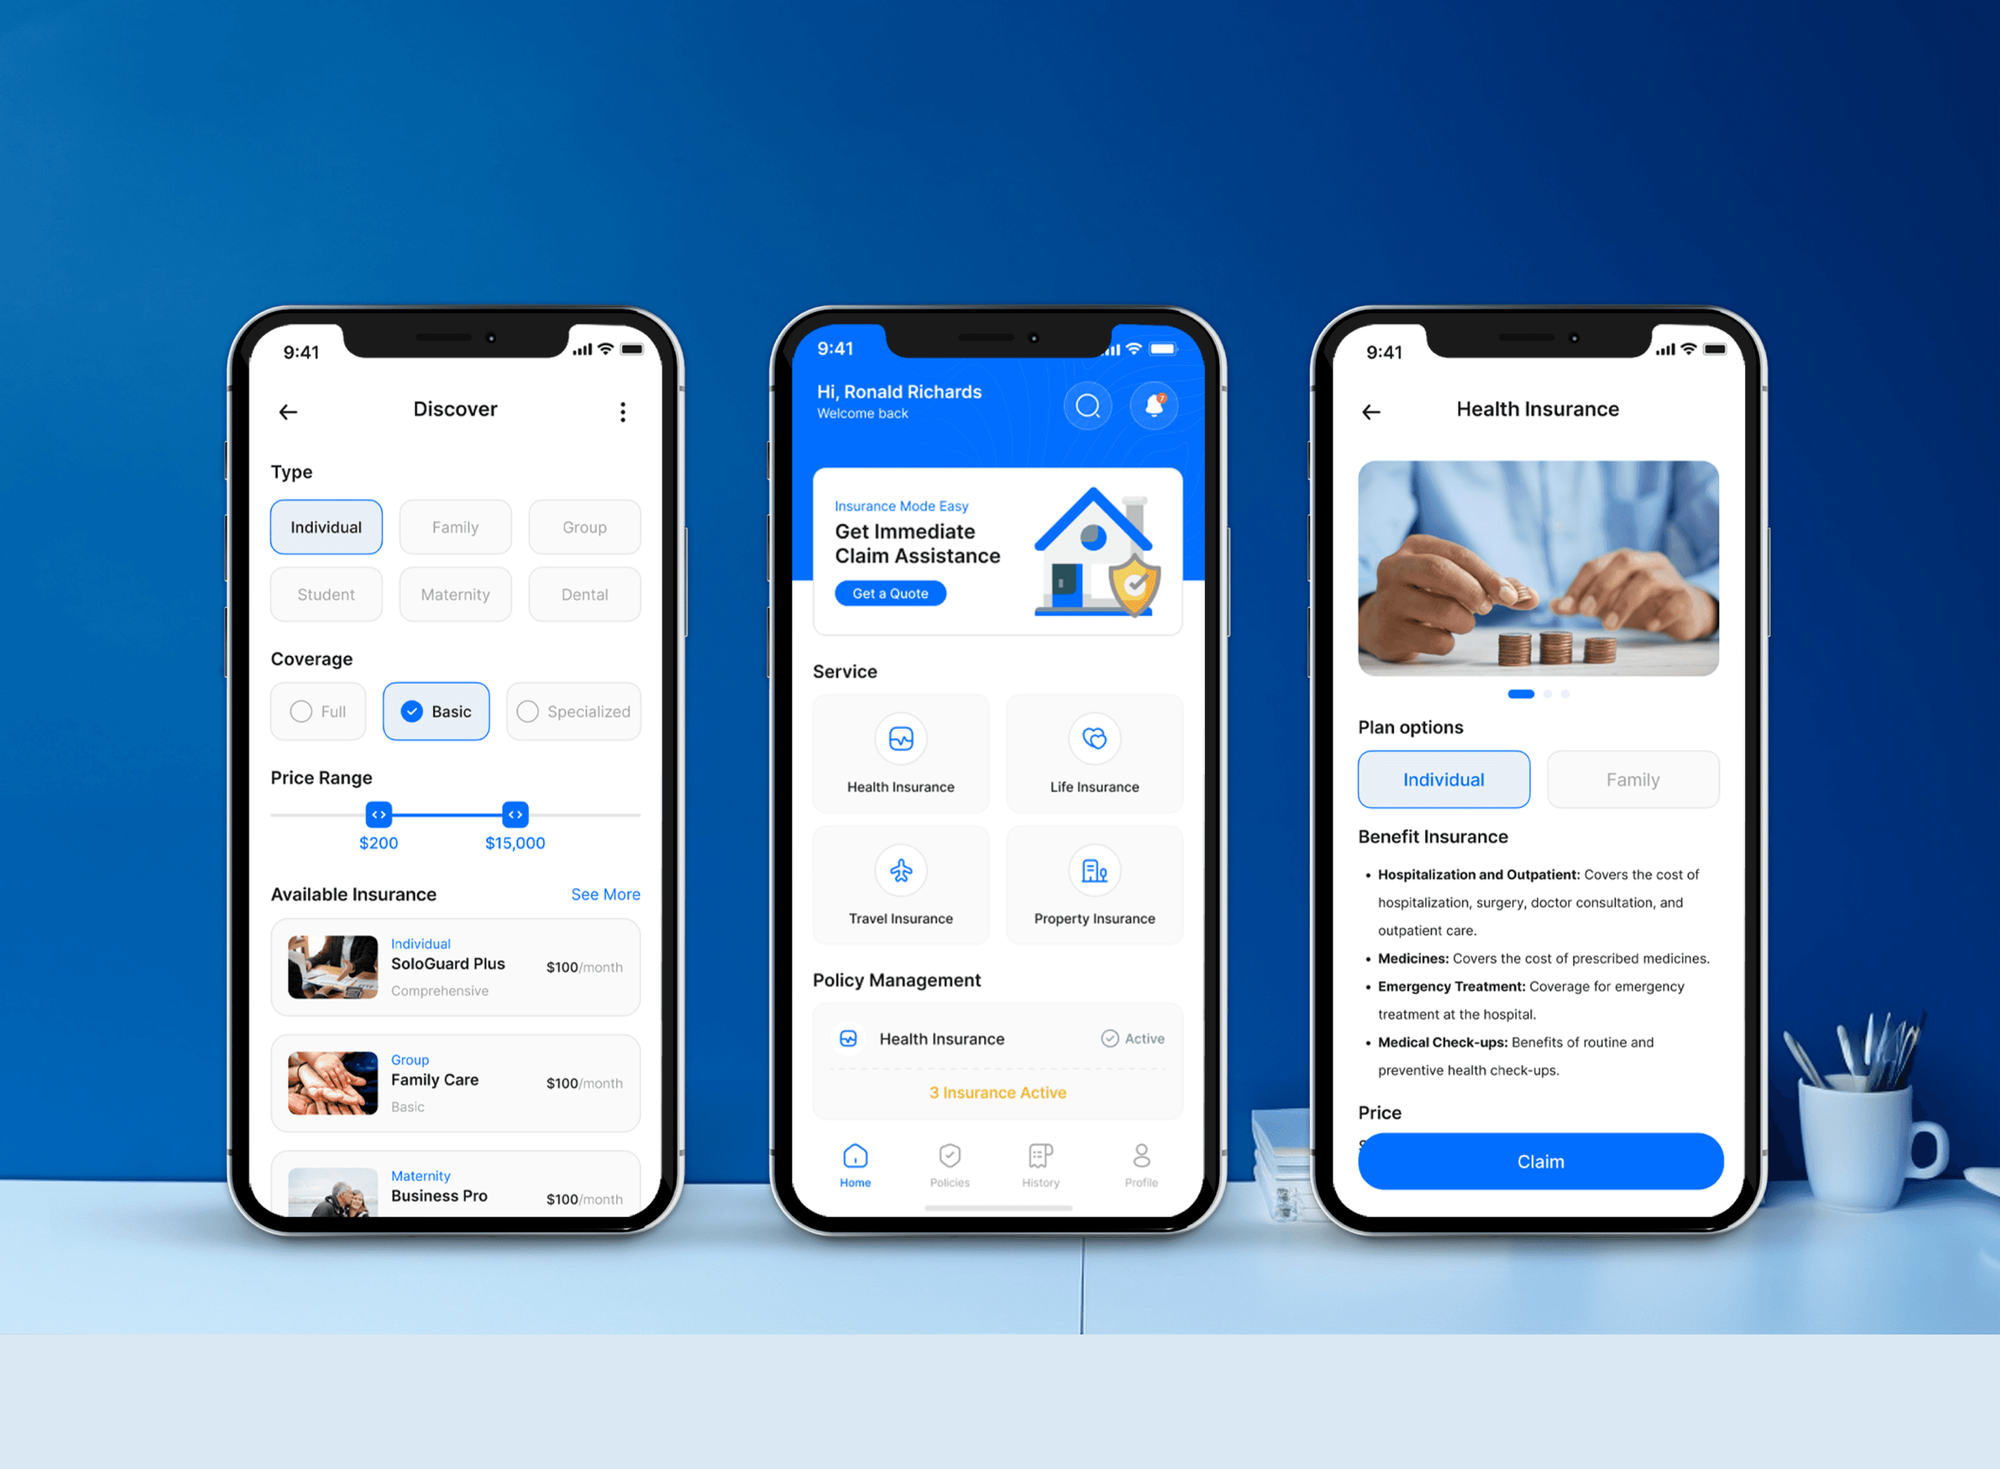
Platforms we built for HR, recruiting, and insurance teams that hold sensitive records worth protecting. These are builds, not forensic cases.
What Our Clients Say
Feedback from teams we have built websites, apps, and platforms for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Forensic work is only as good as its handling. These habits keep the evidence clean and the findings honest, even when the answer isn't the one you hoped for.
We work on copies and leave the original device sealed after collection. If anyone challenges the findings, it can be copied again and checked against our hash.
We report what the records show and how sure we are. Whether that adds up to misconduct or a breach is for you and your counsel to decide.
We don't give expert witness testimony. If your matter is heading to court, we say so on the first call and point you to the right specialist.
Copies sit in encrypted storage, open only to the examiner on your case. At the end, you choose handover or verified deletion.
You hear what we've found as it firms up, not only at the end. That lets you make HR or legal moves while the facts are fresh.
The price is set by the questions and the number of sources, agreed before collection. New questions get a new quote, not a surprise invoice.
Overview
DeveloperLook provides digital forensics services for business investigations: insider data theft, account misuse, and the evidence side of security incidents. We collect read-only, hash every copy, keep a chain-of-custody log, and report findings tied to evidence. Work starts from $1,050, and most cases take 1 to 6 weeks.
DEVELOPERLOOK
Project facts · Digital Forensics Services
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Companies with a departing employee
Your sales manager resigned and a competitor now calls your clients. You need to know whether files went to USB, cloud storage, or personal email.
Businesses after a security incident
Your systems are back up, but your insurer wants to know which records the attacker opened. You need the evidence half of digital forensics and incident response.
HR teams investigating account misuse
Your HR team received a complaint about a manager's account activity. You need digital forensics experts who report the facts neutrally, without taking sides.
Counsel who need facts early
Your counsel needs to know what happened before deciding whether to notify or sue. You want cyber forensics services that document how evidence was handled.
MSPs without forensic staff
Your client wants a proper investigation, and your team hasn't imaged a drive under custody rules before. You want an examiner who works under your brand.
Not a fit
Court testimony needed
You need an expert to testify in court or sign a sworn report. We don't offer that, so your counsel should engage a litigation forensics firm.
Attack still underway
The attacker is still active in your systems. Our incident response services contain it first, and forensic work follows once things are stable.
Personal or family matters
You want a spouse's phone or a personal device examined. We only work on business-owned systems with proper written authorization.
Mailbox fraud only
One mailbox sent fake invoices, and you need it locked and traced fast. Our business email compromise response service is built for that case.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the number of devices and accounts and the questions you need answered, and you get a fixed proposal after a free scoping call.
For Agencies
You own the client relationship. We supply the examiner: collection steps for your technicians, hashed copies, a custody log, and a findings report in your format. Your client gets a proper investigation without you hiring forensic staff.
White label: your client only ever sees your brand
Send what the client needs answered and which devices are involved.
You get collection steps, a custody form, and a fixed price.
We examine the copies and deliver the findings under your brand.
Send what the client needs answered and which devices are involved.
You get collection steps, a custody form, and a fixed price.
We examine the copies and deliver the findings under your brand.
The Right Technology for Your Project
We use open, widely documented forensic tools, so another examiner can repeat our steps and check our results.
 AWS CloudTrail
Related Services
Forensics answers what happened. These services stop what's still happening, handle the special cases, and look for attackers you haven't found yet.
This page
Digital Forensics Services
Pairs with the 6 services around it
FAQ
Straight answers on cost, timing, chain of custody, remote collection, and when you need a licensed examiner.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Digital forensics services start at $1,050 for one laptop, server, or cloud account with a focused question. Investigations across up to 5 devices or accounts start at $3,100, and full incident forensics across up to 15 sources starts at $6,400. You get a fixed price after a free scoping call, set by sources and questions.
One device usually takes 1 to 2 weeks from collection to report. Cases across several devices and cloud accounts take 3 to 6 weeks, mostly because timelines from different sources must be merged and checked by hand. Urgent questions, such as whether a file left the company, can be answered first.
It's the practice of finding out what happened on a computer or account using records that can be checked later. The rules are about handling: copy without changing anything, hash every copy, and log every handoff. The analysis then rebuilds who did what, when, and from which device or account.
Because decisions after an incident or a departure need facts that hold up. Without forensic handling, timestamps change and deleted data is overwritten the moment someone looks around. With it, you can show an insurer which records were touched, or show HR exactly when files were copied, and defend that finding.
In cyber security, it's the evidence side of an attack: how the attacker got in, what they ran, and which data they reached. The work uses memory captures, endpoint logs, and cloud audit trails. Those findings feed containment, insurance claims, and the decision on whether breach notification is needed.
DFIR joins two jobs: incident response stops the attack and restores systems, and forensics proves what happened. In a live case they run side by side, because containment choices decide what evidence survives. We do the forensic half here; our incident response page covers containment and recovery.
Start with what the findings are for. For internal decisions, insurers, or counsel's fact-finding, a business examiner like DeveloperLook fits; for court testimony, your counsel should engage a firm whose examiners testify. Ask any digital forensics companies you compare how they hash evidence, keep custody, and which tools they use.
Yes, for business-owned devices and accounts you're authorized to examine. Our digital forensic services cover insider cases, account misuse, and incident evidence. In some US states, forensic work for a lawsuit counts as private investigation and needs a licensed investigator. We check your state's rules before taking litigation-related work.
Chain of custody is the written record of who collected, handled, moved, and stored each piece of evidence, and when. Paired with a SHA-256 hash taken at collection, it shows the evidence wasn't altered along the way. Without it, the other side can challenge every finding, however accurate it is.
Yes, for most business cases. Velociraptor and KAPE collect the key records from Windows, macOS, and Linux machines over the network, and cloud logs come through admin APIs. Full disk images can be taken by your IT with a write blocker and our instructions, then uploaded encrypted.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.