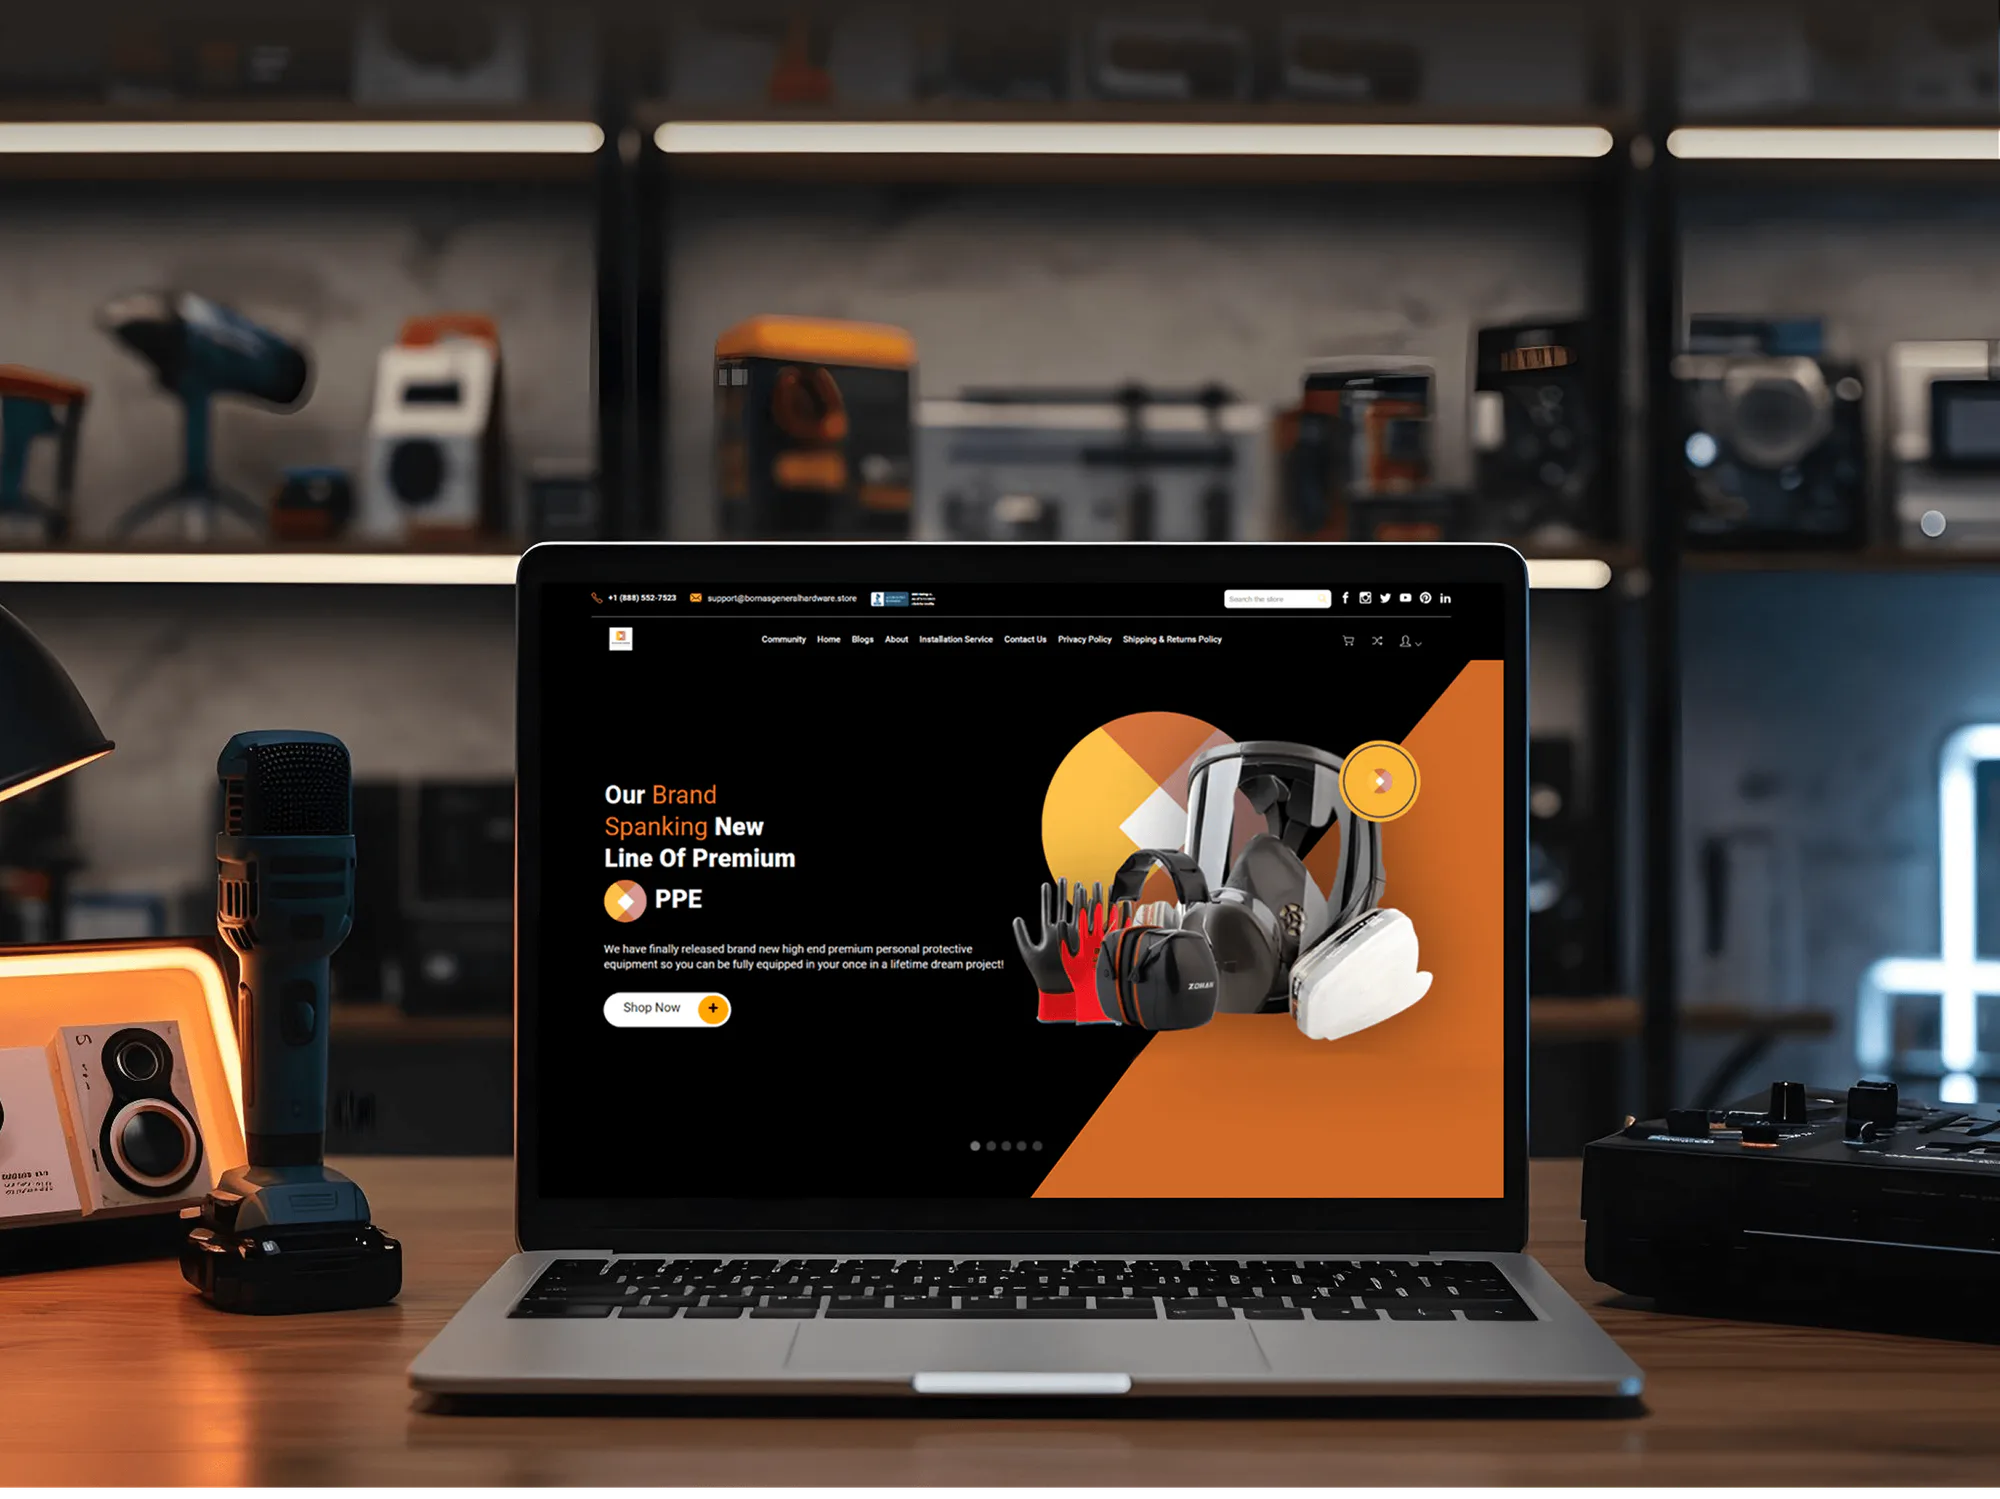
Borna's General Hardware Ecommerce Website
- Retail
- E-commerce
- Website

For online stores with years of staff logins, apps, and checkout scripts: we lock down access, watch your checkout for changes, and slow card testing. From $950.
100%
Staff logins on two-step verification
30days
Of checkout script change alerts
How your project runs
01 · FreeIndustry leaders we work with
 Shopify
 WooCommerce
 BigCommerce
 Magento
 Stripe
 PayPal
 Braintree
 Cloudflare
 AWS
 OWASP
 Burp Suite
 Chrome DevTools
The Problem
It shows up when your payment provider flags card testing, a customer reports a strange charge, or an old app still reads your orders.
Old access
Former staff and agencies still hold admin logins.
Old access
Every account is reviewed, then protected with two-step verification or removed.
Card testing
Bots test stolen cards on your checkout overnight.
Card testing
Rate limits, bot challenges, and gateway rules stop repeat attempts from one source.
Cart scripts
Nobody knows which scripts run on the cart page.
Cart scripts
Each cart and checkout script gets an owner and a change alert.
App access
Apps you uninstalled can still read your orders.
App access
App permissions and API keys are checked, trimmed, or revoked.
Your store still has staff logins for people who left, and an agency you stopped paying keeps admin access. A long list of apps can read your orders and customers. Then your payment provider emails about hundreds of small declined charges overnight: someone used your checkout to test stolen cards. A week later, a customer asks why their card was used somewhere else after buying from you. Nobody can say which scripts load on your cart page, or who added them.
We start with the five ways into a store: staff access, apps, checkout scripts, payment settings, and customer data. Every staff login gets two-step verification, and old access comes out. Each script on your cart and checkout pages gets an owner and a change alert. Card testing meets rate limits and gateway rules. The next stolen card hits a limit on your checkout, not your payment account.
Every login has an owner
Staff, agency, and app access is listed, trimmed, and protected with two-step verification.
Checkout scripts under watch
Scripts on cart and payment pages get owners, and any change sends an alert to our team.
Card testing slowed at checkout
Rate limits, bot challenges, and gateway rules make stolen card runs fail fast.
Our Ecommerce Security Services Process
You see the access list, the script list, and every fix before it goes live, and you approve each change to staff logins and payment settings.
We look at your platform, plan, apps, and checkout from the outside, then ask a few questions about staff and payments. You get a risk note and a fixed price. If your platform's built-in settings already cover a small store, we'll tell you before we quote.
Projects We've Built
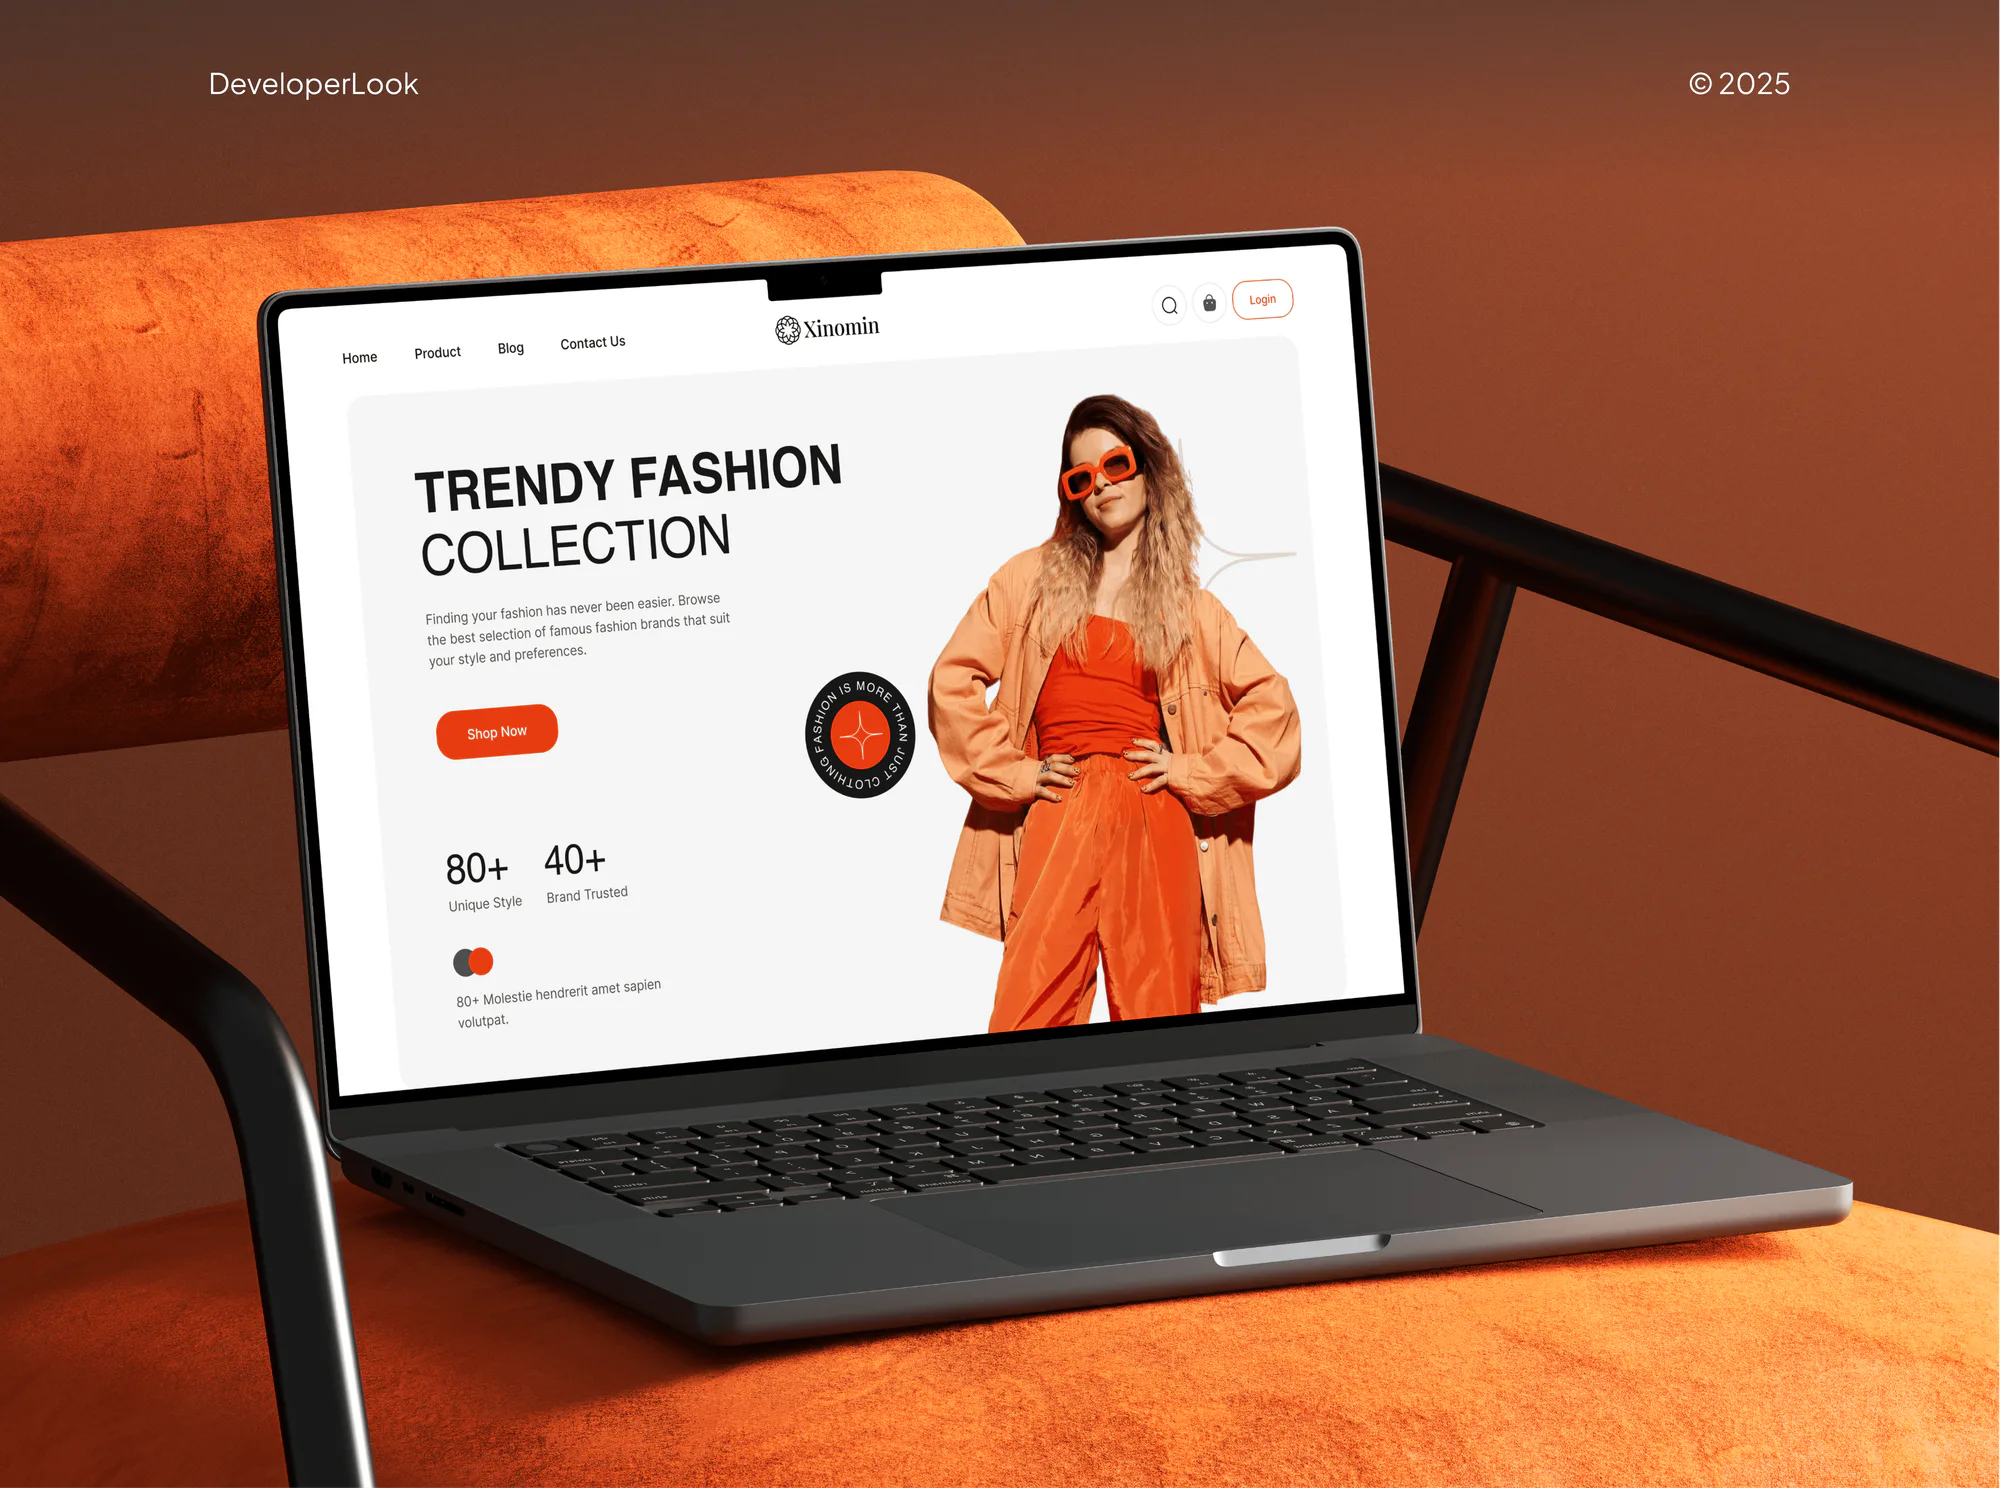
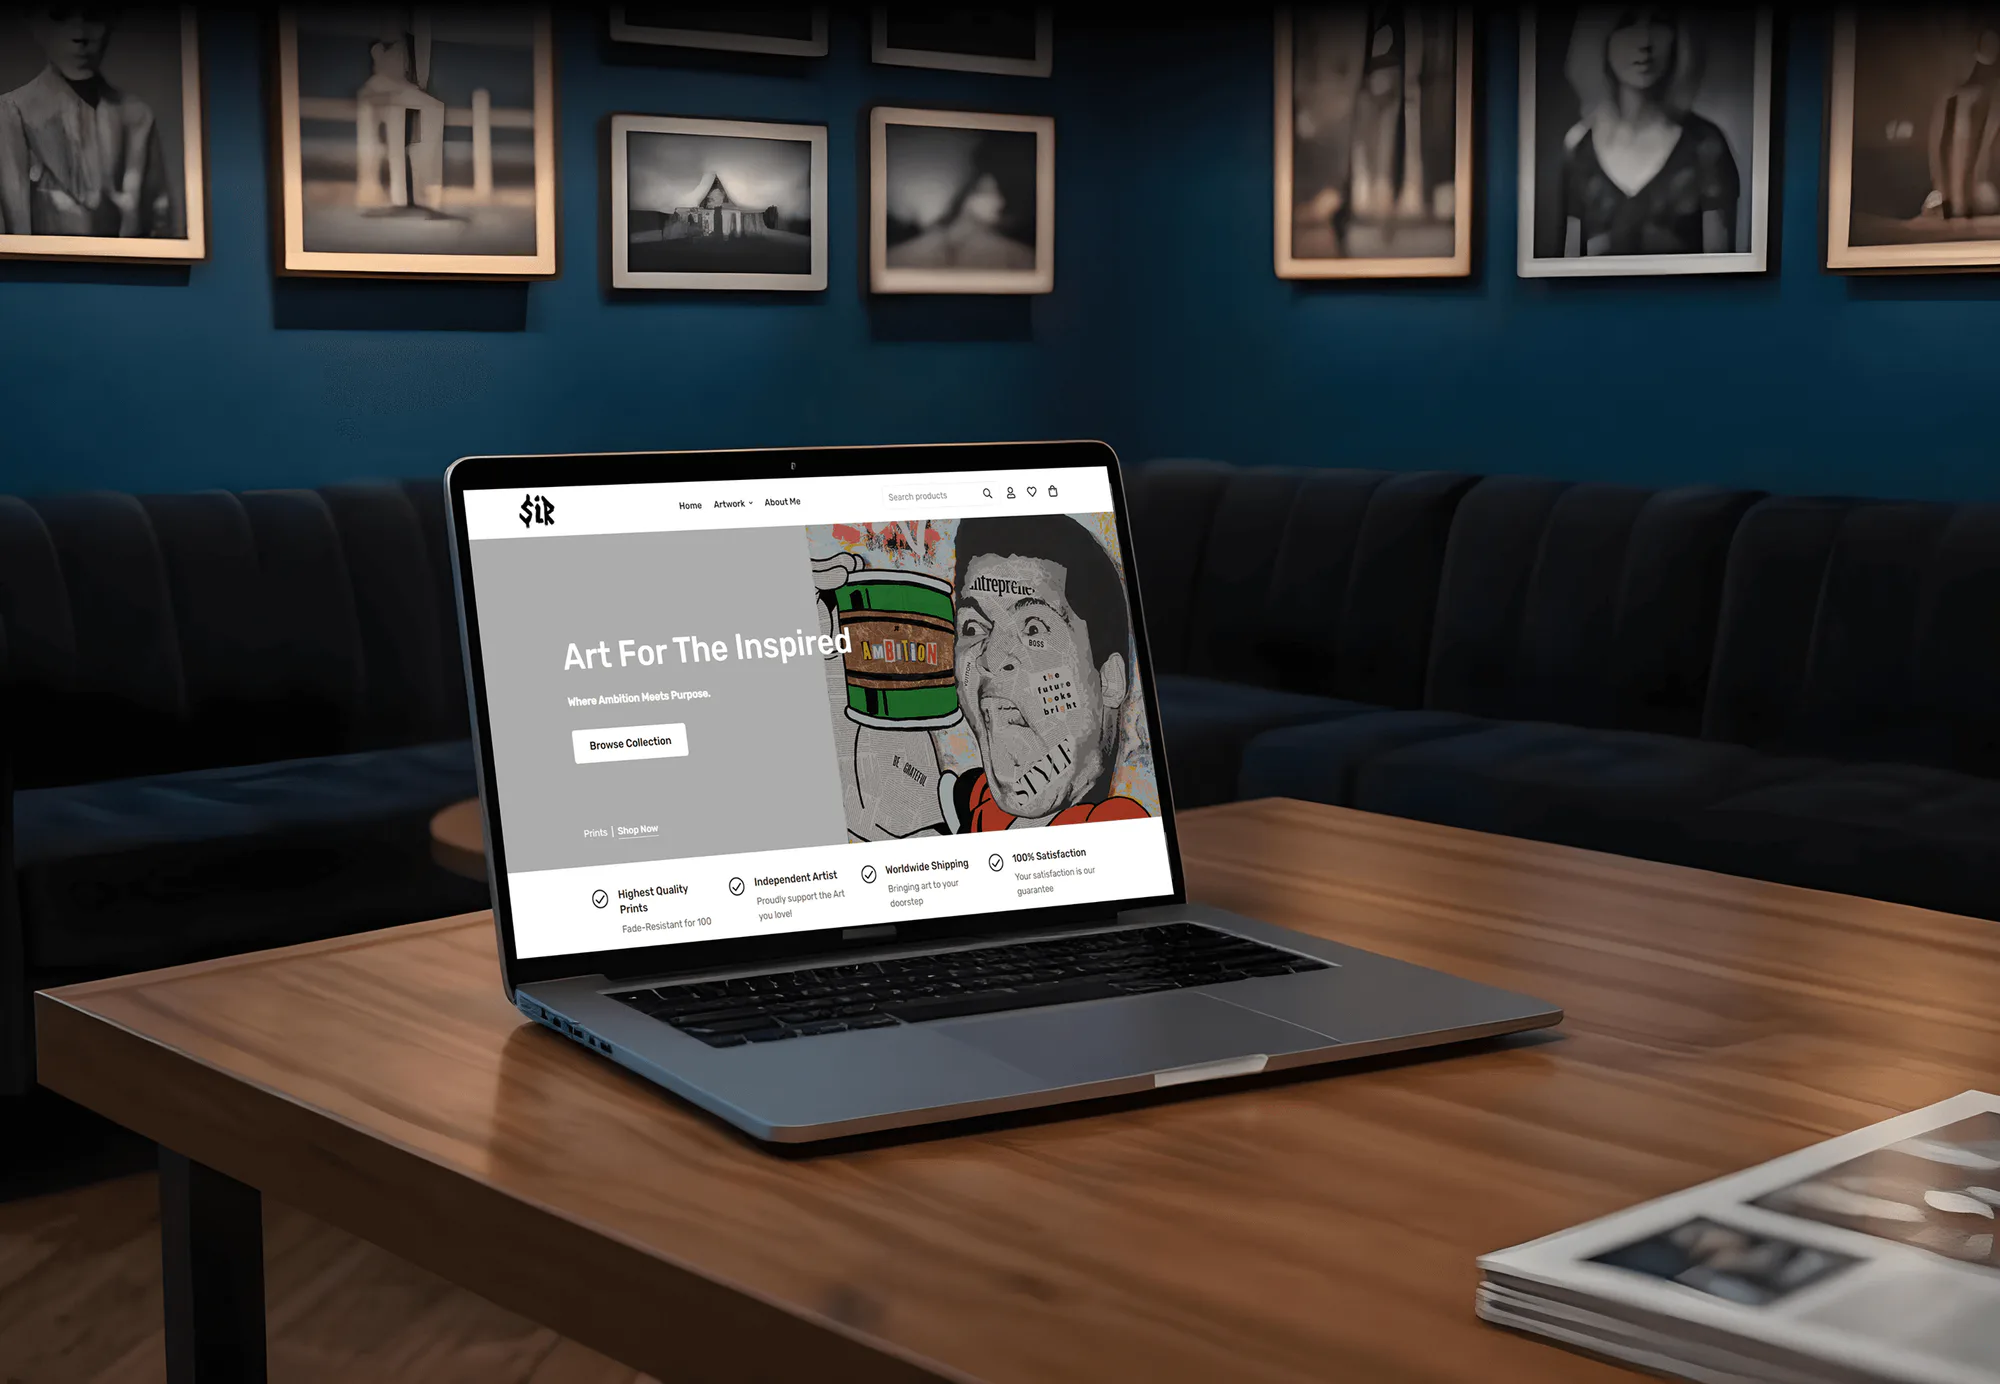
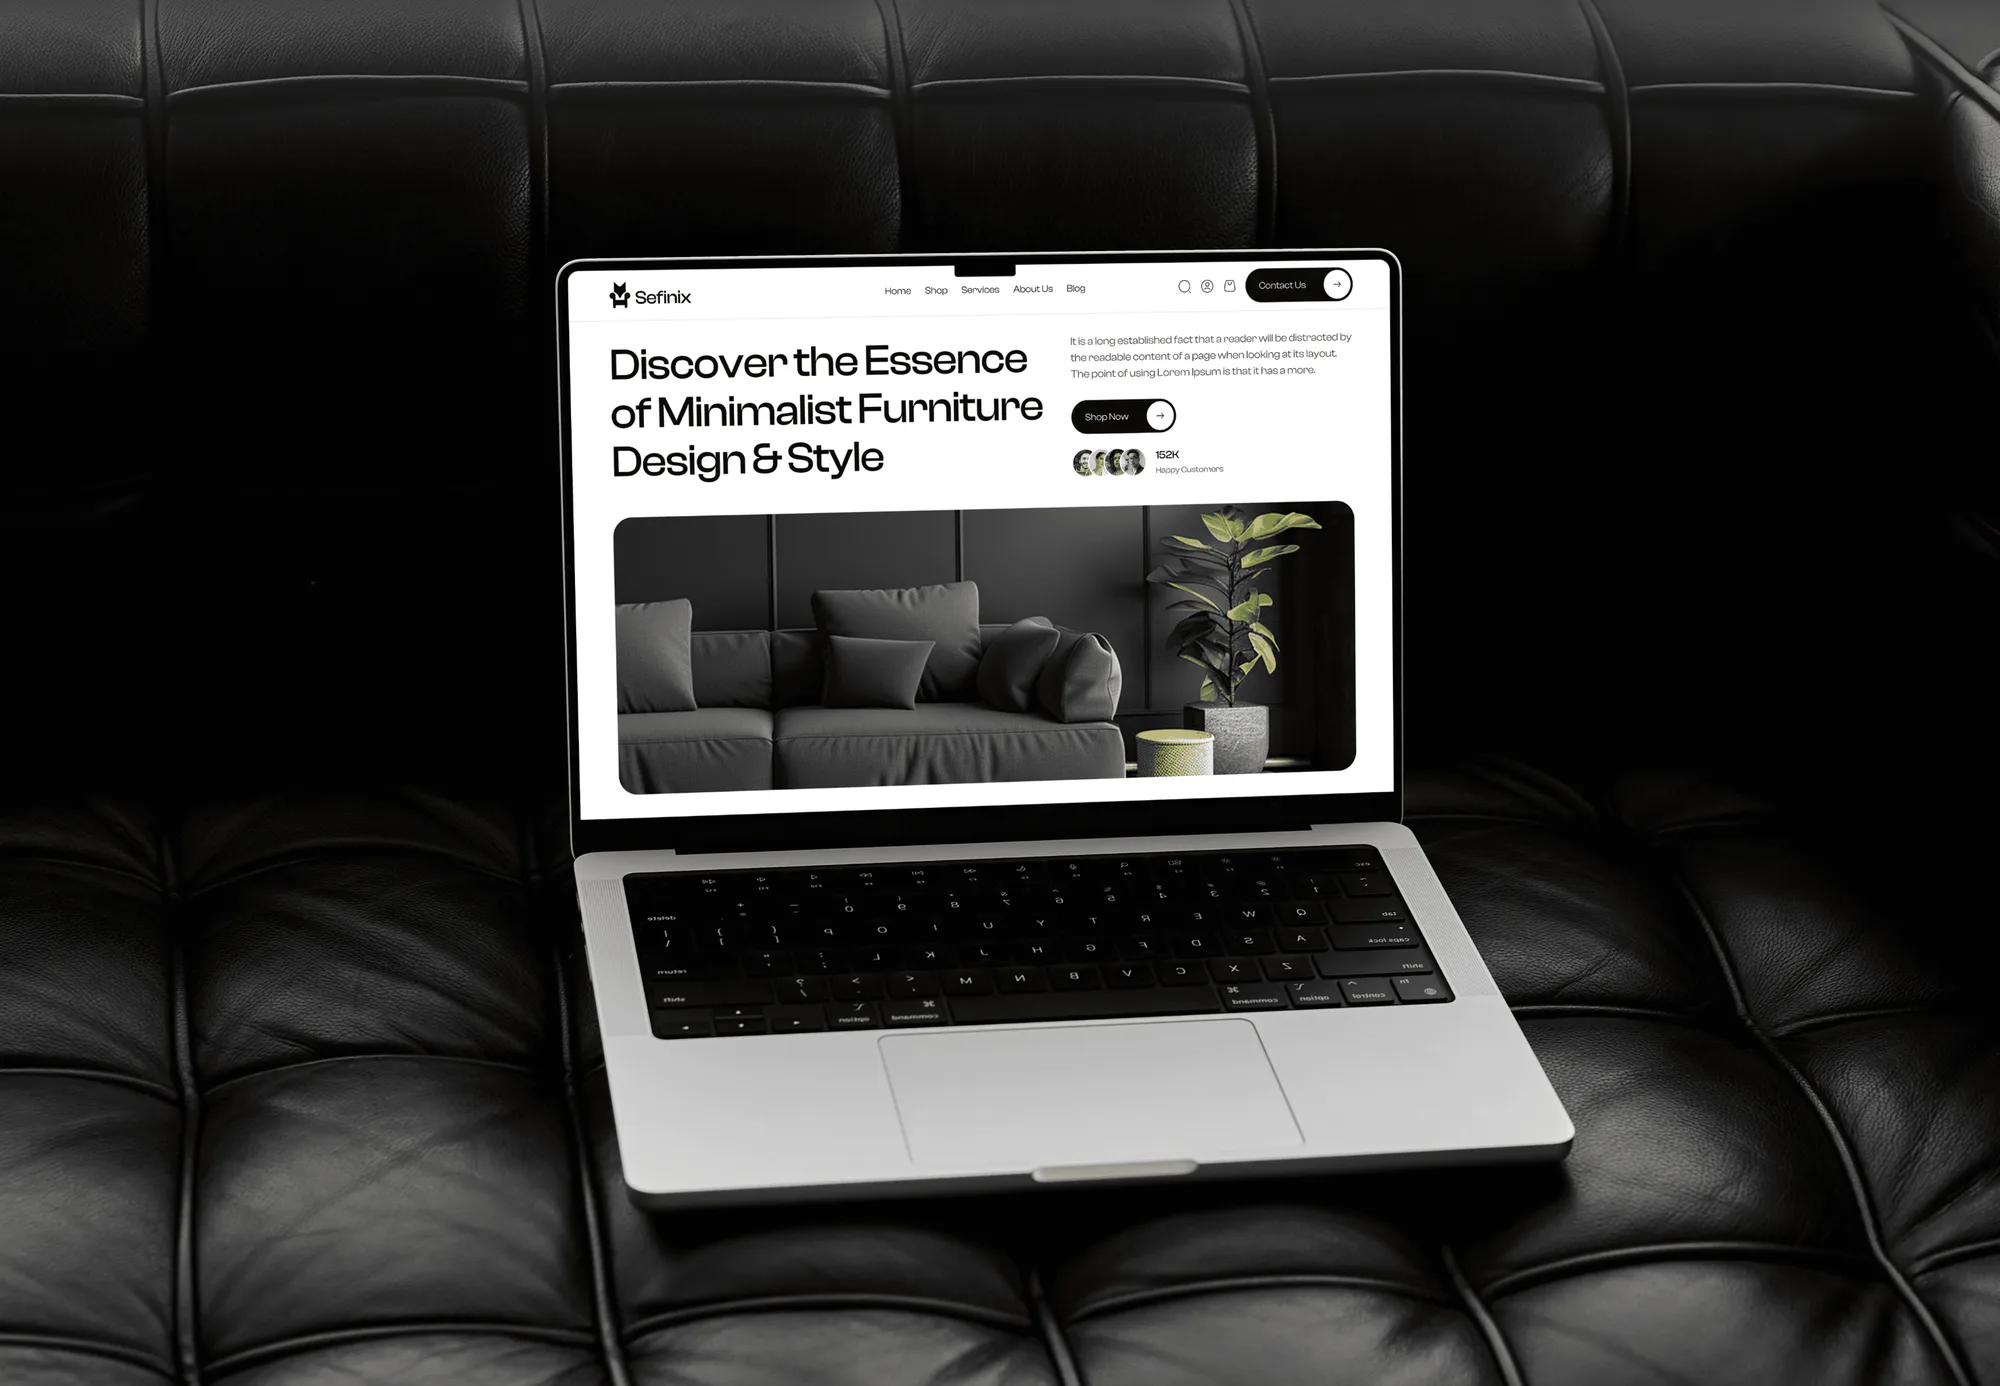
Stores with catalogs, carts, and customer accounts that we designed and built. They weren't security projects, but they show the admin areas and checkouts this work protects.
What's Included
An access review, an app and API key cleanup, a checkout script inventory with change alerts, card testing defenses, customer account protection, and a recheck with handover notes.
Compare Options
A security app is quick to install, and your platform's defaults cost nothing extra. For ecommerce security on a store with staff, apps, and real card traffic, here is where each holds up.
| Feature | DeveloperLookBest fit | Security app | Platform defaults |
|---|---|---|---|
| Staff and app access | Every account and app reviewed | Rarely covered | Settings you turn on yourself |
| Checkout scripts | Inventoried, with change alerts | File scans on some apps | Hosted checkout only |
| Card testing | Rate limits and gateway rules | Often a CAPTCHA add-on | Gateway defaults |
| Customer logins | Credential stuffing defenses | Login limits on some apps | Varies by platform |
| Fixes | Done inside your store | Alerts, then you fix | You fix |
| Platforms | Shopify, WooCommerce, BigCommerce, Magento | Usually one platform | Your platform only |
| Time to start | 1 to 2 weeks | Minutes to install | Already running |
| Cost | From $950 one-time | Free to a small monthly fee | Included in your plan |
What Our Clients Say
Feedback from teams we have built stores, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Stores lose sales when security work is rushed. These habits keep orders flowing while access gets tighter and checkout scripts stay watched.
We place a test order after every change to checkout, payments, or login rules. A fix that blocks real customers isn't a fix, so it rolls back.
We don't hand you a list of stale logins and leave. With your approval, we remove them, rotate the keys, and confirm your apps still work.
Shopify and BigCommerce run your servers and core checkout, while WooCommerce and Magento stores own theirs. We secure the part that's actually yours instead of selling everyone one package.
We explain how your checkout setup affects PCI DSS scope, then say plainly that your bank or assessor makes the call. We don't promise compliance.
Each fix lands in a change log with the date, the reason, and how to undo it. Your next developer or auditor can follow it.
Admin access, API keys, and alert inboxes stay in your name. When we finish, our own access comes out too, and you confirm it.
Overview
DeveloperLook provides ecommerce security for online stores on Shopify, WooCommerce, BigCommerce, and Magento. We review staff and app access, add two-step verification, inventory checkout scripts with change alerts, and set card testing defenses. Reviews start at $950 and take 1 to 2 weeks, with fixes done inside your store.
DEVELOPERLOOK
Project facts · Ecommerce Security Services
Reviewed 26 Oct 2026 by Saimul Islam
Good fit
Shopify stores with many staff and apps
Your Shopify store has years of staff accounts and apps with order access, and you want security for ecommerce that starts with who can log in.
WooCommerce stores on their own hosting
Your WooCommerce store runs on a server you manage, and a plugin flaw in the news made you wonder what else is open.
Stores hit by card testing
Your payment provider flagged a burst of small declined charges, and you need card testing stopped before it costs you fees or your merchant account.
Teams running several storefronts
Your team runs stores on BigCommerce and Magento and wants one standard of security for ecommerce websites across every brand.
Agencies managing client stores
Your agency looks after client stores and wants a security review you can deliver under your brand before peak season.
Not a fit
Need a PCI compliance program
You need your SAQ chosen, policies written, and evidence gathered for your bank. Our PCI Compliance Services cover that program, and this page stays with technical fixes.
Magento store behind on patches
Your main worry is a Magento or Adobe Commerce store missing security releases. Our Magento Security Patches and Audit service handles patching and skimmer cleanup.
Only want a written audit
You want findings for your own developers to fix. Our Website Security Audit Services deliver a ranked report from $450.
Tiny store, one login
You sell a handful of products on a hosted plan with one login and no apps. Your platform's two-step login and default fraud settings are enough for now.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your platform, store count, and checkout scripts, and you get a fixed proposal after a free store risk check.
For Agencies
You own the client relationship. We supply the security engineering behind it: access reviews, checkout script inventories, card testing defenses, and fixes inside each client's store. Your clients get a safer checkout before peak season, delivered under your brand.
White label: your client only ever sees your brand
Send the store URLs, platforms, app lists, and any fraud alerts so far.
We run a free risk check on each store and give a fixed price.
We fix, retest, and hand over notes written under your brand.
Send the store URLs, platforms, app lists, and any fraud alerts so far.
We run a free risk check on each store and give a fixed price.
We fix, retest, and hand over notes written under your brand.
The Right Technology for Your Project
We work inside your store platform, your payment gateway, and the edge network in front of your site, with tools your team can keep running.
ShopifyWooCommerceBigCommerce MagentoStripePayPalBraintreeCloudflareAWSOWASPBurp SuiteChrome DevTools
FAQ
Straight answers on cost, timing, customer data, payment gateways, card testing, and PCI.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Ecommerce security services from DeveloperLook start at $950 for one store. That covers the review, two-step verification on every staff login, stale access removed, and 30 days of script alerts. The $2,250 plan fixes every high and medium finding. The $4,400 plan covers up to 3 stores or a self-hosted server, plus a firewall.
A security review of one store takes 1 to 2 weeks, and a review with every fix takes 3 to 6 weeks. Checkout changes take longest because we place test orders after each one and avoid your busiest sales hours. Several storefronts or your own servers put you at the top of that range.
You secure an ecommerce website by closing the five ways in: staff logins, apps, checkout scripts, payment settings, and customer data. Good security for ecommerce website owners starts with two-step verification on every admin account. Next, remove apps and API keys nobody uses. Then list every script on the cart and checkout, and set gateway rules that slow card testing.
Ecommerce security protects customer data by limiting who and what can read it, and by keeping card numbers off your systems. Hosted payment fields or a redirect to the gateway mean card data doesn't pass through your server. Customer exports get locked to named staff, apps lose order access they don't need, and customer logins get rate limits against credential stuffing.
Start with the threats aimed at online stores: stolen staff logins, card testing, skimming scripts, and risky apps. Off-the-shelf ecommerce security solutions such as security apps help with scanning, but they can't decide who should have access. Turn on two-step verification, remove unused apps, and watch your checkout scripts for changes.
Choose a gateway that keeps card data off your site and gives you fraud controls you can tune. Look for hosted payment fields or a hosted checkout, 3D Secure support, and rules that block repeated declines. Stripe, PayPal, Braintree, and Adyen all offer these, so the right pick depends on your platform and markets.
Shopify isn't more secure for every store, but it takes more of the work off your hands. Shopify and BigCommerce run the servers and core checkout, and Shopify runs custom pixels in a sandbox without access to the checkout page itself. On WooCommerce and Magento you own the server, patches, and plugins too. Either way, staff logins and apps stay your job.
You stop card testing by making repeated attempts from one source slow and costly. We add rate limits on checkout and payment requests, a bot challenge when attempts spike, and gateway rules that block repeated declines. Stripe Radar, for example, supports custom rules for repeated attempts.
No, security work alone doesn't make a store PCI compliant, because your acquiring bank or a Qualified Security Assessor decides that. We fix technical gaps that PCI DSS reviews often raise, such as shared admin logins and unknown payment page scripts. For the full program with scoping and evidence, our PCI Compliance Services page covers readiness work.
Every plan includes 30 days of checkout script change alerts and fix support after handover. When a script changes, we check who made the change and remove anything that shouldn't be there. After that, run the alerts yourself with our runbook, or move to a monthly plan on our Website Security Monitoring page.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.