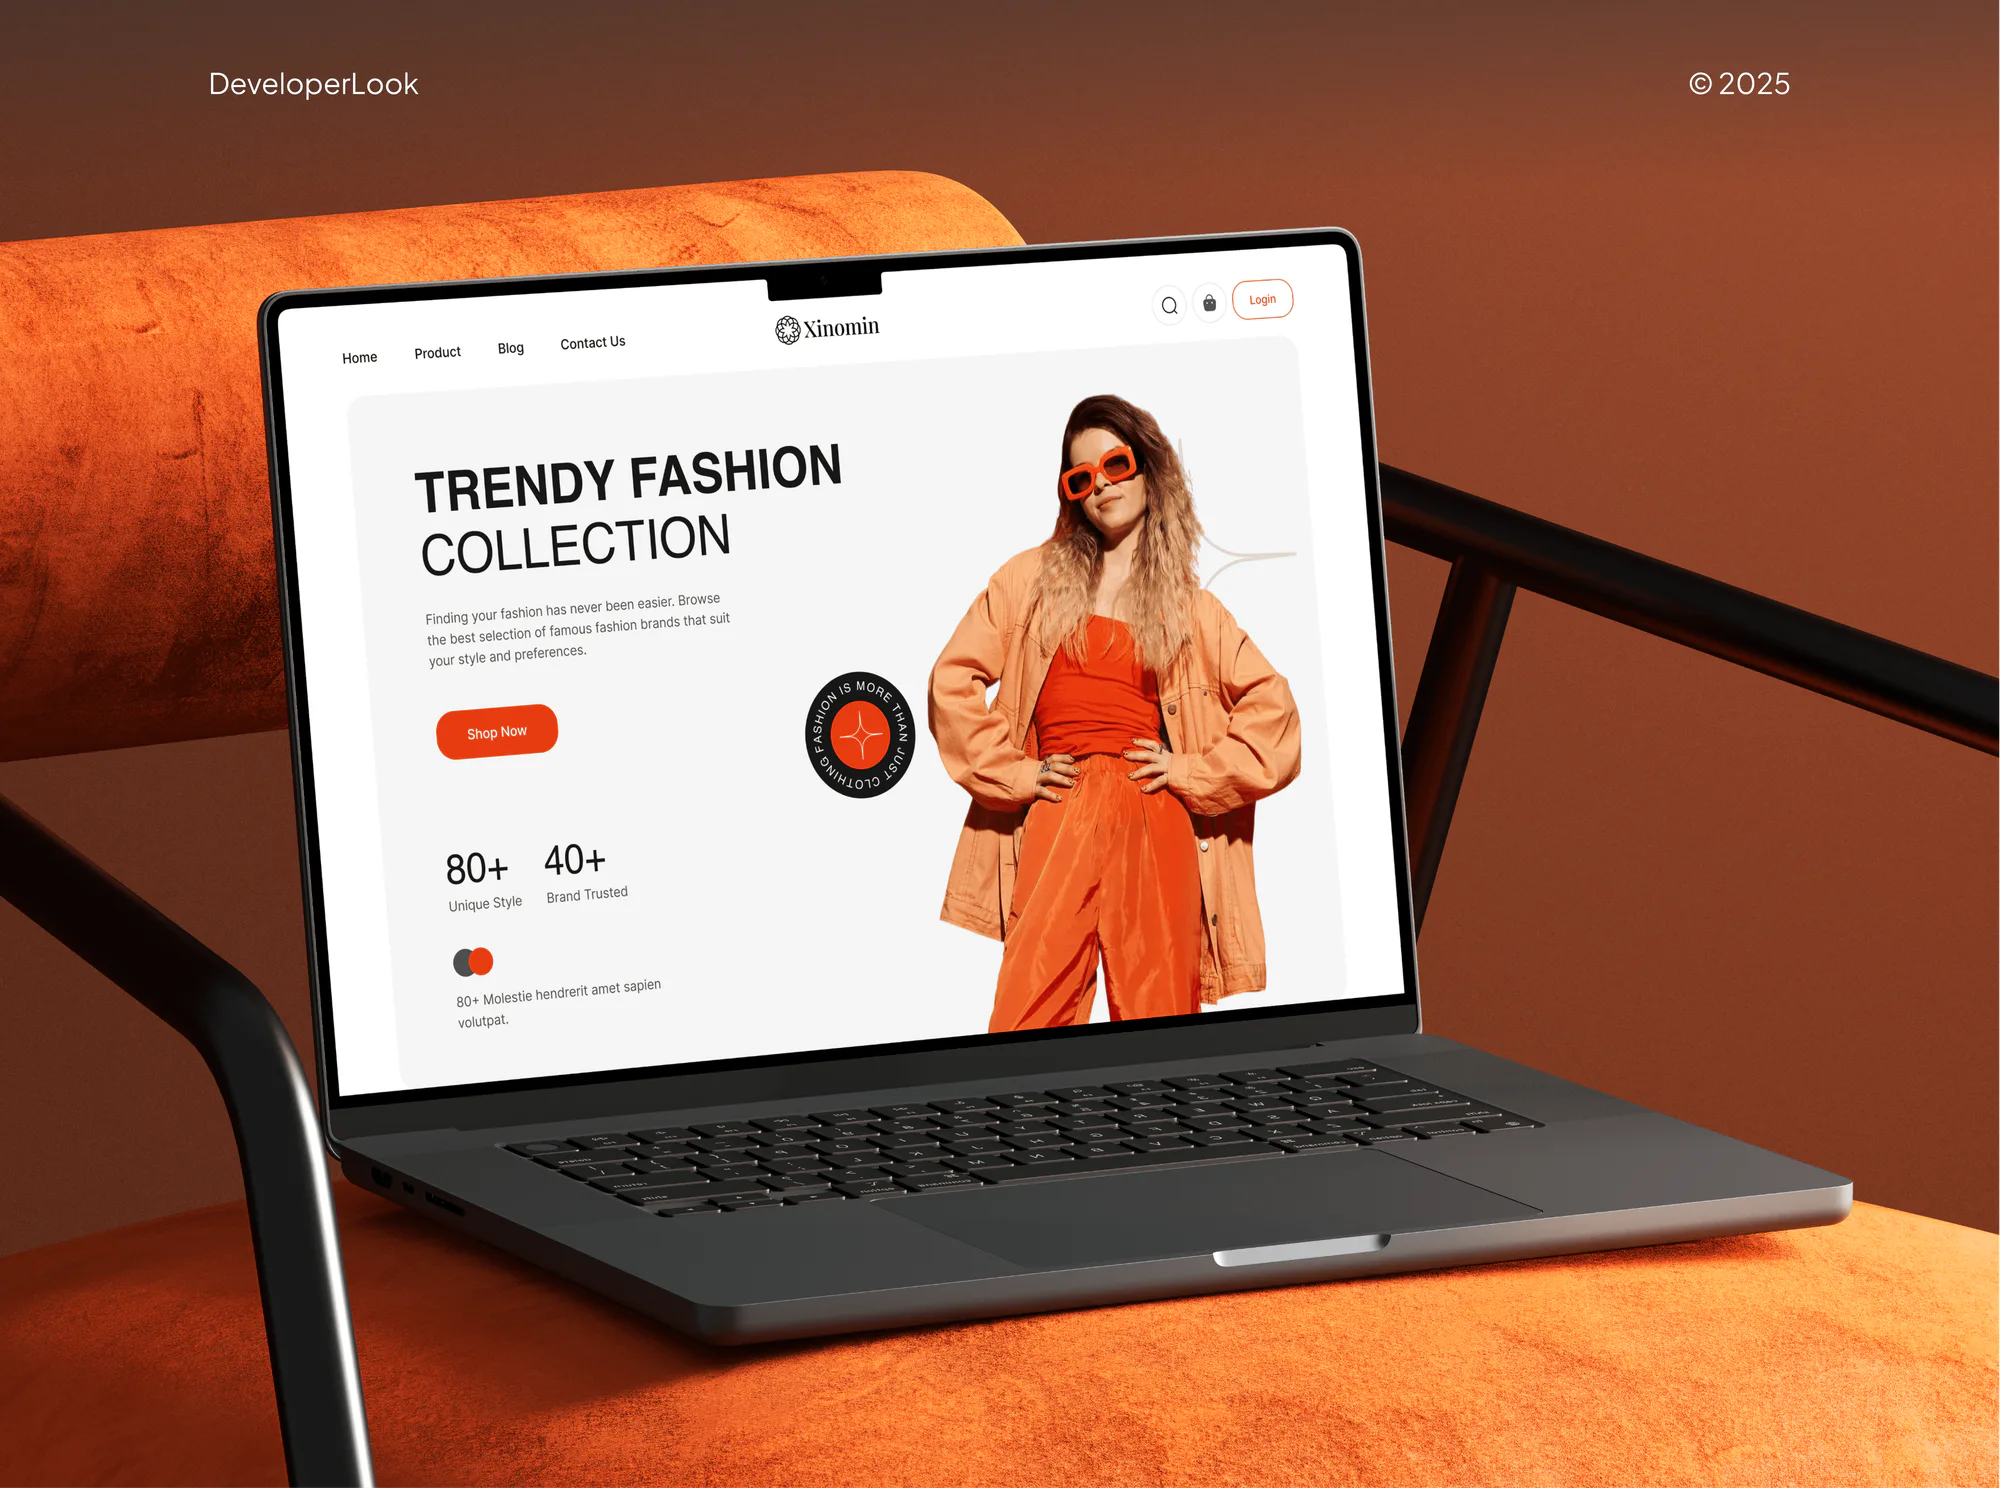
Xinomin Fashion Ecommerce Website and Admin Dashboard
- Fashion
- E-commerce
- Dashboard

For online merchants on hosted fields, iframes, or their own checkout: every script on your payment page listed, approved, locked down, and watched for changes.
100%
Payment page scripts inventoried
2/2
Requirements mapped to evidence
How your project runs
01 · FreeIndustry leaders we work with
 Shopify
 WooCommerce
 Magento
 BigCommerce
 Stripe
 PayPal
 Braintree
 Chrome DevTools
 OWASP
 Google Tag Manager
 Cloudflare
 Node.js
The Problem
It shows up when an assessor asks for your script inventory, or a tag manager quietly adds a chat widget where customers type card numbers.
Inventory
Nobody can list every script that runs on checkout.
Inventory
A live inventory with owner, reason, and approval for each payment page script.
Tag manager
Marketing tags can add scripts to checkout without review.
Tag manager
Tag manager rules that keep new tags off payment pages unless approved.
Integrity
A third-party file could change without anyone noticing.
Integrity
Subresource Integrity hashes and a strict policy that block unapproved or altered code.
Detection
Skimmer code could sit on the page for weeks.
Detection
Change and tamper alerts on scripts and headers, reviewed and logged every week.
Your checkout loads more than a dozen scripts. You know about the payment form and analytics. The rest came from a tag manager, a reviews app, a chat widget, and a heatmap trial someone forgot to cancel. Any one of them could be swapped for a skimmer that copies card numbers as customers type. Then your assessor asks for the script inventory, each script's justification, and proof you'd notice a change. You have a spreadsheet from last year.
We start by loading your payment pages the way a customer's browser does and recording every script, including ones injected by other scripts. Each one gets an owner, a reason, and an approval, or it comes off the page. Then we lock the page with a Content Security Policy and Subresource Integrity, and set up alerts for script and header changes. You get a checkout you can account for, not a spreadsheet that's already out of date.
Every script, every source
First-party, third-party, and scripts loaded by other scripts, recorded as the browser sees them.
Locked with CSP and SRI
Only approved scripts run, and static files are pinned to a hash so silent edits fail.
Changes trigger alerts
Script and security header changes on payment pages alert your team, with a weekly review log.
Our PCI DSS 6.4.3 and 11.6.1 Compliance Process
You see every script we find, approve which ones stay, and test the locked-down checkout on staging before it goes live.
We load your payment pages and share a first list of the scripts that run there. You get a fixed quote, a read on your likely SAQ type, and an access list.
Projects We've Built
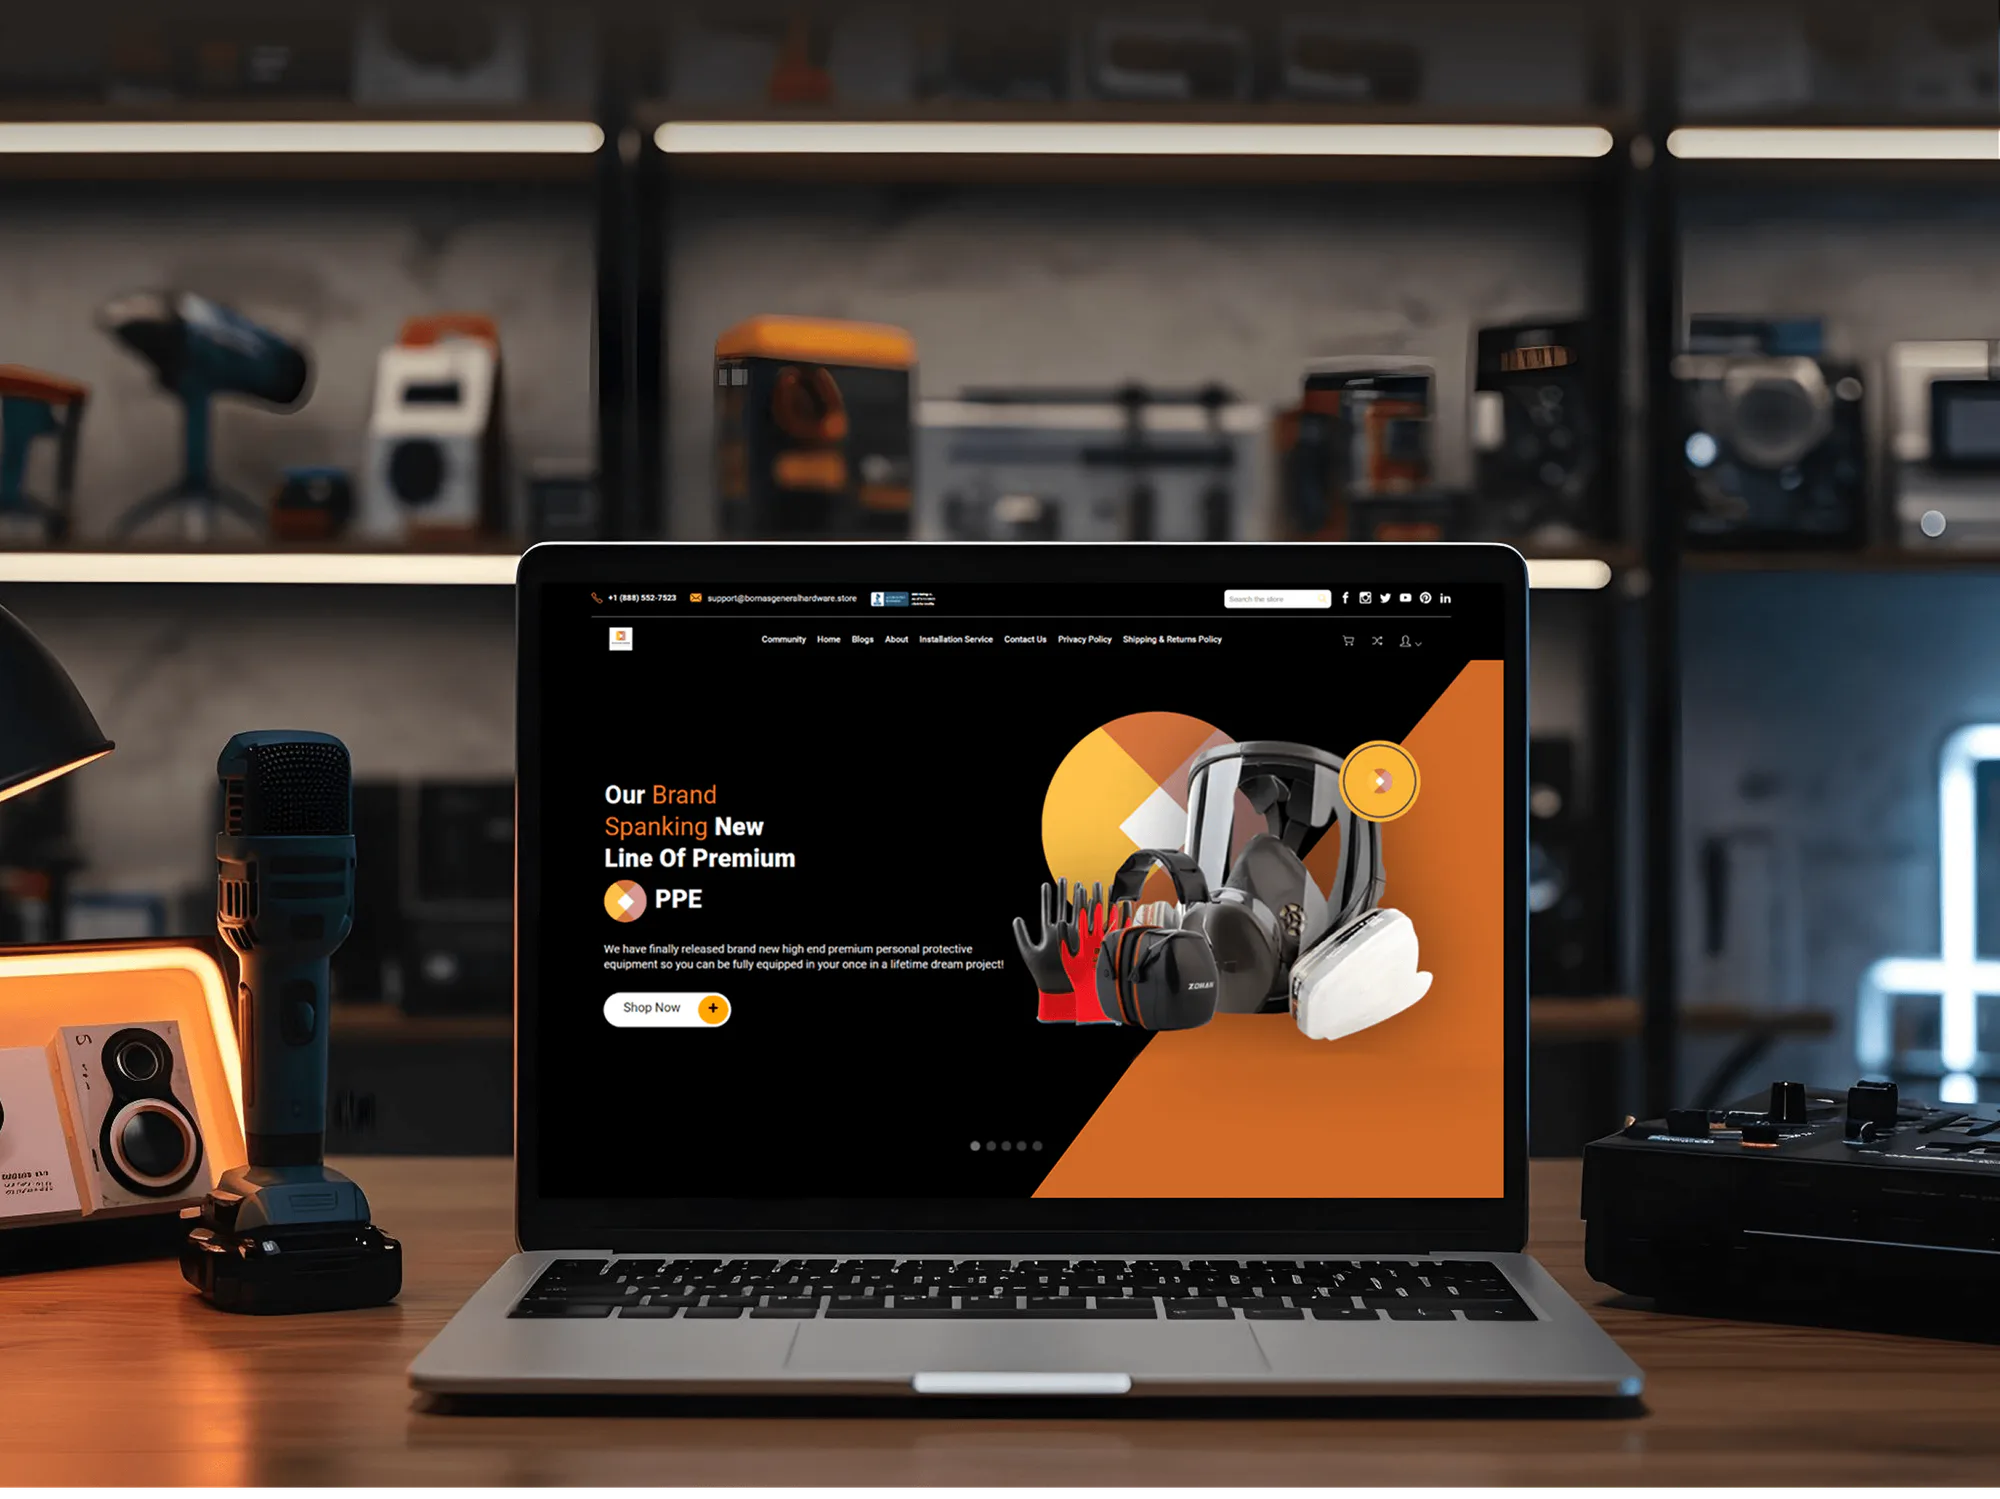
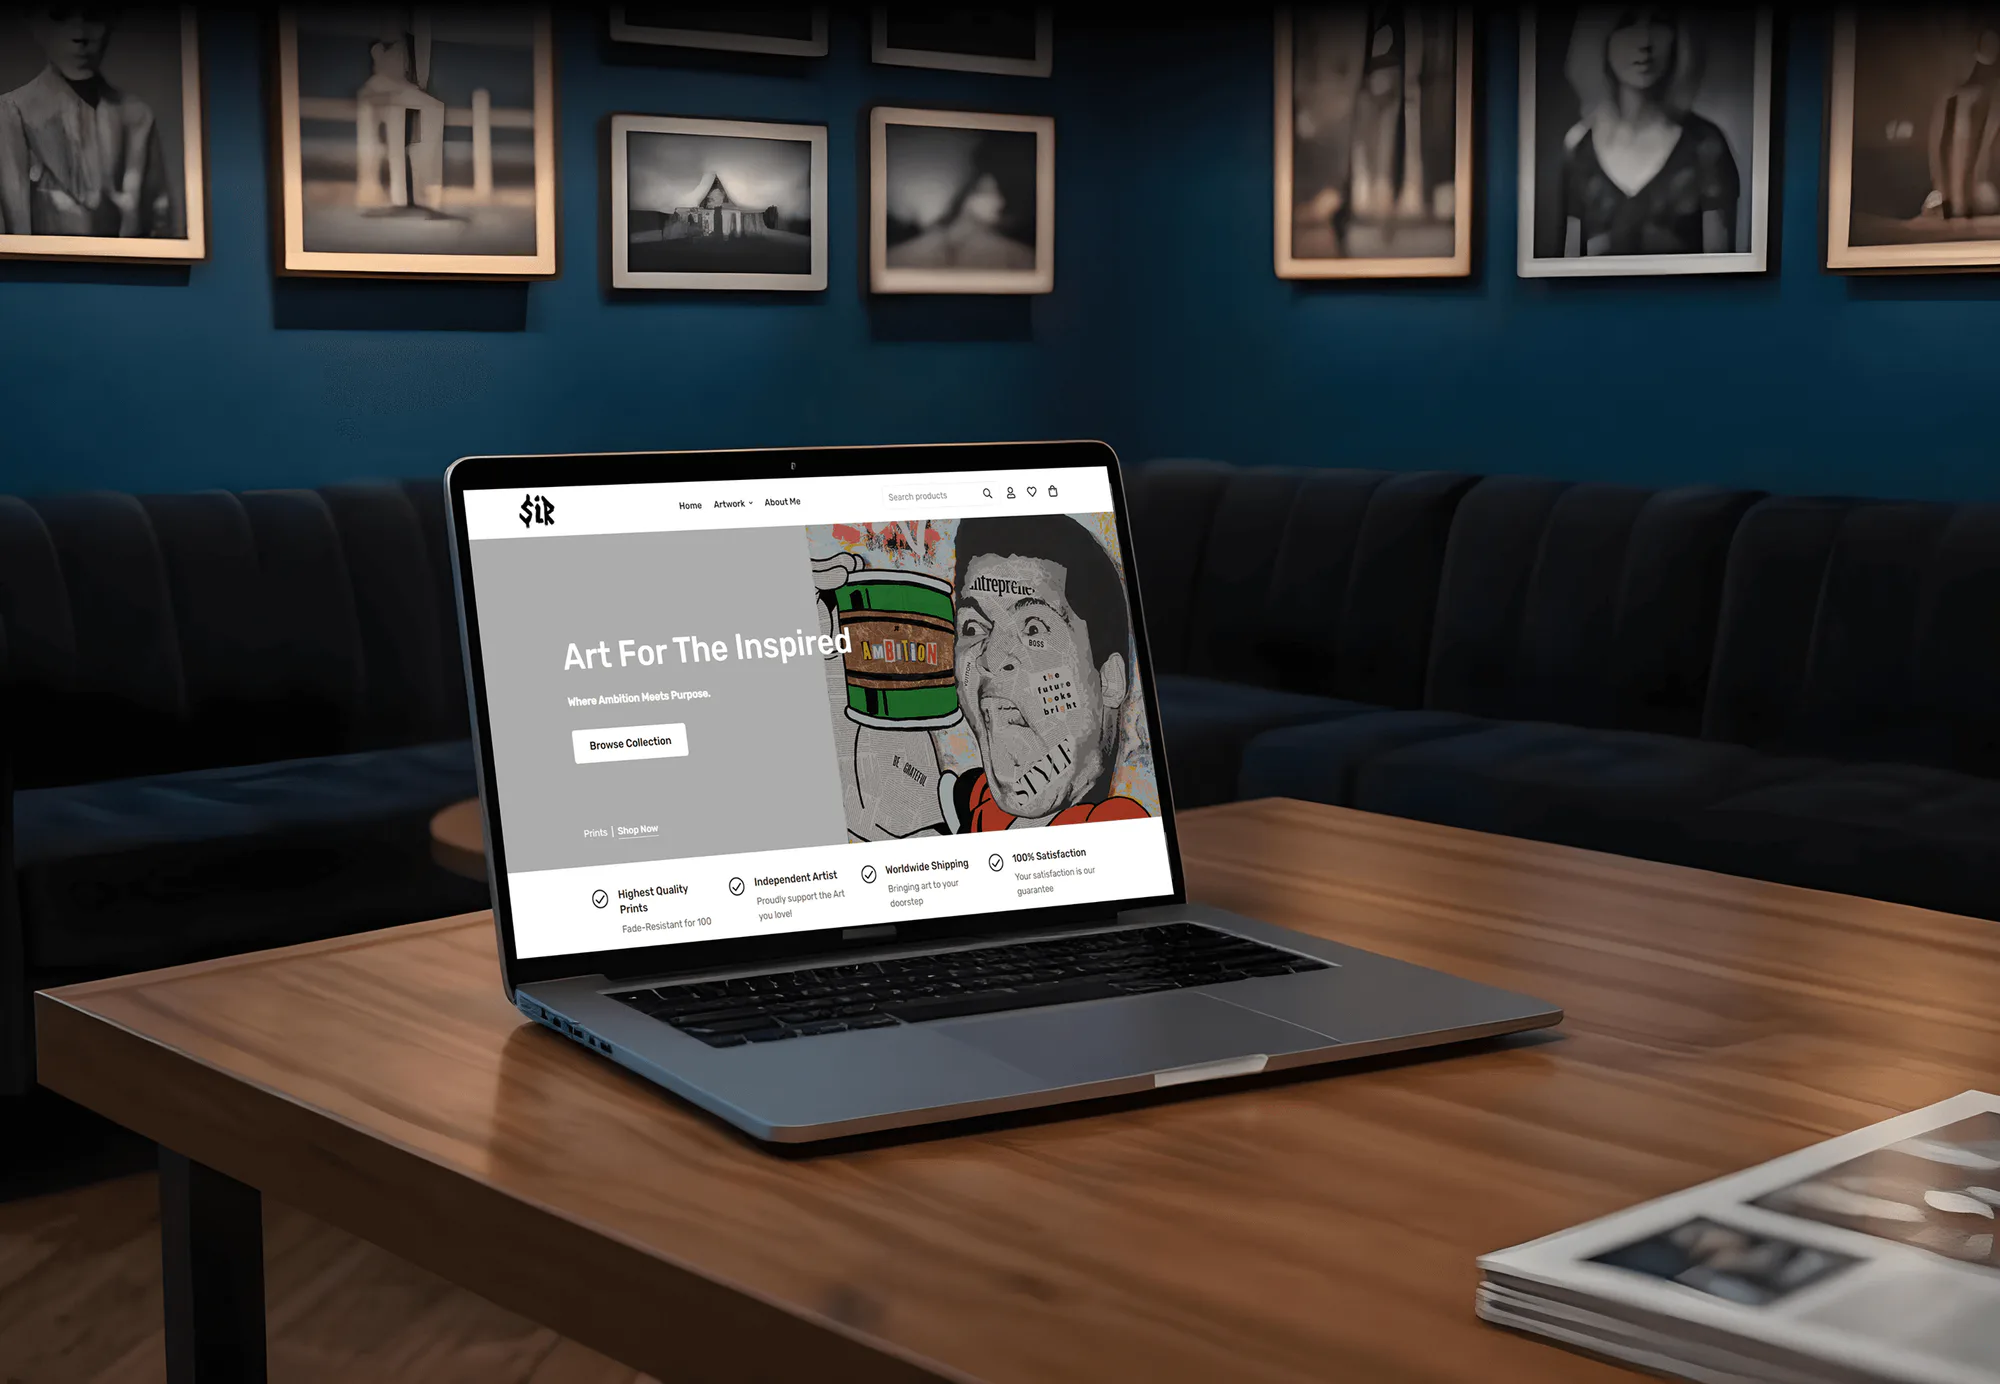
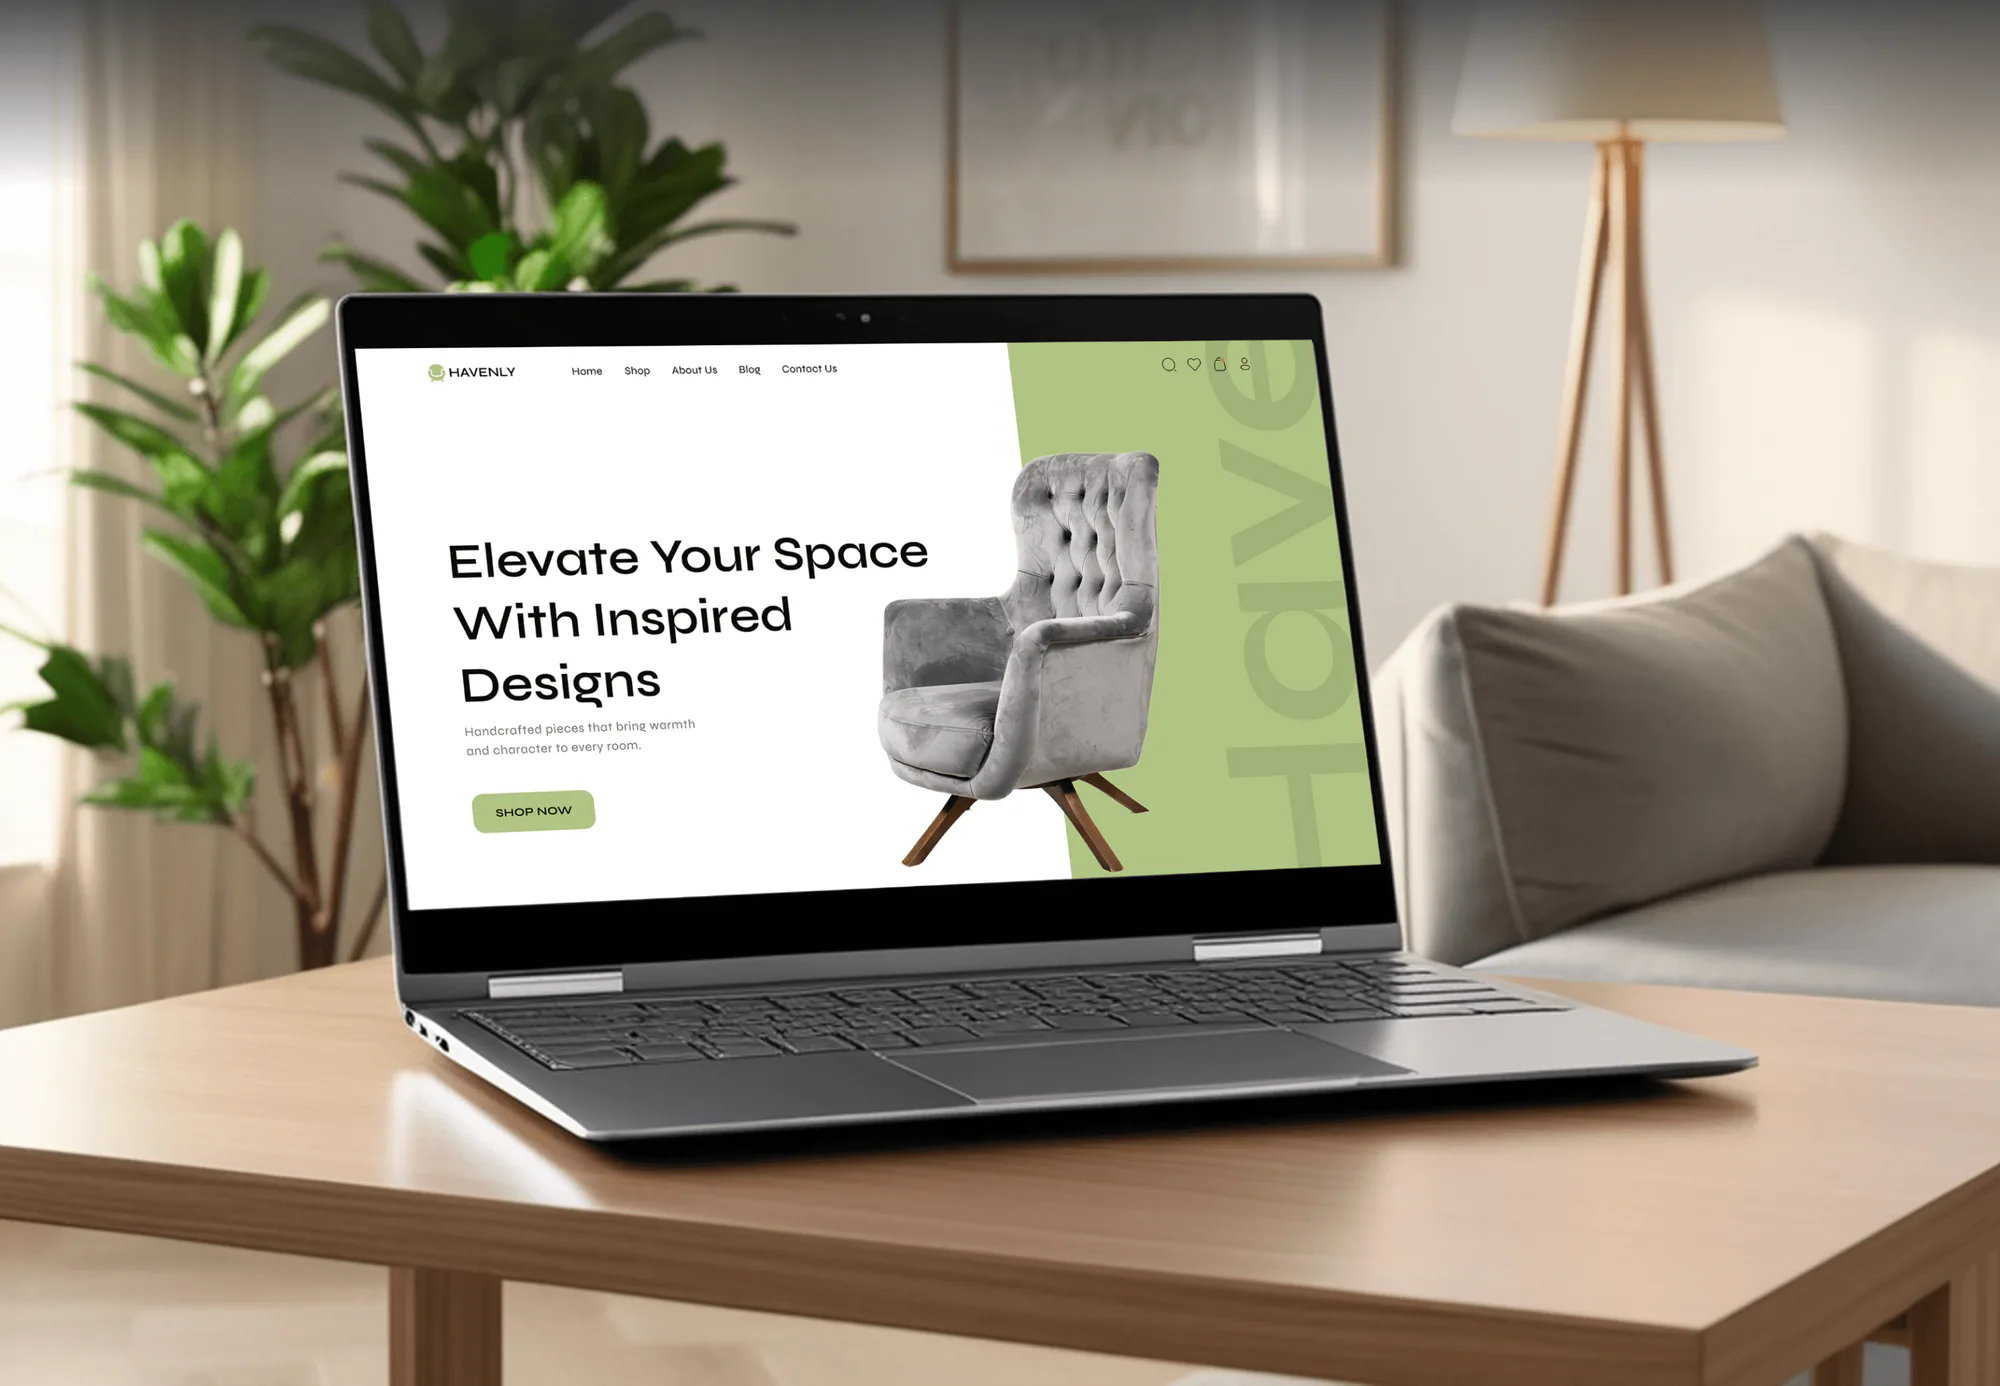
Ecommerce stores we designed and built for fashion, hardware, art, and furniture brands. They show the kind of checkouts we secure, not PCI script projects.
What's Included
Each project covers a script inventory, an approval workflow, integrity controls, tag manager rules, change and tamper detection, and an evidence pack for your assessor.
Compare Options
Monitoring subscriptions and your payment provider's hosted fields both reduce risk. Here is where each stops when you need evidence for both requirements.
| Feature | DeveloperLookBest fit | Monitoring tool | Payment provider only |
|---|---|---|---|
| Script inventory | Built and justified per script | Automated discovery | Covers its own iframe |
| Authorization records | Owner and approval per script | Approval features vary | Not included |
| Integrity controls | CSP and SRI set up | Monitors, rarely configures | Inside its iframe only |
| Change detection | Set up and tuned | Their core strength | Not on your page |
| Fixes on your site | Done on staging first | Your team does them | Not included |
| Assessor evidence | Packed by requirement | Reports from the tool | Its own compliance attestation |
| Cost | Fixed price from $700 | Monthly subscription | Included in fees |
| Ongoing effort | Weekly review log handed over | Low once tuned | None for its part |
What Our Clients Say
Feedback from teams we have built platforms, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Locking down a checkout for PCI 6.4.3 can break it if you rush. These habits keep payments working while every script on the page gets accounted for.
A new Content Security Policy runs in report-only mode first. We read the reports and fix gaps before enforcement, so customers don't hit a blocked payment form.
If your payment page is fully hosted by your provider, the script work may not be yours to do. We'll tell you before we quote.
We agree tag rules with the people who run your ads. They keep their tracking on product pages, and checkout stays clean.
We build the controls and the evidence, and your QSA or acquirer assesses them. You won't get a compliance certificate from us.
Policy changes go live outside your busiest days, with a rollback ready. Holiday sale weeks stay frozen unless you ask otherwise.
Policies, alerts, and records live in your own accounts. If you switch agencies or tools later, nothing stays locked inside ours.
Overview
DeveloperLook handles PCI 6.4.3 and 11.6.1 for online merchants by finding every script on your payment pages and putting it under control. We build the inventory with reasons, set approvals, add CSP and SRI, and set up change and tamper alerts. Projects start at $700 and take 1 to 5 weeks.
DEVELOPERLOOK
Project facts · PCI DSS 6.4.3 and 11.6.1 Compliance
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Merchants embedding payment iframes
Your checkout embeds your provider's card fields in an iframe, and you need to know which script rules still apply to your own page.
Stores with their own checkout
You run a custom or headless checkout that collects card data on your own page, so PCI DSS 6.4.3 covers every script on it.
Teams facing a QSA assessment
Your QSA asked for script inventories, authorization records, and weekly tamper check evidence, and your team has 3 weeks to produce them.
Buyers comparing security vendors
You searched for the best companies specializing in 6.4.3 and 11.6.1 cybersecurity and found subscriptions, but you still need someone to fix the page.
Agencies running client stores
You manage stores for clients and need one repeatable way to keep marketing scripts off payment pages without breaking checkout.
Not a fit
Need full PCI scope work
You need SAQ selection, scope reduction, and all 12 requirements covered. Our PCI Compliance Services page handles full assessment readiness.
Failing ASV scans
Your gap is failing external vulnerability scans, not payment page scripts. Our PCI ASV Scan Remediation page covers fixing scan findings.
Fully hosted redirect checkout
Customers leave your site to pay on your provider's hosted page. Those scripts are the provider's job, so an SAQ eligibility check may be all you need.
Want a compliance certificate
You want someone to certify your store as PCI compliant. Only your QSA or acquirer's process does that, and we prepare the controls and evidence.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your checkouts, the scripts that load there, and your platform, and you get a fixed proposal after a free script scan.
For Agencies
You own the client relationship. We supply the script inventories, CSP and SRI work, and tamper alerts under your brand, so your merchants meet both script requirements without extra hires.
White label: your client only ever sees your brand
Send the platform, payment provider, checkout URLs, and any assessor requests.
We build the inventory and controls on staging for your review.
We turn on alerts, hand over evidence, and brief your team under your brand.
Send the platform, payment provider, checkout URLs, and any assessor requests.
We build the inventory and controls on staging for your review.
We turn on alerts, hand over evidence, and brief your team under your brand.
The Right Technology for Your Project
We work inside the platforms, payment providers, and tag tools your checkout already uses, with browser standards doing the locking.
ShopifyWooCommerce MagentoBigCommerceStripePayPalBraintreeChrome DevToolsOWASPGoogle Tag ManagerCloudflareNode.js
FAQ
Straight answers on cost, iframes and Stripe, script integrity, and the evidence assessors expect.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
With us, PCI DSS 6.4.3 work starts at $700 for one checkout's inventory with owners, reasons, and a gap memo. Locking scripts down with CSP and SRI, plus tamper alerts and an evidence pack, starts at $1,950. Several storefronts start at $3,900. Any monitoring tool bills its own subscription.
One checkout usually takes 1 to 2 weeks for the inventory and gap memo. Adding enforced policies, approvals, and alerts brings it to 3 to 5 weeks, because the policy runs in report-only mode before we enforce it. We plan around your busiest sales weeks.
PCI DSS 6.4.3 requires managing every script that runs on a payment page in the consumer's browser. You confirm each one is authorized, assure its integrity, and keep an inventory with written justification. 11.6.1 requires a mechanism that alerts on unauthorized changes to scripts and security-impacting headers, run at least weekly or as your risk analysis sets.
Start by listing every script on each payment page as the browser loads it. Give each script an owner and a written reason, and remove the rest. Then add an approval step for new scripts, and use Subresource Integrity, a Content Security Policy, or both to block unapproved or altered code. Keep the records, because assessors ask for them.
It means controlling the JavaScript that runs on your payment page in the customer's browser. Attackers inject skimming code into a trusted script or tag, and it copies card data as people type. The requirement makes you know, approve, and verify every script, so injected code has nowhere to hide.
Subresource Integrity (SRI) is a browser feature that checks a script file against a hash written into your page. If the file changes, the browser refuses to run it. It's one way to assure integrity under 6.4.3, but it only suits static files, so scripts that change often need a Content Security Policy or another method.
Use SRI hashes for static files, a Content Security Policy that limits where scripts load from, or a tool that compares scripts against approved versions. We test the setup by changing a staging script on purpose and confirming the browser blocks it or an alert fires.
Most QSAs ask for a script inventory with written justification, authorization records for each script, and proof of the integrity method. Many load the page themselves to compare it with your inventory. For 11.6.1 they want the alert setup and logs of the weekly checks. Requests vary, so we ask for your assessor's list early.
It depends on how your checkout uses Stripe. With hosted Stripe Checkout, customers pay on a page Stripe serves, so those scripts aren't yours. With Elements or the Payment Element, card fields sit in iframes from Stripe's domain, but scripts on your own page still matter. SAQ A merchants must confirm their site isn't susceptible to script attacks (PCI SSC FAQ 1588).
Ask what they'll change on your page, not only what they'll monitor. A good partner inventories scripts as the browser loads them, tests policies on staging, and hands you evidence by requirement. Also weigh top-rated security solutions for 6.4.3 and 11.6.1, since a tool alone can work if your team makes the fixes.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.