Havenly Furniture Ecommerce Website
- Furniture
- E-commerce
- Dashboard

For Magento and Adobe Commerce stores behind on security releases: every missing patch installed on staging first, plus a skimmer check of files and database. From $700.
100%
Released security patches applied
2
Skimmer checks: files and database
How your project runs
01 · FreeIndustry leaders we work with
 Magento Open Source
 PHP
 MySQL
 Cloudflare
The Problem
It shows up when Adobe posts a security bulletin, your payment provider traces card fraud to your checkout, or a patch install fails on staging.
Missing patches
Nobody knows which security releases the store lacks.
Missing patches
Your version is matched against Adobe's bulletins, listing every missing patch.
Risky updates
The last update broke checkout for a day.
Risky updates
Patches go to staging first, then checkout and admin get tested.
Hidden skimmers
Card-stealing code hides in the database, not just files.
Hidden skimmers
Files and database get scanned for skimmer code, including head scripts.
Stale admins
Old admin users and API tokens still work.
Stale admins
Admin users, integrations, and tokens are reviewed, trimmed, and rotated.
Your store runs Magento with a long list of extensions, and nobody remembers when the last security release went on. The developer who knew the codebase moved on. Adobe keeps publishing security bulletins, and each one feels risky because the last update broke checkout for a day. Meanwhile, your payment provider asks whether you've checked for card skimmers. You haven't, because nobody knows where to look.
We start by matching your exact version against Adobe's security bulletins, so you see every missing Magento security patch in one list. Patches go onto a staging copy first, then checkout, admin, and extensions get tested before release. We also check your files and database for skimmer code and clean anything we find. Your store gets current on security, not another broken checkout.
Every missing patch listed
Your exact version is checked against Adobe security bulletins and isolated patch releases.
Staging before your live store
Each patch is applied and tested on staging, including checkout and your key extensions.
Skimmer checks in two places
Files and database are both scanned, since injected scripts can hide in store configuration.
Our Magento Security Patches and Audit Process
You see the missing patches, the scan results, and the staging test before anything touches your live store, and you pick the release window.
We read your Magento version from the outside where we can, confirm it with you, and list the security releases that apply. You get a short note and a fixed price. If your store is already current and clean, we'll tell you before we quote.
Projects We've Built
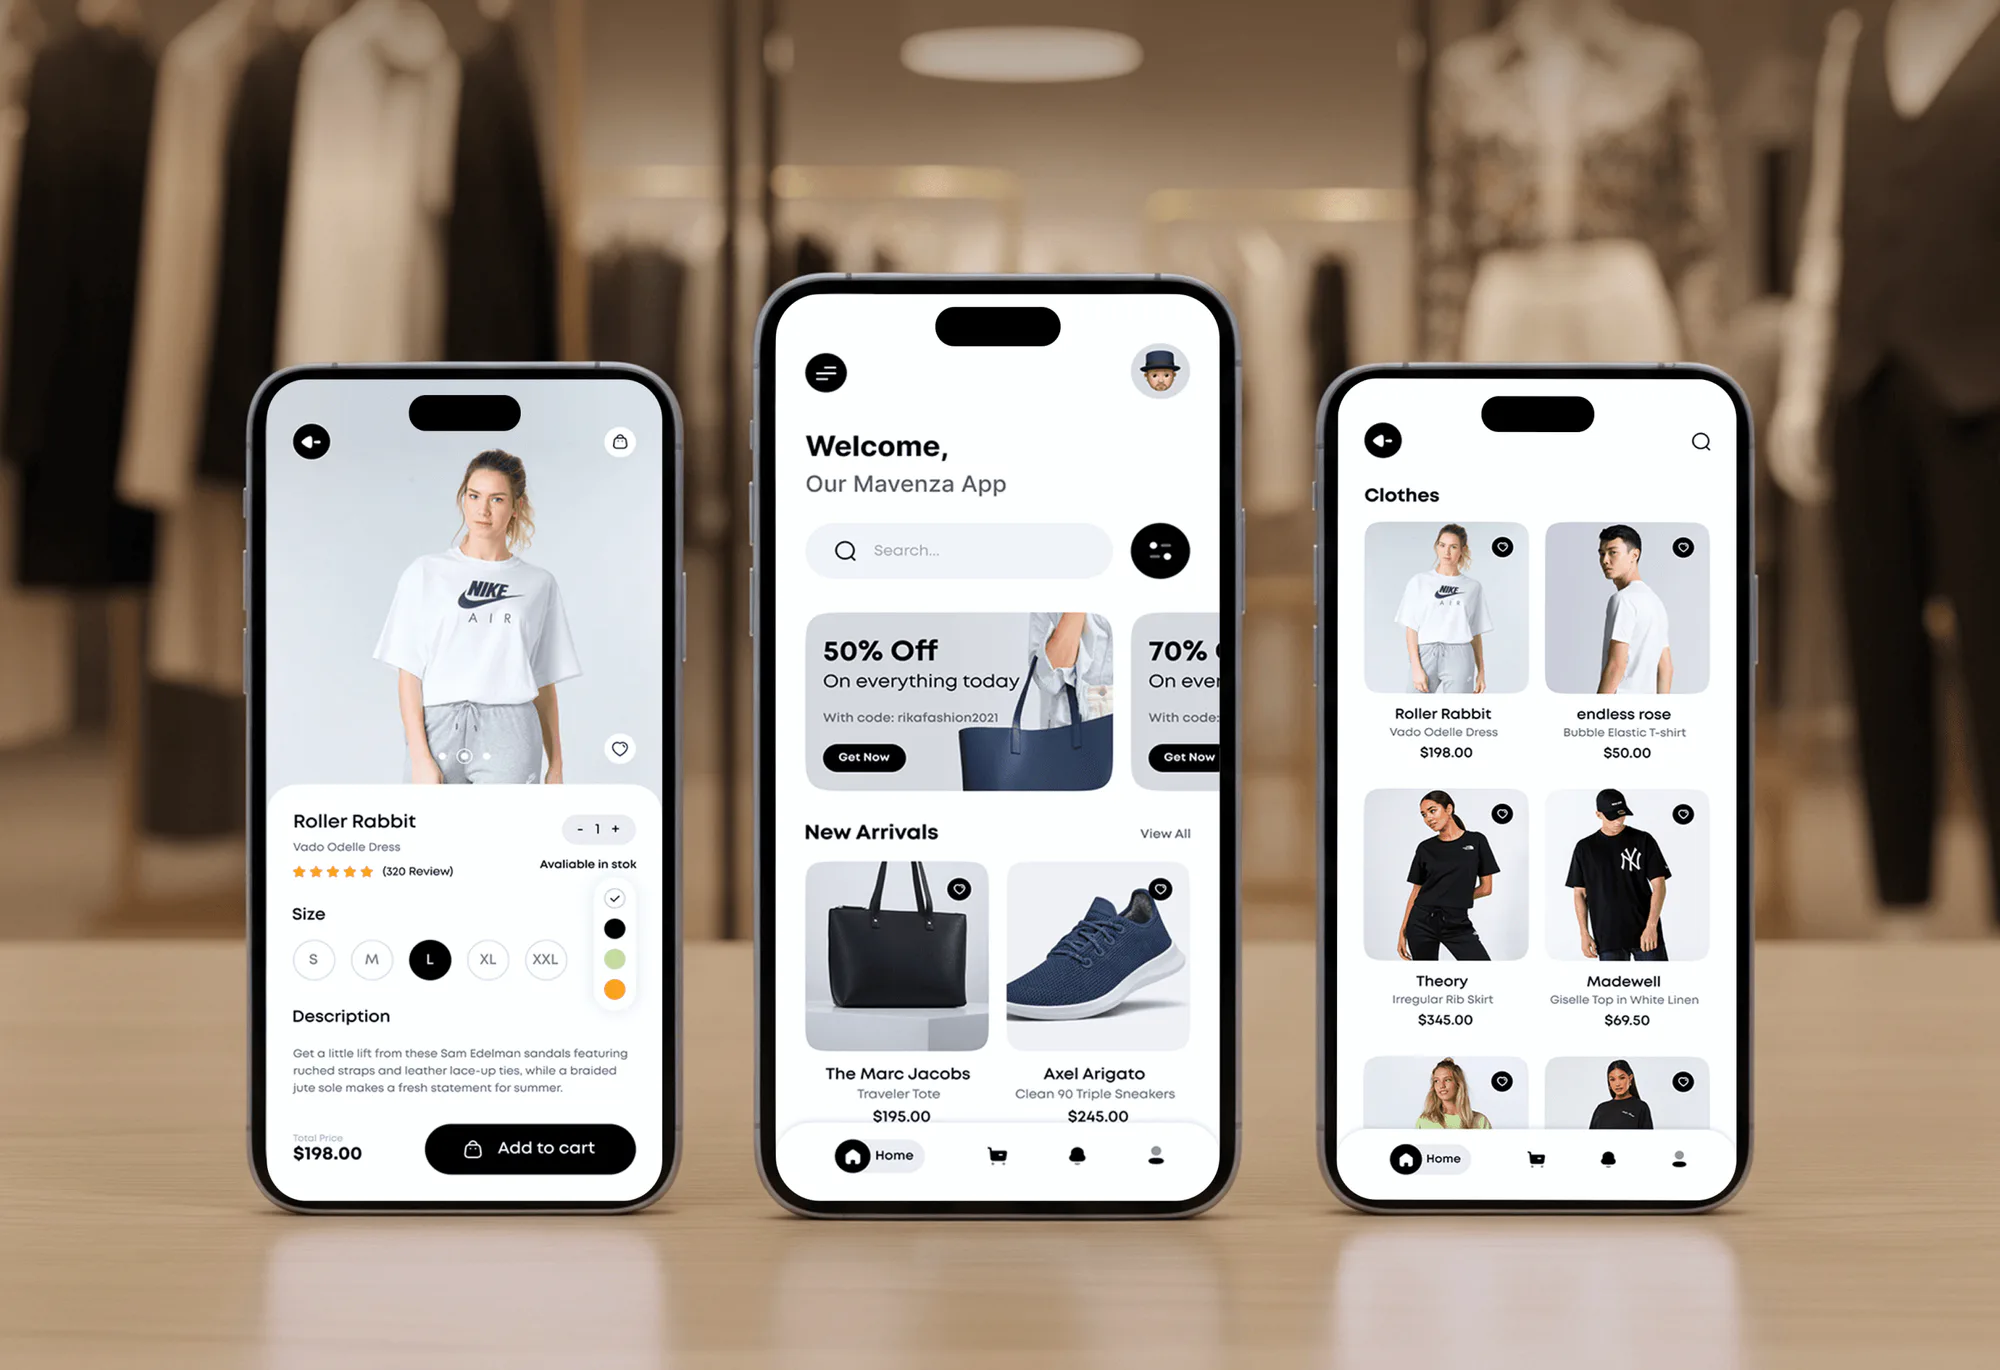
Stores with large catalogs, admin dashboards, and checkouts that we designed and built. They weren't Magento patch projects, but they show the setups this work keeps safe.
What's Included
A version and bulletin audit, the latest security release installed on staging then live, a skimmer and malware scan, cleanup where needed, admin hardening, and a report.
Compare Options
A freelancer can cost less per hour, and DIY with Composer costs nothing but your time. For a Magento security patch done with staging tests and a skimmer check, here is the difference.
| Feature | DeveloperLookBest fit | Freelancer | DIY patching |
|---|---|---|---|
| Patch audit | Every bulletin checked for your version | Usually the latest patch only | You read each bulletin |
| Testing | Staging, test orders, extensions | Varies by freelancer | Often straight on live |
| Isolated patches | Applied in release order | Sometimes missed | Easy to apply out of order |
| Skimmer scan | Files and database checked | Rarely included | Adobe scan tool only |
| Malware cleanup | Included on plans 2 and 3 | Quoted separately | Risky without a clean baseline |
| Admin review | Users, tokens, and keys rotated | Not usually | If you think of it |
| Time to start | 1 to 2 days | Depends on availability | Today, at your own risk |
| Cost | From $700 one-time | Often a lower hourly rate | Free, plus your time |
What Our Clients Say
Feedback from teams we have built stores, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Patching a live Magento store is where checkouts break. These habits keep your orders coming in while the store gets current on security.
Every patch runs on a copy of your store first. Test orders, admin logins, and your busiest extensions get checked before the live release.
Adobe builds isolated patches on the latest security release, so order matters. We apply them in sequence, which avoids the conflicts that make patching feel risky.
Skimmers can hide in store configuration and CMS blocks. We search your database too, because a clean file scan alone can miss them.
If your release line is past Adobe's support dates, we tell you and show the upgrade path. Patching an unsupported version only buys time.
Live releases happen in your quietest hours with a backup ready. You pick the window, and we stay on until the store checks out.
Admin passwords, integration tokens, and payment keys are rotated after cleanup and stay in your name. Our access comes out at handover.
Overview
DeveloperLook finds and installs every missing Magento security patch for your release line, tested on staging before it goes live. We audit your version against Adobe security bulletins, scan files and the database for skimmers, and clean malware where needed. Patch installs start at $700 and take 2 to 4 business days.
DEVELOPERLOOK
Project facts · Magento Security Patches and Audit
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Stores several patches behind
Your Magento store missed several security releases, and you want them applied without another weekend of broken checkout.
Stores linked to card skimming
Your payment provider traced fraud to your checkout, and you need Magento website malware removal and a root cause, not just a scan.
Teams with no Magento developer
Your Magento developer left, and you need someone to run a Magento security patch check and keep your store current.
Adobe Commerce Cloud merchants
You run Adobe Commerce on Cloud and need isolated patches applied through the Quality Patches Tool with the right deploy steps.
Agencies with Magento clients
Your agency supports Magento clients and needs security patches for Magento applied under your brand, with a report for each store.
Not a fit
Need a version upgrade
You're on Magento 2.4.6 or older and need a new minor release, not just patches. Our Magento 2 Upgrade and Migration Services handle that move.
Want monthly patching
You want patches, monitoring, and developer hours every month. Our Magento Support and Maintenance plans cover that from $450 per month.
Still on Magento 1
Your store runs Magento 1, which Adobe stopped supporting in June 2020. Patches won't fix that, so a move to a supported platform comes first.
Store on a hosted platform
Your store runs on Shopify or BigCommerce, which patch the platform for you. Our Ecommerce Security Services cover access and checkout scripts there instead.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your version, extensions, and any cleanup needed, and you get a fixed proposal after a free patch check.
For Agencies
You own the client relationship. We supply the Magento engineering behind it: bulletin audits, staged patch releases, skimmer scans, and cleanup when a store is compromised. Your clients stay current on security without your team losing weekends to patch days.
White label: your client only ever sees your brand
Send store URLs, versions, hosting access, and any bulletins clients asked about.
We check each store's version and patches, then give a fixed price.
We patch on staging, release, and hand over reports under your brand.
Send store URLs, versions, hosting access, and any bulletins clients asked about.
We check each store's version and patches, then give a fixed price.
We patch on staging, release, and hand over reports under your brand.
The Right Technology for Your Project
We patch with Adobe's own tools and Composer, check stores with Adobe's scanner and our own file and database searches, and work on your existing hosting.
 Magento Open SourcePHPMySQLCloudflare
 Chrome DevTools
 OWASP
FAQ
Straight answers on cost, timing, installing patches, Magento 1, malware removal, and supported versions.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our Magento security patches installation service starts at $700 for one store. That covers your bulletin audit, the latest security release on staging then live, a skimmer check, and 30 days of fix support. The $1,600 plan adds malware cleanup and an admin review. The $3,200 plan rebuilds a compromised store from a clean install and rotates every key.
A patch install takes 2 to 4 business days, including the audit, staging tests, and the live release. If your store is several releases behind, it takes longer when extensions need updates to match. Malware cleanup or a full recovery takes 1 to 3 weeks, depending on how deep the injected code goes.
You install Magento security patches by moving to the latest security release for your line with Composer, then running the upgrade and deploy steps. On a staging copy, update the version in Composer, then run setup:upgrade, compile, and static content deploy. Test your checkout and admin, back up production, and release in a quiet hour.
A single urgent fix ships as an isolated patch file, which you apply on top of the latest security release for your line. Adobe Commerce stores use the Quality Patches Tool, and Open Source stores apply the file with Composer patches or Git. Adobe tests isolated patches only against the latest release, so get your store current first.
Adobe ships a new Magento minor release about once a year, and security releases at least yearly for every supported line. Urgent fixes arrive as isolated patches in between, such as the September 2025 hotfix for the SessionReaper flaw (CVE-2025-54236). That's why we check your store against every bulletin, not only the last release.
Apply them on a staging copy first, in release order, and test your checkout before going live. Treat each Magento 2 security patch as a release: check extension compatibility, back up your database, and use maintenance mode during the deploy. Pick a low-traffic window, then watch your logs and orders for a day.
Adobe stopped releasing Magento 1 patches when support ended in June 2020, so no official patches exist now. The community OpenMage LTS project still publishes fixes, but you'd rely on volunteers for a store that takes payments. The safer path is moving to Magento 2 or another platform, and we'll help you weigh that first.
You remove malware from a Magento site by cleaning both the files and the database, then closing the way in. Compare core files to a clean Composer install, and search your database for injected scripts, especially the HTML head settings and CMS blocks. Remove unknown admin users and cron jobs, rotate every key, and patch the flaw used to get in.
Adobe's lifecycle policy gives Adobe Commerce 2.4.7 standard support until May 31, 2027, 2.4.8 until May 31, 2028, and 2.4.9 until May 31, 2029. Version 2.4.6 left standard support on August 11, 2026. If your store runs 2.4.6 or older, patches alone won't keep it covered, so plan a minor upgrade.
Every plan includes 30 days of fix support after patching. If the update affects an extension, your checkout, or a cron job, we fix it within that window. You get a report with your version, the patches applied, and what we found. For monthly patching after that, our Magento Support and Maintenance plans take over.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.