Client-by-client BA status
Each client and product checked against the HIPAA definition, so you know where business associate HIPAA duties start.

For health tech, billing, IT, and transcription vendors whose clients send BAAs: every promise you signed mapped to a real safeguard, from $850.
100%
BAA promises traced to controls
1register
Of every BAA deadline
How your project runs
01 · FreeTeams we have built for:














The Problem
It surfaces when a hospital's vendor review asks for your risk analysis or a client changes its BAA template. Sometimes a support ticket with a patient name lands in the wrong inbox first.
Mixed deadlines
Each client BAA sets a different breach reporting window.
Mixed deadlines
One register with every client's deadline, owner, and notice contact.
Stray PHI
Patient names sit in support tickets and debug logs.
Stray PHI
Logs masked, tickets redacted, and support tools set up for patient data.
Contractor gap
An offshore contractor sees patient data without a BAA.
Contractor gap
Subcontractor BAAs signed, and access limited to what each role needs.
Missing analysis
A hospital review asks for a document you don't have.
Missing analysis
A written risk analysis of your product, team, and vendors, kept current.
Your sales team signed a BAA to close the clinic deal, then another client sent its own template with a 5-day breach reporting clause. Nobody compared them. Patient names sit in support tickets, debug logs, and a shared drive, and your offshore contractor can see all three without a BAA of their own. A hospital's vendor review now asks for your security risk analysis, and the honest answer is that you don't have one. Leave it, and one incident turns every unread clause into a contract breach.
We start with the contracts, because they set your real deadlines. Every signed BAA is read and its promises go into one register: reporting windows, subcontractor terms, and what happens to data at termination. Then we map where patient data actually flows in your product and team, write the risk analysis and policies, and sign BAAs with your own vendors. Your HIPAA program then matches what you promised, not a template's guess.
Every BAA read closely
Signed agreements compared clause by clause, so different client deadlines stop hiding in PDFs.
Patient data mapped end to end
Tickets, logs, backups, analytics, and AI tools traced, because PHI leaks outside the product.
Your own vendors covered
Cloud, support, and contractor BAAs signed downstream, so your promises carry through the chain.
Our HIPAA Compliance for Business Associates Process
You see your BAA obligations side by side first, then approve the data map, the risk analysis, each policy, and every vendor agreement before your team is trained.
We go over what you sell, which providers you serve, what patient data you touch, and the BAAs you have signed. You leave with a fixed quote. If your contracts and data flow are simple enough for a short policy set, we'll tell you before we quote.
What's Included
Everything a vendor needs to keep its BAA promises: a status check by client, an obligations register, a data map, a risk analysis, downstream agreements, training, and a breach notice runbook.
Compare Options
Compliance software and a healthcare lawyer each cover part of a vendor's HIPAA duties, and each is the better choice for some jobs. The rows show what each one handles and what is left over.
| Feature | DeveloperLookBest fit | Compliance software | Law firm |
|---|---|---|---|
| Planning | Free call, fixed written scope | Self-serve onboarding | Hourly engagement letter |
| BAA review | Every clause logged with deadlines | Upload and store only | Strong on terms and liability |
| Data mapping | Product, support, logs, contractors | Cloud integrations only | Not usually included |
| Risk analysis | Written for your product | Questionnaire-based template | Rarely written in-house |
| Technical safeguards | MFA, logs, access checked | Automated cloud checks | Not covered |
| Team training | Live session, signed records | Video course and quiz | Not usually included |
| Cost | Fixed price from $850 | Low yearly subscription | Hourly, often higher |
| Ownership | Documents and register stay yours | Stored in the platform | Yours, in legal memos |
Projects We've Built
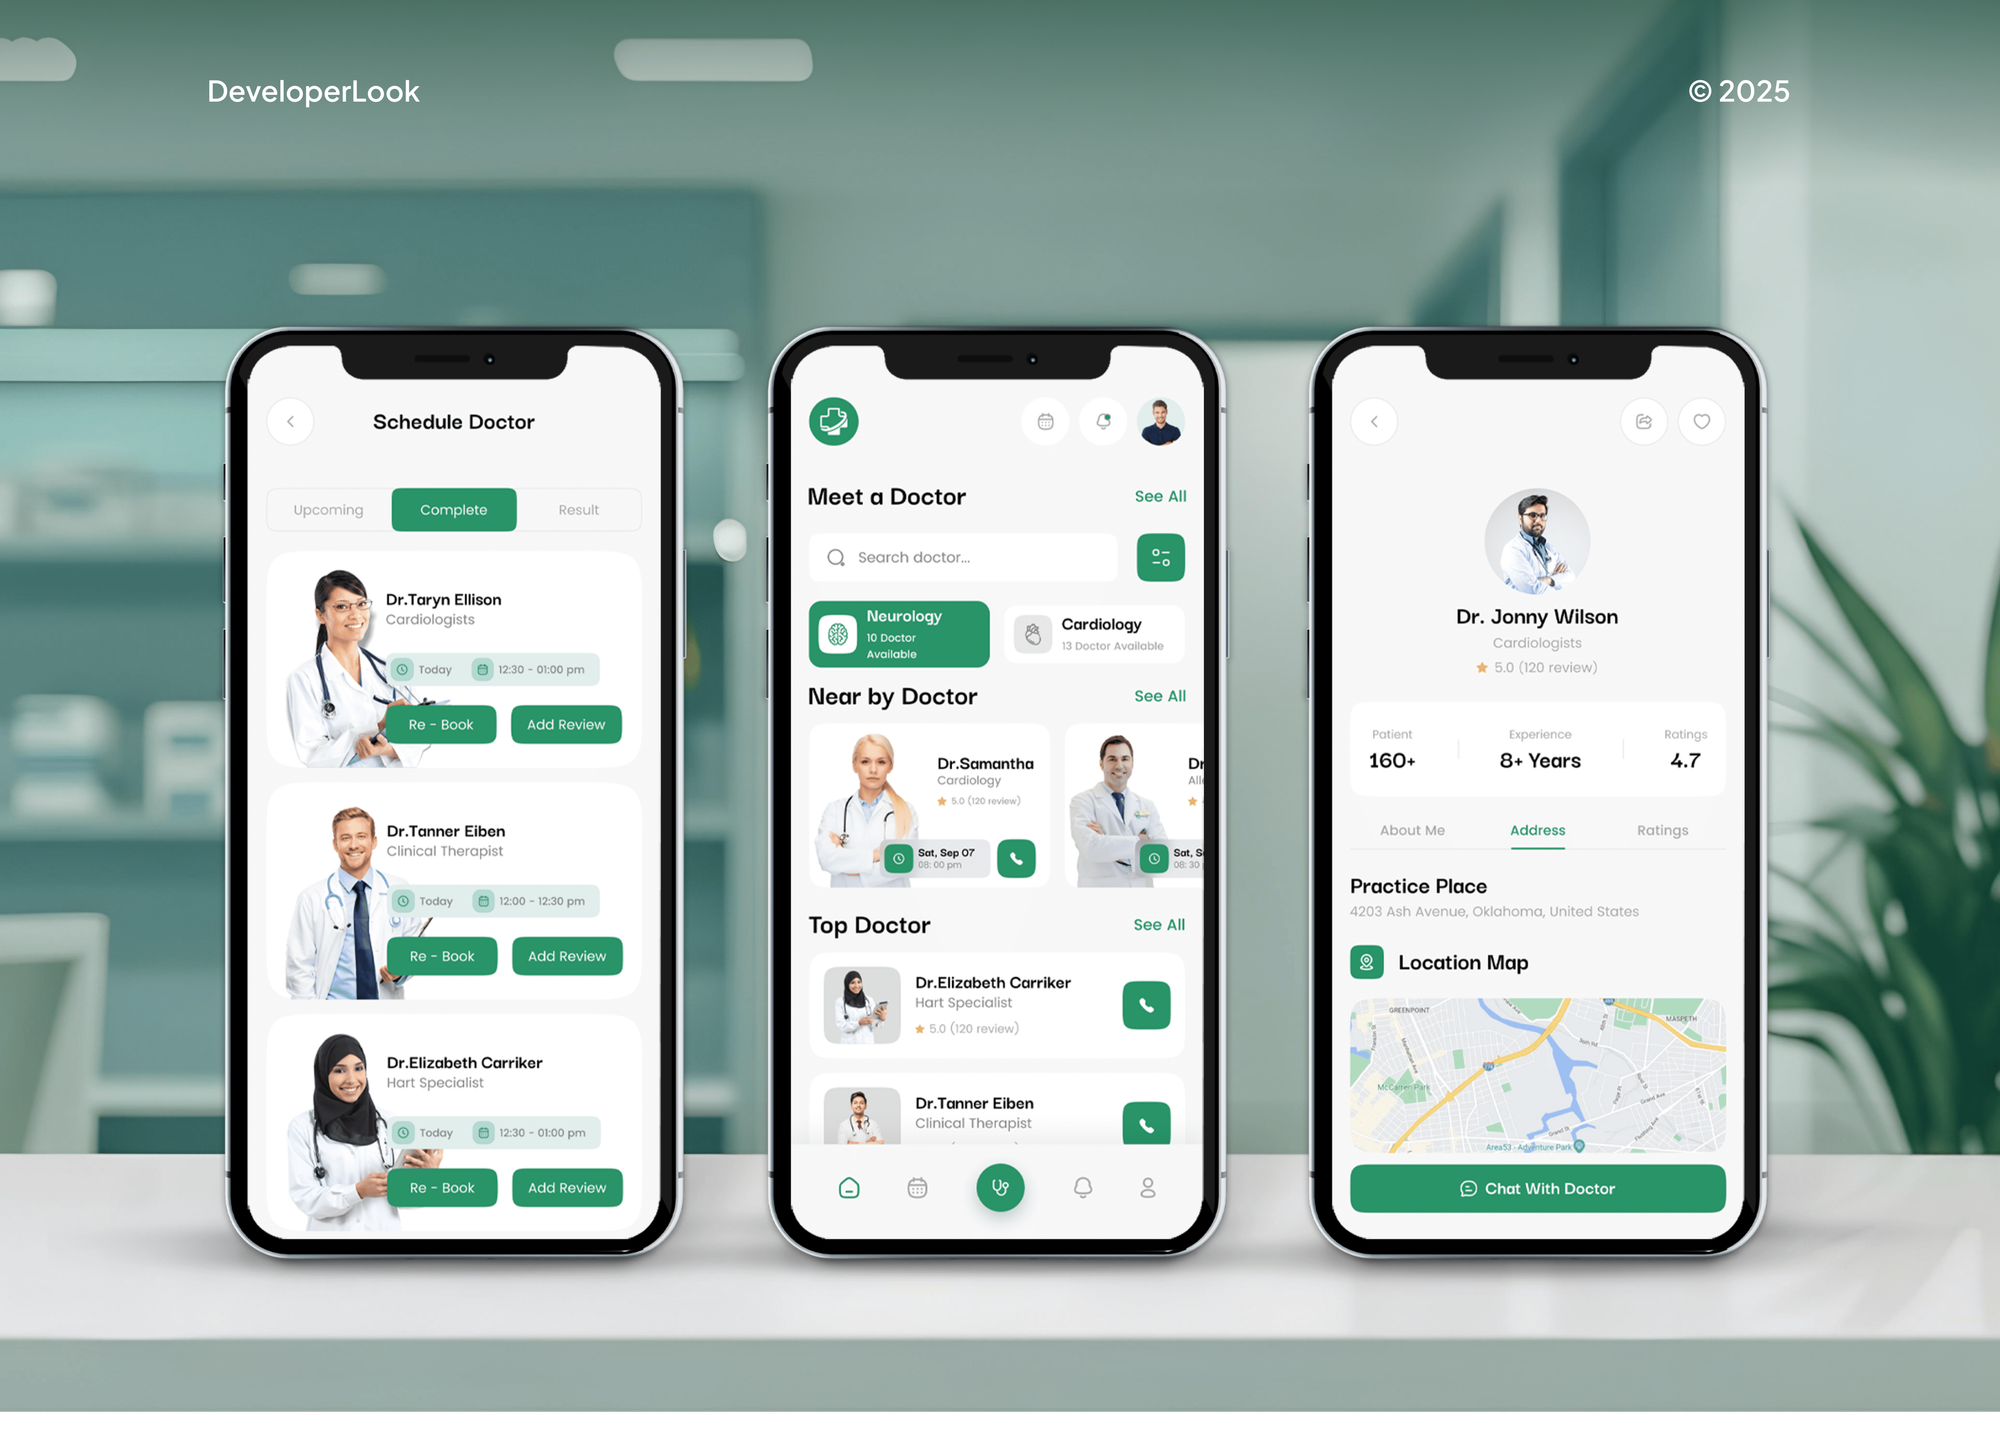
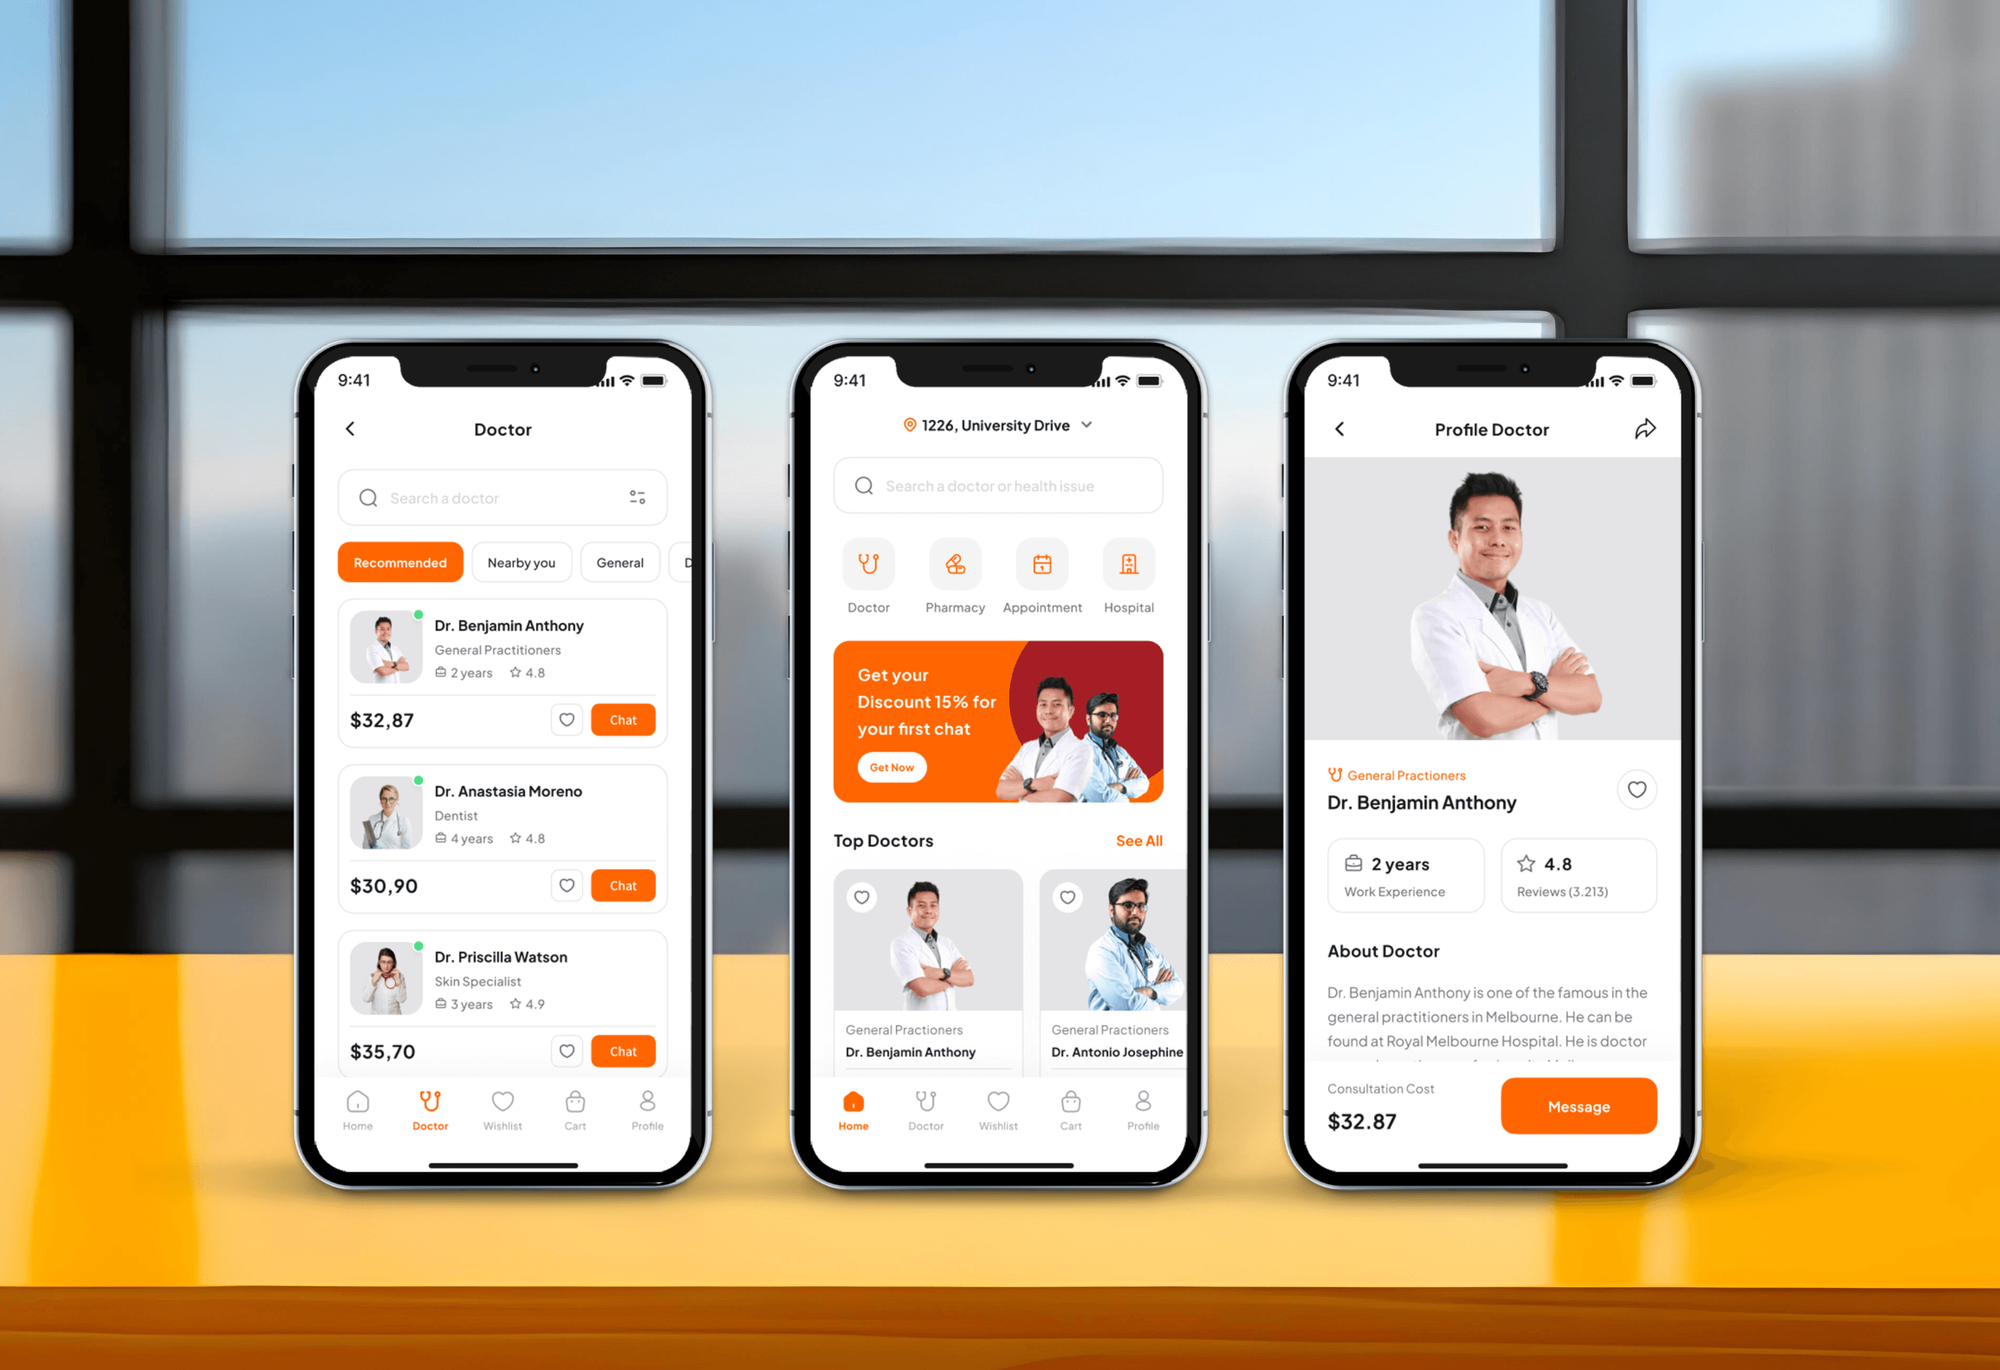
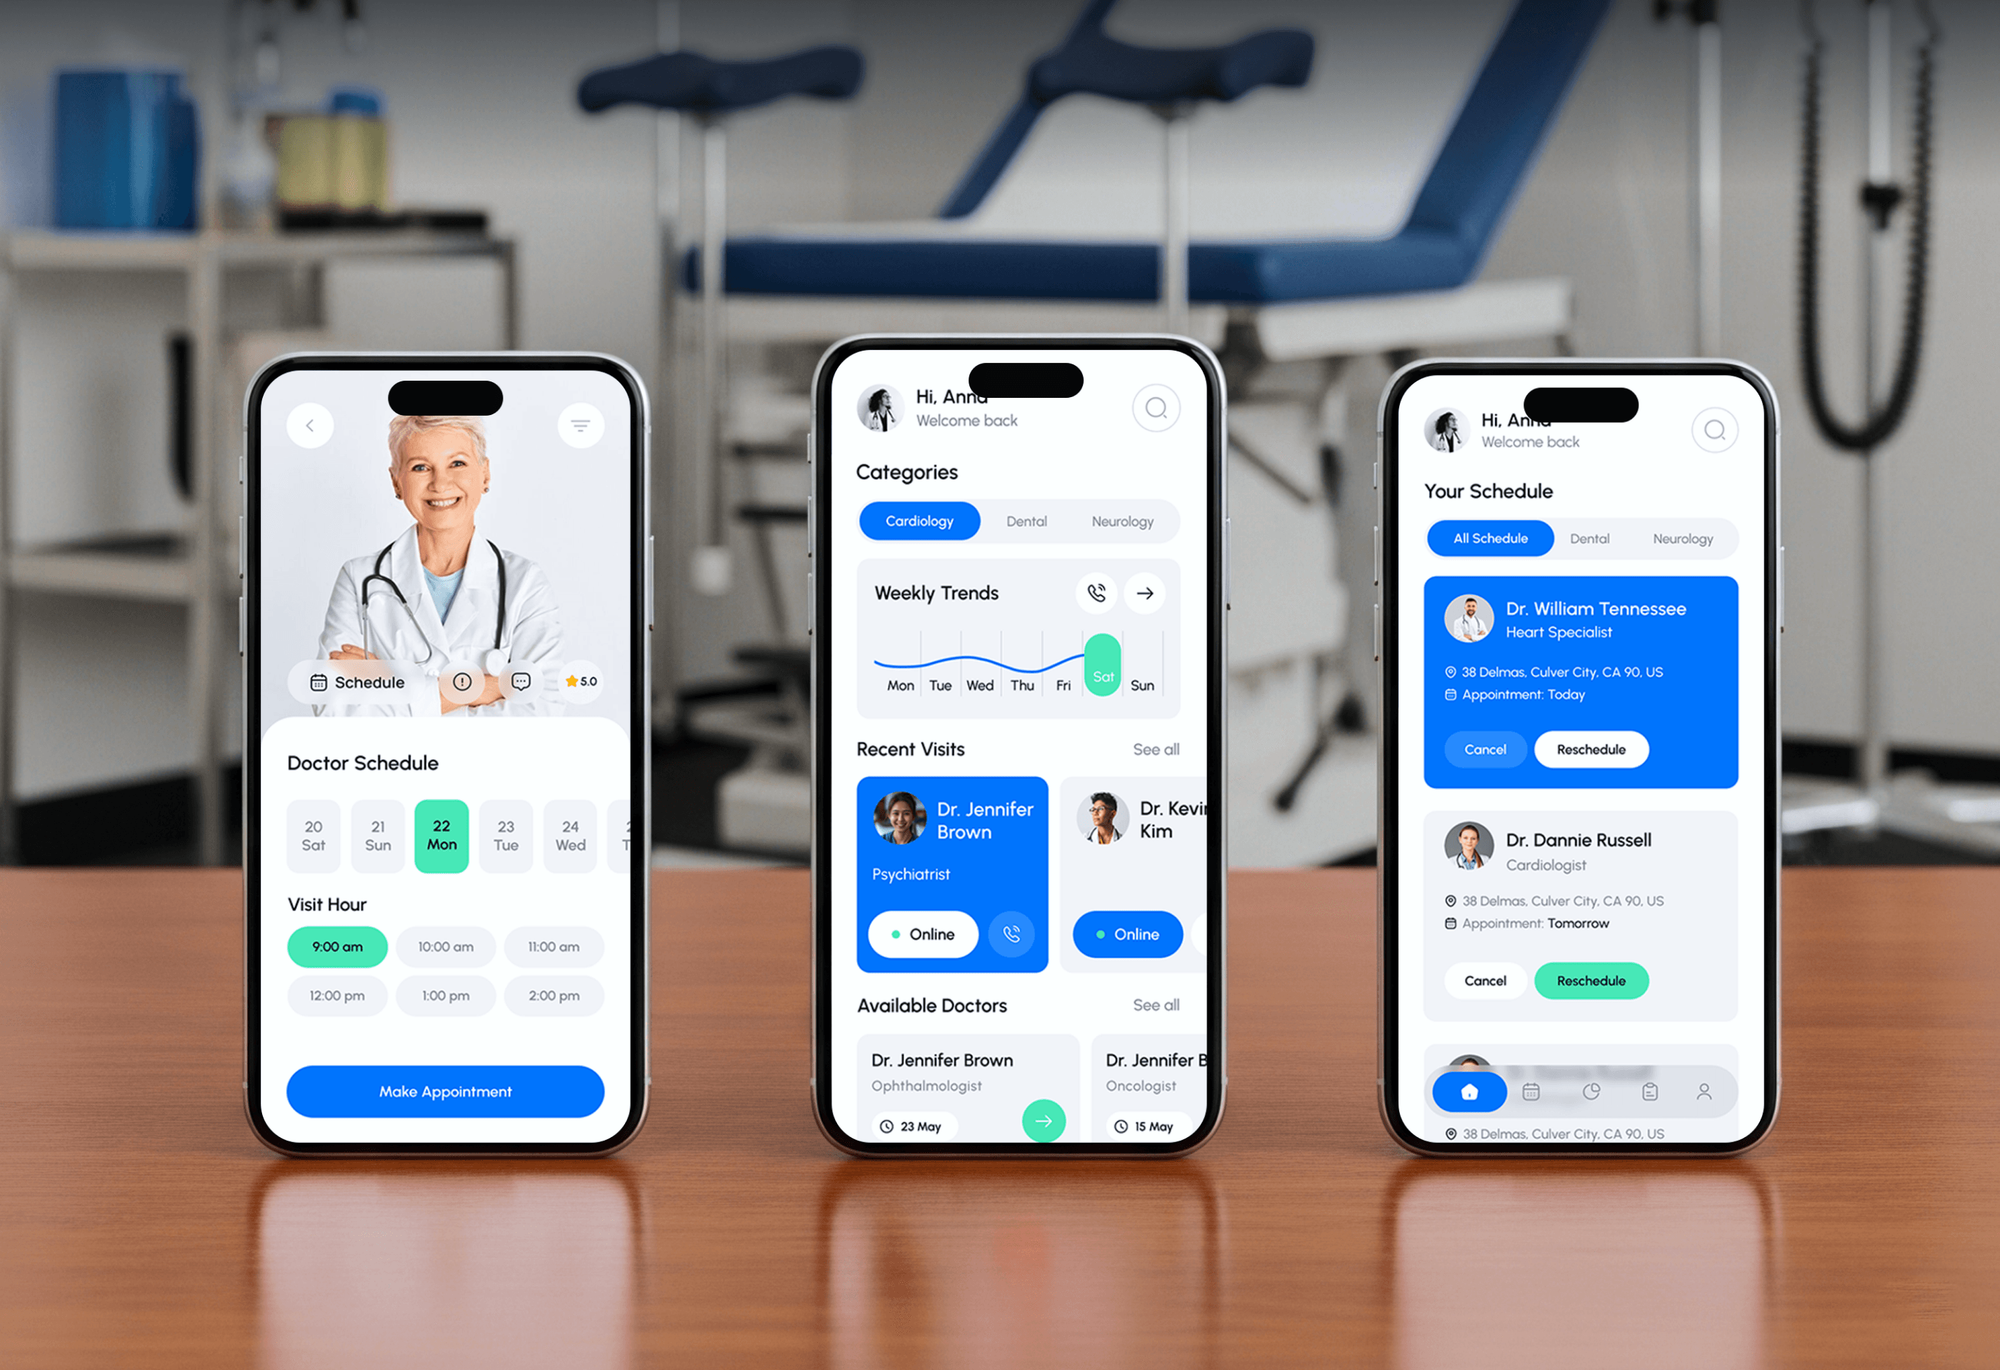
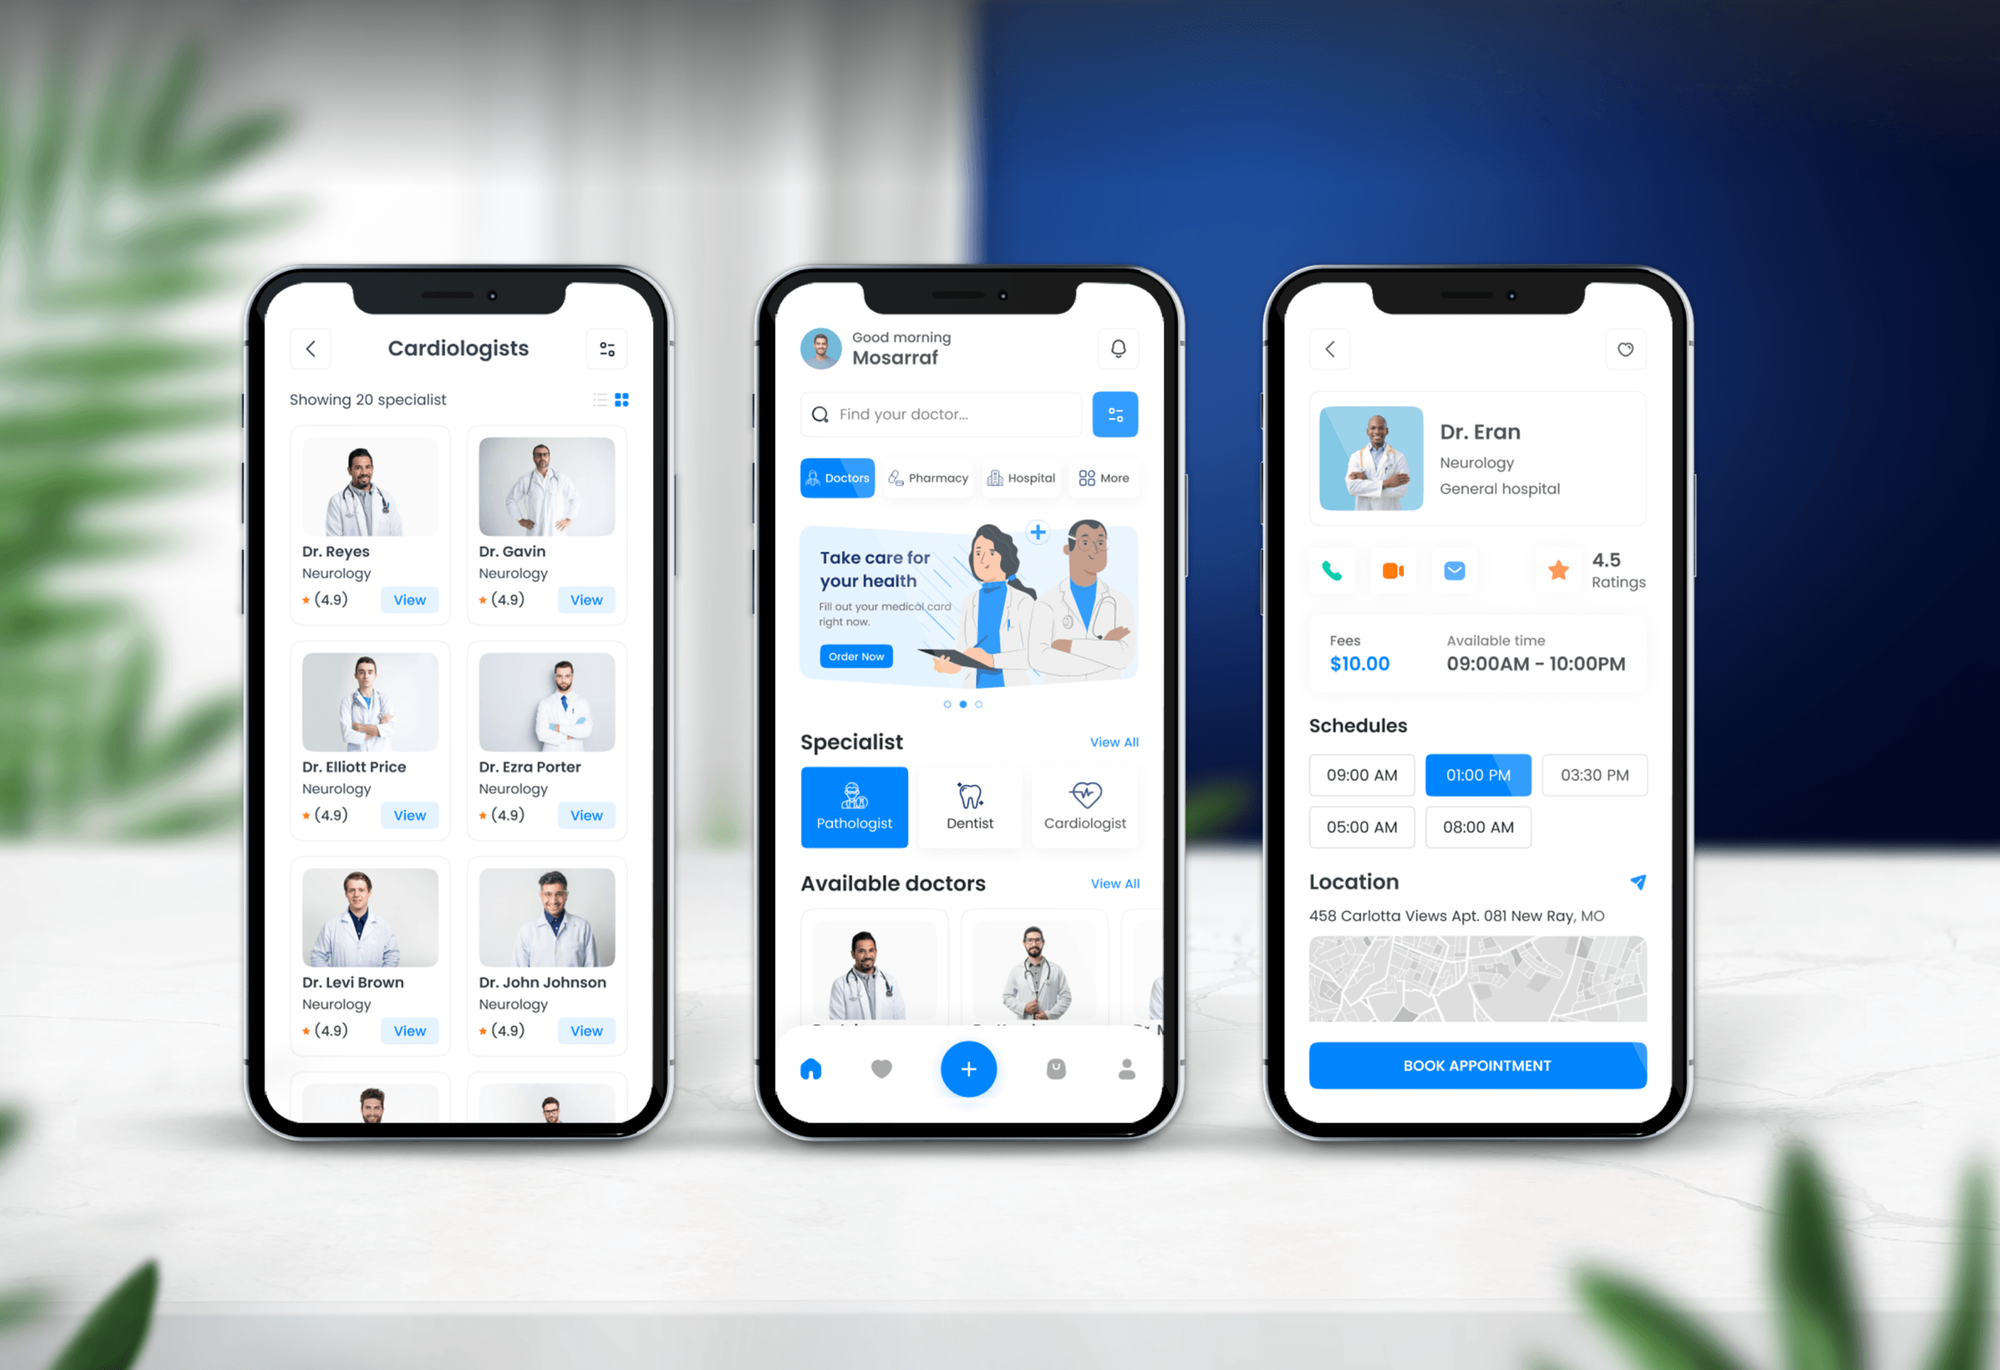
These patient booking and medical apps were design and build projects, the kind of software health vendors sign BAAs for. None was a HIPAA compliance engagement.
What Our Clients Say
Feedback from teams we have built apps, portals, and platforms for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
We work from your contracts, your product, and your team's real habits. That keeps the program practical for vendors without a compliance department or a security hire.
We read your signed BAAs before writing a single policy. Your duties come from those agreements, so a generic template can miss the clause that matters.
Our team knows logs, APIs, and cloud settings, not just policy language. We can tell where patient data really travels inside your product.
HIPAA for business associates applies only where you handle a provider's patient data. We tell you when a client relationship falls outside it.
We work beside your lawyer on contract terms rather than replacing them. You get the technical evidence while legal advice stays with counsel.
You get one price for your products, clients, and team size before work starts. Extra products get their own quote up front.
Policies, the register, training records, and the risk analysis sit in one folder you own. A client review takes hours instead of weeks.
Overview
DeveloperLook sets up HIPAA compliance for business associates such as health tech, billing, IT, and transcription vendors. We confirm your status by client, log every BAA promise, map patient data, write the risk analysis and policies, and sign downstream BAAs. Projects start at $850, a full program takes 4 to 10 weeks, and every document stays yours.
DEVELOPERLOOK
Project facts · HIPAA Compliance for Business Associates
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Health tech SaaS selling to providers
Your first hospital customer sent a BAA and a long vendor security review, and nobody on your team has written a HIPAA policy before.
Medical billing and coding companies
You handle claims, remittances, and patient balances for many practices, and each client's BAA sets a different breach reporting window.
IT providers and MSPs for clinics
Your technicians reach EHR servers and backups through remote tools, and a clinic just asked for proof of your business associate HIPAA safeguards.
AI scribe and transcription vendors
Your product records visits and stores notes in the cloud, so HIPAA business associates rules apply to every audio file you keep.
Agencies serving health tech clients
You run compliance or engineering work for health vendors and need BAA readiness delivered under your brand, with your client signing off.
Not a fit
You're the provider
You run a clinic or practice and need your own program as a covered entity. HIPAA Compliance Services covers providers rather than their vendors.
Risk analysis only
You only need the written security risk analysis for one client's review. HIPAA Security Risk Assessment Services is the narrower and cheaper fit.
Need a legal opinion
You need contract terms negotiated, indemnity advice, or an answer to an OCR letter. That is legal work for a healthcare lawyer, and we work alongside your counsel.
Budget under $850
You have one small client, no subcontractors, and under $850 to spend. HHS's sample business associate agreement provisions and a short policy set are a better start.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your products, the number of client BAAs, and your team size, and you get a fixed proposal after a free vendor call.
For Agencies
You own the health tech client and the relationship. We supply the HIPAA work behind it: BAA reviews, data maps, risk analyses, policies, and training, delivered in your branding for your client's team to approve and sign.
White label: your client only ever sees your brand
Share the product, client BAAs, and team size, and we scope it in 2 business days.
One fixed white-label price and a named lead for each vendor client.
Register, policies, and training records arrive under your brand for client approval.
Share the product, client BAAs, and team size, and we scope it in 2 business days.
One fixed white-label price and a named lead for each vendor client.
Register, policies, and training records arrive under your brand for client approval.
The Right Technology for Your Project
These are the cloud, identity, support, and record tools where business associates keep patient data. We secure what your team already runs before suggesting anything new.
 AWS
 Google Cloud
 Microsoft Azure
 Cloudflare
 Zendesk
 Slack
 Google Sheets
Related Services
Vendors that finish this work often add a full risk assessment, a security questionnaire library, or SOC 2. Each page below covers one of them.
This page
HIPAA Compliance for Business Associates
Pairs with the 6 services around it
FAQ
Straight answers on cost, timing, who counts as a business associate, BAA terms, and team training.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our work starts at $850 for a BAA readiness review covering up to 5 signed BAAs and one product. You get the status check, the obligations register, a data map, and a ranked gap list. A full program with risk analysis, policies, subcontractor BAAs, and training costs $2,250, and vendors with several products start at $4,500.
A BAA readiness review takes 1 to 2 weeks. A full program takes 4 to 10 weeks, depending on how many products, client agreements, and subcontractors you have. Most of that time goes to the data map and policy approvals, which we schedule around your releases so engineering keeps shipping.
A business associate is a person or company that creates, receives, maintains, or transmits protected health information for a covered entity. HHS defines the term in 45 CFR 160.103. The test is the work you do with patient data, not your job title, and a covered entity can also be another provider's business associate.
Common examples are billing and coding companies, EHR and practice software vendors, IT providers, cloud hosts, transcription services, and claims processors. Lawyers, accountants, and consultants count too when their work involves patient data. A provider's own employees are part of its workforce, so they aren't business associates.
Usually you still are, because HHS treats cloud services that store patient data as business associates even when they can't read it. The narrow exception covers pure conduits, such as internet providers or couriers, that only carry data briefly. Storing encrypted backups for a clinic doesn't qualify for that exception.
A BAA is a business associate agreement: the written contract a covered entity must have before a vendor handles its patient data. It limits how the vendor may use the data, requires safeguards, and sets reporting duties. The same contract is required between you and any subcontractor that touches that data.
45 CFR 164.504(e) lists the HIPAA business associate agreement requirements. The contract must limit uses and disclosures, require safeguards, and make you report breaches and improper uses. It must also flow the same terms to subcontractors and support patient access and amendment requests. It opens your records to HHS and requires return or destruction of data at termination.
Our session covers the patient data your team actually sees: support tickets, logs, screenshots, exports, and recorded calls. It explains what counts as PHI, the minimum necessary rule, phishing, lost devices, and how to report an incident inside the client deadline. Everyone signs an attendance record, and new hires get a short version.
Yes, and ours follows your contracts rather than a generic list. It checks BA status, signed BAAs, a written risk analysis, policies, access controls, audit logs, encryption, subcontractor agreements, training records, and breach procedures. This is the HIPAA compliance business associates owe their clients, and the checklist stays yours after handover.
Your named security officer does, using the register, runbook, and yearly calendar we leave. The calendar sets dates to refresh the risk analysis, retrain staff, review access, and recheck every client and vendor BAA. We answer questions for 30 days after handover, and later reviews can be booked as fixed-price jobs.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.