Control inventory
What you really run across engineering, IT, HR, and support, written down before any answer.

For SaaS teams whose enterprise deals wait on a vendor review: honest, evidence-backed answers delivered on deadline, and a library that makes the next one faster.
2X
Faster answers next time
100%
Answers tied to evidence
How your project runs
01 · FreeTeams we have built for:














The Problem
It shows up at the end of an enterprise sale, when procurement sends a vendor security questionnaire. Then your founder, CTO, and sales lead each answer a different tab.
Ownership
Sales, the CTO, and IT each answer different tabs.
Ownership
One owner per topic, with answers drafted from interviews and evidence.
Old answers
Last year's answers get pasted in unchecked.
Old answers
Every reused answer checked against current settings before it goes out.
Gaps
Rows about missing controls get an optimistic Yes.
Gaps
A plain No or Partial, with context and a planned fix date.
Format
Each buyer's spreadsheet starts from a blank page.
Format
A library mapped to common formats, so new spreadsheets fill faster.
Procurement sent a spreadsheet with hundreds of rows and a ten-day deadline. Sales forwarded it to your CTO, who answered the encryption tab at midnight. Someone pasted answers from last year's response, including a pen test you didn't run this year. Half the rows ask about policies nobody has written down. The deal now waits on a document that can come back to bite you, because buyers can treat those answers as promises in the contract.
We start with your real controls, not the questionnaire. We interview the people who run engineering, IT, and support, collect the evidence, and answer each question from what exists. A No stays a No, with context and a date when a fix is planned. Then every answer goes into a library mapped to the common formats, so the next questionnaire starts mostly filled in.
Evidence behind every answer
Each answer links to a policy, screenshot, or report section a reviewer can ask to see.
Honest No answers
Missing controls are answered plainly, with context and a date when a fix is planned.
A library that compounds
Answers mapped to SIG, CAIQ, and VSA formats, so later questionnaires start mostly done.
Our Security Questionnaire Response Process
You see every drafted answer with its evidence, approve the wording of each No, and decide what goes back to the buyer.
We look at the questionnaire, the deadline, and the deal stage, and ask which reports you already have. You get a fixed quote and a plan that meets the buyer's date.
What's Included
Each project covers a control inventory, the urgent questionnaire, an evidence folder, and the reusable library and fixes your plan includes.
Compare Options
Questionnaire software speeds up repeat answers, and your own team knows the product best. Here is where each one fits and where it falls short.
| Feature | DeveloperLookBest fit | Questionnaire software | In-house team |
|---|---|---|---|
| Answer source | Interviews plus evidence | Past answers and documents | Whoever is free that day |
| Honest No answers | Written with context and dates | Depends on the source answers | Often softened under deal pressure |
| Speed on repeats | Fast once the library exists | Strong, built for reuse | Slow, starts from scratch |
| Evidence links | Every answer linked to proof | Varies by tool setup | Rarely tracked |
| Fixing gaps | Quick fixes on the top plan | Not included | Possible, competes with the roadmap |
| Cost | Fixed price from $600 | Yearly subscription | Engineering and sales time |
| Product knowledge | Learned through interviews | Only what's documented | Strong, they built it |
| Ongoing desk | Handed back with a library | Strong, runs continuously | Ongoing, but internal |
Projects We've Built
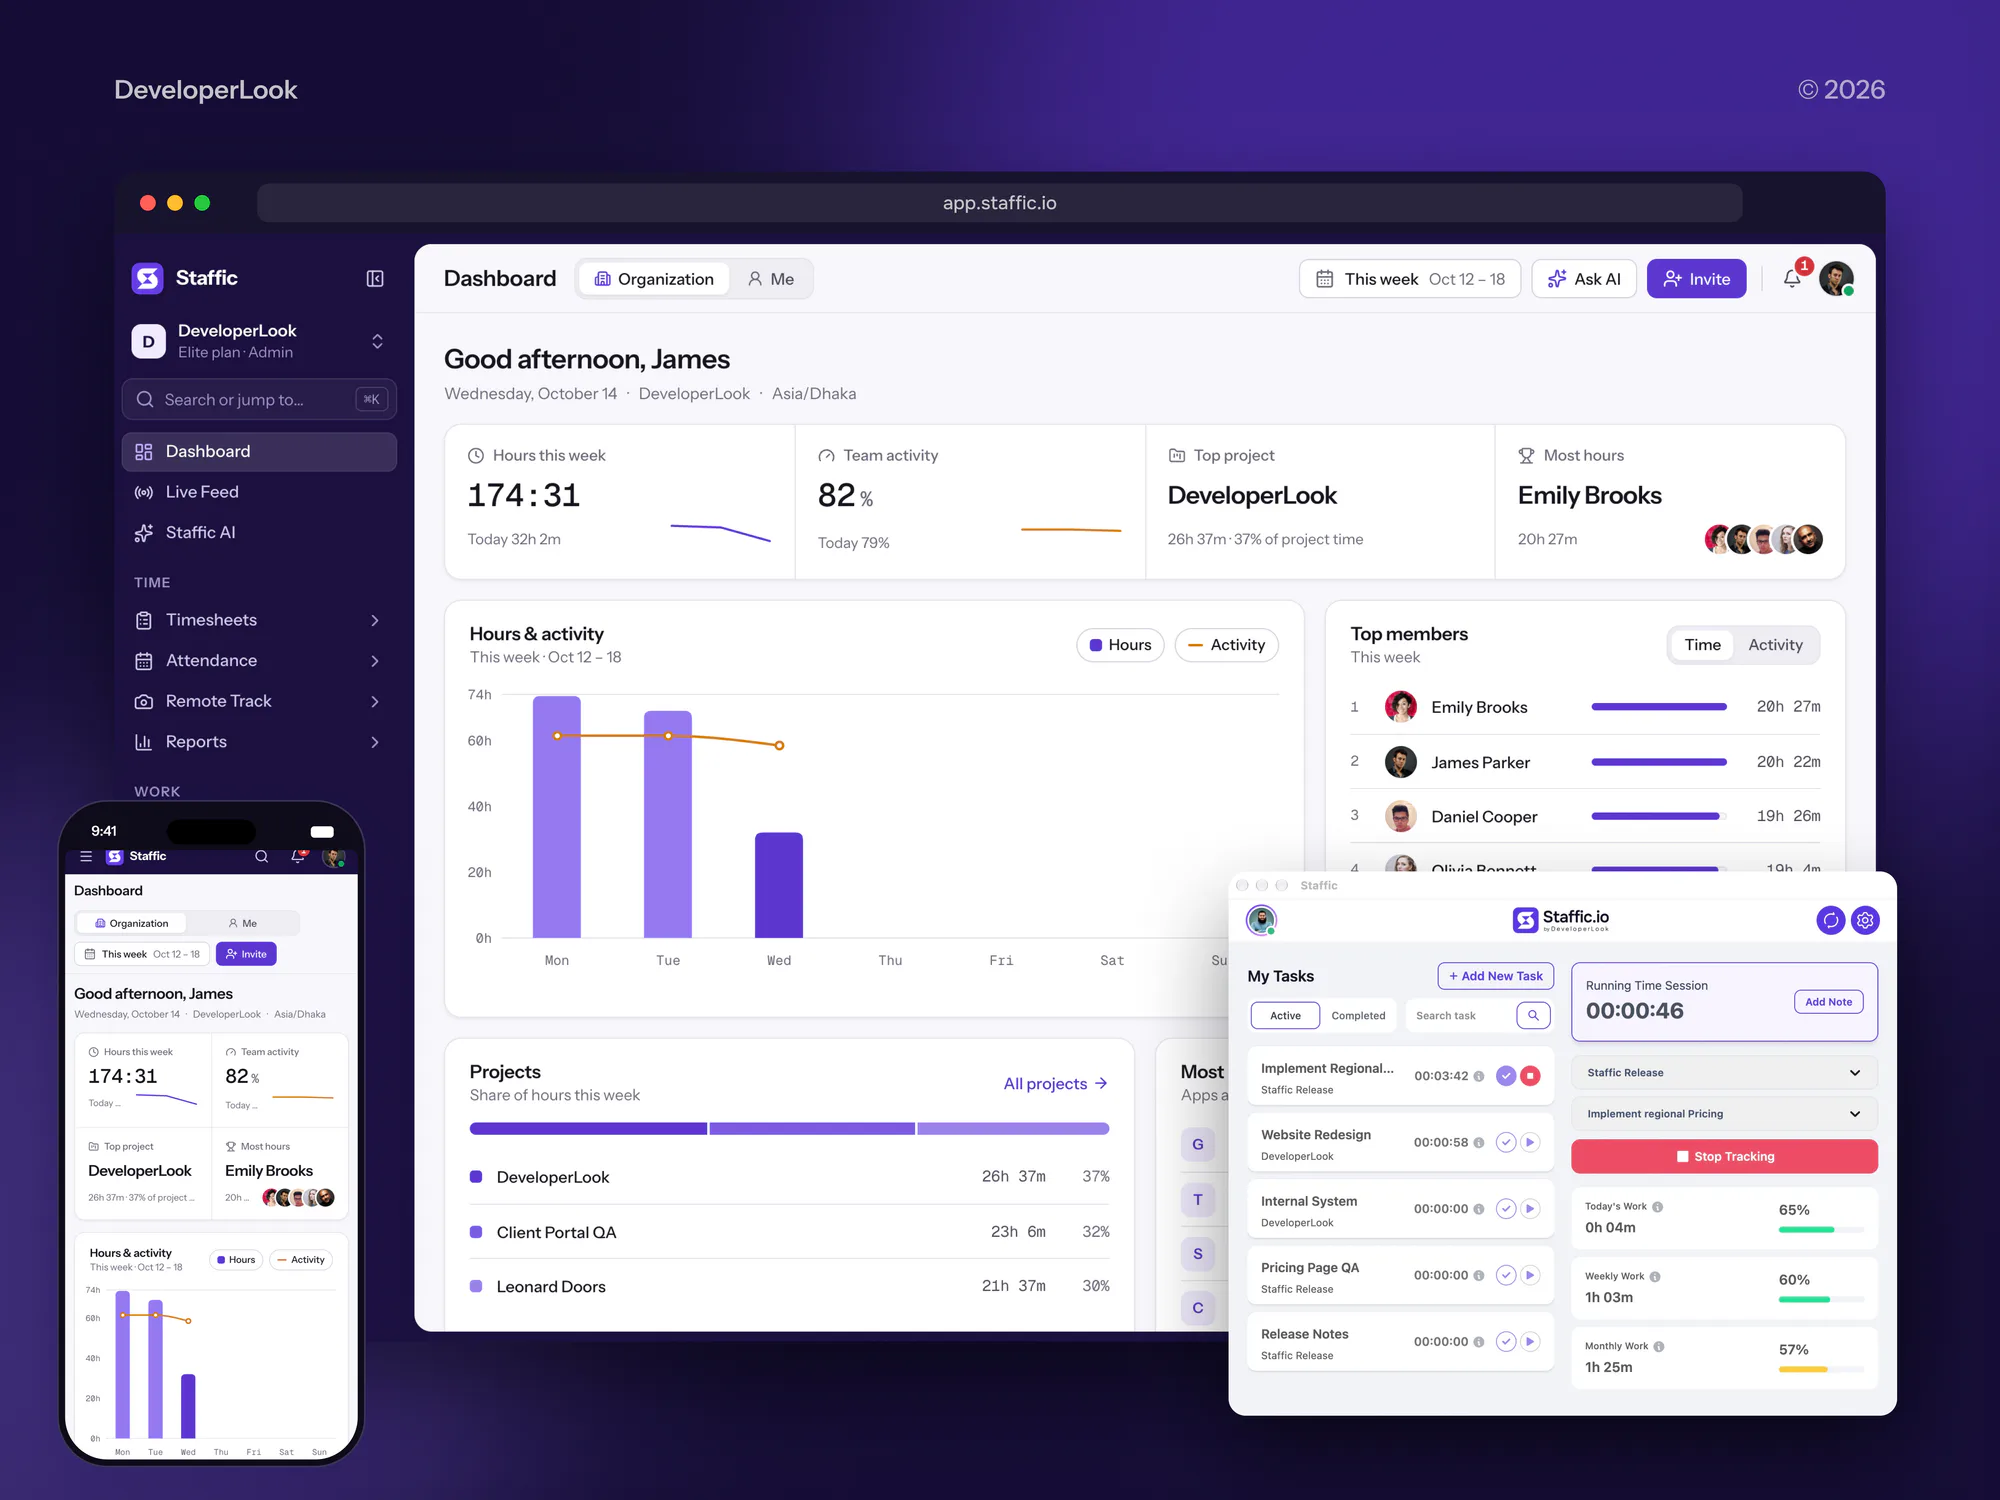
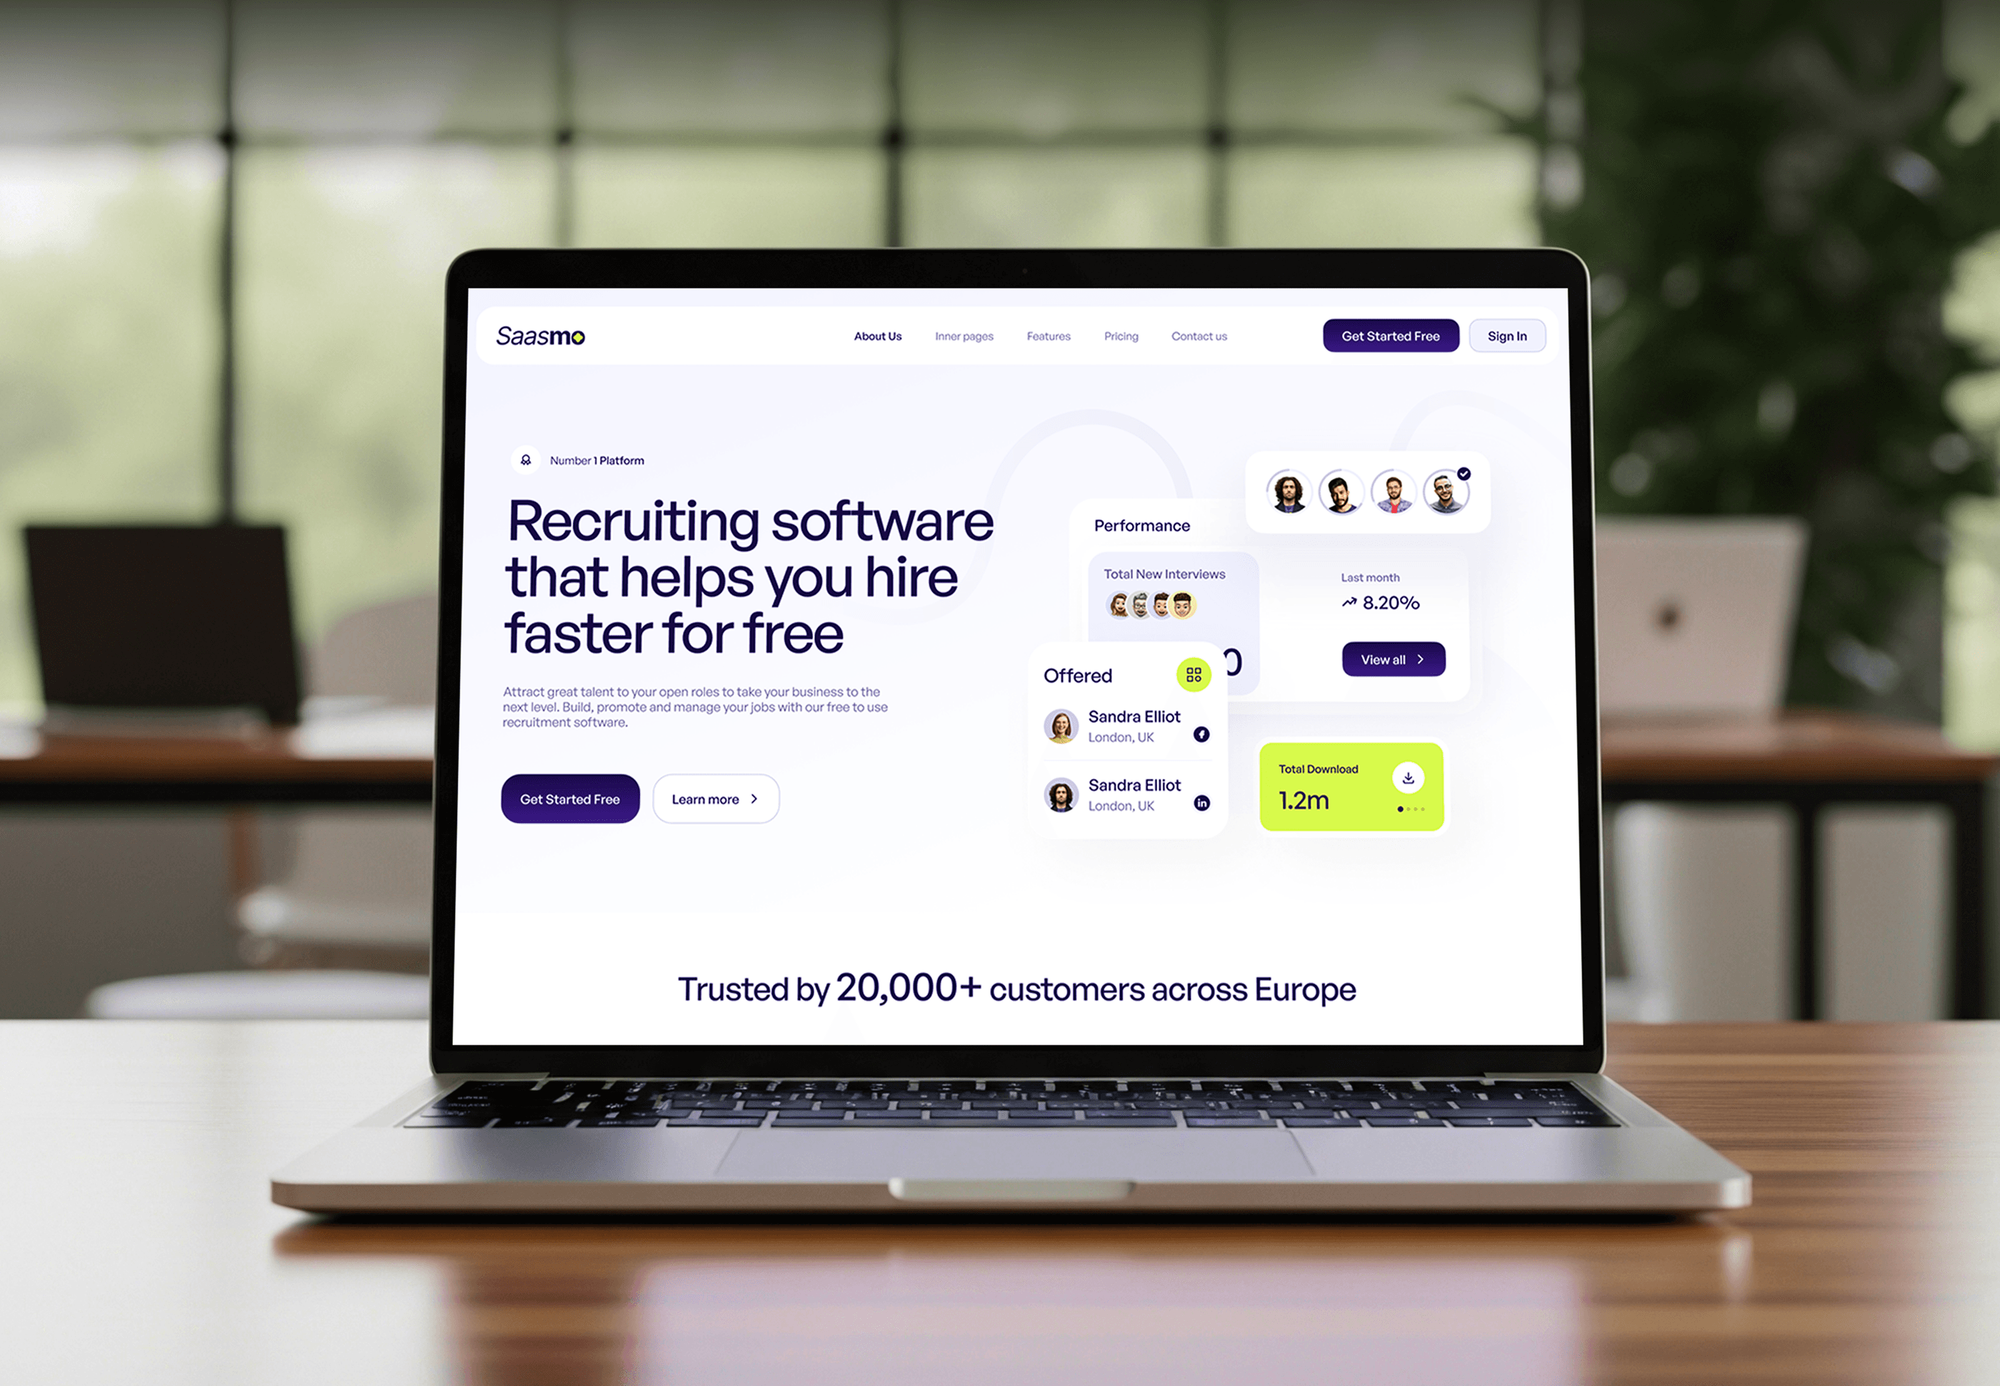
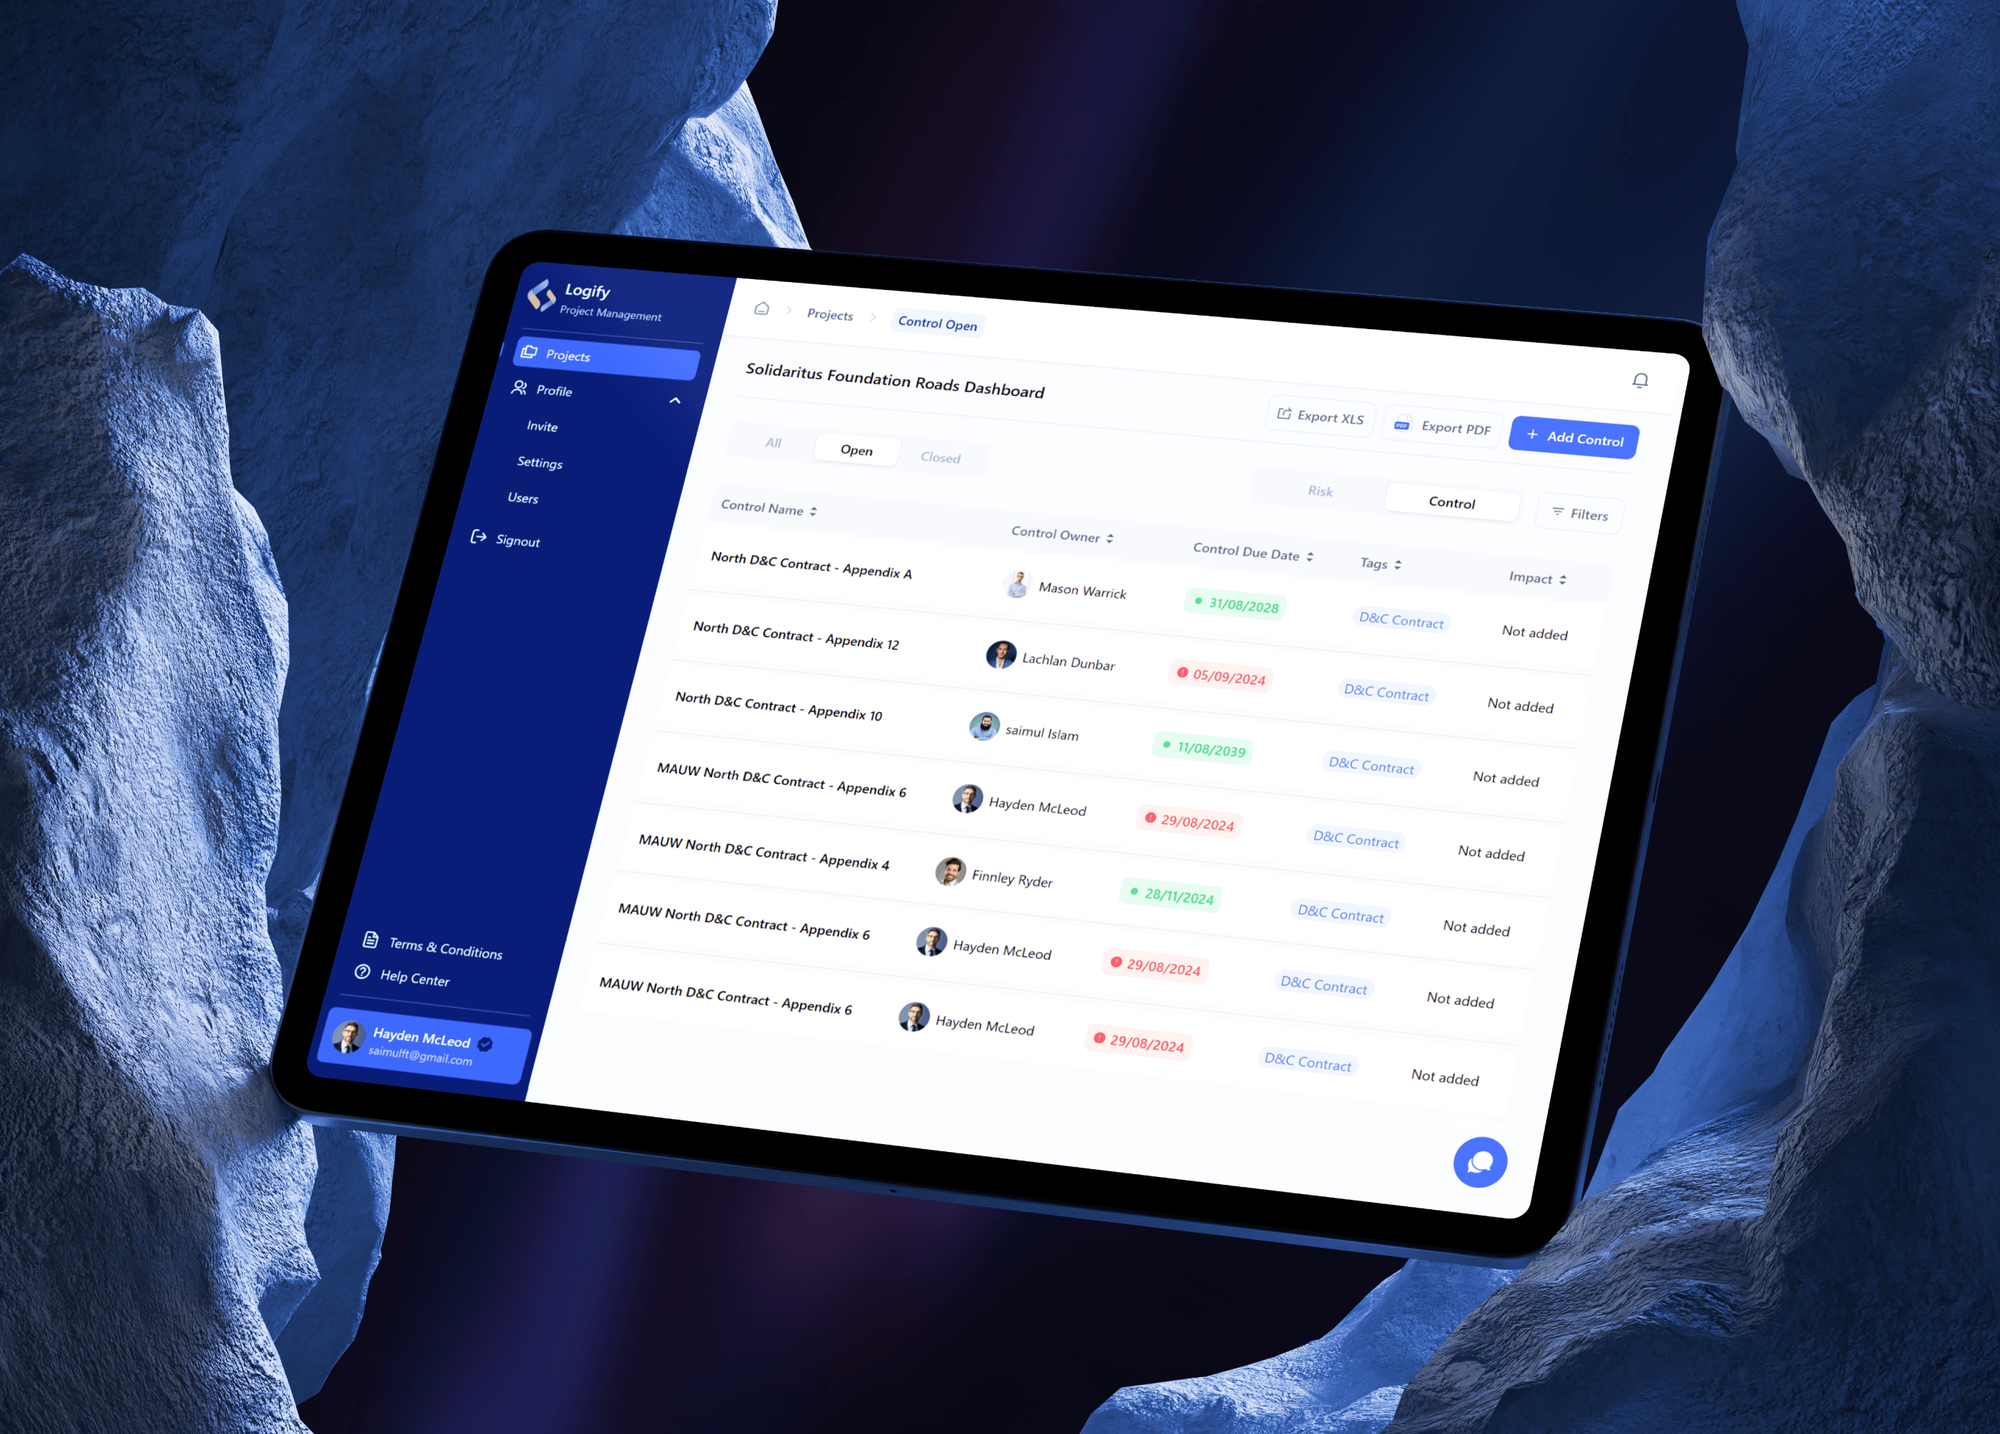
Time tracking, recruiting, logistics, and finance SaaS products we designed and built. They show our engineering on real products, not past questionnaire work.
What Our Clients Say
Feedback from teams we have built platforms, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A questionnaire answer can end up in your contract. These habits keep every answer true, provable, and quick to reuse.
We don't turn a missing control into a Yes to save a deal. Buyers can treat answers as promises, so honest context protects you later.
Every answer starts from a policy, setting, or report we can open. Wording comes second, so a reviewer's follow-up questions have ready evidence.
We work from the buyer's due date, not from our queue. Drafts reach you early enough to review without a midnight scramble.
Most answers need interviews and screenshots, not admin rights. When we do need access, it's read-only and removed as soon as we finish.
If questionnaire software would serve you better than a service, we'll tell you before we quote. Teams with steady volume often need both.
Quotes depend on question count, formats, and fixes, and they're fixed before work starts. A second urgent questionnaire is quoted the same day.
Overview
DeveloperLook handles security questionnaire responses for SaaS teams in enterprise deals, with every answer tied to evidence. We inventory your real controls, complete the urgent questionnaire, and build a reusable answer library for SIG, CAIQ, VSA, and custom spreadsheets. Projects start at $600, take 1 to 8 weeks, and no answer claims a control you lack.
DEVELOPERLOOK
Project facts · Security Questionnaire Response Service
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
SaaS teams in their first enterprise deal
Your first enterprise buyer sent a security assessment questionnaire with a ten-day deadline, and nobody on the team has filled one in.
Startups without a security lead
Your CTO spends more time answering security questionnaires than shipping, and you need someone to own the next three before the quarter ends.
Sales teams losing time in review
Your sales cycle stalls for weeks at the vendor security assessment questionnaire stage, and you want answers ready before procurement asks.
Companies with SOC 2 or ISO 27001
Your SOC 2 report covers most questions, but each cyber security questionnaire asks them in a different format, so answers get retyped every time.
Vendors serving regulated buyers
Your buyers in finance or healthcare send a security compliance questionnaire with every renewal, and last year's answers no longer match your setup.
Not a fit
Need an ongoing security desk
You get questionnaires every week and want someone answering them on a retainer. Our vCISO Services page covers that ongoing role.
Have almost no controls yet
You have almost no security controls in place, so most answers would be No. Our SOC 2 Compliance Services or Cybersecurity Services pages come first.
Want answers that hide gaps
You want every answer marked Yes regardless of what exists. We won't do that, because buyers can rely on those answers in contracts.
Need buyer-side reviews
You're the buyer and need to send and score vendor questionnaires. Our Vendor Risk Management Services page covers that side of the review.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on question count, formats, and the fixes you want included, and you get a fixed proposal after a free call.
For Agencies
You own the client relationship. We supply the control interviews, drafted answers, and answer library under your brand, so your SaaS clients clear vendor reviews without you staffing a security writer.
White label: your client only ever sees your brand
Send the questionnaire, the deadline, and any SOC 2 report or policies the client has.
We interview the client's team and draft evidence-backed answers for your review.
You approve the answers, and we hand over a white-label library for reuse.
Send the questionnaire, the deadline, and any SOC 2 report or policies the client has.
We interview the client's team and draft evidence-backed answers for your review.
You approve the answers, and we hand over a white-label library for reuse.
The Right Technology for Your Project
We work in the formats buyers send and keep the answer library in tools your team already uses.
 Google Sheets
 AWS
 Slack
Related Services
Teams often add a SOC 2 report, ISO 27001, SCIM for enterprise buyers, or an outside CISO to keep answers current.
This page
Security Questionnaire Response Service
Pairs with the 6 services around it
FAQ
Straight answers on cost, speed, the common formats, and how to answer honestly without losing the deal.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our work starts at $600 for one questionnaire of up to 250 questions, answered from interviews and evidence. A reusable library mapped to SIG, CAIQ, and VSA with up to 3 questionnaires starts at $1,900. Adding fixes for up to 5 quick gaps and up to 6 questionnaires starts at $4,100.
Most single questionnaires take 3 to 5 business days, depending on question count and how quickly your team joins the interviews. A full answer library takes 2 to 4 weeks. If a buyer's date is tighter, tell us on the first call and we'll plan backward from it.
It's a list of questions a buyer sends a vendor before signing, to check how the vendor protects data. Questions cover access control, encryption, incident response, backups, and staff security. Some buyers use a standard format such as SIG or CAIQ, while others send their own spreadsheet.
It's the same idea under another name: a security assessment questionnaire is the form a buyer uses to assess a vendor's security before buying. Procurement teams often send it as part of a wider vendor review, alongside requests for a SOC 2 report, policies, or a pen test summary.
SIG, the Standardized Information Gathering questionnaire, is a widely used format from Shared Assessments for assessing third-party risk. It comes in a shorter SIG Lite and a fuller SIG Core, and Shared Assessments updates it regularly. Organizations that send it license it, and vendors answer the version they receive.
The VSA questionnaire is a free vendor security questionnaire published by the Vendor Security Alliance, a group of companies that assess their suppliers. It comes in a shorter core version and a full version. Our answer library maps your answers to it alongside SIG and CAIQ, so one answer can serve all three.
Respond from evidence, not memory. Confirm what the buyer actually needs, gather the policies and settings behind each topic, then answer each row plainly, including No and Partial where true. Attach or offer evidence, and keep the approved answers in a library so the next response starts from them.
Split it by topic and give each topic one owner: engineering, IT, HR, or legal. Answer from current evidence, flag questions that don't apply with a short reason, and have one person review the whole set for consistency. We run this same flow on every questionnaire we handle.
Build once, then reuse. A library of approved answers mapped to SIG, CAIQ, and VSA turns most new questionnaires into a review job instead of a writing job. A security overview document or SOC 2 report sent early can also shorten what the buyer asks for.
Ask the buyer early whether a standard format or your SOC 2 report can replace their custom spreadsheet. Skip sections that don't apply with a one-line reason instead of a long answer. After handover you also get 30 days of follow-up help with buyer questions on what you submitted.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.