HHS performance goal scorecard
Each site scored on the 10 essential and 10 enhanced goals, with gaps ranked by patient impact.

For clinic groups, care networks, and health tech vendors: every site scored against HHS's 20 performance goals, gaps fixed, and restores timed. From $1,000.
20/20
HHS performance goals scored
1restore
Timed before you need it
How your project runs
01 · FreeTeams we have built for:














The Problem
The gap shows up when a site goes back to paper charts or a hosted vendor's outage stops claims. It also shows up when a hospital partner asks which HHS performance goals you meet.
Restores
Nobody knows how long restoring the EHR server takes.
Restores
A restore of one critical system is timed, and the result goes into the plan.
Site habits
Each clinic sets up logins and laptops its own way.
Site habits
Every site meets one baseline built on the essential HHS performance goals.
Vendor risk
Hosted vendors holding patient data weren't asked about security.
Vendor risk
Each vendor gets written security requirements and an incident reporting term.
Downtime
The paper fallback lives in one manager's head.
Downtime
Downtime procedures are written with clinical leads and kept at every site.
At 6 a.m. the EHR at one of your clinics won't load, and the front desk starts writing appointments on paper. Nobody knows when a backup was last restored, or how long a restore takes. Your newest site still shares one login for the PACS viewer, and the billing mailbox has no MFA. The vendor hosting your patient portal hasn't been asked about its own security. Every site does it differently. Then a hospital partner asks which HHS performance goals you meet.
We start by scoring every site against the 10 essential and 10 enhanced HPH Cybersecurity Performance Goals that HHS published. Then we close the essential goals first: MFA, email security, separate admin accounts, same-day leaver removal, and patching for known exploited flaws. We time a real restore of a critical system and write EHR downtime procedures your clinical leads sign off. Every site ends up meeting one standard, and you can show it.
All 20 HHS goals scored
Every site measured against the essential and enhanced performance goals, with gaps ranked.
Restores timed, not assumed
A real restore of a critical system, timed, so downtime plans use real numbers.
Downtime plans clinicians use
Paper workflows for registration, orders, and medications for when the EHR is unreachable.
Our Healthcare Cybersecurity Services Process
You approve the scope and the change windows, and your clinical leads sign off the downtime procedures before they reach any site or partner.
We ask how many sites you run, which EHR and PACS systems you use, and who hosts them. You leave the call with a scope outline, and a fixed price follows in writing. If HHS's free 405(d) resources fit your size, we'll say so first.
What's Included
The full scope covers scoring every site against the HHS goals, the essential fixes, a timed restore, downtime procedures, and vendor requirements. The top plan adds segmentation, logging, and an asset inventory.
Compare Options
Cybersecurity in healthcare needs both daily IT and a standard to measure against. A healthcare MSP runs devices well, and compliance software tracks tasks. Here is where each one fits.
| Feature | DeveloperLookBest fit | Healthcare MSP | Compliance software |
|---|---|---|---|
| Framework | All 20 HHS performance goals | Varies by provider | HIPAA checklist modules |
| Clinical downtime | Procedures written with clinicians | Rarely covered in contracts | Not covered |
| Restore testing | Timed restore of a critical system | Backups run, restores seldom timed | Not covered |
| Fixing gaps | Essential goals put in place | Strong at day-to-day IT fixes | Tracks tasks, fixes nothing |
| Vendor risk | Requirements and reporting terms written | Not usually included | Questionnaire templates included |
| Ongoing operations | 30 days, then your team or MSP | Ongoing support in the contract | Ongoing dashboard and reminders |
| Partner evidence | Folder mapped to the HHS goals | Gathered when someone asks | Policy library and reports |
| Cost predictability | Fixed price from $1,000 | Monthly fee per device | Yearly subscription per user |
Projects We've Built
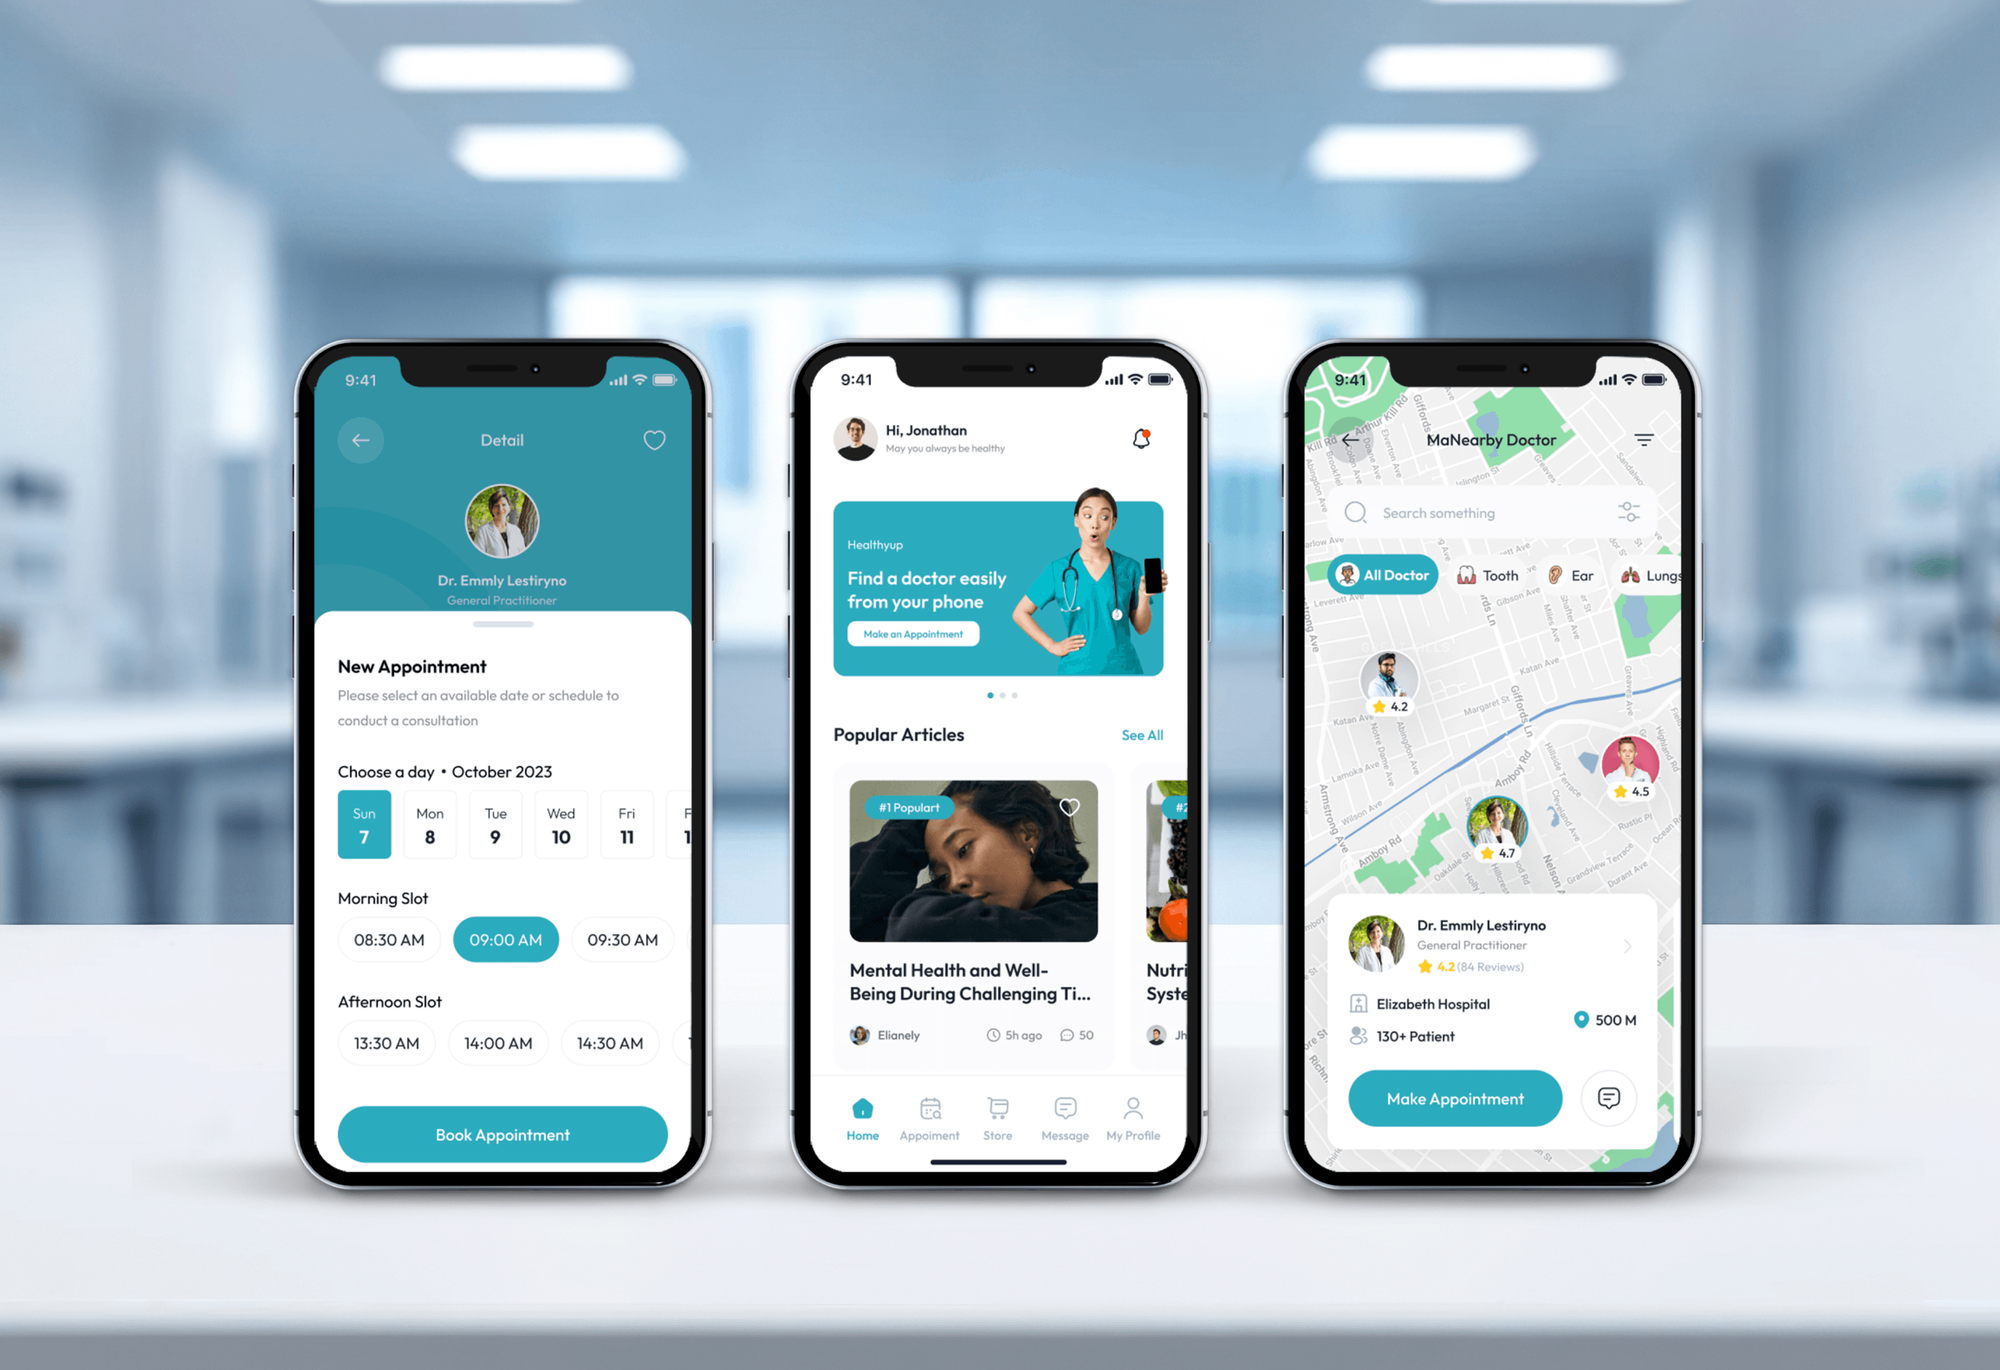
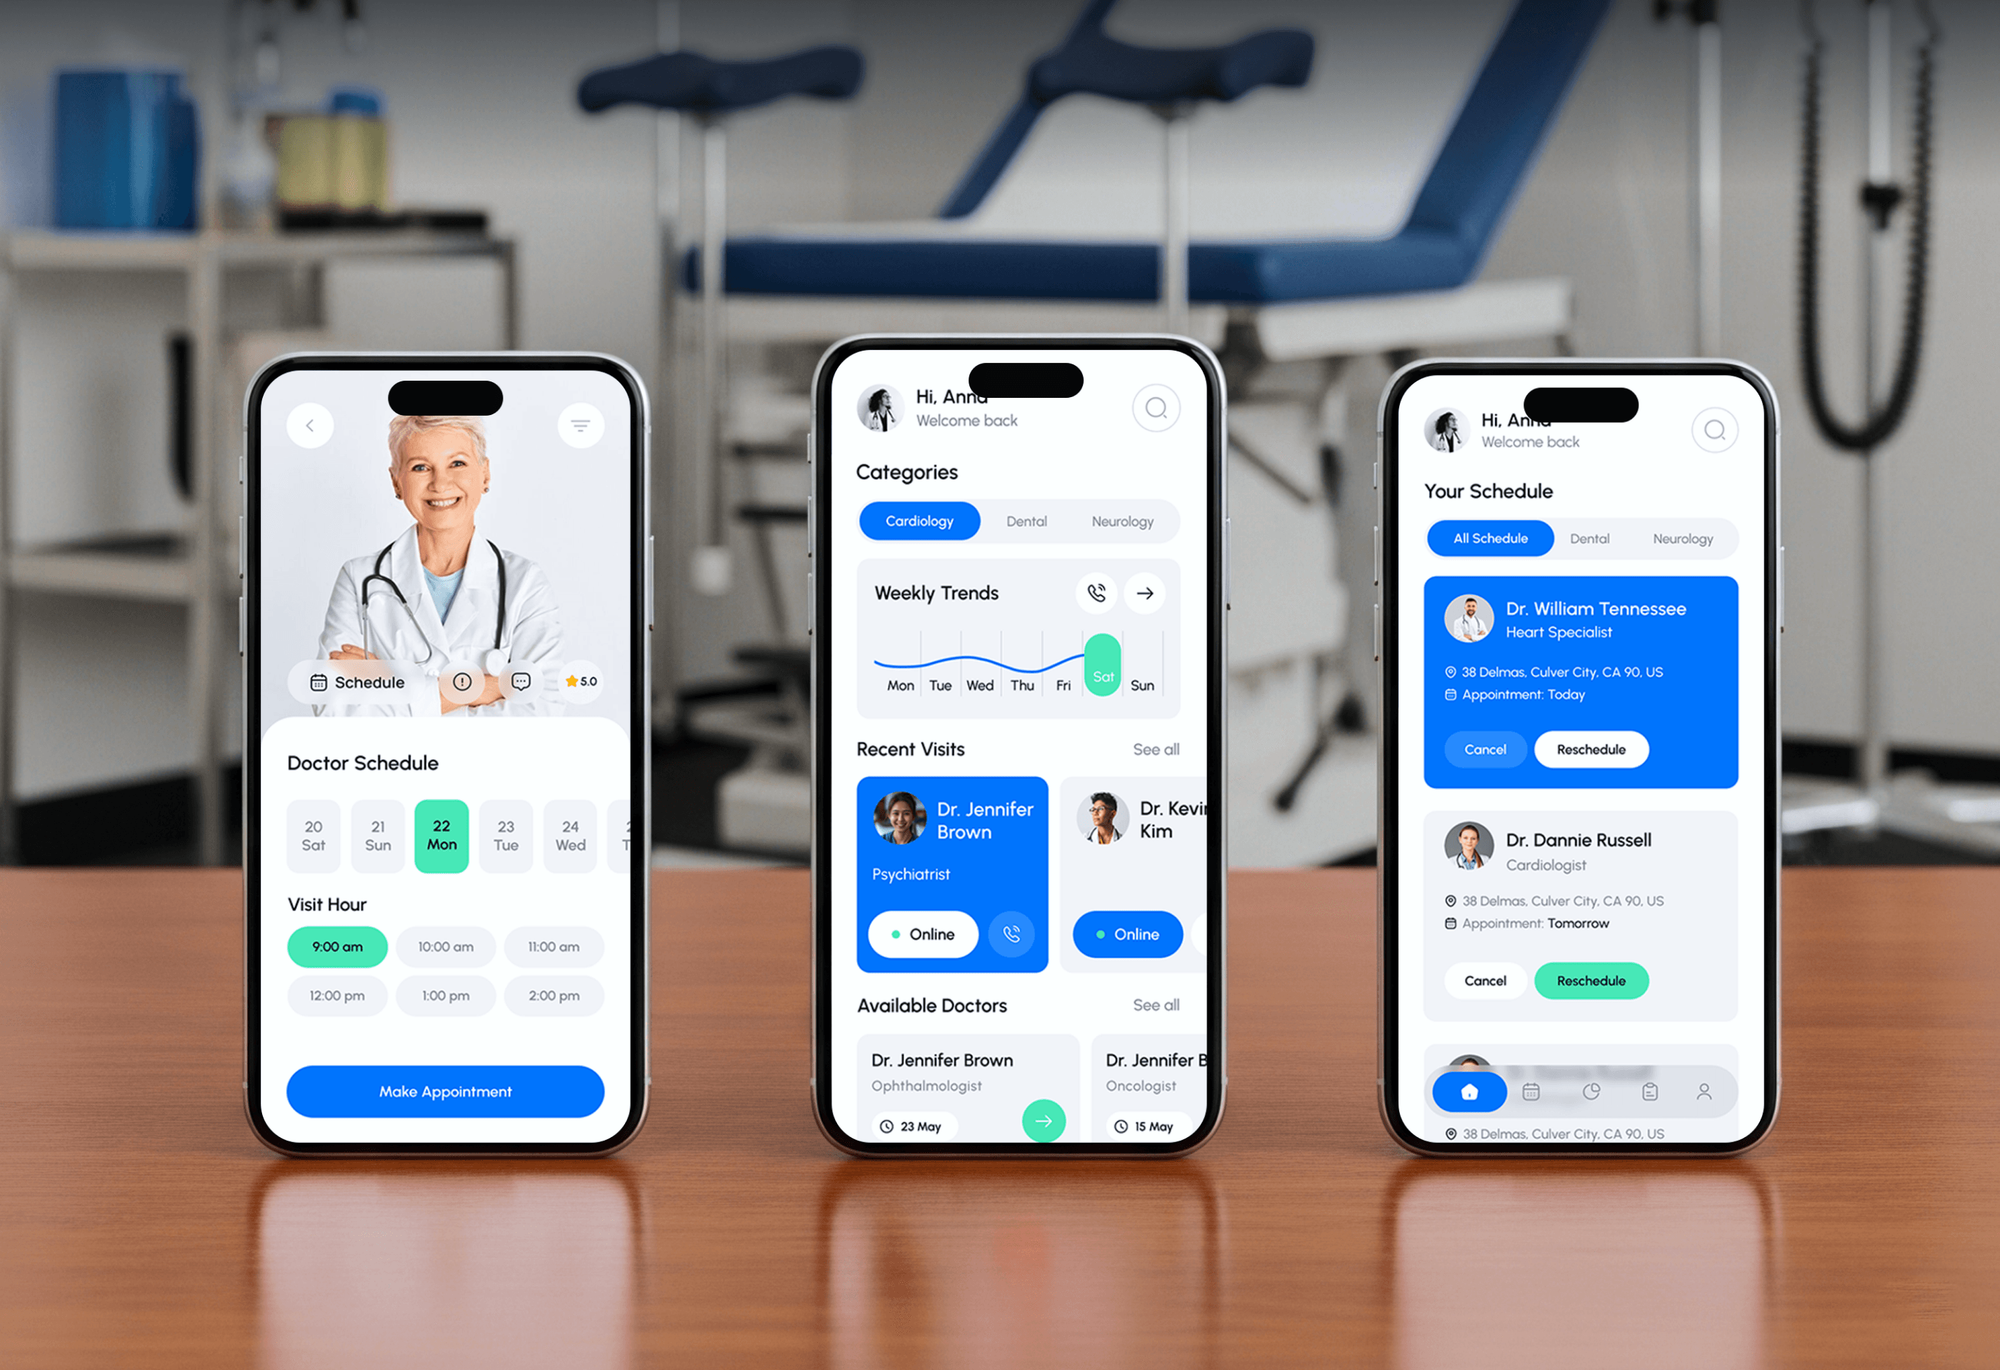
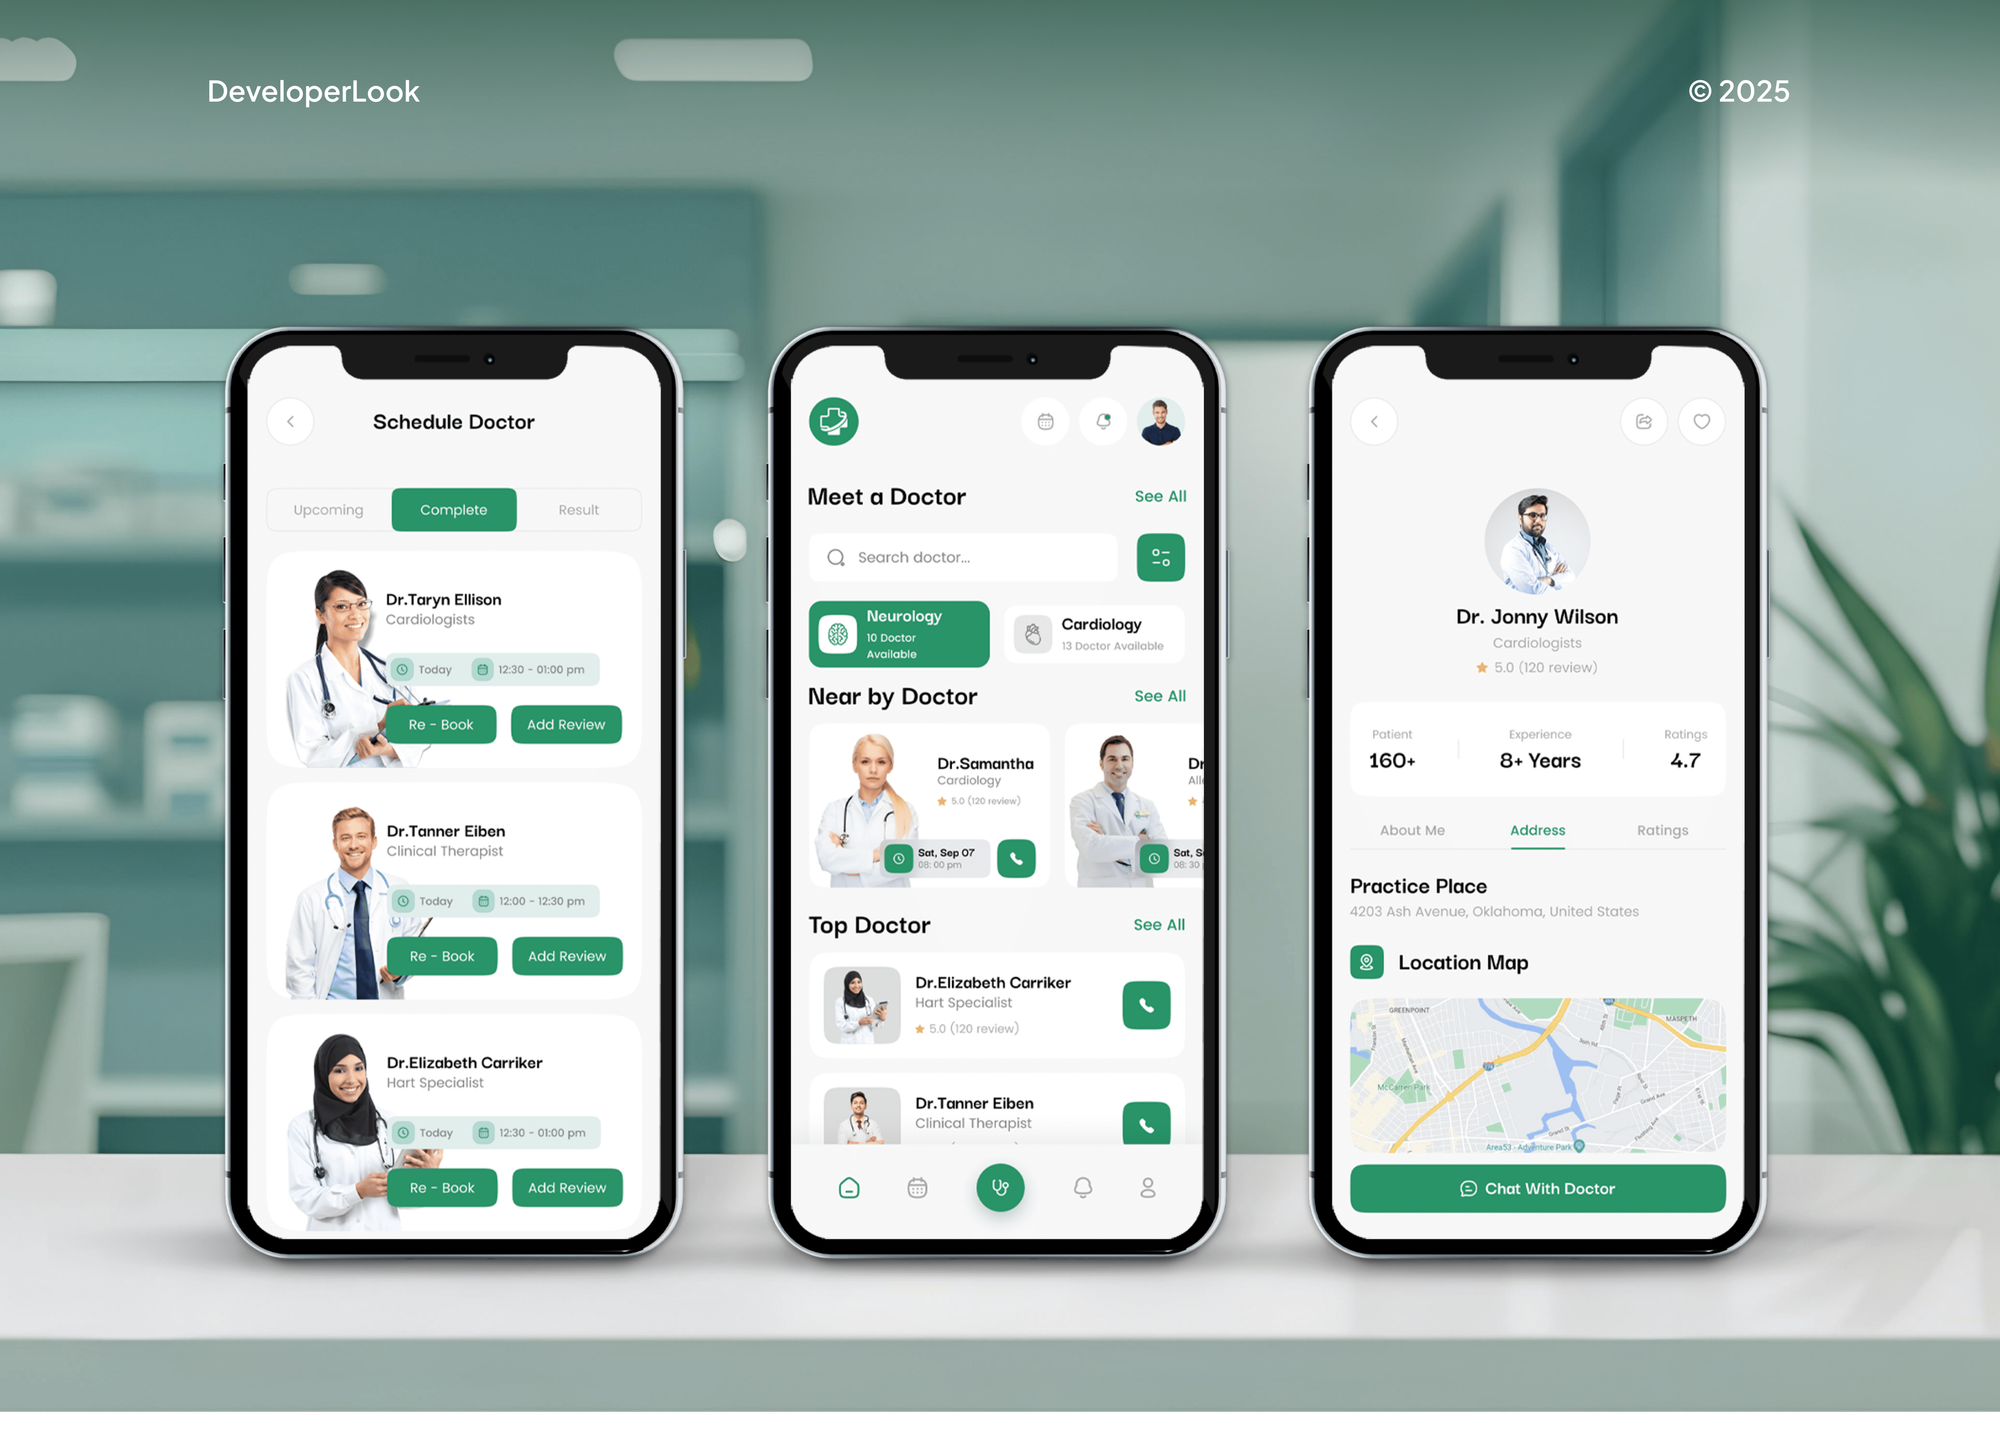
Medical apps, doctor booking platforms, and care websites we designed and built. They hold the same patient data a healthcare security program has to protect.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Healthcare cybersecurity services touch systems clinicians need every minute. These habits keep care running while the work happens, and keep patient data where it belongs.
We schedule MFA rollouts, restores, and network changes outside clinic hours and on-call peaks. A security change shouldn't slow a patient check-in.
Our work uses configuration, logs, and access lists, not patient records. When a test needs real data, your staff run it while we observe.
Downtime procedures are written with the nurses and front desk staff who would use them. Plans that only IT understands fail on the first paper day.
Security Rule duties belong to you as the covered entity or business associate. We set up controls and evidence, and your privacy officer or counsel decides compliance questions.
Leadership gets a single page for each site: the gaps, the patient impact, and the decision needed. Every acronym on it gets a plain explanation.
You get one fixed price for the sites and systems in scope. Adding a clinic later gets its own quote before any work starts.
Overview
DeveloperLook provides healthcare cybersecurity services for clinic groups, care networks, and health tech vendors. We score every site against HHS's 10 essential and 10 enhanced performance goals, close the essential gaps, time a real restore, and write EHR downtime procedures. Projects start at $1,000 and take 2 to 10 weeks, at a fixed price.
DEVELOPERLOOK
Project facts · Healthcare Cybersecurity Services
Reviewed 26 Oct 2026 by Saimul Islam
Good fit
Multi-site clinic groups
Your group added 3 clinics in 2 years, each with its own IT habits, and you need one security standard that every site meets.
Health tech vendors selling to providers
Your hospital customers send security questionnaires and BAAs, and you need cybersecurity for healthcare providers' demands answered with real controls.
Surgery, imaging, and specialty centers
Your center can't stop for an outage, and you need downtime procedures that still work when the EHR or PACS is unreachable.
Home health and behavioral health agencies
Your clinicians work from cars and homes on tablets, and you need healthcare cybersecurity solutions that protect patient data outside the clinic.
Healthcare IT teams stretched thin
Your 2-person IT team runs everything, and you want healthcare cybersecurity consulting that ranks the next 90 days instead of a report nobody reads.
Not a fit
One practice, daily safeguards
You run a single medical practice and need its daily safeguards set up room by room. Our cybersecurity for medical practices page covers that work.
Need risk analysis and BAAs
You need the documented HIPAA risk analysis, policies, and business associate agreements. Our HIPAA compliance services page covers that paperwork.
Hospital with a security team
You're a hospital with your own security operations staff and need hands-on medical device testing. A firm that tests devices on your network is the better first call.
Budget under $1,000
You want a first look before spending $1,000. HHS's free 405(d) resources and the published performance goals are a good place to start.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your sites, your clinical systems, and how far the fixes go, and you get a fixed proposal after a free site review call.
For Agencies
You own the clinic or health tech relationship. We supply the HHS goal scoring, essential fixes, and downtime procedures in your name while the client keeps calling you. Each client gets healthcare-specific security work, and you skip a new hire.
White label: your client only ever sees your brand
Share each client's sites, EHR and PACS systems, and hosting vendors.
You get a written scope and one fixed price per organization.
We deliver the scorecards, fixes, and downtime plans for you to present.
Share each client's sites, EHR and PACS systems, and hosting vendors.
You get a written scope and one fixed price per organization.
We deliver the scorecards, fixes, and downtime plans for you to present.
The Right Technology for Your Project
These are the frameworks HHS points healthcare to, plus the identity, backup, and clinical systems where the essential goals are put in place.
 AWS
 Microsoft Azure
Related Services
Healthcare teams that finish this work often add HIPAA paperwork, practice-level safeguards, vendor reviews, or network fixes. These pages cover those next steps.
This page
Healthcare Cybersecurity Services
Pairs with the 6 services around it
FAQ
Straight answers on what healthcare cybersecurity is, why it matters, why attackers target it, cost, and how to put it in place.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Healthcare cybersecurity is the protection of the systems, data, and devices that patient care depends on, from EHRs and imaging to billing and patient portals. It covers availability as well as privacy, because a locked EHR delays care as surely as a leaked record harms a patient. HHS's HPH Cybersecurity Performance Goals give the sector a shared starting list.
Because an outage in healthcare stops care, not just work. When ransomware locks an EHR, clinics divert patients, delay procedures, and fall back to paper. Patient records also carry insurance and identity details that criminals sell. Good cybersecurity in healthcare keeps that data private and keeps clinical systems available when staff need them.
Because compliance covers paperwork, while attackers test your actual systems. HIPAA sets the duty to protect patient data, but hospital partners, cyber insurers, and patients judge you on whether care keeps running. HHS published its voluntary performance goals for that reason: they focus on the controls that stop common attacks, such as MFA and email security.
Healthcare combines valuable data with a low tolerance for downtime, so attackers expect victims to pay quickly. Many organizations also run older systems and medical devices that are hard to patch. Add the vendors with remote access to clinical systems, and an attacker has several ways in and a strong reason to expect a ransom.
The main benefits are fewer outages, faster recovery, and easier partner and insurer reviews. Timed restores and written downtime procedures turn a crisis into a planned paper day. A scored set of HHS goals also shows hospital partners and cyber insurers where you stand, which shortens questionnaires and can make renewals smoother.
Our healthcare cybersecurity services start at $1,000 for scoring up to 2 sites against all 20 HHS goals, with one timed restore. Putting the essential goals and downtime procedures in place for up to 5 sites costs $2,700. Networks of up to 10 sites that add the enhanced goals, segmentation, and logging start at $5,400.
Start by scoring every site against the HHS essential goals, then fix gaps in order of patient impact. MFA, email security, and leaver removal usually come first, followed by restore testing and downtime procedures. Enhanced goals such as segmentation and central logging come next. Scoring takes 2 to 3 weeks, and a full program takes 6 to 10 weeks.
Focus on the few controls that stop most attacks, and skip tools nobody will run. Turn on MFA everywhere, patch the flaws on CISA's Known Exploited Vulnerabilities list first, separate admin accounts, and remove leavers the same day. Then test one restore and write downtime steps. A 2-person IT team can keep that running week to week.
You mitigate them before they start and contain them fast when they do. Before: segment clinical networks, keep an offline or immutable backup copy, and rehearse downtime. During: disconnect affected devices but leave them powered on for evidence, switch sites to paper, call your cyber insurer's hotline, and reset credentials from clean devices.
They fall into three groups: EHR and device makers with built-in security features, managed providers that monitor healthcare networks, and advisory firms that build programs. Healthcare cybersecurity companies worth shortlisting know clinical workflows, downtime planning, and the HHS goals. We're an advisory and implementation firm, working alongside your EHR vendor and IT provider, with 30 days of support after handover.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.