
Assessment type decision
A written choice between e1, i1, and r2, tied to the customer contracts that require HITRUST.

For health tech and healthcare vendors whose customers ask for HITRUST: the right assessment chosen, cloud controls inherited, and evidence ready for your assessor.
100%
Inheritable controls claimed
1of 3
Assessment types matched to buyers
How your project runs
Teams we have built for:














The Problem
It shows up when a health system's security review asks for HITRUST, a payer contract names it, or a rival wins a deal with a certification you lack.
01 · Level
Nobody knows whether customers need an e1, i1, or r2.
We read your customer contracts and match the assessment to what they require.
02 · Cloud
Controls your cloud provider already covers get tested twice.
We claim inherited controls through HITRUST's inheritance program before scoping is final.
03 · Policies
HIPAA policies weren't mapped to the HITRUST CSF.
Each requirement gets a policy, a procedure, and implementation evidence mapped to it.
04 · Timing
Fieldwork gets booked before the evidence exists.
You book the assessor once our readiness review shows the evidence holds.
Your largest hospital prospect added HITRUST to its vendor requirements, and your sales team promised it by next quarter. Nobody knows whether you need an e1, an i1, or an r2. Your platform runs on AWS, but no one has checked which controls you can inherit. Policies exist for HIPAA, yet nobody has mapped them to the HITRUST CSF. An assessor quote just arrived, and you don't want to pay for fieldwork before the evidence is ready.
We start by matching the assessment type to what your customers actually require, then define scope around the systems that hold their data. We claim inherited controls from your cloud provider, fix the gaps that remain, and organize evidence in MyCSF the way assessors test it. You book fieldwork when the evidence is ready, not when the sales deadline says so.
Right assessment chosen first
An e1, i1, or r2 matched to the contracts and buyers that actually ask for HITRUST.
Cloud controls inherited
Controls your AWS, Azure, or Google Cloud provider already covers are claimed instead of retested.
Evidence in MyCSF order
Policies, procedures, and proof organized the way External Assessors test each requirement.
Our HITRUST Certification Support Process
You approve the assessment type and scope, see every gap with its owner, and review the evidence package before your External Assessor sees any of it.
We read what your customers ask for, the systems that hold their data, and your target date. You get a written scope and a fixed price. If a SOC 2 report or HIPAA risk analysis will satisfy your buyers, we'll tell you before we quote.
What's Included
Each engagement covers the assessment choice, scope and inheritance, a requirements map, technical fixes, the MyCSF evidence package, and the mock validation your plan includes.
Compare Options
Your in-house lead knows your systems best, and only an authorized External Assessor can perform the validated assessment. Here is where each option fits your path to certification.
| Feature | DeveloperLookBest fit | Assessor firm | In-house lead |
|---|---|---|---|
| Assessment choice | Matched to your customer contracts | Advised before the engagement | Often guessed from a questionnaire |
| Cloud inheritance | Planned before scoping is final | Reviewed during validation | Often missed |
| Technical fixes | Engineers fix cloud and code gaps | Cannot fix what it assesses | Yes, between other duties |
| Evidence | Organized for each requirement | Tested, not prepared | Gathered as requests arrive |
| Validated assessment | Prepared for your assessor | Yes, performs the validation | Not possible |
| Speed to start | Within a week of scoping | Depends on assessor capacity | Already on staff |
| Support | 90 days after handover | During the engagement | Ongoing, alongside other work |
| Cost | Fixed price from $1,250 | Separate assessment fee | Salary plus training |
Projects We've Built
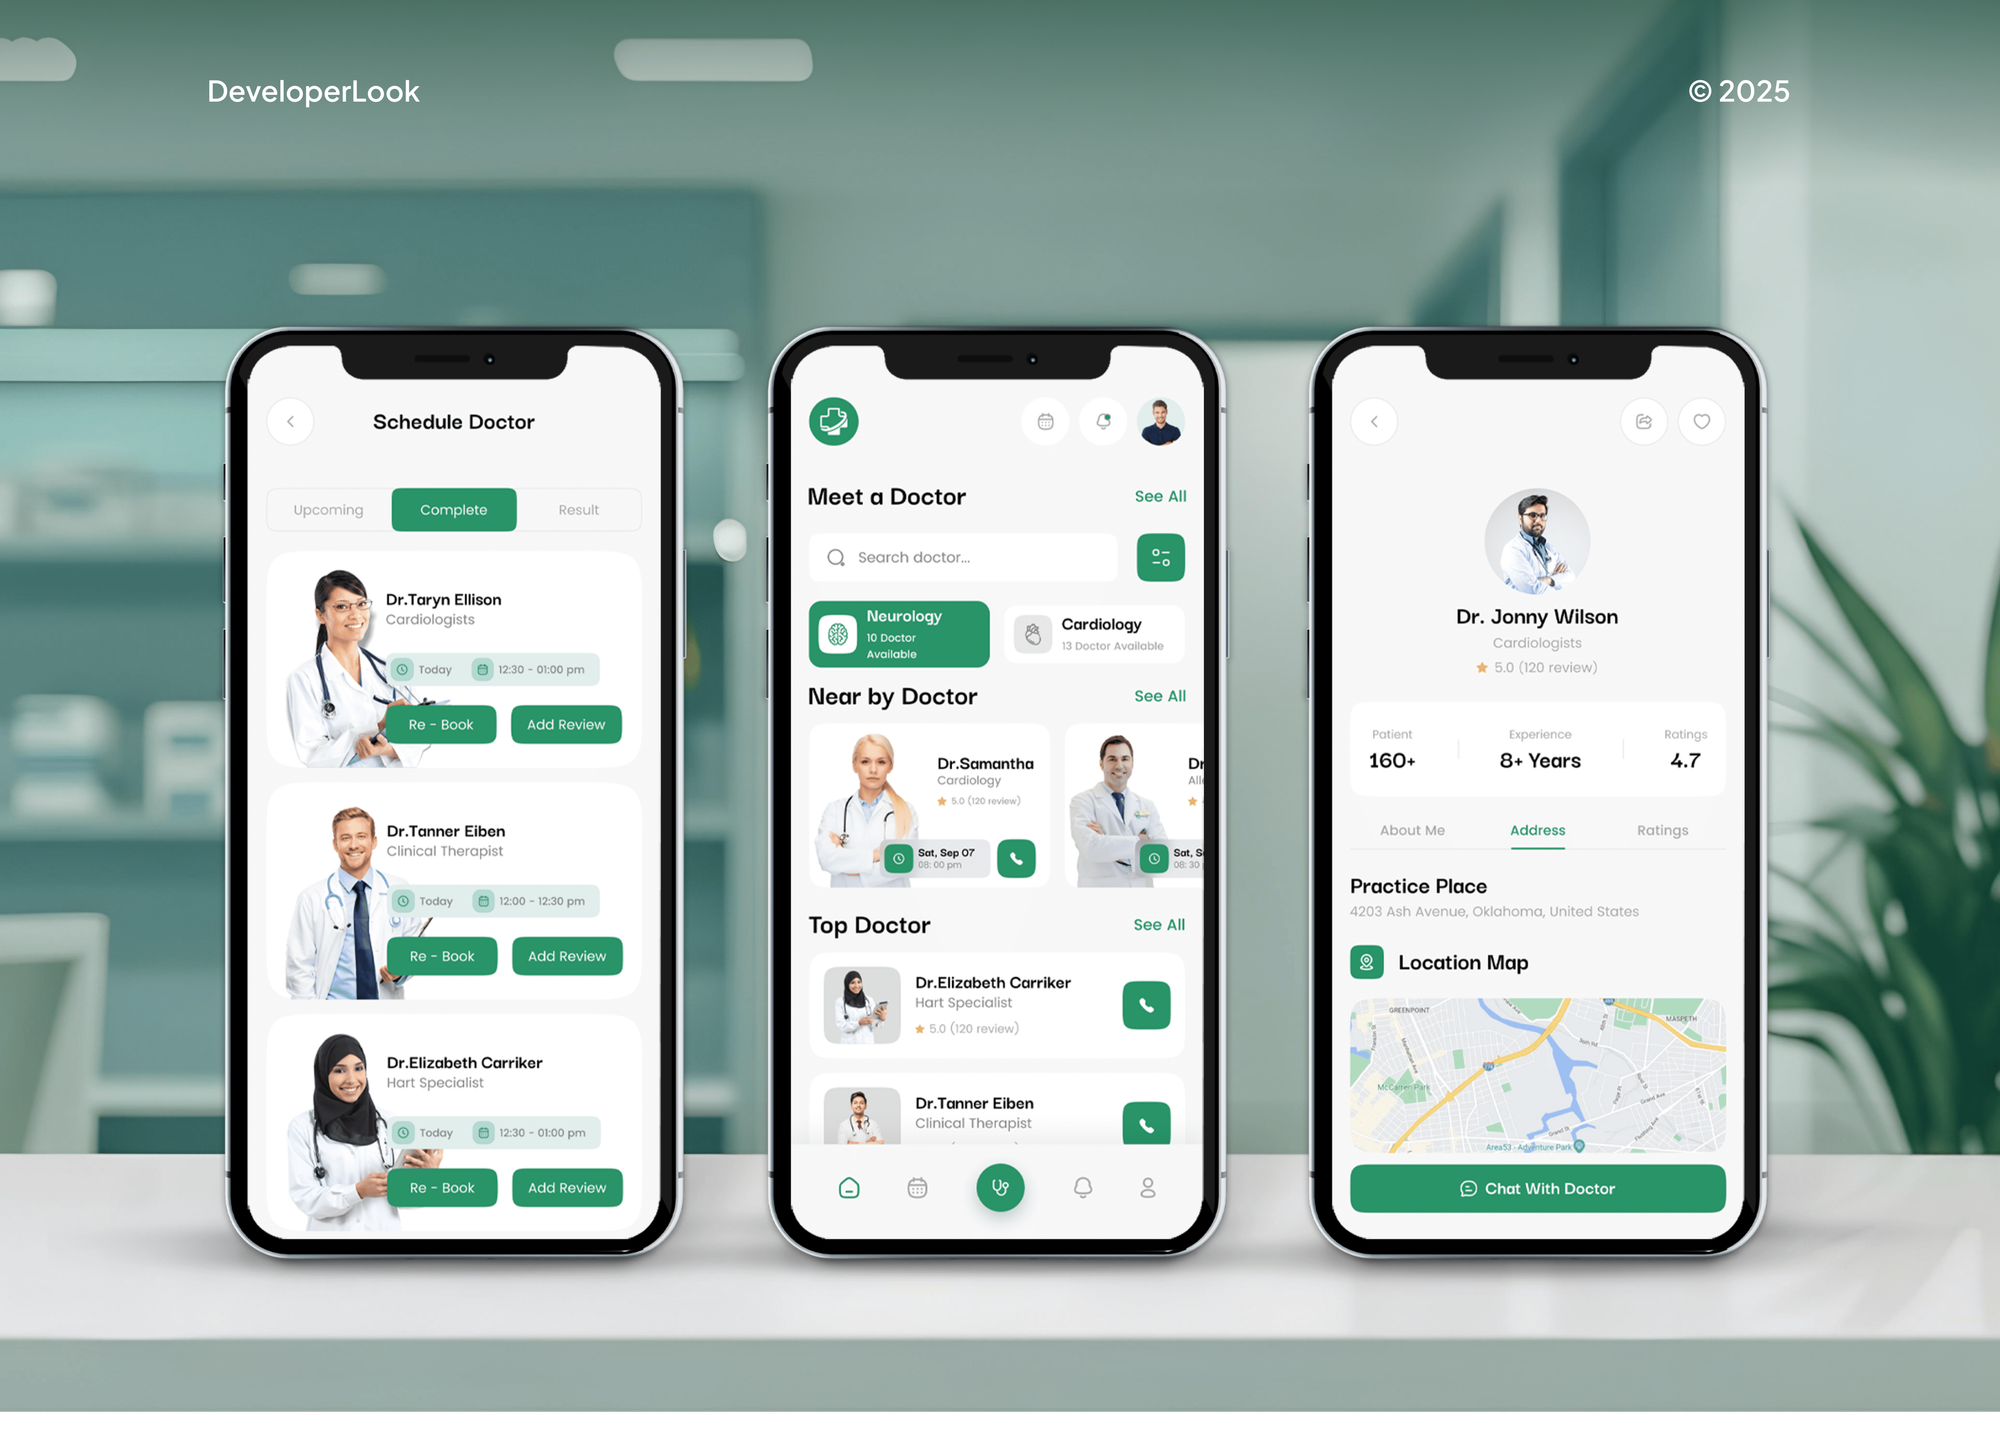
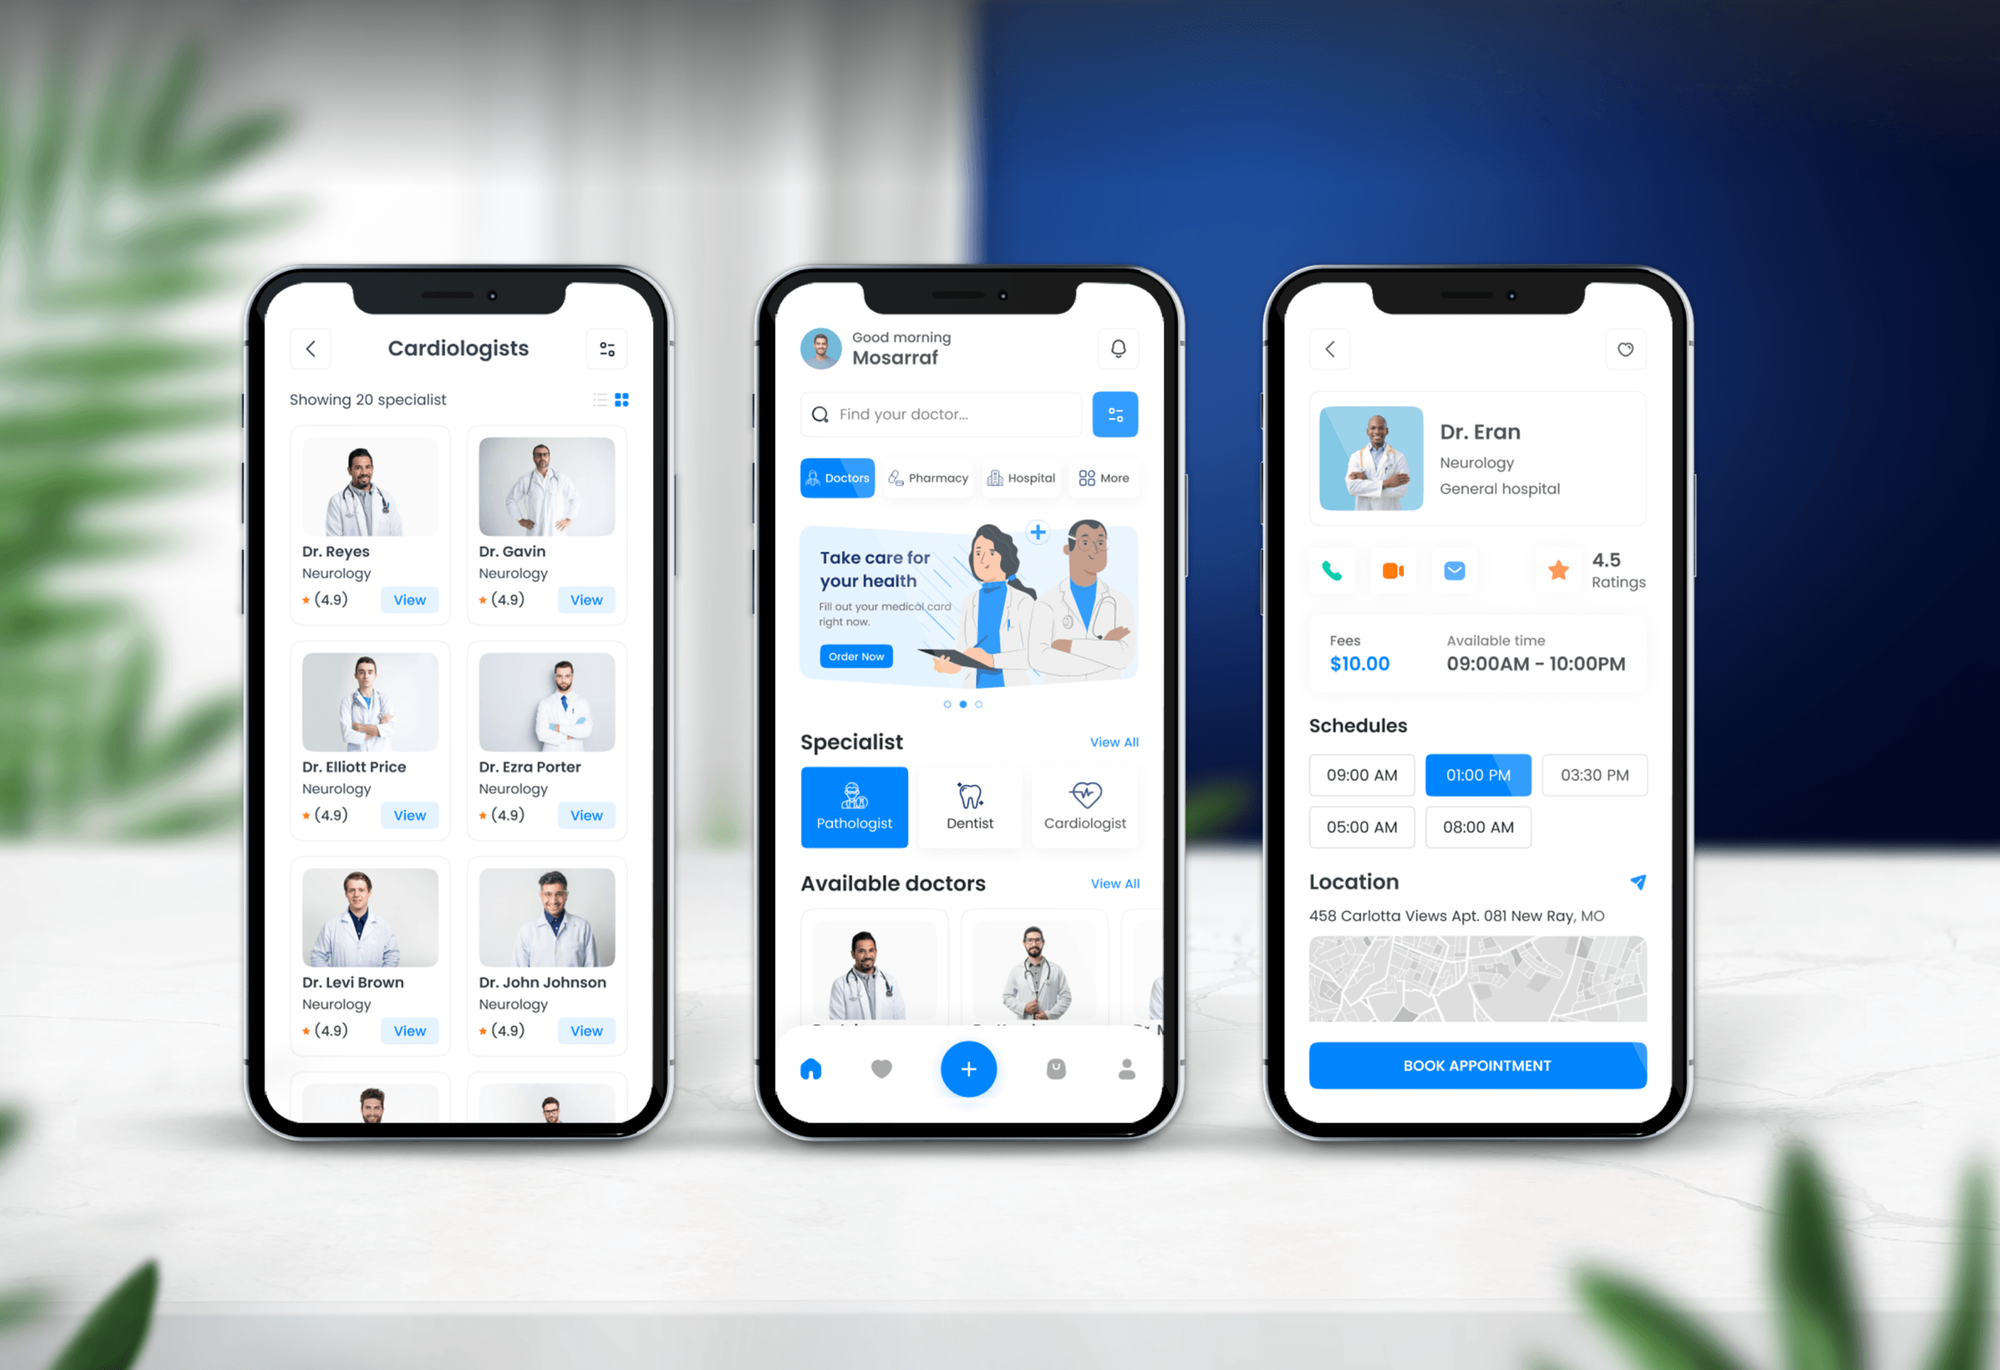
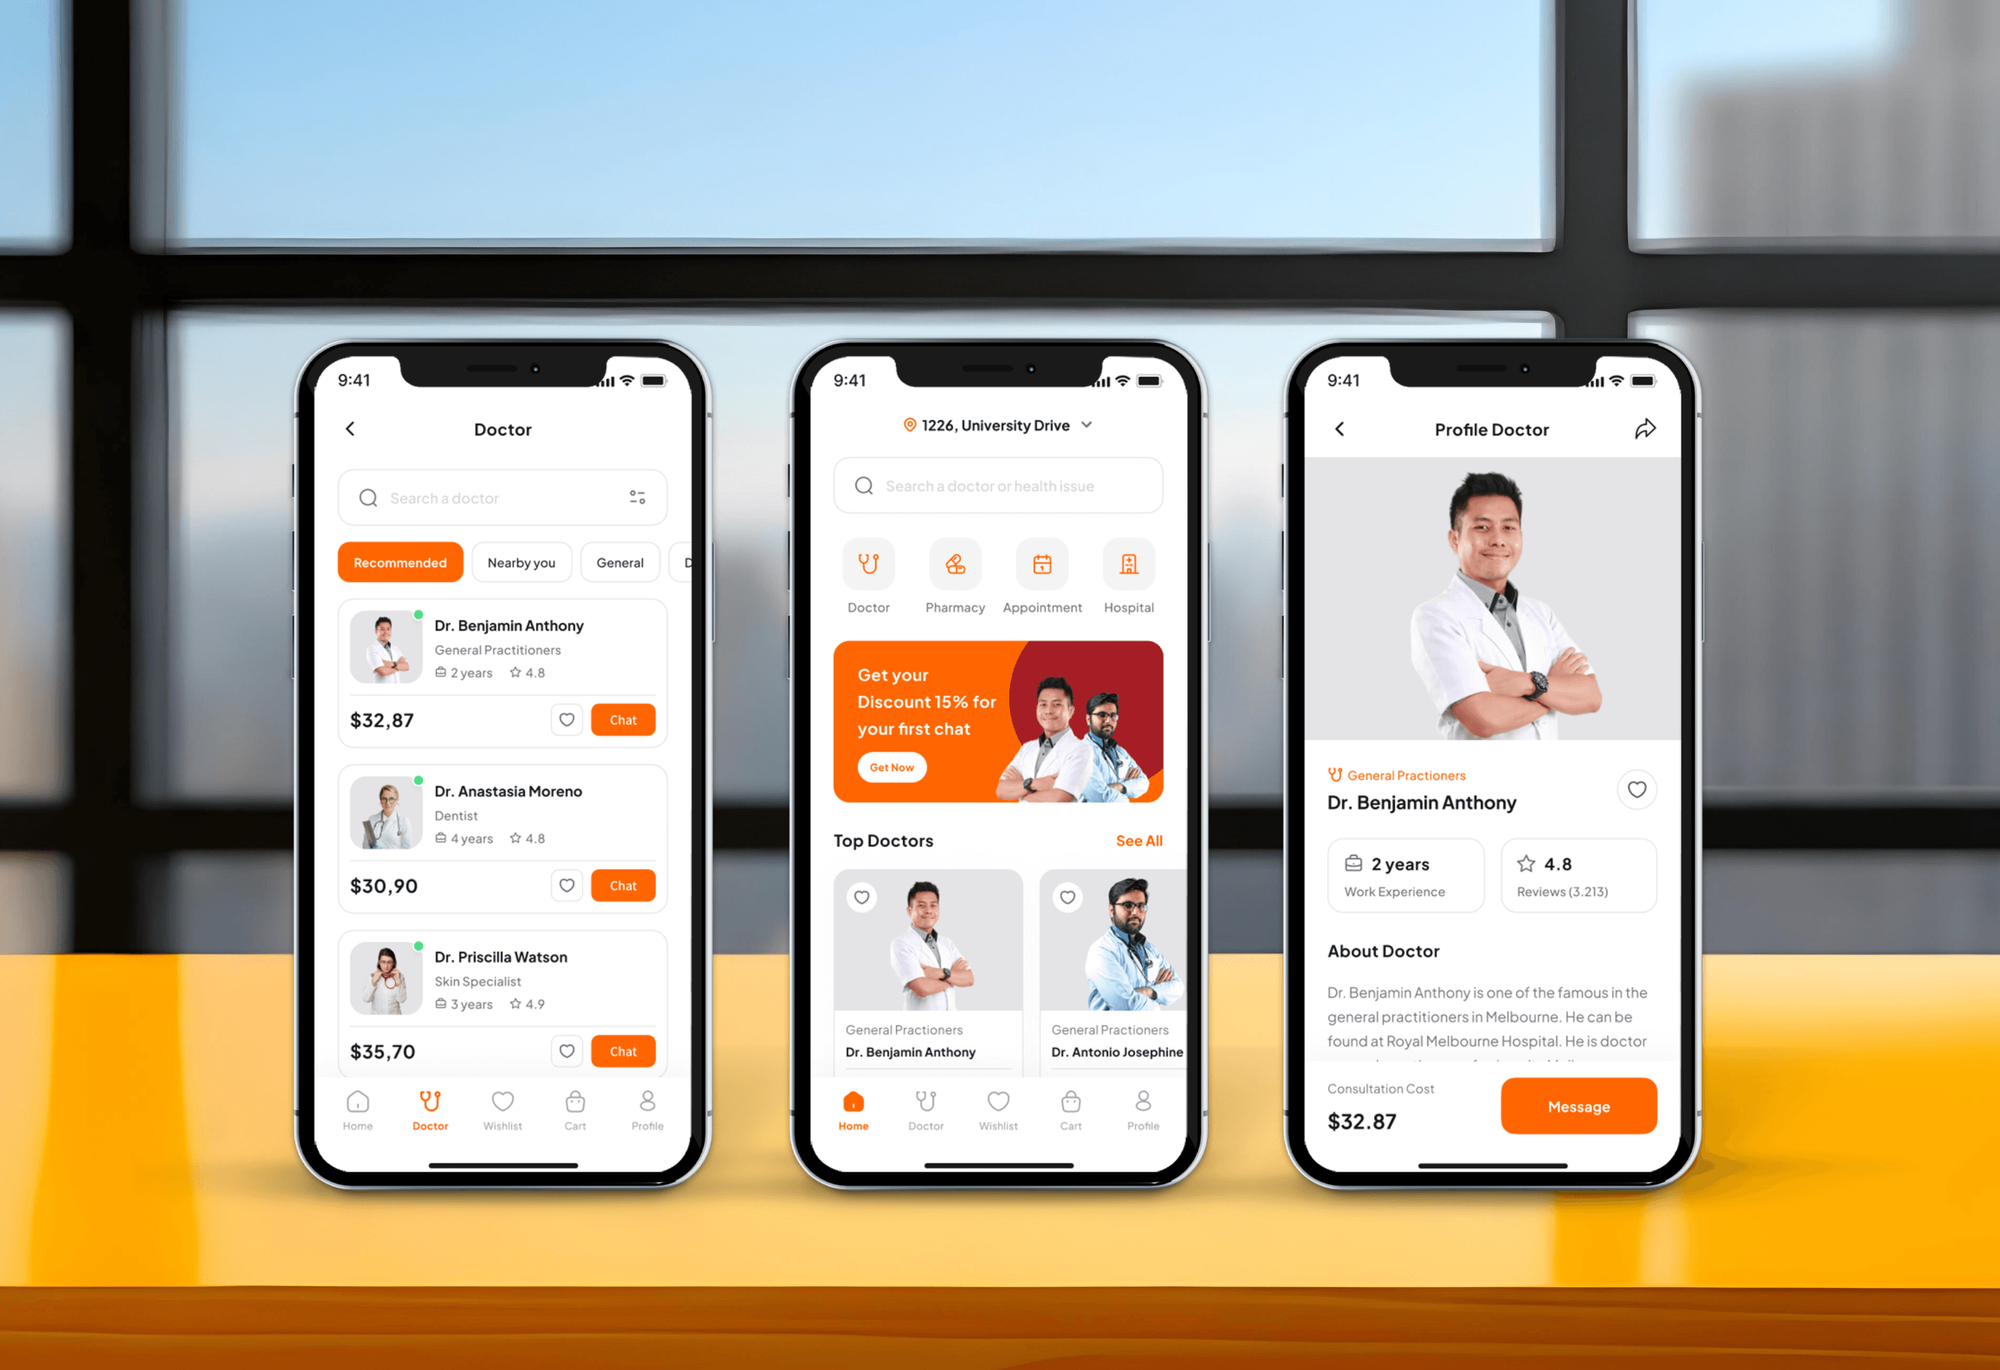
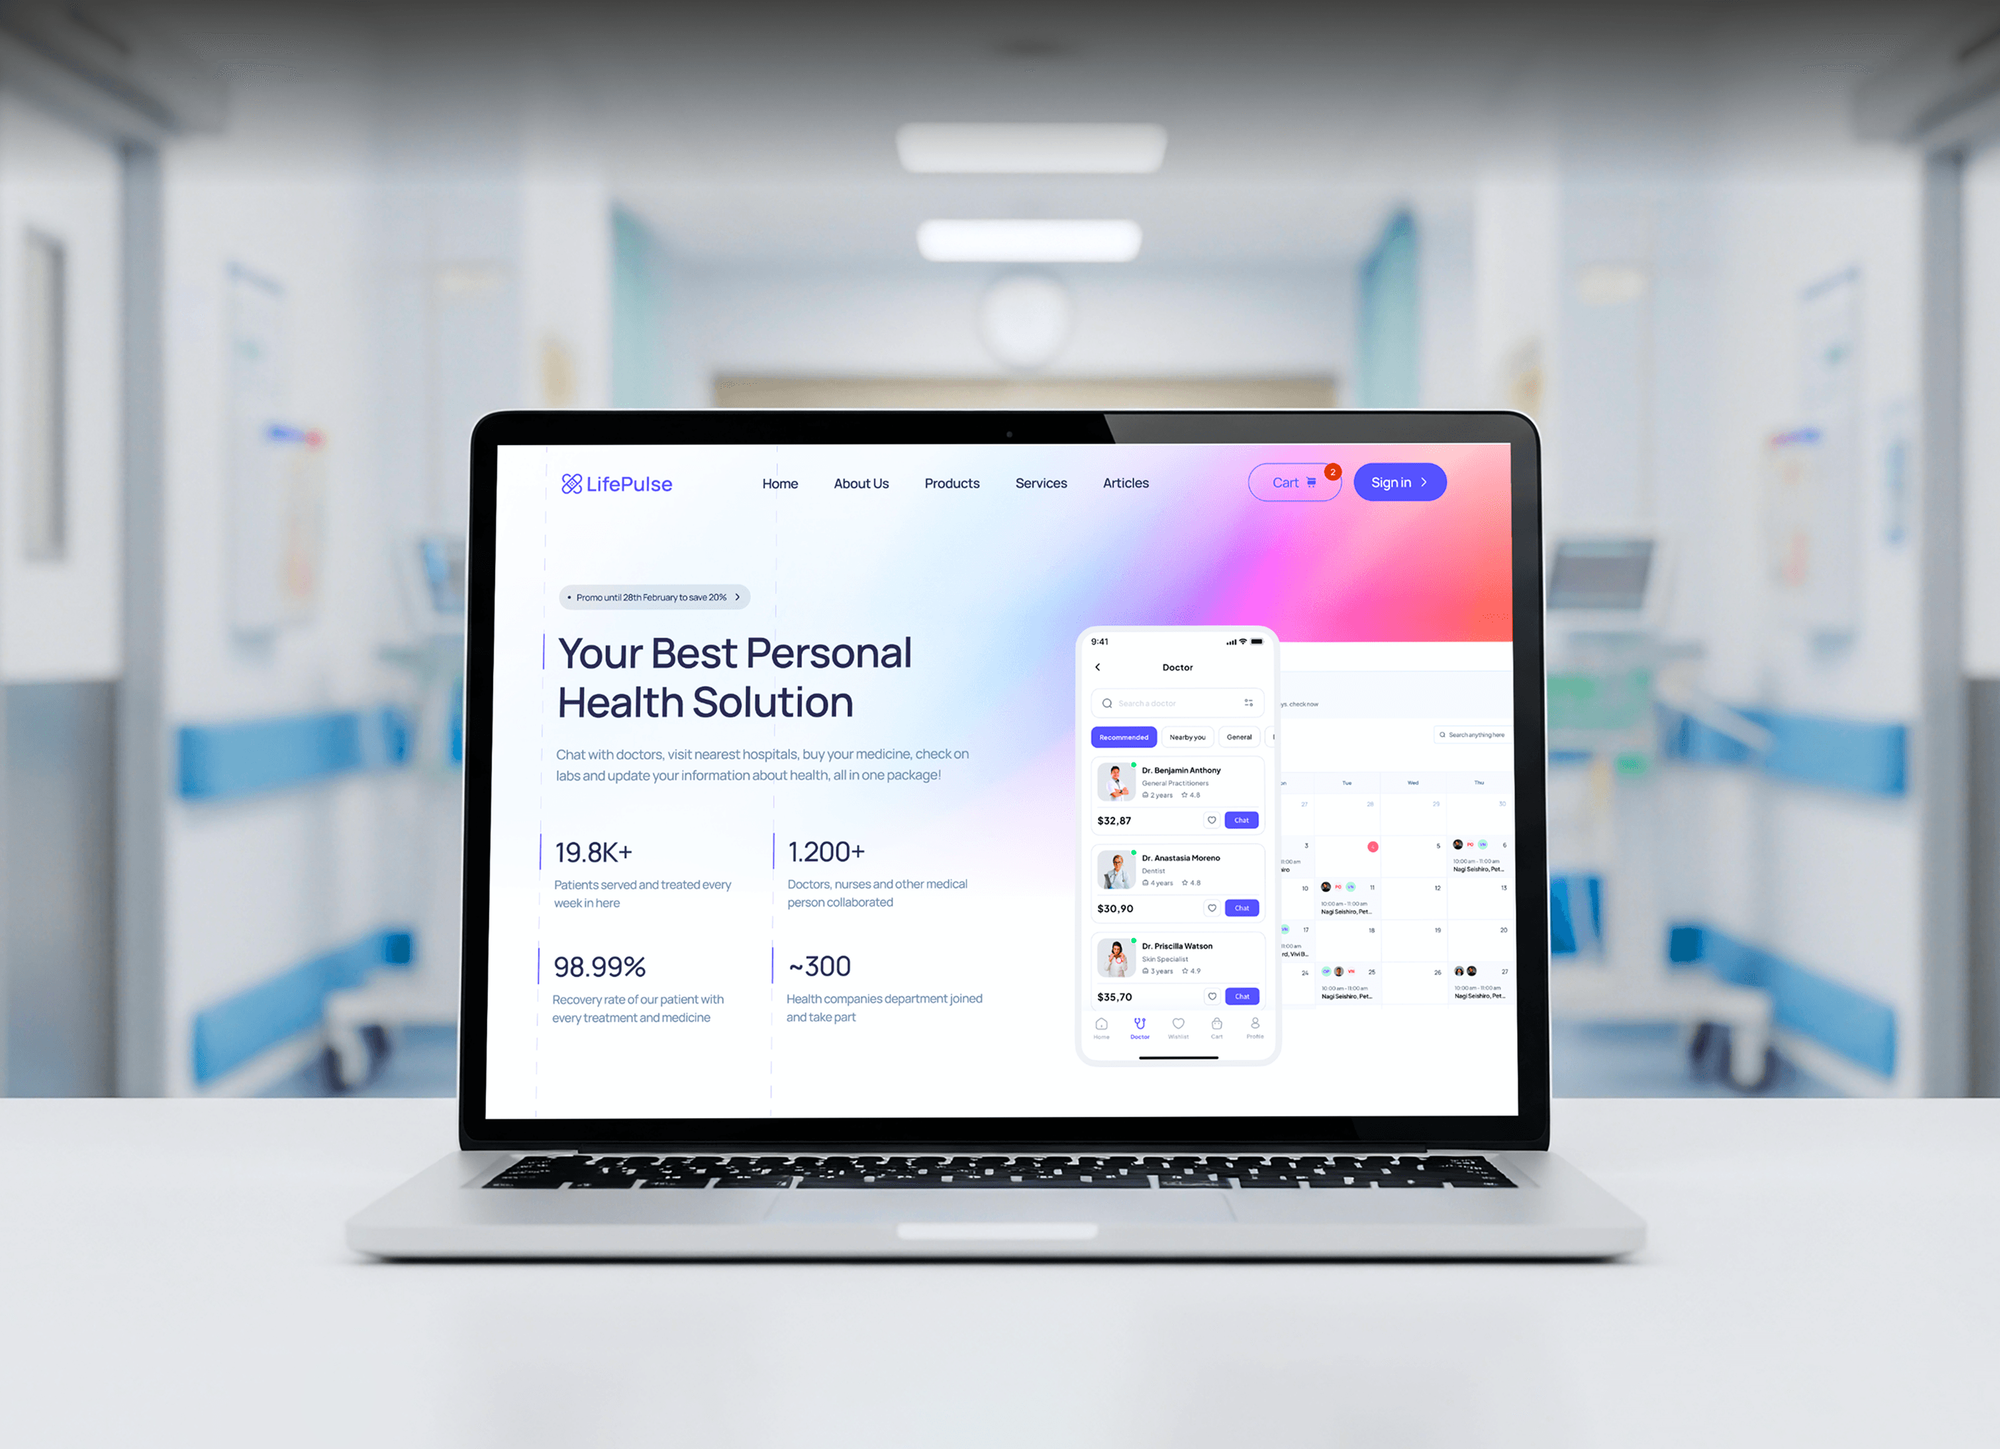
Medical apps, doctor booking tools, and healthcare platforms we designed and built. Products like these hold the patient data HITRUST assessors test.
What Our Clients Say
Feedback from teams we have built healthcare platforms, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
HITRUST readiness touches patient data and big customer deals. These habits keep the evidence honest and the assessment scoped to what your buyers really need.
We're not a HITRUST External Assessor, so we don't validate or score your controls. Our job ends where the assessor's begins: evidence ready, questions answered, fieldwork supported.
If an e1 satisfies your buyers, we won't sell you r2 readiness. The right level saves months of work and a larger assessor fee.
Controls your cloud provider already covers shouldn't be built or tested twice. We check inheritance before any gap gets an owner.
Every screenshot, export, and policy gets a date, a source, and a requirement number. Assessors sample faster when evidence is labeled the way they test.
Most readiness work needs settings and documents, not patient records. When protected data must be seen, we view it on your systems and keep no copies.
The MyCSF account, policies, and evidence stay in your name and systems. We hand back every login at the end, along with a record of what we changed.
Overview
DeveloperLook provides HITRUST certification support for health tech and healthcare vendors. We match an e1, i1, or r2 to what your customers ask for, claim inherited cloud controls, fix gaps, and organize evidence in MyCSF. Projects start at $1,250 and take 2 to 20 weeks, and we never act as your External Assessor.
DEVELOPERLOOK
Project facts · HITRUST Certification Support
Reviewed 23 Oct 2026 by Saimul Islam
Good fit
Health tech SaaS vendors
Your hospital customer added HITRUST to its vendor requirements, and you need to know whether an e1, i1, or r2 will satisfy the contract.
Revenue cycle and billing companies
Your payer and provider clients want every vendor HITRUST CSF certified, and your claims platform has not been through a formal assessment yet.
Digital health startups after HIPAA
Your HIPAA risk analysis is done, and now a health system wants HITRUST certifications from every vendor that touches its patient data.
Companies due for an r2 interim
Your r2 is due for its interim assessment, and the person who ran the first one has left the company with the evidence map.
MSPs serving healthcare clients
Your healthcare clients need HITRUST readiness work, and you want engineers who deliver it quietly under your brand.
Not a fit
Need the assessment itself
You need the validated assessment performed. Only an authorized HITRUST External Assessor can do that, so we prepare you and support your team during fieldwork.
HIPAA is all buyers ask
Your buyers only ask for HIPAA safeguards and a risk analysis. Our HIPAA compliance services page covers that at a lower cost.
Buyers want SOC 2
Your buyers outside healthcare want a SOC 2 report. Our SOC 2 compliance services page covers that readiness work.
Budget under $1,250
Your budget is under $1,250 and no customer requires HITRUST yet. A HIPAA risk analysis is usually the better first step.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the assessment type, your scope, and the gaps to close, and you get a fixed proposal after a free scoping call.
For health tech vendors that need the right assessment chosen and a clear gap list.
$1,250one-time, USD
For vendors preparing for an e1 or i1 assessment with gaps still to close.
$4,200one-time, USD
For companies preparing for an r2 with risk-based scoping and assessor fieldwork.
$8,900one-time, USD
For Agencies
You own the client relationship. We supply the assessment choice, gap fixes, and MyCSF evidence work under your brand. Your healthcare clients get HITRUST readiness without you hiring a dedicated compliance engineer.
White label: your client only ever sees your brand
Send the client's customer requirements, systems, cloud provider, and target date.
You get a written scope, an evidence request list, and a fixed price per client.
We close gaps, organize evidence, and hand it over in your template.
You present the plan while we work behind your brand.
Evidence organized the way your client's assessor will sample it.
Fixes made with patient data and clinical uptime in mind.
One client's e1 or several clients' renewals each year.
The Right Technology for Your Project
We fix gaps in the cloud, identity, and logging tools health tech teams already run, and organize the evidence for HITRUST's MyCSF platform.
 AWS
 Microsoft Azure
 Google Cloud
FAQ
Straight answers on cost, timing, the e1, i1, and r2 levels, who needs HITRUST, and how long it lasts.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our HITRUST certification support starts at $1,250 for choosing the assessment and a readiness review. e1 or i1 readiness with gap fixes moves you to $4,200, and r2 readiness with fieldwork support starts at $8,900. HITRUST's own fees and the External Assessor's fee are separate, so your total HITRUST certification cost depends on the assessment type and scope.
HITRUST certification takes from several weeks to about a year, depending on the assessment type. HITRUST says an e1 can take as few as 4 to 6 weeks and that most companies complete an i1 within 6 to 12 months. Your HITRUST certification timeline also includes assessor testing and HITRUST's quality review after our 2 to 20 weeks of readiness work.
It is a security assurance report that HITRUST issues after an authorized External Assessor tests your controls against the HITRUST CSF. Healthcare organizations use it to judge vendors that handle sensitive data. The CSF maps to frameworks such as HIPAA, NIST, and ISO 27001, so one assessment can answer many security questionnaires.
It works in three stages: you prepare evidence in MyCSF, an External Assessor tests it, and HITRUST reviews and certifies it. Before that, you choose the assessment type and define the scope. HITRUST runs a quality assurance review of the assessor's work, and open gaps can be handled with corrective action plans.
There are three main levels: e1, i1, and r2. In CSF v11.9 the e1 covers 44 foundational requirement statements and the i1 covers 182, while the r2 is tailored through risk-based scoping. Pick the lowest level your customers accept, because each step adds requirements, evidence, and assessor time.
Mostly vendors that handle health data for hospitals, health plans, and other organizations that require it in contracts. Health tech SaaS companies, revenue cycle firms, and data processors hear the request most. If no customer asks for it, a HIPAA risk analysis or a SOC 2 report is often the better first step.
No, it is voluntary, and no law requires it. HIPAA requires safeguards and a risk analysis but no certification, and HHS doesn't recognize private HIPAA certifications. HITRUST becomes required in practice when a customer contract demands it, as some health systems and payers do for their vendors.
To get HITRUST certified, you pick an assessment, define the scope, close the gaps, and hire an authorized External Assessor to validate your controls. You set up the assessment in MyCSF and upload evidence, and the assessor tests and submits it. HITRUST then reviews the work and issues the certification.
An e1 or i1 certification is valid for one year, and an r2 for two years. The r2 also needs an interim assessment around the one-year mark to stay valid. Plan renewal work a few months ahead, so your evidence and fixes are current before the assessor starts fieldwork.
There is no official ranking. Only HITRUST certifies, and the assessments are done by authorized External Assessor firms that HITRUST lists. Choose an assessor with healthcare clients your size and a clear fieldwork schedule. DeveloperLook is not an assessor: we prepare you, so the firm you choose spends its time testing instead of waiting.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.