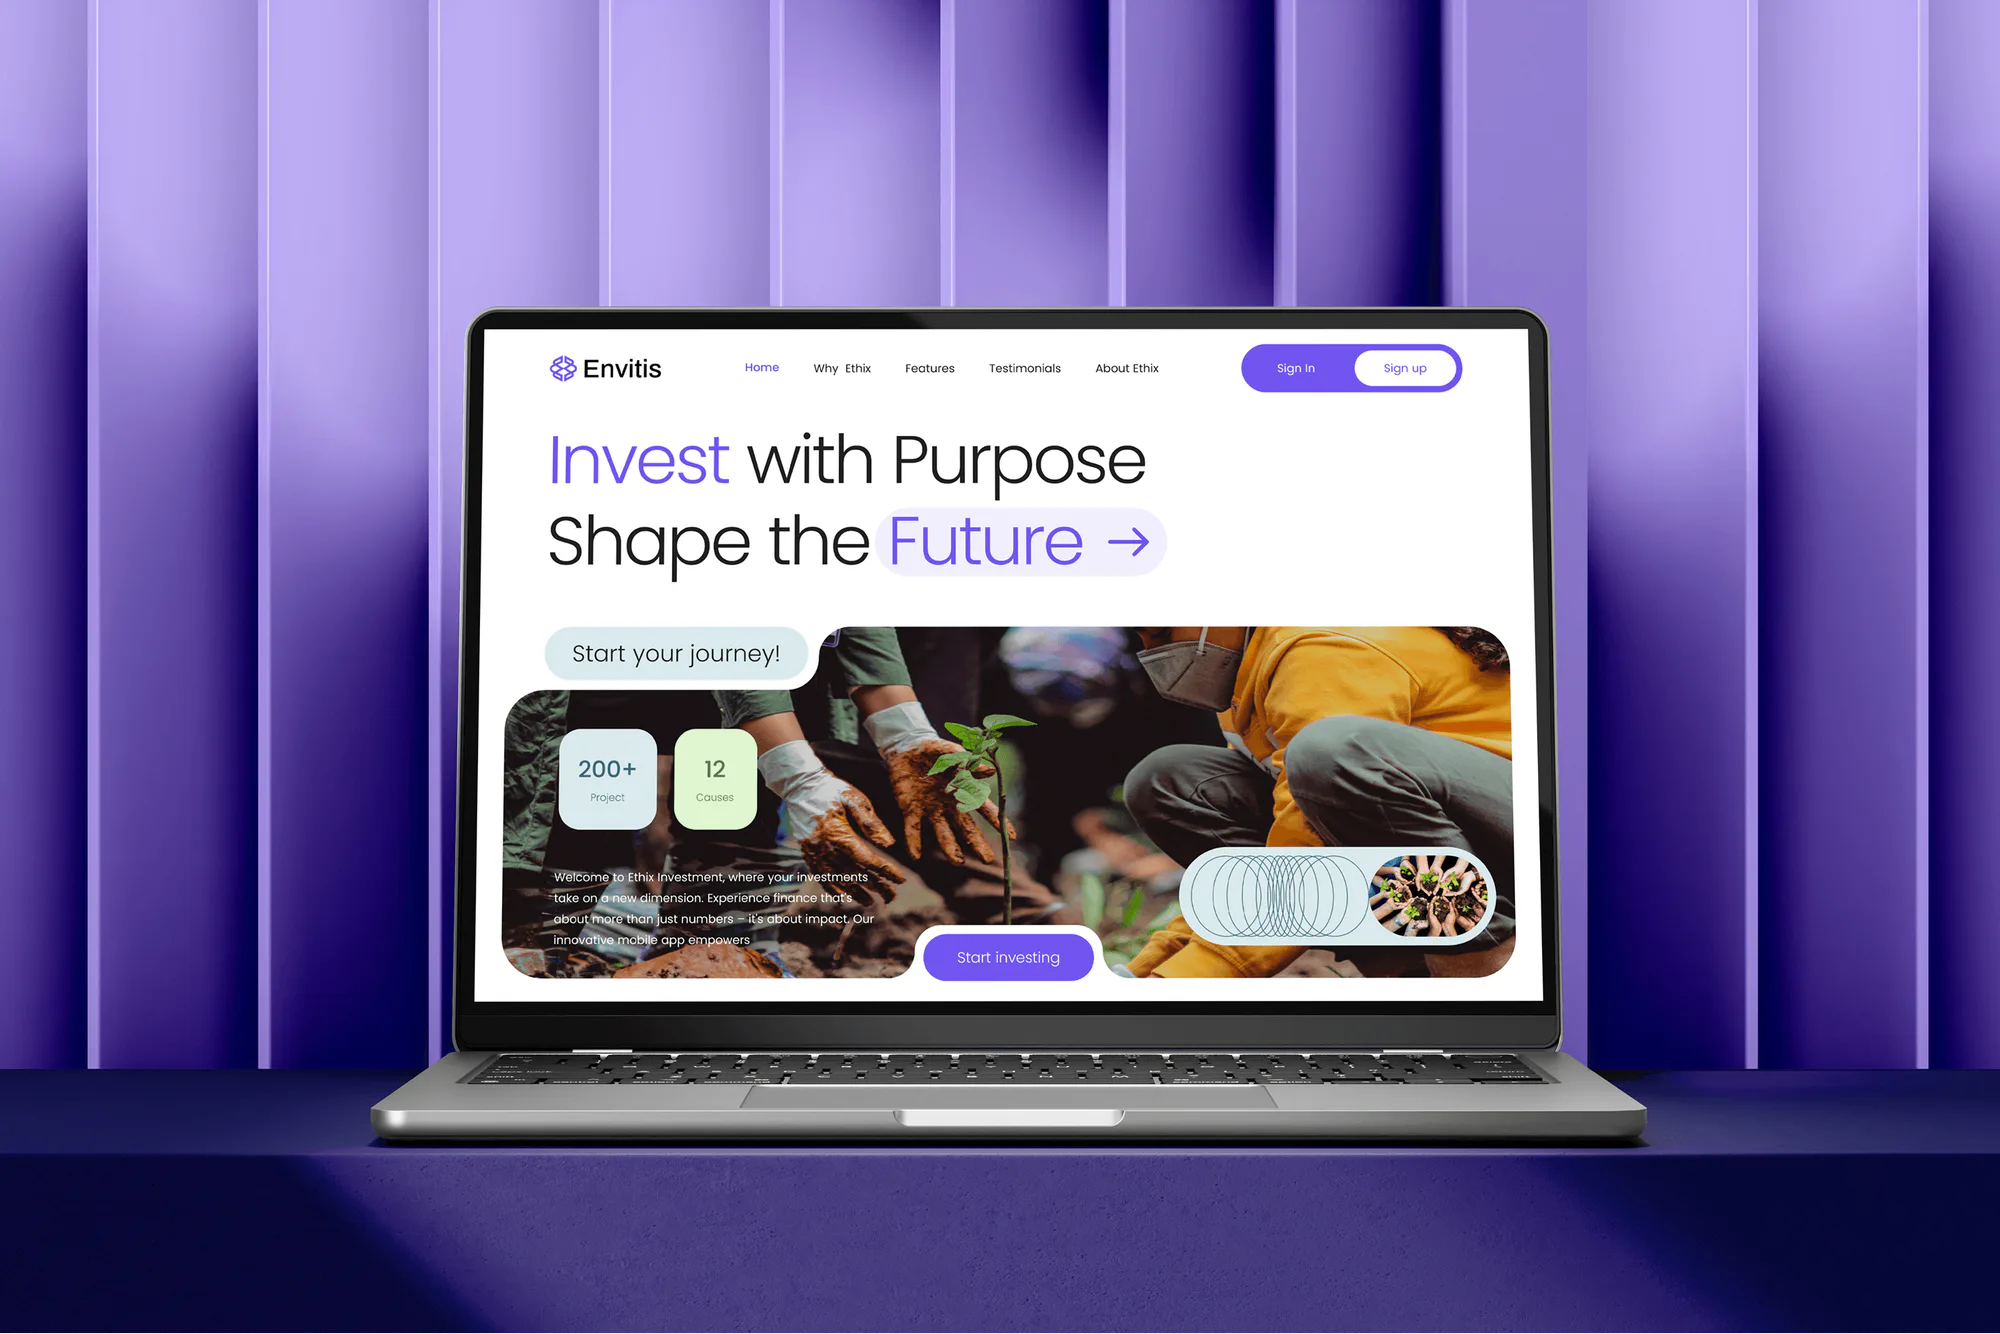
Envitis Investment Website Design & Development
- Finance
- Dashboard
- Website

For private equity firms and corporate buyers who need a target's security risk in plain terms before signing, with every finding tied to a deal action, from $950.
5days
To a pre-LOI red-flag memo
100%
Findings tied to deal actions
How your project runs
01 · FreeIndustry leaders we work with
 Cloudflare
 AWS
 Microsoft Azure
 Google Cloud
 Google Sheets
The Problem
It surfaces when the target answers yes to every question on the security questionnaire, or when a ransomware note arrives in your first month of ownership.
Rosy answers
The questionnaire says yes to every security control.
Rosy answers
Evidence requested for each answer: exports, screenshots, and a short interview.
Exposed edge
A VPN appliance runs firmware with a public advisory.
Exposed edge
An outside-in scan of exposed services and versions before the LOI is signed.
Untested backups
Nobody can say when backups were last restored.
Untested backups
A restore test, or written proof of one, checked against the stated recovery time.
Vague reps
Counsel drafts a cyber rep without technical findings.
Vague reps
A findings memo your counsel can use to scope reps and closing conditions.
The data room holds a 2-page security policy and a questionnaire where every answer is yes. Nobody has checked whether MFA covers the admin accounts, whether backups were ever restored, or which former employees still have remote access. The target's email domain has no DMARC record, and its VPN appliance runs firmware with a public advisory. Your lawyers can draft a cyber rep, but they can't tell you what it should cover. Sign without looking, and the first incident lands on the portfolio company's budget and your value creation plan.
We start outside the target, with what anyone on the internet can see: exposed services, email and domain records, certificates, and public breach history. After the LOI we work through the data room and interview the target's IT lead, then check the evidence behind each answer. Every finding gets a severity and a deal action, so your team raises it before signing, not after the first incident.
Outside-in screen before LOI
Exposed services, domain records, and breach history checked without contacting the target or touching its systems.
Evidence behind every answer
Questionnaire claims tested against exports, screenshots, and interviews, so a yes means yes.
Findings mapped to deal actions
Each issue tagged as a closing condition, a topic for counsel, or a 100-day plan item.
Our Cyber Due Diligence Services Process
Each step fits the deal clock. You get a red-flag memo before the LOI, approve the request list for the data room, and review findings with your deal team before signing.
We go over the target, the deal timeline, the sector, and what your investment committee needs to see. You leave with a fixed quote and a start date that fits the LOI. If a lighter outside-in screen answers your question, we'll tell you before we quote.
Projects We've Built
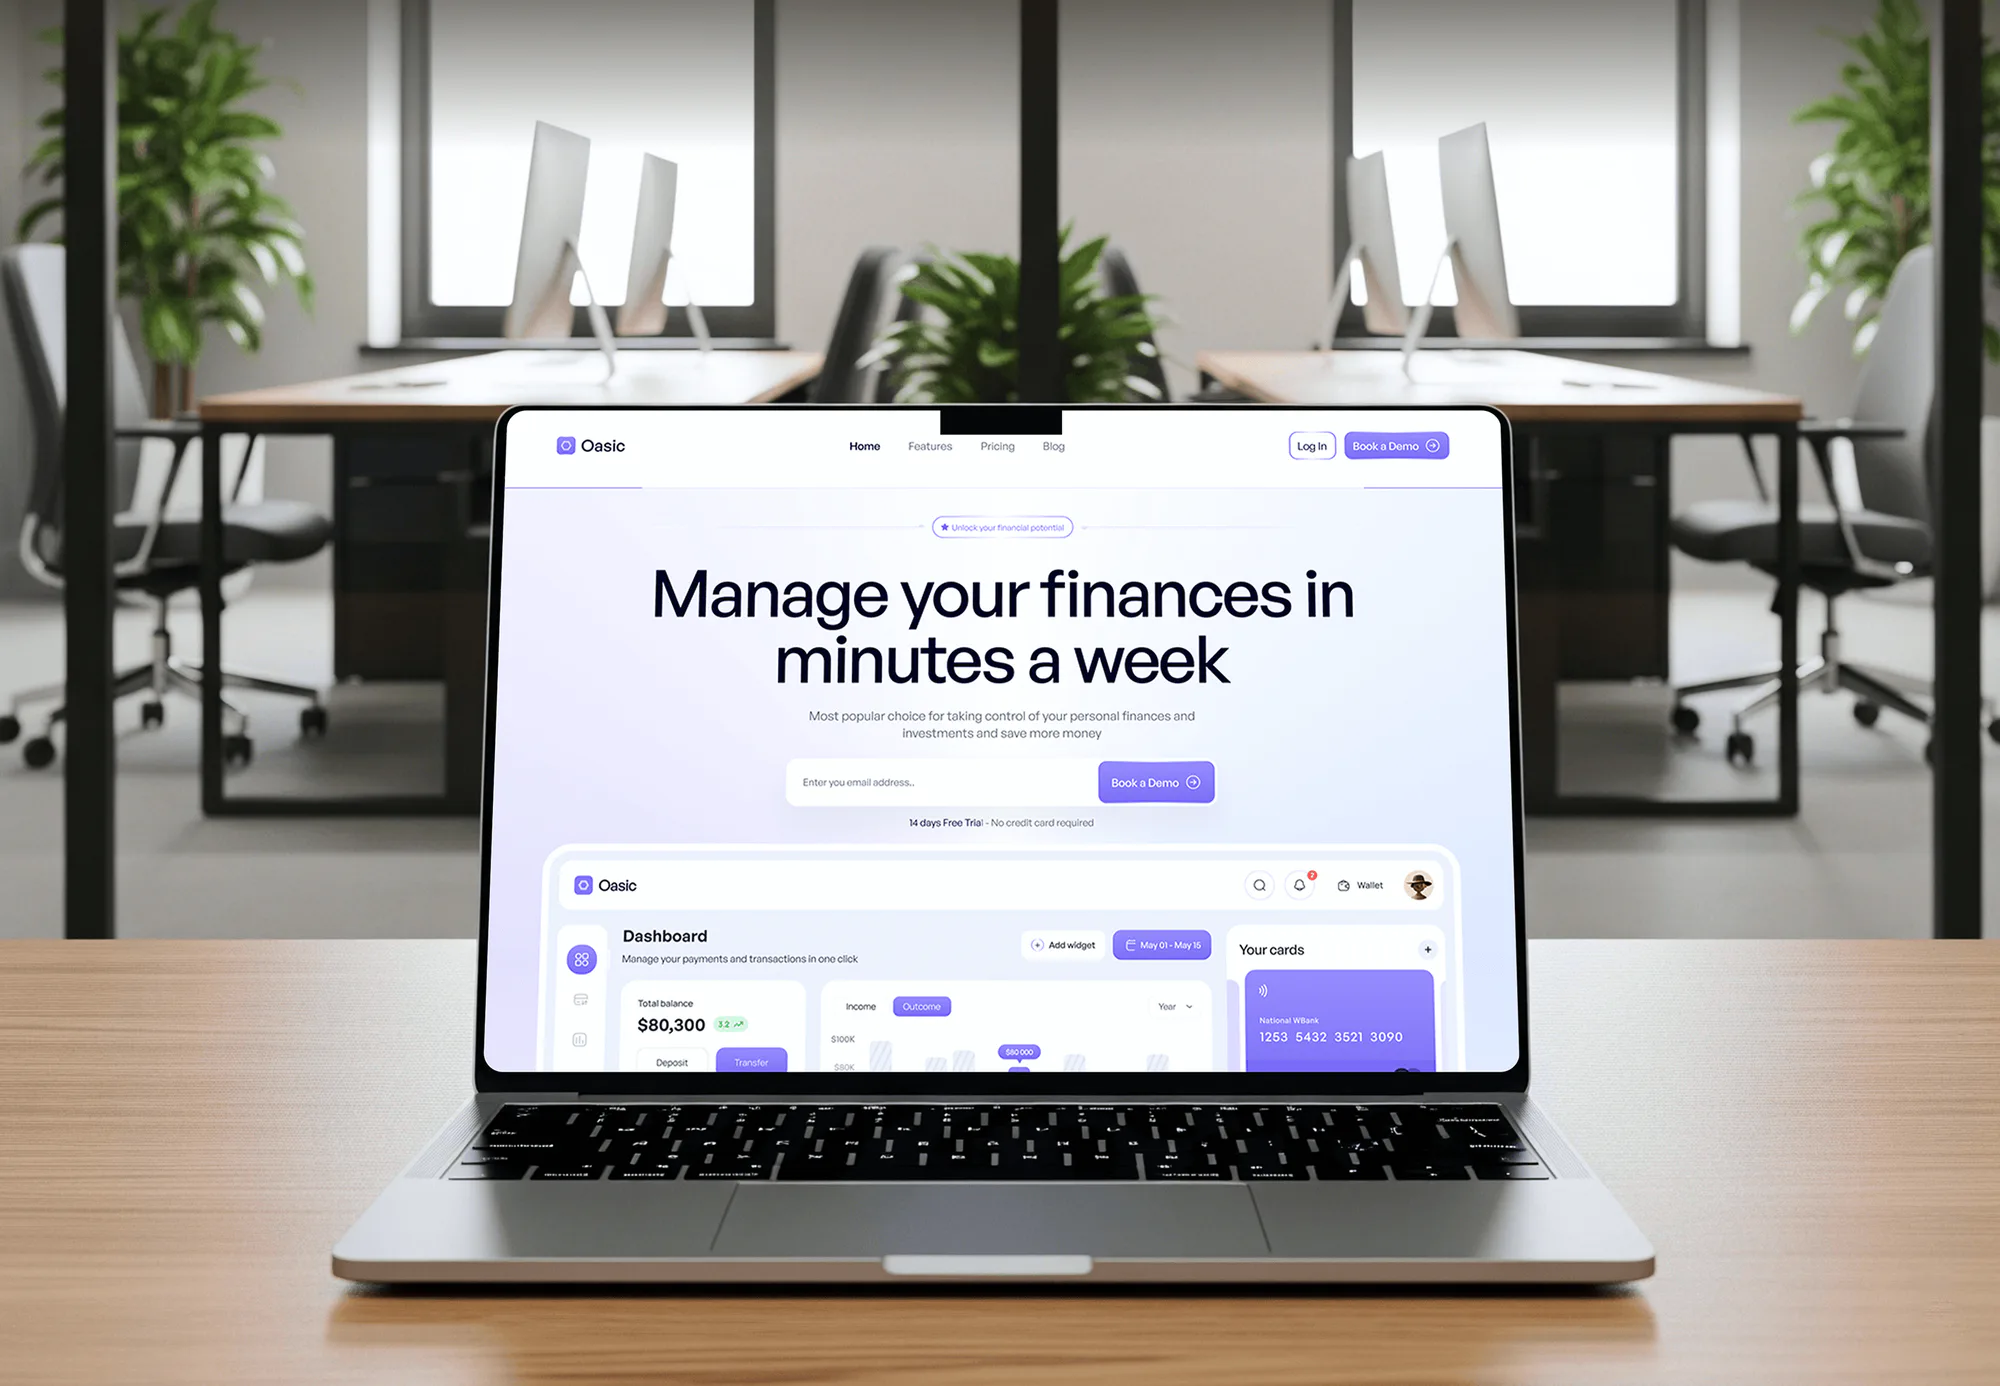
These investment, fintech, and fiduciary websites were design and build projects for finance teams, not diligence engagements. They show we know how financial firms present data.
What's Included
Everything a deal team needs to weigh security risk with its counsel: an outside-in screen, a data room review, evidence checks, deal-tagged findings, and a 100-day security plan.
Compare Options
Large advisory firms and a seller questionnaire both have a place in cybersecurity m&a due diligence. The rows show where each one fits and where it leaves gaps for a buyer.
| Feature | DeveloperLookBest fit | Large advisory firm | Questionnaire only |
|---|---|---|---|
| Planning | Free call, fixed price per deal | Engagement letter and team staffing | Template sent by the deal team |
| First view | Red-flag memo in 3 to 5 days | Weeks, depending on staffing | As fast as the seller replies |
| Outside-in scan | Included before the LOI | Included, often as a tool export | |
| Evidence checks | Exports, screenshots, and IT interview | Thorough, with large teams | Seller's word only |
| Deal actions | Every finding tagged for the deal | Strong ties to legal and tax | Not provided |
| Complex carve-outs | Up to 3 entities per review | Built for large global deals | Not suited |
| Cost | Fixed price from $950 | Higher fees, broader scope | Free to the buyer |
| Ownership | Report and plan stay yours | Yours, under their terms | The seller's document |
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Deal work runs on short clocks, partial access, and strict confidentiality. We built this service around all three, so your team gets answers it can act on.
We stage the work to your LOI, exclusivity, and signing dates. You get the red flags early, while they can still change the terms.
We test a target's systems only with its written consent. Outside-in checks use public information, so the seller stays in control of its own network.
Deal names, findings, and data room files stay with a small named team under NDA. Your deal doesn't sit in a shared ticket queue.
Every finding says what is wrong, why it matters to the deal, and how long a fix takes. Partners can read the summary without a security glossary.
We supply technical findings, while your lawyers draft reps and your advisors handle value. Nobody receives a legal opinion dressed up as a security report.
You get one price per target before work starts, with no hourly surprises during exclusivity. A second target or a carve-out gets its own quote up front.
Overview
DeveloperLook provides cyber due diligence services for private equity firms and corporate buyers. We screen the target from outside, review the data room, interview its IT lead, check evidence for key controls, and tag every finding with a deal action. Screens start at $950 with a red-flag memo in 3 to 5 business days, and full reviews take 2 to 4 weeks.
DEVELOPERLOOK
Project facts · Cyber Due Diligence Services
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Private equity deal teams
Your firm is heading toward an LOI on a software or services company, and the investment committee wants cyber risk covered before exclusivity ends.
Corporate development teams
You buy smaller competitors every year, each with a different IT setup, so you need the same cyber due diligence m&a assessment every time.
Operating partners after close
You closed on a company whose security wasn't reviewed before signing, and you need a 100-day plan the portfolio CEO can fund.
Family offices and independent sponsors
You invest without a large deal team, so m&a cyber due diligence has to fit a smaller budget and a short exclusivity window.
M&A advisors and law firms
Your client asks for a security view of the target, and you want cybersecurity for merger and acquisition work delivered under your brand.
Not a fit
Need a code review
You need the target's code quality, architecture, and engineering team assessed. Technical Due Diligence Services covers that, and both reviews can run side by side.
Seller preparing for sale
You're the seller and want your company ready before buyers ask. Cybersecurity Risk Assessment Services fits a seller-side review better than this page.
Need legal or valuation advice
You need reps drafted, indemnity negotiated, or a valuation adjustment set. That is work for deal counsel and financial advisors, and we support them with findings.
Budget under $950
You want a check under $950 on a target with a handful of staff. A seller questionnaire reviewed by your own IT lead is a cheaper start.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on target size, entity count, and seller access, and you get a fixed proposal after a free deal call.
For Agencies
You own the client and the deal relationship. We supply the security diligence behind it: outside-in screens, data room reviews, evidence checks, and 100-day plans, delivered in your branding for your client's deal team.
White label: your client only ever sees your brand
Send the target, timeline, and access limits, and we scope it in 1 business day.
One fixed white-label price and a named lead for each target.
Memo, findings, and plan arrive ready for your client's investment committee.
Send the target, timeline, and access limits, and we scope it in 1 business day.
One fixed white-label price and a named lead for each target.
Memo, findings, and plan arrive ready for your client's investment committee.
The Right Technology for Your Project
These are the scanning, identity, and evidence tools we use to check a target. Outside-in tools need no access, and the rest run only with the seller's consent.
CloudflareAWSMicrosoft AzureGoogle CloudGoogle SheetsFAQ
Straight answers on cost, timing, what gets checked, access to the target, and how findings shape the deal.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
DeveloperLook's deal reviews start at $950 for a pre-LOI red-flag screen of one target. A confirmatory review with the data room, an IT interview, and evidence checks costs $2,850. Larger targets, carve-outs, and reviews that add a 100-day plan start at $5,600, priced per deal before work begins.
A red-flag screen takes 3 to 5 business days, and a confirmatory review takes 2 to 4 weeks. The seller's response time sets most of that range, so we send the request list on day 1 of exclusivity. Rushed deals can get a shorter evidence check, with the gaps listed in the report.
Due diligence in cyber security is checking how well a company protects its systems and data before you buy it or invest. In a deal, that covers exposure, controls, incidents, and vendors. Due diligence cyber security work differs from a pen test because it weighs findings against the deal, not just the network.
In acquisitions, this diligence is the buyer's review of a target's security risk before closing, run alongside financial and legal diligence. It looks for exposed systems, weak controls, past incidents, and costs the buyer would inherit. Findings feed the reps, the closing conditions, and the 100-day plan.
DeveloperLook offers them for buyers, and sellers can book a matching readiness review. Buyers get the screen, data room review, and evidence checks on this page. Sellers preparing for a buyer's questions usually start with our Cybersecurity Risk Assessment Services, so policies, MFA, and backups are documented before the data room opens.
It checks exposed internet services, email security records, MFA coverage, admin accounts, backups and restore tests, endpoint protection, vendor access, and incident history. We also read the cyber insurance policy and any breach notices. Each finding is rated by severity and tied to a deal action, so the report reads like a deal document.
Not for the first screen, which uses only public information such as DNS, email records, certificates, and exposed services. Deeper checks need the seller's written consent and run through exports, screenshots, or read-only reviews. We don't scan or test a target's network without that permission.
Each finding gets one of three tags: a closing condition, a topic for counsel, or a 100-day plan item. Counsel uses the findings to scope cyber reps and any special indemnity, and your advisors decide on value. We don't give legal or valuation advice, and we point out which findings deserve those conversations.
The report becomes the start of the 100-day security plan. Critical fixes such as MFA on admin accounts and tested backups go first, each with an owner and a budget range. Your operating partner can hand the plan to the portfolio company's IT lead, or our vCISO Services can run it for the first months.
You get 30 days of follow-up questions after delivery, including calls with counsel or lenders about specific findings. If the deal changes scope, we quote any extra checks before starting. Reports, evidence, and the plan stay yours, so a later buyer or insurer can see what was reviewed.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.