
Architecture and structure review
How the code is organized, where it's tangled, and whether it can grow with your product.

For founders and product owners who need an honest read on their codebase: what's solid, what's risky, and what to fix first, from $650.
Top 10
Fixes ranked by risk and cost
100%
Dependencies checked for known flaws
How your project runs
Teams we have built for:














The Problem
The doubt usually shows up at a handover: an agency leaves, a freelancer goes quiet, or a new developer says everything needs a rewrite. You need a second opinion you can trust.
01 · Second opinion
A new developer says the whole app needs a rewrite.
We measure the code and show which parts truly need rebuilding, if any.
02 · Dependencies
Nobody has checked the project's packages since launch.
Every dependency is checked against known vulnerability databases and its license terms.
03 · Secrets
Passwords and API keys sit in plain config files.
We flag exposed secrets and show how to move them into a secret manager.
04 · AI code
Large parts of the code came from an AI assistant.
We read AI-written code for logic errors, unsafe patterns, and missing tests.
Your MVP was built by a freelancer you found online, and it works, mostly. Now a new developer says half of it should be rewritten, and quotes to match. You can't tell if they're right. Nobody has looked at the 140 npm packages in the project since launch. There are no tests, the admin password sits in a config file, and parts of the code came straight from an AI assistant. You're about to fund the next phase without knowing what you're building on.
We start by reading the code the way a new senior hire would, then back that up with scans. Static analysis measures complexity and duplication, dependency checks flag known vulnerabilities and license risks, and a manual review covers architecture, tests, and how data and secrets are handled. You get a plain-English source code audit with every finding ranked by risk and cost to fix. You decide on evidence, not on whoever sounds most certain.
Read by a senior developer
Scanners find patterns. A person checks whether the architecture fits what your product needs to do.
Fixes ranked, not dumped
Each finding has a severity, an effort estimate, and an order, so you know what to fix first.
Plain English for owners
A summary written for non-developers, plus technical notes your developers can act on directly.
Our Code Audit Services Process
You see the scope and price before we start, and you can question every finding before the report is final.
We ask what the software does, who built it, and what decision the audit has to support. You share the stack, the rough size, and where the code is hosted. You get a fixed price and a list of what we'll review.
What's Included
A full read of your codebase across 6 areas, backed by automated scans. Every finding comes with a severity, an effort estimate, and a suggested fix.
Compare Options
Scanners are cheap and fast, and your own developer knows the history. Here's what each one catches, so you can pick the right check for your decision.
| Feature | DeveloperLookBest fit | Automated scanner | In-house developer |
|---|---|---|---|
| Independence | No stake in the codebase | Neutral, but no judgment | Reviewing their own work |
| Architecture judgment | Senior developer review | Not covered | Strong on history |
| Known vulnerable packages | Scanned and explained | Fast and thorough | Depends on habits |
| Business logic errors | Read on critical paths | Rarely caught | Often caught |
| Report for non-developers | Owner summary included | Raw findings only | Usually informal |
| Fix priorities | Ranked by risk and cost | Ranked by severity only | Based on preference |
| Cost | Fixed, from $650 | Free to a low monthly fee | Salary time, no invoice |
| Time to results | About 1 to 2 weeks | Minutes | When time allows |
Projects We've Built
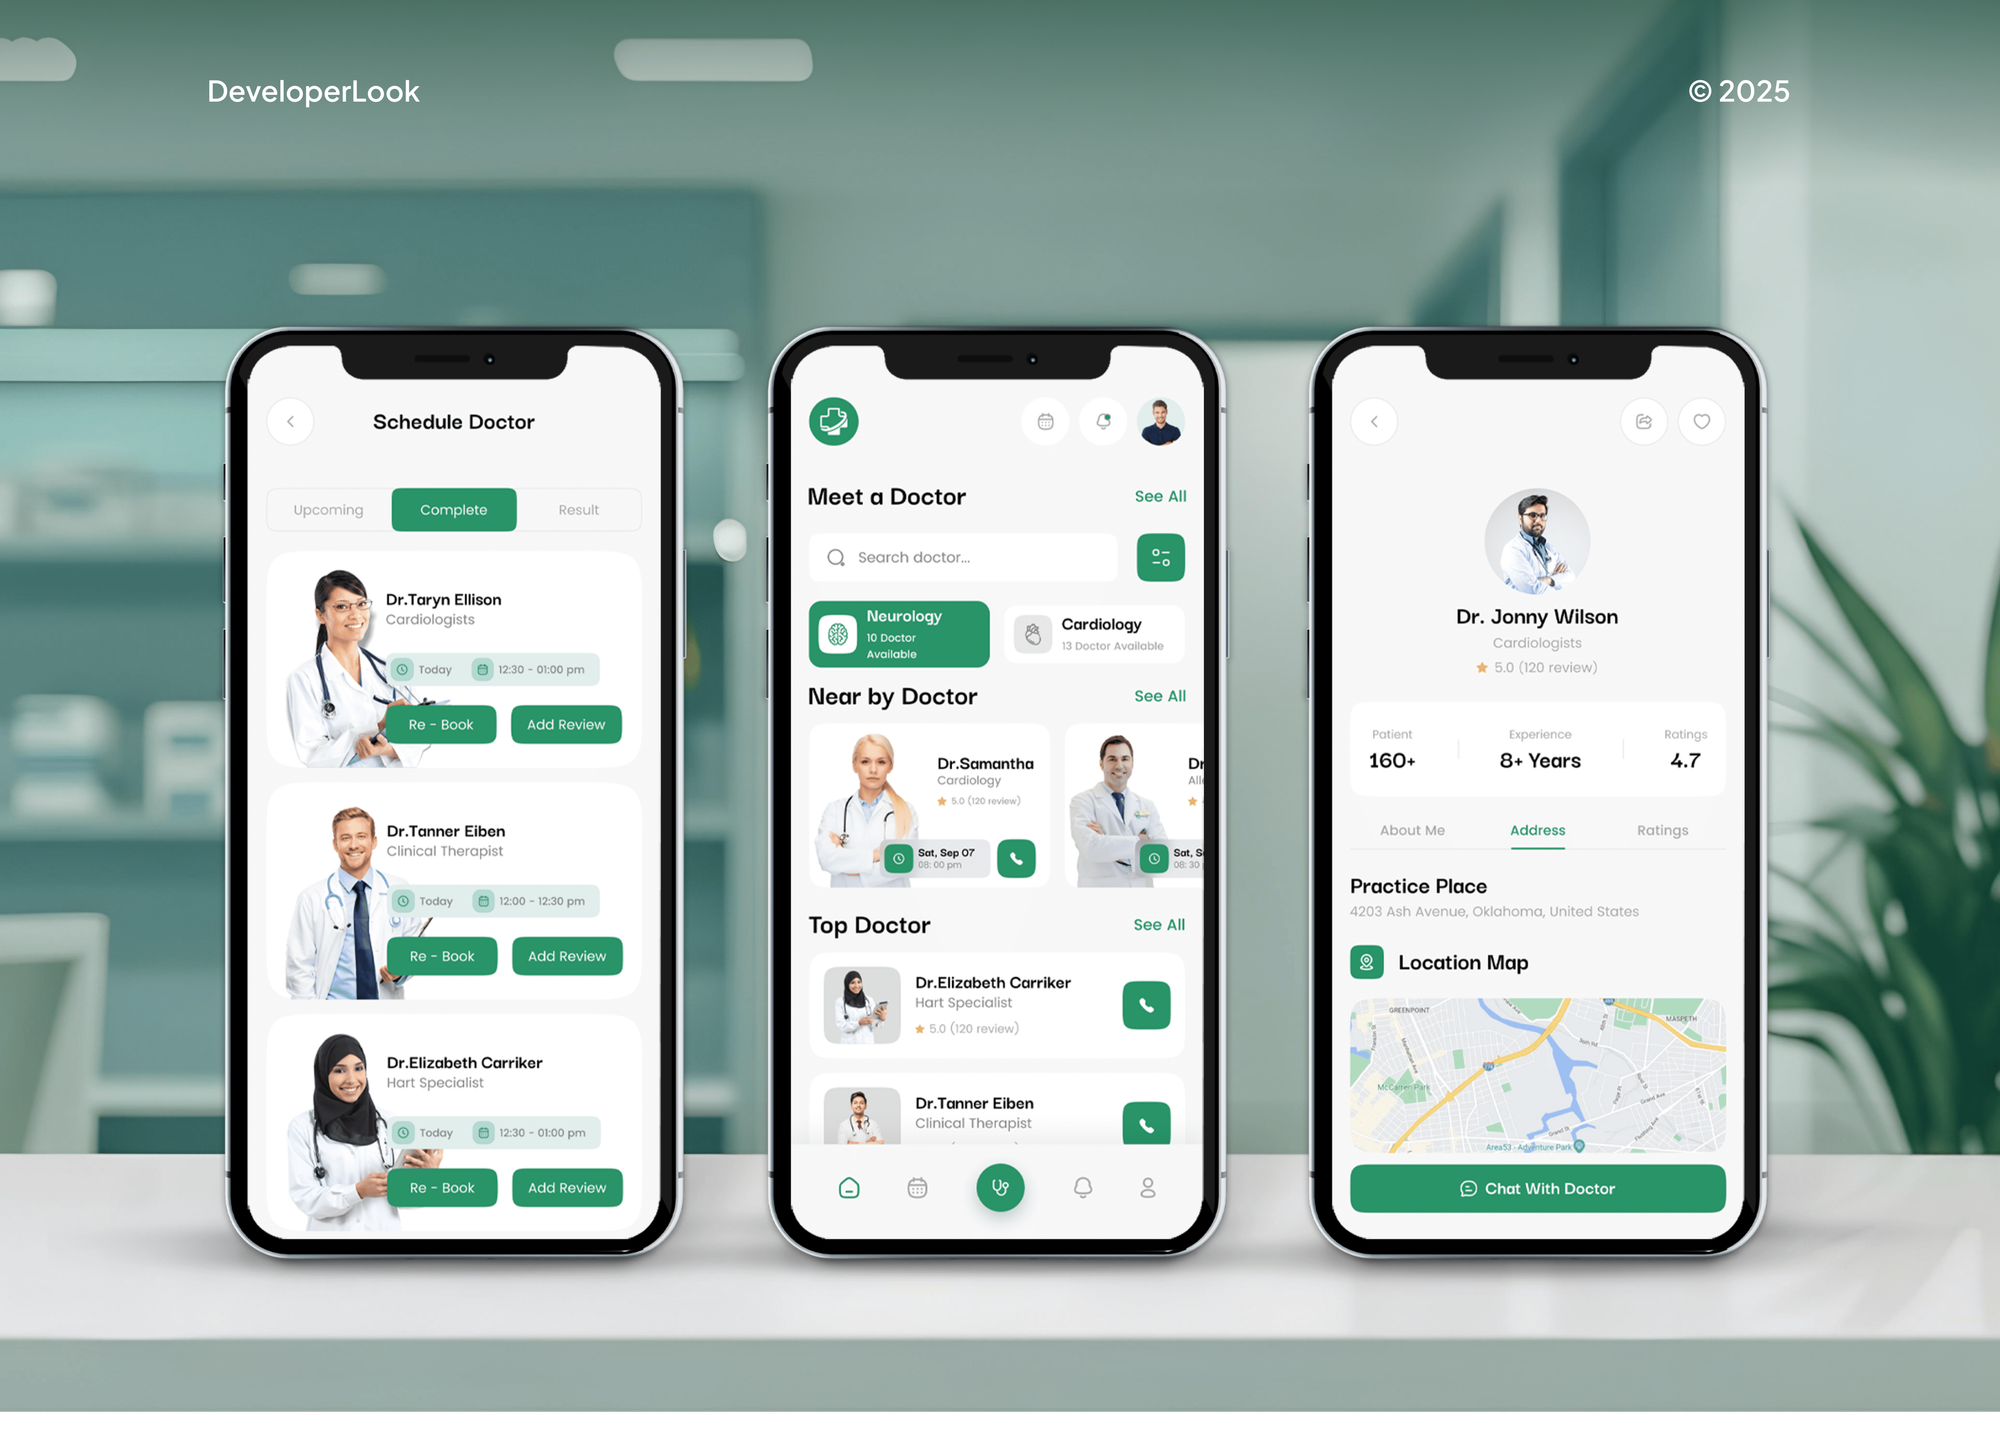
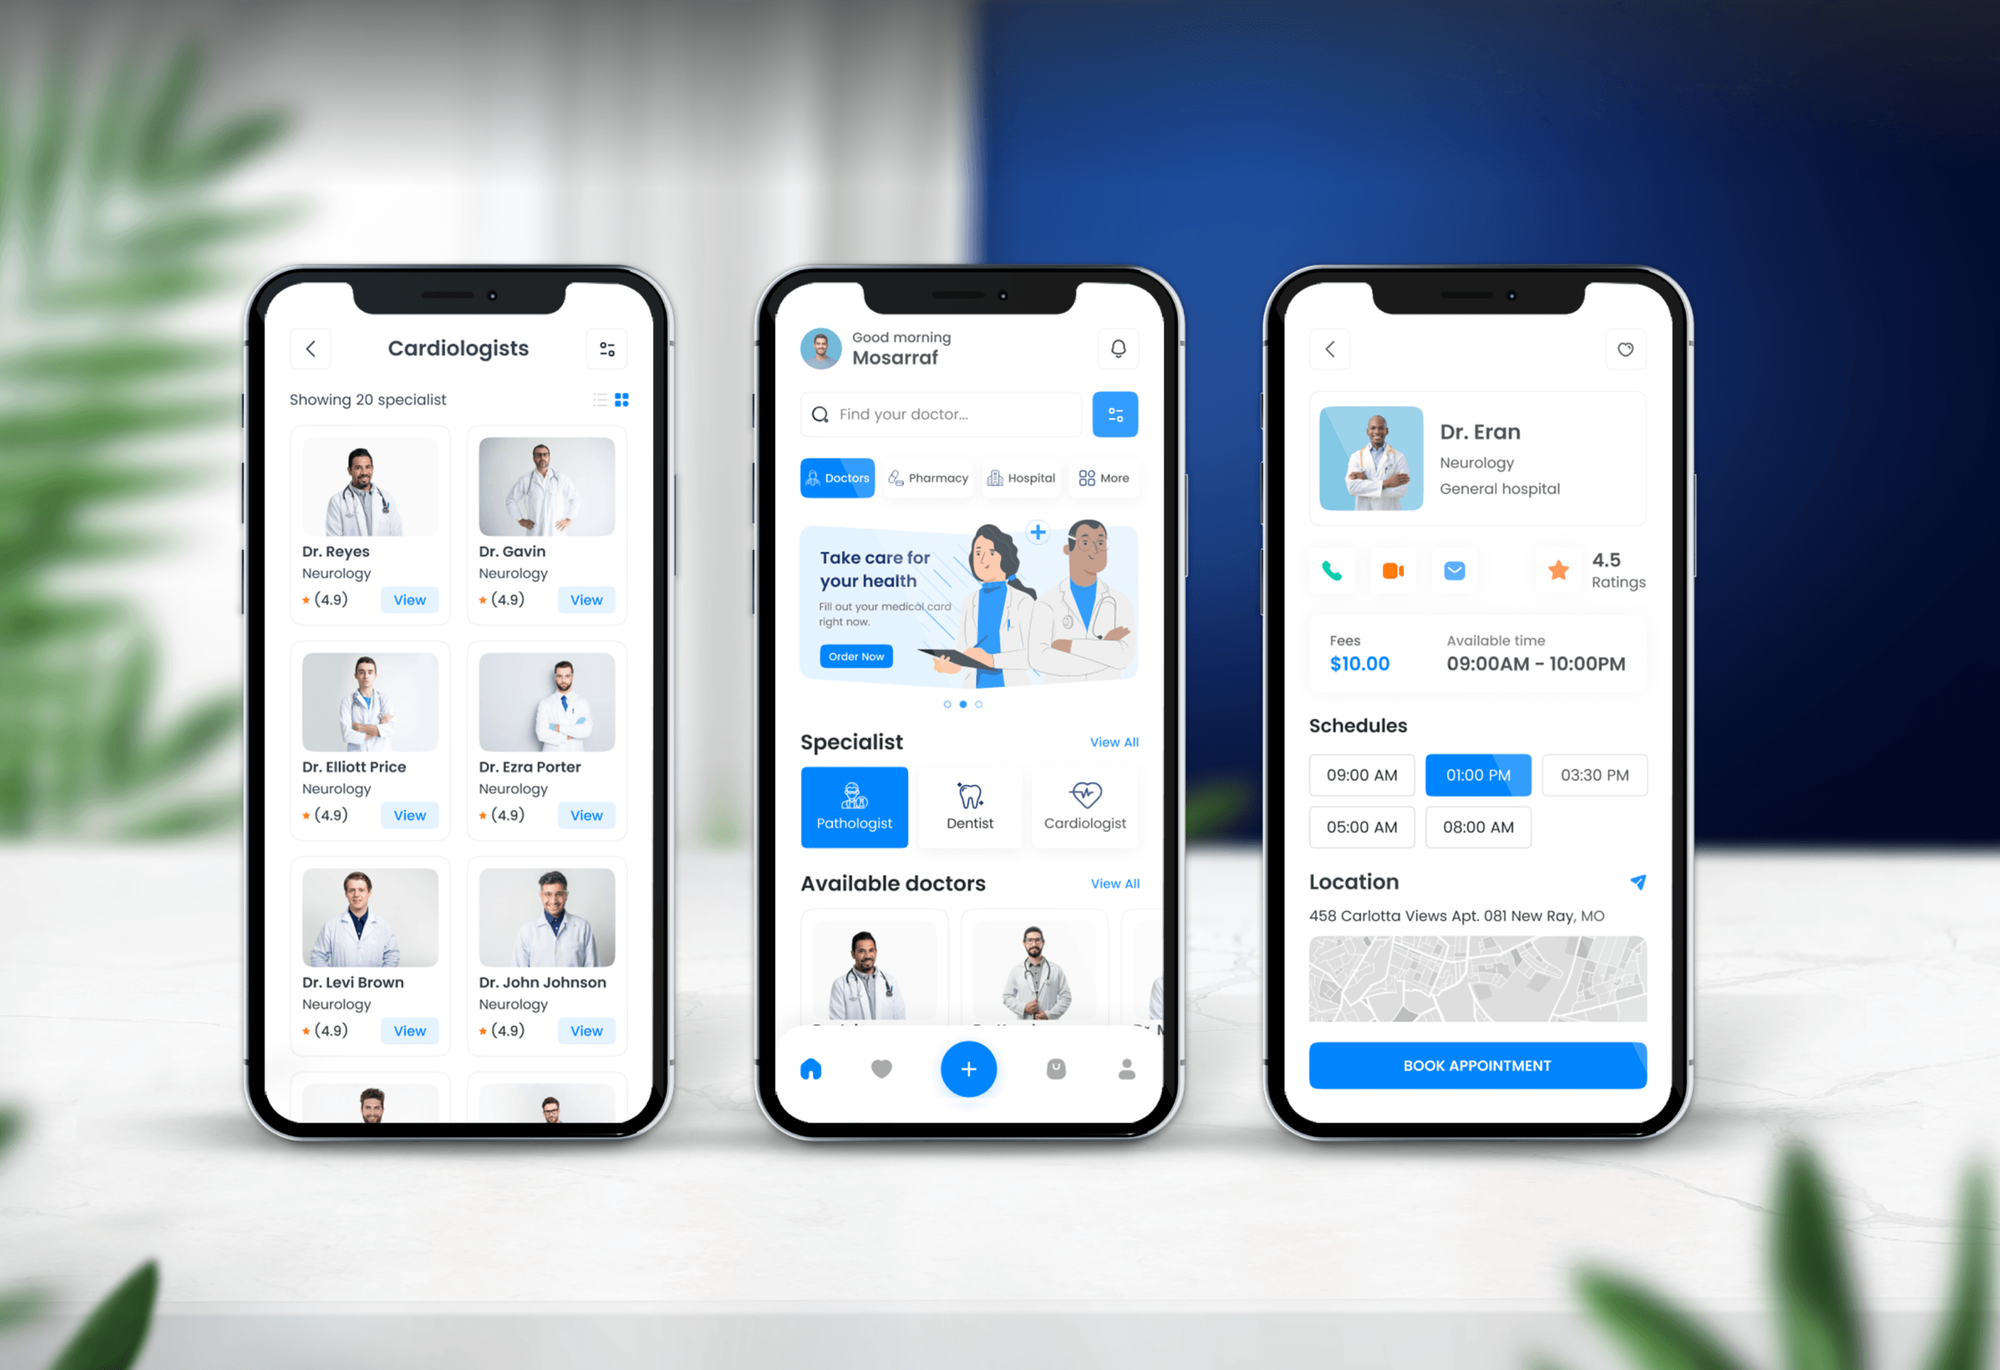
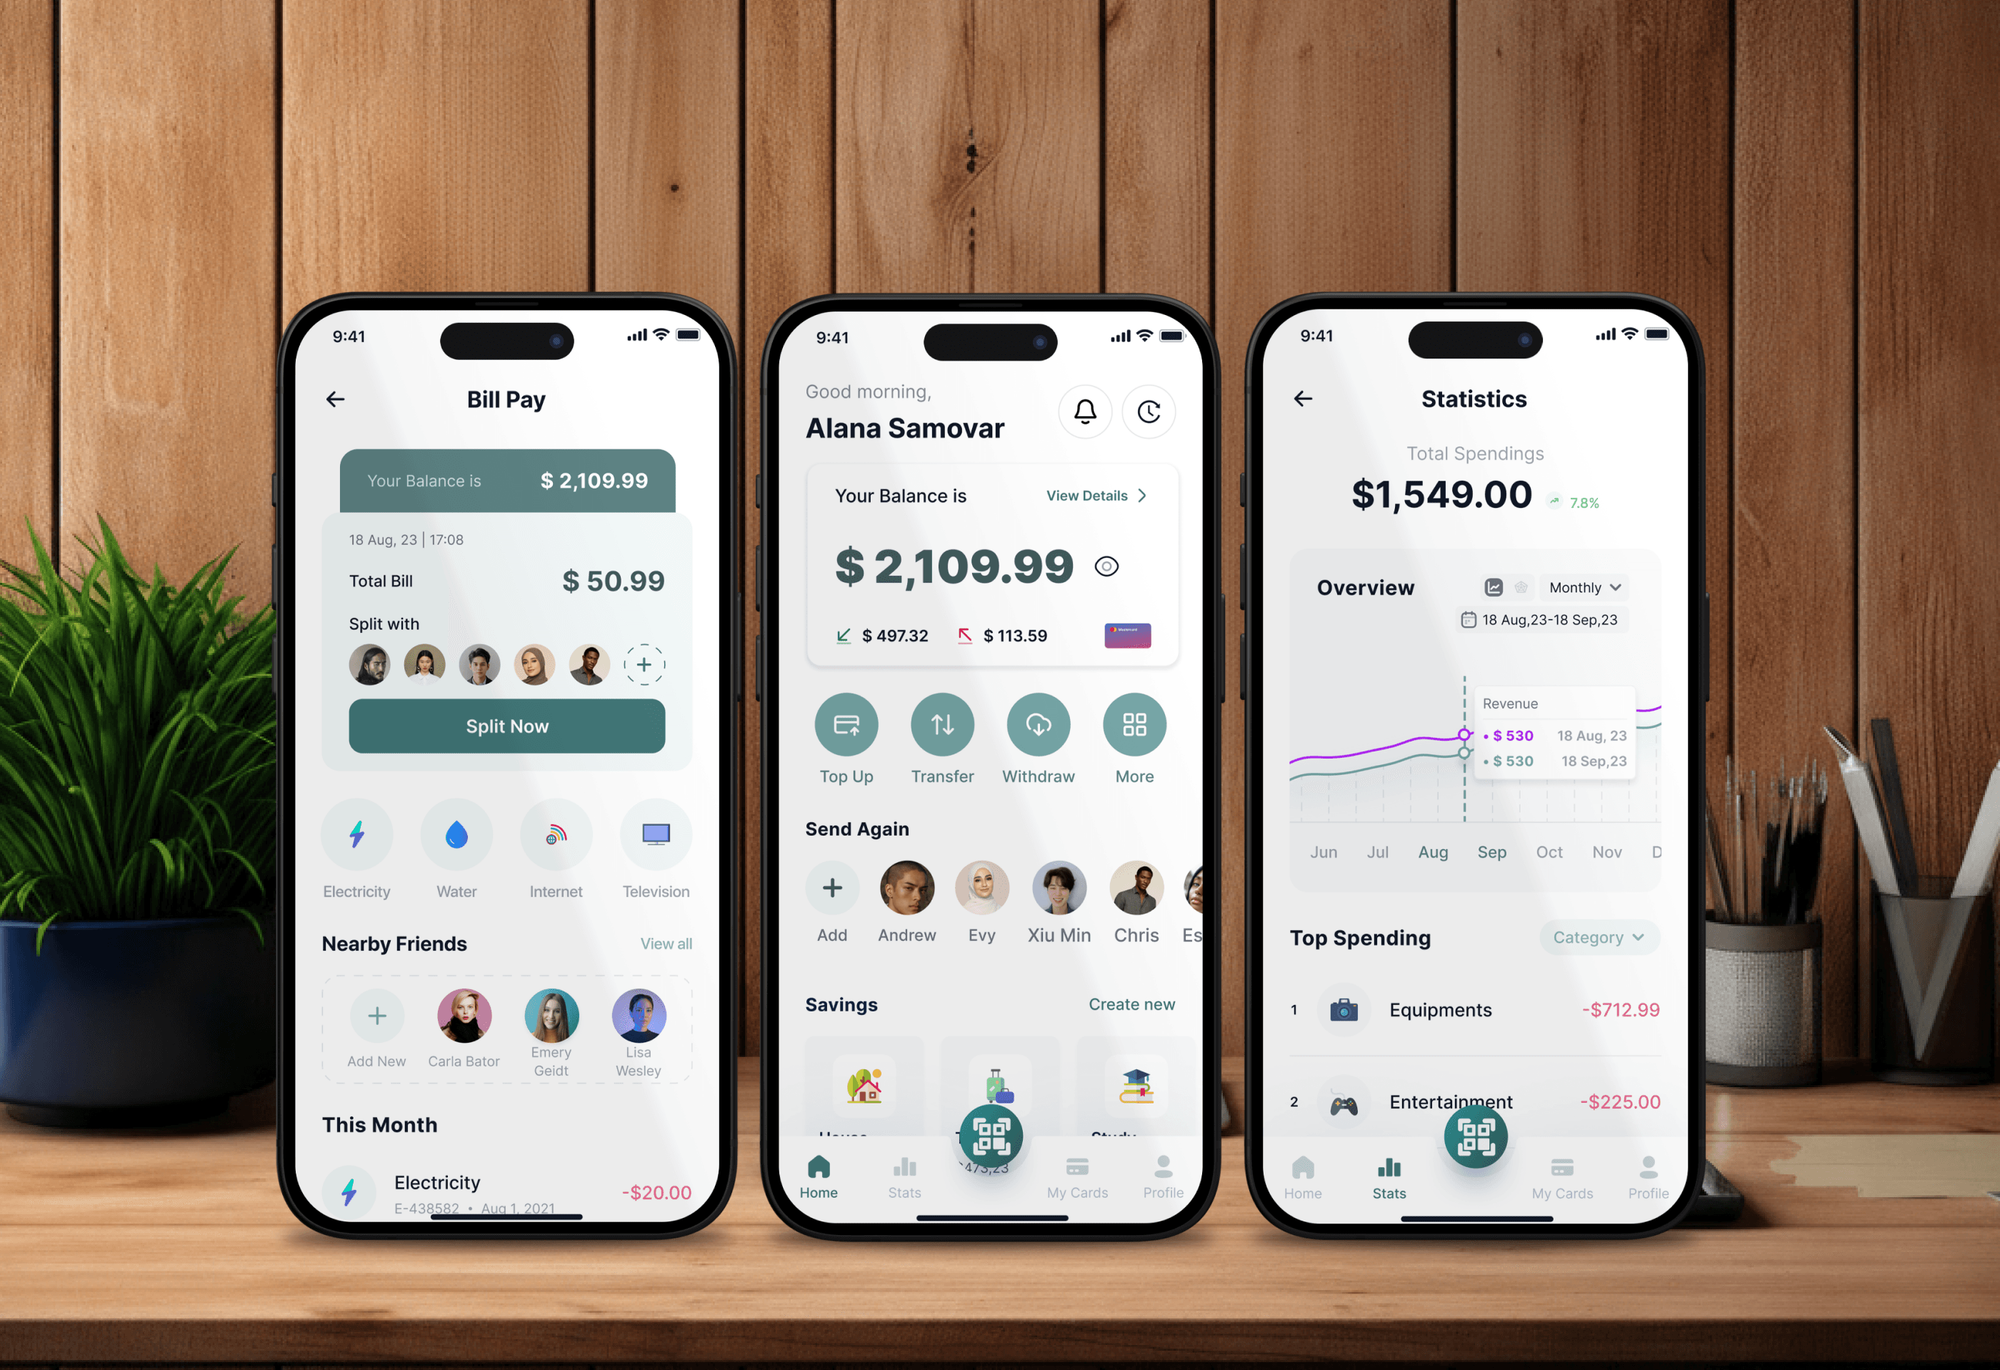
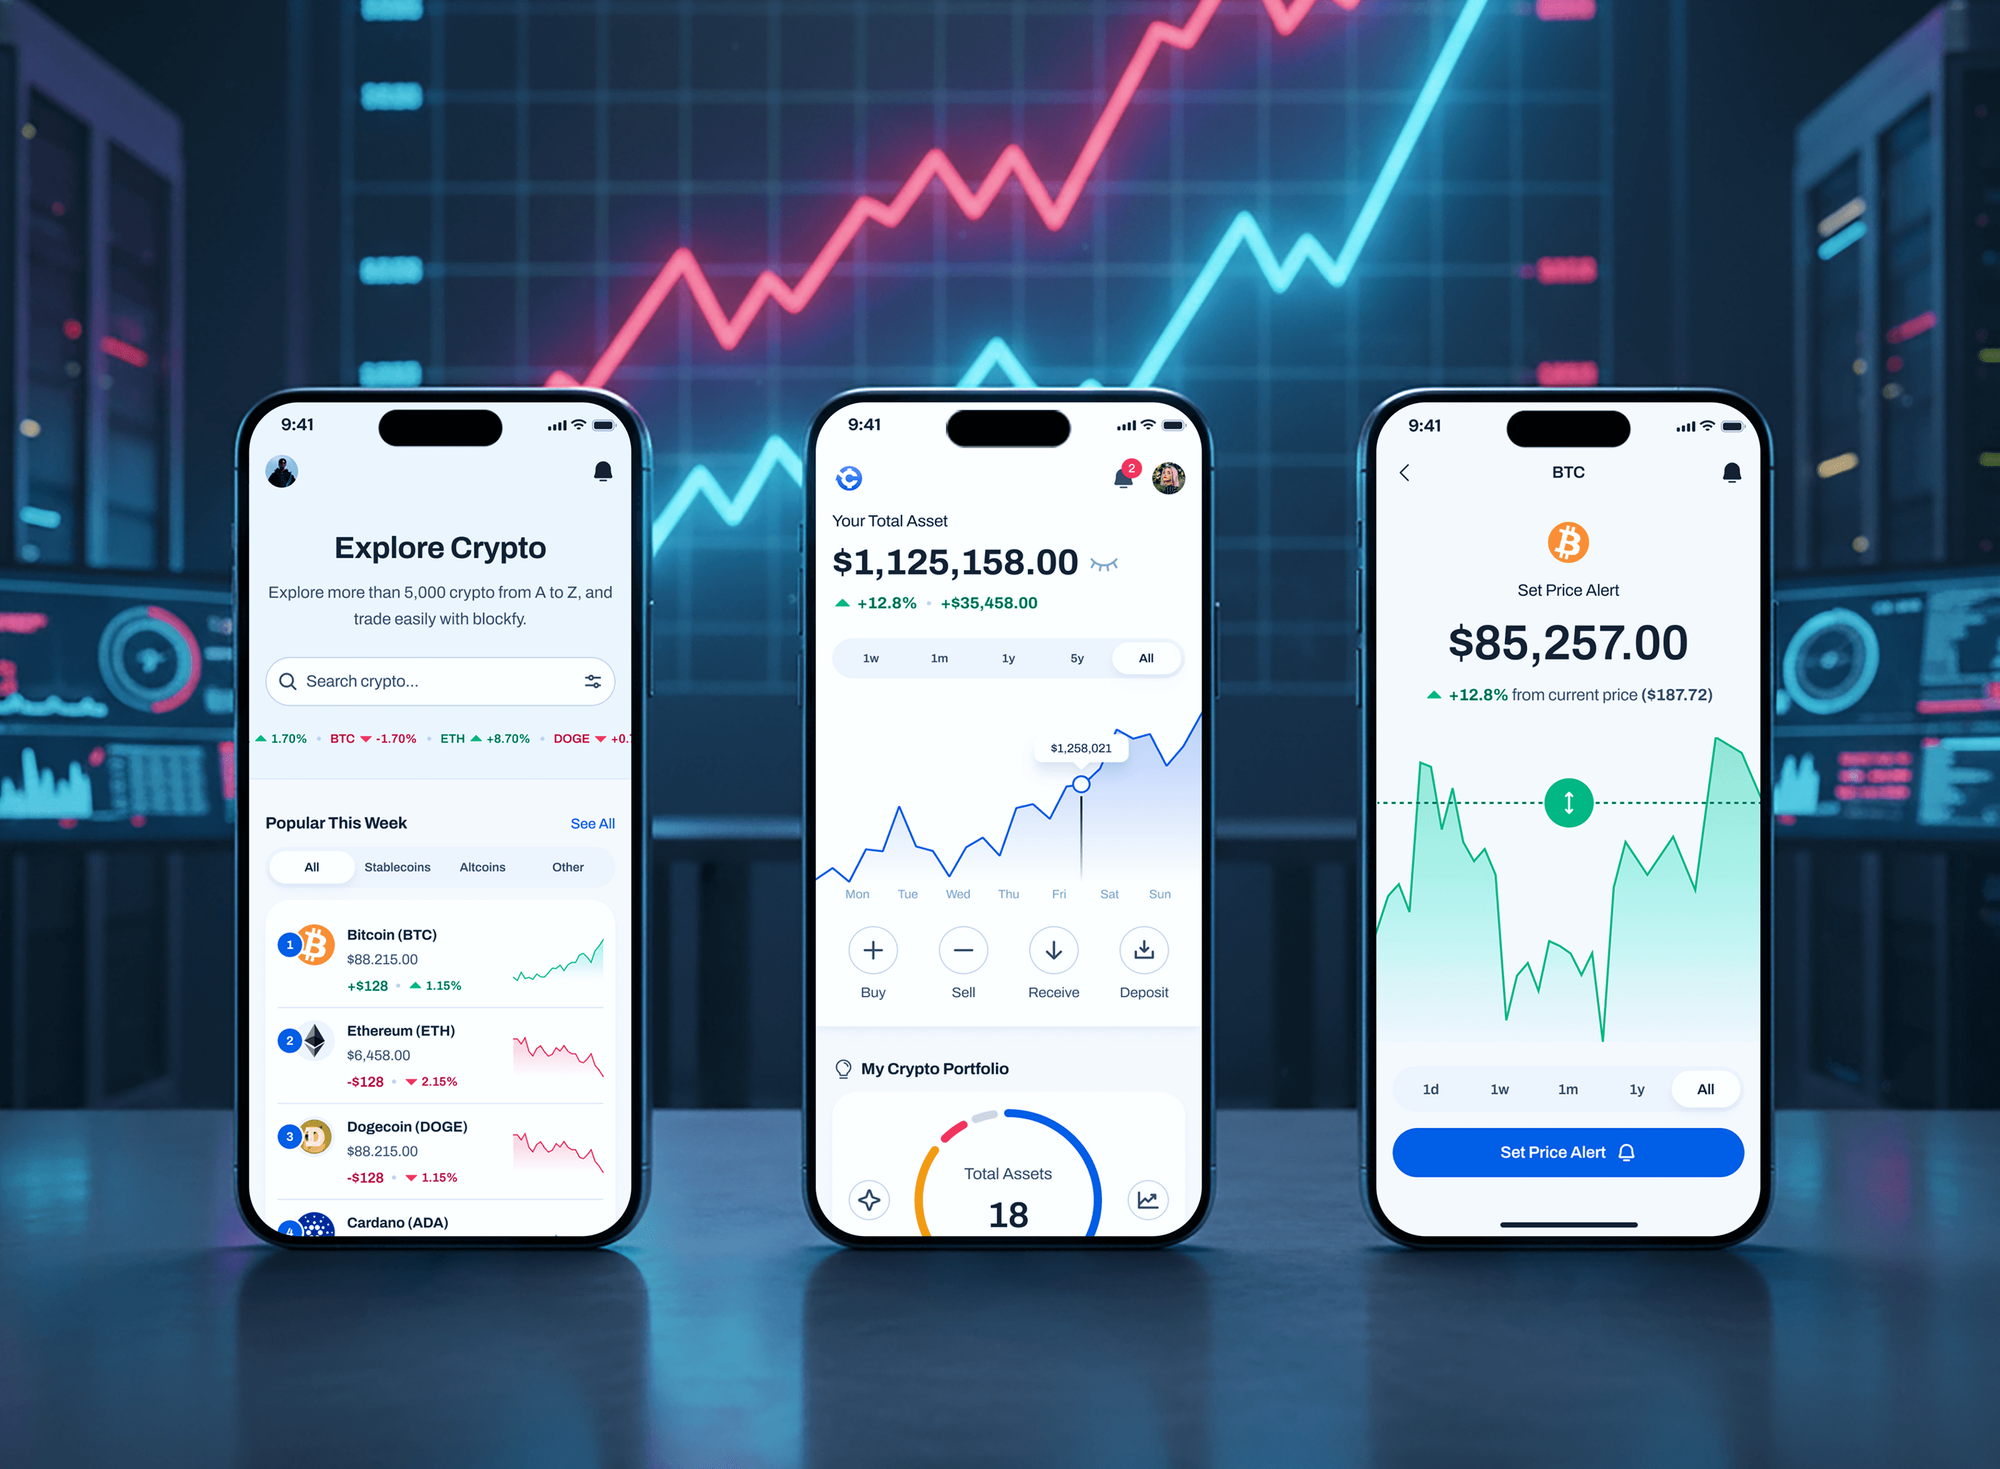
Apps we designed and built, including healthcare and finance products. They show the kind of code we read, not audits we performed.
What Our Clients Say
Feedback from teams we have built web and mobile apps for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
An audit is only useful if it's honest and readable. These habits keep our findings fair to the people who wrote the code and useful to the people paying for it.
We judge code by the constraints it was written under, not by hindsight. Findings describe problems and fixes, not the people behind them.
Each issue comes with an hour estimate to fix it. You can budget the next quarter from the report instead of guessing.
We don't sell a rewrite on the back of an audit. If most of your code is sound, the report says so in its first paragraph.
We work from read-only repository access and sign your NDA before we look. Production data and passwords stay out of the review.
Code written by AI assistants often looks right but skips edge cases and input checks. We read those sections line by line.
The summary is for you, and the technical notes are for your developers. Both read the same findings, so nobody argues later about what was said.
Overview
DeveloperLook provides code audit services for web and mobile apps built by agencies, freelancers, or AI tools. A senior developer reviews architecture, maintainability, dependencies, tests, and security risks, backed by automated scans. Audits start at $650, most take 1 to 2 weeks, and you get a plain-English report with fixes ranked by risk and cost.
DEVELOPERLOOK
Project facts · Code Audit Services
Reviewed 8 Oct 2026 by Saimul Islam
Good fit
Founders with a freelancer-built MVP
Your MVP works, but the freelancer who built it is gone, and you want a software code audit before funding the next phase.
Owners taking over from an agency
Your agency contract just ended, and you want to know what you actually received before you hand the code to a new team.
Teams shipping AI-generated code
Your developers ship faster with AI assistants, and you want a person to check what those tools wrote before customers find the bugs.
Healthcare and finance app owners
Your app stores health or payment data, and you need to know where the code handles it carelessly before a customer's security review.
Agencies needing a second opinion
You inherited a client project and want a code audit company to review it under your brand before you quote any changes.
Not a fit
Need a penetration test
You need an attacker's view of your live app, not a review of its code. Web Application Penetration Testing Services covers that.
Live website check only
You want speed, SEO, and design checked on your marketing site. Website Audit Services reviews the live site, not the repository.
Need a compliance certificate
You need a SOC 2 report or a HIPAA attestation. An audit firm issues those; our findings support the work but certify nothing.
Budget under $650
You want a quick opinion on a few files. A free automated scanner or an hour with a freelancer costs less than our Code Snapshot.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the size of the codebase, the number of repositories, and the stack, and you get a fixed proposal after a free scoping call.
For founders who need a fast, honest read on one small app before a decision.
$650one-time, USD
For products heading into a funding round, a team change, or a major release.
$1,400one-time, USD
For teams with several repositories or services who need a costed plan and a recheck.
$2,250one-time, USD
For Agencies
You own the client relationship. We supply the independent review: a full audit under your brand before you quote changes, take over a project, or defend your own team's work. Your client sees your logo on the report.
White label: your client only ever sees your brand
Give read-only access and tell us what the client needs to decide.
We scan, read, and rank the findings, then check them with you first.
You present the report, and we join the walkthrough if you want us there.
Reports carry your brand, and we stay off client calls unless invited.
Price takeover work from measured findings, not a gut feeling.
Developers who've maintained code in every major web stack.
A Code Snapshot is usually ready in about 1 week.
The Right Technology for Your Project
The languages we read and the scanners behind our reviews. Every automated result is checked by a person before it reaches the report.
 JavaScript
 TypeScript
 PHP
 Python
 Java
 .NET
 React
 Next.js
 Node.js
 Laravel
 Django
 Flutter
 OWASP
 PostgreSQL
 MySQL
 MongoDB
 Firebase
FAQ
Straight answers on price, timing, what an audit covers, and how your code stays confidential.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Our audits start at $650 for a snapshot of one repository with the top 10 fixes ranked. A Full Code Audit costs $1,400, and the Audit and Fix Plan for up to 3 repositories costs $2,250. Size and stack set the price, and you get a fixed quote after the free scoping call.
A review of one code change takes well under an hour, but auditing a whole app takes 1 to 2 weeks. Careful reading slows down over long sessions, so we split the audit into focused sessions and back them with scans. Several repositories can take up to 3 weeks.
A code audit is an independent review of a whole codebase, done before a decision rather than before a single merge. It checks architecture, code quality, dependencies, tests, and security risks. Code auditing ends in a report with ranked findings and effort estimates, not a long list of line comments.
Code review is a developer checking a colleague's change before it's merged into the main codebase. It catches bugs, unclear logic, and style problems while they're small. It's a daily team habit, while an audit looks at the whole project at once. Code review as a service gives small teams an outside reviewer on a schedule.
Code review is important because it catches defects when they're cheapest to fix: before they ship. It also spreads knowledge, so one developer leaving doesn't take the system's logic with them. Teams that skip regular reviews tend to pile up the duplication and shortcuts a later audit has to untangle.
You do a code audit when a decision depends on the code's real condition. Common triggers are taking over from an agency, raising money, hiring a new team, or planning a big release. The audit tells you whether to fix, refactor, or rebuild, and roughly what each option will cost.
AI-generated code needs human review because it often looks correct while missing edge cases, input checks, and error handling. Assistants can also suggest outdated or nonexistent packages and repeat insecure patterns. A developer who knows your product's rules catches what the tool can't know about your business.
We can review your healthcare app's code against the technical safeguards in the HIPAA Security Rule: access control, audit controls, integrity, authentication, and transmission security. We trace where protected health information is stored, logged, or exposed. Our findings support your compliance work, but HIPAA compliance stays your organization's responsibility, and we don't certify it.
A website code audit from us covers JavaScript, TypeScript, PHP, Python, Java, and .NET, plus frameworks like React, Next.js, Laravel, and Django. We also review Flutter mobile apps and the databases behind them. If your stack falls outside that list, we'll say so on the scoping call instead of learning it on your budget.
Yes. We sign your NDA before we get access, work from read-only repository rights, and delete our local copies when the engagement ends. We don't need production data or customer records for the review. You own the final report and can share it with investors, buyers, or a new development team.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.