
OT asset inventory
Every PLC, HMI, historian, and engineering workstation seen on the wire, with its role and connections.

For plant and operations leaders who need the control network mapped and segmented without risking production: passive discovery, zone design, one vendor path. From $1,100.
IT/OT
Boundary mapped with rules
1gateway
For every vendor's remote access
How your project runs
Teams we have built for:














The Problem
The risk shows up when ransomware reaches a competitor's floor or a customer questionnaire asks about OT. That's when plants find out nobody can list every controller or vendor connection.
01 · Unknown assets
Nobody can list every PLC, HMI, and drive on the network.
Captured traffic becomes an inventory with each device's role, vendor, and visible firmware.
02 · Flat network
Office PCs and plant controllers share one flat network.
Zones and conduits separate office, supervisory, and control systems with explicit rules.
03 · Vendor access
Each machine builder left its own remote access box behind.
One gateway with MFA and session logs replaces the scattered remote tools.
04 · Scan fear
An active scan once froze a controller, so nothing gets checked.
We work from copied traffic, so controllers receive no probe traffic from us.
Your plant network grew one machine at a time. The packaging line has its own switch, and the new press came with a vendor's remote access box. The historian talks to an office PC that also opens email. Nobody can list every PLC and HMI, because an active scan once froze a controller and scans were banned. Then ransomware hits a competitor's ERP and spreads to their floor. Your plant manager asks a fair question: if that email had opened here, which machines would have stopped?
We start by listening, not scanning: your team mirrors a switch port, and we study the captured traffic offline. From that we build an asset inventory, map who talks to whom, and draw the line between IT and OT. Then we design zones, conduit rules, and one controlled path for vendors, matched to ISA/IEC 62443. Your engineers make the changes in planned downtime. Production keeps running while the risk shrinks, instead of stopping for a security project.
Passive discovery only
No active scans on the control network: we learn from captured traffic your team provides.
Clear IT and OT boundary
Firewall rules between office and plant systems, written so your engineers can apply them.
One path for vendors
Every integrator and machine builder reaches the plant through one gateway with MFA and logs.
Our OT Security Services Process
You approve the capture plan, review the inventory with us, and sign off every rule set before your engineers apply it.
On a video call, you walk us through the lines, the network closets, and the vendor connections you know about. You get a written scope and a fixed price. If your OT vendor's built-in tools already cover what you need, we'll tell you before we quote.
What's Included
The full scope runs from a passive asset inventory to zone design, conduit firewall rules, a single vendor access path, and a monitoring plan for larger sites.
Compare Options
OT platform vendors and controls integrators are both useful: one watches traffic all year, the other knows your PLC logic. Here is where each fits a plant security project.
| Feature | DeveloperLookBest fit | OT platform vendor | Controls integrator |
|---|---|---|---|
| Discovery method | Passive capture, analyzed offline | Sensor appliance on your network | Site walkdown and drawings |
| Asset inventory | Built from real traffic | Continuous once licensed | From project documents |
| Zone design | Mapped to ISA/IEC 62443 | Suggested by the platform | Done during new installs |
| Vendor access | One gateway with MFA and logs | Monitored, not redesigned | Their own remote tool |
| PLC and safety logic | Left to your engineers | Not touched | Their core skill |
| Ongoing monitoring | Design and alert rules | Included with the license | Not included |
| Ownership | Inventory and rules you keep | Data inside their platform | Drawings in the project file |
| Cost predictability | Fixed price from $1,100 | Yearly license per site | Quoted per project |
Projects We've Built
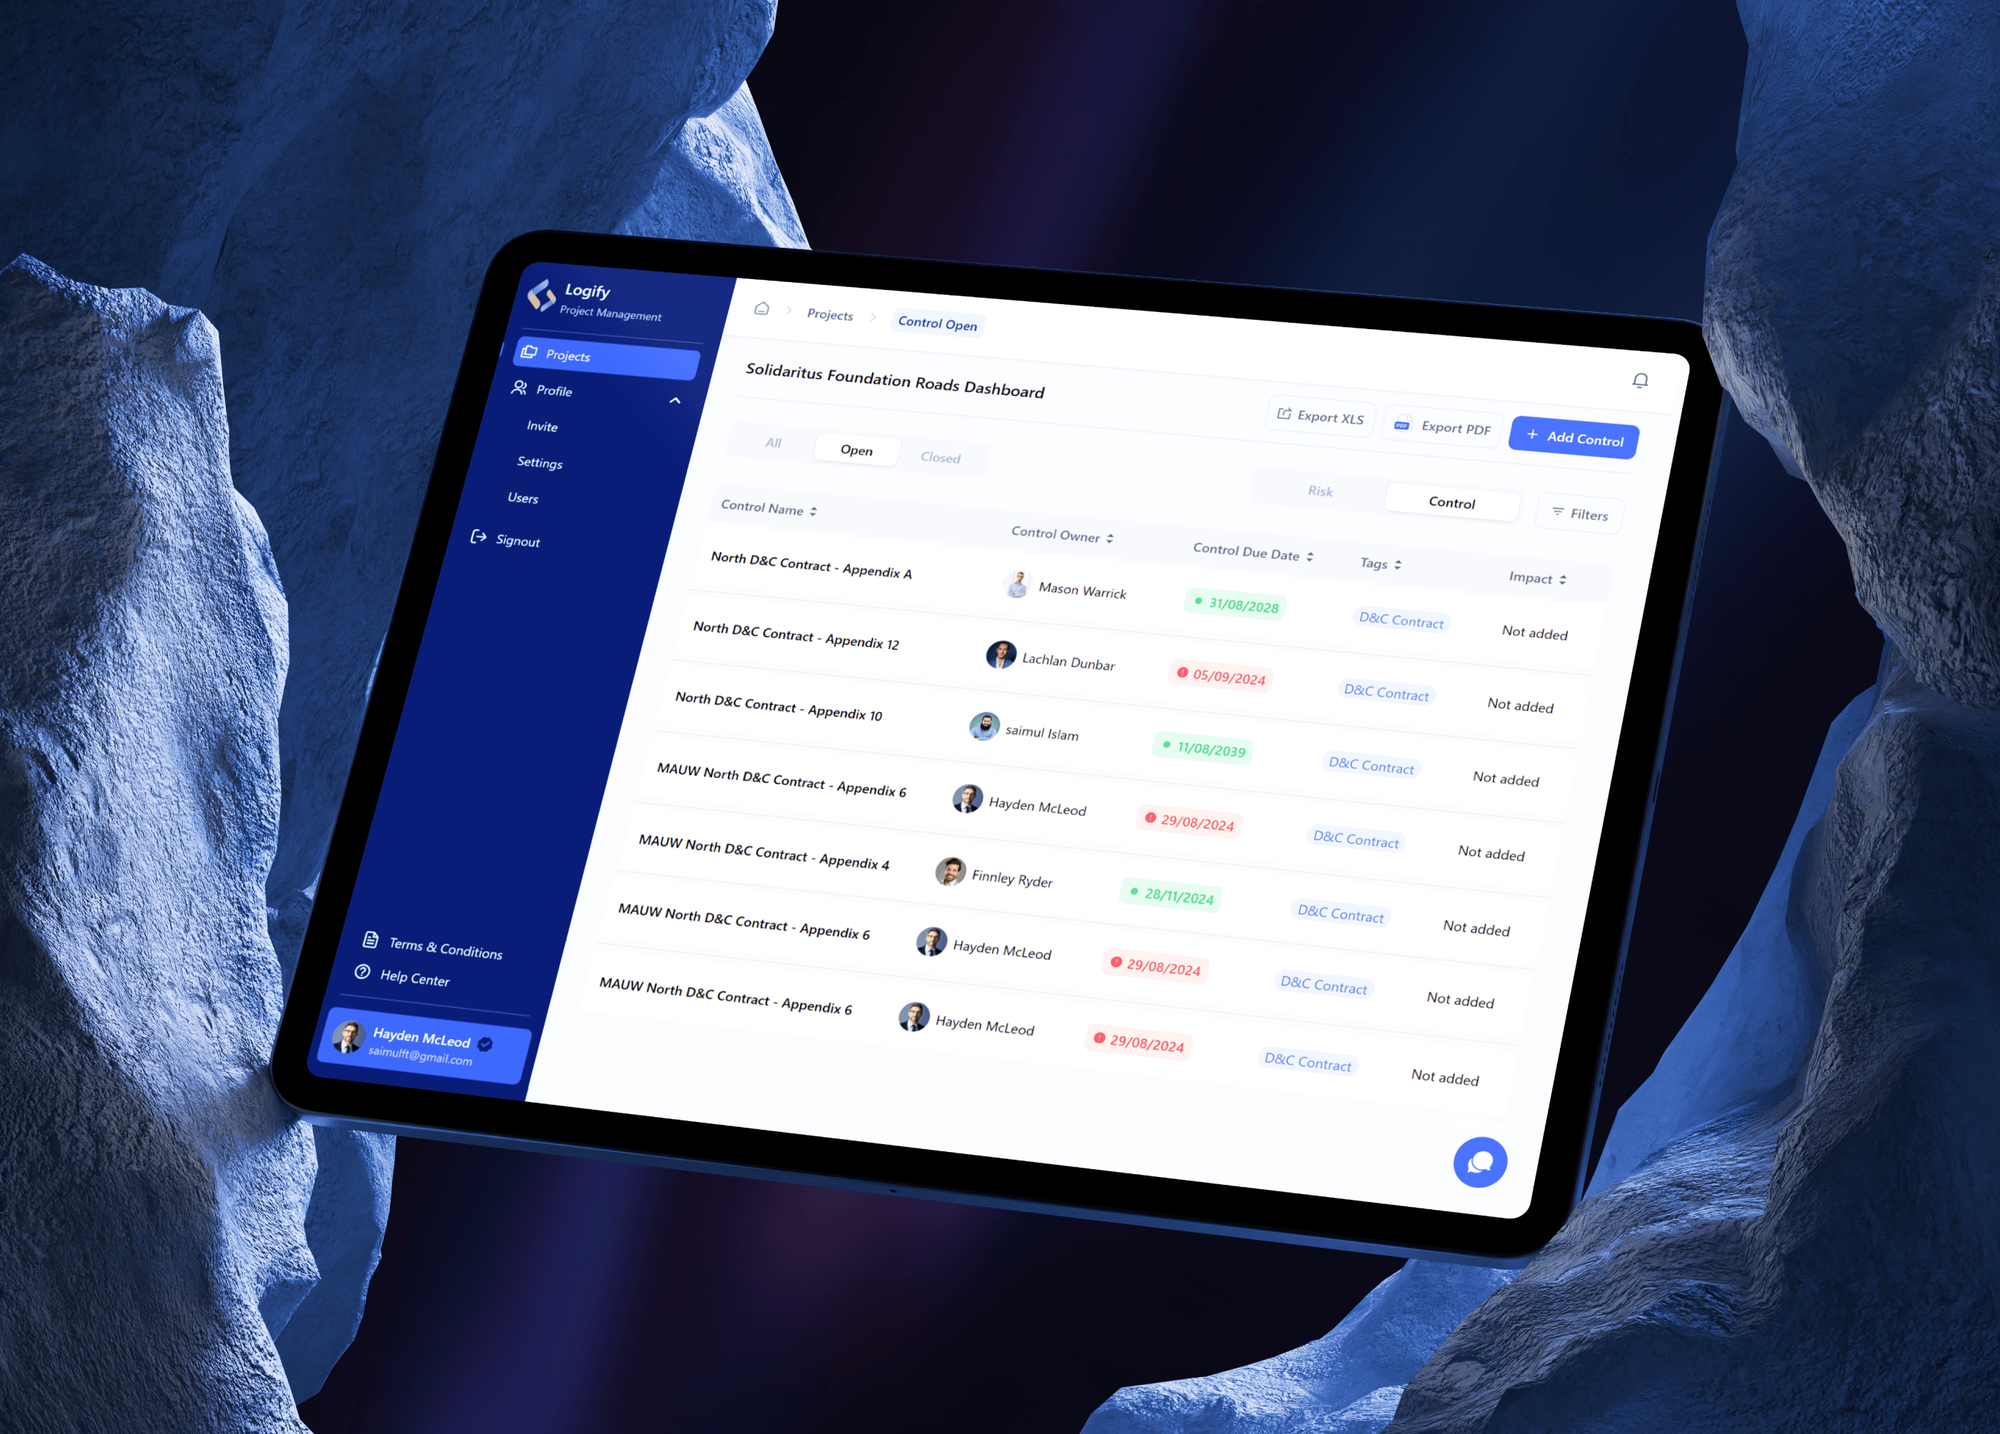
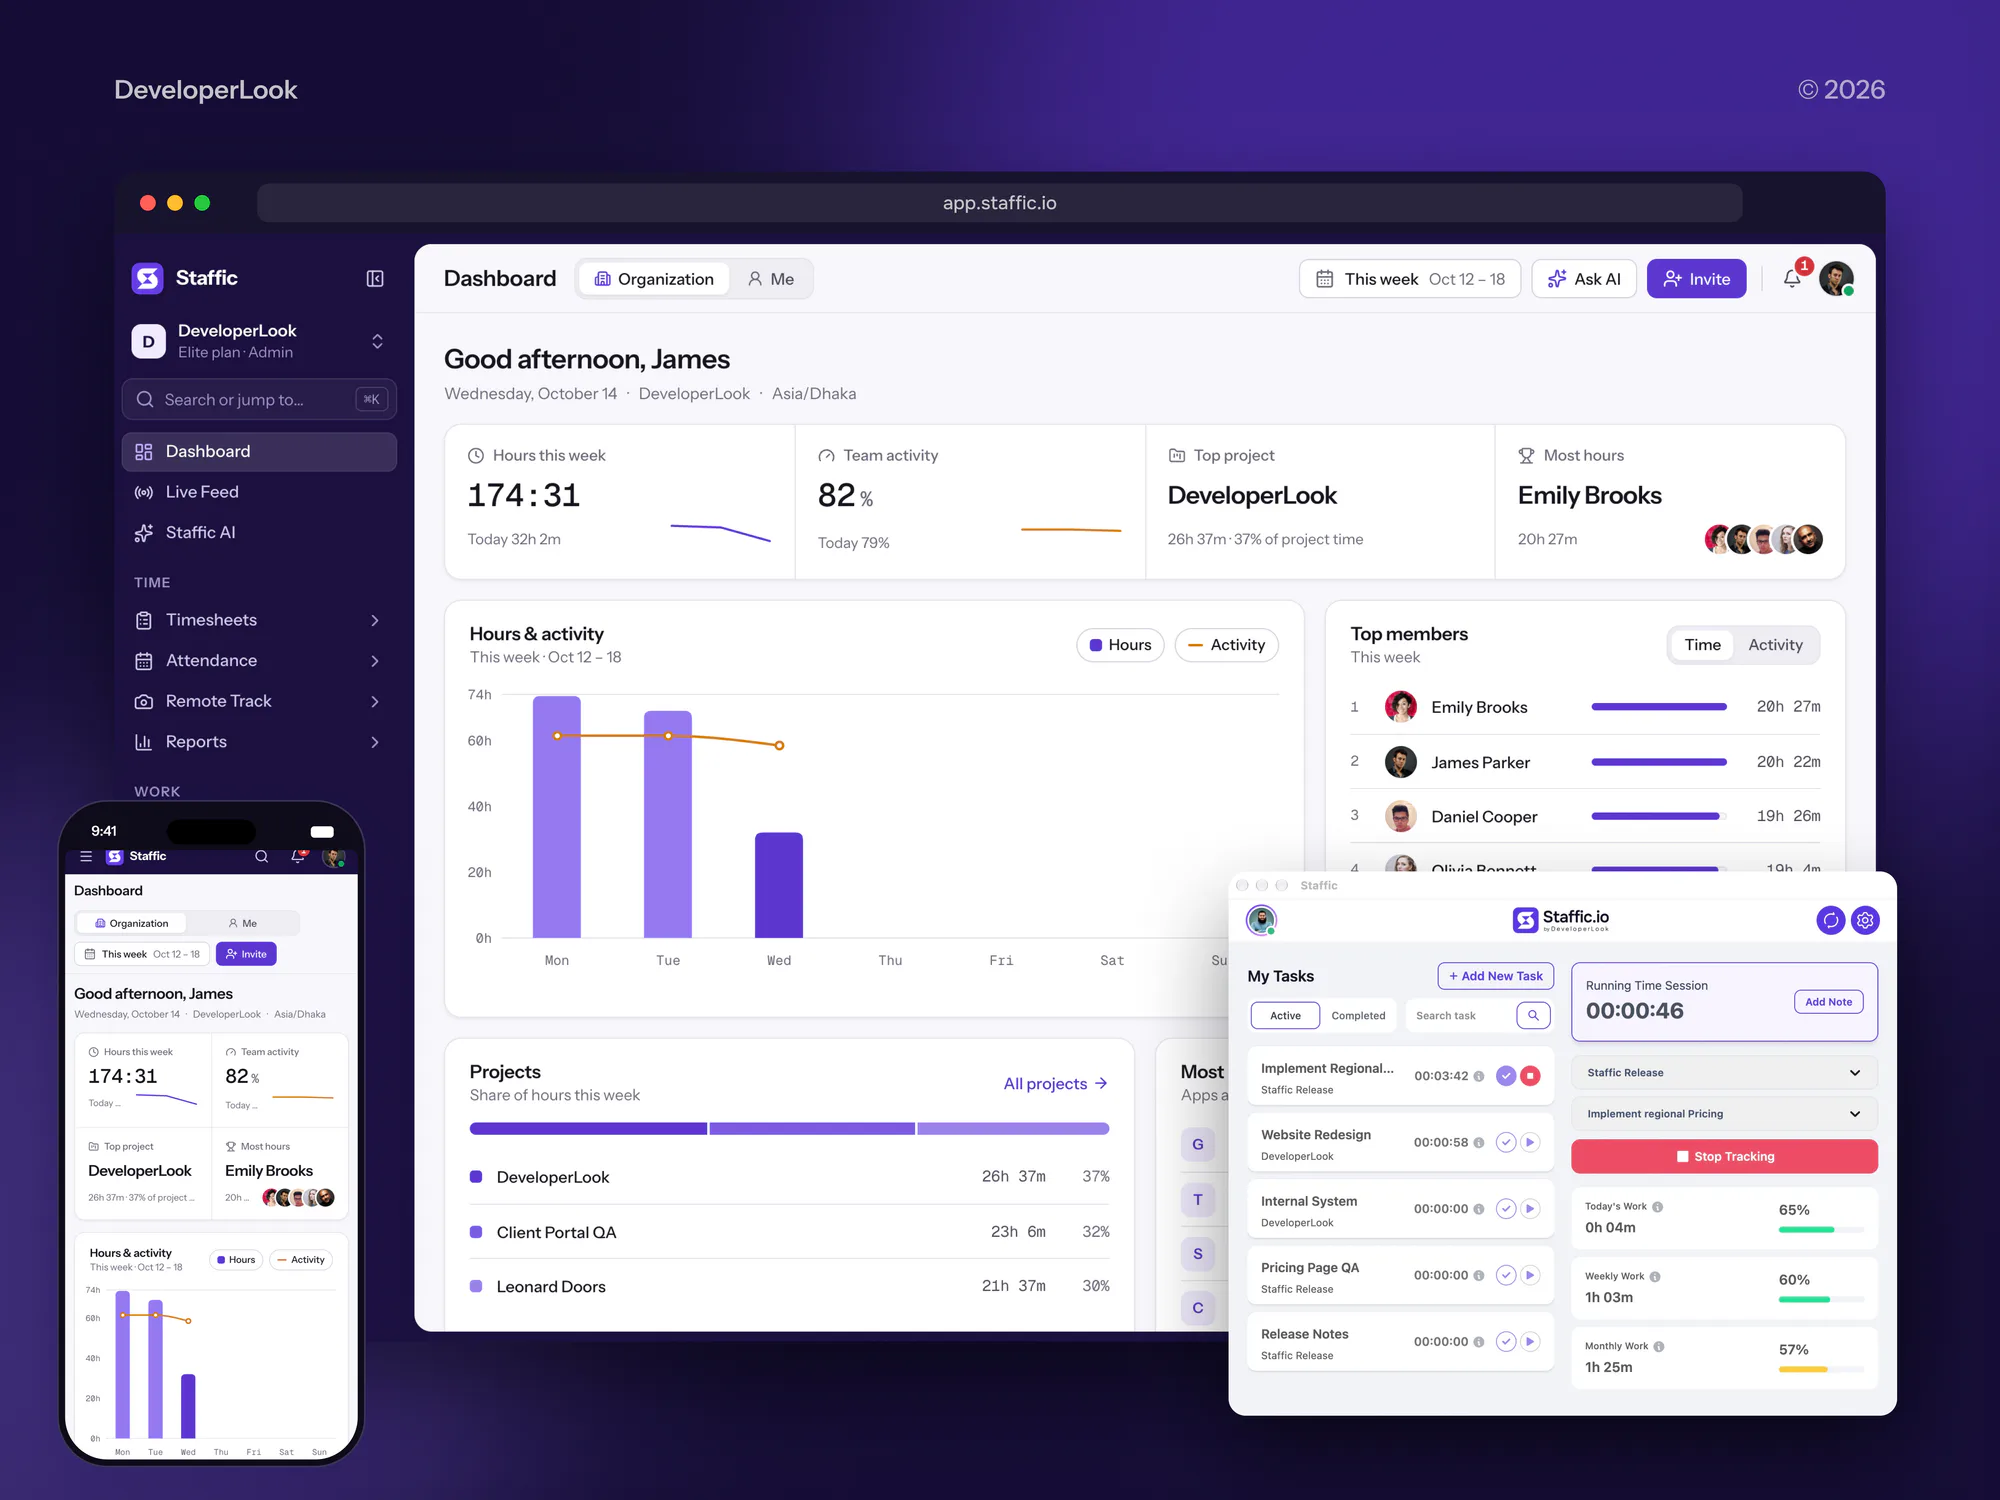
Project tracking, operations, and business platforms we designed and built. None are plant control systems, but each shows how we handle data and access.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
OT work happens next to machines that make product and keep people safe. These habits keep production running while the network gets safer.
We don't run active scans on your control network. Everything we learn comes from traffic your team captures, so fragile controllers see nothing new.
We write the rules and stay on call, but your controls team applies them. The people who know the line keep their hands on it.
Every change goes into a window you already planned. A security project should not be the reason a line stops.
Designs map to ISA/IEC 62443 and NIST SP 800-82 Rev. 3, not to one product. You can buy any firewall or monitoring tool and keep the design.
Some HMIs can't be patched without a vendor upgrade. We say so plainly and design compensating controls instead of pretending the risk is gone.
You get the scope and price before any traffic is captured. If you add a line or a plant, we quote it before the work starts.
Overview
DeveloperLook provides OT security for manufacturers whose plant networks grew one machine at a time. We build a passive asset inventory, draw the IT/OT boundary, design zones and conduits, lock down vendor remote access, and plan monitoring. Projects start at $1,100 and take 2 to 10 weeks, and changes near safety systems happen only with your engineers.
DEVELOPERLOOK
Project facts · OT Security Services
Reviewed 23 Oct 2026 by Saimul Islam
Good fit
Discrete manufacturers with flat networks
Your CNC machines, PLCs, and office PCs share one flat network, and a ransomware email in the office could reach the plant floor.
Process plants with aging HMIs
Your HMIs run Windows versions the vendor stopped patching, and replacing them means downtime you can't schedule this year.
Plants with many vendor connections
Your machine builders and integrators each left a remote access tool behind, and nobody knows which ones still work.
Defense and automotive suppliers
Your customer's security questionnaire now asks about manufacturing OT security, and you need an honest answer backed by a real assessment.
Integrators and IT providers serving plants
You support plant IT, and your client wants IT-OT security work done without anyone running scans on their control network.
Not a fit
Need a certified assessment
Your customer contract requires a report from an accredited ISA/IEC 62443 certification body. A certified assessment firm is the right choice for that.
Office network only
Your site has no control network to protect, and the gap is office Wi-Fi, firewalls, and laptops. Our network security services page covers that work.
Safety system changes
You need changes to safety instrumented systems or PLC logic. That belongs with your controls engineers or the system's integrator, not an outside security team.
Need DFARS paperwork first
Your main gap is DoD contract clauses, CUI handling, and incident reporting rather than the plant network. Our DFARS 252.204-7012 compliance page covers that.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the number of plants, lines, and vendor connections, and you get a fixed proposal after a free plant walkthrough.
For one plant that needs to know what's on its control network and how vendors reach it.
$1,100one-time, USD
For plants ready to split the network into zones, with your engineers making the changes.
$3,100one-time, USD
For manufacturers with up to 3 plants that need one security standard across every site.
$6,400one-time, USD
For Agencies
You own the plant relationship. We supply the passive assessment, zone design, and rule sets under your brand, while your engineers stay the ones on site. Your clients get plant security work without you hiring control system specialists.
White label: your client only ever sees your brand
Send the site list, network drawings, and the vendor connections your client knows about.
You get a capture guide for your technicians and a fixed price per plant.
We deliver the inventory, zone design, and rule sets for your team to apply.
Your technicians handle plant visits while we work behind your brand.
Inventory, maps, and rule sets delivered in your templates and branding.
PLC, HMI, and historian traffic read by people who know control networks.
Run a single plant first, then repeat the design across your client's sites.
The Right Technology for Your Project
These are the tools we use to read plant traffic and secure the boundary, chosen because none of them needs to touch a running controller.
 Python
FAQ
Straight answers on cost, timing, what OT means, the standards behind it, and how we work without touching production.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
DeveloperLook's OT work starts at $1,100 for a passive assessment of one plant. That covers the asset inventory, the IT/OT boundary map, and a remote access design. Zone and conduit design with firewall rule sets and a vendor gateway is $3,100. Programs for up to 3 plants with a monitoring design start at $6,400.
An assessment of one plant takes 2 to 3 weeks. That covers a few days of traffic capture, a week of analysis, and a review call with your controls lead. Zone design and firewall rules add 4 to 7 weeks, mostly spent waiting for planned downtime. Multi-plant programs run site by site, so the first plant is protected sooner.
OT cyber security protects control systems from digital attacks: ransomware spreading from office IT, misused vendor remote access, and unauthorized changes to PLC logic. It differs from IT security because availability and safety come first. A server can reboot at midnight, but a running line may only stop during planned downtime, so every control has to respect that.
In cyber security, OT is the category of systems that control physical equipment, kept apart from IT systems that handle business data. Teams treat it as its own domain because the devices are older, many protocols lack authentication, and patches need vendor approval. Many OT security companies lead with a monitoring platform, while we start with an assessment you own.
OT stands for operational technology. You'll also see ICS (industrial control systems) and SCADA used for parts of it, and people often write ICS/OT security for the whole field. IT/OT convergence describes the growing links between plant and office networks. Those links help reporting and remote support, and they're also how most attacks reach a plant floor.
Operational technology is the hardware and software that monitors and controls physical processes: PLCs, distributed control systems, HMIs, sensors, drives, robots, and historians. In a plant, it runs the presses, ovens, packaging lines, and chillers. OT equipment often stays in service for decades, which is why unsupported operating systems are still common on the plant floor.
The main standards are the ISA/IEC 62443 series, which defines zones, conduits, and security levels, and NIST SP 800-82 Rev. 3, NIST's guide to operational technology. Power utilities also follow NERC CIP. We map designs to 62443 and 800-82 but hold no 62443 certification, so a certified assessment needs an accredited certification body.
No. We use passive analysis only: your team mirrors a switch port, and we study the copied traffic offline, so controllers receive no probe traffic from us. Firewall changes come later, inside downtime you already planned. Your engineers apply them with a rollback step written for each rule, and we stay on the call while they do.
We replace scattered remote tools with one gateway. Each vendor gets a named account with MFA, access is approved per session, and every session is logged. OT security solutions such as jump hosts and vendor access platforms both work, so we design around what you already own. Old modems and forgotten remote boxes get listed so you can switch them off.
Usually not right away. Equipment the vendor no longer patches can often stay in service inside a tightly ruled zone with no internet path and few conduits. We flag each unsupported device, rate its exposure, and write compensating controls. Replacement then goes on your capital plan with a clear reason, instead of being forced on you mid-year.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.