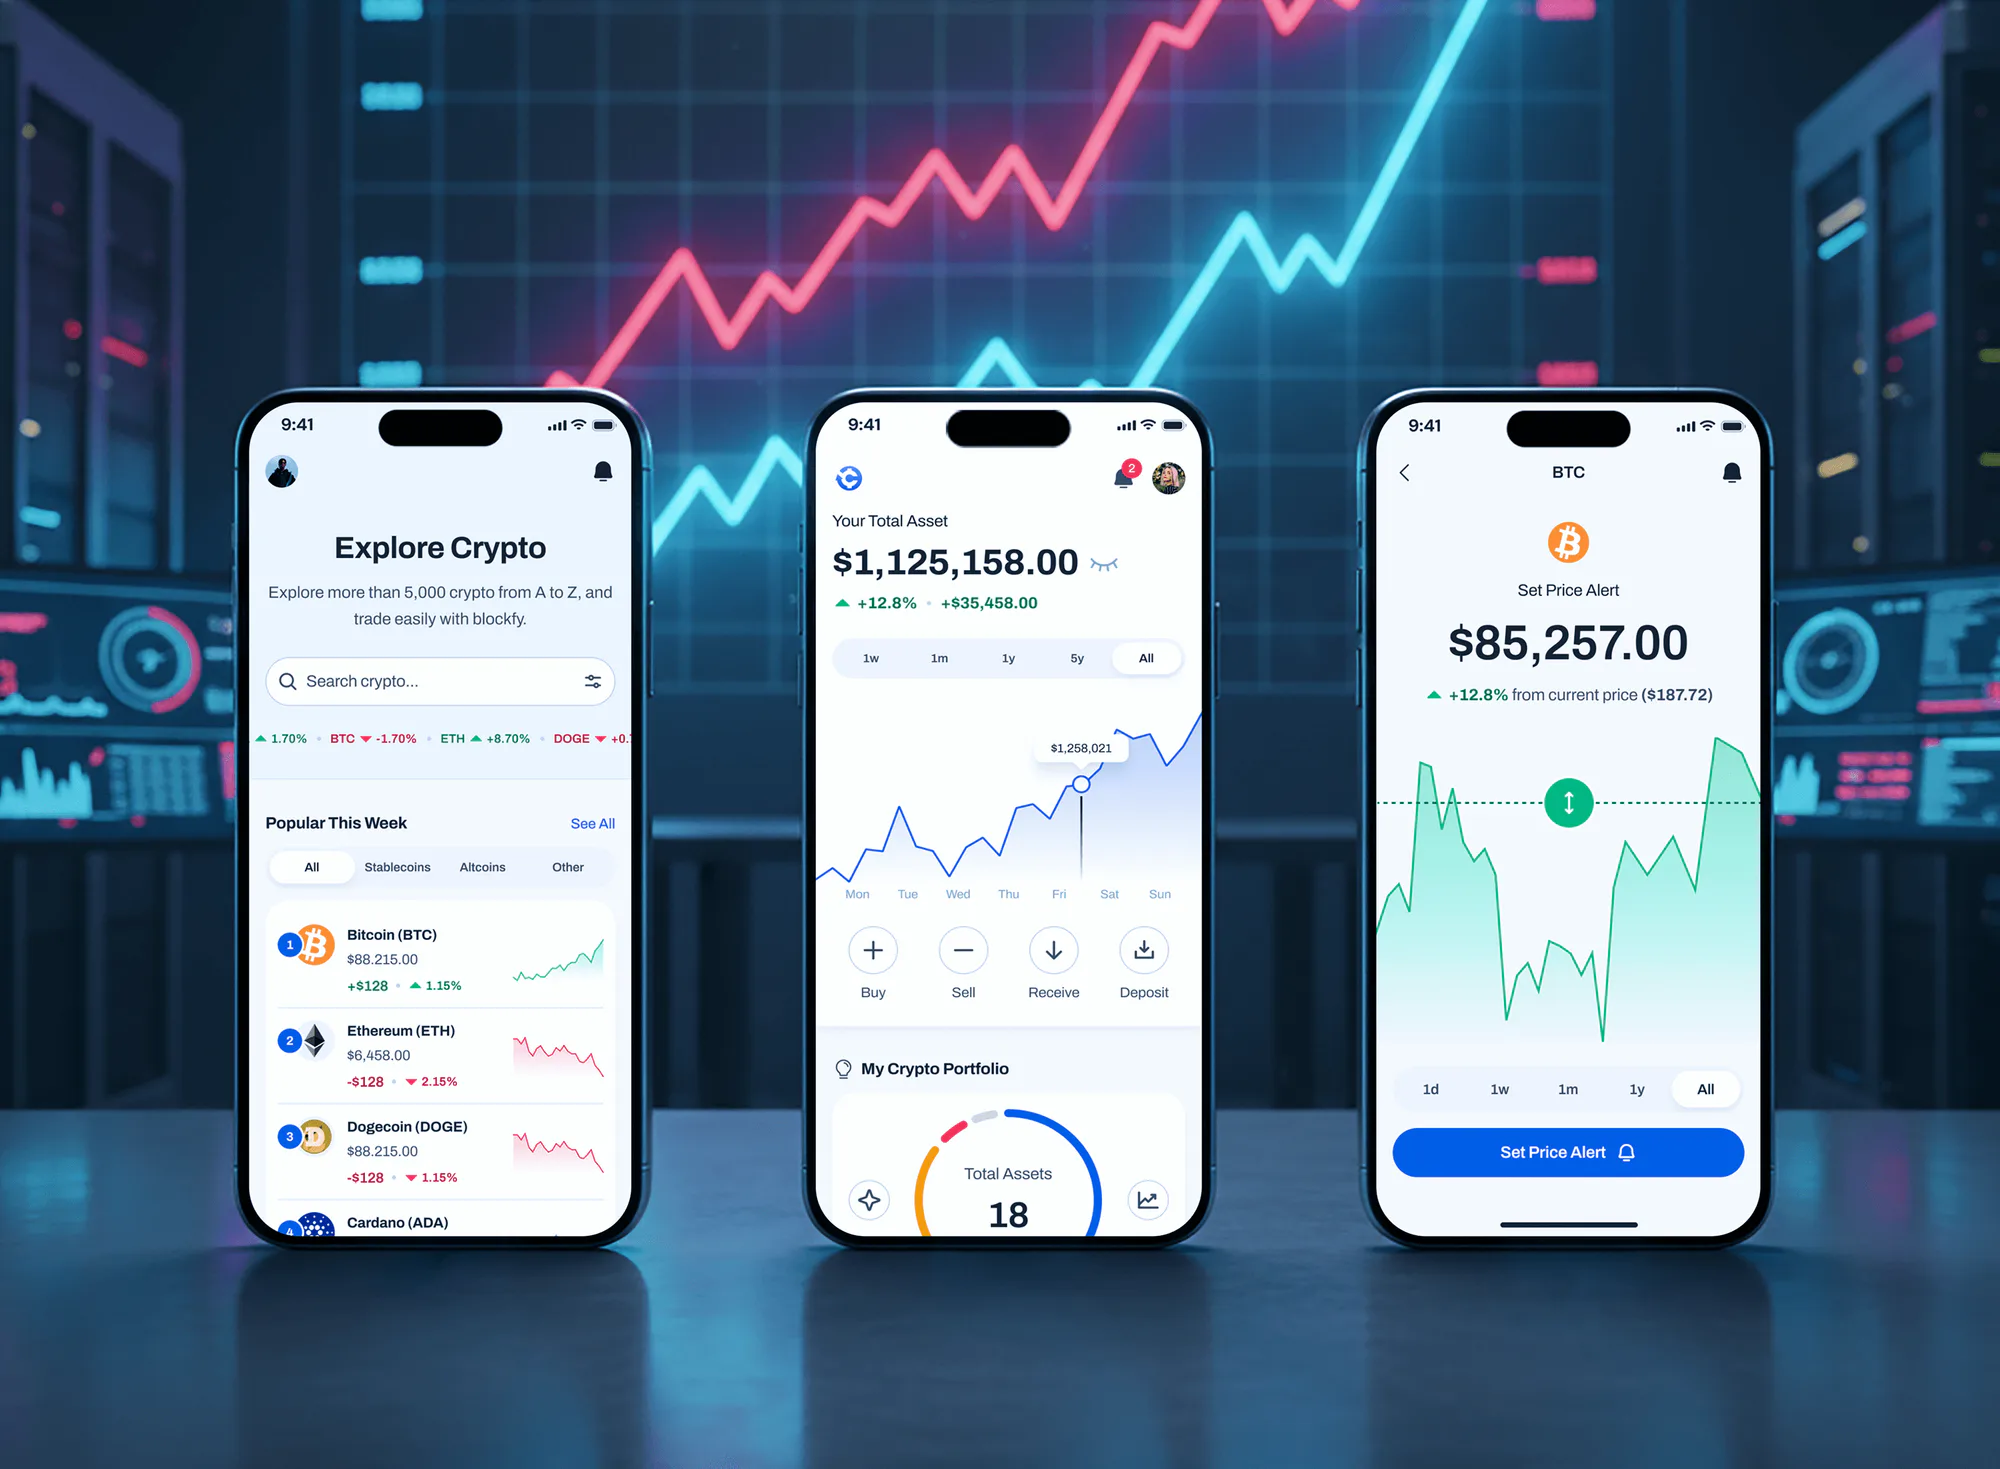
CoinSphere Crypto App Design & Development
- Crypto & NFT
- Dashboard
- Mobile App

For DeFi teams, exchanges, and wallet builders: your dApp front end, domains, signing flows, and keys audited, with findings ranked by funds at risk. From $1,400.
100%
Signing screens matched to calldata
1retest
After you fix findings
How your project runs
01 · FreeIndustry leaders we work with
 Cloudflare
 AWS
 Google Cloud
The Problem
The gap shows up the day a dependency update ships to your dApp or a registrar account gets phished. It also shows up when a signer approves a transaction the screen didn't explain.
Dependencies
One poisoned npm package could rewrite your connect button.
Dependencies
Dependencies are pinned, scanned, and served with integrity checks your build enforces.
Domain
The registrar login has no hardware key or lock.
Domain
Registrar and DNS accounts get hardware keys, registry lock, and change alerts.
Blind signing
Signers approve a hash they can't read.
Blind signing
Transactions are simulated and decoded on a separate device before anyone signs.
Leaked keys
An RPC key with write access sits in repo history.
Leaked keys
Secrets move to a vault, old keys are rotated, and repo history is scanned.
Your contracts went through a code audit, and the report sits on your docs site. Meanwhile, the dApp front end pulls in hundreds of npm packages, and any one of them could change what the connect button does. Your domain registrar login has no hardware key. 3 signers approve multisig transactions from personal laptops, reading a hash they can't verify. An RPC key with write access sits in your repo's history. Users wouldn't see any of it until their approvals emptied a wallet.
We start with the paths an attacker takes around your contracts, not through them. We review the front end's dependencies and build, lock down DNS and hosting, and check that every signing screen matches the calldata it sends. Then we look at how signers, deploy keys, and RPC credentials are handled day to day. You get findings ranked by how much money each one puts at risk, and a retest after your fixes. Contract code audits stay with a dedicated contract auditor.
Front-end supply chain reviewed
Dependencies, build pipeline, and script integrity checked so a poisoned package is harder to slip in.
Signing screens match calldata
Every wallet prompt checked so users see what a transaction really does before approving it.
Signer and key operations
Multisig thresholds, signer devices, and deploy keys reviewed against how your team really works.
Our Web3 Security Audit Services Process
You approve a scope that names every system we test, see findings as we confirm them, and decide which fixes ship before the retest.
We map where funds and keys live, from the front end and DNS to signers and cloud accounts. You get a written scope naming every system we'll test, with a fixed price. If you hold no user funds yet, we'll suggest waiting.
Projects We've Built
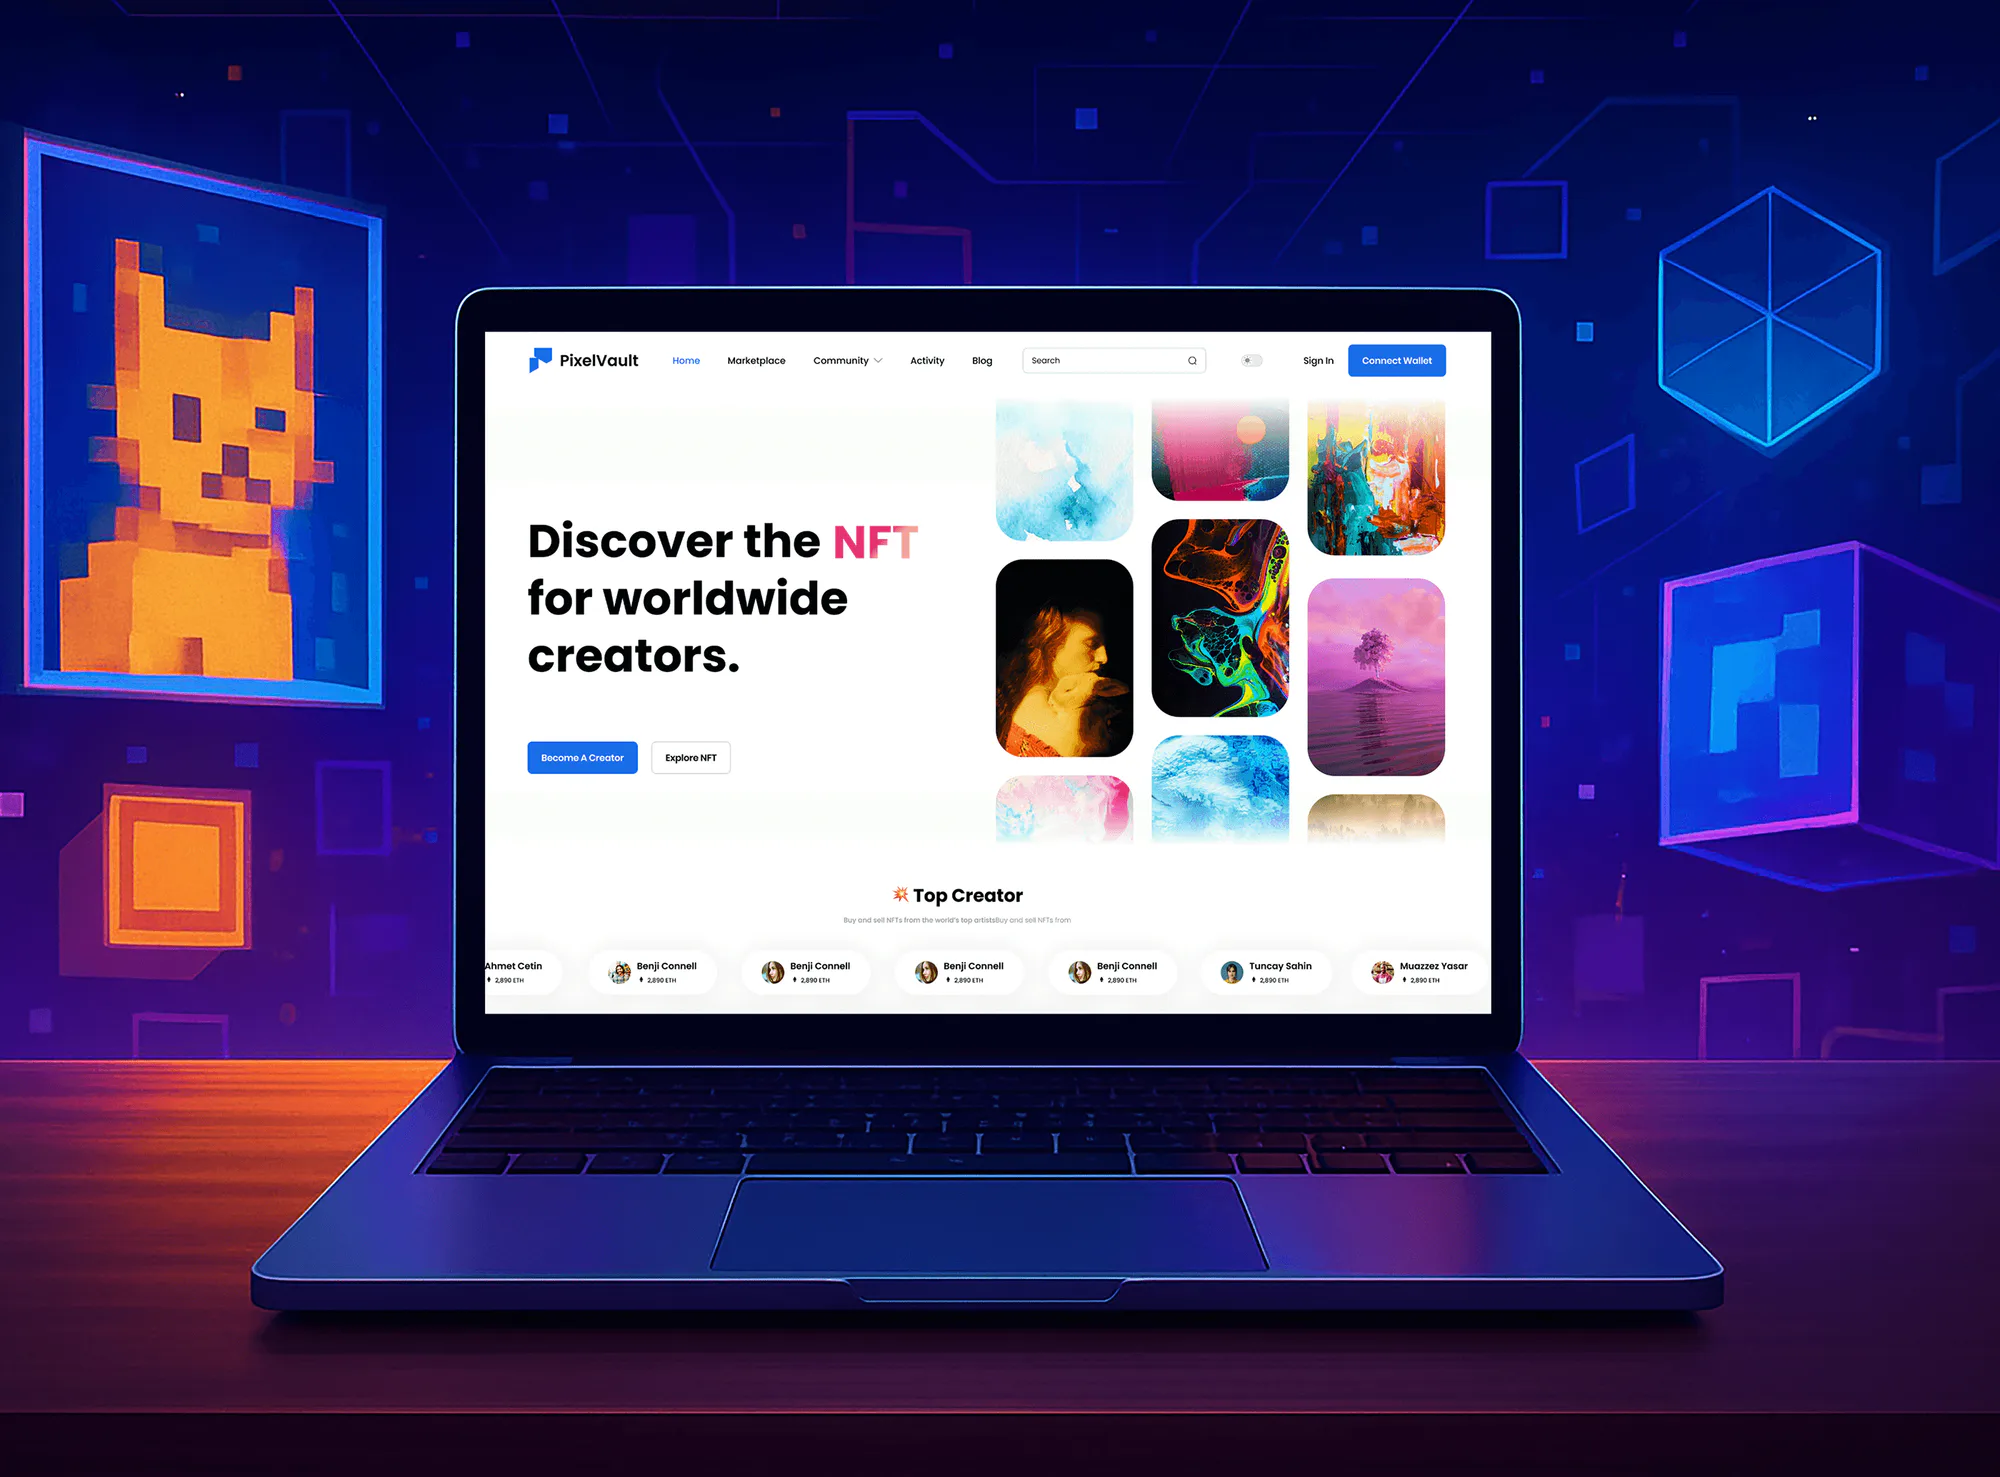
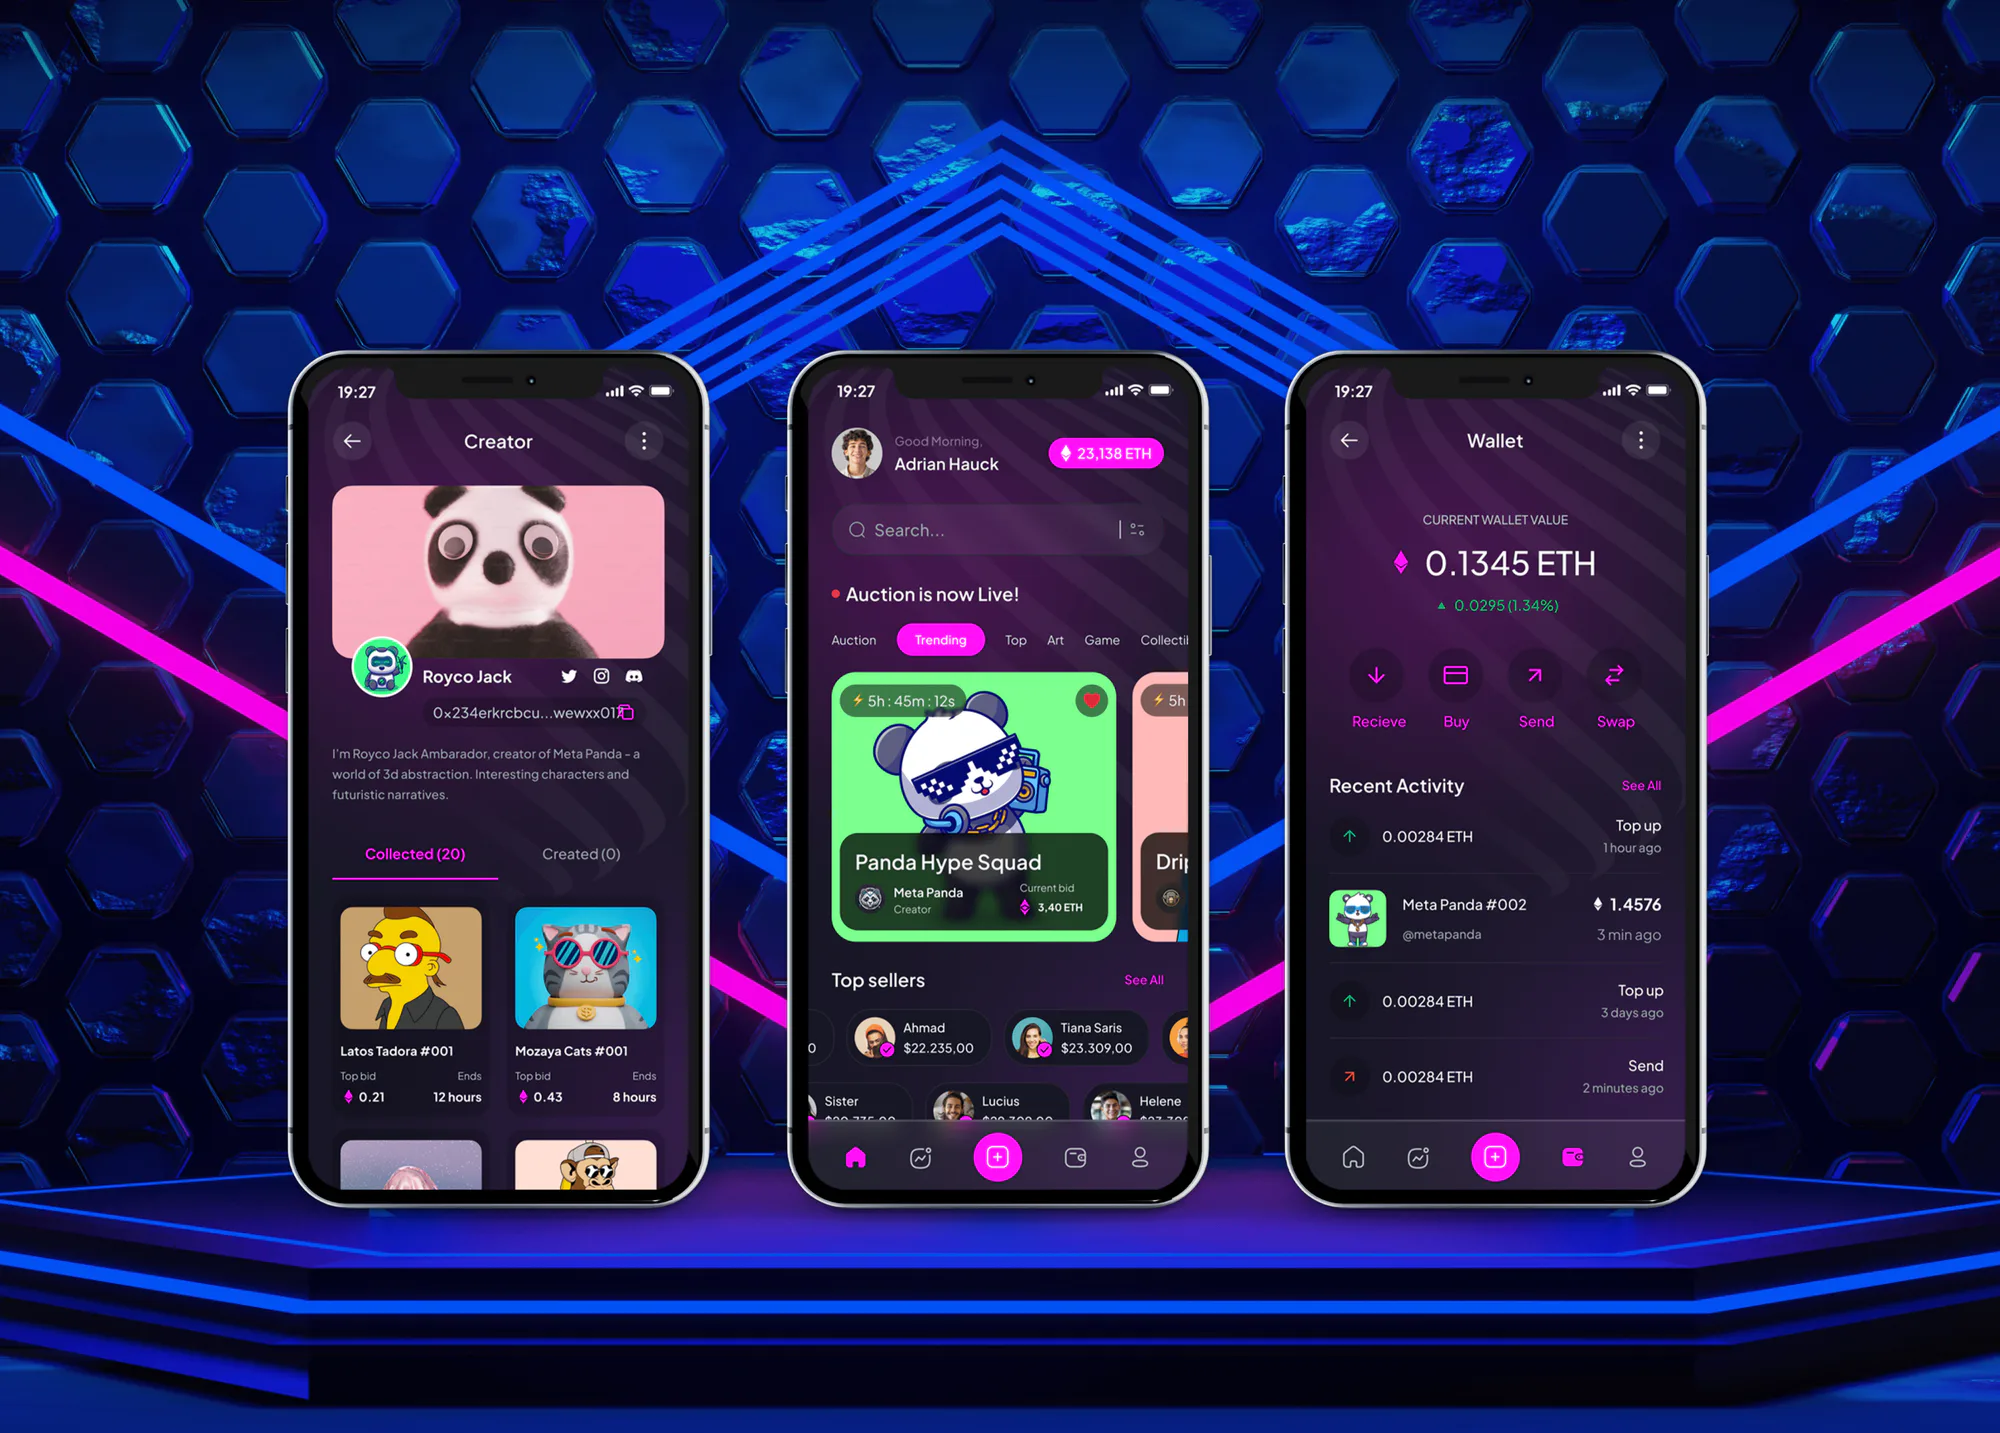
Crypto apps, NFT marketplaces, and trading dashboards we designed and built. They are the kind of front ends and signing flows this audit covers.
What's Included
The full scope covers the dApp front end, domains, signing flows, signer and key operations, and infrastructure. Exchange and custody reviews add wallet flows, withdrawals, and key ceremonies.
Compare Options
A contract auditor is the right call for Solidity code, and a bug bounty keeps eyes on a live product. This page covers the web3 security in between. Here is where each fits.
| Feature | DeveloperLookBest fit | Contract auditor | Bug bounty |
|---|---|---|---|
| Scope | Front end, keys, and infrastructure | Smart contract code | Whatever researchers choose to test |
| Contract code review | Left to a contract auditor | Line by line, their specialty | Paid only when bugs are found |
| Signing flows | Every prompt matched to calldata | Usually out of scope | Only if someone finds a flaw |
| Keys and signers | Multisig and deploy keys reviewed | Out of scope | Rarely tested |
| Retest | One retest included | Fix review included | Pay per valid report |
| Timing | Before launch or a big upgrade | Before contract deployment | Ongoing after launch |
| Report | Findings ranked by funds at risk | Severity-rated code findings | Separate researcher reports |
| Cost predictability | Fixed price from $1,400 | Quoted by code size | A bounty pool you fund |
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus
1,250+
Projects shipped
10+
Years of experience
5 stars
Clutch rating
5 stars
GoodFirms rating
Excellent
Trustpilot rating
Top 3%
Upwork Top Rated Plus

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Web3 security audit services work close to keys and funds. These habits keep our access read-only, our findings specific, and your signers in control of every transaction.
We test with read-only roles and test wallets you fund on testnets. Seed phrases and signer devices stay with you for the whole engagement.
Each finding says which funds or users it could expose, and how. You fix the expensive problems first, not the noisy ones.
An audit lowers risk, but it can't remove it. We say what we tested, what we didn't, and what still needs monitoring after launch.
We reproduce issues on testnets or mainnet forks, not with your live contracts. Nothing we do moves real funds or touches your production signers.
Contract code audits, custody licensing, and reserve attestations are named as out of scope. You know who covers each gap before work starts.
You get one fixed price for the systems named in the scope. A new chain or product is quoted before we look at it.
Overview
DeveloperLook provides web3 security audit services for the systems around your smart contracts. We audit the dApp front end and its dependencies, lock down domains and DNS, check signing prompts against calldata, and review signers, deploy keys, and cloud secrets. Audits start at $1,400 and take 1 to 7 weeks, with one retest included.
DEVELOPERLOOK
Project facts · Web3 Security Audit Services
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
DeFi teams with audited contracts
Your contracts passed a code audit, but nobody has reviewed the front end, DNS, and deploy keys that sit between users and those contracts.
Crypto exchanges and trading desks
You run hot and cold wallets for customers, and you need crypto exchange security reviewed beyond the matching engine itself.
Funds and treasuries holding digital assets
You hold digital assets for a fund or treasury, and you want institutional crypto asset security checked against how signers really approve transfers.
Wallet and crypto checkout builders
You ship a wallet or crypto checkout, and you need a crypto security audit of signing flows, keys, and APIs before launch.
Teams comparing security providers
You're comparing crypto security companies and want a written scope that names exactly which off-chain systems get tested.
Not a fit
Contract code review only
You only need Solidity reviewed line by line. Our Smart Contract Audit service covers contracts another team wrote. If we built your contracts, use another auditor so the review stays independent.
Need a wallet built
You need a self-custody wallet app built rather than audited. Our crypto wallet development page covers that build.
Need a license or attestation
You need a custody or money transmission license, or a proof of reserves attestation. That's work for counsel and an accounting firm; we review controls only.
Pre-launch, no user funds
You're pre-launch, hold no user funds, and have no admin keys yet. A dependency scanner and careful code review may be enough until you do.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on your systems, chains, and signer setup, and you get a fixed proposal after a free threat model call.
For Agencies
You own the Web3 client relationship. We supply the front-end, key, and infrastructure audit under your brand, while you keep the client contract and the credit. Your studio can offer off-chain security reviews without a security hire.
White label: your client only ever sees your brand
Share the client's dApp URL, repos, chains, and signer setup.
You get a scope naming every system and one fixed price.
We deliver findings and a retest report for you to present.
Share the client's dApp URL, repos, chains, and signer setup.
You get a scope naming every system and one fixed price.
We deliver findings and a retest report for you to present.
The Right Technology for Your Project
These are the tools we use to test the off-chain stack, plus the wallet, chain, and cloud systems most Web3 products run on.
CloudflareAWSGoogle CloudFAQ
Straight answers on web3 security, secure development, custody checks, crypto payments, cost, timing, and scope.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Web3 security is protecting everything a decentralized app depends on: contracts, keys, front end, domains, and infrastructure. Contracts get most of the attention, but many losses start off-chain. In February 2025, Bybit's signers approved a transfer through a tampered Safe{Wallet} interface, and the contracts did exactly what they were told.
Treat everything that can move funds as production code from day one. Pin and scan dependencies, keep deploy keys in hardware or a vault, put admin actions behind a multisig with a timelock, and test signing prompts against calldata. Get contract code audited separately, and plan monitoring before launch, because fixes after deployment are slow.
Our web3 security audit services start at $1,400 for one dApp front end, its domain and DNS, and its signing prompts, with one retest. Adding backends, RPC and cloud secrets, and multisig operations costs $3,700. Exchange and custody reviews with wallet flows, withdrawals, and key ceremonies start at $7,400.
A front-end and DNS audit takes 1 to 2 weeks. Adding backends, cloud secrets, and signer operations brings it to 3 to 5 weeks, and exchange or custody reviews take 4 to 7 weeks. The retest usually follows within a week of your fixes, so plan the audit before a launch date, not the week of it.
Ask for evidence, not promises. A custodian should share an independent SOC 2 Type II report or similar. It should also explain how keys are generated, split, and backed up, and how withdrawals are approved and limited. Proof of reserves shows assets, not controls. Our Exchange and Custody Review checks those controls for your operation or a provider you're choosing.
They can be, when the processor and the integration are set up carefully. Most risk sits in the integration: unverified webhooks, unconfirmed transactions treated as paid, and wallet keys stored on a web server. Use a processor that settles to your account, wait for confirmations, and verify every webhook signature. Our crypto payment gateway integration page covers that build.
A crypto exchange security review covers how customer assets move and who can move them. That means hot and cold wallet limits, withdrawal approvals and allowlists, key generation and backup ceremonies, staff access and offboarding, and alerts for unusual transfers. We test approval flows on staging and walk through a key compromise scenario with your team.
Compare written scopes, not marketing. Good crypto security companies name every system they will test, separate contract code from off-chain work, include a retest, and share a sample report. Be wary of anyone promising that funds can't be lost. Ask who actually performs the testing and how findings are ranked, since that decides what you fix first.
It's the set of controls a fund, treasury, or company needs before holding digital assets at scale. Think signer quorums, separation of duties, hardware or MPC key storage, written transfer policies, and regular access reviews. The goal is that no single person, laptop, or vendor can move assets alone. Our top plan reviews those controls against daily practice.
No, contract code review is a separate audit by a dedicated contract auditor. We cover everything around the contracts: front end, domains, signing flows, keys, and infrastructure. Many teams run both before launch, and our findings often point the contract auditor at admin functions worth a closer look. After handover you get 30 days of support.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.