Audit report with ratings
Findings rated high, medium, or low, each with the criterion, the evidence, and a recommended fix.

For companies facing a customer audit, SOC 2, or ISO 27001: your controls tested with real samples, findings rated, and a checklist you keep. From $1,100.
25 to 60
Controls tested with samples
1
Reusable audit checklist
How your project runs
01 · FreeTeams we have built for:














The Problem
Policies get written for a customer or an insurer, then nobody checks whether daily practice matches. The gap stays invisible until an auditor or an attacker finds it.
Leavers
Former staff still have access weeks after leaving.
Leavers
We sample leavers and trace every account against HR end dates.
Encryption
The policy says encrypted laptops, but some aren't.
Encryption
We check encryption status on a sample of devices in your device manager.
Changes
Production changes go live with no ticket or approval.
Changes
We match recent changes to tickets and approvals, then list the gaps.
Evidence
Proof is scattered across inboxes when auditors ask.
Evidence
You get an evidence index that maps every control to its proof.
Your access policy says leavers lose access on their last day. Your laptop standard says every device is encrypted. Your backup plan says restores are tested each quarter. They read well, but nobody has tested them since they were written. Then a customer's auditor asks for proof, picks 5 leavers at random, and finds 2 still active in the CRM. The policies weren't wrong. Practice drifted, and nobody was checking.
We audit the way external auditors do, before they arrive. We write testable criteria from your policies and chosen framework, pull samples from real records, and test whether each control is designed well and actually works. Every finding comes with evidence, a rating, and an owner who signs off on the fix. Your next audit finds a tested program, not a set of good intentions.
Tested against written criteria
Each control is checked against a criterion from your policy or framework, not opinion.
Sampled from real records
We test real leavers, laptops, backups, and changes, picked the way auditors pick samples.
Findings with named owners
Every finding gets a rating, a management response, and a named owner with a date.
Our Cybersecurity Audit Process
You approve the criteria and sample plan, upload evidence once, see findings as they are confirmed, and add your responses before the report is final.
We agree why you need the audit, such as a customer review or SOC 2 prep, and the criteria we'll use. You get a scope, a sample plan, and a fixed price. If an internal checklist would do, we'll tell you before we quote.
What's Included
Every plan ends with a report your auditors and customers can read. Larger plans test more controls and add the follow-up work.
Compare Options
An internal checklist is cheap, and a certification auditor issues the report your customers need. Here is what each does and where a readiness audit fits.
| Feature | DeveloperLookBest fit | Internal checklist | Certification auditor |
|---|---|---|---|
| Planning | Criteria and sample plan first | Whatever the template lists | Formal audit plan and scope |
| Independence | Outside team with no stake | Your team grades itself | Independent, licensed or accredited |
| Control testing | Design and practice, with samples | Yes or no answers | Sampled testing by set rules |
| Report you can show | Readiness report, not certification | Internal notes only | SOC 2 report or ISO certificate |
| Fix help | Fixes on the remediation plan | Up to your team | No, independence rules prevent it |
| Timing | 2 to 12 weeks | Whenever you have time | Booked ahead for set audit periods |
| Cost | From $1,100, fixed price | Free apart from staff time | Higher, set by the firm |
| Best moment | Before the formal audit | Between audits | When you're ready to certify |
Projects We've Built
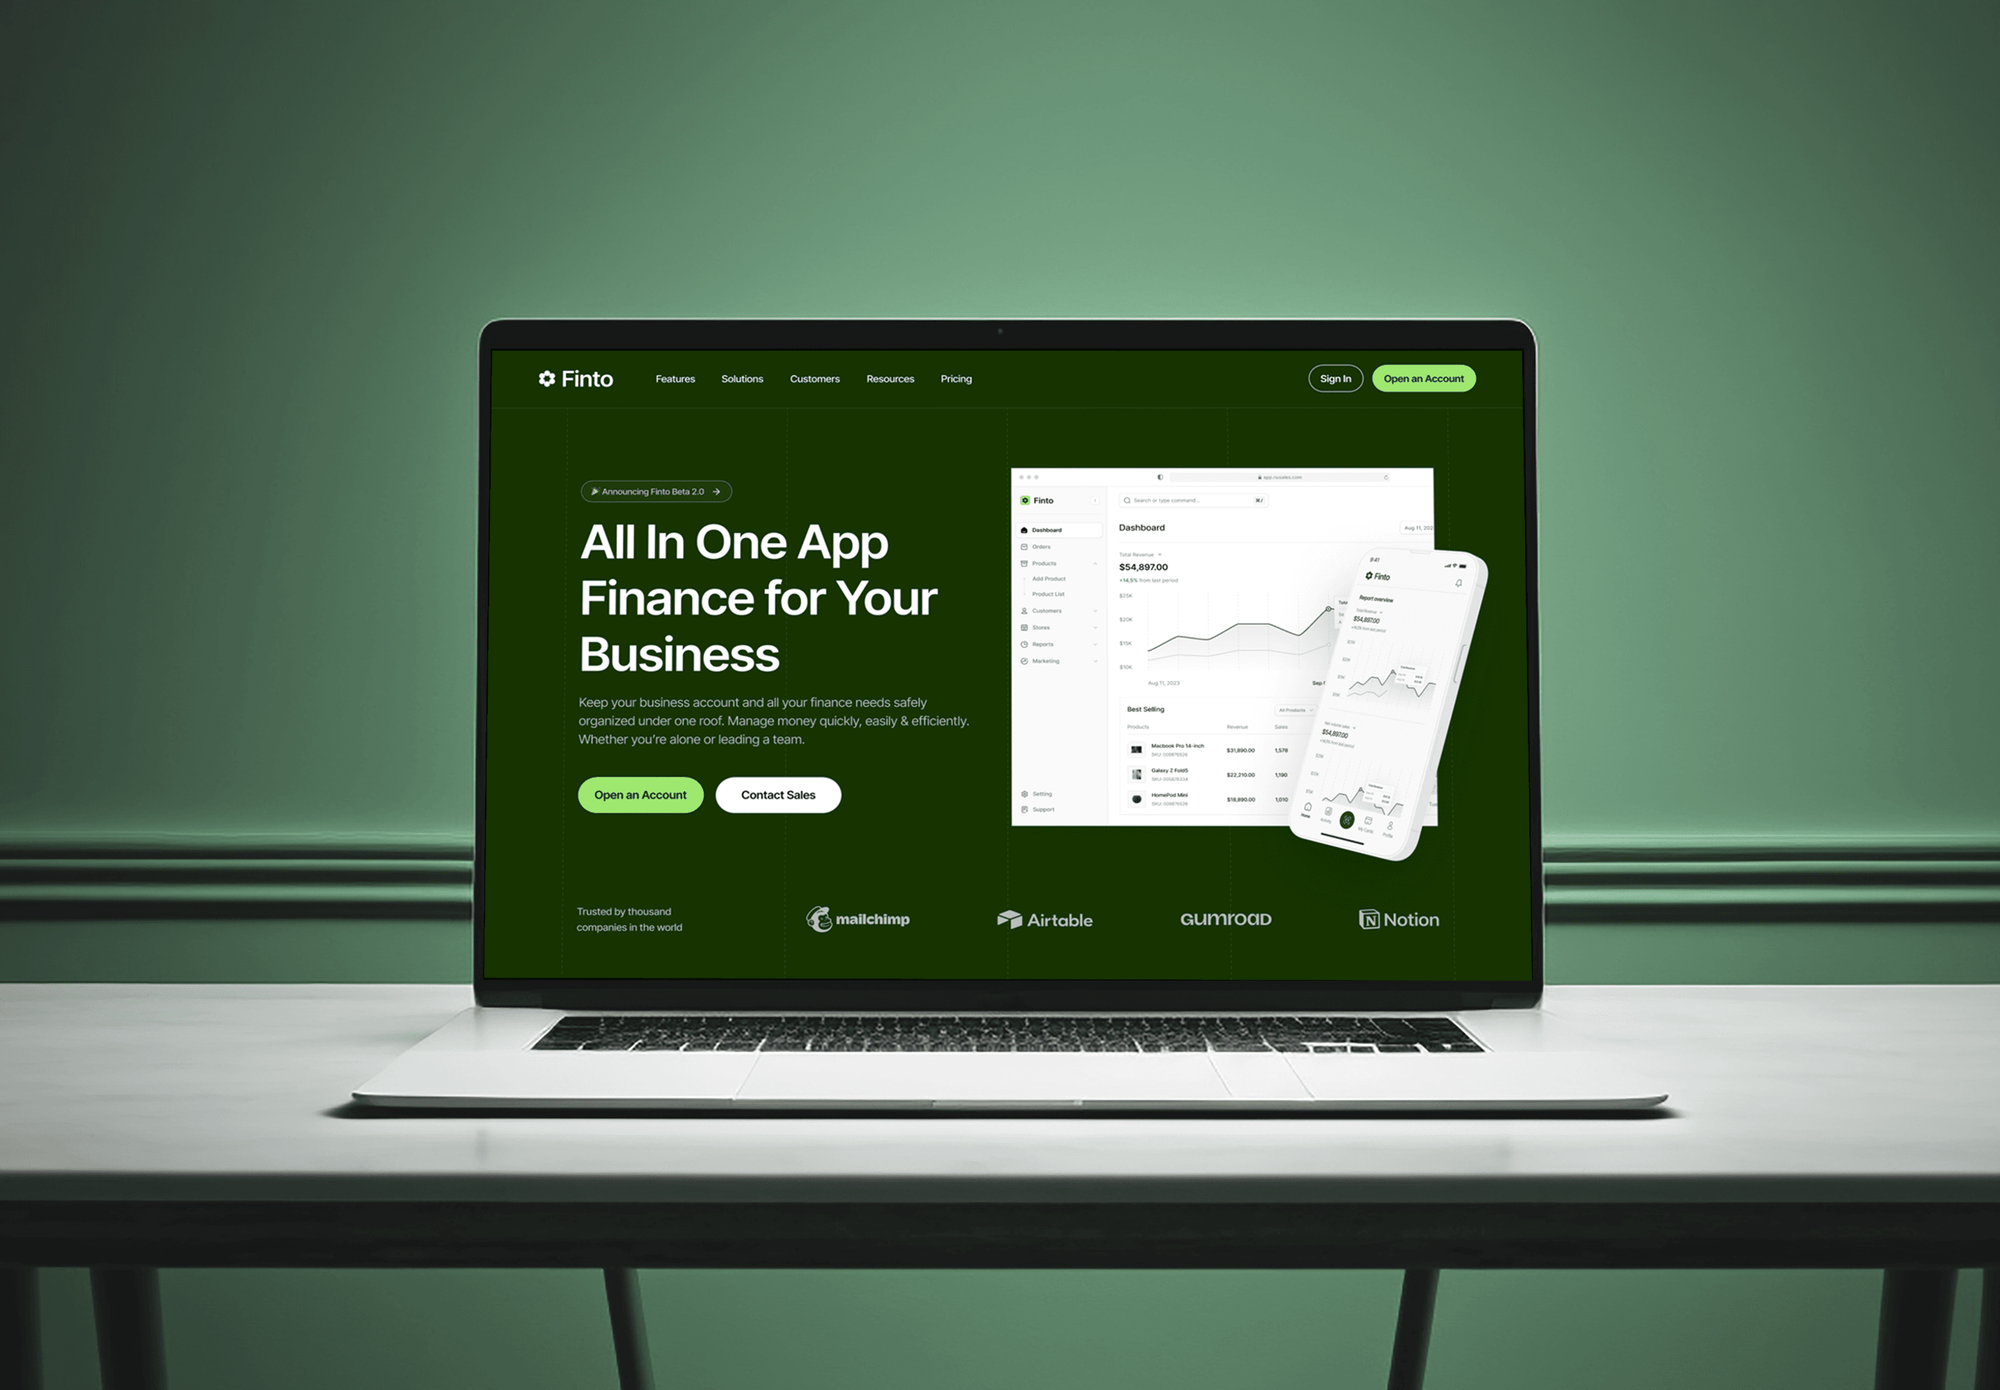
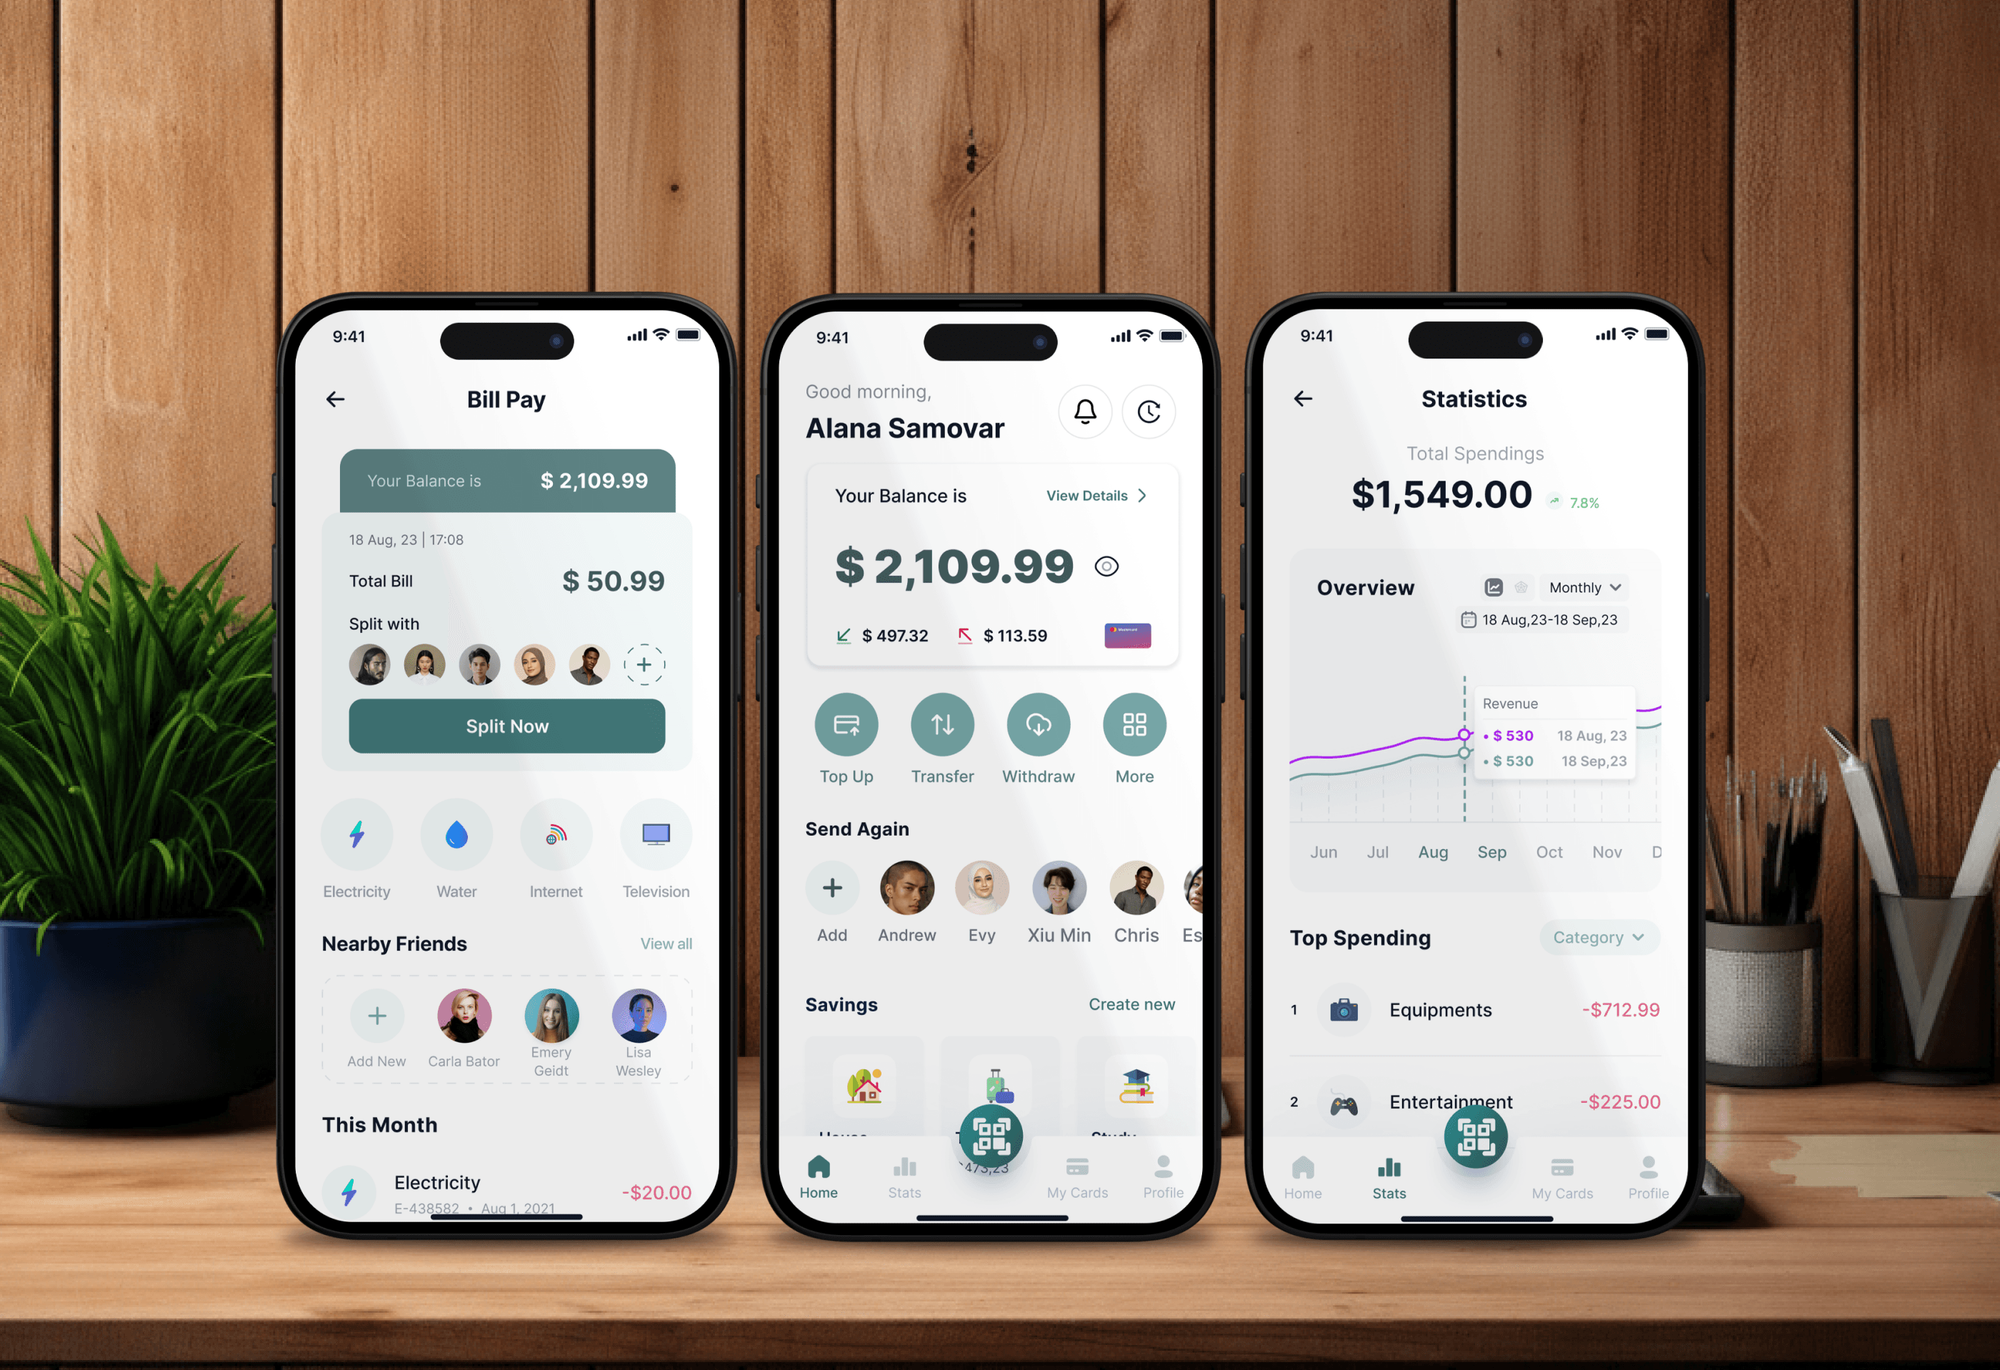
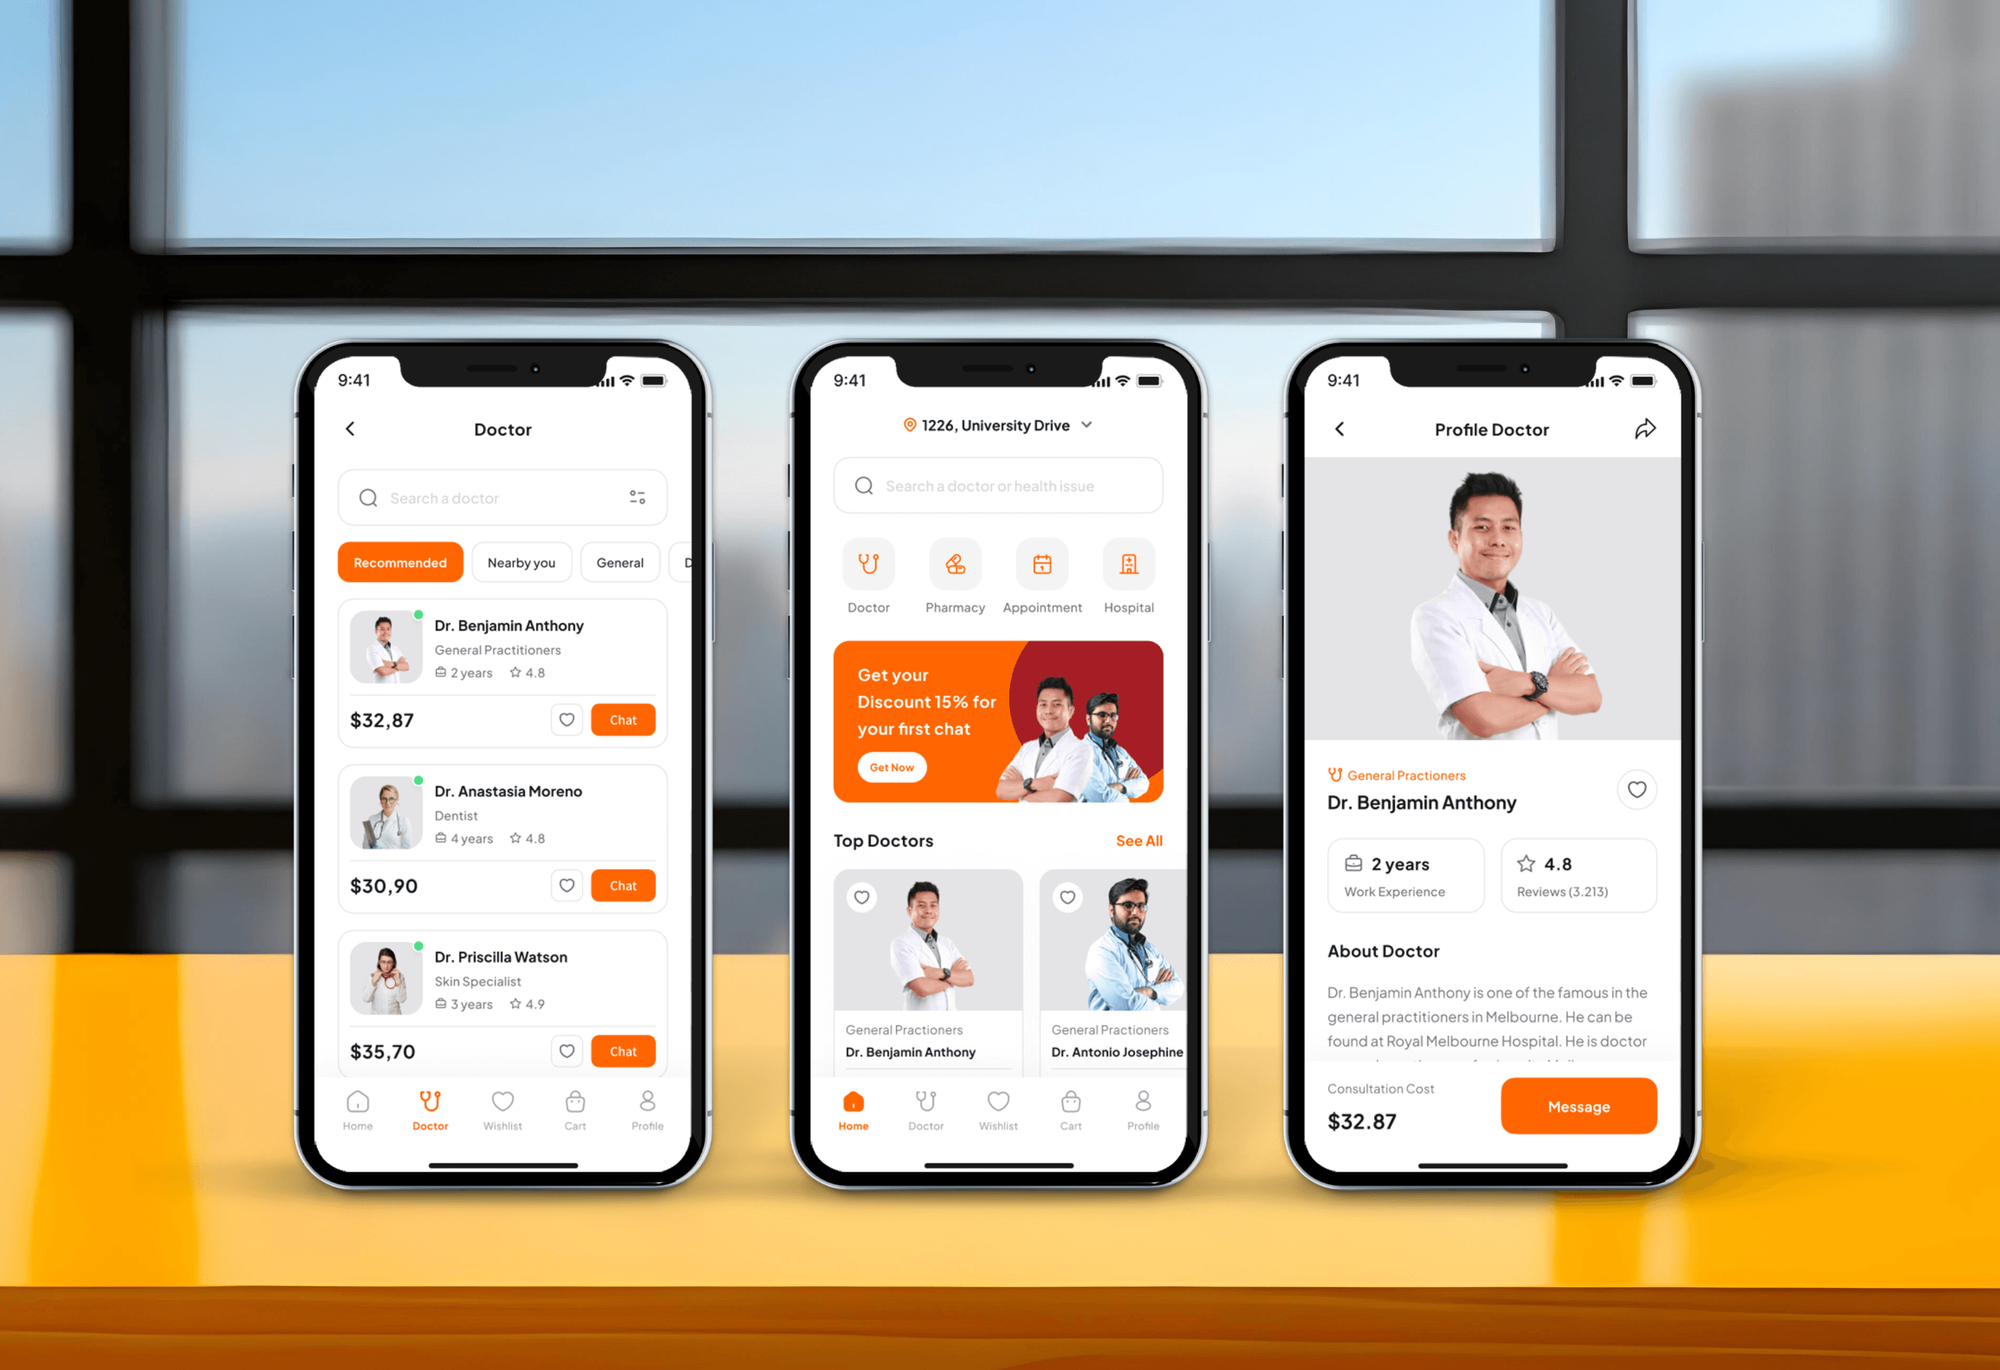
Finance and healthcare apps we built for clients, the kind of systems customers and regulators audit. They are build projects, not audits.
What Our Clients Say
Feedback from teams we have built finance, health, and business apps for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
We test the way an external auditor would, report the way a colleague would, and stay clear about what our report is and isn't.
We agree what passing means for each control before testing starts. That stops arguments about findings later and keeps the audit fair.
We test real records: leavers, devices, backups, and changes picked by a set method. A finding backed by samples is hard to dispute and easy to fix.
Our report is a readiness audit, not a SOC 2 report or an ISO certificate. We say so on the cover, so nobody shows it to a customer as one.
You see each finding as we confirm it, not all at once at the end. Owners can start fixing while testing continues.
Our engineers can configure the controls they test, on the remediation plan. You get practical fixes, not just a list of failures.
The checklist, test steps, and evidence index stay with you. Next year's audit, or your own internal one, starts from a proven method.
Overview
DeveloperLook provides cybersecurity audit services for companies preparing for customer audits, SOC 2, or ISO/IEC 27001. We test up to 60 controls against written criteria with real samples, rate every finding, and give you a reusable checklist. Audits start at $1,100, take 2 to 6 weeks, and prepare you for the formal audit without replacing it.
DEVELOPERLOOK
Project facts · Cybersecurity Audit Services
Reviewed 27 Oct 2026 by Saimul Islam
Good fit
Startups facing their first SOC 2
Your startup has a SOC 2 audit booked, and you want a cybersecurity compliance audit first to find failures while they're cheap to fix.
Companies with an ISO 27001 target
You're preparing for ISO/IEC 27001 certification and need internal audit evidence before the certification body's Stage 2 audit.
Boards asking for independent proof
Your board wants proof that security policies are followed in Microsoft 365 or Google Workspace and AWS or Azure, tested by an outside team.
Teams facing customer audit rights
Your largest customer can audit you under contract, and you want information security audit services to test your controls before their team does.
Agencies and MSPs
You manage IT for clients who ask for yearly audits, and you want IT security audit services delivered under your brand.
Not a fit
SOC 2 report needed
You need the SOC 2 report your customers ask for. Only a licensed CPA firm can issue it; our SOC 2 Compliance Services page prepares you for that audit.
Website-only security check
You only need your website or online store checked. Our Website Security Audit Services page covers site scans, plugins, and admin access.
Need a maturity baseline
You want a broad 0 to 5 score for each security area, not control testing. Our Cybersecurity Assessment Services page is the better first step.
No written policies yet
You have no security policies to audit against yet, or a budget under $1,100. Start with our Information Security Policy Development page, then audit.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the number of controls, samples, and systems in scope, and you get a fixed proposal after a free planning call.
For Agencies
You own the client relationship. We plan the criteria, test the samples, and write the findings under your brand, so you can offer yearly audits without hiring an auditor. Your team presents the report and quotes the fixes.
White label: your client only ever sees your brand
Share the client's goal, framework, and deadline, and we confirm controls, samples, and price.
We request evidence and test samples under your name, with your team copied.
You present the branded report, and we join the readout when asked.
Share the client's goal, framework, and deadline, and we confirm controls, samples, and price.
We request evidence and test samples under your name, with your team copied.
You present the branded report, and we join the readout when asked.
The Right Technology for Your Project
We pull evidence from the identity, device, cloud, and ticketing tools you already use, and test it against the criteria your auditors will apply.
 AWS
 Google Sheets
 Loom
Related Services
An audit tests what you have. These services set a baseline, score business risk, prepare you for SOC 2, write missing policies, and check your website.
This page
Cybersecurity Audit Services
Pairs with the 6 services around it
FAQ
Straight answers on what an audit tests, its purpose, cost, timing, and what it can and can't certify.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
A cybersecurity audit is a formal check of whether your security controls meet set criteria and work in practice. Auditors test controls with evidence and samples, such as user lists and device reports, and rate each failure. Unlike a broad assessment, it gives a pass or fail view against a standard.
Its purpose is to prove, with evidence, that your security controls work as your policies and customers expect. It finds gaps before an attacker, a customer's auditor, or a certification body does. It also gives leaders an independent view instead of the IT team's own report.
Cybersecurity audit services from DeveloperLook start at $1,100 for a Focused Audit of up to 25 controls. The Full Audit is $2,750 and tests up to 60 controls against SOC 2, ISO/IEC 27001, or your policies. Audit and Remediation is $5,450 and adds up to 20 hours of fixes and a 90-day follow-up audit.
A Focused Audit takes 2 to 3 weeks, and a Full Audit takes 4 to 6 weeks, from planning call to report. Audit and Remediation runs 8 to 12 weeks, with the follow-up audit at 90 days. Evidence requests are the usual bottleneck, so one upload list keeps dates on track.
In cybersecurity, a security audit tests your controls against a standard such as SOC 2 criteria, ISO/IEC 27001 Annex A, or your own policies. It covers access, devices, data, backups, logging, and change management. Security audit services differ from a penetration test, which tries to break in instead.
An IT audit checks whether your technology controls are designed well and running as intended. It usually covers access, change management, backups, and operations: the general IT controls auditors rely on. A cybersecurity audit is the security-focused part of that work, with deeper tests on identity and devices.
Start with the criteria your buyers care about, usually SOC 2, and audit only the systems that hold customer data. For a startup we test identity, laptops, code changes in GitHub, cloud access, and backups with small samples. Then fix the high findings before your auditor's observation period starts.
Check 3 things: who issues what, how they test, and what you keep. Only a licensed CPA firm can issue a SOC 2 report, and only an accredited body can certify ISO/IEC 27001. Cyber security audit companies that prepare you should test with samples and hand over their method.
No. Our readiness audit tests your controls and prepares you for the formal audit. Only a licensed CPA firm issues a SOC 2 report, and only an accredited certification body issues ISO/IEC 27001 certificates. Many teams use our cybersecurity compliance audit as a dry run before the formal one.
After the report you get 30 days of email support and a findings list with owners and dates. Your team can fix them, or we can on the Audit and Remediation plan, followed by a retest at 90 days. Keep the checklist: it makes next year's audit faster.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.