
Incident response program
Written steps to detect, respond to, and recover from unauthorized access to customer information.

For independent and small RIAs that need the amended Regulation S-P in place: an incident program, customer notice steps, vendor oversight, and safer logins. From $650.
30days
Customer notice deadline mapped
100%
Vendors checked for notice terms
How your project runs
Teams we have built for:














The Problem
The gap shows up when a mailbox is compromised, a vendor has a breach, or an SEC exam request asks for the program the amended rule now requires.
01 · Incident program
The firm has a privacy policy but no incident plan.
A written program covers detection, response, recovery, and who leads each step.
02 · Customer notice
Nobody knows which clients to notify, or by when.
A notice procedure maps sensitive data to clients and the 30-day deadline.
03 · Vendor terms
Vendor contracts say nothing about telling you of a breach.
Oversight steps require notice within 72 hours and track each vendor's reply.
04 · Mailbox rules
A compromised mailbox forwarded client email for a week.
MFA and forwarding alerts on every mailbox catch silent rule changes.
Your firm uses a custodian portal, a CRM, planning software, and Microsoft 365, and each one holds account numbers and Social Security numbers. Last month an assistant's mailbox quietly forwarded every email to an outside address for a week. Nobody knew whether that counted as an incident under the amended rule, which clients had to be told, or by when. Your vendor contracts say nothing about telling you of a breach. And the SEC exam request list asks for your written incident response program by Friday.
We start with the Regulation S-P requirements and your actual setup: every system and vendor that holds customer information. Then we write an incident response program your team can run. It includes a notice procedure built around the 30-day deadline and vendor terms that require notice within 72 hours. On the top plan, we also fix the safeguards behind it: MFA, email security, and managed devices. Your CCO gets a program that works on an ordinary Tuesday, not only during an exam.
Incident program written
Detect, respond, and recover steps written for your firm, with a named lead for each.
Customer notice ready
A notice procedure and letter template built around the 30-day deadline.
Vendors held to 72 hours
Custodian, CRM, and planning tool terms checked for breach notice within 72 hours.
Our Cybersecurity for Financial Advisors and RIAs Process
You approve the scope, review the gap list with your CCO, and sign off every document before it becomes part of your compliance manual.
We ask about your AUM, custodians, CRM, planning tools, and who handles compliance today. You get a written scope and a fixed price. If your compliance consultant's program already covers the amended rule, we'll tell you before we quote.
What's Included
The full scope covers the incident response program, customer notice, vendor oversight, records, and the technical safeguards behind them for firms that want those fixed too.
Compare Options
A compliance consultant handles filings and mock exams well, and an IT provider fixes devices quickly. Here is where each fits the amended rule.
| Feature | DeveloperLookBest fit | Compliance consultant | IT provider |
|---|---|---|---|
| Policy writing | Written around your real systems | Strong policy templates | Not included |
| Vendor oversight | Contracts checked for 72-hour notice | Vendor questionnaire | Not included |
| Incident response | Program plus a practice run | Program document | Technical cleanup afterward |
| Technical safeguards | MFA, DMARC, and devices set up | Recommended, not configured | Configured on request |
| Exam support | Documents mapped to the rule | Mock exams and filing help | Not included |
| Speed | 1 to 6 weeks, fixed scope | Often part of a retainer | Quick for single fixes |
| Ownership | Every document in your files | Templates under their license | Settings in your tenant |
| Cost predictability | Fixed price from $650 | Monthly retainer | Hourly or per device |
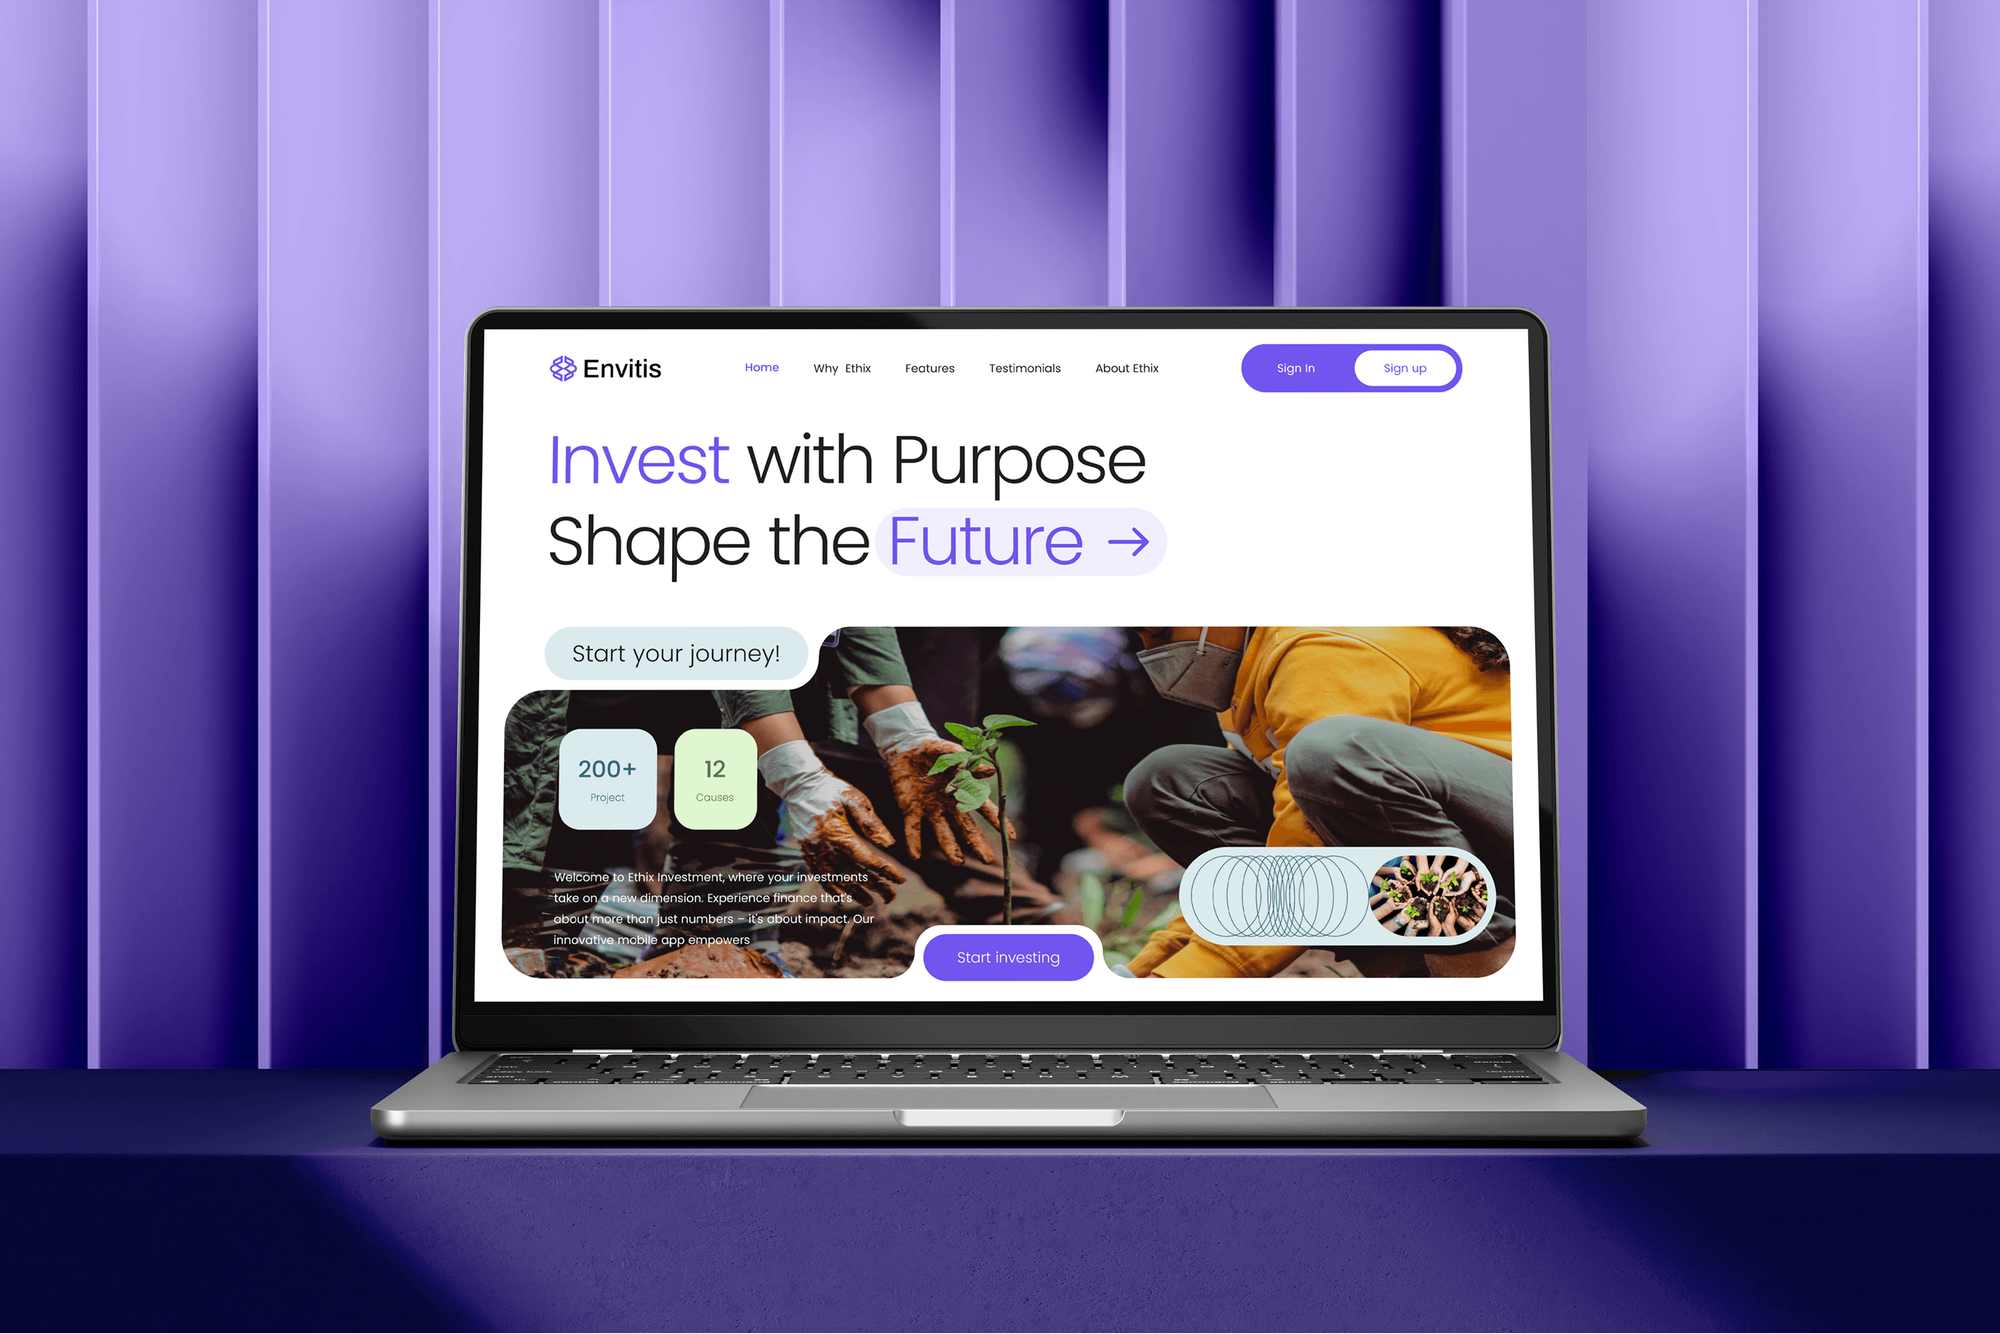
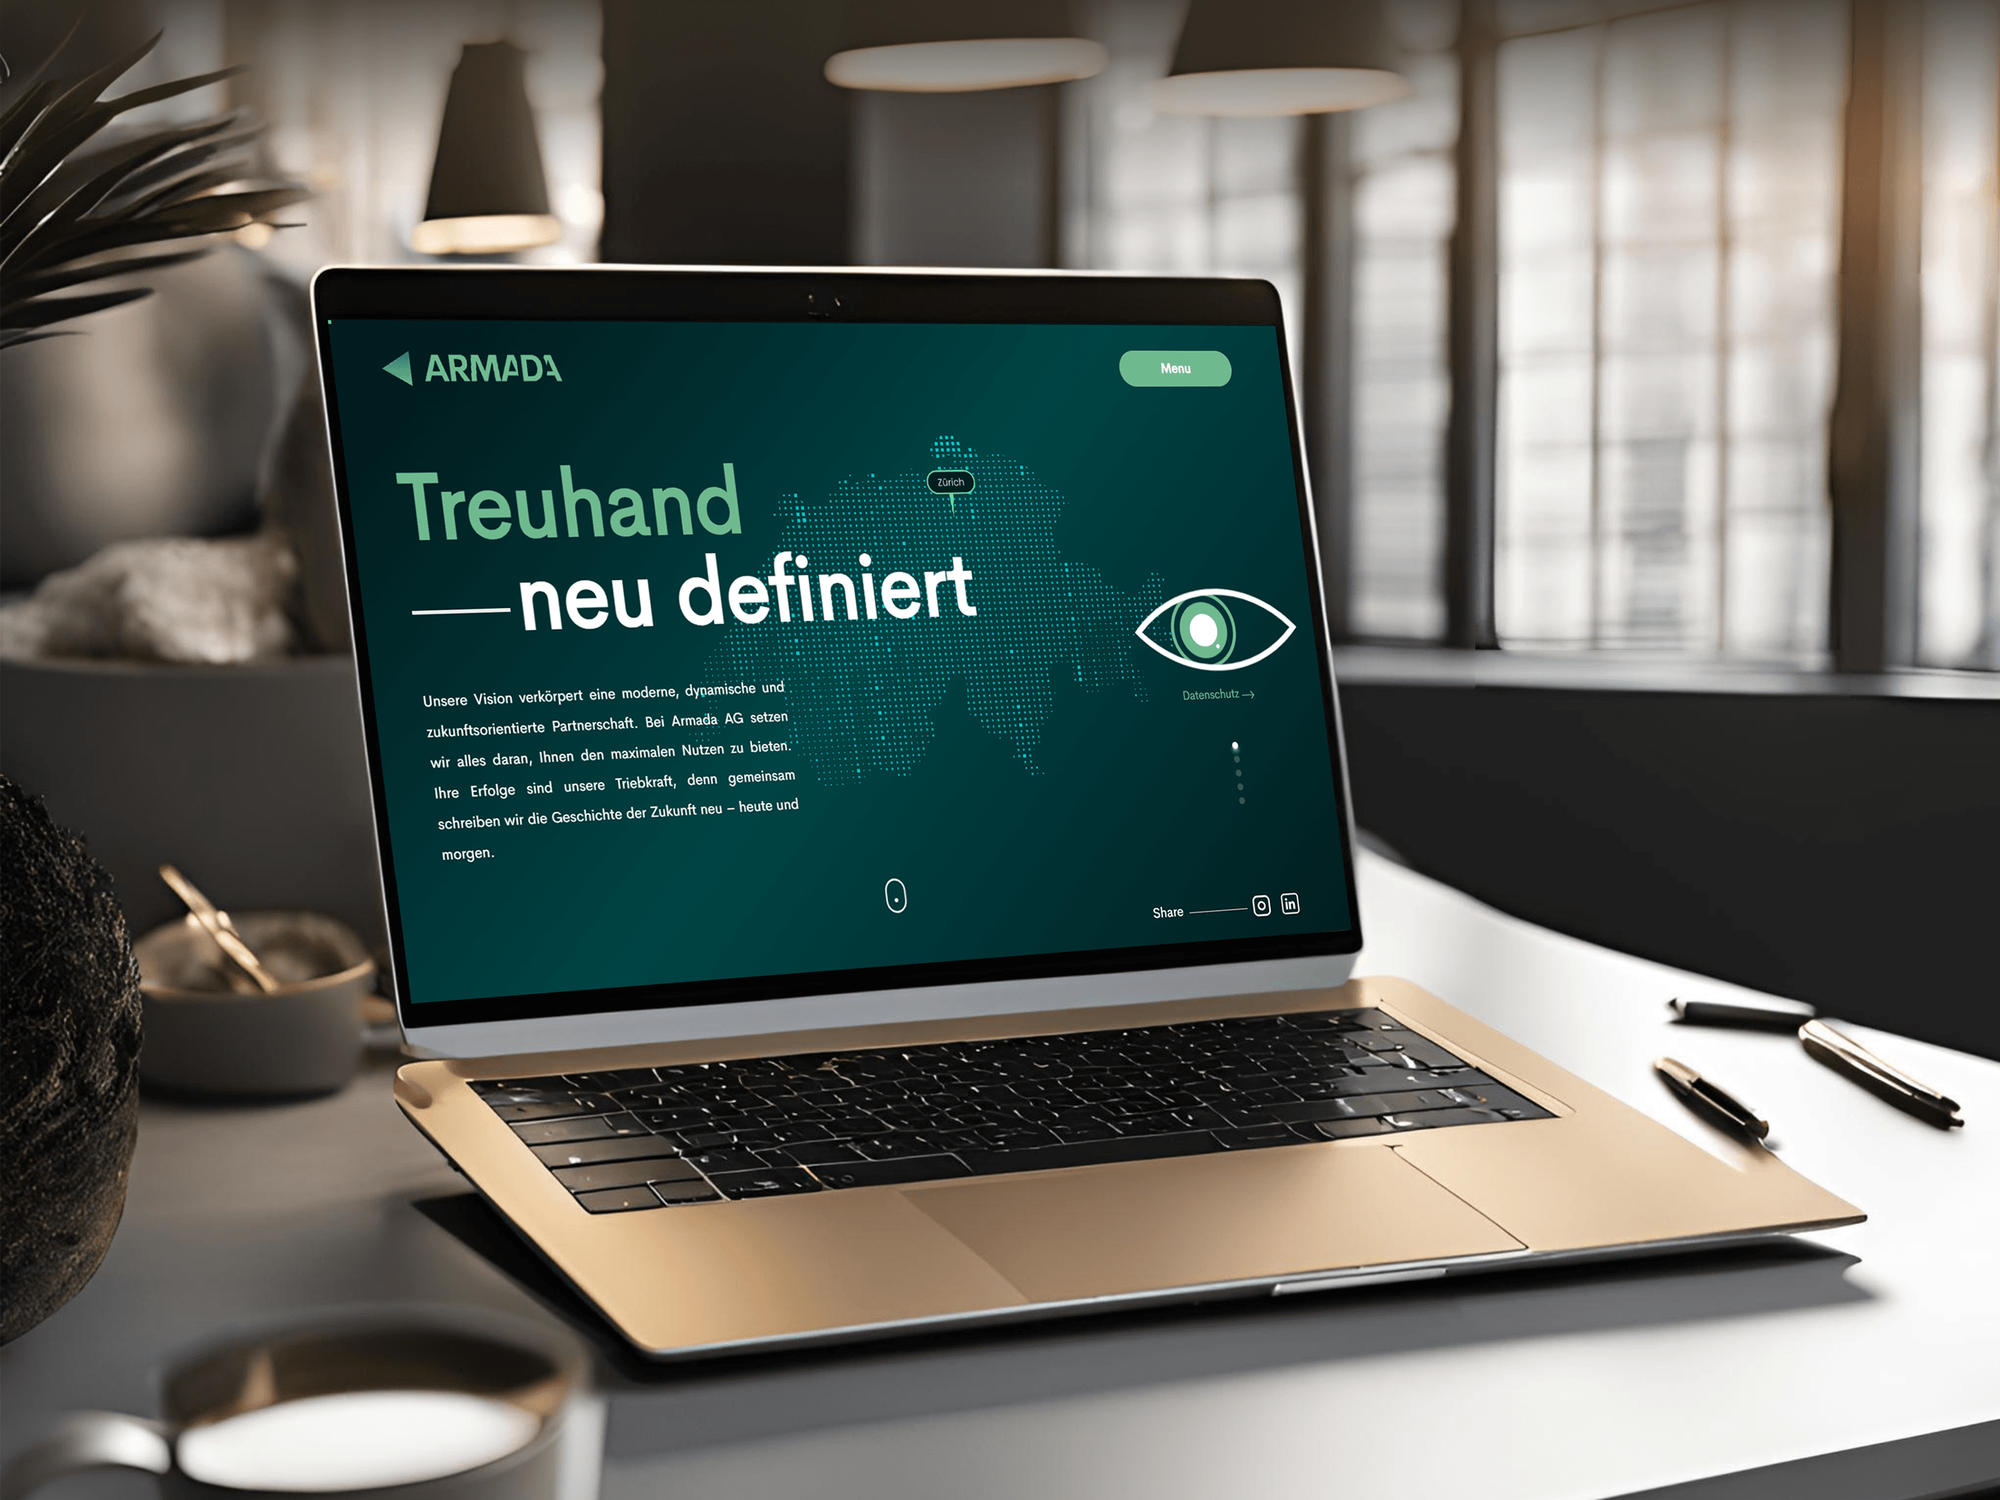
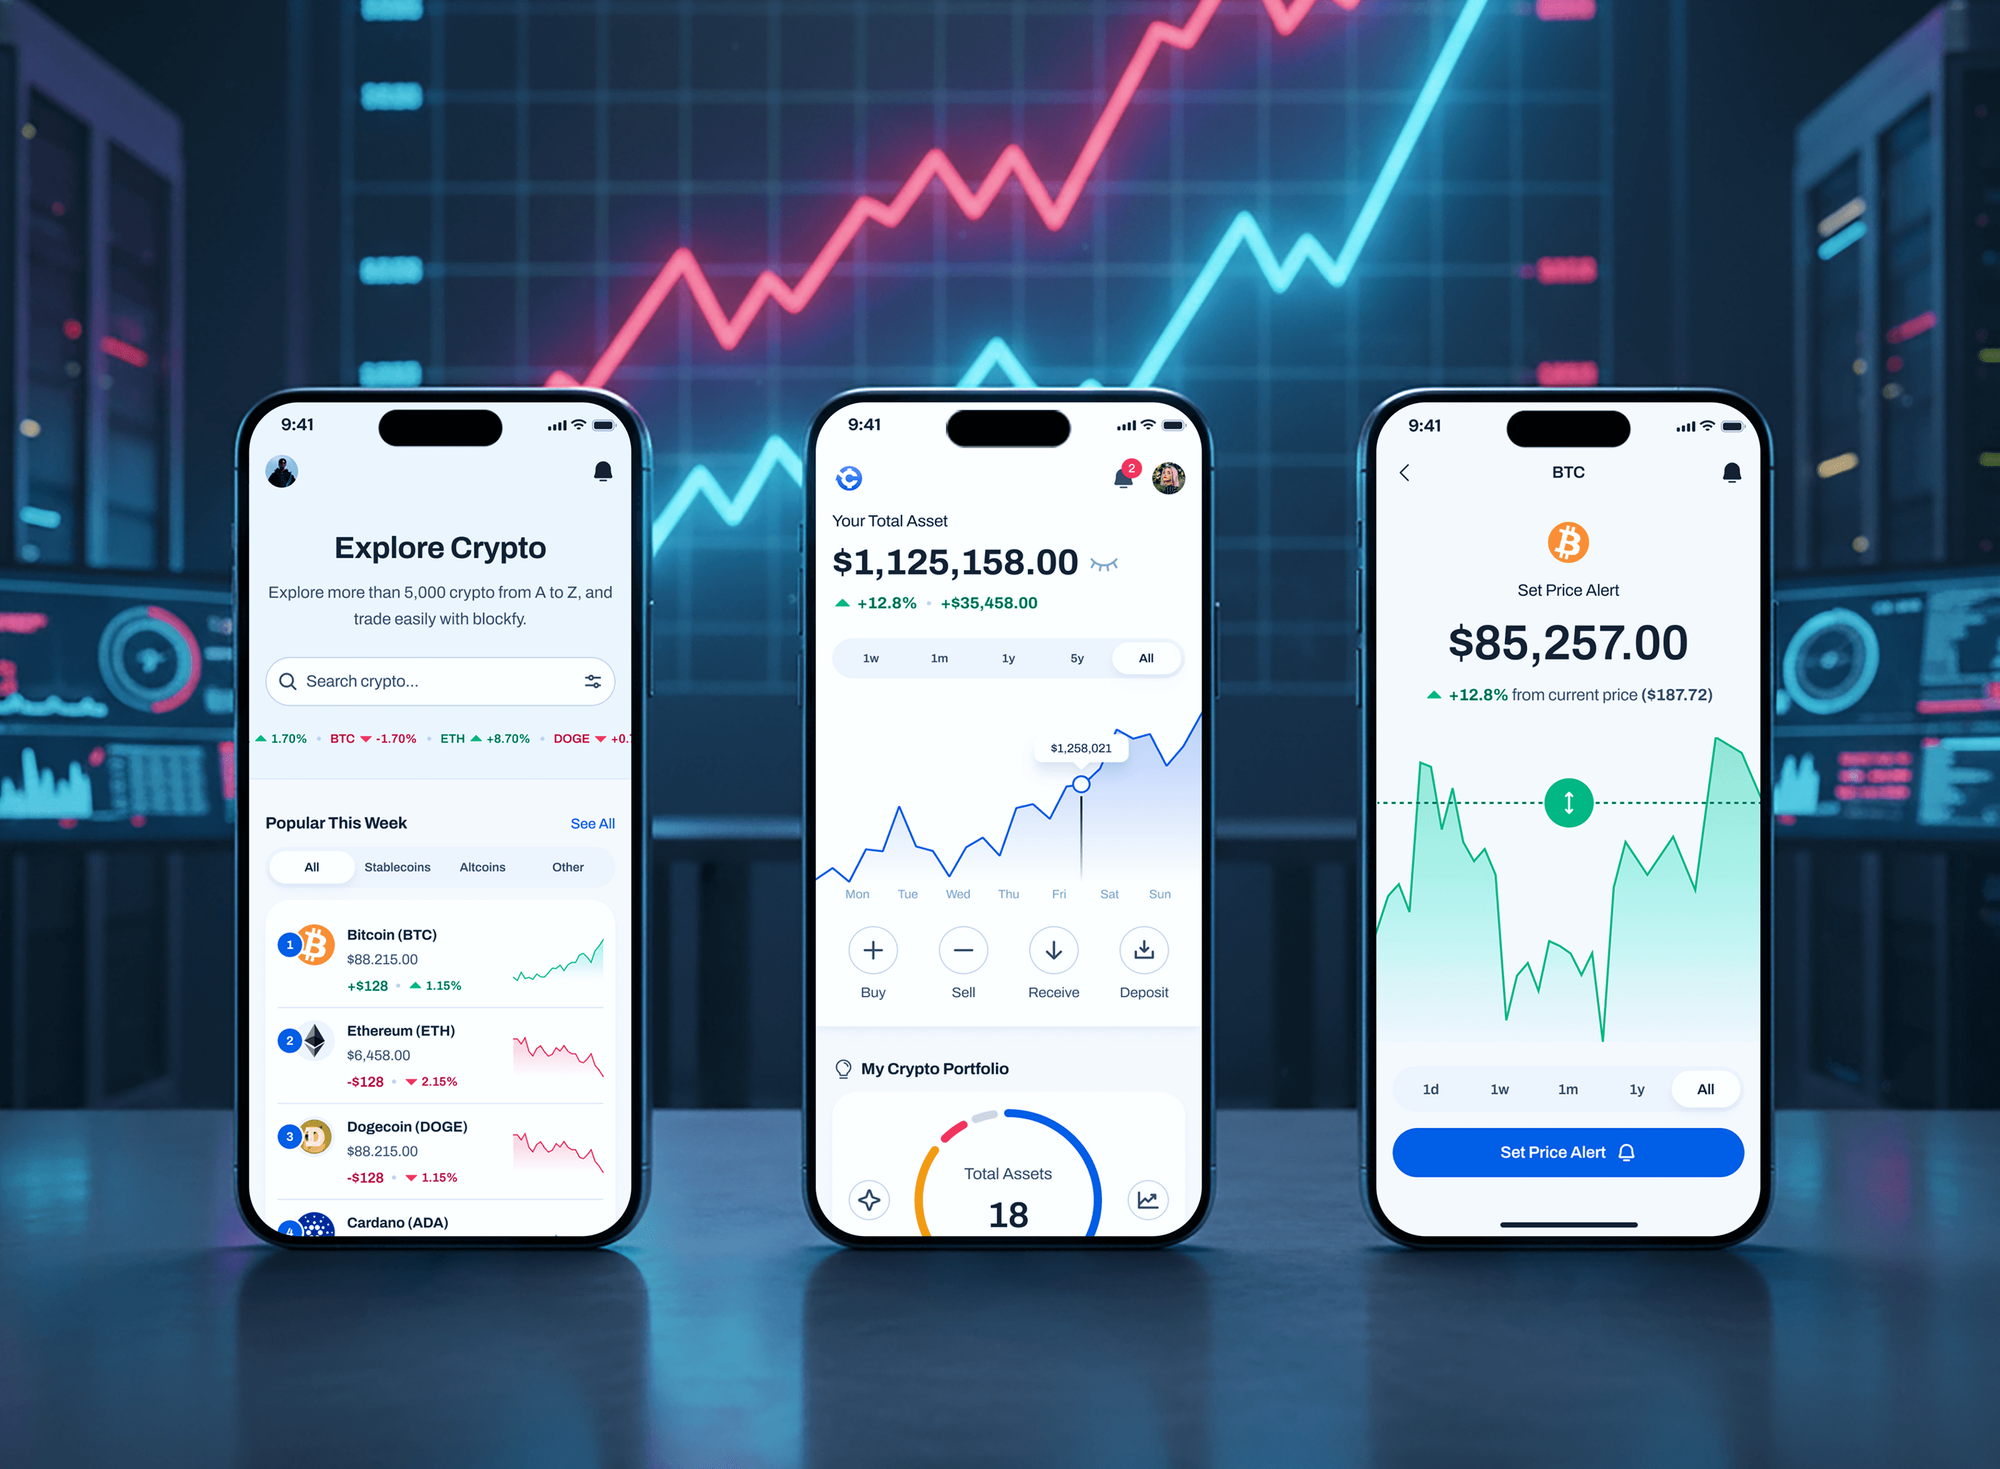
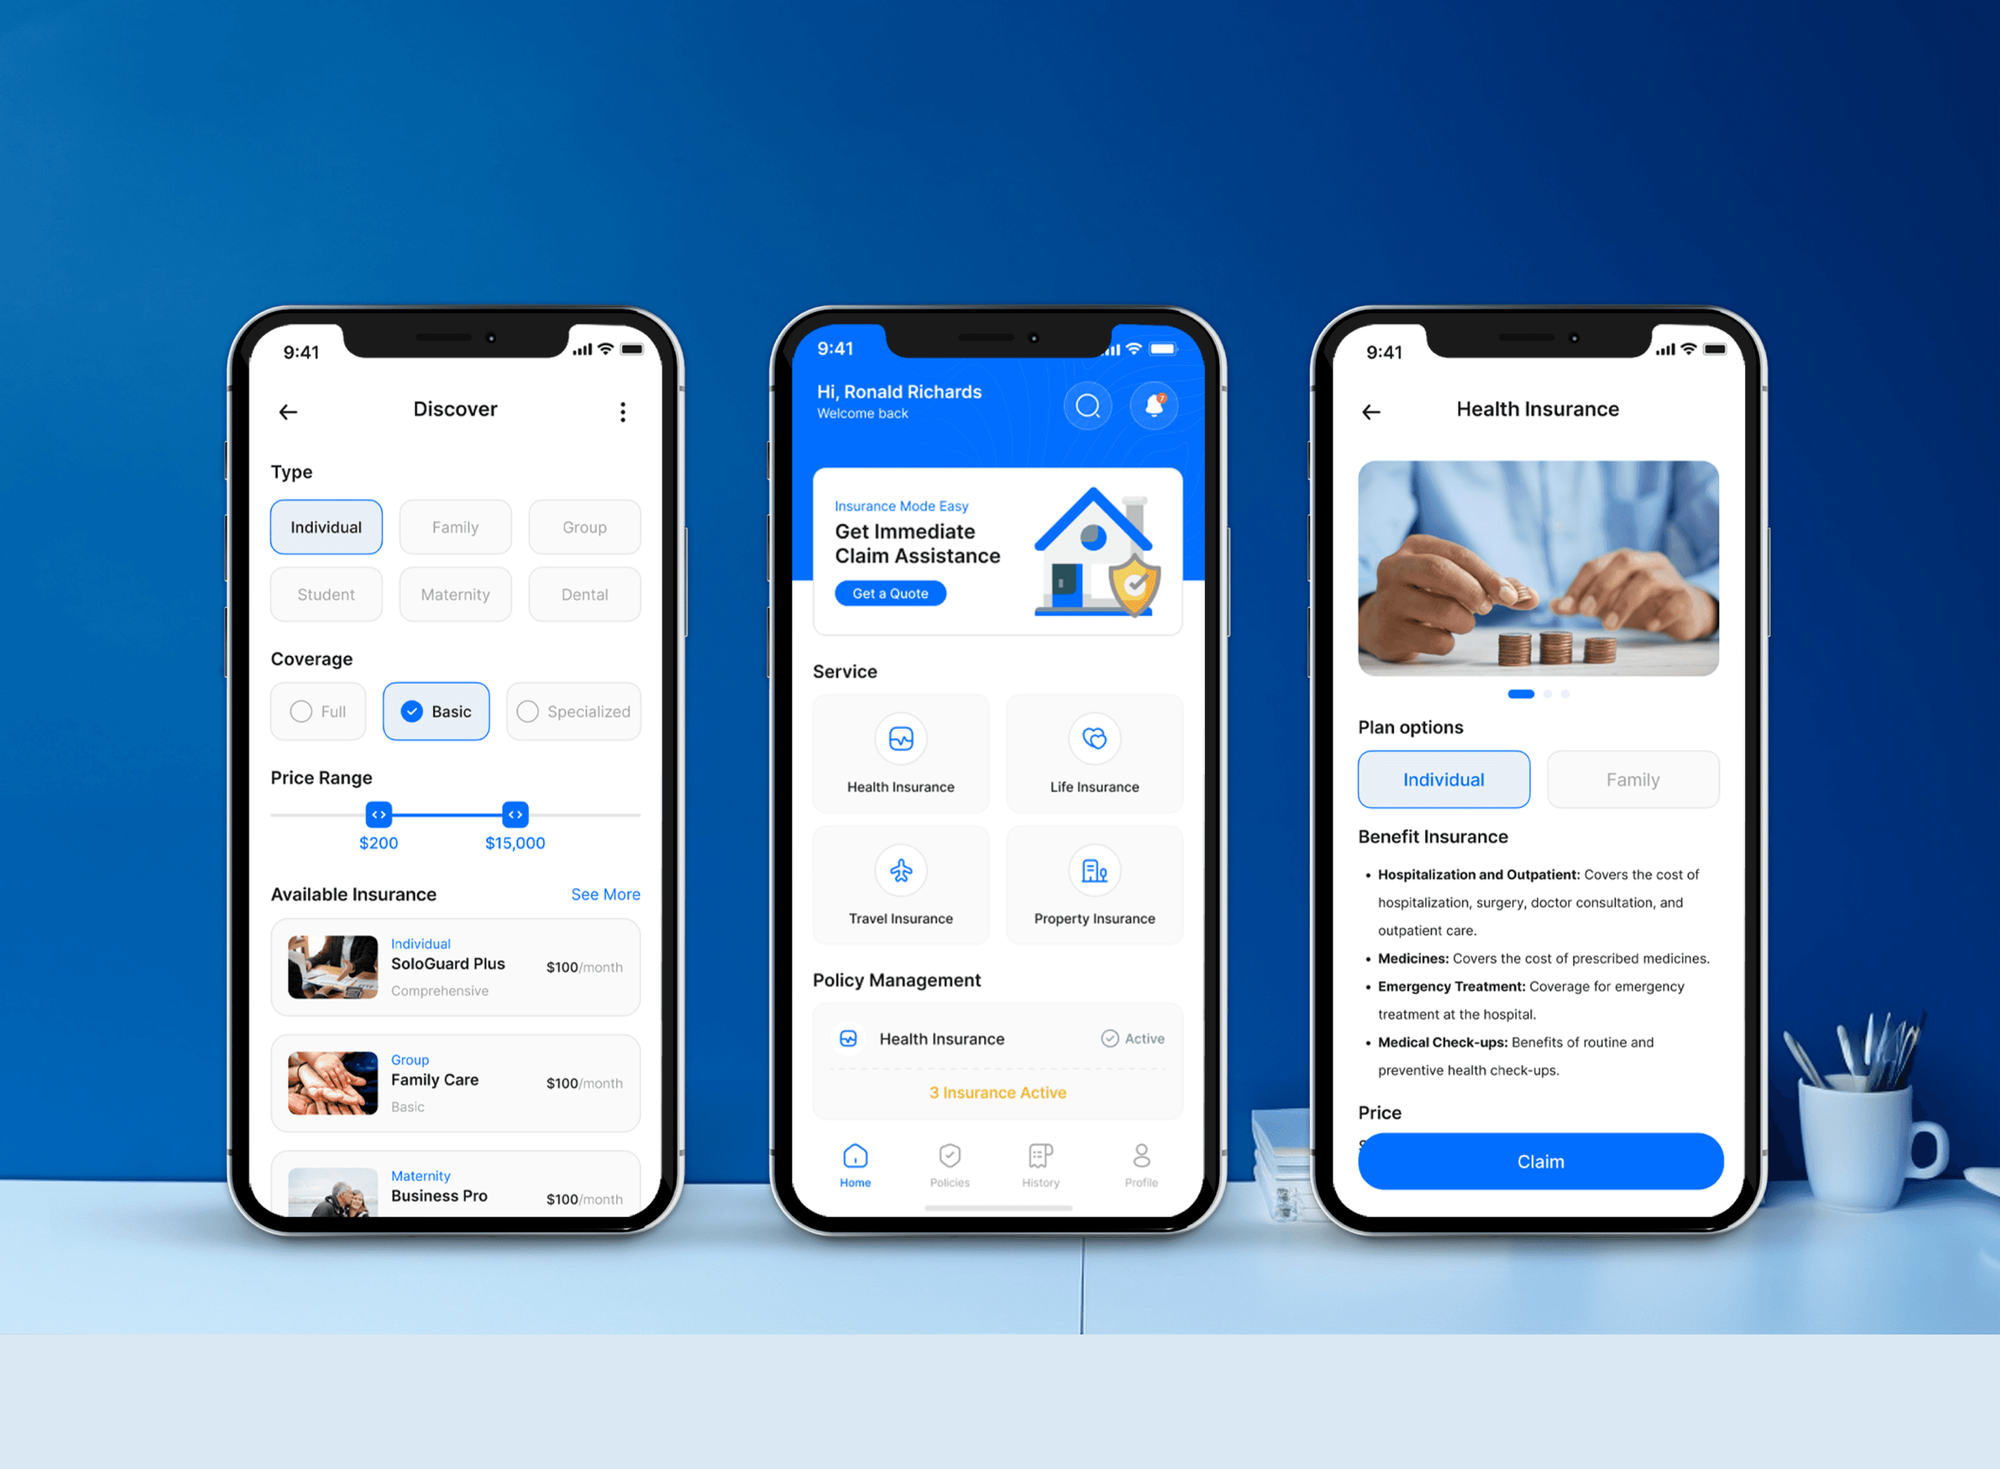
Projects We've Built
Investment, fiduciary, and finance websites and apps we designed and built. Products like these hold the kind of client information the rule protects.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
Security work for an advisory firm touches client trust, your custodian, and your exam file. These habits keep all three in order.
Every policy goes to your chief compliance officer before it's final. The program is yours, written in your firm's language, not ours.
We map where customer information lives without copying any of it. Account numbers and Social Security numbers stay inside the systems you control.
We explain what the rule asks and say when a question needs securities counsel. You won't get a guess about state notice laws from us.
A written program means little if a mailbox can forward client email unnoticed. We fix the settings behind the policy when your plan includes it.
We know which controls your custodian already runs and which fall to your firm. Your program covers the gaps instead of repeating theirs.
Plans are built for independent and small RIAs. You get one fixed price, and anything added later is quoted before we start.
Overview
DeveloperLook helps registered investment advisers meet Regulation S-P with working security, not just a binder. We write the incident response program, set notice steps for the 30-day deadline, add 72-hour vendor notice terms, and fix email, MFA, and device gaps. Projects start at $650 and take 1 to 6 weeks.
DEVELOPERLOOK
Project facts · Cybersecurity for Financial Advisors and RIAs
Reviewed 23 Oct 2026 by Saimul Islam
Good fit
Independent RIAs under $1.5 billion in AUM
Your firm counted as a smaller entity, the June 3, 2026 date has passed, and your incident response program still isn't written.
Breakaway advisors starting a firm
You left a wirehouse, opened your own RIA, and need cybersecurity for independent financial advisors set up before client accounts transfer.
Firms preparing for an SEC exam
Your exam request list asks for your Regulation S-P policies, incident program, and vendor oversight records, and the due date is close.
Multi-advisor practices with many vendors
Your firm runs a CRM, planning software, a portfolio tool, and two custodians, and nobody tracks which vendors must report a breach to you.
Compliance consultants and IT providers
You support RIAs and need cybersecurity services for financial advisors that your clients' CCOs can sign off without rewriting.
Not a fit
Bank, credit union, or lender
You run a bank, credit union, or lender examined under GLBA and FFIEC guidance. Our financial services cybersecurity page covers that program.
CRM is the real mess
Your real problem is client data scattered across a CRM nobody trusts. Our CRM for financial advisors page sets that up from $1,200.
Need a legal interpretation
You need a legal view on whether an incident requires notice in a specific state, or help with an SEC deficiency letter. Securities counsel is the right first call.
Budget under $650
Your budget is under $650 and you're a solo adviser on one custodian and Microsoft 365. The SEC's small entity compliance guide plus MFA everywhere is a sensible start.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on staff count, vendors, and whether we fix safeguards too, and you get a fixed proposal after a free Reg S-P call.
For independent advisers who need to know where they stand against the amended rule.
$650one-time, USD
For RIAs that need the incident program and vendor oversight written and in use.
$1,700one-time, USD
For firms with up to 25 staff that want the technical safeguards fixed as well.
$3,450one-time, USD
For Agencies
You own the advisory firm relationship. We supply the Reg S-P program, vendor oversight, and safeguard fixes under your brand, and your clients' CCOs review them with you. Your RIA clients meet the amended rule without you hiring a security specialist.
White label: your client only ever sees your brand
Send each RIA's AUM, custodians, CRM, and current compliance documents.
You get a fixed price per firm and a schedule your clients approve.
We deliver the program and safeguard fixes for your team to present.
Programs and records delivered under your name and templates.
The same method for each advisory firm you support, adjusted to its vendors.
Programs reflect what each custodian runs and what falls to the firm.
MFA, email security, and devices fixed, not only recommended.
The Right Technology for Your Project
These are the custodian, CRM, and Microsoft or Google tools advisory firms already run, plus the identity and device tools we use to secure them.
 Salesforce Financial Services Cloud
FAQ
Straight answers on cost, compliance dates, what the amended rule requires, who it covers, and what it means for your reps.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
It starts at $650 with DeveloperLook for a gap review against the amended Regulation S-P. A written incident response program, customer notice procedure, and vendor oversight is $1,700. Firms with up to 25 staff that also want MFA, email security, and managed devices start at $3,450. Most projects finish in 1 to 6 weeks.
Larger firms had to comply by December 3, 2025, and smaller firms by June 3, 2026. For registered investment advisers, larger means $1.5 billion or more in assets under management. Both dates have passed, so every SEC-registered adviser should now run the amended program. Our written program usually takes 3 to 6 weeks to finish.
It primarily focuses on protecting customer information and telling customers how it's used. The rule has two halves: privacy notices and opt-outs, and the safeguards and disposal rules that require written protection policies. The 2024 amendments added an incident response program, customer breach notices, and service provider oversight to the safeguards half.
They require a written incident response program to detect, respond to, and recover from unauthorized access to customer information. You must notify affected people within 30 days when their sensitive information was, or likely was, accessed without authorization. You must also oversee service providers, keep records of it all, and protect a wider set of customer information than before.
It applies to SEC-registered broker-dealers, including funding portals, investment companies, registered investment advisers, and registered transfer agents. The amendments call them covered institutions. Banks, credit unions, and most lenders follow other GLBA rules instead, and state-registered advisers fall under state rules rather than the SEC's version, so check yours with counsel.
Yes. Every investment adviser registered with the SEC must follow it, whatever its size. The rule treats advisers under $1.5 billion in assets under management as smaller entities only for the compliance date, not for the duties. So cybersecurity solutions for financial advisors still need to cover the incident program, the notices, and the vendors.
Investment adviser representatives follow the rule through their firm's policies, because the rule binds the registered adviser itself. In practice, each IAR needs MFA on email, the CRM, and custodian logins. Reps must also report odd activity right away and handle client files the way the program says. A rep working from home on a personal laptop is a common gap we close.
You need written procedures to oversee service providers, including due diligence and ongoing monitoring. Providers must protect customer information and tell you as soon as possible, and within 72 hours, after they learn of a breach affecting your customers' data. We check each contract and send a short request to any vendor whose terms are silent.
Start with MFA on email, the CRM, and every custodian login. Then add email security that flags new forwarding rules and blocks spoofed domains. Encrypt laptops and phones, and keep a list of every vendor holding client data. Those steps close the most common gaps in small advisory firms and support the written program.
You own every document, and we answer questions for 30 days after handover. We suggest reviewing the program yearly and after any new custodian, CRM, or major vendor. When an SEC exam asks for it, your CCO has the program, the vendor records, and the practice run notes together in one folder.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.