
Monthly rule review
Unused, shadowed, and overly broad rules flagged each month and fixed with your approval.

For businesses with a firewall nobody has touched since it was installed: rules cleaned up and owned, firmware patched fast, and every change approved and logged. From $400 per month.
7days
To install critical firmware fixes
12
Rule reviews a year
How your project runs
Teams we have built for:














The Problem
It shows up when a vendor announces a critical firewall flaw on a Friday, or someone needs a new rule and nobody remembers what the existing hundreds do.
01 · Rule sprawl
Hundreds of rules, and nobody knows which are safe to delete.
Hit counts and owners show which rules to keep, tighten, or remove.
02 · Old firmware
Firmware sits versions behind while attackers exploit known flaws.
Critical firmware fixes get scheduled as soon as the vendor releases them.
03 · Leftover access
VPN accounts for former staff still work.
VPN users are reviewed and removed as soon as someone leaves.
04 · Allow any
New requests get a broad allow-any rule at the top.
Each change is scoped to the exact source, destination, and port needed.
Your firewall has hundreds of rules. Some were added for a vendor who left years ago, others for a server that no longer exists, and nobody knows which are safe to delete. The firmware is two major versions behind, and the vendor just announced a flaw attackers are already using. VPN accounts still work for former staff. When someone asks for a new rule, it goes in at the top as allow any, because that worked last time.
We start with a backup and a baseline: every rule exported with its hit count, and the firmware checked against vendor advisories and CISA's known exploited list. Then we remove what's unused, tighten what's broad, and give each rule an owner and a reason. Each month we review rules, apply firmware fixes, and run changes through an approval step. Your firewall stays tidy, not just switched on.
Every rule owned and explained
Each rule carries an owner, a reason, and a review date, so cleanup stays safe.
Firmware fixes within 7 days
Critical vendor fixes installed within 7 days of release, in a window you approve.
Changes approved and logged
Every change request goes through approval, with a rollback step and a log entry.
Our Managed Firewall Services Process
You approve the cleanup plan and every rule change before it happens, and firmware upgrades run only in maintenance windows you choose.
We look at your firewall models, sites, VPN users, and who changes rules today. You get a scope and a monthly price. If your vendor's own support plan already covers what you need, we'll tell you before we quote.
What's Included
Rule reviews, firmware updates, config backups, change requests, VPN users, and monthly reporting, handled on the firewalls you already own at every site.
Compare Options
A vendor support plan is the cheapest route to firmware downloads and hardware swaps, and in-house IT knows your network best. Here is how they compare with managed firewall providers.
| Feature | DeveloperLookBest fit | Vendor support | In-house IT |
|---|---|---|---|
| Rule hygiene | Monthly review with owners | Not included | When someone has time |
| Firmware | Critical fixes within 7 days | Downloads provided, you install | Often delayed for fear of outages |
| Change control | Approval, scope, and rollback | Not included | Informal requests |
| Config backups | Daily, stored off the box | Not included | Manual, now and then |
| Hardware failure | Restore from backup, RMA help | Replacement unit shipped | Depends on spares |
| Vendor mix | FortiGate, Palo Alto, SonicWall, pfSense | Their own brand only | Whatever staff know |
| Network knowledge | Learned during onboarding | No view of your setup | Deepest over time |
| Cost | From $400 per month | Cheapest yearly fee | Staff time and training |
Projects We've Built
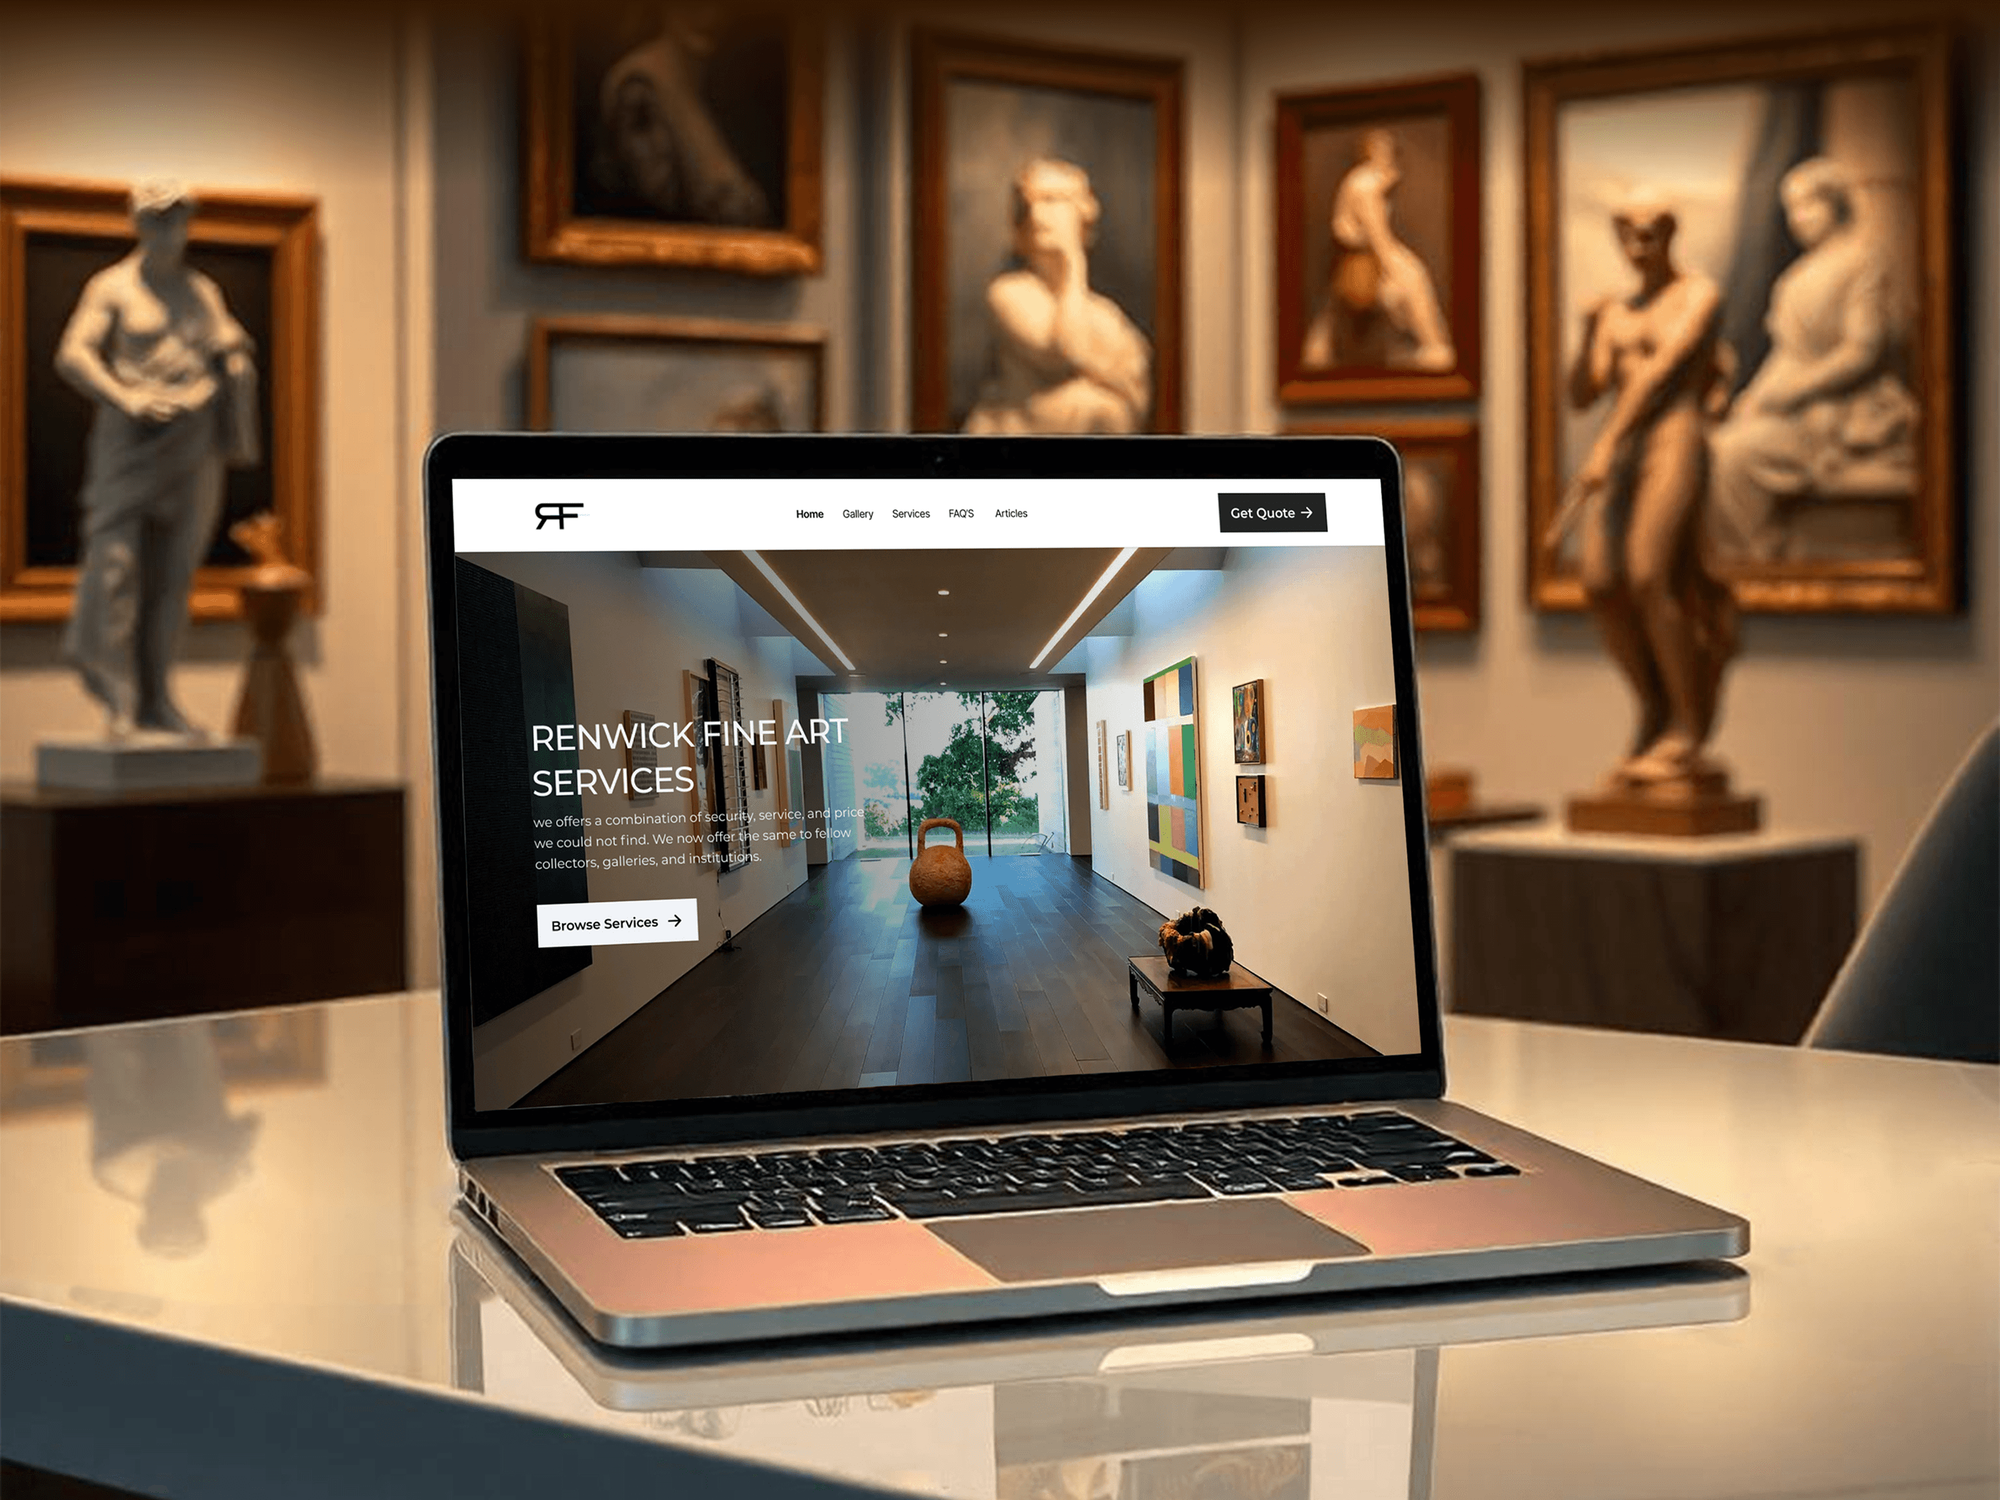
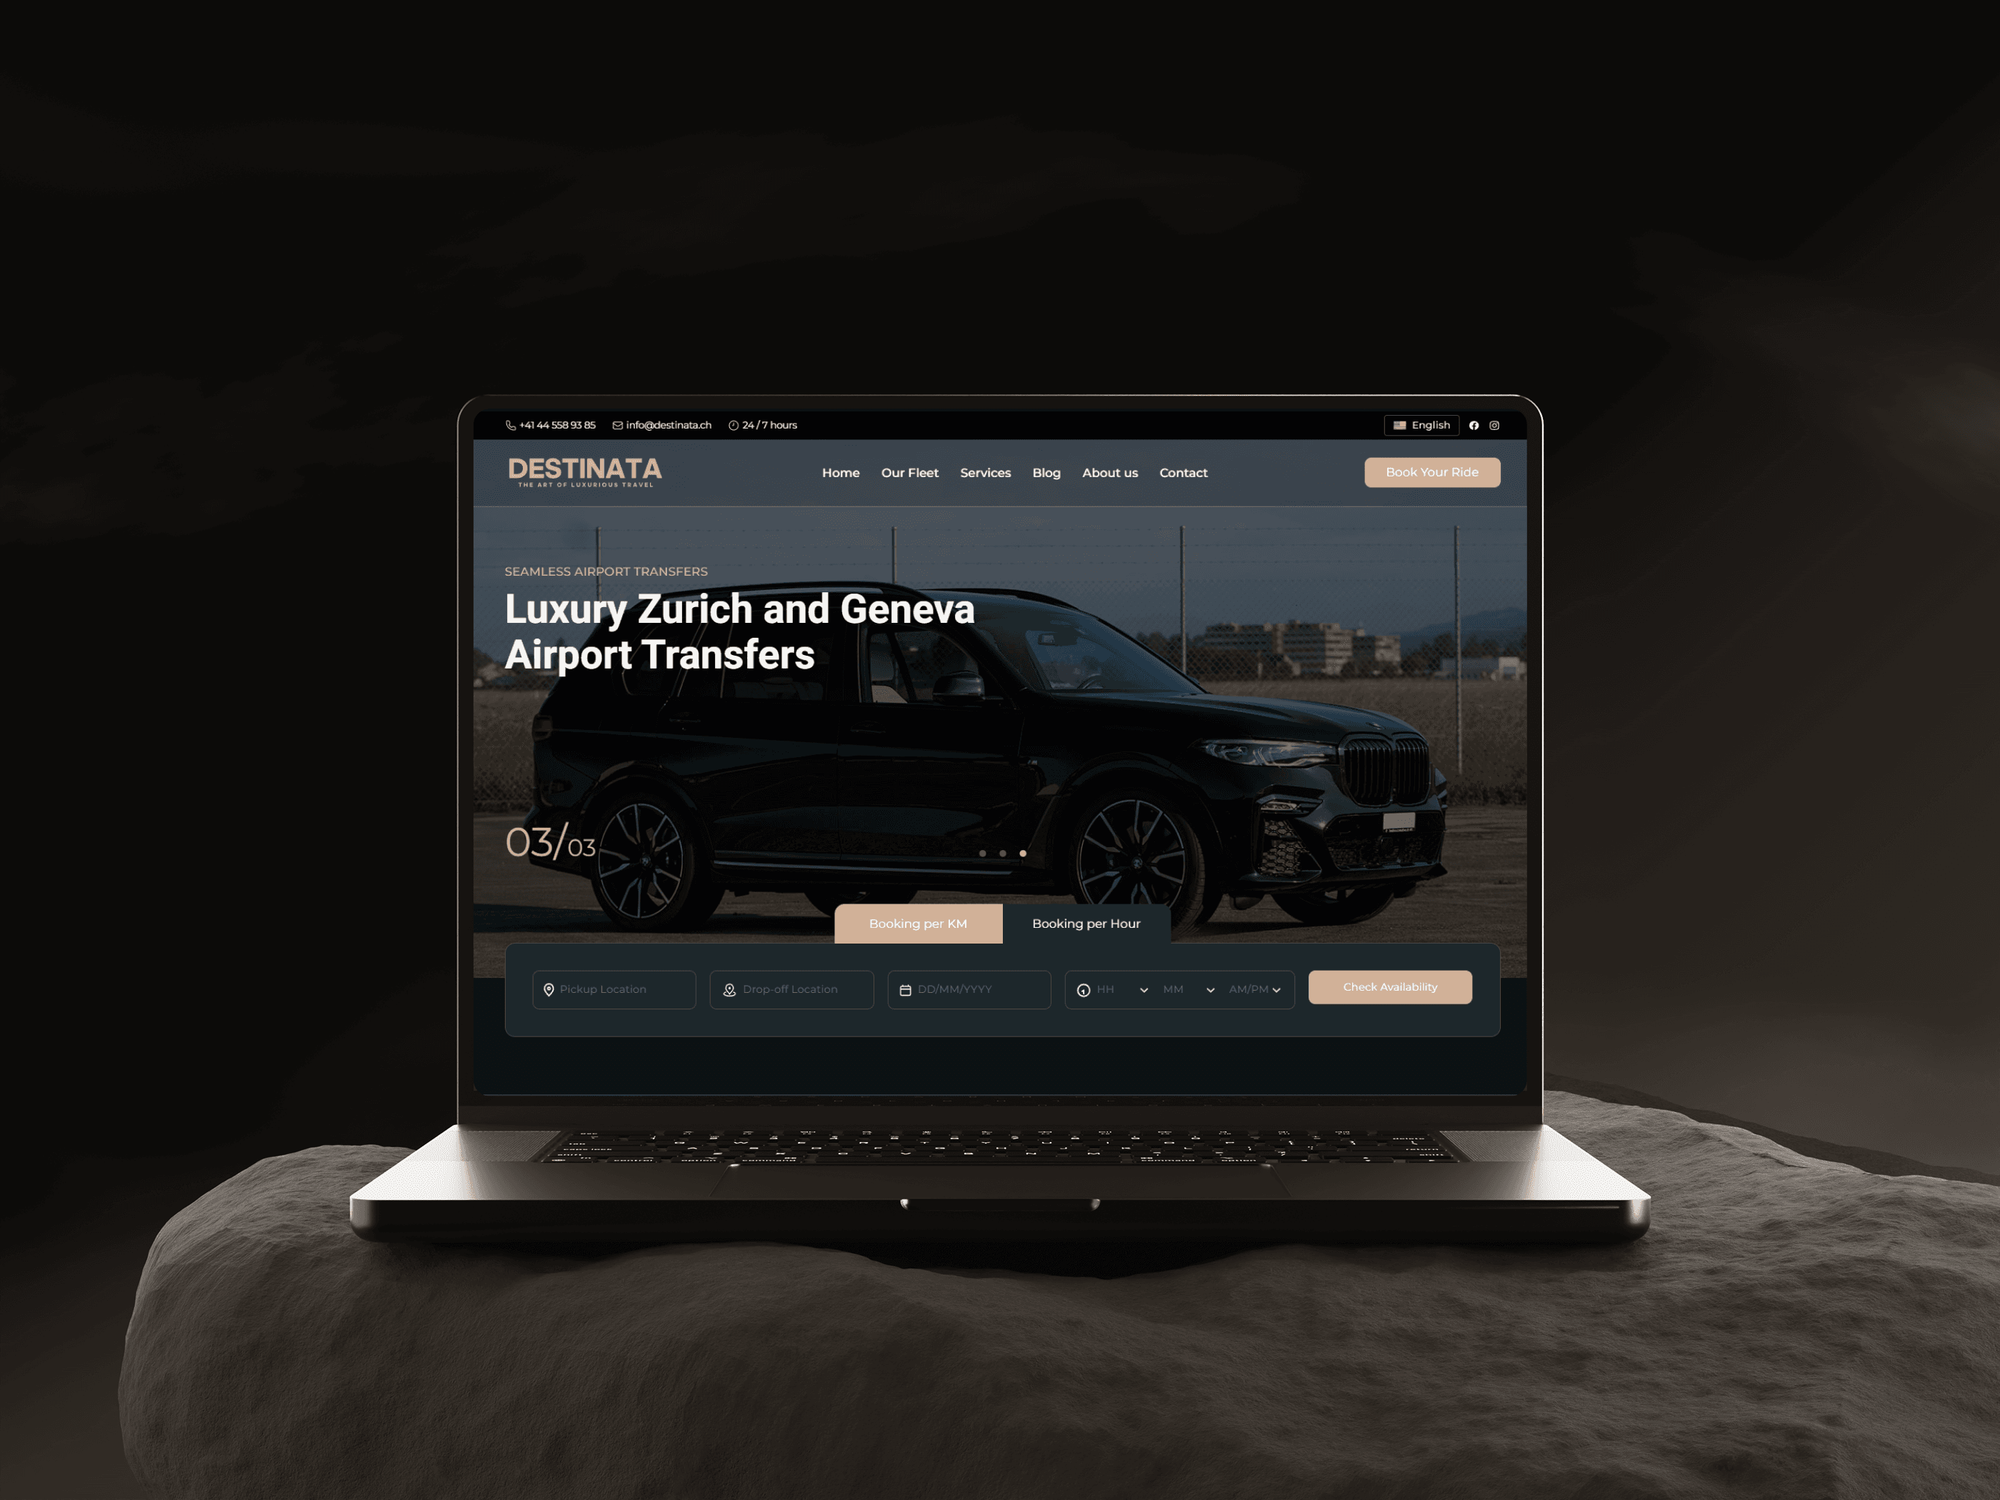
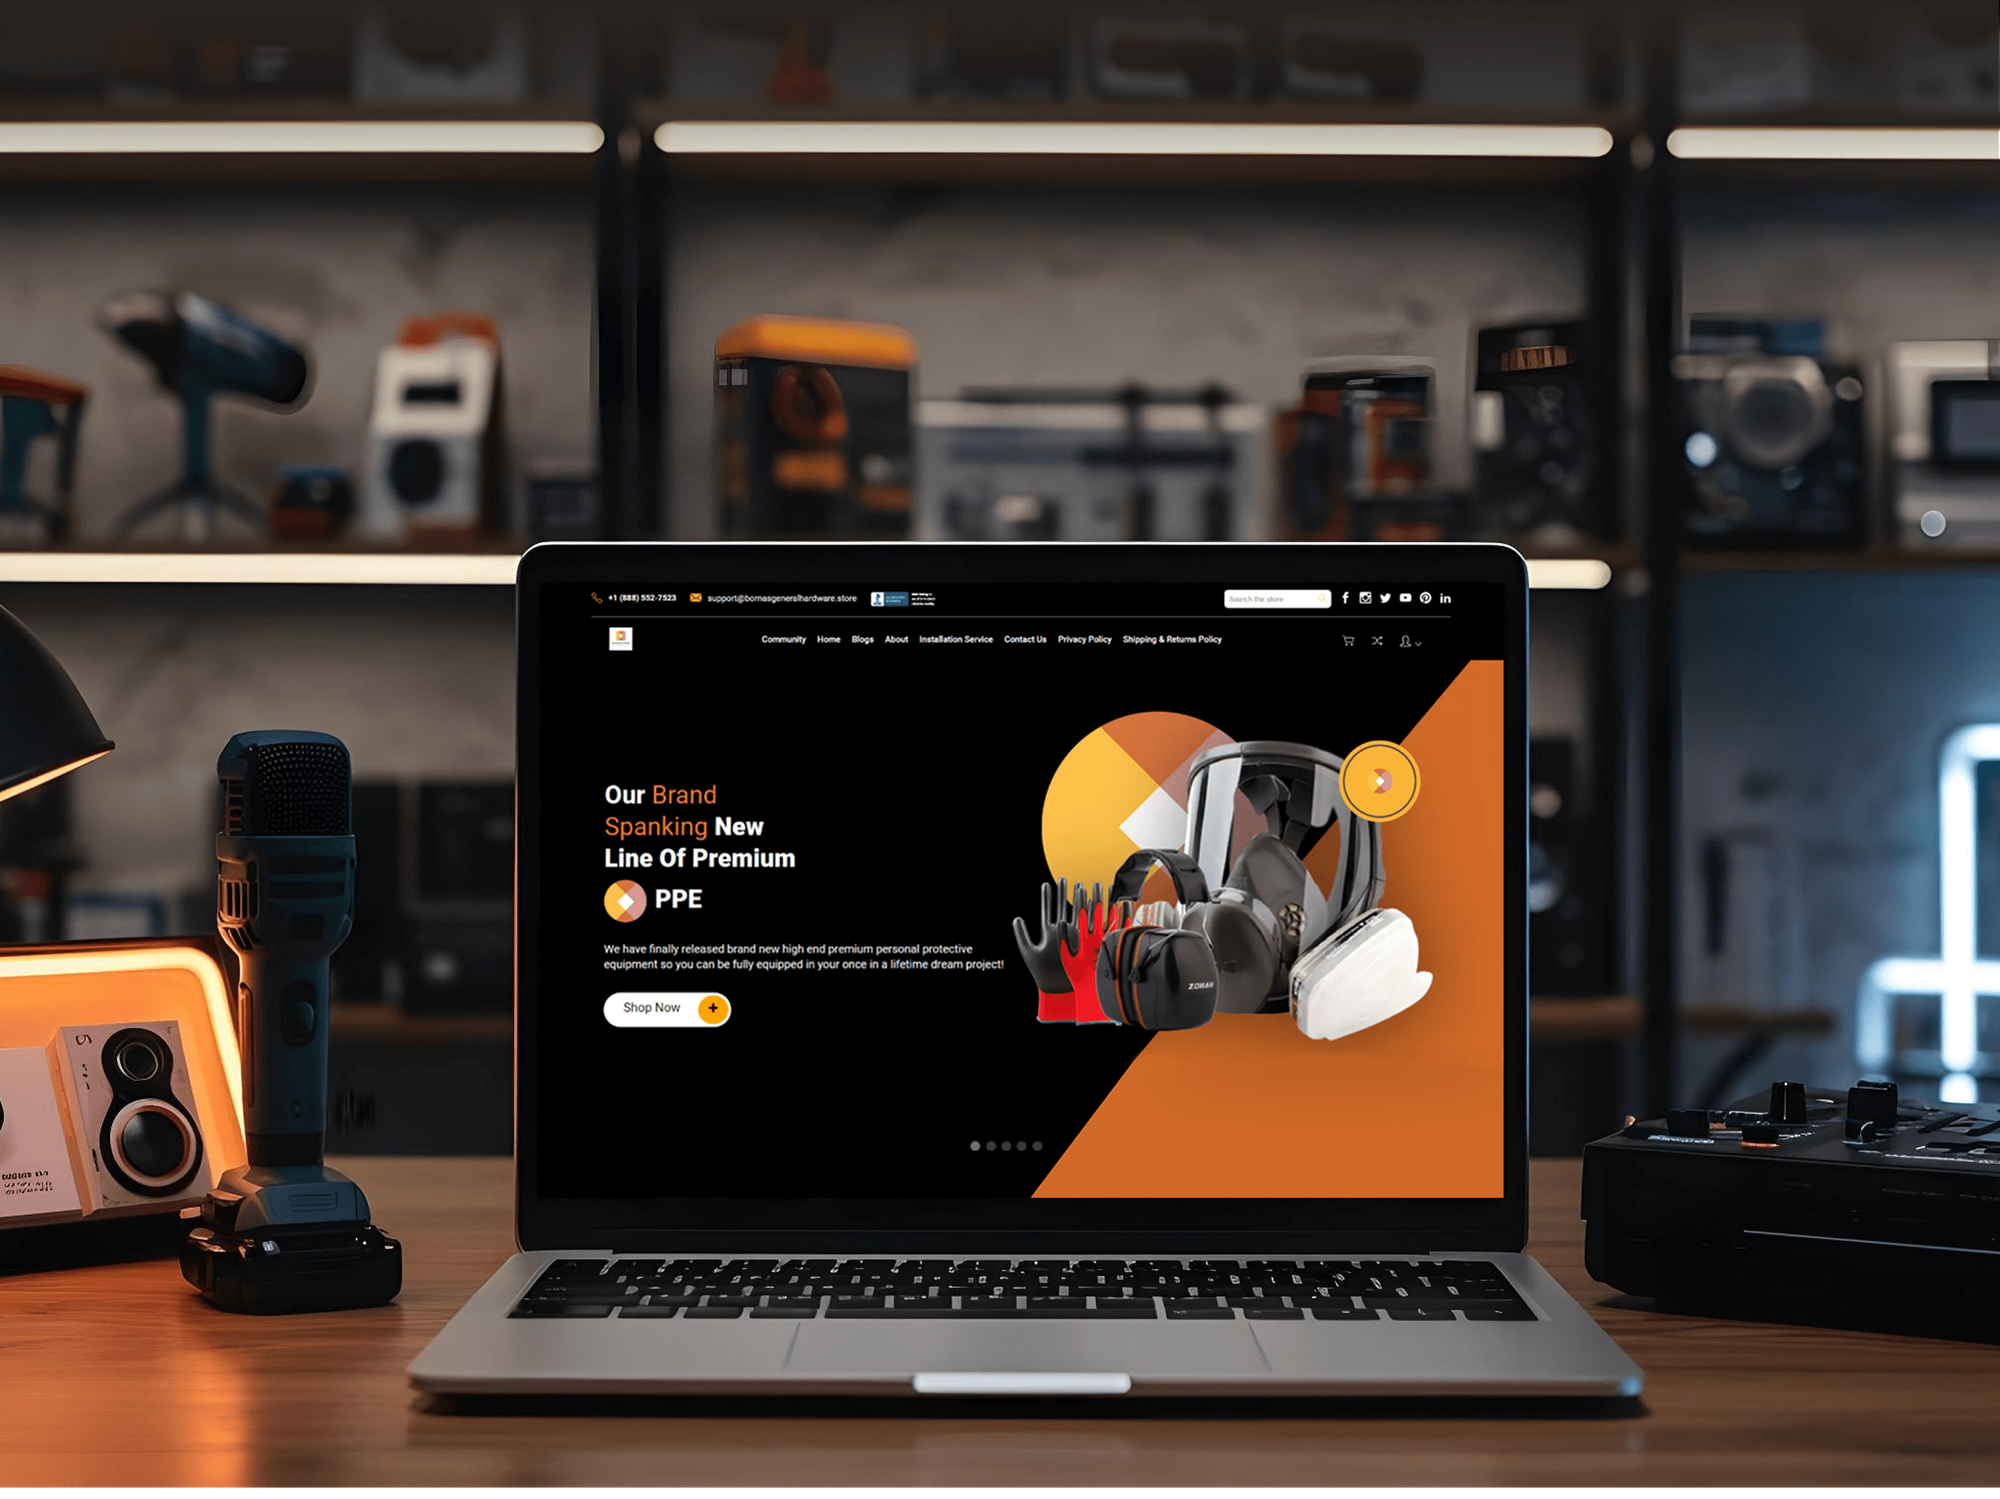
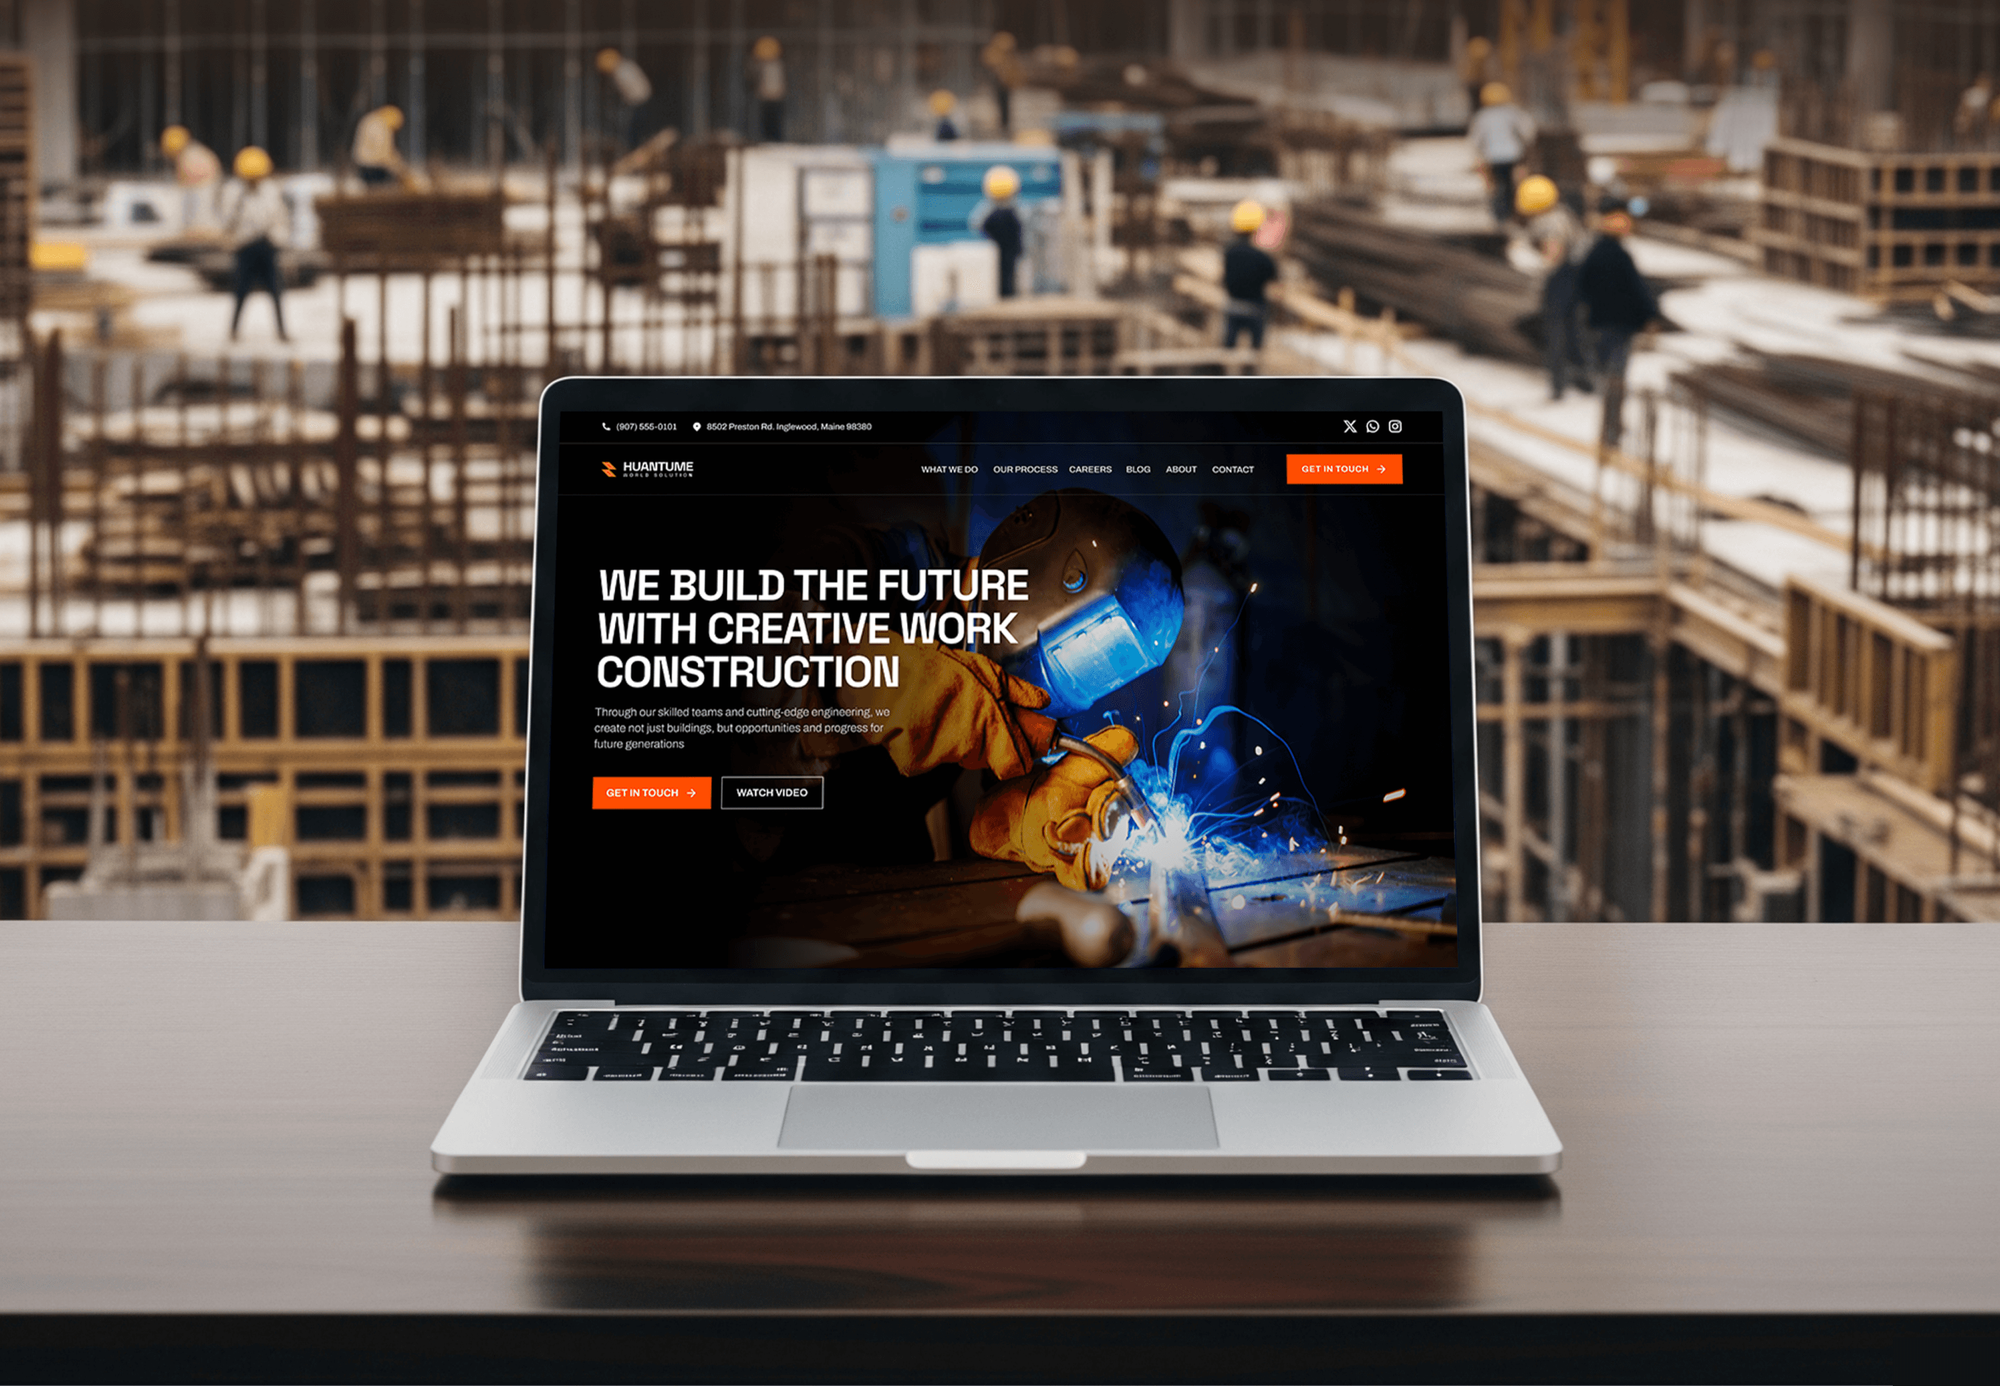
Websites and booking systems we built for an art logistics firm, a limousine service, a hardware store, and a builder. Businesses like these run offices and sites behind firewalls.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A bad firewall change can take an office offline or open it to the internet. These habits keep every change small, approved, tested, and easy to undo.
Every rule change has a named requester and an approver on your side. Emergency fixes still get logged and confirmed with you afterwards.
We save the config and write the undo step before touching a rule. If a change misbehaves, the previous config goes straight back on.
If your firewall is out of vendor support, we'll say so and price the replacement plainly. We won't keep patching a box that no longer gets fixes.
We'd rather tighten an existing rule than add a new one. A smaller rule set is easier to review and leaves fewer gaps to exploit.
Admin accounts, configs, and backups belong to you and stay in your password manager. If you leave, you keep every rule note and backup.
Firmware upgrades and risky changes run in maintenance windows you choose. Card terminals, phones, and bookings keep working through the day.
Overview
DeveloperLook provides managed firewall services for businesses running one to eight firewalls. We review rules monthly, install critical firmware fixes quickly, back up configs daily, manage VPN users, and handle change requests with approval and rollback. Plans start at $400 per month, and onboarding takes 1 to 2 weeks.
DEVELOPERLOOK
Project facts · Managed Firewall Services
Reviewed 22 Oct 2026 by Saimul Islam
Good fit
Businesses with an untouched firewall
Your firewall was set up years ago, nobody has reviewed its rules since, and you want monthly upkeep that starts with a cleanup.
Offices with several sites
You run firewalls at 3 offices joined by site-to-site VPNs, and each one was configured by a different person.
Companies facing PCI DSS reviews
Your PCI DSS assessor wants dated proof that firewall settings get reviewed twice a year, and today there's no record at all.
IT managers with no network time
You handle IT alone and want a managed firewall service provider to take rule changes and firmware off your list.
MSPs needing firewall specialists
Your clients run a mix of FortiGate, SonicWall, and pfSense, and you need engineers who manage them all under your brand.
Not a fit
Need a one-time network cleanup
You want your network mapped, segmented, and hardened once, not managed every month. Our network security services cover that project from $1,050.
Want all security tools managed
You want identity, email, devices, and the firewall looked after as one program. Our managed security services cover that from $850 a month.
Need a web app firewall
You need to block attacks on a website or API at the application layer. A web application firewall setup is the better fit for that job.
Home-office router only
You have one consumer router and a few laptops. Updating its firmware, changing the admin password, and turning off remote management may be all you need.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are monthly starting points in USD. Your plan depends on firewall count, sites, and change volume, and you get a fixed proposal after a free firewall review.
For one office with a single firewall that needs steady, documented upkeep.
$400/month
For companies with up to 3 firewalls or sites and regular change requests.
$700/month
For organizations with up to 8 firewalls, cloud firewalls, and audit needs.
$1,100/month
For Agencies
You own the client relationship. We manage the firewalls behind it: rule reviews, firmware, backups, and change requests across mixed vendors, reported in your format. Your clients get steady firewall care without you hiring a network engineer.
White label: your client only ever sees your brand
Send the client's firewall models, sites, VPN users, and change contacts.
We back up configs, report rule health, and give a fixed monthly price.
We handle changes and firmware, then report monthly in your template.
You take client requests while we make changes quietly under your brand.
FortiGate, Palo Alto, SonicWall, pfSense, and Meraki under one process.
Monthly firewall reports written in your format and wording.
Every client change logged with requester, approver, and rollback step.
The Right Technology for Your Project
We manage firewalls through their own vendor consoles and keep versioned config backups off the box, so any unit can be rebuilt from a known good state.
 AWS security groups
FAQ
Straight answers on pricing, onboarding, what a managed firewall is, remote management, and rule cleanup.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Managed firewall service pricing at DeveloperLook starts at $400 per month for one firewall. That includes monthly rule reviews, daily config backups, and critical firmware fixes within 7 days. The $700 plan covers up to 3 firewalls or sites. The $1,100 plan covers 8, including cloud firewalls and a full rule cleanup. Hardware and vendor licenses stay on your own account.
Firewall onboarding with DeveloperLook takes 1 to 2 weeks. We back up configs, export every rule with its hit count, check firmware against vendor advisories, and agree the change process with you. Obvious cleanup happens in that window. On the largest plan, the full policy sprawl cleanup finishes within the first month, with every change approved first.
A managed firewall is a firewall that an outside team configures, updates, and watches for you under an ongoing agreement. Managed firewall security services usually leave you owning the hardware and licenses, while the provider handles rule changes, firmware, backups, and reviews. It suits businesses that rely on their firewall but have no network specialists on staff.
A managed service firewall usually means the provider supplies the firewall itself for a monthly fee, as a leased appliance or a cloud firewall. Bundled managed firewall solutions like these can be convenient, but leaving often means returning the box. DeveloperLook manages firewalls you own, so the hardware and configs stay yours.
Firewall management is the routine work of keeping a firewall's rules, firmware, and access correct over time. That means reviewing rules, removing ones nobody needs, applying updates, backing up configs, and controlling changes. Under PCI DSS v4.0, firewall configurations need a review at least every six months, which sets a sensible minimum pace for everyone.
Before you select a managed firewall service provider, check four things: vendor support, change control, firmware speed, and config ownership. Ask how changes are approved and rolled back, and how quickly critical fixes go in. Request a sample monthly report and change log. Avoid contracts that tie you to hardware you can't keep.
You likely need a managed firewall if it protects card payments, remote access, or several sites and nobody reviews it regularly. Warning signs include unknown rules, firmware months behind, and VPN accounts for former staff. If you run one simple office and someone updates the firmware each month, a vendor support plan may be enough.
Yes, most firewalls are managed remotely, through the vendor's cloud console or a secured admin connection. We limit admin access to named accounts with MFA and, where possible, to a management VPN instead of the open internet. Site visits are only needed for cabling or swapping failed hardware, which a local technician can handle.
Firewall policy sprawl is managed by measuring before deleting. Export every rule with its hit count, find unused, shadowed, and overly broad rules, then give each remaining rule an owner and a review date. Remove rules in small, approved batches with rollback steps. Large estates do the same through central managers such as FortiManager or Panorama.
Yes. The firewalls, licenses, admin accounts, and every config backup belong to you. When you leave, we hand over the rule notes, the change log, and the latest backups, then remove our named admin accounts. Your next provider or in-house team picks up from a documented, known good state.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.