
Log collection platform
Microsoft Sentinel or Wazuh deployed in your account, with identity, email, endpoint, firewall, and cloud logs connected.

For growing companies that need a security operations center without building one: logs collected, alerts triaged, and audit evidence kept in accounts you own. From $800 per month.
12months
Of logs kept for audits
3+
Log sources in one view
How your project runs
Teams we have built for:














The Problem
It shows up when an auditor, insurer, or enterprise customer asks for last quarter's sign-in records, and the answer is scattered across five consoles with short retention.
01 · Short retention
Firewall and sign-in logs roll over before anyone needs them.
Retention is set to your audit needs, and older logs are archived.
02 · Scattered alerts
Each tool alerts on its own, so linked events look unrelated.
Logs land in one platform where detections join events across systems.
03 · Manual exports
Audit requests mean days of hand-exported CSV files.
Saved searches and monthly reports produce audit evidence on request.
04 · Lock-in
Leaving a provider means losing your logs and detection rules.
The platform, detection rules, and logs live in accounts you own.
Your firewall overwrites its logs every few days. Microsoft 365 keeps sign-in history for a limited time, and logging in the cloud account was never switched on. Then a customer's security review asks how you'd spot a stolen admin login, and an auditor wants a year of access records. Someone exports CSV files by hand. Each tool alerts on its own, so a slow attack across three systems looks like noise.
We start by choosing a log platform in your own cloud: Microsoft Sentinel for Microsoft shops, or open-source Wazuh on your server. We connect identity, email, endpoint, firewall, and cloud logs, write detections mapped to MITRE ATT&CK, and set retention to match your audits. Engineers triage alerts every business day. The platform, rules, and logs stay yours instead of living in a provider's system.
Logs in your own cloud
The log platform runs in your Azure tenant or on your server, so the data stays yours.
Detections mapped to ATT&CK
Rules written for your systems and labelled with the MITRE ATT&CK techniques they catch.
Retention set for audits
Log storage sized for PCI DSS, SOC 2, or insurer requests, with older data archived.
Our SOC as a Service Process
You approve the log sources, retention, and escalation rules before collection starts, then review cases, detections, and storage costs with us every month.
We list your systems, what they log today, and what auditors or customers ask for. You get a log source plan, an estimate of storage costs on your cloud bill, and a monthly price. If simpler alerting covers you, we'll tell you before we quote.
What's Included
Log collection, detections, automation, daily triage, case records, and audit-ready retention, built in your own cloud and run by engineers who also fix systems.
Compare Options
Large SOC as a service providers staff analysts around the clock, and an in-house SOC knows your systems best. Here is how each compares on coverage, ownership, and cost.
| Feature | DeveloperLookBest fit | Large provider | In-house SOC |
|---|---|---|---|
| Coverage hours | Business days, plus automation | Around the clock | Your shift pattern |
| Log platform | In your own cloud | Usually theirs | Yours to build |
| Detections | Tuned to your systems | Shared rule library | Written by your team |
| Ownership on exit | Platform, rules, and logs stay | Logs often exported | Fully yours |
| Root-cause fixes | Engineers who also fix | Recommendations only | If staff have time |
| Setup time | 2 to 4 weeks | Several weeks | Months of hiring |
| Audit retention | Set to your framework | Per their contract | Whatever you configure |
| Cost | From $800 per month | Higher, per device or GB | Several full salaries |
Projects We've Built
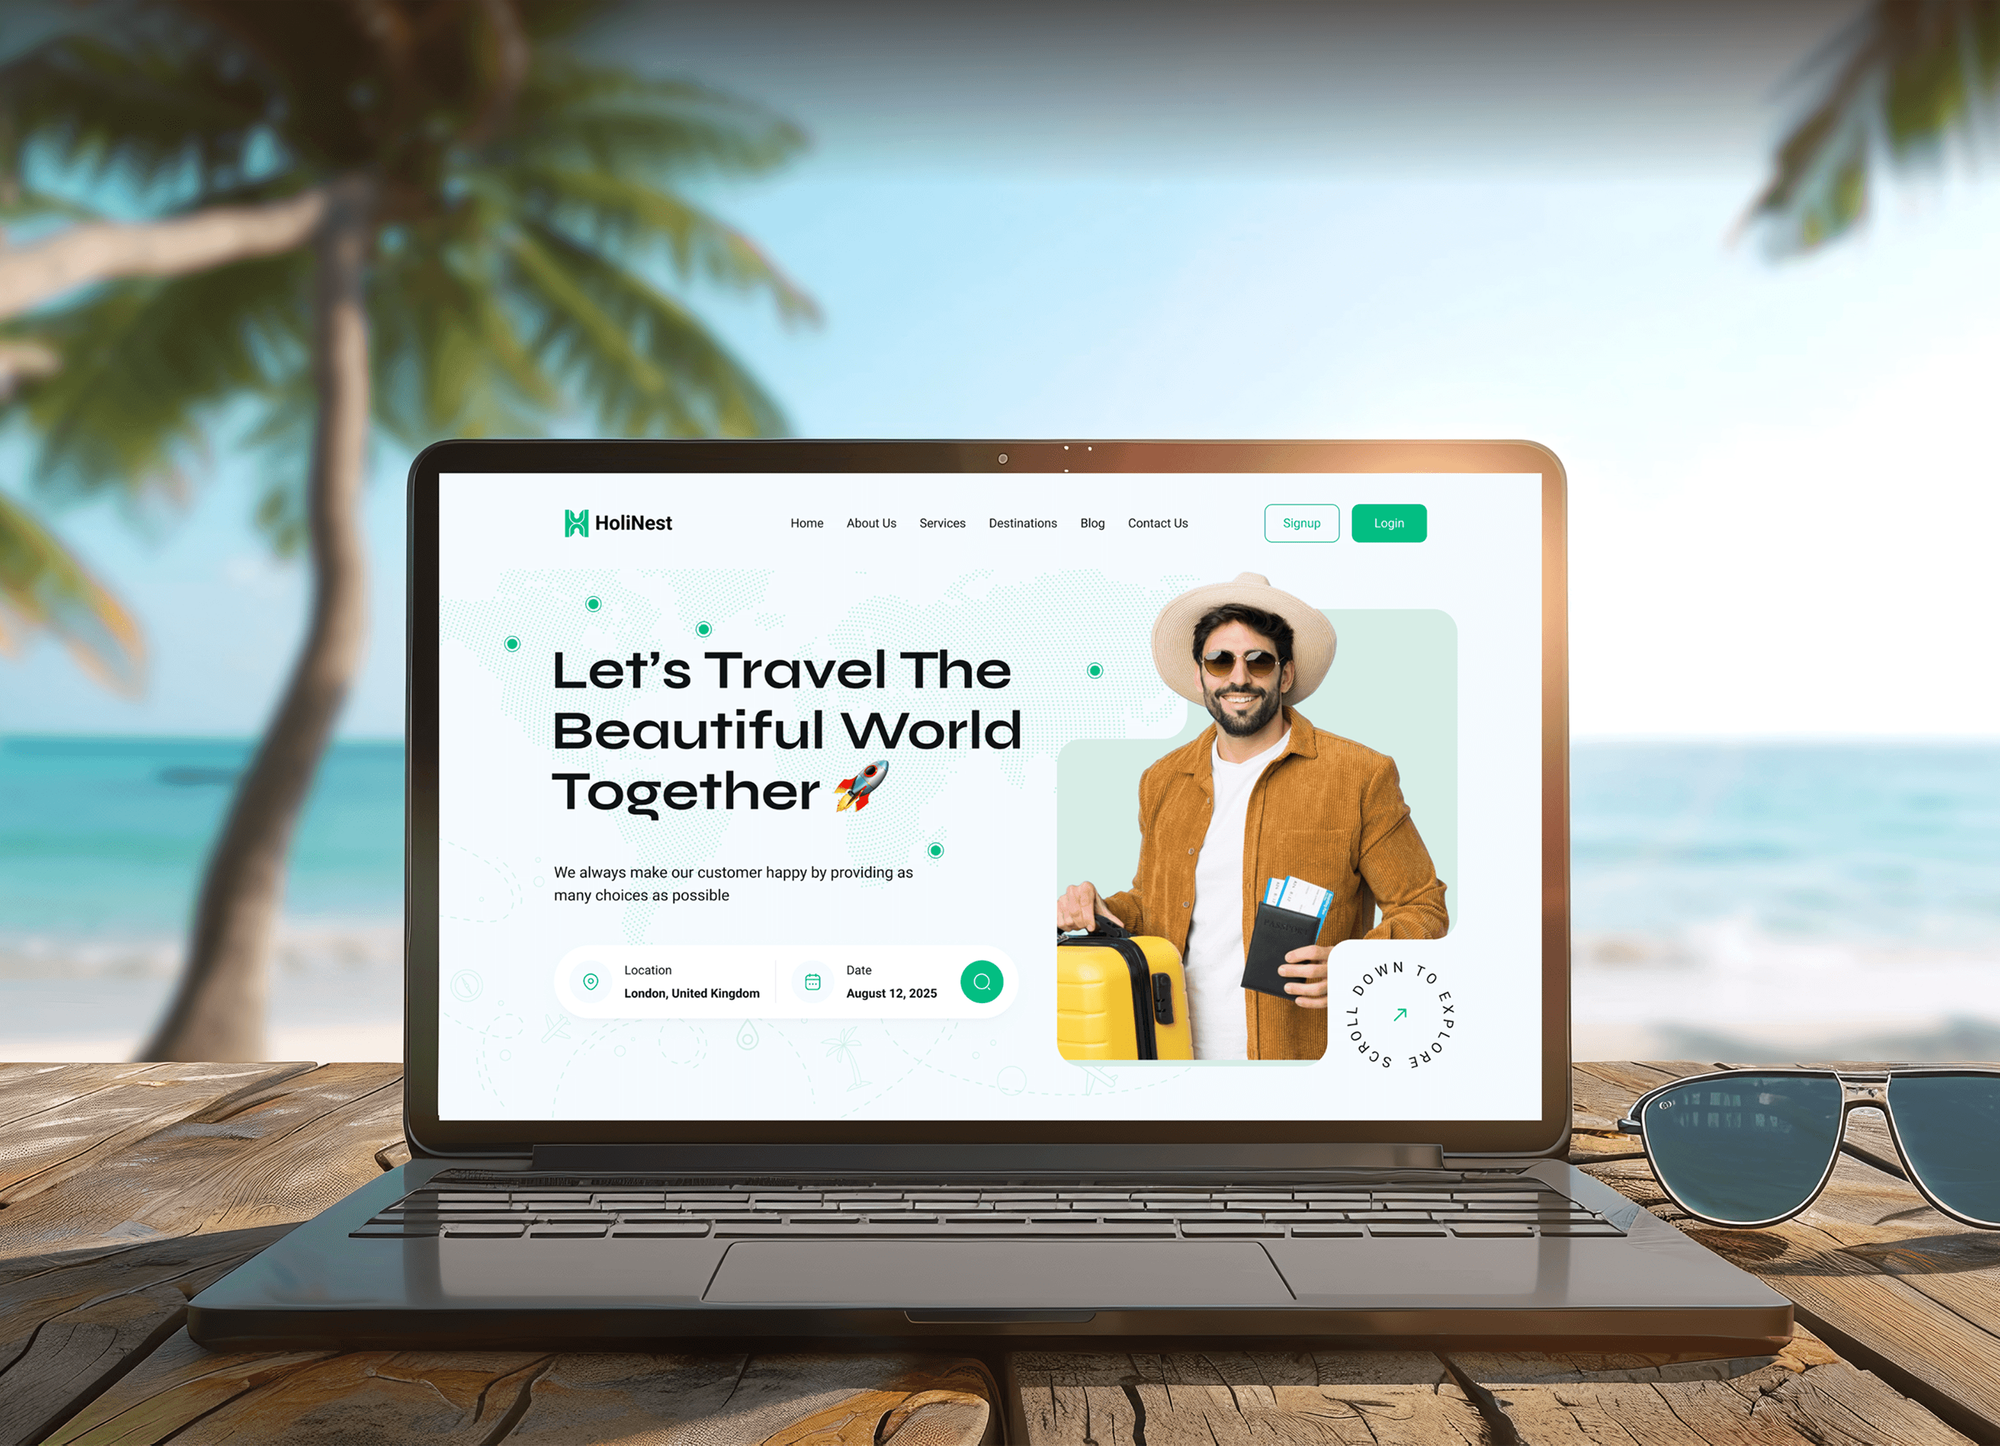
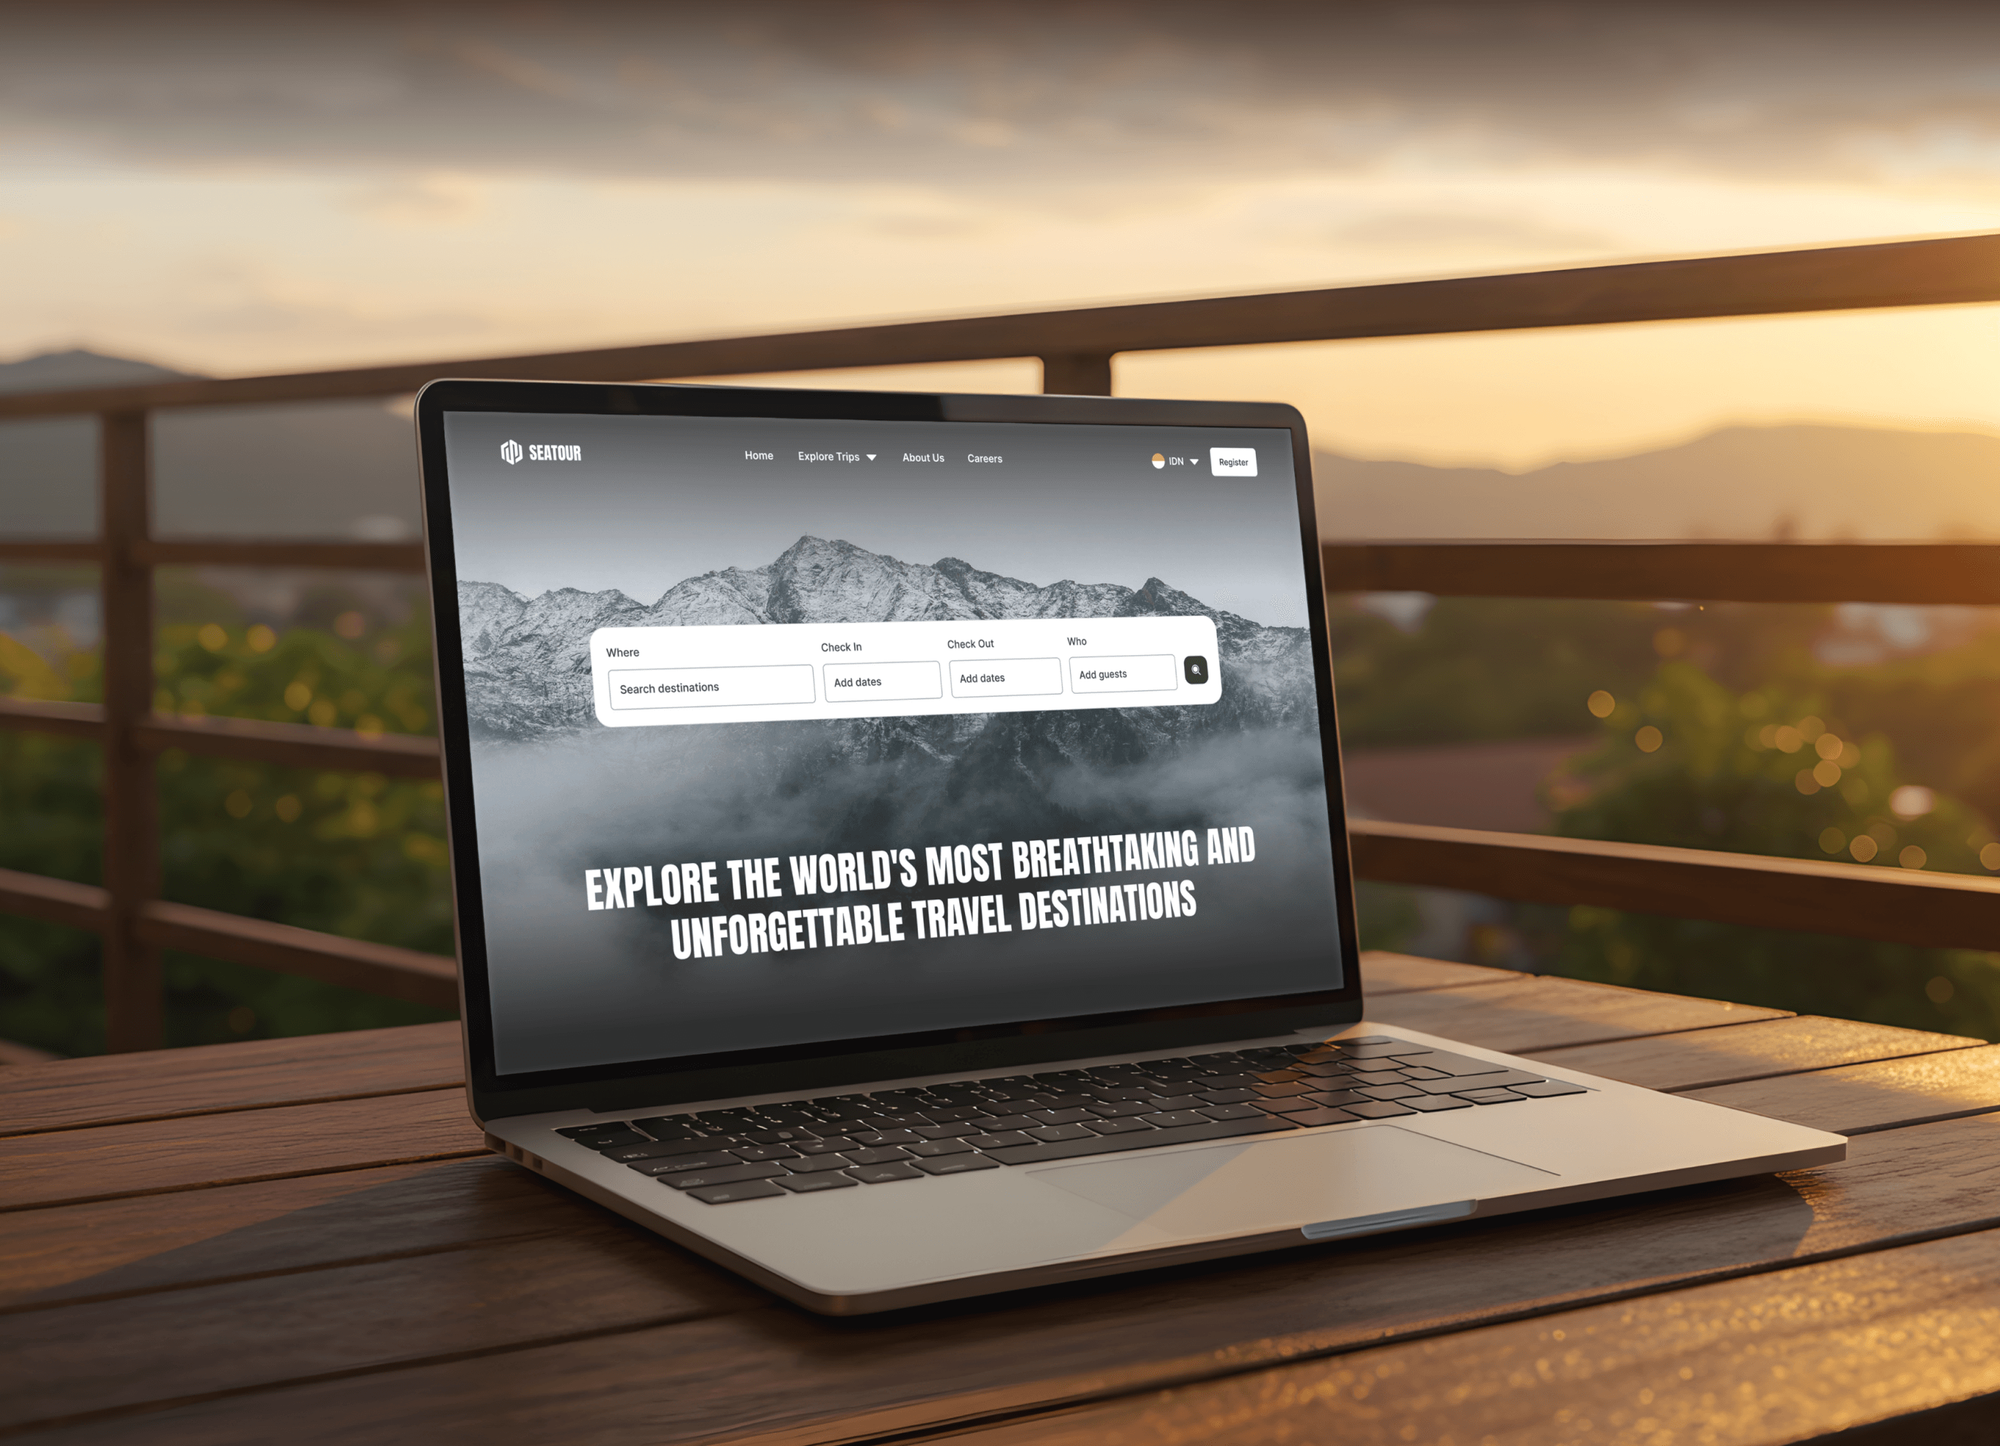
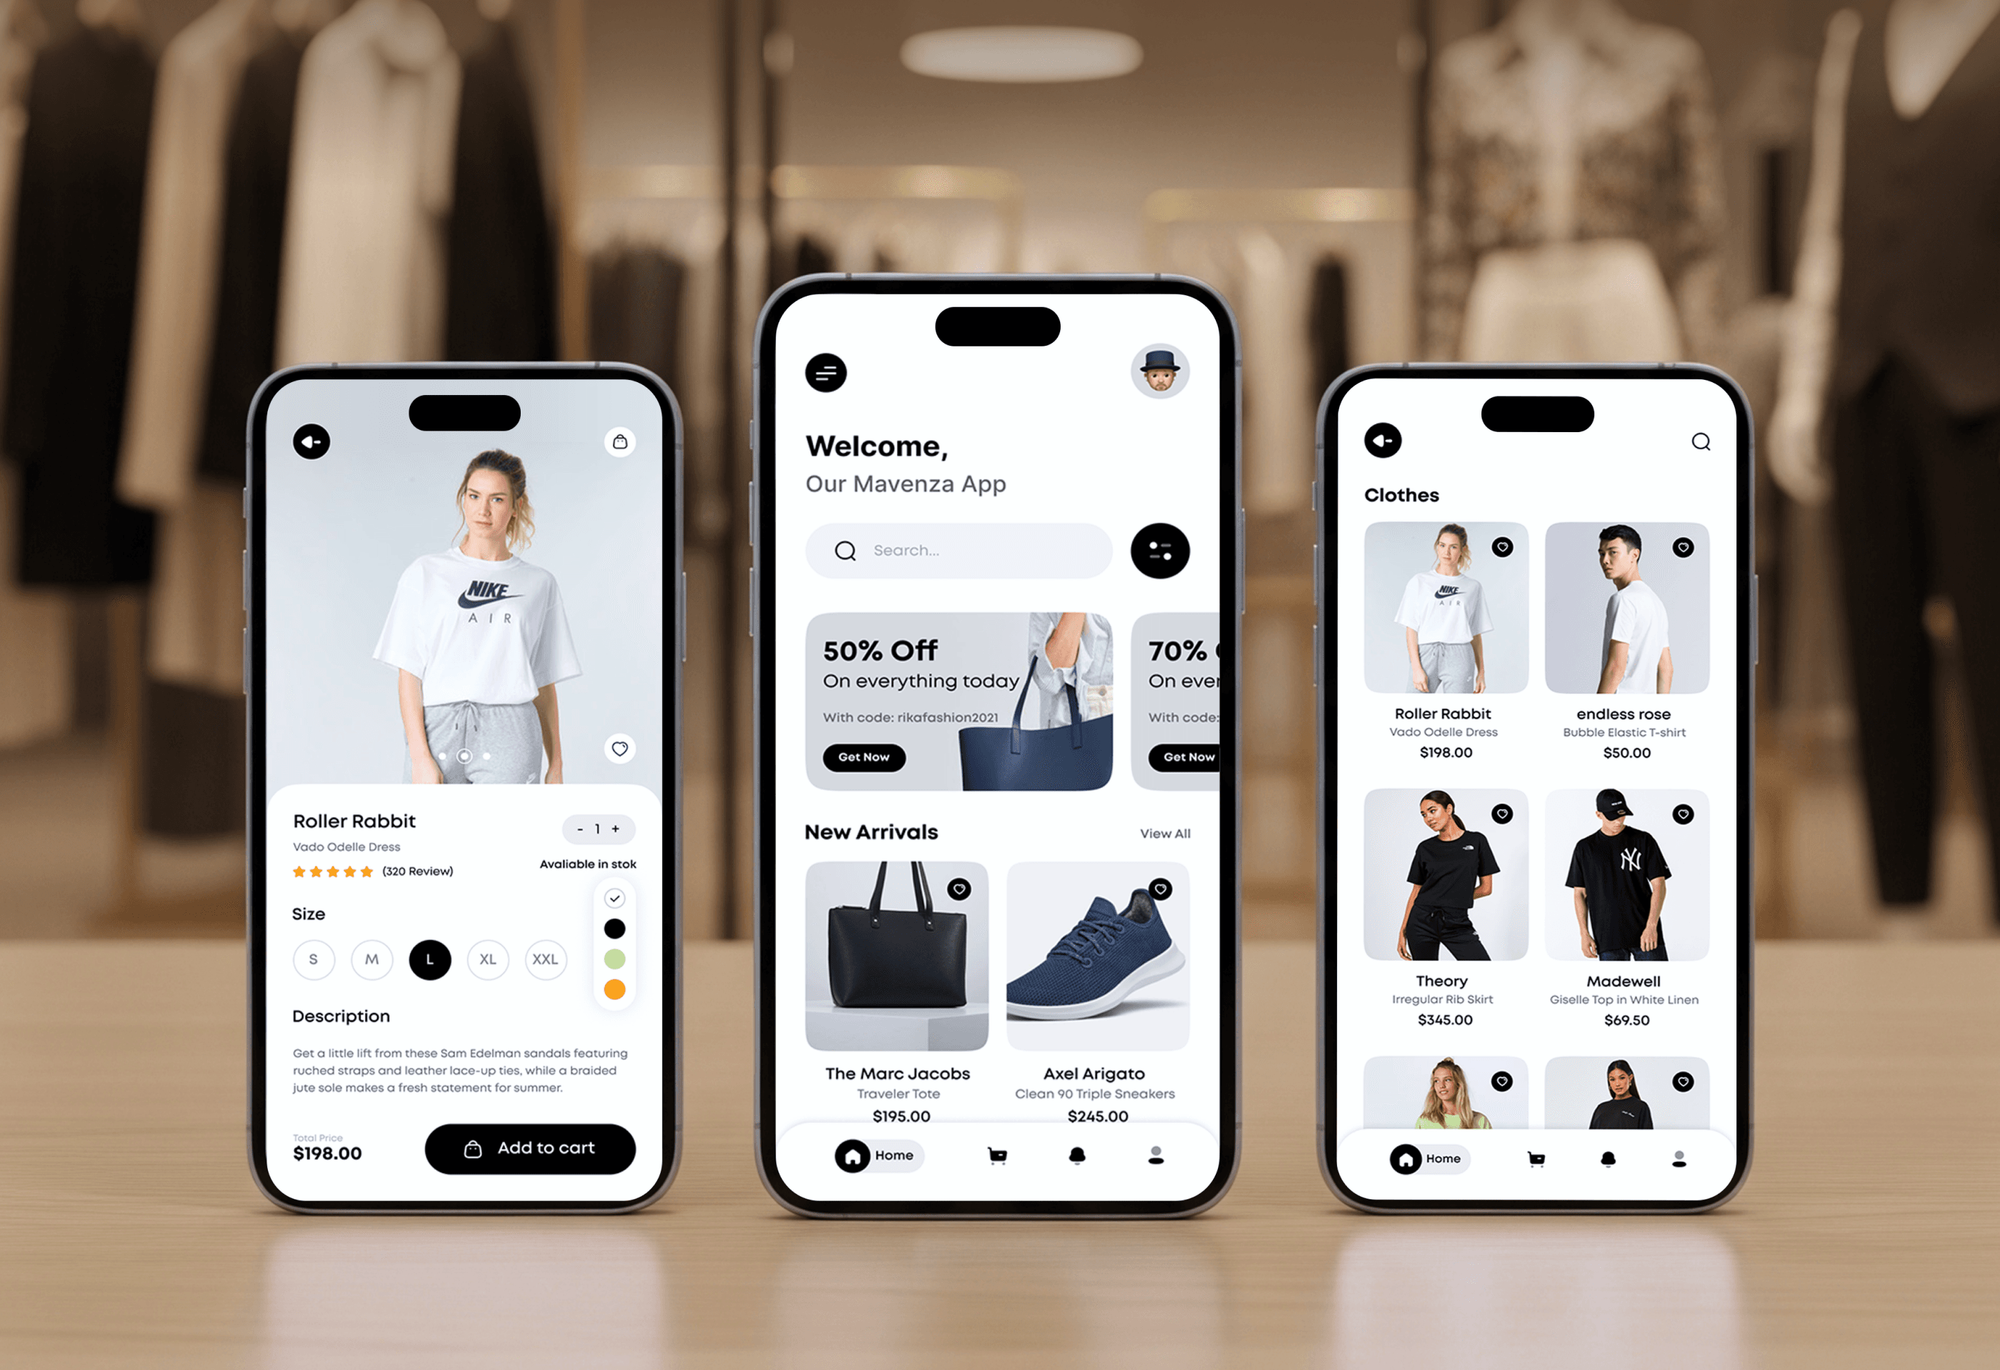
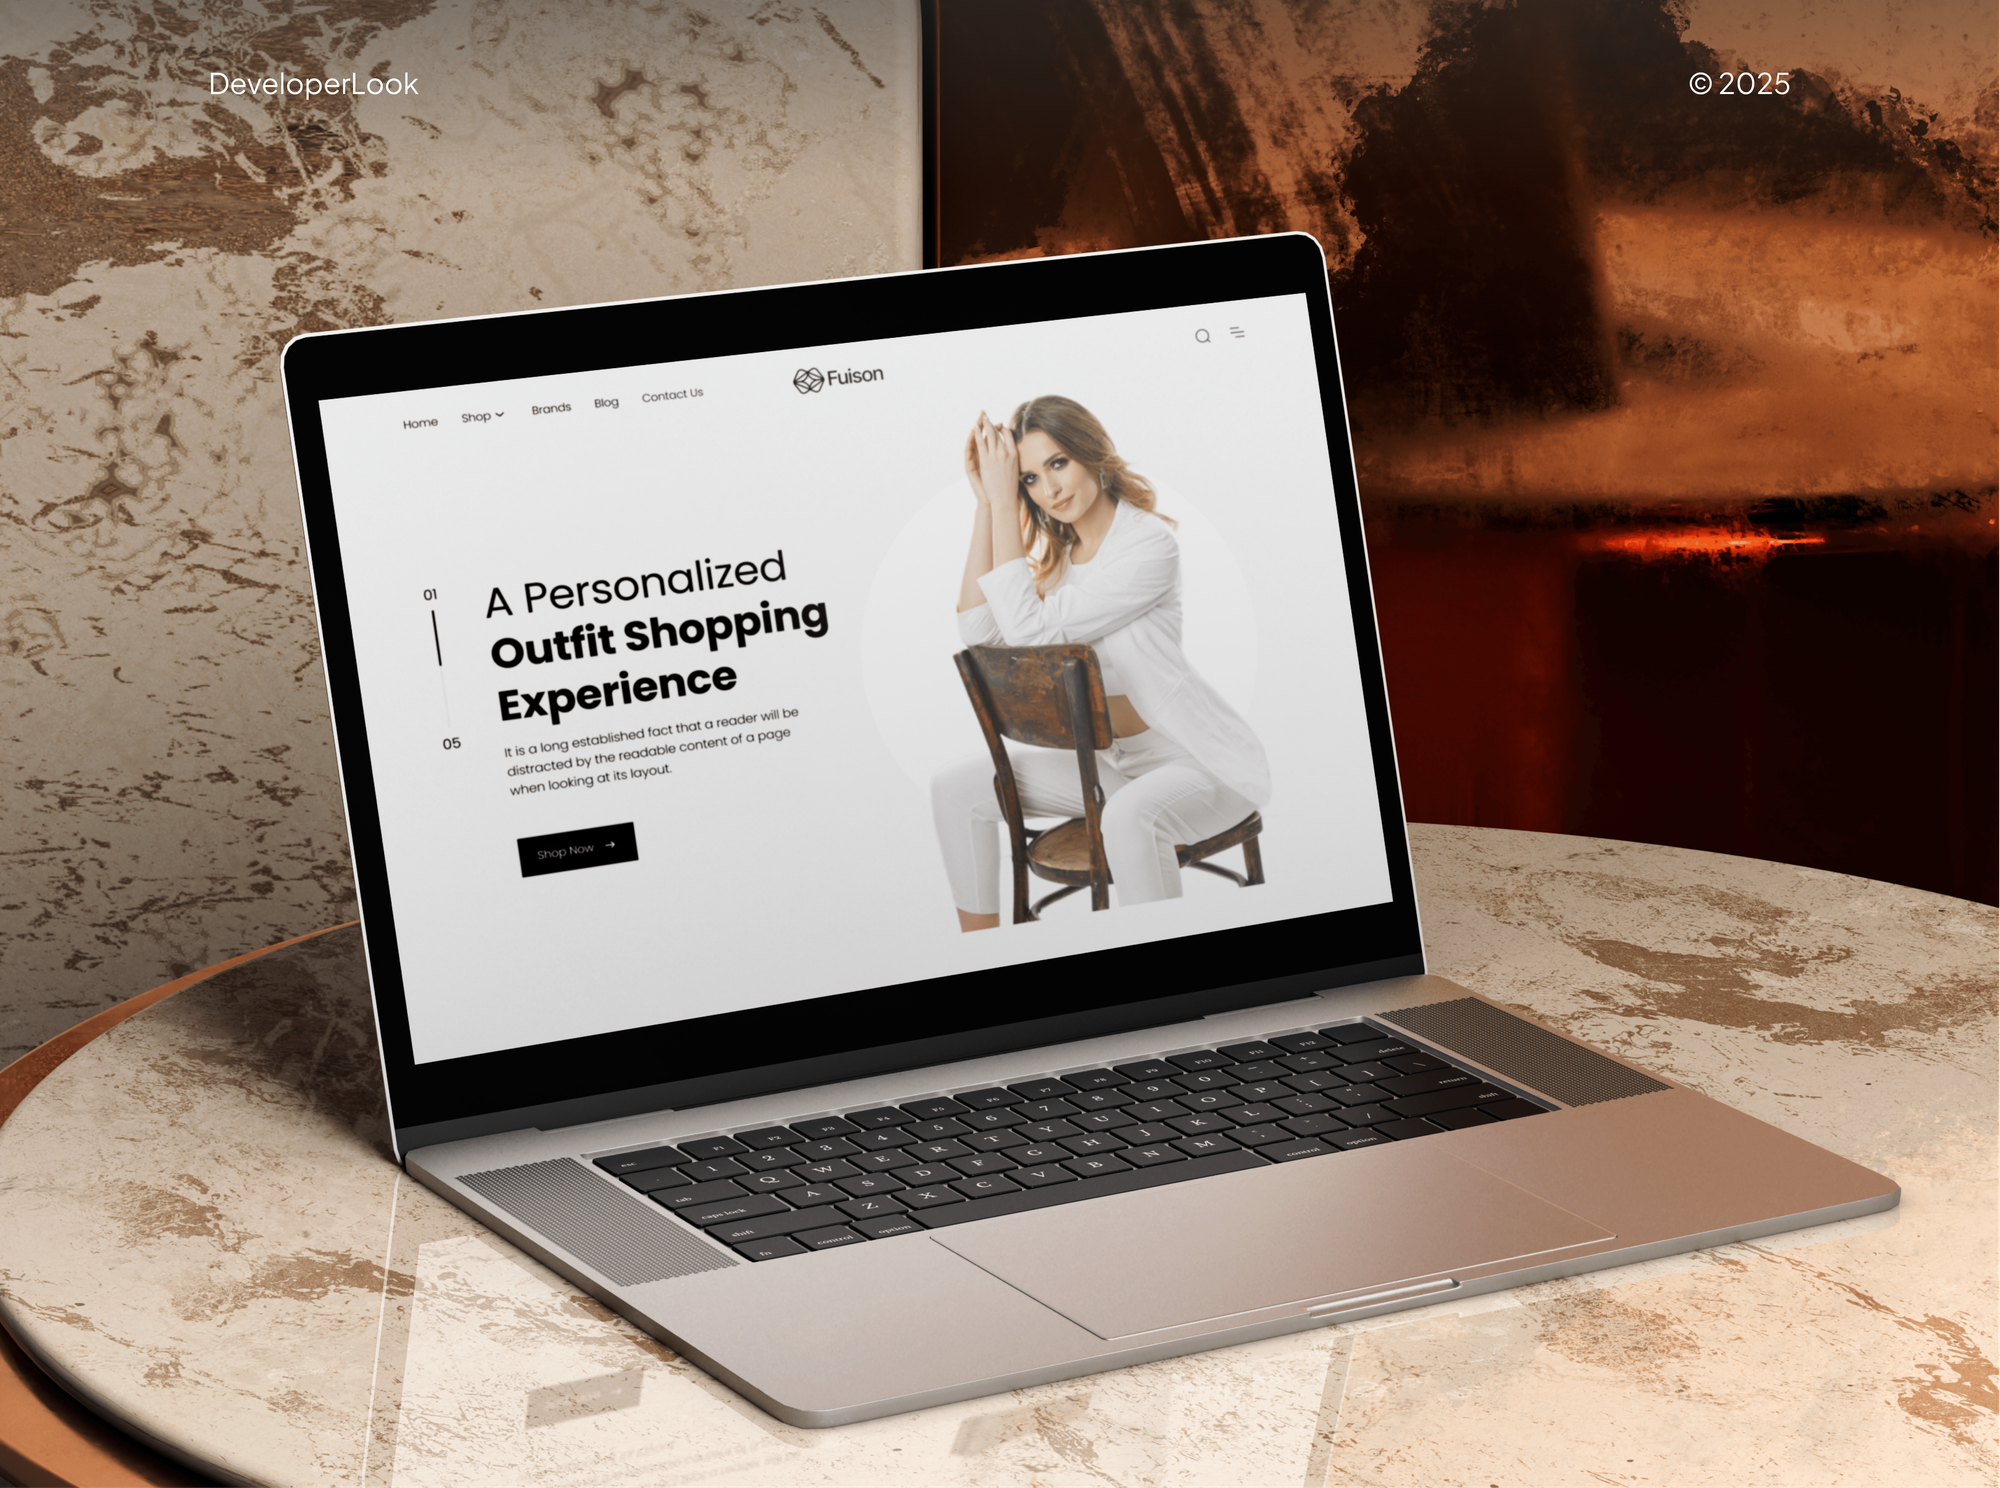
Booking platforms and store dashboards we built for travel and fashion brands. Systems like these write the sign-in, payment, and admin logs a SOC reviews.
What Our Clients Say
Feedback from teams we have built apps, platforms, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
A SOC sees your sign-ins, mailboxes, and admin actions. These habits keep that view narrow, every action recorded, and your log bill predictable.
We collect the sources on your signed plan and nothing else. Message content and personal files stay out unless a case needs them and you agree.
Storage and ingestion costs sit on your own cloud bill, so we show them every month. Noisy sources get filtered before they inflate the invoice.
Our engineers triage on business days, and automated playbooks act at any hour. If you need people on shift overnight, we'll say so before you sign.
Each real alert becomes a case with a timeline, actions, and the decision you made. Auditors and insurers can follow the trail later.
Workspace, rules, playbooks, and history stay in accounts you own. If you change providers, the next team starts with everything we built.
When a case points to a misconfigured server or a weak policy, our engineers fix it. You don't get a ticket telling you to find someone else.
Overview
DeveloperLook runs SOC as a service for growing companies that need security monitoring without hiring a SOC team. We set up Microsoft Sentinel or Wazuh in your own cloud, connect your logs, write detections, triage alerts on business days, and keep audit evidence. Plans start at $800 per month, with setup in 2 to 4 weeks.
DEVELOPERLOOK
Project facts · SOC as a Service
Reviewed 22 Oct 2026 by Saimul Islam
Good fit
Companies facing their first audit
Your SOC 2 or PCI DSS audit needs a year of access logs and proof that someone reviews alerts, and today neither exists.
Microsoft-based teams wanting a managed SOC
You run Microsoft 365 and Azure, and you want a managed SOC built on Sentinel in your own tenant rather than a provider's portal.
SaaS firms answering security reviews
Your enterprise customers ask who monitors your security logs, and you need SOC services you can describe honestly in their questionnaire.
Teams leaving their current provider
You're tired of soc managed services that keep your logs in their system, and you want detections and history you can take with you.
IT leads comparing quotes
You're comparing managed soc providers on what's included and want managed SOC pricing you can explain to finance line by line.
Not a fit
Need analysts on shift overnight
You need people watching logs at night with a contracted response time. A large provider with round-the-clock staff fits better, and we'll help you compare quotes.
Mainly worried about laptops
Your worry is laptops and servers, not logs from every system. Our managed detection and response service covers EDR alerts from $600 a month.
No security basics yet
You don't have MFA, device protection, or email security in place yet. Our managed security services set that base first, from $850 a month.
Budget under $800 a month
Your budget is under $800 a month and you run only a couple of systems. Turning on the alerts built into Microsoft 365 or Google Workspace is a sensible start.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are monthly starting points in USD. Your plan depends on log sources, retention, and detection work, and you get a fixed proposal after a free scoping call.
For small teams that need core logs collected, watched, and kept for audits.
$800/month
For growing companies with servers, cloud accounts, and a VPN to watch.
$1,350/month
For companies with up to 15 log sources and formal audit or customer requirements.
$2,100/month
For Agencies
You own the client relationship. We run the security operations behind it: log platforms in each client's cloud, detections, daily triage, and monthly reports in your format. Your clients get a SOC without you hiring analysts.
White label: your client only ever sees your brand
Send the client's systems, audit needs, cloud accounts, and escalation contacts.
You get a log source plan, a storage cost estimate, and a fixed monthly price.
We set up the platform, triage alerts, and report monthly in your template.
You present the reports while we triage quietly under your brand.
Each client's logs stay in their own tenant and never mix.
Monthly SOC reports written in your format and wording.
Add log sources and clients as your security offer matures.
The Right Technology for Your Project
We build on log platforms you can own outright and connect the sources you already run. Detections follow MITRE ATT&CK, so coverage is easy to explain to auditors.
 AWS CloudTrail
 Google Sheets
FAQ
Straight answers on pricing, setup, what a managed SOC does, choosing a provider, and coverage hours.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
DeveloperLook's SOC as a service starts at $800 per month for up to 3 log sources, daily triage, and 12-month retention. The $1,350 plan covers 8 sources with custom detections and monthly tuning. The $2,100 plan covers 15 sources with compliance reports and runbooks. Log storage is billed separately by your cloud provider, and we estimate it before you sign.
SOC setup with DeveloperLook usually takes 2 to 4 weeks. The first one or two weeks deploy the log platform and connect your sources. The next one or two weeks switch on and tune detections, and triage starts once noisy rules are under control. Adding a source later takes a few days, depending on the system.
A managed SOC is a security operations center run by an outside team, sometimes sold as security operations center as a service. It combines people, process, and tools that watch logs and respond to alerts. The provider handles detections, triage, and case records, while you keep decisions about your systems. Ours runs on a platform in your own cloud.
SOC services are the daily jobs of a security operations center: collecting logs, writing detections, triaging alerts, investigating incidents, and reporting. A full SOC also covers threat intelligence and hunting for attacks that slipped past rules. Smaller companies usually buy these jobs as a subscription, because staffing them in-house takes several full-time roles.
Start with a short checklist: included log sources, coverage hours, who owns the platform and logs, retention, and what happens when an alert is real. Then compare quotes on the same scope, because some providers price per device and others per gigabyte of logs. Ask whether storage costs sit inside the quote or on your cloud bill.
Evaluate threat hunting by asking how often a provider hunts, what it looks for, and what you receive afterwards. Good hunts start from a hypothesis tied to MITRE ATT&CK techniques, use your own logs, and end with new detections or fixes. A provider that only reruns its standard rules is monitoring, not hunting. Our SOC Program plan includes a quarterly hunt.
A midsize business should weigh five criteria: tool fit, real coverage needs, log ownership, audit support, and total cost including storage. Check that the provider has worked with your identity and cloud platforms. Ask for a sample monthly report, then confirm how escalation reaches your on-call people at night.
Managed SOCaaS providers keep response timely with automation, runbooks, and clear escalation. Automated playbooks act on high-confidence alerts at any hour, runbooks tell analysts what to contain, and escalation lists say who to call. Ask each provider for its contracted response times in writing. DeveloperLook triages on business days and relies on automation outside them.
Choose one by asking who is awake at night: staffed analysts, an on-call engineer, or only automation. Ask for contracted response times, a sample incident report, and what the service may do inside your systems without asking. DeveloperLook doesn't staff a 24/7 SOC, and we'll help you compare providers that do whenever you need one.
Yes. The log workspace, detection rules, playbooks, and case history live in your own Azure tenant or server, never in ours. When you leave, we hand over documentation for every rule and source, then remove our named accounts. Your next provider or in-house team can keep running the same platform.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.