
Access inventory
Every app, account, and admin role listed against your HR records, so orphaned and shared accounts surface.

For IT leads at 50 to 500 person companies who want one login per person, MFA on every app, and access that ends when someone leaves.
100%
Accounts matched to an owner
1login
Per person in every connected app
How your project runs
Teams we have built for:














The Problem
It shows up when an auditor asks for an access list, an old contractor account turns up active, or a new hire waits days for logins.
01 · Leavers
Former staff can still log in to the CRM months later.
Leaver steps disable the account in every connected app from one place.
02 · Shared admins
Three people share one cloud root login.
Each admin gets a named account, scoped rights, and phishing-resistant MFA.
03 · Onboarding
New hires wait days while access requests bounce around email.
Roles grant the right apps automatically when HR adds the new hire.
04 · Audit evidence
The access list for auditors is a spreadsheet nobody trusts.
Scheduled access reviews leave signed records your auditor can read.
Your company added apps as it grew: a CRM, a finance tool, a cloud console the developers set up themselves. Each keeps its own passwords and admins. A sales rep who left in spring can still log in to the CRM. Three people share the AWS root login. New hires wait days for access while requests bounce around email. When the auditor asks who can reach customer data, the honest answer is a spreadsheet nobody trusts. Without an IAM program, every new tool adds another door you can't see.
We start with an access inventory: every app, account, and admin role matched to your HR list. Then one identity provider becomes the source of every login, apps connect through SAML or OpenID Connect, and accounts follow joiner, mover, and leaver events. Admins get separate accounts with phishing-resistant MFA. Access gets reviewed on a calendar, not after an incident.
Every account accounted for
Each login in each app is matched to a person, a role, and an owner.
One identity per person
A single provider handles sign-in and MFA for every app you connect to it.
Clean exits
Departing staff lose access to every connected app from one action in your identity provider.
Our Identity and Access Management Services Process
You see the inventory, approve the design, and watch every login change go to a pilot group before anyone else is affected.
We walk through your apps and how people join and leave today. You get a short list of the riskiest gaps. If your Microsoft 365 or Google Workspace plan already covers what you need, we'll tell you before we quote.
What's Included
An access inventory, a ranked risk list, one identity provider for every login, automated joiner and leaver steps, tighter admin rights, and a first access review.
Compare Options
Most identity and access management companies sell a platform or a monthly seat. Both suit some teams. Here is where each one stops.
| Feature | DeveloperLookBest fit | Platform vendor | Managed IT provider |
|---|---|---|---|
| Starting point | Access inventory before any tool | Their product's setup wizard | Tickets as they arrive |
| Vendor choice | Neutral across Entra, Okta, Google | Their platform only | Whatever they resell |
| App connections | SSO for the apps you use | Fast for gallery apps | Common apps only |
| Leaver removal | Driven by HR events | Possible with higher licenses | Manual, on request |
| Admin accounts | Separate, phishing-resistant logins | Feature exists, setup is yours | Shared admin logins common |
| Access reviews | First review run with you | Reports you run yourself | Rarely offered |
| Getting started | 4 to 10 week rollout | Quick start for simple setups | Included in a support contract |
| Cost model | Fixed project price | Per-user license | Monthly per-seat fee |
Projects We've Built
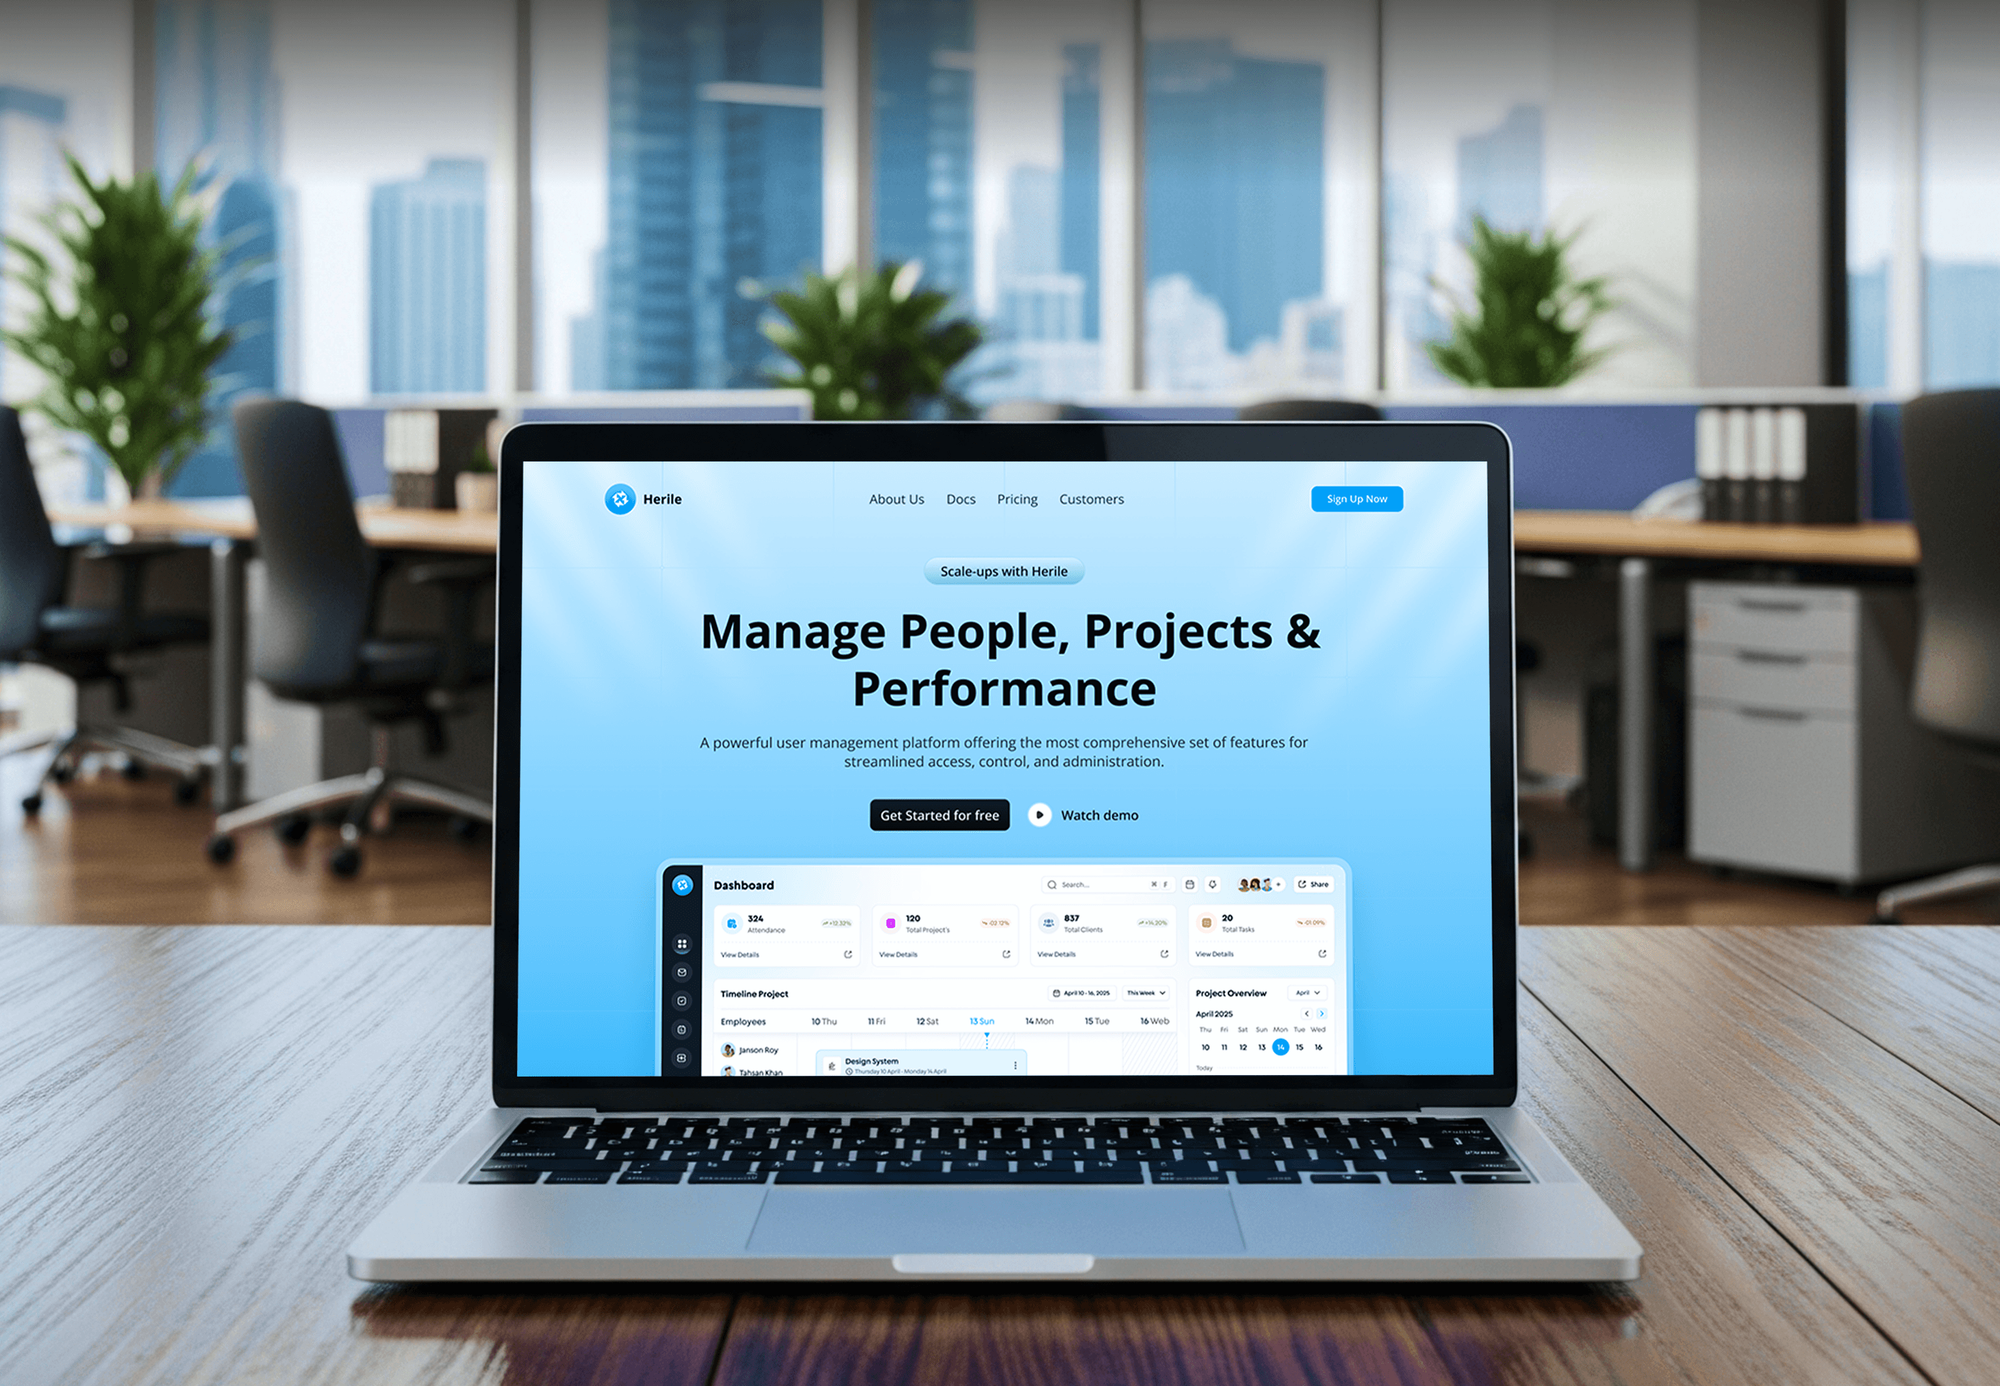
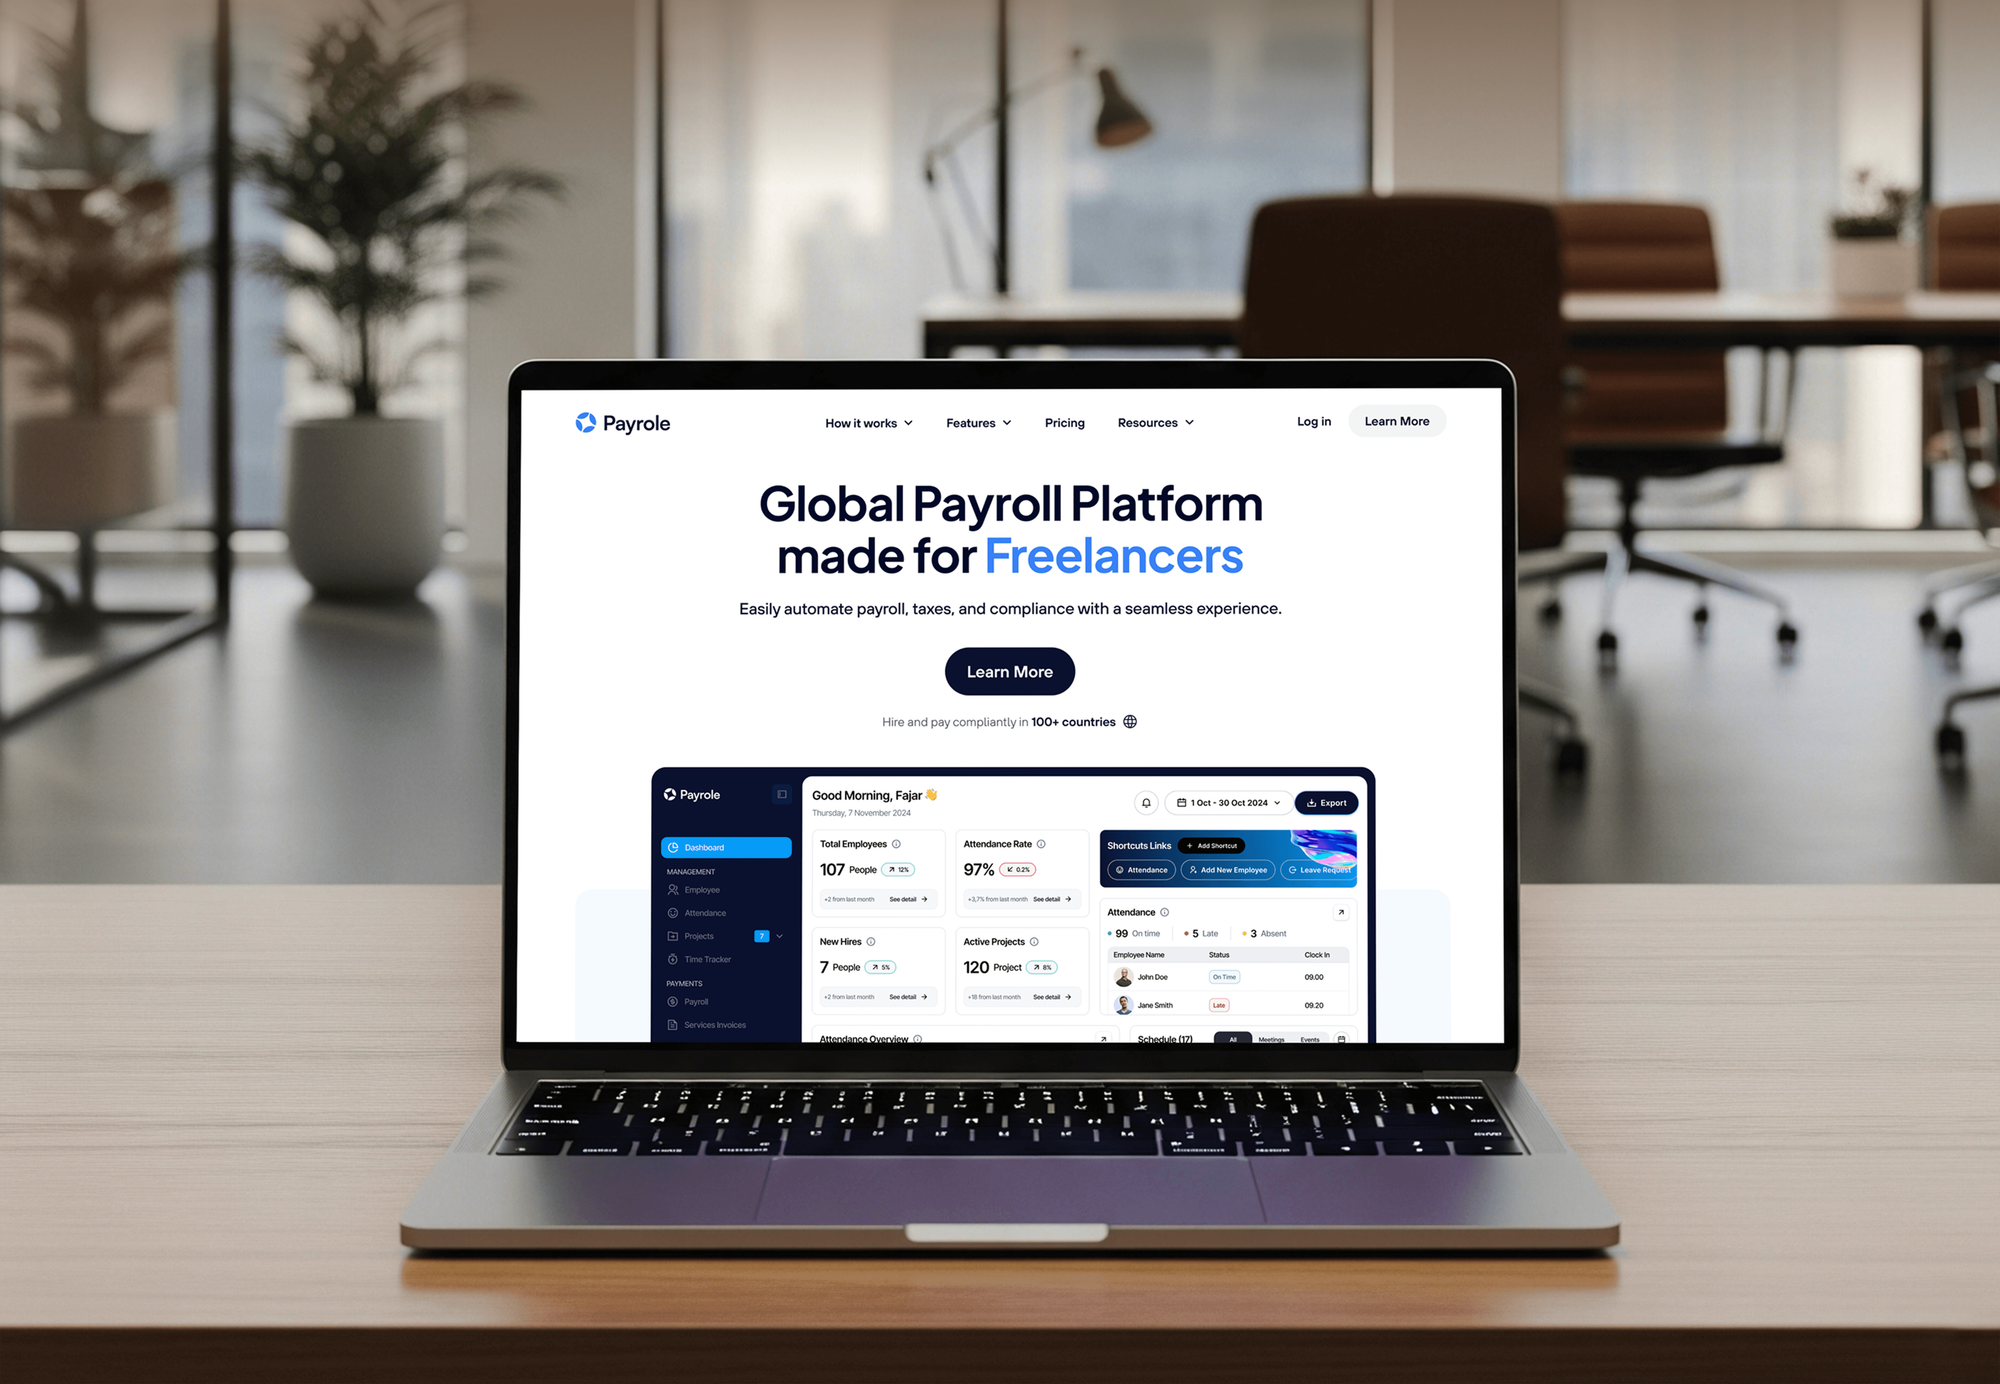
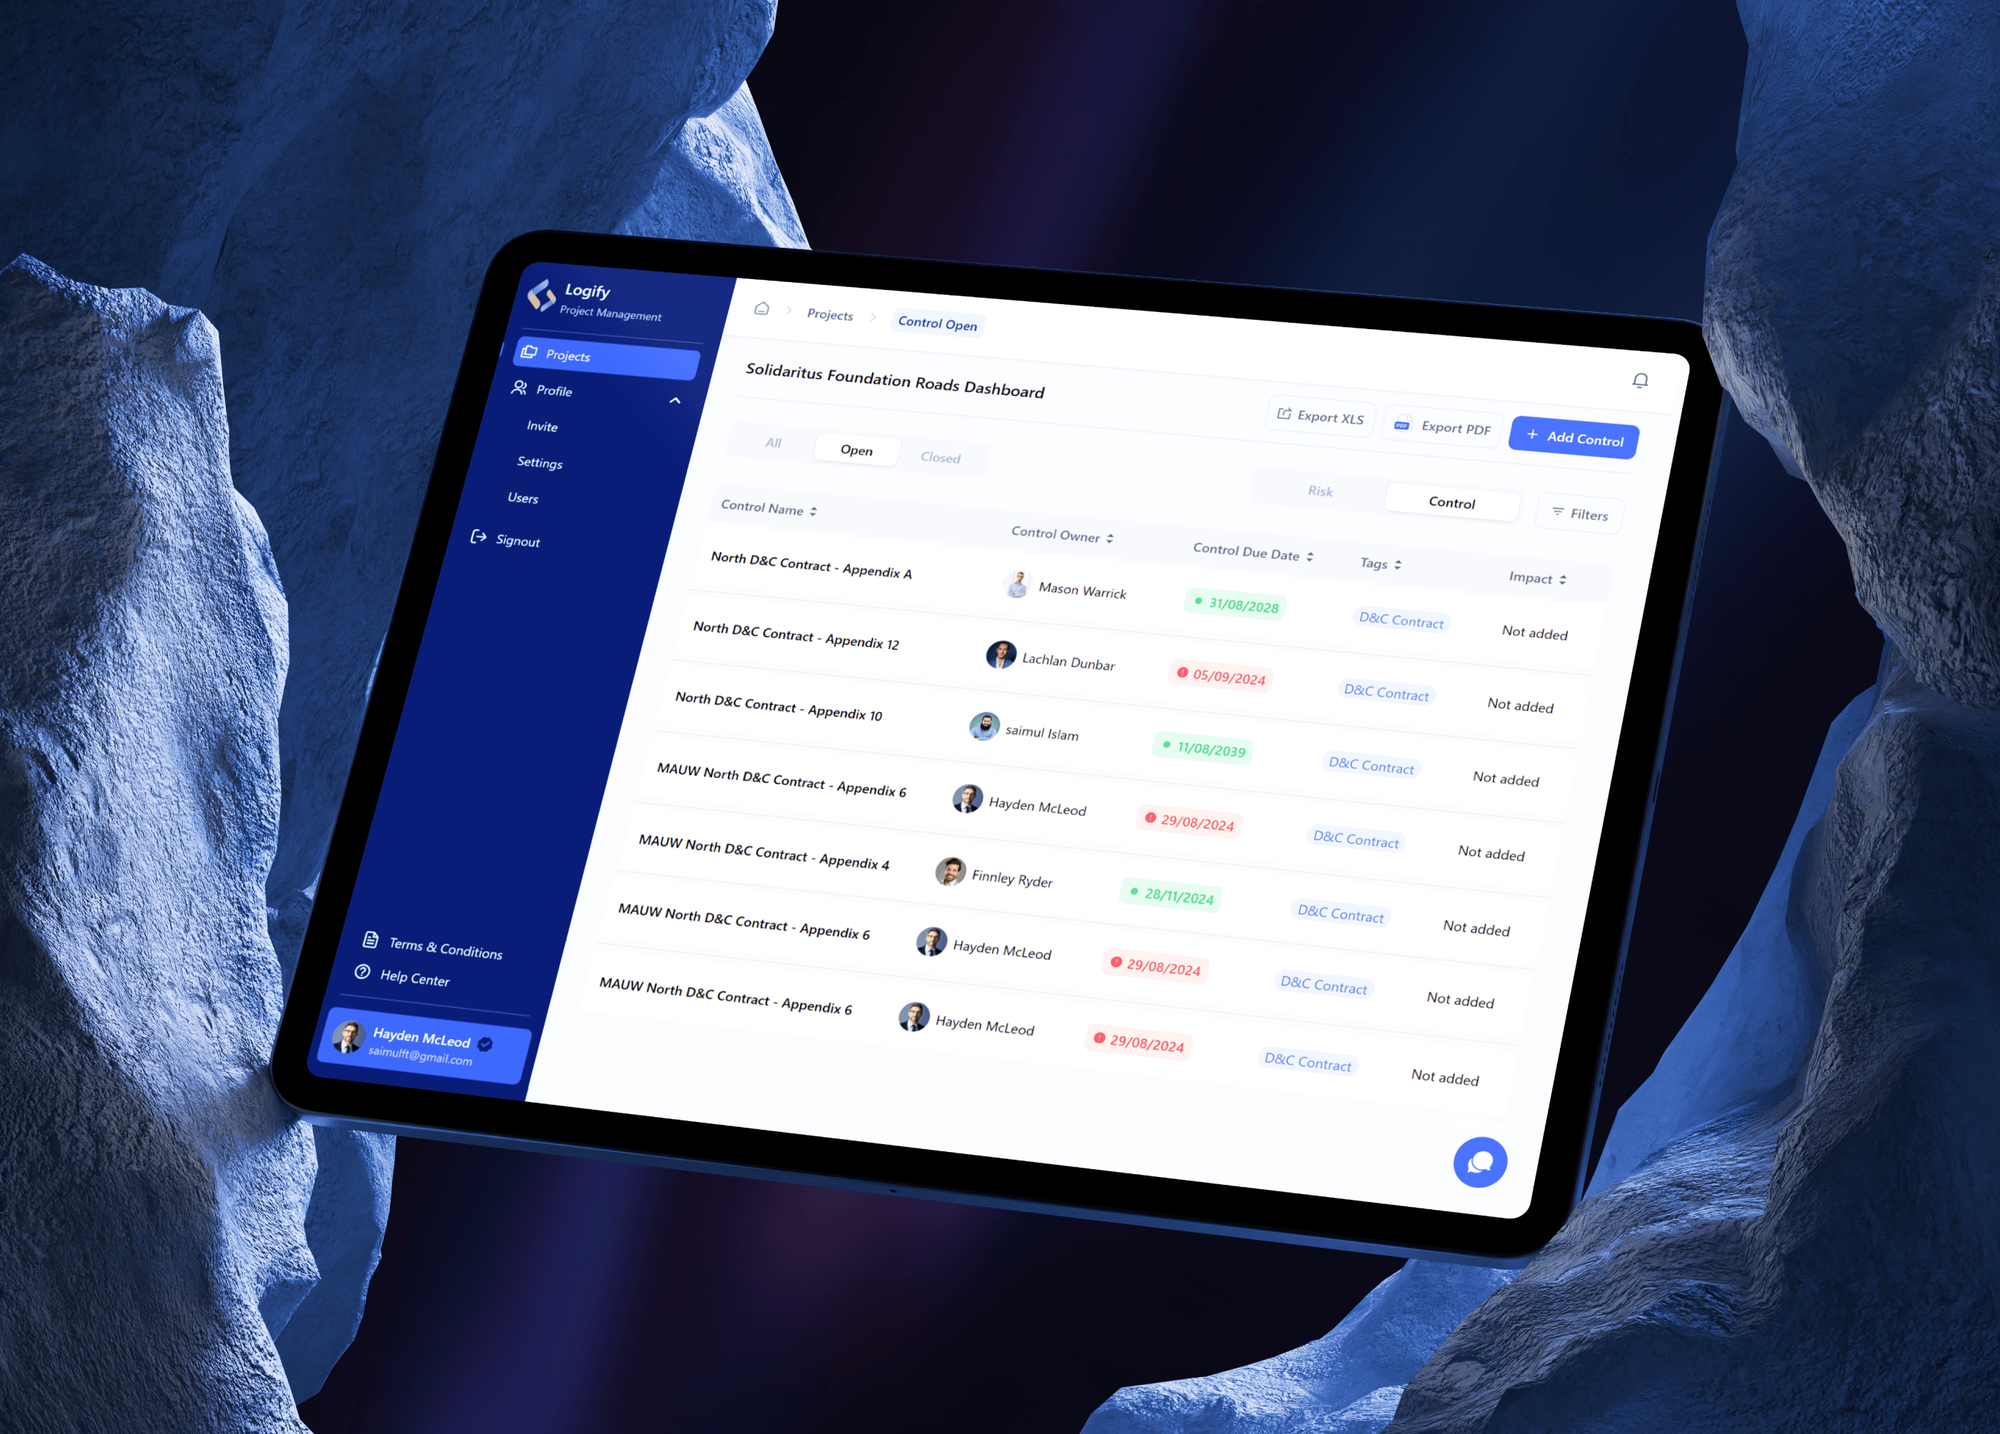
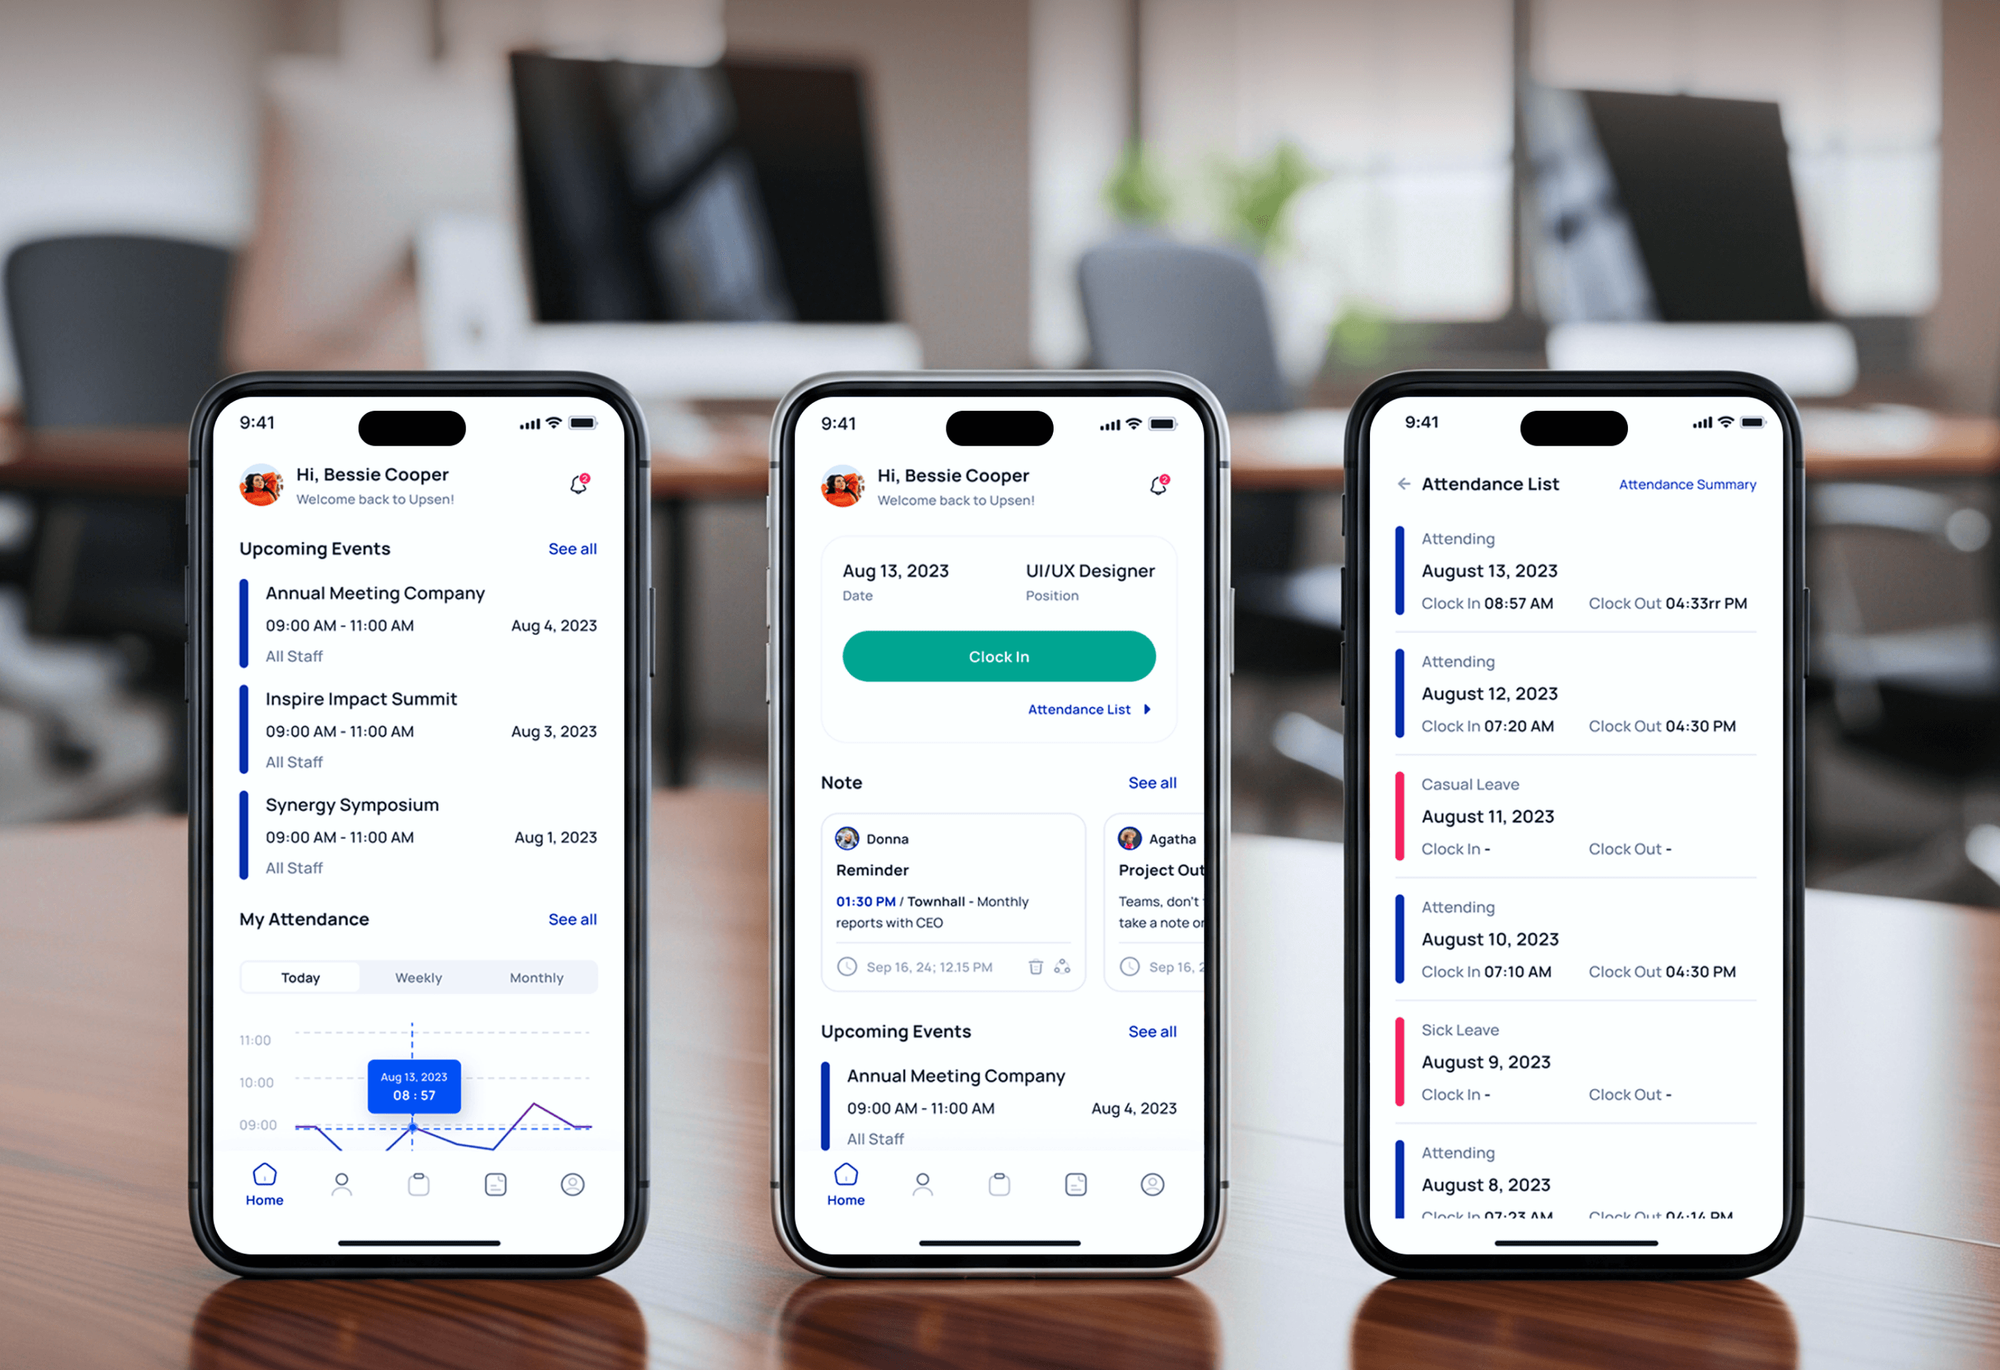
HR, payroll, and project control platforms we designed and built. Systems like these hold employee records and admin roles that an access review covers.
What Our Clients Say
Feedback from teams we have built platforms, apps, and websites for.
We had a pretty specific idea of what we wanted our website to become, but I wasn’t sure how easily we could explain all of it to a development team. There were quite a few moving parts, and we were working toward a deadline, so I expected a few things to get lost along the way. That never really happened. They understood what we were trying to achieve, kept us updated throughout the process, and got everything ready within the agreed timeline. The final site feels much easier to navigate, works beautifully on mobile, and is noticeably smoother for our customers. It was a huge relief seeing the original idea actually turn into the website we had in mind.
The mobile experience is probably my favourite part of the new site. We had spent a lot of time making sure the desktop version looked right, and the team kept pushing us to think about how everything would actually feel on a phone too. They were right. The navigation is clean, the interactions feel natural, and everything we’ve tested so far works exactly as it should. They also went through the links, forms, integrations, and other details more than once before launch, which I really appreciated. And even after going live, we could still reach out when something came up. The whole process felt friendly, organised, and surprisingly straightforward.
What I appreciate most is that the website is actually easy for us to manage now. We can update content ourselves instead of sending a developer a message every time we need to change something small. They also paid attention to the technical SEO side, which mattered to us because we didn’t want a new website to create problems for the traffic we already had. I’ve probably asked more questions than I should have since launch, but every question has been handled patiently and without any fuss. The team is easy to work with, they explain things clearly, and when we need something changed, they focus on getting it done rather than making the process complicated.
1,250+
Projects shipped
10+
Years of experience
Top 3%
Upwork Top Rated Plus
5 stars
Average review score

Want results like these?
Tell us what you are building. You get a reply within 24 hours on business days, then a written estimate.
Work Culture
IAM work touches every login in your company, so we move in small, reversible steps and write everything down.
We find every account before we recommend a product. Identity projects stall when nobody knows which apps exist, so we start from your real list.
We work with Microsoft Entra ID, Okta, and Google Workspace and don't resell licenses. You get the platform that fits your apps and budget.
Every login change goes to a small pilot team before the whole company. Problems show up with five people, not five hundred.
We set up two break-glass admin accounts kept out of normal sign-in policies. If your identity provider has an outage, you can still get in.
Each rollout wave comes with a one-page note for staff. That means fewer help desk tickets and fewer people locked out on Monday.
Admin rights, settings, and runbooks stay in your tenant under your accounts. If we part ways, nothing breaks and nothing needs handing back.
Overview
DeveloperLook provides identity and access management for companies of 50 to 500 people, from risk assessment to rollout. We inventory every account, design roles, connect apps to SSO and MFA in Entra ID, Okta, or Google Workspace, and automate leaver removal. Projects start at $1,050, roll out in 4 to 10 weeks, and stay vendor-neutral.
DEVELOPERLOOK
Project facts · Identity and Access Management Services
Reviewed 23 Oct 2026 by Saimul Islam
Good fit
Companies of 50 to 500 staff
Your team grew app by app, and nobody can say who still has admin rights in Salesforce, AWS, or the finance system.
IT leads facing a SOC 2 audit
Your auditor wants proof of access reviews and leaver removal, and today that proof lives in spreadsheets and memory.
Teams moving to one identity provider
You're consolidating Google and Microsoft logins, or moving to Microsoft Entra ID or Okta, and need an identity and access management strategy first.
Companies after an access scare
Your former contractor's account was still active months later, or a shared admin password leaked, and leadership wants it fixed properly.
MSPs and IT agencies
You manage Google Workspace and Microsoft tenants for clients and want an identity and access management consultant to design the baseline you roll out.
Not a fit
Team under 10 people
You're a team of under 10 on one suite. Built-in MFA and security defaults cover most of your risk, and our cybersecurity services review is the lighter fit.
SSO inside your own product
You want your customers to sign in to your SaaS with their company login. That's product work, covered by our SSO integration service, not a workforce IAM program.
Whole security program first
You need a risk register across email, devices, cloud, and vendors before deciding where identity fits. Start with cybersecurity consulting, then bring the identity work here.
Looking for a license reseller
You only want to buy identity platform licenses at a discount. We don't resell, so the vendor or a licensing partner is the better place to buy.
Not sure we're the right fit?
Book a free call or message us. We'll tell you honestly whether we're the right team.
Pricing
These are starting points in USD. Your final price depends on the apps and users in scope and whether your HR system can drive accounts. You get a fixed proposal after a free access review.
For companies that need a clear picture of who can access what before choosing tools.
$1,050one-time, USD
For teams of up to 200 people moving every app to one identity provider.
$3,050one-time, USD
For organizations of up to 500 people that need HR-driven accounts and audit-ready reviews.
$6,300one-time, USD
For Agencies
You own the client relationship. We supply the identity work behind it: access inventories, identity provider setup, and leaver workflows in each client's tenant. It's documented in your format, so you don't need an identity specialist on staff.
White label: your client only ever sees your brand
Send the client's user count, apps, identity provider, and the problem to fix.
You get an access inventory plan and a fixed price to present under your brand.
We configure, pilot, and document, while you keep the client relationship.
You run the client calls while we build quietly under your brand.
The same tested policy set, adjusted to each client's apps and licenses.
People who have rolled out SSO and MFA across many company tenants.
Take on identity projects in busy months without making a new hire.
The Right Technology for Your Project
We work in the identity platform you already pay for where it fits, and use open standards so apps stay portable.
FAQ
Straight answers on what IAM is, why it matters, how it's rolled out, and what it costs.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
DeveloperLook's IAM projects start at $1,050 for a risk assessment covering up to 25 apps. The $3,050 Identity Rollout adds SSO and MFA for up to 15 apps and 200 people. The $6,300 Full IAM Program covers up to 40 apps, HR-driven accounts, and a first access review. You get a fixed quote after the free review.
Most IAM rollouts take 4 to 10 weeks after a 1 to 2 week assessment. A team of 100 people with 15 apps usually lands near the short end. HR-driven provisioning, older apps without SAML or OpenID Connect support, and staff spread across time zones push it toward 10 weeks.
Identity and access management is the set of policies and tools that decide who someone is and what they can open. In practice it covers one login per person, MFA, roles that grant the right apps, and removing access when someone leaves. Most companies run it from an identity provider such as Microsoft Entra ID, Okta, or Google Workspace.
It matters because every app, file, and admin console is reached through an account. When accounts are shared, left active after exits, or guarded only by a password, one phished login can open payroll and customer data. IAM gives you one place to require MFA, grant access by role, and switch everything off.
You need it because a Microsoft 365 or Google login only covers that suite. Your CRM, accounting tool, and cloud console each keep their own passwords and admins. An IAM setup connects them to the same identity, so MFA, roles, and leaver removal apply everywhere. That suite can often be the identity provider, which avoids a new license.
The main benefits are fewer passwords, faster onboarding, clean exits, and audit evidence on demand. New hires get the right apps on day one from their role. Departing staff lose access everywhere from one action. SOC 2 and ISO 27001 auditors get access review records instead of screenshots.
The hardest parts are apps without SSO support, messy groups, and pushback on MFA. Older tools may need a password vault such as 1Password instead of SSO. Groups built over years grant far more than anyone remembers, so we rebuild them from job roles. A pilot group keeps MFA from becoming a week of lockouts.
Identity management proves who a person is, while access management decides what that person can open. Identity covers accounts, passwords, MFA, and the lifecycle from hire to exit. Access covers roles, groups, permissions, and reviews of who holds them. Good identity management solutions handle both from one provider, which is why the two are sold together.
It works by making one identity provider the source of truth for every login. Apps trust that provider through SAML 2.0 or OpenID Connect, so people sign in once and MFA runs in one place. Groups map to roles inside each app, and SCIM can create or disable accounts automatically when HR records change.
Start with an inventory of every app and account, then choose one identity provider and roll out in waves. We connect the riskiest apps first: email, finance, and cloud consoles. A pilot team tests each wave. Leaver steps and admin separation come before the long tail of small apps, because they remove the most risk per hour.
Saimul IslamFounder & CEO, DeveloperLookStill have questions?
Send a message or book a call with the team.
Free 30-min callGoogle Meet
Book a call
In 30 minutes on Google Meet we walk you through how we would build it, how long it takes and what it costs. Then you get a written estimate.
Calendar not showing? Book on cal.com or send a brief.